
@nflux
Patoranking and Tiwa Savage made magic with this track.
XFEDI
ActivityPubFederated
HELLO, FEDIVERSE
Good conversations travel.
Public updates from xsukax and this corner of the network.
Sign In to your accountPublic posts known to this server, including selected instances.

For my latest project I've been lucky enough to work with several collaborators. Friends, colleagues and specialists.
This includes Dr David Mills @dtl
He kindly imaged some golf equipment for me.
(I'll also post a follow up)
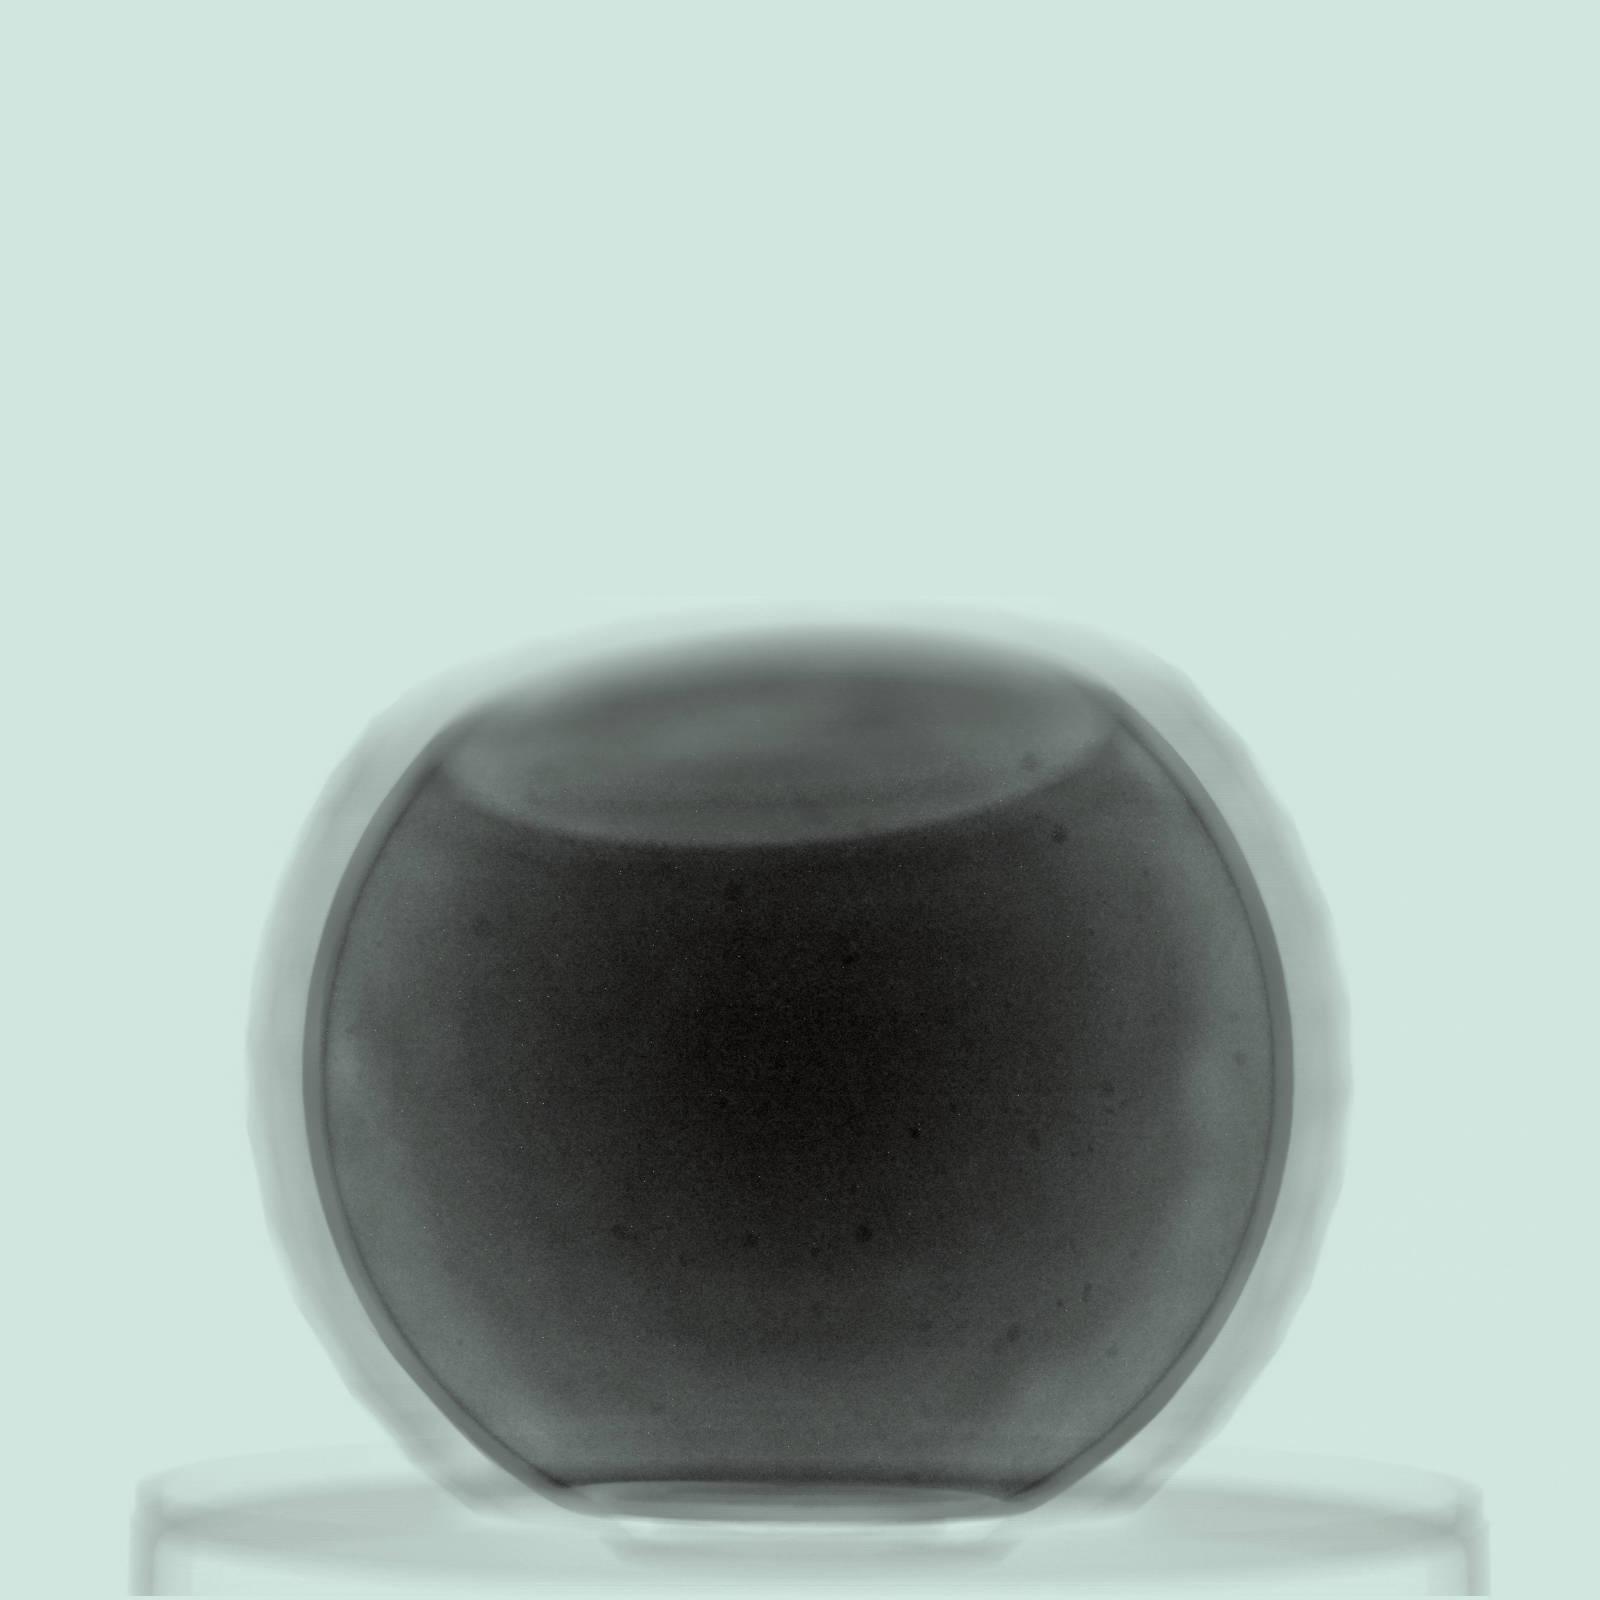
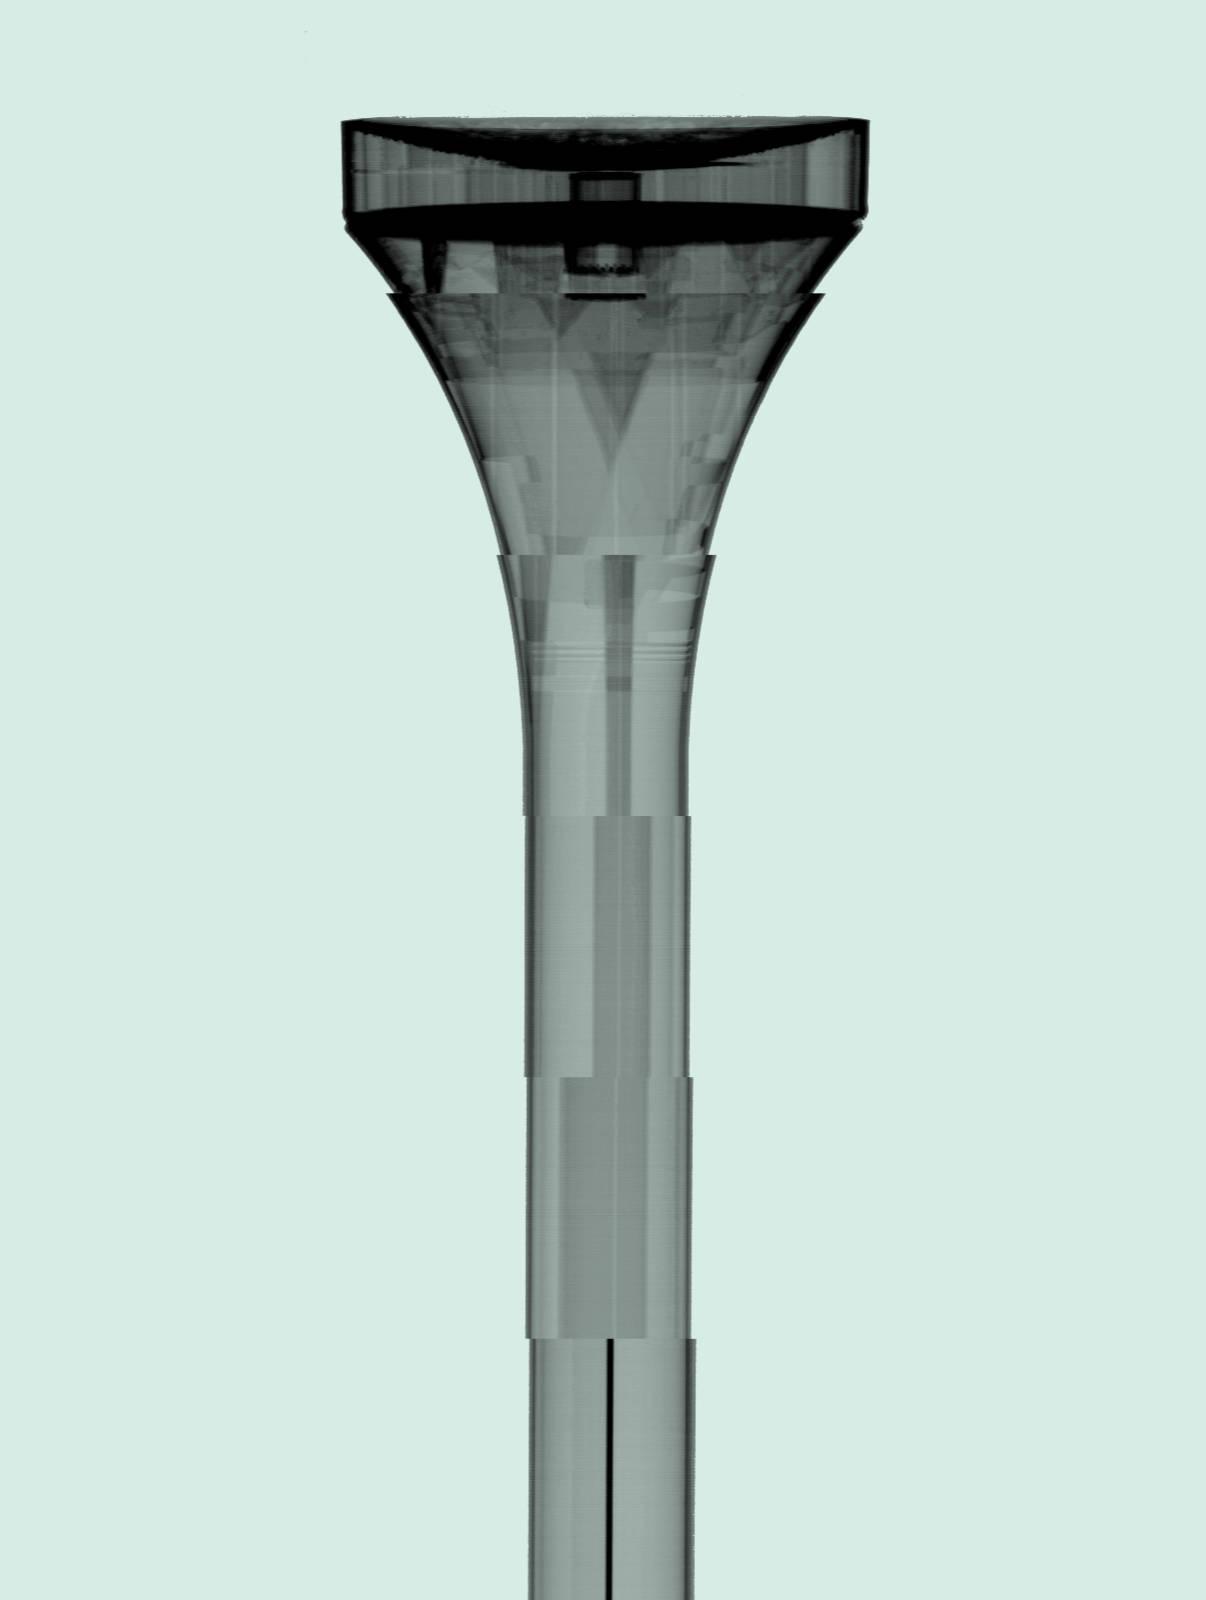
 slackwiseLuke Harby - Work - Spade-MashieLuke Harby. Artist working with photographic film.
🚨 Breaking: CVE-2026-111585 — High 8.8
Impacted if: TeamViewer Full Client < 15.83
Integer overflow · over the network · no login · a user must act
https://ax-news.com/cve/CVE-2026-111585
#CVE #infosec
 AX-NEWSCVE-2026-111585: TeamViewer Full Client integer overflow — High 8.8CVE-2026-111585 — High 8.8 · TeamViewer Full Client < 15.83; and 2 other products · Integer overflow · over the network · no login · a user must act. Covered by 1 outlets.

One under appreciated aspect of modern cyber security which comes into focus today with the news that (probably North Korean state) hackers have attempted to steal more than $6bn from Binance and got away with a huge proportion of that sum, is just how good ‘traditional’ banks and other financial institutions have become at cyber resilience when it comes to protecting deposits and transactions, in marked contrast to the seemingly terrible security in the crypto sector.
There is no way a compromised dev ops’ laptop in a bank gets a hacker access to $6billion.
Over the last decade, hackers have walked off with nine or ten figure sums from crypto hacks on more than thirty occasions. The number of traditional banks who have suffered a loss of more than $100million as a result of a cyber attack in the same period is zero or one (depending on how you categorise an event in Brazil last year). The last definite major notable bank event was the North Korean hit on the Bank of Bangladesh in February 2016 which saw them make off with $81 million, as Geoff White has so brilliantly chronicled.
Given the extraordinary hype around cyber security this month these details matter. First, based on what we know so far this hack was no some crazy new AI thing. The main technique used is long established. This event is entirely precedented - the only thing new about it is the amount stolen. Second; there is no specific cause for alarm over the financial system’s security in general as a result of this event: it’s been a notable success. Crypto on the other hand….
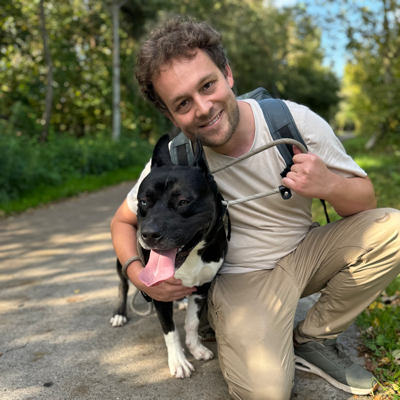
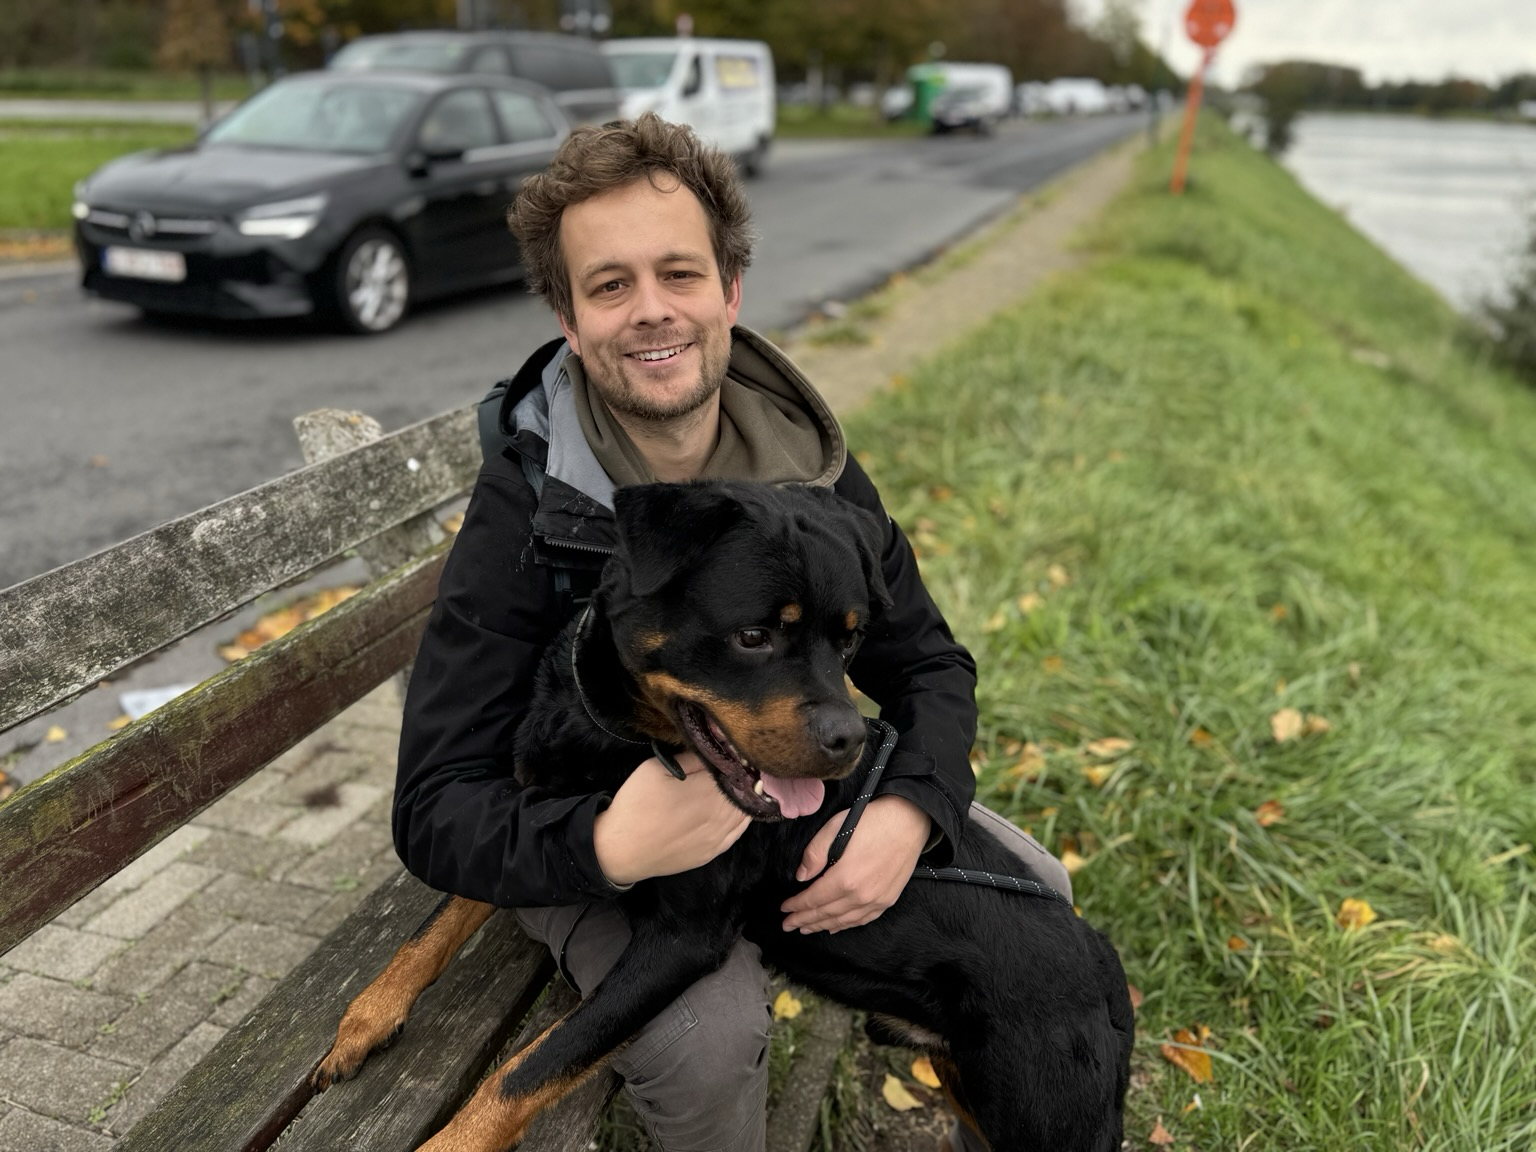
Walking a #Rottweiler from the animal shelter in #Ghent. He is a bit jumpy towards joggers but very likeable. He’ll need to learn to play with humans without biting.


Gemini 4 Carbon lidera la IA pero no está disponible
https://blog.elhacker.net/2026/10/gemini-4-carbon-lidera-la-ia-pero-no.html
 Blog elhacker.NETGemini 4 Carbon lidera la IA pero no está disponibleBlog sobre informática, tecnología y seguridad con manuales, tutoriales y documentación sobre herramientas y programas
The naira's exchange rate (as with most prices in a market economy) is a signal of how demand and supply are aligned — or not.
Address the causes of the misalignment, rather than taking the economic motor to a quack auto repair shop to adjust the dials to your preferred reading.

Požar, eksplozija 30. 10. 2026 08:56
Ob 8.56 je v naselju Završe v občini Mislinja gorel traktor. Gasilci PGD Mislinja in PGD Dolič - Šentflorjan so zavarovali kraj dogodka, odklopili akumulator, pogasili požar in požarišče pregledali s termovizijsko kamero. Poškodovanih ni bilo.
https://spin3.sos112.si/javno/zemljevid/473749
Tehnična in druga pomoč 30. 10. 2026 10:25
Ptuj
https://spin3.sos112.si/javno/zemljevid/473757
Požar, eksplozija 30. 10. 2026 10:18
Celje
https://spin3.sos112.si/javno/zemljevid/473756

Veja a letra da música “Brainless” de Eminem
#Eminem #Brainless
https://daletra.com.br/eminem/letra/brainless.html

 DaLetraBrainless - EminemOr Eminem has a full line of chainsaws. Eminem, Eminem, Eminem, Eminem, Eminem, Eminem. Marshall Mathers, Eminem, the rapper, Eminem. Who can say for sure?

Hands-on research at Berlin Science Week
Berlin Science Week offers activities at research centers, museums and cultural venues for anyone who wants to discover something new. Here's what visitors can expect at the science festival.
https://www.berlin.de/en/news/10726964-5559700-handson-research-at-berlin-science-week.en.html
#berlin #news
 berlin.deHands-on research at Berlin Science WeekBerlin Science Week offers activities at research centers, museums and cultural venues for anyone who wants to discover something new. Here's what visitors can expect at the science festival.

[2172576] Selecting "cancel" from the restart confirmation dialog doesn't cancel the restart
 LaunchpadBug #2172576 “Selecting “cancel” from the restart confirmation d...” : Bugs : update-manager package : UbuntuSteps to reproduce:
1. use update manager to install updates that require a restart
2. after installing the updates, update manager asks whether to restart now or later: select restart now
3. realize you have unsaved work, so from the additional restart confirmation dialog that pops up, select "cancel"
What I expect to happen
For the restart to get cancelled
What happens instead
A restart; ther
Encore un qui ne sait pas ce qu'il dit :
« Le PIB recule de 0,1 % au troisième trimestre 2026 en France, le ministre de l'Économie déplore ‹ une économie à l'arrêt › »

Sexy Sadie #TheBeatles

Short Video 420 Nintendo Switch 2 ニンテンドースイッチ2 Mario Kart World マリオカートワールド https://www.youtube.com/watch?v=GYsmQhYeBPY
This has to be top poshness:
Neighbours dismayed at the embassy flying a "tacky looking" and "gaudy" flag (their country flag)
An American resident is concerned by the "impact on her mental health of the arrival next door of Montenegro, a country that has been involved in recent scrapes with Russia." (surely the USA has not been involved in recent scrapes with anyone recently)
"Some of those critics, frustrated by the lack of planning application before the installation of the embassy flagpole and plaque, were somewhat placated when drinks were put on by the chargé d’affaires of the west Balkans state."
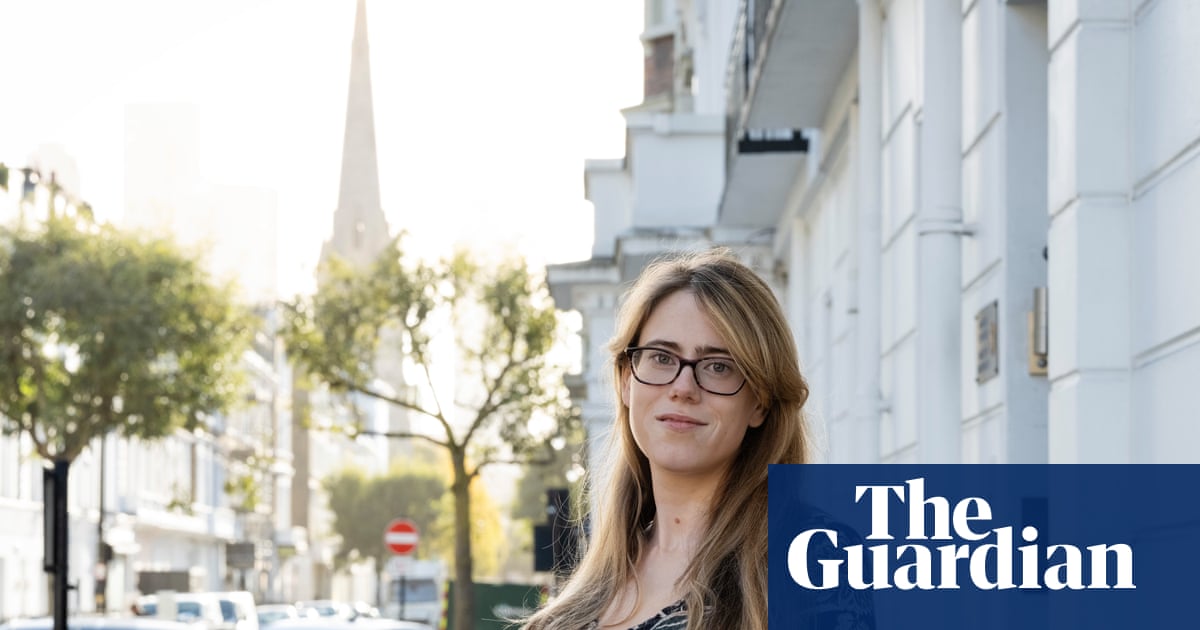 the GuardianNeighbour of new Montenegro embassy in London sues council over impact on mental healthExclusive: Case in Pimlico is latest instance of tensions between residents and small countries seeking a space in the capital
@nflux
Smooth lovers rock vibes from Patoranking on this one.
A sneaky peak into something new I've been tinkering on in my free time 👀
I've wanted a semi-realistic way of representing data about energy and wind farms for a while now. And now I finally have it!
It's an interactive WebGL scene in a Web browser that you can move around in. Change the time of day, move clouds, make the sea stormy, etc.
The wind turbine and ship models are custom-made, that's been the most fun (and critical) part of all this.
Maybe it should be a game? That could be fun…

Redmayne goes for 58 (44) c Cheatle b Coyte.
Heat 138/4 (17.5) have lost 3/21.
#WBBL12 #T20
#cricket #womenscricket
https://cricket.com.au/matches/CA:40623/brisbane-heat-women-sydney-sixers-women-weber-wbbl-12

Spannend
Há ainda três cidadãos portugueses em prisão efectiva e um em prisão domiciliária, divulgou Rangel durante audição do Orçamento de Estado de 2027.
https://www.publico.pt/2026/10/30/mundo/noticia/quatro-portugueses-continuam-presos-razoes-politicas-venezuela-2193154 #notícias
"""
On the earnings call, executives admitted that Google's Gemini-powered AI mode search queries make less money, at least right now, than traditional search. Google search users are actually spending more time with AI mode, but that isn't converting to revenue for search in the way that it used to pre-AI mode. And this is the argument that Google executives were making, which is, yes, we've lit the search business on fire because of AI mode, but we have plans to monetize AI mode, too. Analysts were unconvinced, and the market decline followed.
"""
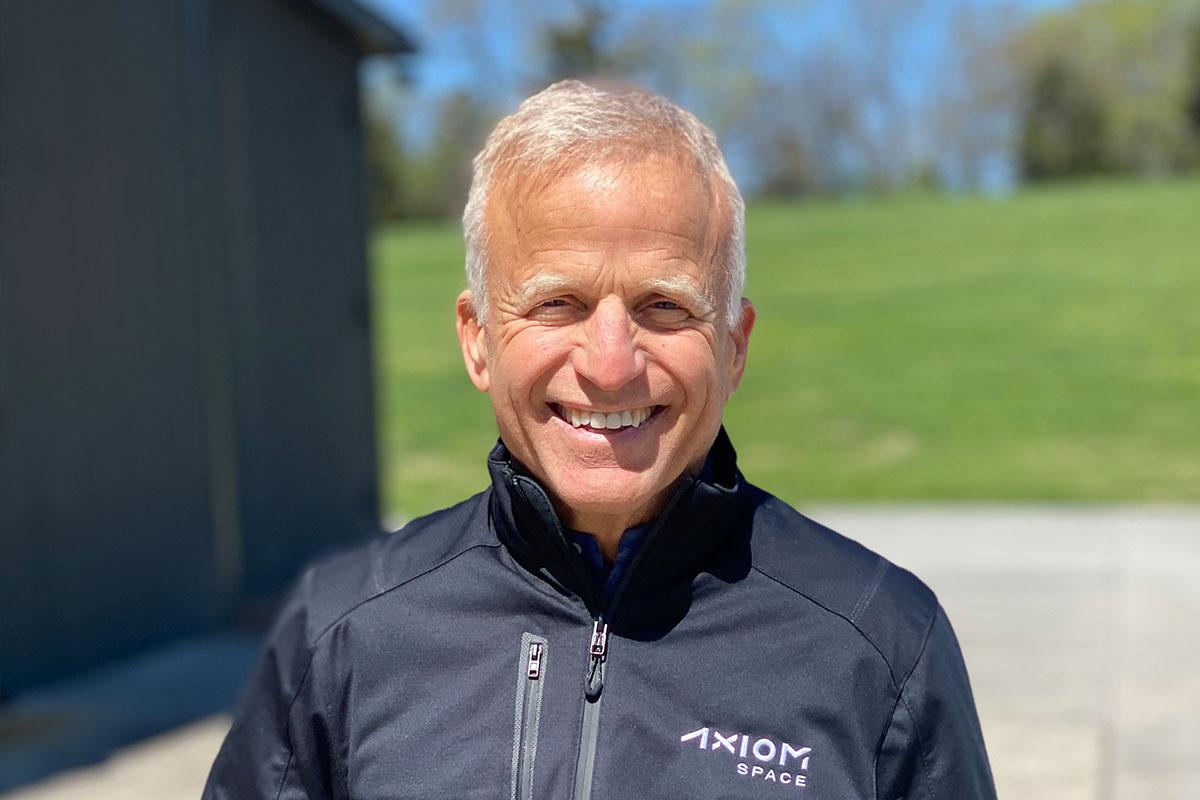
Astronaut spotlight
John Shoffner (Occasional Spaceflight)
Date of Birth: 27/07/1955
Nationality: American
Agency: Axiom Space
First flight: 21/05/2023
Last flight: 21/05/2023
John Shoffner is an American space tourist. He is according to Axiom Space a pilot, champion GT racer, and active supporter of life science research from Knoxville, Tennessee....
Good morning peeps! It's Friday! TGIF to all it applies! I work today and tomorrow. We are a bit cooler and the leaves are falling fast. I hope everybody has a fantastic day! Be safe! Be kind! Be you! Peace, Love and Harmony
Zionism in action.
--
(and for those of you who only give a shit about western victims, the victim was a us citizen)

Gibt es eigentlich eine App für Schülys, um die verschiedenen Arten des Unterrichtsausfalls an Schulen zu erfassen?
Das wäre mal eine interessante Visualisierung...
https://www.tagesschau.de/inland/gesellschaft/unterrichtsausfall-klage-rheinland-pfalz-100.html
 tagesschau.deKlage in Rheinland-Pfalz: Wie viel Unterrichtsausfall ist zu viel?Ein ehemaliger Schüler verklagt das Land Rheinland-Pfalz, weil während seiner Oberstufenzeit zu viel Unterricht ausgefallen sein soll. Mit dem Fall beschäftigt sich jetzt das Verwaltungsgericht Neustadt. Von C. Kehlbach und H. Diekert.
☁️#ANM (☁️#AutoritateaNaționalăMeteo): 🟡#CodGalben de ploi în cinci județe, de sâmbătă dimineața.
Ninsori în zona Carpaților Meridionali.
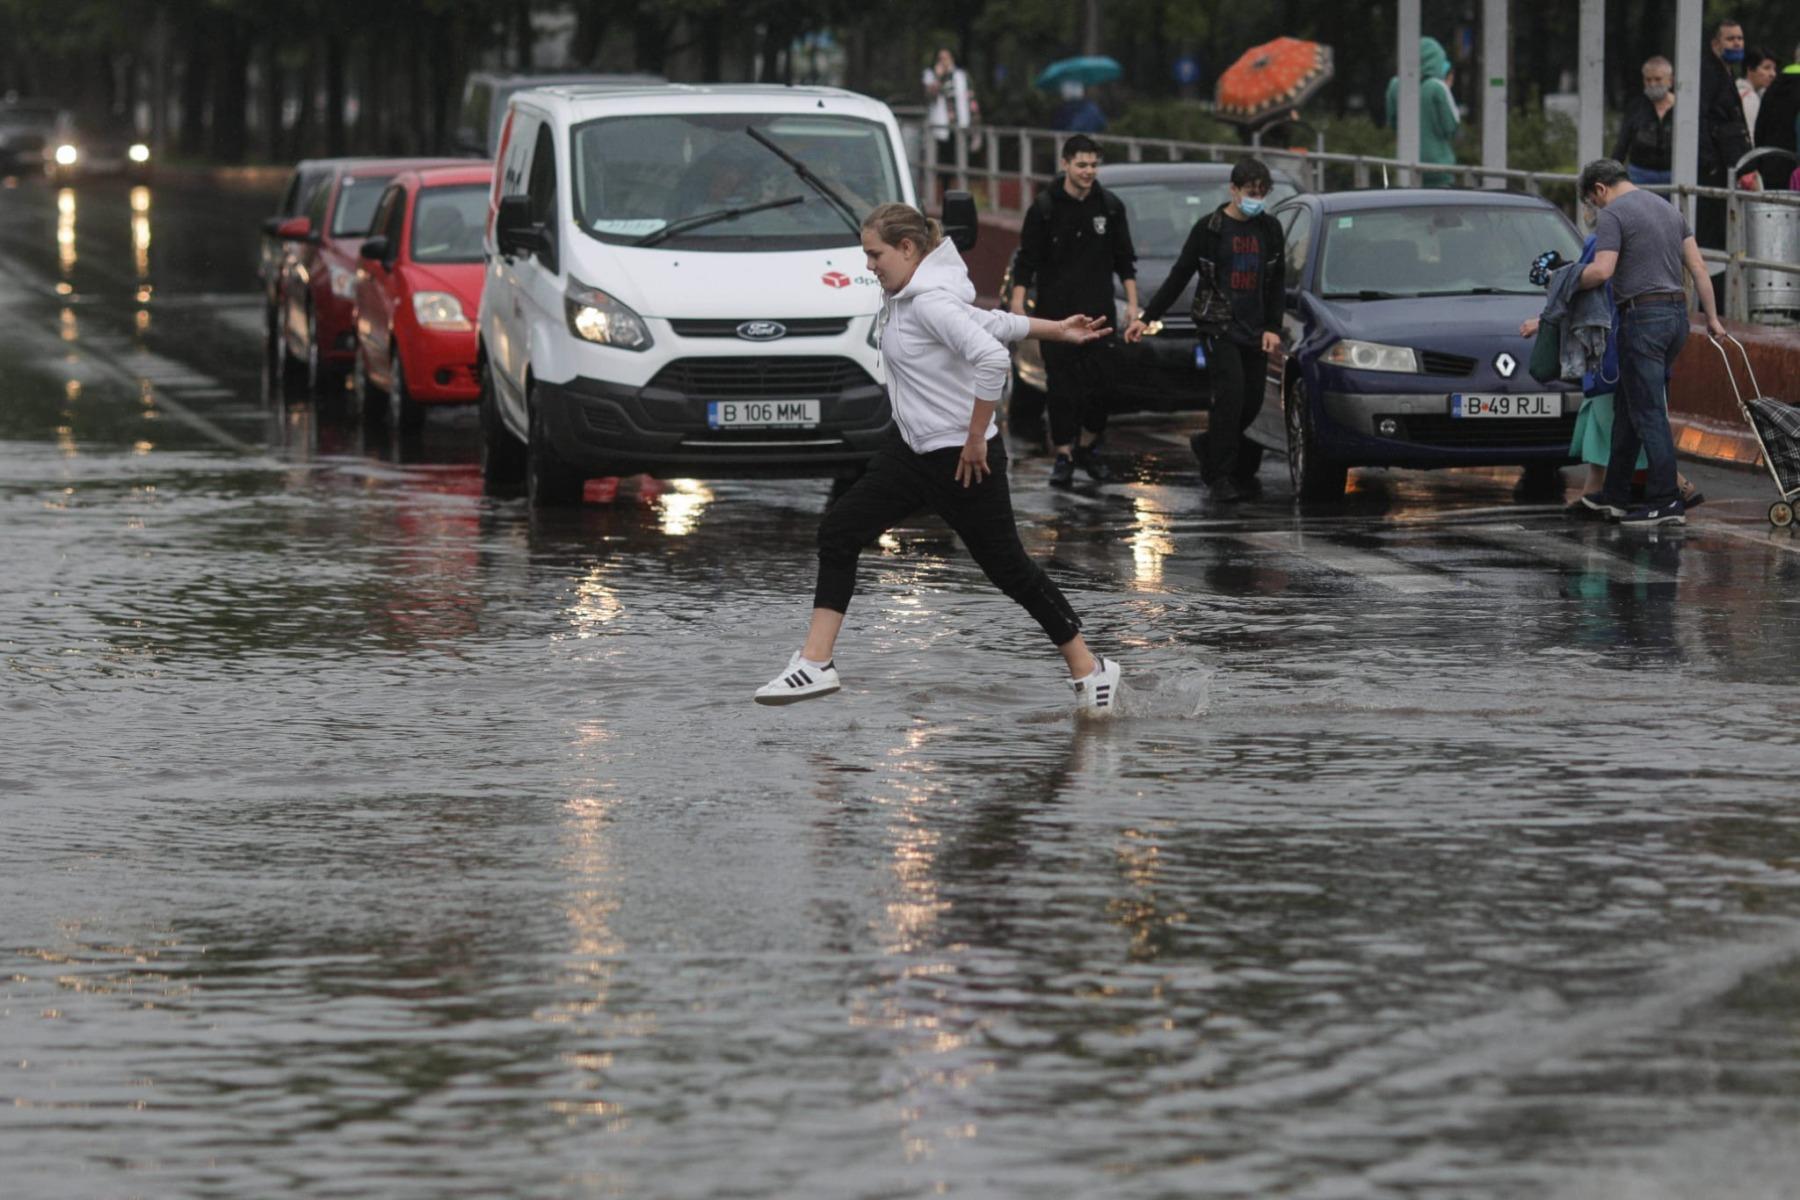
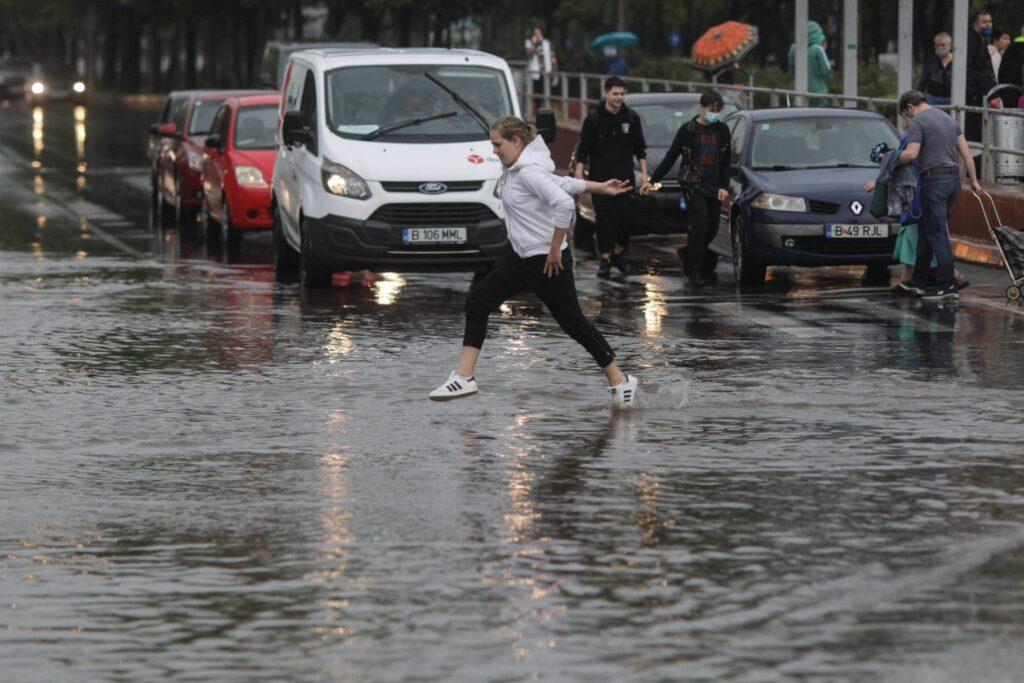
 G4Media.roANM: Cod galben de ploi în cinci judeţe, de sâmbătă dimineaţa / Ninsori în zona Carpaţilor MeridionaliAdministraţia Naţională de Meteorologie (ANM) a emis, vineri, o atenţionare Cod galben de ploi în cinci judeţe, dar şi de ninsori în Carpaţii Meridionali, valabilă până duminică dimineaţa, relatează Agerpres.
CVE-2026-119144 — Frappe Framework SSTI, CVSS 8.8
The CVE describes DB read/write via Jinja2 template injection. The August research describes the full chain: frappe.new_doc writes a Python file, frappe.db.set_value registers it as an installed app, frappe.call executes it. Shell as the frappe user.
The only sandbox was a string check for ".__" — bypassed by calling privileged functions by name.
Patch: 15.111.0 / 16.21.0 (Framework), 15.119.1 / 16.32.0 (ERPNext).