X XFediYour place in the Fediverse
XFEDI

Federated

ActivityPub
HELLO, FEDIVERSE

Good conversations travel.

Public updates from xsukax and this corner of the network.

Sign In to your account

Public posts known to this server, including selected instances.

Documents reveal the US military is developing an agentic AI system called ECHOTRIBBLE designed to autonomously hack adversarial networks. Still in the whitepaper phase, the tool represents a new frontier in autonomous cyber operations powered by AI agents. https://gizmodo.com/documents-reveal-military-plan-for-agentic-ai-that-hacks-u-s-adversaries-2000827957 #AIagent #AI #GenAI #AIGovernance

GizmodoDocuments Reveal Military Plan for Agentic AI That Hacks U.S. AdversariesThe tool, called ECHOTRIBBLE, is still in the whitepaper phase.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

----------------

🎯 AI
===================

NorForge published an investigation into publicly exposed control panels of AI-driven penetration-testing systems, with Cairn as the central case. The value here is documentation of actual offensive use of autonomous agent stacks, not a threat model on a slide.

Context

In September 2026, Gambit Security reported a criminal intrusion campaign against online marketplaces. The recovered attacker staging server showed AI harnesses in active use: Hermes, Strix, and Cairn. These tools ship with web UIs, and operators keep putting them on the open internet. Shodan and Censys queries surface hosts running various harnesses. Most require authentication. Some do not.

Findings per the source
• More than 20 exposed Cairn panels were assessed as likely associated with malicious activity. Targeting data, language, and task instructions connected several panels to the same actors.
• Panel content is unusually rich. A single open panel can disclose target identity, discovered weaknesses, account secrets, API keys, and whether a compromise already succeeded. One captured task view even showed root access to the attacker's own data drop.
• Legitimate red team operations appear in the same search results, which potentially puts their clients at risk.
• NorForge redacted extracted data aggressively and is withholding panel addresses until takedown. Treat instance-level specifics as unverified until publication.

How Cairn works
• Each task is a project with a defined origin and a predefined goal. The authors position Cairn as a state-based problem-solving engine rather than a dedicated pentest engine.
• Progress cycles through intents and facts. A fact is something an agent discovered. An intent is the next action it decided on.
• Facts go to a project-internal blackboard. Human operators can inject hints onto the same blackboard, and every worker agent reads it.
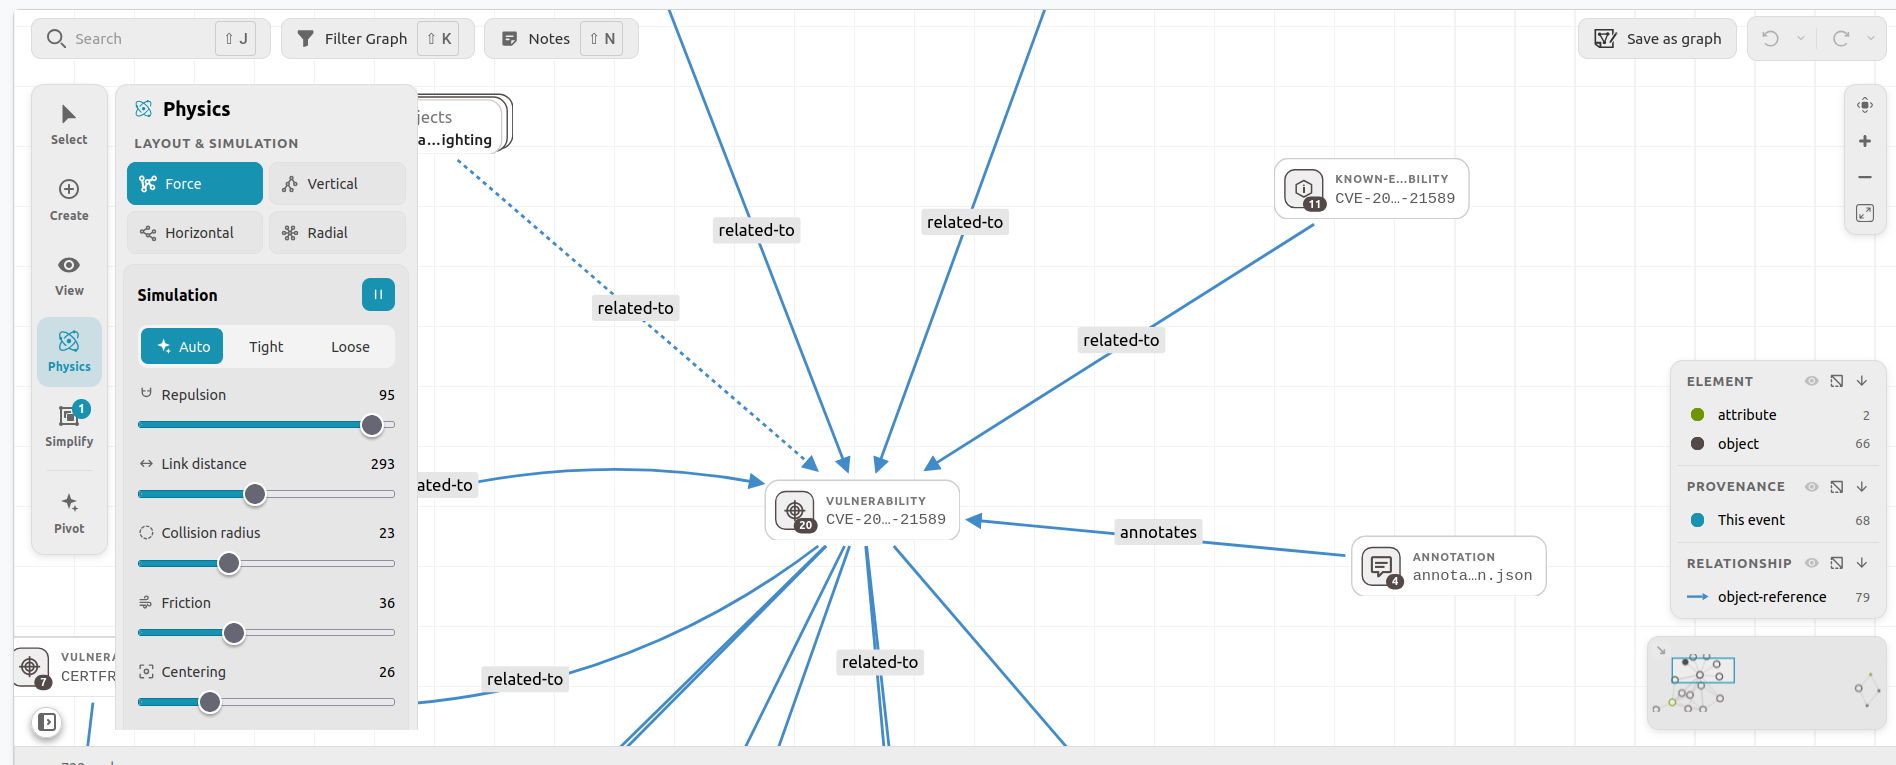
• The state graph renders visually. In the cited example, an attack against a major US online retailer converged from origin to a stated end of "GOAL MET: Webshell injected into the site."

Attack chain as described

1. Target selection: the operator feeds a target and objective in as a project.
2. Reconnaissance: agents investigate the target and post facts to the blackboard.
3. Exploitation: intents direct probing of weaknesses and break-in attempts.
4. Persistence: the sample run ended with a webshell injected into the site.

Implications, stated plainly:
• Agent-loop observability cuts both ways. The same blackboard that coordinates an attack also logs it for anyone who finds the panel.
• Anyone running agent harnesses should give the web console admin-panel treatment: authentication, network restrictions, and rotation of any keys that passed through it.
• Red teams should inventory their own deployments. Per the source, client exposure is a real risk, which is an uncomfortable finding for the industry.

Attribution remains the researchers' assessment, not confirmed actor identification. The available article text cuts off mid-section, so the full report may add detail on the legitimate operators.

🔹 Cairn #AISecurity #ThreatIntelligence #AutonomousAgents #OSINT

🔗 Source: https://norforge.com/blog/inside_cairn

NorForgeInside Cairn: Open Windows into massive AI-Driven Cyber Operations - NorForgeNorForge research into publicly exposed Cairn AI pentesting panels: how threat actors select targets, direct autonomous agents, exploit vulnerabilities, and expose their victims' secrets in the process.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

I never truly understood the micromanagement quality-gatekeeping in #OSS. Surely, from past experience, we can expect that X will have more favourable tradeoffs than Y. But as long as Y provides direct value to the user with potential refactoring Y->X without change to the surface API, then why not accept? Why have lingering PRs for years? Why discourage contributors? Why defer value?
Ultimately every codebase is a spaghetti pile of crap. Relatively, subjectively and as time goes objectively.

↩ Reply ♡ 0 · ↻ 0 ↗ Original

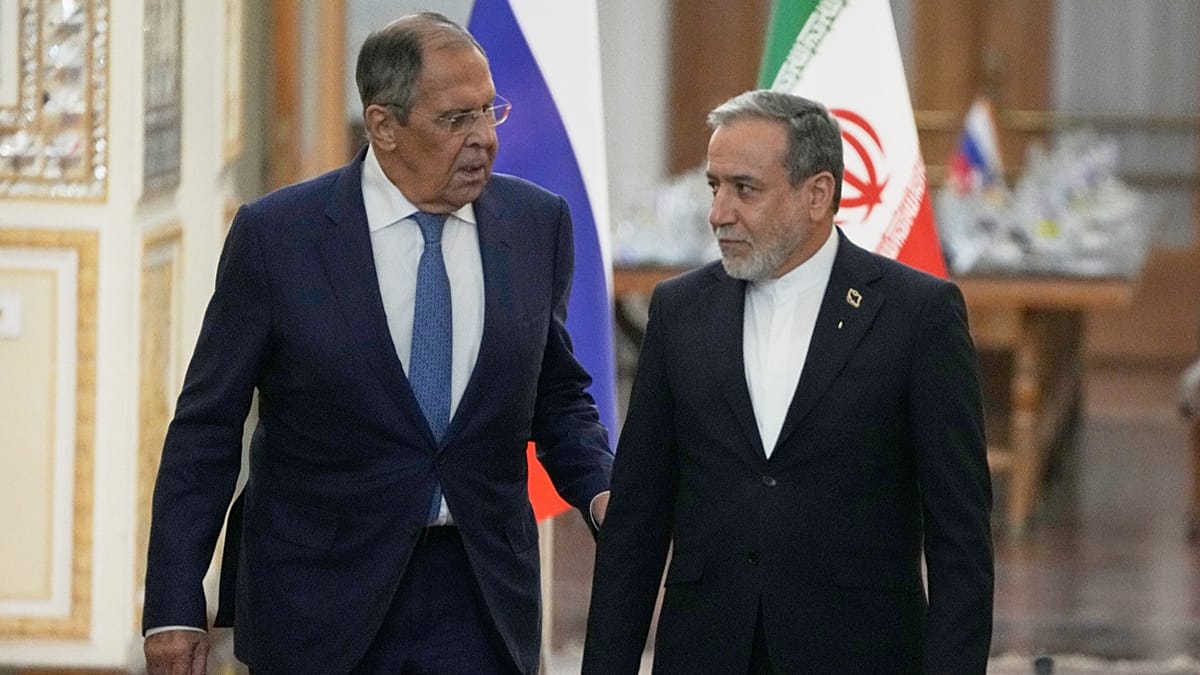
"I am confident that Iran's cause, like Russia's, is a just cause," Russian Foreign Minister Sergei Lavrov said on Monday at a joint press conference in Tehran with his Iranian counterpart, Abbas Araghchi. https://www.euronews.com/2026/10/19/lavrov-backs-iran-hours-after-trump-says-russia-doing-very-little-to-help-tehran

euronewsLavrov backs Iran after Trump says Russia doing 'little' for TehranJust hours after Trump publicly claimed Russia was doing “little” to help Iran, Moscow reaffirmed its full support for Tehran, with Foreign Minister Lavrov describing Iran's fight as a "just cause." #EuropeNews
↩ Reply ♡ 0 · ↻ 0 ↗ Original

https://www.google.gp/share.google?q=JlyJRckxoebGdkHhJ&vGe4139YUaNHSfUdSNRW

@coppercrush @fuzzy @jasontheaverage @justmichelle @surdfish @mebbiedraws @marcelcosta @RunicArmasaur @little_foxtoy @Baransu @Barrelephants @barTouf @barefootwarrior @buyildiz @TomBardout @757fd51791131e51eb033538721ba67a526466c26ed5940a56962d94f8d83c53 @96ae8563bd224ac9fa384aabcaf409124eb07ab1be074e51b9f17b00c1d02337 @toddbarn33 @CaperBill @BEEPS @beepbopbleep @coe @hamaca @collignonjos @_tillwe_ @lolercoaster @urofuchs1 @jlagrue @Trudo @AndreasEK @mestressadecasa

↩ Reply ♡ 0 · ↻ 0 ↗ Original

RE: https://mastodon.online/@BrentToderian/117471045554723882

This. 🎯

#Alberta #Referendum #Canada #NationalSecurity #CanadianSovereignty #Democracy #ForeignInterference

❞ Quoted postBrent Toderian

As Canada awaits the Alberta separation referendum results, let’s remember how stupid this all is. Huge public money spent on a Russian & American-fuelled separation movement for an awfully-written and badly managed unbinding referendum on whether to hold a binding referendum tha

Mastodon.onlineBrent Toderian (@[email protected])As Canada awaits the Alberta separation referendum results, let’s remember how stupid this all is. Huge public money spent on a Russian & American-fuelled separation movement for an awfully-written and badly managed unbinding referendum on whether to hold a binding referendum that would be illegal.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Piloted flights protecting Scotland's waters from illegal fishing have more than halved due to cutbacks
https://www.theferret.scot/flights-illegal-fishing-cutbacks/

The FerretPiloted flights protecting Scotland's waters from illegal fishing have more than halved due to cutbacksThe Scottish Government is selling surveillance planes to save money and says drones are used to prevent illegal fishing. But critics argue that losing experienced pilots could mean criminality goes unchecked.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Just in case you see any headlines about Alberta voting to remain a province of Canada tomorrow, please remember that we actually voted to not have a second vote where we would decide whether or not to start a formal process to leave Canada, a thing that is basically impossible for us to do regardless of votes. The whole thing was an idiotic waste of money, astroturfed by American and Russian interests, that was never meant to amount to anything but continuing to keep our fascist government's far-right core base good and riled up for a few more years.

Oh, also we voted 'yes' on all of the fun bonus questions that amounted to 'do you hate brown people?', so this province still fuckin' sucks, for the record.

↩ Reply ♡ 0 · ↻ 0 ↗ Original

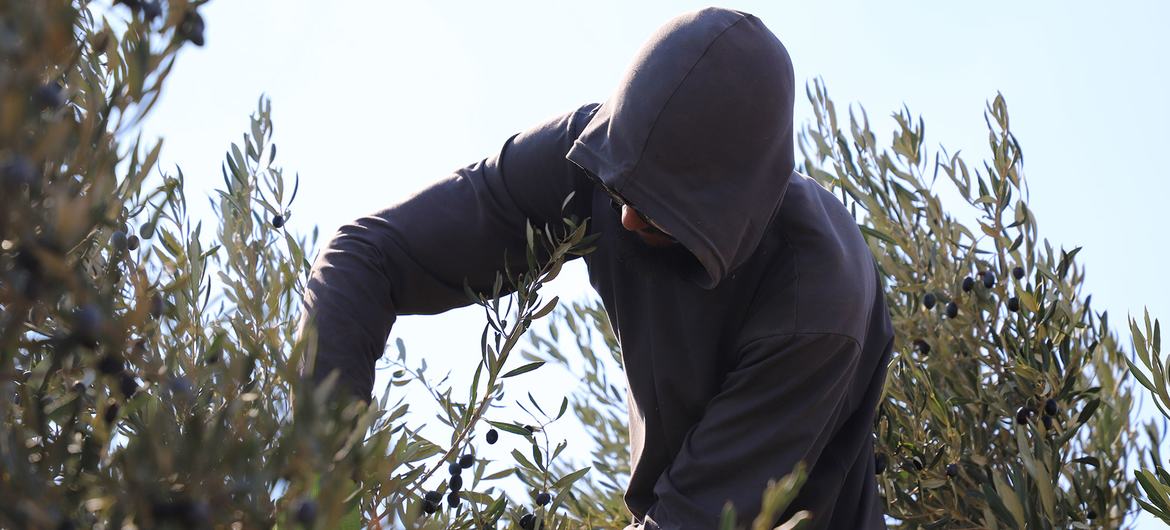
‘Season of fear’: Escalating Israeli attacks on #WestBank olive farmers, deadly strikes on #Gaza
https://www.globalissues.org/news/2026/10/19/44379

www.globalissues.org‘Season of fear’: Escalating Israeli attacks on West Bank olive farmers, deadly strikes on GazaIsraeli attacks on war-torn Gaza over the weekend killed at least six Palestinians, including children, despite a year-old ceasefire agreement. Meanwhile, in the occupied West Bank, settler violence continued through the ongoing olive harvest, with UN independent experts on Monday urging Israel to protect Palestinian farmers.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

https://www.google.ae/share.google?q=iSdAVsResTvxI9Hoz&IYz6069oyPOrYlQO

@dulcedemon @pernia @beef @beer_nondaro @nichiyou_bee @beedee @Beere @AaronDavid @Gorfram @Neat_hot @SteveJB @Te_Kanawa @amiserabilist @capnwatsisname @dottygumboots @flux @jakery @johncomic @melindrea @meyltje @mycotropic @sunumbral @thomas @vac @beizero @Beehaw_Girl @savvyhomstead @BeerAndMala @barrbaric @BarefootScott @Bart @barnaby__jones @MrNobody @Beeschurger @beeside @beethescientist @beesis @Kristine @JustFi @QueenRandumb @Shelly @Suzdal92 @Thatmermaid_J @bkahn

↩ Reply ♡ 0 · ↻ 0 ↗ Original

MISP Modules v3.0.13 is a substantial release, bringing a new wave of OSINT and threat intelligence enrichment capabilities, new ways to export indicators into operational security tools, and new workflows for publishing IOCs directly to security platforms.

@misp

🔗 https://github.com/MISP/misp-modules/releases/tag/v3.1.0

#misp #cti #threatintel #intelligence #cybersecurity #osint

vulnerability-lookup expansion modules in MISP 3.0
GitHubRelease MISP Modules v3.1.0 - More pivots, more integrations, more actionable intelligence · MISP/misp-modulesMISP Modules v3.0.13 is a substantial release, bringing a new wave of OSINT and threat intelligence enrichment capabilities, new ways to export indicators into operational security tools, and new w...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

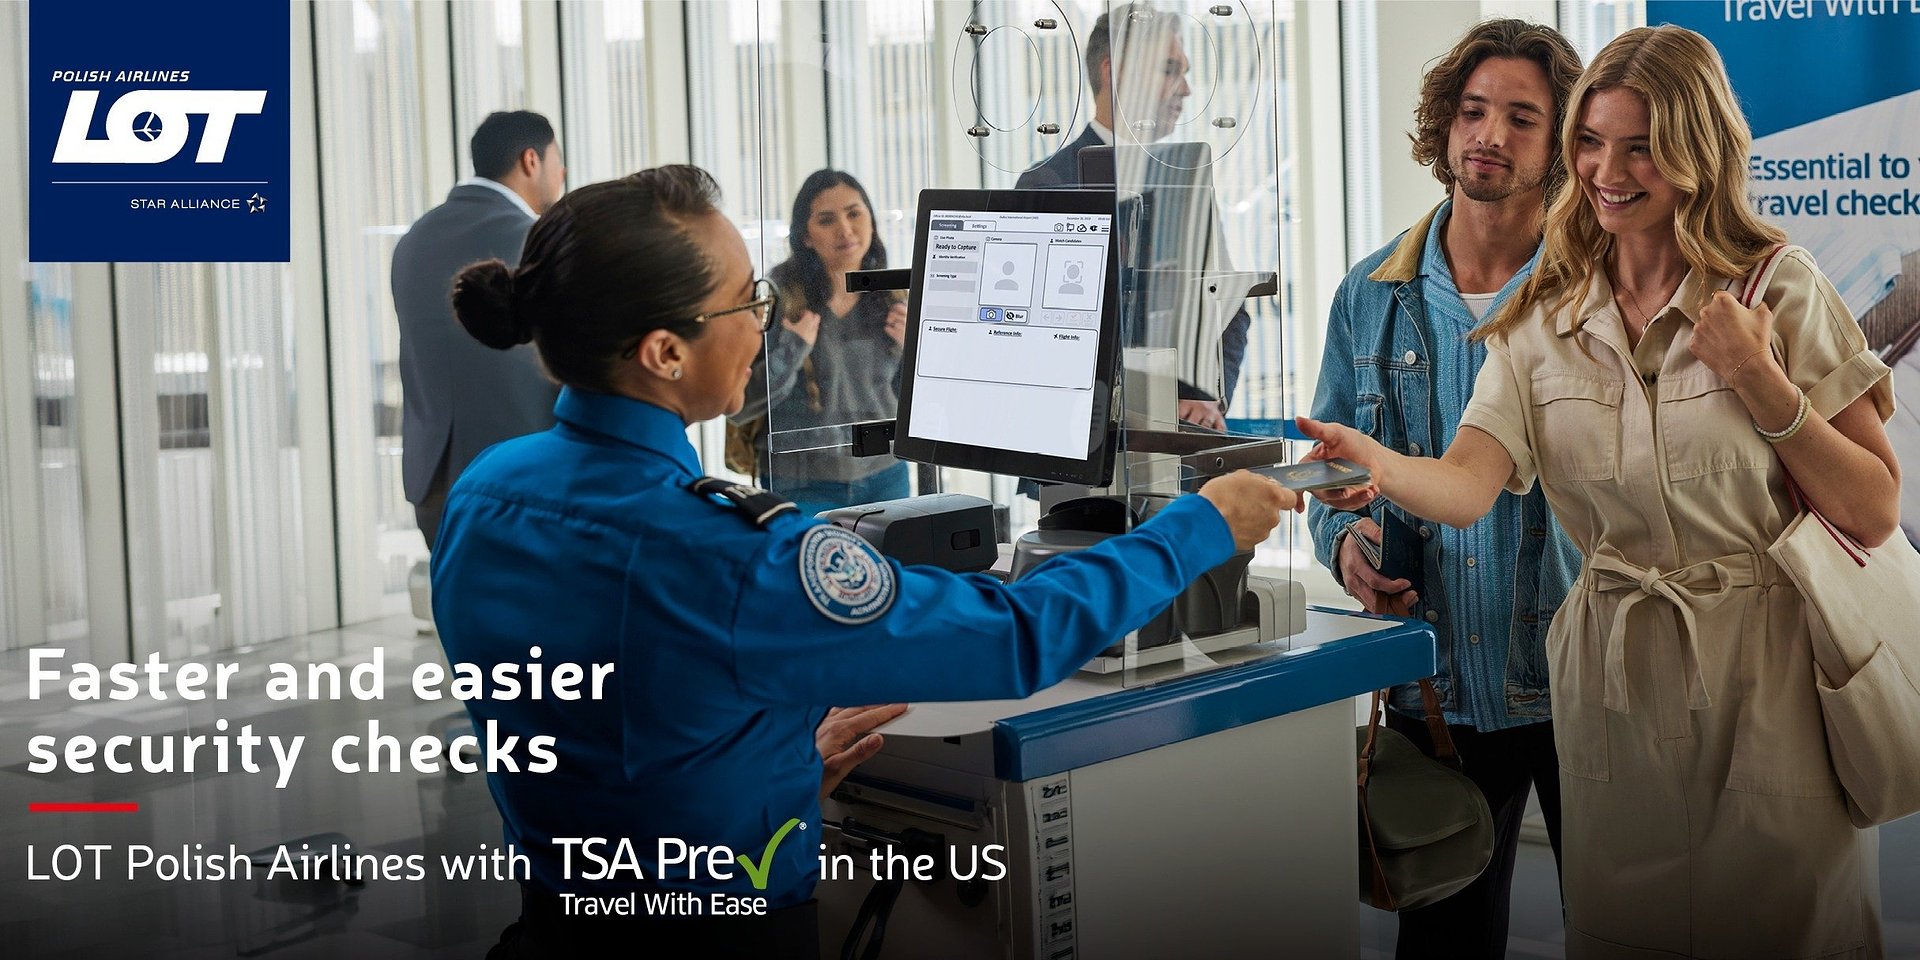
Aviation24: lot joins tsa precheck for departures from us airports: https://www.aviation24.be/airlines/lot-polish-airlines/lot-joins-tsa-precheck-for-departures-from-us-airports/ #airline #skynews #airlinenews #news

Aviation24.beLOT joins TSA PreCheck for departures from US airportsLOT Polish Airlines has joined TSA PreCheck, allowing eligible passengers departing from participating US airports to use dedicated expedited security
↩ Reply ♡ 0 · ↻ 0 ↗ Original

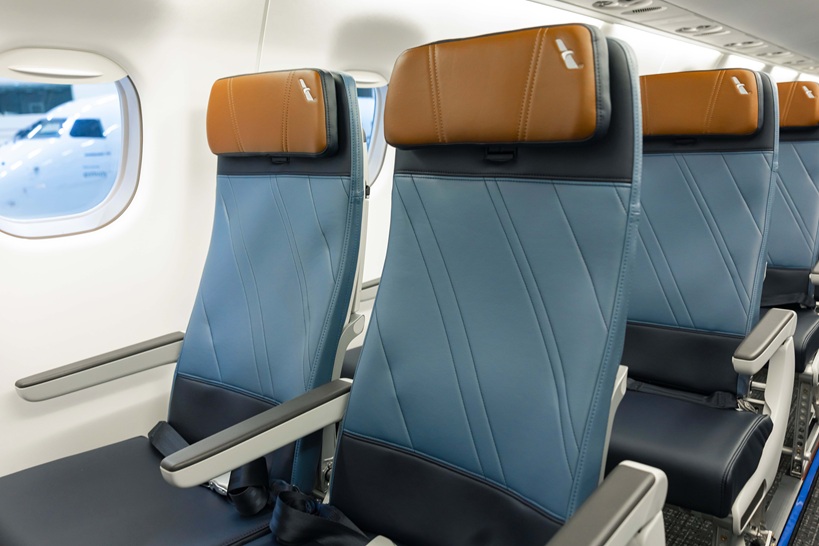
Aviation24: american airlines receives first embraer e175 with recaro r2 seats: https://www.aviation24.be/airlines/american-airlines/american-eagle/american-airlines-receives-first-embraer-e175-with-recaro-r2-seats/ #airline #skynews #airlinenews #news

Aviation24.beAmerican Airlines receives first Embraer E175 with RECARO R2 seatsEmbraer has delivered the first E175 equipped with RECARO R2 passenger seats to American Airlines, introducing a cabin upgrade intended to improve comfort
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CISA to AI labs: Share test-network IPs to flag rogue agents

CISA urges AI labs to share IP addresses to track rogue agents threatening critical infrastructure. While transparency could boost cybersecurity, experts debate its practicality due to cloud complexity and AI's dynamic nature. Alternative solutions like detection signatures are suggested. Public sector orgs should proactively test AI systems and prioritize vulnerability patches.

https://www.techtarget.com/cybersecurity/news/366651845/CISA-to-AI-labs-Share-test-network-IPs-to-flag-rogue-agents

#InfoSec #CyberSecurity

CybersecurityCISA to AI labs: Share test-network IPs to flag rogue agents | TechTargetCISA urges AI labs to share IPs and ASNs so defenders can recognize and flag rogue agents early. Research analysts, however, had mixed reactions. Learn why.
↩ Reply ♡ 0 · ↻ 0 ↗ Original