X XFediYour place in the Fediverse
XFEDI

#AppSec

ActivityPub

Public posts with this hashtag.

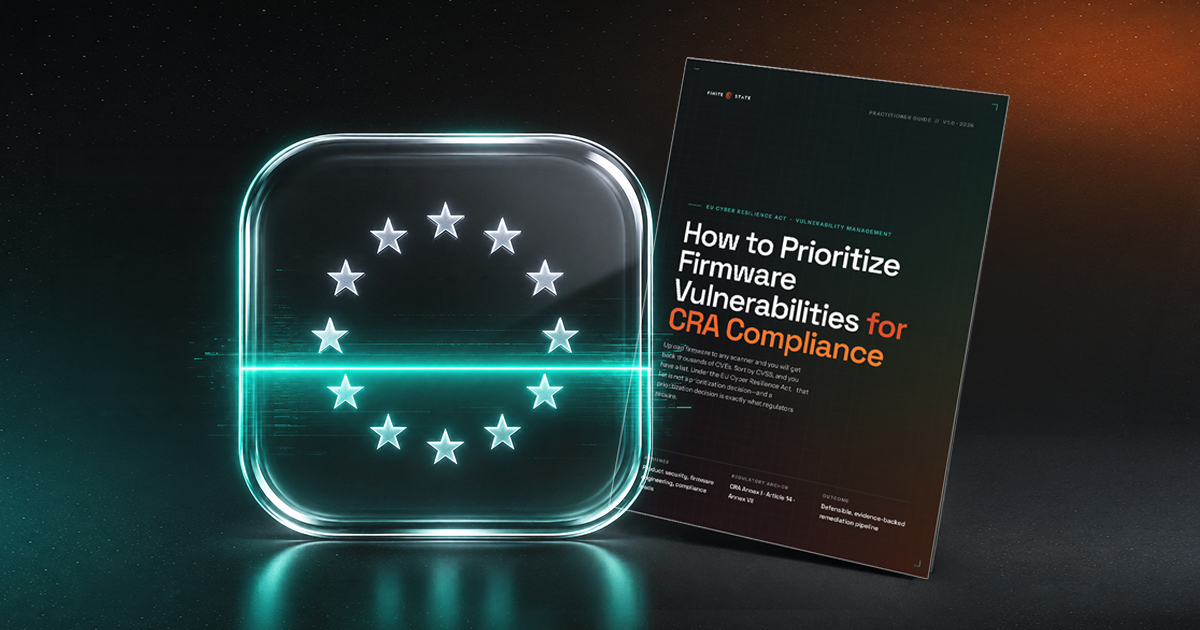
Firmware scanners can return tens of thousands of CVEs, but the EU Cyber Resilience Act (CRA) expects remediation decisions to be risk-based, proportionate, and documented.

How do you find the signal in the noise? 🔍

Our Silver Sponsor, Finite State, put together a practitioner's guide outlining a 5-step framework to filter out low-impact noise using CVSS, EPSS, and binary reachability.

Read the guide here: https://finitestate.io/resources/how-to-prioritize-firmware-vulnerabilities-cra-compliance

Thank you, Finite State, for your support this year!

#AppSec #CyberResilienceAct #FirmwareSecurity #VulnerabilityManagement #SBOM

Media attachment
finitestate.ioHow to Prioritize Firmware Vulnerabilities for CRA ComplianceCut 26,000 firmware CVEs to a defensible 47-item list. Learn the CVSS, EPSS, and reachability framework the EU Cyber Resilience Act actually requires.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Do you have any last minute question before the Open Security Conference? Check our FAQ, the answer might be in there already: https://opensecurityconference.org/faq/

Your point is not covered? Feel free to reach out :) https://opensecurityconference.org/contact/

We will soon send more information to all participants so you can prepare for the event. We're already looking forward to welcoming you!

#osco #osco26 #Security #CyberSecurity #InfoSec #AppSec [lisi]

Open Security ConferenceFAQWelcome to the Open Security Conference (osco), the people-centred international gathering for everyone interested in cybersecurity. Join us 5-8 November 2026 in Rückersbach, Germany.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
T

🚨 17 CVEs across 12 AI agent frameworks — one disclosure wave, same three design failures.

6× CVSS 9.8 unauthenticated RCE:
- Piflow: POST /chat → exec_shell, no auth
- Langchain-Chatchat: /tools/call invokes shell tool, no auth
- DB-GPT: mock auth grants everyone admin
- Letta: compose.yaml omits LETTA_SERVER_SECURE, all routes open
- Cognition: no auth on REST/SSE API (fixed: 0.13.0)

5× 8.8: approval gates return True, unsandboxed python3, async sub-agents skip interrupt_on.

2× 8.3 IDOR: IBM Langflow OSS (fixed: 1.12.5), Coze Studio (fixed: 0.5.2).

7 products have no published fix. Put an auth proxy in front, bind DB ports to localhost, and rotate every secret in the execution environment.

https://threataft.com/articles/ai-agent-framework-rce-mega-cluster-17-cves

#InfoSec #AIAgent #LLM #RCE #CVE #AppSec

ThreatAftAI Agent RCE Cluster: 17 CVEs, Auth Defaults Off | ThreatAft17 AI agent framework CVEs in one disclosure wave: auth defaults off, sandboxing absent, approval gates bypassable. Full CVE list and fixes.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

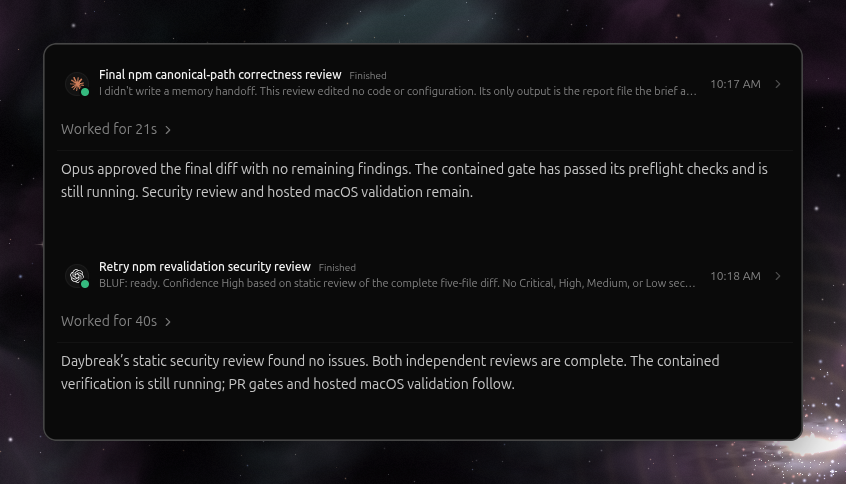
If you're not running routine security reviews of your PRs, you need to rethink your workflow. Use more than one model to review work and propose fixes.

Opus 5.5, Daybreak Blue, and GLM 5.3 are all excellent to use in tandem. Time to update your AGENTS.md.

Give each model a clear scope, ask for concrete failure cases and fixes, then verify the fixes before merging. Opus 5.5 is great for correctness and if you don't have access to Daybreak Blue, request it, and use GLM 5.3 in the meantime.

#InfoSec #AppSec #AISecurity

Two finished agent review tasks. 10:17 AM, correctness review: Opus approved the final diff with no remaining findings, while a contained gate is still running. 10:18 AM, security review: Daybreak's static review of the five-file diff found no Critical, High, Medium, or Low issues. Both independent reviews complete, with PR gates and macOS validation to follow.
↩ Reply ♡ 0 · ↻ 0 ↗ Original