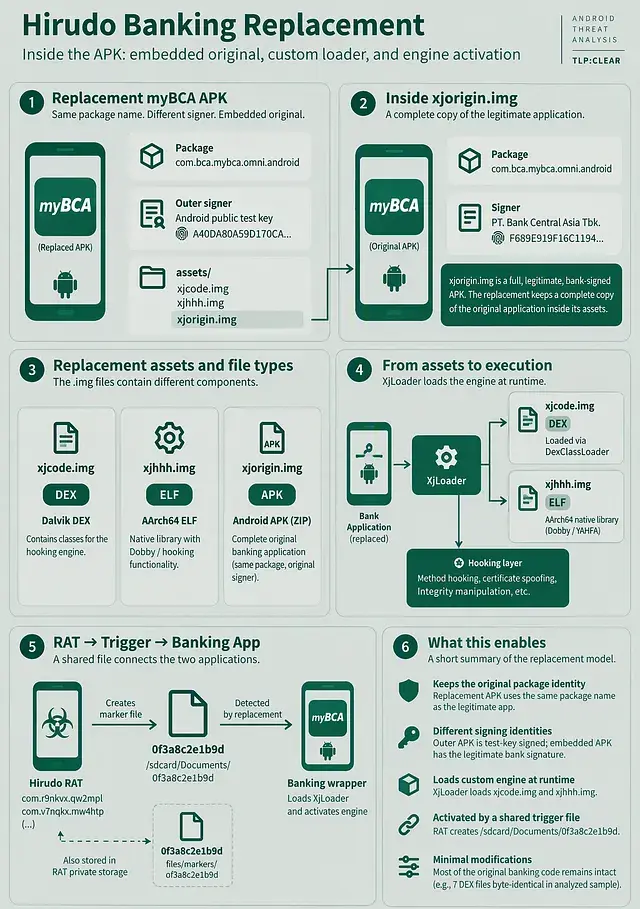
I’ve published an independent technical investigation into Hirudo, an Android banking RAT, focusing on its Indonesian banking-app replacement workflow, recovered APK artifacts, and associated infrastructure. This independent investigation was inspired by the research published by ThreatFabric. Motivated by their findings, I conducted a separate static reverse-engineering investigation focusing on Indonesian banking-app replacement artifacts, MQTT-based RAT communications, and additional infrastructure indicators. Sharing these findings with the cybersecurity community Cyber Defense Indonesia & Surabaya Hacker Link, to contribute to technical knowledge-sharing and further research into Android banking malware.
Findings include: Banking app replacement (Recovered samples) associated with m-BCA, myBCA, BNI, BRI, BTN, Livin, JakOne, and BSI.
RAT infrastructure: Hardcoded C2 references and MQTT broker configurations recovered from DEX code, including 134[.]122.153[.]8:18085 and 134[.]122.153[.]8:1884.
APK internals: Hooking-engine artifacts, shared trigger-file mechanisms, certificate-substitution evidence, and embedded development paths.
Infrastructure pivots: Additional API endpoints, APK-processing panels, and certificate/DNS correlations for further investigation. The analysis is based primarily on static reverse engineering and supporting OSINT evidence. Live infrastructure behavior, several suspected relationships, and threat-actor attribution remain unverified. The objective is to document reproducible technical evidence and provide additional pivots for malware researchers, threat hunters, and incident responders.
#CyberSecurity #ThreatIntelligence #MalwareAnalysis #ReverseEngineering #DFIR #ThreatHunting #AndroidSecurity #DigitalForensics #InfoSec #InformationSecurity #CyberDefense #FinancialSecurity
 MediumReverse-Engineering Hirudo: Indonesian Banking Targets, APK Replacement, and RAT InfrastructureAn independent technical investigation into Hirudo, focusing on Indonesian banking-app replacement workflows, artifacts recovered from…