X XFediYour place in the Fediverse
XFEDI

#CyberSecurity

ActivityPub

Public posts with this hashtag.

KrebsOnSecurity, citing two unnamed sources, reports FBI investigators suspect an executive at a U.S. consulting firm helped run ShinyHunters' Shinywire extortion site (nearly 100 victims listed). No charges so far; the firm is unnamed. Negotiator Edward Dubrovsky is charged with extortion conspiracy (complaint sealed). CyberAcuView's Mark Camillo calls percentage fees for negotiators an inherent conflict of interest.

https://krebsonsecurity.com/2026/10/feds-suspect-ransom-negotiator-ran-shinyhunters-extortion-site/

#ShinyHunters #Ransomware #InfoSec #Cybersecurity

krebsonsecurity.comFeds Suspect Ransom Negotiator Ran ShinyHunters Extortion Site – Krebs on Security
↩ Reply ♡ 0 · ↻ 0 ↗ Original

GitHub says its new package firewall, in public preview for Enterprise Cloud only, screens npm packages for malware at install time. GitHub's docs show limits: npm only, each endpoint must be configured to use it, and direct registry remotes can bypass it. Default minimum package age is 1 day, while GitHub's Dependabot default cooldown is 3 days. Free in preview; metered billing at GA, no rates given.

https://github.blog/changelog/2026-10-20-github-package-firewall-in-public-preview/

#SupplyChain #npm #GitHub #Cybersecurity

The GitHub BlogGitHub package firewall in public preview - GitHub ChangelogAn increasing number of malware attacks exploit systems at package installation time, harvesting credentials on CI/CD hosts or developer workstations without even running the package’s code. To stem this tide…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PHP's notice names no bug type, CVE IDs or affected versions for two critical flaws (CVSS v4.0 9.2 each) due to be fixed Oct 21 at 14:00 UTC, sooner if details go public. A leak says RCE, CVE-2026-109618 and CVE-2026-109619, PHP 5 onward. watchTowr, a security testing vendor, says it confirmed the leak, but its FAQ calls the scope unverified. PHP supports only 8.2 to 8.5.

https://news-web.php.net/php.announce/509

#PHP #InfoSec #Cybersecurity

news-web.php.netphp.announce: [ANNOUNCE] Upcoming Critical PHP Security Release
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Tor's advisory on hijacked relays gives no count or cause. Researcher Kaba counted 333 of about 3,000 exits redirecting SSH to interception servers from Oct 2 and says attackers tried to install Ebury. An AI-assisted public-data analysis counted 377 relays with changed exit policies, 71 of 101 other-operator FranTech relays vs 13 of 9,054 elsewhere. Operator Quetzalcoatl blames its own reused plaintext password for two rooted servers.

https://kaba.cx/posts/20261020_Tor/

#Tor #Ebury #InfoSec #Cybersecurity

kaba.cxHow I got over 300 Tor exit nodes removed
↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

watchTowr confirmed no exploitation in the wild yet and no workaround exists — patching is your only option. Apply the PHP security release immediately; Thursday's timeline is no longer the plan.

Reward: You've received a Rushed Release Medal — it pairs beautifully with your Unplanned Overtime Trophy.

https://www.bleepingcomputer.com/news/security/php-warns-admins-of-two-critical-flaws-emergency-patches-coming-tomorrow/

#PHP #ZeroDay #RCE #CVE #CyberSecurity #EmbargoBreach (2/2)

BleepingComputerPHP warns admins of two critical flaws, emergency patches coming tomorrowThe PHP security team is warning administrators to prepare for emergency security updates tomorrow to address two critical vulnerabilities, as information about the flaws has reportedly leaked ahead of their scheduled disclosure.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

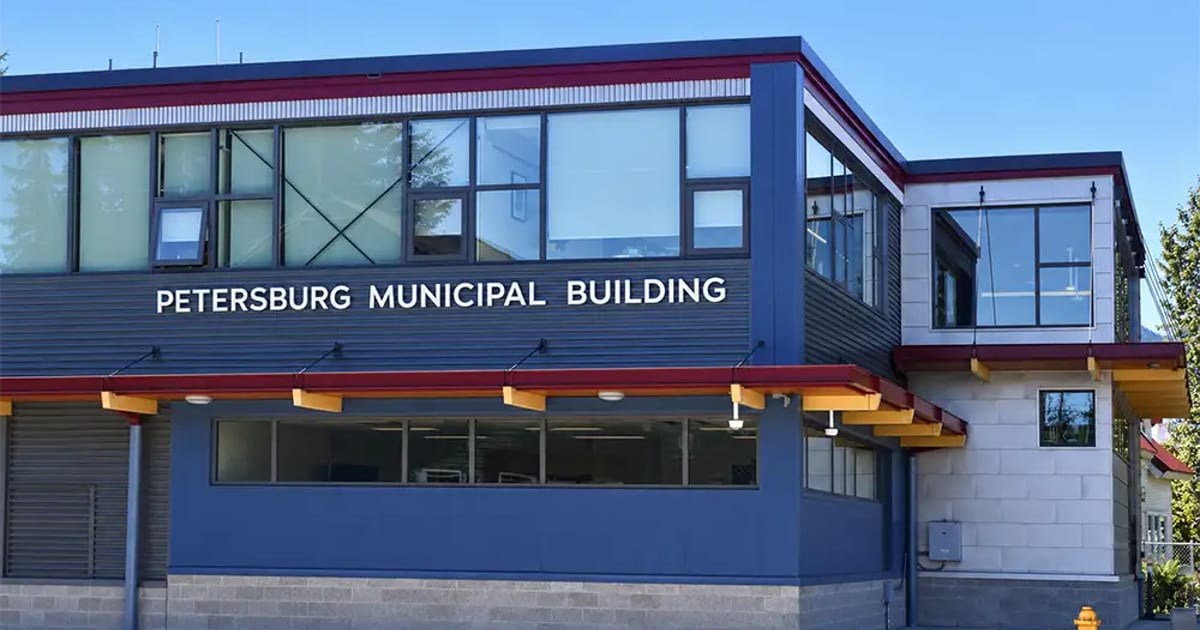
A ransomware attack affected utility billing software at Petersburg Borough in Alaska after a July 11 network intrusion. Officials disclosed the attack more than three months later.

The borough said customer names and utility account numbers were accessible through the software, but it has not confirmed whether attackers viewed or copied them. The duration of the billing disruption and the restoration date remain undisclosed.

https://dysruptionhub.com/petersburg-alaska-ransomware-utility-billing/

#PetersburgBorough #Alaska #Ransomware #UtilityBilling #Cybersecurity

DysruptionHubPetersburg Borough in Alaska discloses ransomware attack affecting utility billingPetersburg Borough disclosed a July ransomware attack affecting utility billing software. Customer names and account numbers were accessible.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

RE: https://merveilles.town/@icco/117476242258823386

Oooh, this is super important to not overlook. If you have brew installed on your computer, there's a new ca-certificates package that you'll want to install ASAP. Run this:

$ brew doctor && brew cleanup -s && brew update && brew upgrade

#brew #certificates #eMudhra #0x4 #infosec #cybersecurity #TLS

❞ Quoted posticco

Oh everything is fucked. https://bsky.app/profile/swtch.com/post/3mydfmedrrc2d #security #cybersecurity

Merveillesicco (@[email protected])Oh everything is fucked. https://bsky.app/profile/swtch.com/post/3mydfmedrrc2d #security #cybersecurity
↩ Reply ♡ 0 · ↻ 0 ↗ Original
J

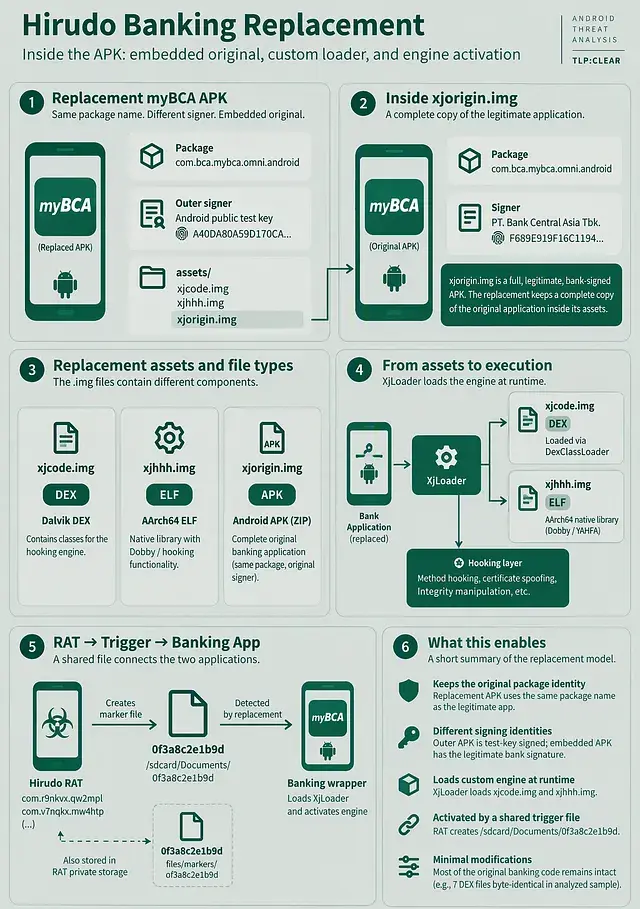
I’ve published an independent technical investigation into Hirudo, an Android banking RAT, focusing on its Indonesian banking-app replacement workflow, recovered APK artifacts, and associated infrastructure. This independent investigation was inspired by the research published by ThreatFabric. Motivated by their findings, I conducted a separate static reverse-engineering investigation focusing on Indonesian banking-app replacement artifacts, MQTT-based RAT communications, and additional infrastructure indicators. Sharing these findings with the cybersecurity community Cyber Defense Indonesia & Surabaya Hacker Link, to contribute to technical knowledge-sharing and further research into Android banking malware.

LINK:https://jeffanzos.medium.com/reverse-engineering-hirudo-indonesian-banking-targets-apk-replacement-and-rat-infrastructure-2b2890f0e4ca

Findings include: Banking app replacement (Recovered samples) associated with m-BCA, myBCA, BNI, BRI, BTN, Livin, JakOne, and BSI.

RAT infrastructure: Hardcoded C2 references and MQTT broker configurations recovered from DEX code, including 134[.]122.153[.]8:18085 and 134[.]122.153[.]8:1884.

APK internals: Hooking-engine artifacts, shared trigger-file mechanisms, certificate-substitution evidence, and embedded development paths.

Infrastructure pivots: Additional API endpoints, APK-processing panels, and certificate/DNS correlations for further investigation. The analysis is based primarily on static reverse engineering and supporting OSINT evidence. Live infrastructure behavior, several suspected relationships, and threat-actor attribution remain unverified. The objective is to document reproducible technical evidence and provide additional pivots for malware researchers, threat hunters, and incident responders.

#CyberSecurity #ThreatIntelligence #MalwareAnalysis #ReverseEngineering #DFIR #ThreatHunting #AndroidSecurity #DigitalForensics #InfoSec #InformationSecurity #CyberDefense #FinancialSecurity

Media attachment
MediumReverse-Engineering Hirudo: Indonesian Banking Targets, APK Replacement, and RAT InfrastructureAn independent technical investigation into Hirudo, focusing on Indonesian banking-app replacement workflows, artifacts recovered from…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Oh everything is fucked. https://bsky.app/profile/swtch.com/post/3mydfmedrrc2d

#security #cybersecurity

Bluesky SocialRuss Cox (@swtch.com)The details are now public, as of two hours ago. https://bugzilla.mozilla.org/show_bug.cgi?id=2083449 The secret P-384 keys for these intermediate CAs are all zeros except the last 8 bits. All not-updated software can be MITM'ed now. IOT boxes that can't or don't update are now trivially MITM'able forever. [contains quote post or other embedded content]
↩ Reply ♡ 0 · ↻ 0 ↗ Original

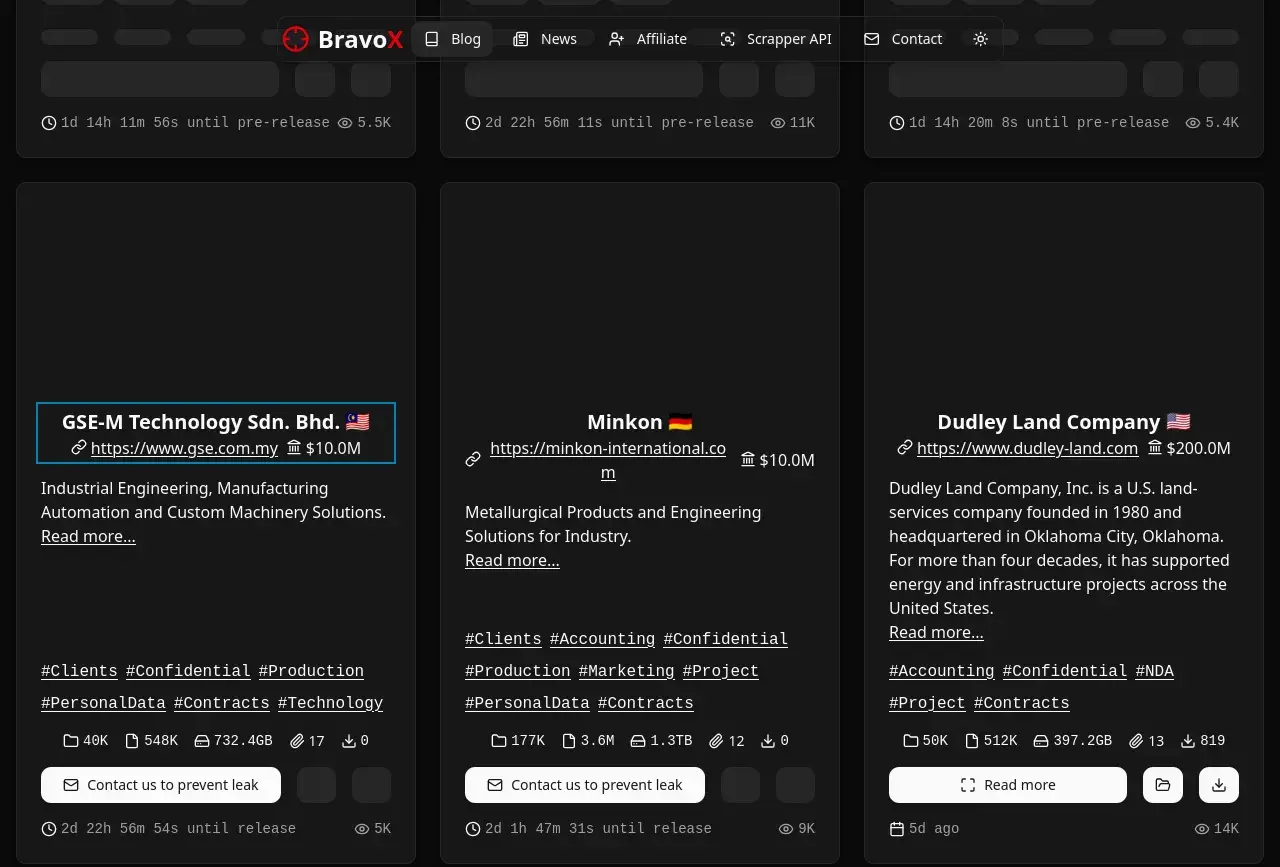
🚨New ransom group blog posts!🚨

Group name: bravox
Post title: GSE-M Technology Sdn. Bhd. 🇲🇾
Organization: GSE-M Technology Sdn. Bhd.
Location: 🇲🇾 MY
Sector: Technology
Info: https://cti.fyi/#disclosure/bravox/GSE-M%20Technology%20Sdn.%20Bhd.%20%F0%9F%87%B2%F0%9F%87%BE

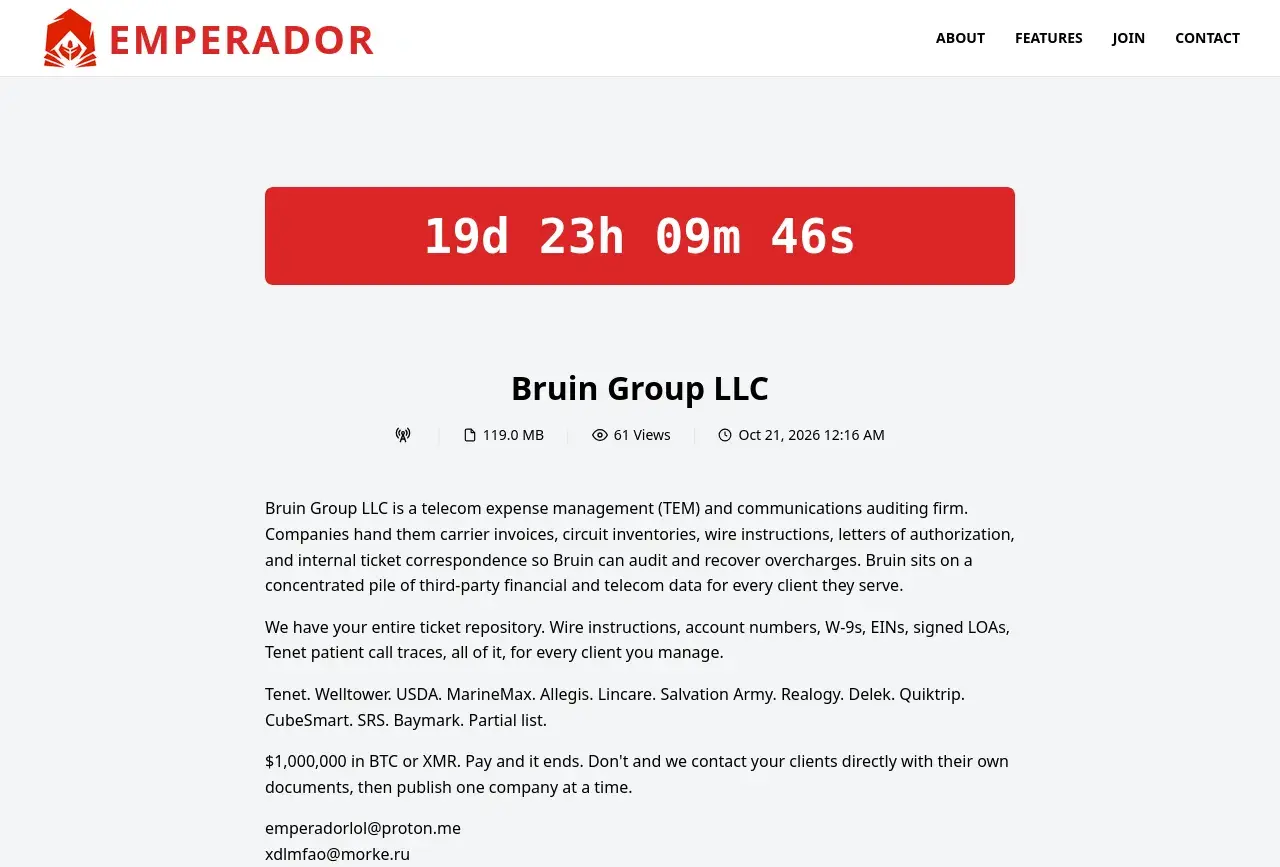
Group name: Emperador
Post title: Bruin Group LLC
Location: 🇺🇸 US
Sector: Construction
Info: https://cti.fyi/#disclosure/Emperador/Bruin%20Group%20LLC

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

⚠️ PATCH NOW

Apache Tomcat fixed two flaws (CVSS 9.1): under load, one user's request or response can land in another's session. No attacker needed.

Affects Tomcat 9.0, 10.1 and 11.0.

Fix: update to 9.0.123 / 10.1.61 / 11.0.27.

https://suriq.io/blog/apache-tomcat-cve-2026-101356-data-mix-up

#CVE #DataBreach #infosec #cybersecurity

Two light streams crossing channels inside a single glass conduit against dark space
SuriqApache Tomcat CVE-2026-101356: Data Mix-Up Flaws, PatchApache Tomcat fixed two CVSS 9.1 flaws (CVE-2026-101356, CVE-2026-103119) that can send one user's request or response to another. Affected versions and what to do.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : TELUS

Our 18th edition, Hackfest Level Up, would not be possible without our sponsors. And this year, we are happy to have Telus, a KIOSK sponsor!

If you want to learn more about this company’s mission, visit their website https://www.telus.com/

PS: YOU CAN STILL BUY YOUR TICKET for October 29–31, 2026 at the Convention Center of Québec ;) More info: https://hackfest.ca/en/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
Hackfest 2026Home — Hackfest 2026Hackfest 2026 - The cybersecurity event of the year
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Between certificates that expire (and thus have caused many an #outage), and now this, that's one #cybersecurity technique that sure has had its share of problems
https://arstechnica.com/security/2026/10/the-internet-goes-on-high-alert-after-discovery-of-8-compromised-tls-certs/

Ars TechnicaThe Internet goes on high alert after discovery of 8 compromised TLS certsIntermediate certs allow anyone to mint web credentials for any Internet server.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

https://www.csoonline.com/article/4237420/f5-rushes-out-emergency-nginx-patches-for-three-critical-flaws.html

#NGINX #CyberSecurity #CriticalVulnerability #F5 #CodeExecution #PatchedOrPerish (4/4)

CSO OnlineF5 rushes out emergency NGINX patches for three critical flawsThe three new NGINX flaws are not yet known to be exploited, but could expose systems to crashes, denial of service and potential code execution.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Henry Stimson, who died OTD in 1950, shut down U.S. cryptanalysis after World War I, saying "Gentlemen do not read each others' mail"; see where cryptanalysis had been done in #NewYorkCity https://cromwell-intl.com/travel/usa/new-york-black-chamber/?s=mb #travel #cybersecurity

Bob's Pages of Travel, Linux, Cybersecurity, and MoreFinding the American Black Chamber in New YorkThe American Black Chamber, America's first peacetime cryptographic bureau and a forerunner of the NSA, and current photographs of its sites in New York
↩ Reply ♡ 0 · ↻ 0 ↗ Original