X XFediYour place in the Fediverse
XFEDI

#Cybersecurity

ActivityPub

Public posts with this hashtag.

CISA review makes the case for eliminating vulnerability classes

CISA urges software makers to eliminate entire vulnerability classes, not just patch individual flaws. The agency highlights that recurring coding errors (like injection attacks) cause most breaches. Solution: adopt Secure by Design principles, automate security processes, and take ownership. Consumers must also demand better security from vendors to drive industry-wide change.

https://www.helpnetsecurity.com/2026/09/01/cisa-on-eliminating-recurring-security-weaknesses/

#InfoSec #CyberSecurity

Help Net SecurityCISA review makes the case for eliminating vulnerability classes - Help Net SecurityCISA makes the case for eliminating recurring security weaknesses at the source, shifting the burden from defenders to software makers.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🚨New ransom group blog posts!🚨

Group name: Deadlock
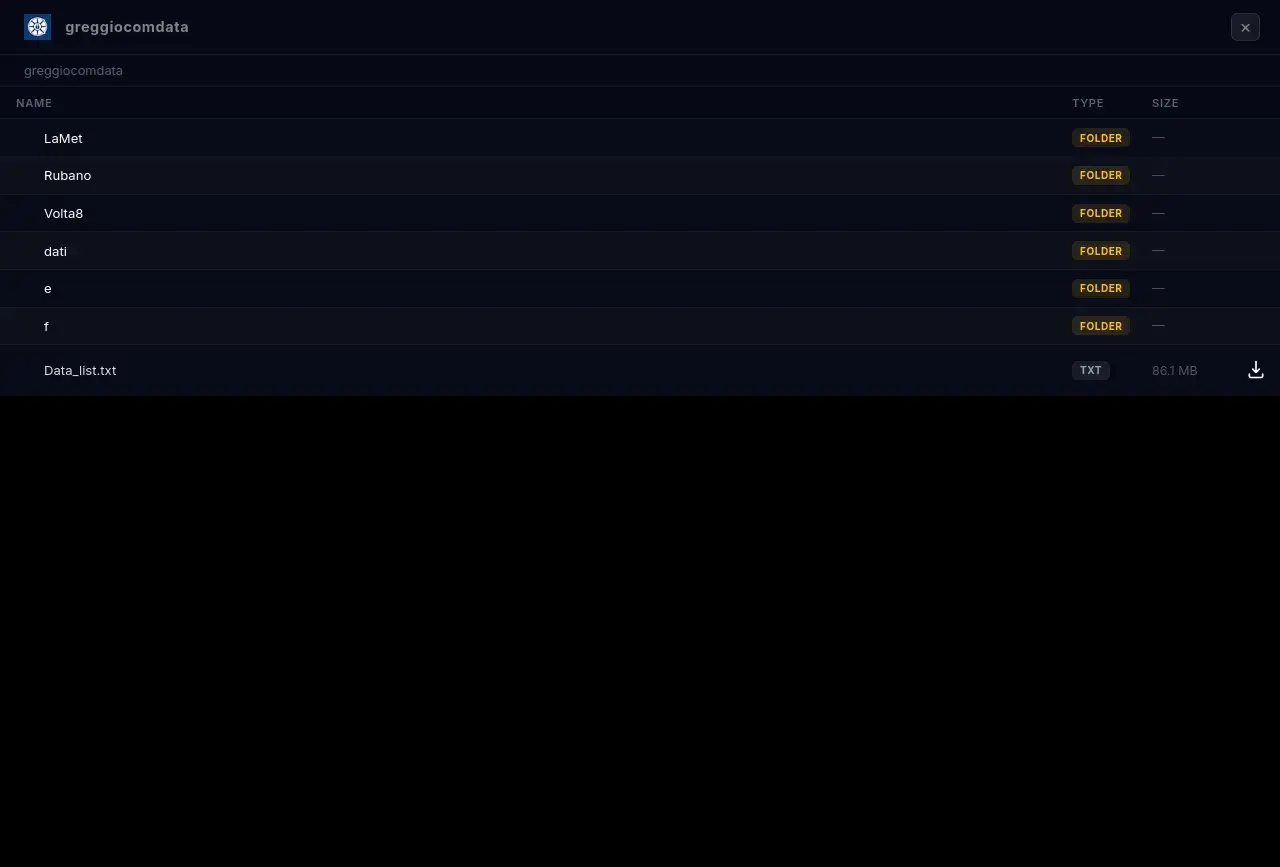
Post title: Greggio Argento
Location: 🇮🇹 IT
Sector: Technology
Info: https://cti.fyi/#disclosure/Deadlock/Greggio%20Argento

Group name: Deadlock
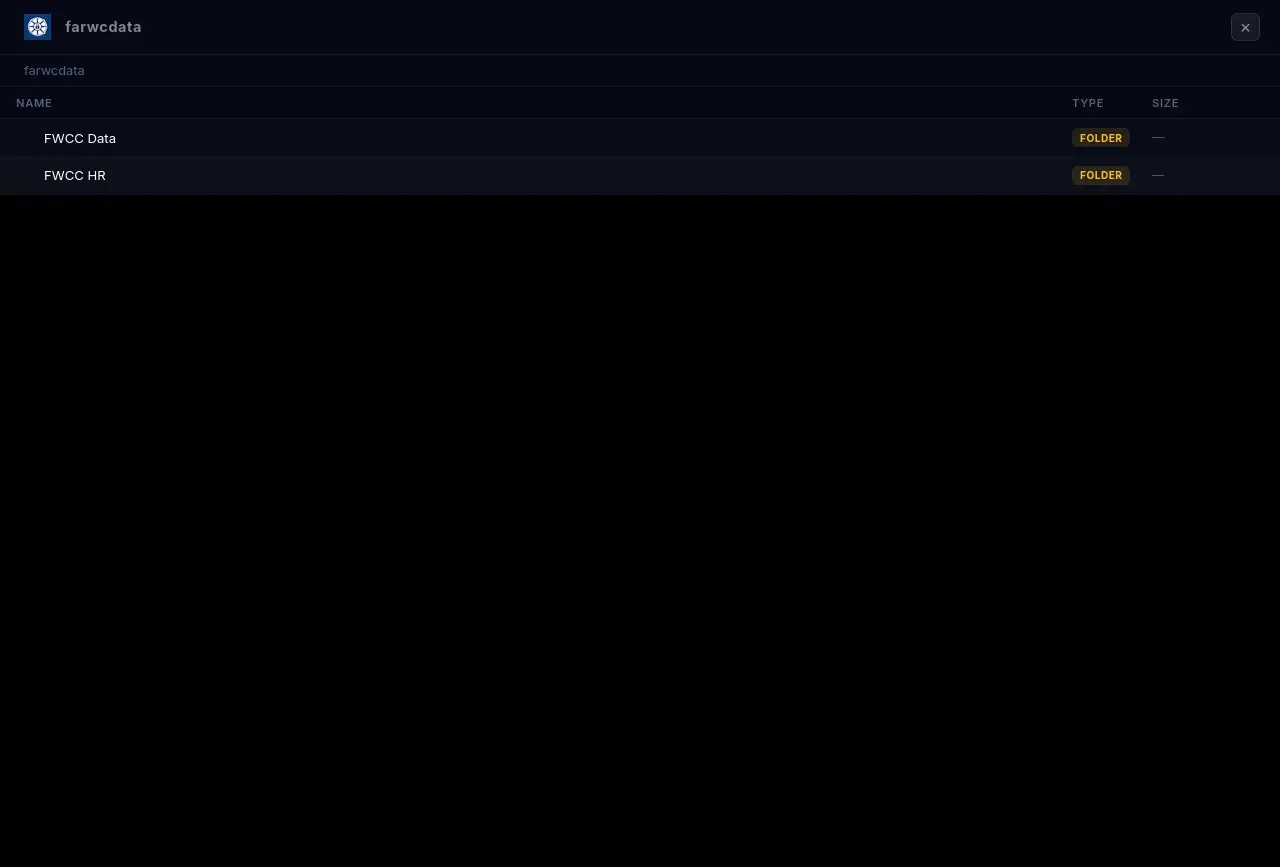
Post title: Far West Contractors
Sector: Construction
Info: https://cti.fyi/#disclosure/Deadlock/Far%20West%20Contractors

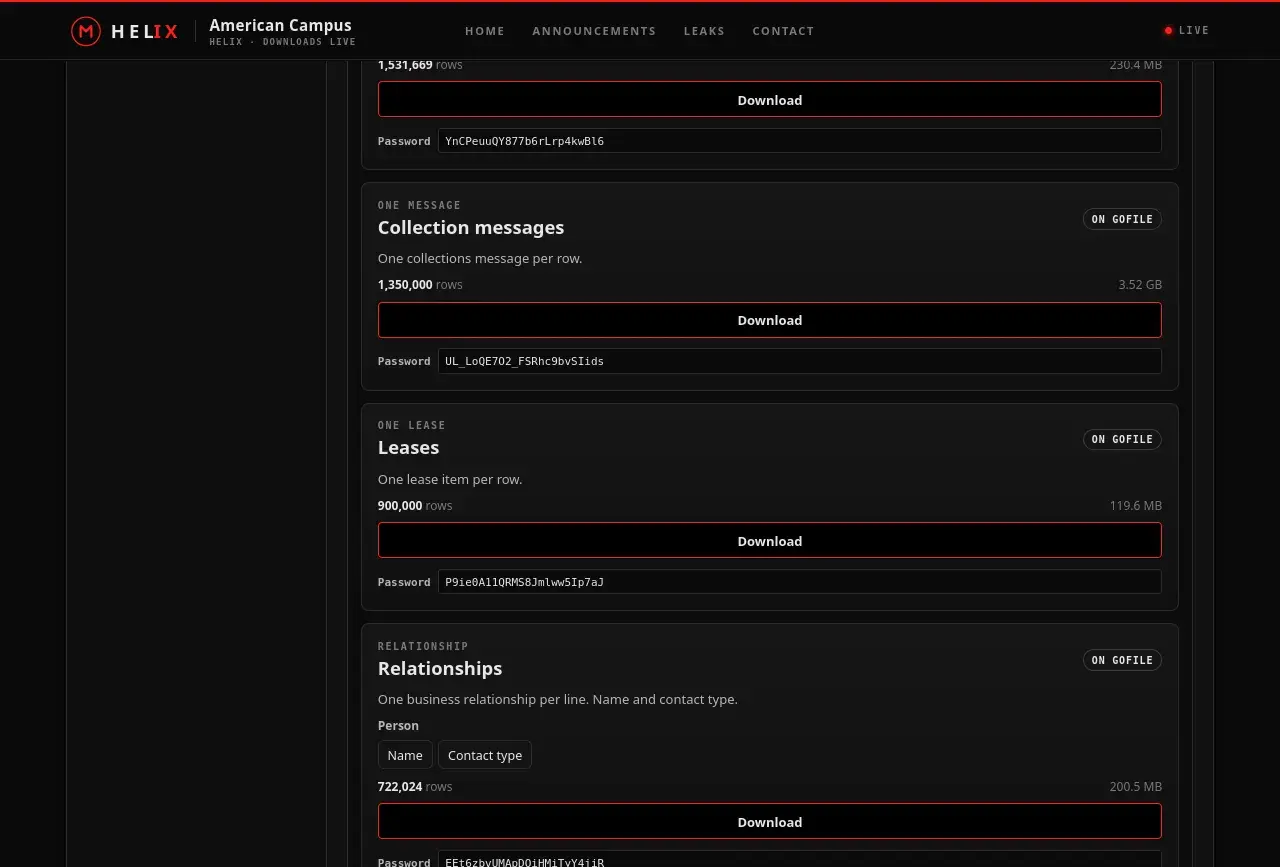
Group name: Helix
Post title: American Campus
Location: 🇺🇸 US
Sector: Education
Info: https://cti.fyi/#disclosure/Helix/American%20Campus

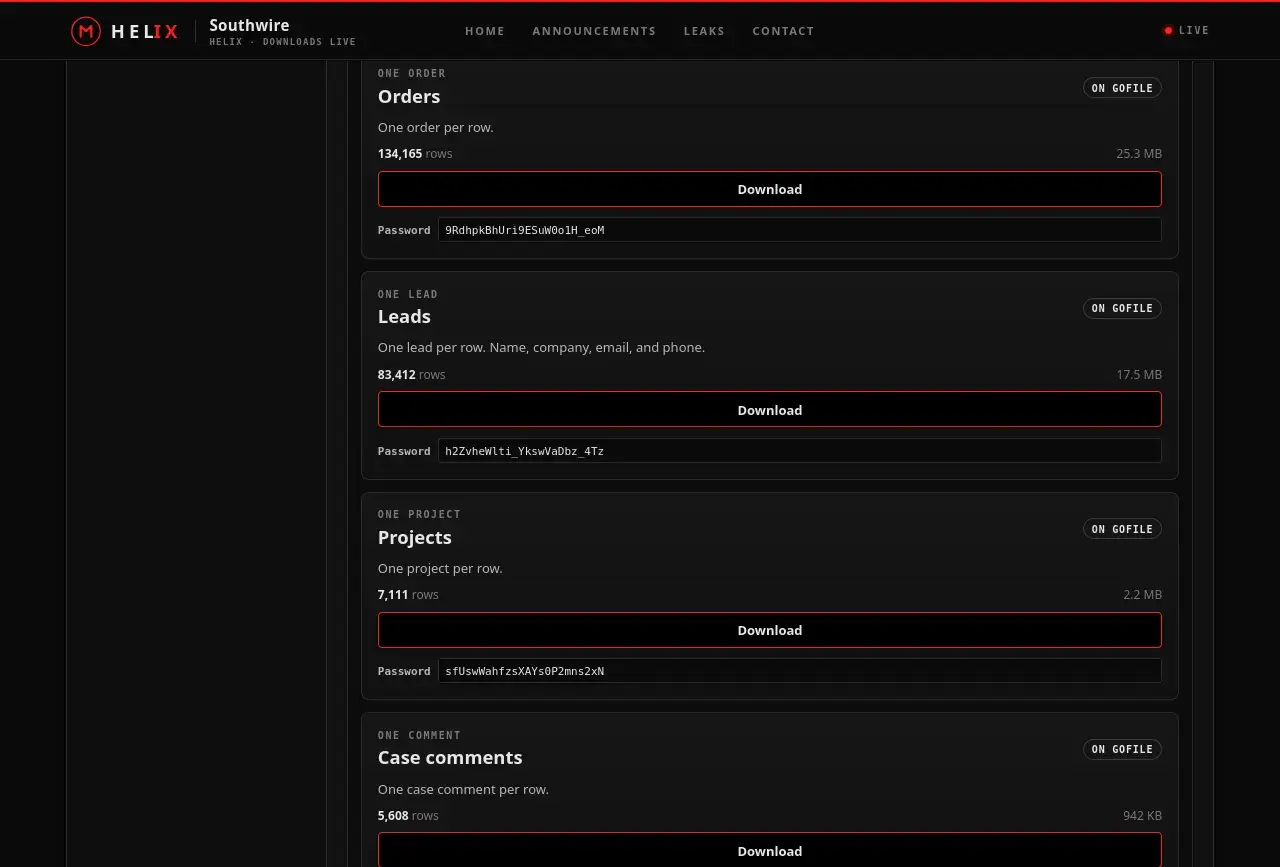
Group name: Helix
Post title: Southwire
Location: 🇺🇸 US
Sector: Manufacturing
Info: https://cti.fyi/#disclosure/Helix/Southwire

Group name: Helix
Post title: Quikrete
Location: 🇺🇸 US
Sector: Construction
Info: https://cti.fyi/#disclosure/Helix/Quikrete

Group name: Helix
Post title: Smith Douglas Homes
Location: 🇺🇸 US
Sector: Construction
Info: https://cti.fyi/#disclosure/Helix/Smith%20Douglas%20Homes

Group name: Helix
Post title: Bay Alarm
Location: 🇺🇸 US
Sector: Technology
Info: https://cti.fyi/#disclosure/Helix/Bay%20Alarm

Group name: Helix
Post title: Personify Health
Location: 🇺🇸 US
Sector: Healthcare
Info: https://cti.fyi/#disclosure/Helix/Personify%20Health

Group name: Helix
Post title: Rheem Global
Location: 🇺🇸 US
Sector: Manufacturing
Info: https://cti.fyi/#disclosure/Helix/Rheem%20Global

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachmentMedia attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

If you received a notification from Burger King Japan, review what data was exposed, monitor linked accounts for suspicious activity, and change passwords on any services sharing those credentials.

Reward: You've unlocked the Compliance Certificate of Insufficient Access Controls. It is laminated. It does not help.

https://www.rescana.com/post/burger-king-japan-smartphone-app-data-breach-exposes-11-million-customer-records-in-2026

#DataBreach #CyberSecurity #BurgerKing #MobileApp (3/3)

RescanaBurger King Japan Smartphone App Data Breach Exposes 11 Million Customer Records in 2026Executive SummaryBurger King Japan, the Japanese subsidiary of the global fast-food chain Burger King, experienced a significant data breach in early October 2026, resulting in the exposure of approxi
↩ Reply ♡ 0 · ↻ 0 ↗ Original
T

🚨 WPSplinter: 16-Year-Old Broadcom Wi-Fi Vulnerability Enables Router RCE

Security researcher Quentin Kaiser has exposed a flaw in Broadcom’s legacy Wi-Fi SDK that could allow attackers within wireless range to execute arbitrary code on vulnerable routers without knowing the Wi-Fi password or completing WPS enrollment.

The exploit chain involves a buffer overflow in EAP-WPS fragment reassembly, memory disclosure, and potential code execution. Demonstrations on ISP gateways reportedly exposed Wi-Fi credentials and achieved interactive reverse-shell access.

⚠️ Disabling WPS may not mitigate the flaw. Legacy firmware and unsupported eCos-based gateways pose particularly difficult remediation challenges.

Technical breakdown, affected platforms, detection toolkit, and mitigation 👇

🔗 https://thecybersecguru.com/exploits/wpsplinter-broadcom-wifi-vulnerability/

#InfoSec #CyberSecurity #WiFiSecurity

❞ Quoted post

The original is being retrieved. Open its source ↗

↩ Reply ♡ 0 · ↻ 0 ↗ Original

NEW - DHS appointees made an unusual request of CISA, its agency that protects election systems: Secretly acquire a voting machine and hack it.

Though not acted on, the request shows how the Trump administration has tried to use CISA for its own ends.
https://www.propublica.org/article/cisa-election-security-donald-trump?utm_source=mastodon&utm_medium=social&utm_campaign=mastodon-post

#News #DHS #Voting #Vote #Election #Midterms #Trump #USPolitics #Cybersecurity

ProPublicaTrump Appointees Asked a Federal Cybersecurity Agency to Secretly Acquire a Voting Machine — and Hack ItThough not acted on, the request shows how the Trump administration has tried to use the Cybersecurity and Infrastructure Security Agency for its own ends while draining it of resources to help its mission of protecting the nation’s voting systems.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

📢 DEF CON Training is now accepting course submissions for 2027!

Whether you’re an experienced instructor or bringing a new course to the community, we’re looking for high-quality, hands-on training that helps security professionals build real-world skills.

Submit your training material today for the opportunity to teach alongside the DEF CON community in locations around the world including Las Vegas, the Middle East, and Singapore!

For more details, see the application. The deadline to apply is November 13, 2026.

Apply here today 🔗: https://forms.cloud.microsoft/r/z2f4igJPuu

Already submitted your course for Singapore March 2027? As long as you selected your other sessions of interest at the end of the application form, you don’t need to reapply! We have your application on file.

Questions? Email us at [email protected]

#DEFCON #DEFCON35 #DEFCONSG #DEFCONME #DEFCONTraining #training #cybersecurity #handsonlearning #infosec #AI #incidentresponse #threathunting #cloud #IoT #hacking

Call for trainers
forms.cloud.microsoftMicrosoft Forms
↩ Reply ♡ 0 · ↻ 0 ↗ Original