I made a Jack-o‘-Lantern carving game with my son. Give it a whirl for a bit of spooky fun, and have a Happy Halloween this weekend!
Public posts with this hashtag.
I made a Jack-o‘-Lantern carving game with my son. Give it a whirl for a bit of spooky fun, and have a Happy Halloween this weekend!
I came across jsfuck. It shows you how to write any JavaScript code using only []()!+. For example alert(1) would become:
[][(![]+[])[+[]]+([![]]+[][[]])[+!+[]+[+[]]]+(![]+[])[!+[]+!+[]]+(!![]+[])[+[
]]+(!![]+[])[!+[]+!+[]+!+[]]+(!![]+[])[+!+[]]][([][(![]+[])[+[]]+([![]]+[][[]
])[+!+[]+[+[]]]+(![]+[])[!+[]+!+[]]+(!![]+[])[+[]]+(!![]+[])[!+[]+!+[]+!+[]]+
(!![]+[])[+!+[]]]+[])[!+[]+!+[]+!+[]]+(!![]+[][(![]+[])[+[]]+([![]]+[][[]])[+
!+[]+[+[]]]+(![]+[])[!+[]+!+[]]+(!![]+[])[+[]]+(!![]+[])[!+[]+!+[]+!+[]]+(!![
]+[])[+!+[]]])[+!+[]+[+[]]]+([][[]]+[])[+!+[]]+(![]+[])[!+[]+!+[]+!+[]]+(!![]
+[])[+[]]+(!![]+[])[+!+[]]+([][[]]+[])[+[]]+([][(![]+[])[+[]]+([![]]+[][[]])[
+!+[]+[+[]]]+(![]+[])[!+[]+!+[]]+(!![]+[])[+[]]+(!![]+[])[!+[]+!+[]+!+[]]+(!!
[]+[])[+!+[]]]+[])[!+[]+!+[]+!+[]]+(!![]+[])[+[]]+(!![]+[][(![]+[])[+[]]+([![
]]+[][[]])[+!+[]+[+[]]]+(![]+[])[!+[]+!+[]]+(!![]+[])[+[]]+(!![]+[])[!+[]+!+[
]+!+[]]+(!![]+[])[+!+[]]])[+!+[]+[+[]]]+(!![]+[])[+!+[]]]((![]+[])[+!+[]]+(![
]+[])[!+[]+!+[]]+(!![]+[])[!+[]+!+[]+!+[]]+(!![]+[])[+!+[]]+(!![]+[])[+[]]+(!
[]+[][(![]+[])[+[]]+([![]]+[][[]])[+!+[]+[+[]]]+(![]+[])[!+[]+!+[]]+(!![]+[])
[+[]]+(!![]+[])[!+[]+!+[]+!+[]]+(!![]+[])[+!+[]]])[!+[]+!+[]+[+[]]]+[+!+[]]+(
!![]+[][(![]+[])[+[]]+([![]]+[][[]])[+!+[]+[+[]]]+(![]+[])[!+[]+!+[]]+(!![]+[
])[+[]]+(!![]+[])[!+[]+!+[]+!+[]]+(!![]+[])[+!+[]]])[!+[]+!+[]+[+[]]])()
And it is the best summary of the Javascript brand that I've ever seen.
New.
"As of October 26, 2026, Rapid7 is not aware of exploitation in the wild, and CVE-2026-111497 is not listed in CISA's Known Exploited Vulnerabilities catalog. However, given the vulnerability's potential to disclose memory or enable remote code execution (RCE), Rapid7 recommends that organizations prioritize remediation."
Rapid7: CVE-2026-111497: Critical out-of-bounds write in the Node.js Brotli decoder https://www.rapid7.com/blog/post/etr-cve-2026-111497-critical-out-of-bounds-write-in-the-node-js-brotli-decoder/ @Rapid7Official #infosec #vulnerability #JavaScript #threatresearch
 Rapid7Rapid7On October 21, 2026, the Node.js Project published a security advisory for CVE-2026-111497, an out-of-bounds write in the Brotli decoder bundled with Node.js. The vulnerability affects the Node.js 26.x, 24.x, and 22.x release lines. Node.js rates the issue High, while Google, the CVE Numbering Authority (CNA), gives it a critical CVSSv4 score of 9.2.
RE: https://podcastindex.social/@rpodcast/117492034712905695
Many thanks to R Weekly for highlighting Samuel's wonderful blog post on building apps and packages for computational biology in #RStats, #Python, #typescript, and #javascript!
Check out the latest R Weekly: https://rweekly.org/
and Samuel's post: https://opensource.posit.co/blog/2026-10-08_genomes-prompts-and-shiny/
Episode 245 of the @rstats @rweekly Highlights Podcast is out! https://serve.podhome.fm/episodepage/r-weekly-highlights/246 🌐 Contributing to R Core @R_Foundation @RConsortium 📦 Explosion of package & environment tools @ivelasq3 🧬 Genomes, Prompts, and Shiny (Samual Bharti) @P
PodcastIndex SocialR-Podcast (Eric) :pci: (@[email protected])Episode 245 of the @[email protected] @[email protected] Highlights Podcast is out! https://serve.podhome.fm/episodepage/r-weekly-highlights/246 🌐 Contributing to R Core @[email protected] @[email protected] 📦 Explosion of package & environment tools @[email protected] 🧬 Genomes, Prompts, and Shiny (Samual Bharti) @[email protected] R Weekly is powered by the communityFrom the @DSLC :rstats:chives:
:rstats: R Packages: How do I make sure my package works? https://youtu.be/RlE8P3f10ZU #RStats
:rstats: :javascript: JS4R: Overview https://youtu.be/GFQbrzLI3BA #RStats #JavaScript
:rstats: Feature Engineering: Global Search Methods https://youtu.be/wT3KfW2gUgM #RStats
:rstats: R for Data Science: Scripts/Exploratory Data Analysis https://youtu.be/mlIgAWOLVuQ #RStats
Support the Data Science Learning Community at https://patreon.com/DSLC
Storybook dev server vulnerability CVE-2026-114125 (CVSS 9.4) enables code injection from malicious websites. Upgrade to 10.6.2, 9.1.21 or 8.6.19.
#Storybook #CVE2026114125 #CodeInjection #JavaScript #npm #DevSecOps #SupplyChain #CyberSecurity
How to Compile JavaScript Into a Single Executable, by @flaviocopes.com:
https://flaviocopes.com/javascript-single-executable/?ref=frontenddogma.com
 flaviocopes.comHow to compile JavaScript into a single executableTurn a JavaScript program into one executable file, like Go and Rust do, with deno compile, bun build --compile and Node.js single executable apps.
MongoDB is hiring Software Engineer 3
🔧 #golang #java #javascript #python #react #aws #azure #docker #gcp #kubernetes #mongodb
🌎 Gurugram, India
⏰ Full-time
🏢 MongoDB
Job details https://jobsfordevelopers.com/jobs/software-engineer-3-at-mongodb-com-sep-24-2026-df82b6?utm_source=mastodon.world&utm_medium=social&utm_campaign=posting
#jobalert #jobsearch #hiring
 jobsfordevelopers.comSoftware Engineer 3 at MongoDBMongoDB is hiring Software Engineer 3
How do you make sense of the JavaScript ecosystem?
From the archives, Andrew Pinkham compares frontend libraries and explores React, Redux, Webpack, fetch, Promises, and thunks.
Watch: https://youtu.be/g8d6UbVCuuw
Join us in 2027: https://ti.to/defna/djangocon-us-2027
#Django #JavaScript
 TitoDjangoCon US 2027DjangoCon US is a five-day international conference for the community, by the community, held each year in North America, about the Django web framework. September 13-15 Talks | September 16-17 Sprints
Recursion Is Dead and HTML Killed It, by @davatron5000:
https://daverupert.com/2026/10/html-recursion/?ref=frontenddogma.com
New.
Securonix: TRUST#GRAFT: JavaScript Attack Targets WordPress Admins with PHP Backdoor https://www.securonix.com/blog/trust-graft-wordpress-admin-php-backdoor/ #infosec #threatresearch #JavaScript #WordPress
 SecuronixTRUST#GRAFT : JavaScript-Compromised Sites Target WordPressSecuronix analyzes TRUST#GRAFT, a JavaScript attack that exploits authenticated WordPress admin sessions to install a persistent, hidden PHP backdoor.
Join me in celebrating International Static Website Week!
The latest Node.js security update addresses over ten vulnerabilities across 26.x, 24.x, and 22.x series, including four high-severity execution flaws.
 Daily Tech NowNode.js Security Update Fixes Critical FlawsThe latest Node.js security update addresses over ten vulnerabilities across 26.x, 24.x, and 22.x series, including four high-severity execution flaws.
The Node.js security release fixes 10 flaws, including a Brotli remote code execution bug, CVE-2026-111497. Update to 26.12.1, 24.22.1 or 22.23.4.
#NodeJS #CVE2026111497 #CVE2026105483 #CVE2026106069 #RemoteCodeExecution #TLS #JavaScript #CyberSecurity
#w3cTPAC breakout
"Thinking outside the browser - More coordination for better web standards for embedding"
🗓️ 28 October 2026, 16:30–17:30 GMT
▶️ https://www.w3.org/events/meetings/3e7f2228-a79c-4477-a163-ae2818dba074/
The web is much more than #browsers. From WebViews and MiniApps to embedded Web engines and #JavaScript runtimes, many communities face similar challenges but rarely get to coordinate.
Join @espinr, @niklasmerz and @bkardell session to share experiences, explore common interests, and plan how to work together more regularly.
 W3C28 October 2026 | Thinking outside the browser - More coordination for better web standards for embedding | CalendarThe World Wide Web Consortium (W3C) is an international community where Member organizations, a full-time staff, and the public work together to develop Web standards.
C3 AI is hiring Senior Software Engineer - Generative AI
🔧 #java #javascript #seniorengineer
🌎 Redwood City, California
⏰ Full-time
🏢 C3 AI
Job details https://jobsfordevelopers.com/jobs/senior-software-engineer-generative-ai-at-c-3-ai-jul-31-2026-487525?utm_source=mastodon.world&utm_medium=social&utm_campaign=posting
#jobalert #jobsearch #hiring
 jobsfordevelopers.comSenior Software Engineer - Generative AI at C3 AIC3 AI is hiring Senior Software Engineer - Generative AI
Do you run #behavioural #psychology #experiments?
Have you tried creating #JavaScript experiments with jsPsych but for stumped by all the coding needed?
I've been working on Tachisto, a #jsPsych builder that should require little or no code.
Give it a go and let me know!
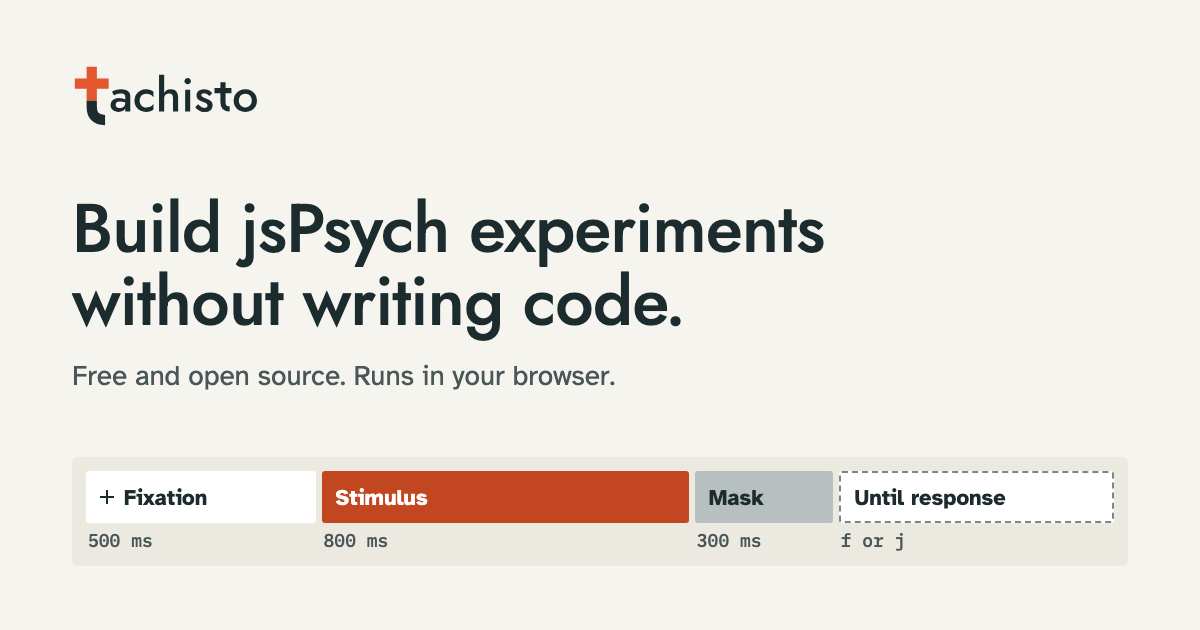 TachistoTachisto: build jsPsych experiments without codeBuild jsPsych experiments without writing code. Free, open source, runs in your browser.
Cloudflare has a new announcement. And judging by the first quote, the bots will be doing the checking?
"Our goal is to help developers spend less time waiting for their code to be checked and more time building. Making TypeScript faster and more memory-efficient also helps bring complete development environments to more places, including right in your browser."
"To be clear, we are not forking TypeScript. We believe the TypeScript team should remain in full control of the language’s design and direction. They have maintained a long-term vision while guiding TypeScript’s adoption across the JavaScript community. We do not want to change that."
Cloudflare: Introducing tsrs: a Port of TypeScript to Rust https://blog.cloudflare.com/typescript-rust-port/ #Cloudflare #Rust #infosec #JavaScript
 Cloudflare BlogIntroducing tsrs: a Port of TypeScript to RustCloudflare is collaborating on tsrs, a Rust port of TypeScript that is up to 8x faster and uses 70% less memory.
Hey, #FediHelp #FediAdvice
TL;DR looking for websites for freelancing for Front End Development.
Any Front End JavaScript Developers using sites where you can pitch for freelance work?
I seemed to have signed up to a couple recently that I am not super impressed with.
I used to use peopleperhour.com although it was quite varied in terms of quality and $ some clients were willing to offer. PPH tried to bring people in line.
Anyway here are some with some descriptors.
Twine
xing.com
People per hour
Any others? I was happy to look to go back to PPH, but not anymore.
Would ideally like something UK centric, or with a heavy UK basis, no AI and ideally not a paid tier model.
(Feel free to retoot for more reach)
#FrontEnd #FrontEndDeveloper #FrontEndDevelopment #Contracting #Contract #Freelance #Freelancing #JavaScript #JavaScriptDeveloper #JavaScriptDevelopment #WebDeveloper #WebDevelopment
Any FOSS or other non-profit project or community that sends email?
I am happy to help :)
 relayRelay: The Open-Source Pledgerelay's open-source pledge, signed by founder Johannes Maron: free services for open-source communities, donations
back, and contributions upstream.
Oh wow, #javascript's Array type has nice stuff like flatMap, reduce etc., but no method to pre/append an element and return a new array (or even the same one)?
Want to trigger CSS animations based on user interactions or scroll position?
The @w3c Animation Triggers specification explores declarative #CSS and #JavaScript #APIs to trigger animations based on DOM events or timelines, including view progress timelines. #timetogiveinput #FPWD
▶️ https://www.w3.org/TR/animation-triggers-1/
Feeback wlc: https://github.com/w3c/csswg-drafts/labels/animation-triggers-1