X XFediYour place in the Fediverse
XFEDI

#ThreatIntelligence

ActivityPub

Public posts with this hashtag.

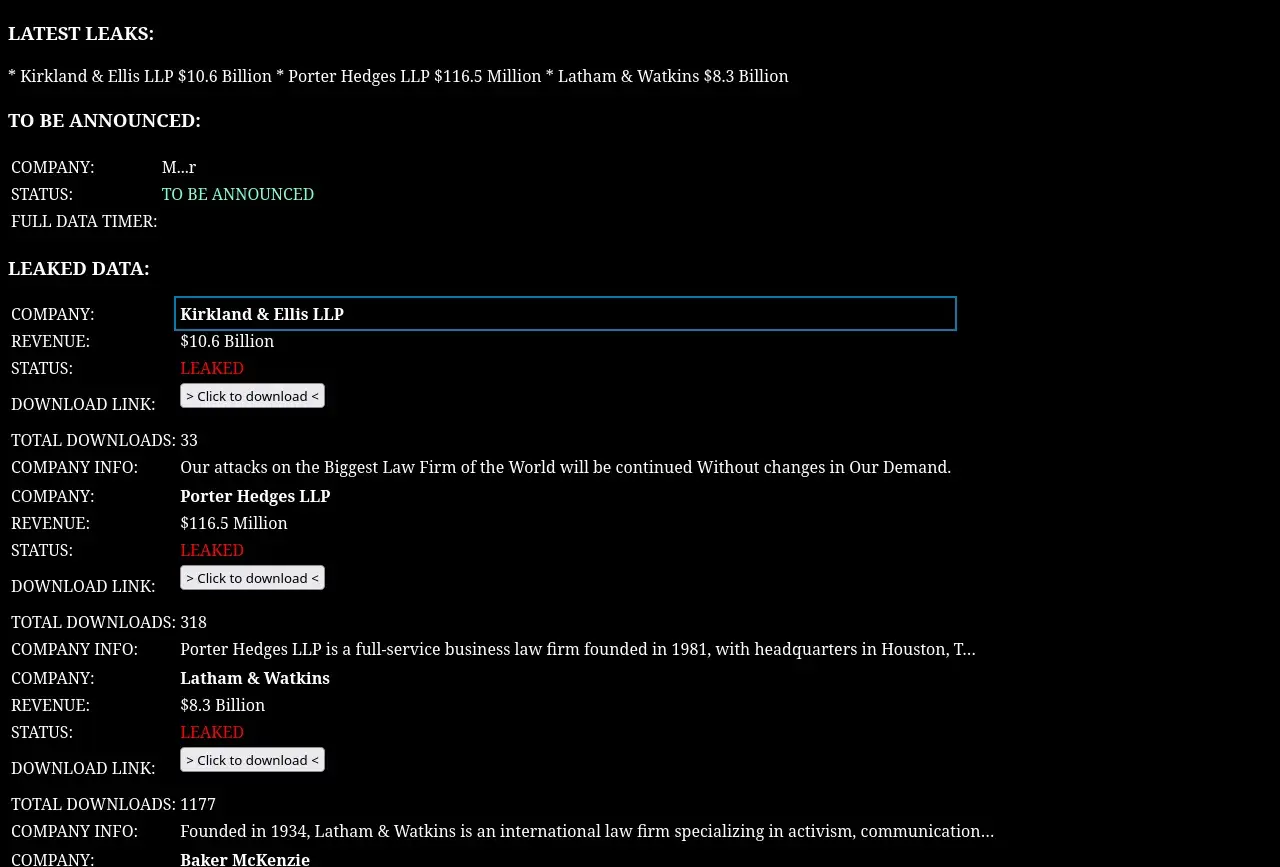
🚨New ransom group blog post!🚨

Group name: SilentRansomGroup
Post title: Kirkland & Ellis LLP
Location: 🇺🇸 US
Sector: Legal
Info: https://cti.fyi/#disclosure/SilentRansomGroup/Kirkland%20%26%20Ellis%20LLP

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

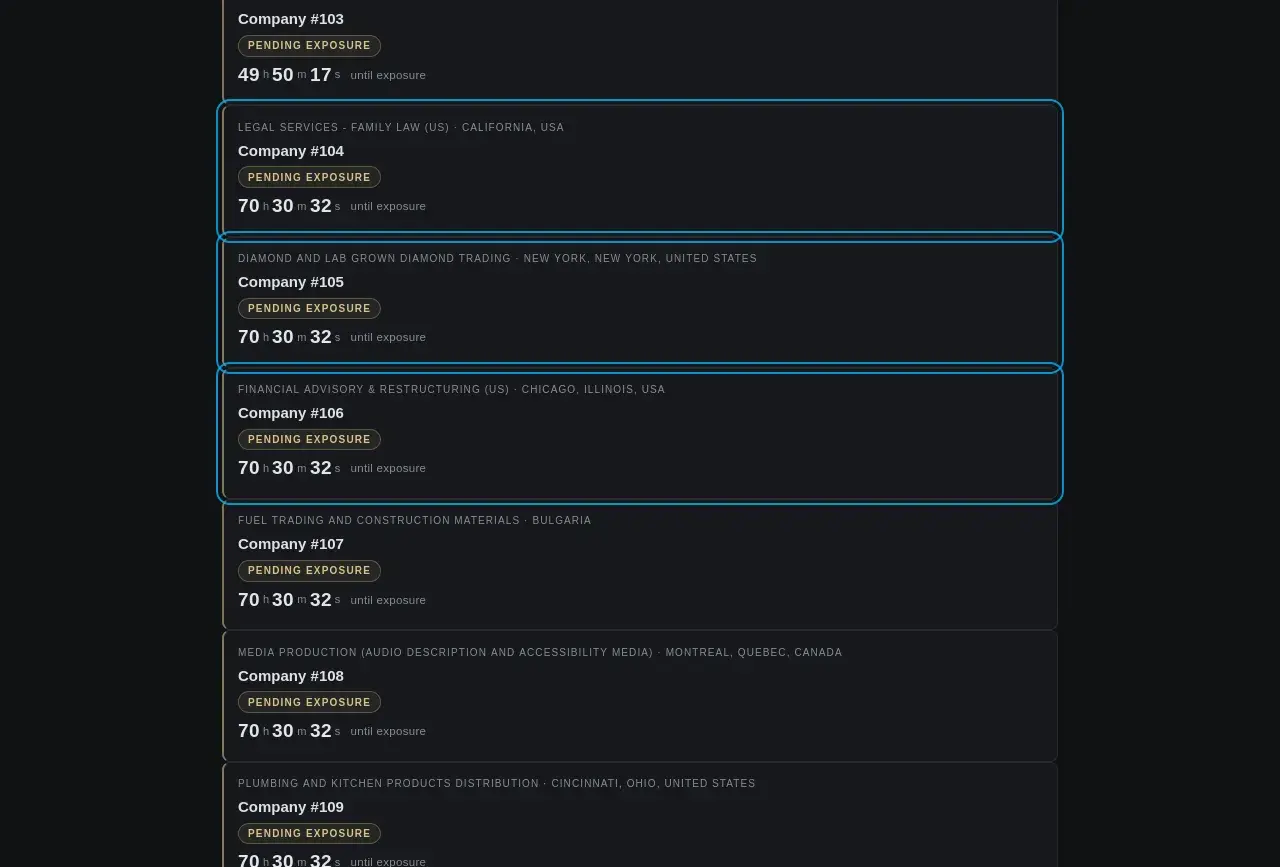
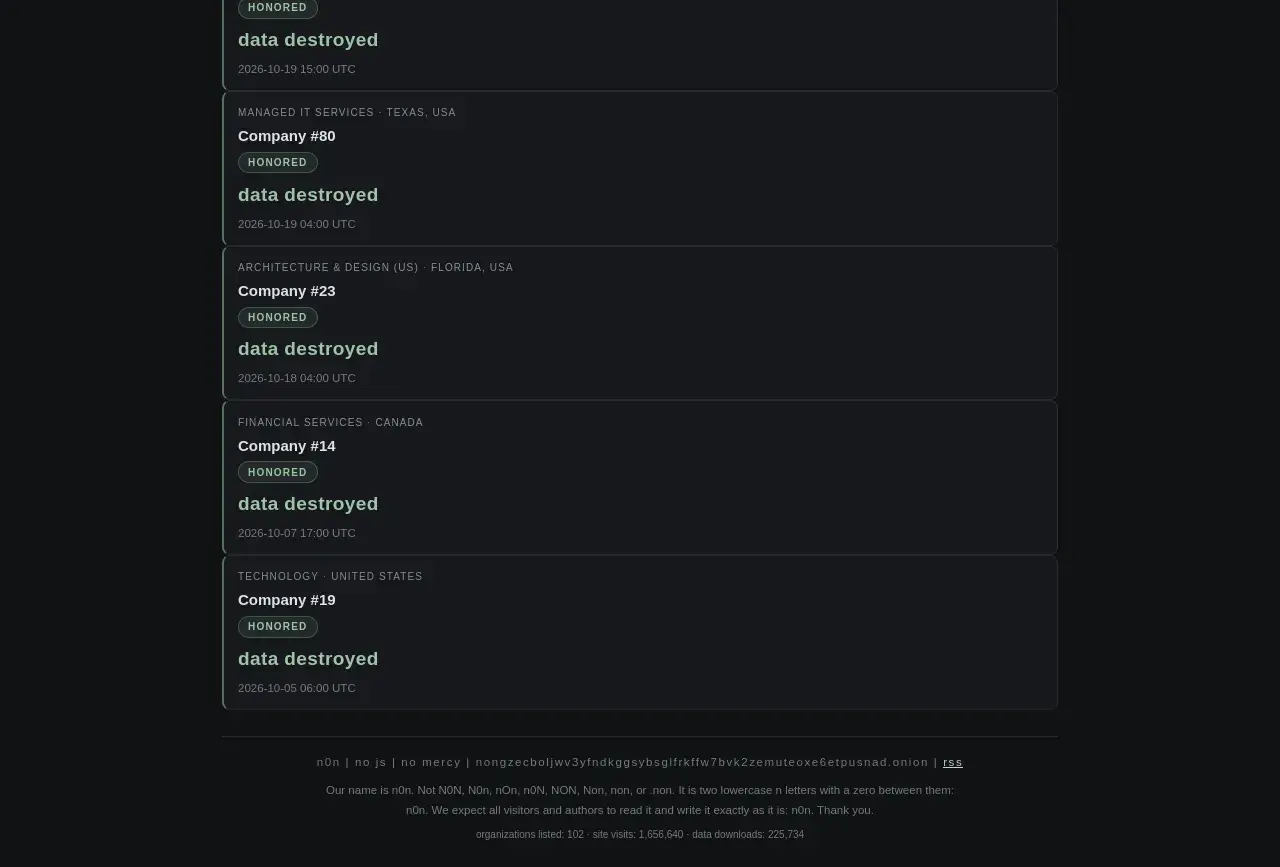
🚨New ransom group blog posts!🚨

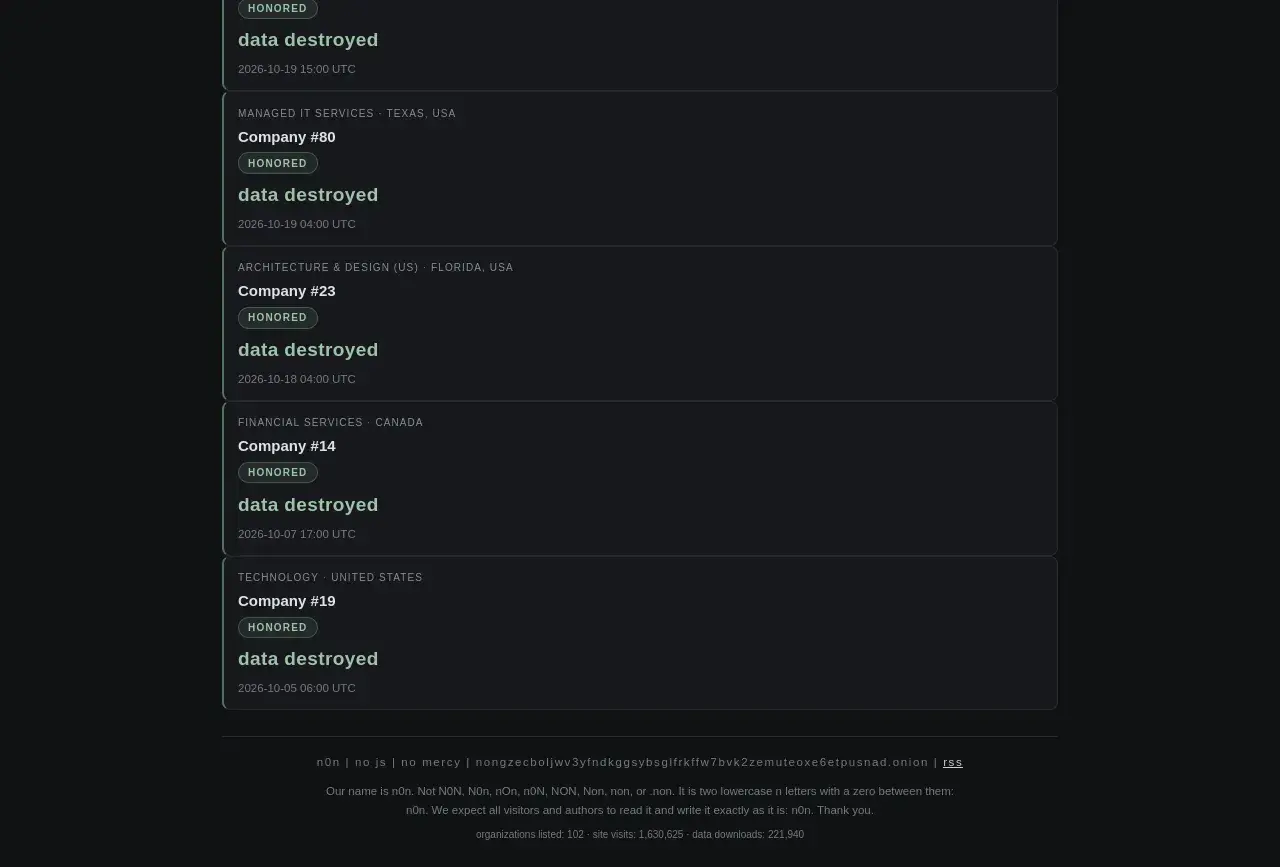
Group name: N0n
Post title: Performance Ford Inc
Location: 🇺🇸 US
Sector: Automotive
Info: https://cti.fyi/#disclosure/N0n/Performance%20Ford%20Inc

Group name: N0n
Post title: Company #104
Info: https://cti.fyi/#disclosure/N0n/Company%20%23104

Group name: N0n
Post title: Company #105
Info: https://cti.fyi/#disclosure/N0n/Company%20%23105

Group name: N0n
Post title: Company #106
Info: https://cti.fyi/#disclosure/N0n/Company%20%23106

Group name: N0n
Post title: Company #107
Info: https://cti.fyi/#disclosure/N0n/Company%20%23107

Group name: N0n
Post title: Company #108
Info: https://cti.fyi/#disclosure/N0n/Company%20%23108

Group name: N0n
Post title: Company #109
Info: https://cti.fyi/#disclosure/N0n/Company%20%23109

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachmentMedia attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

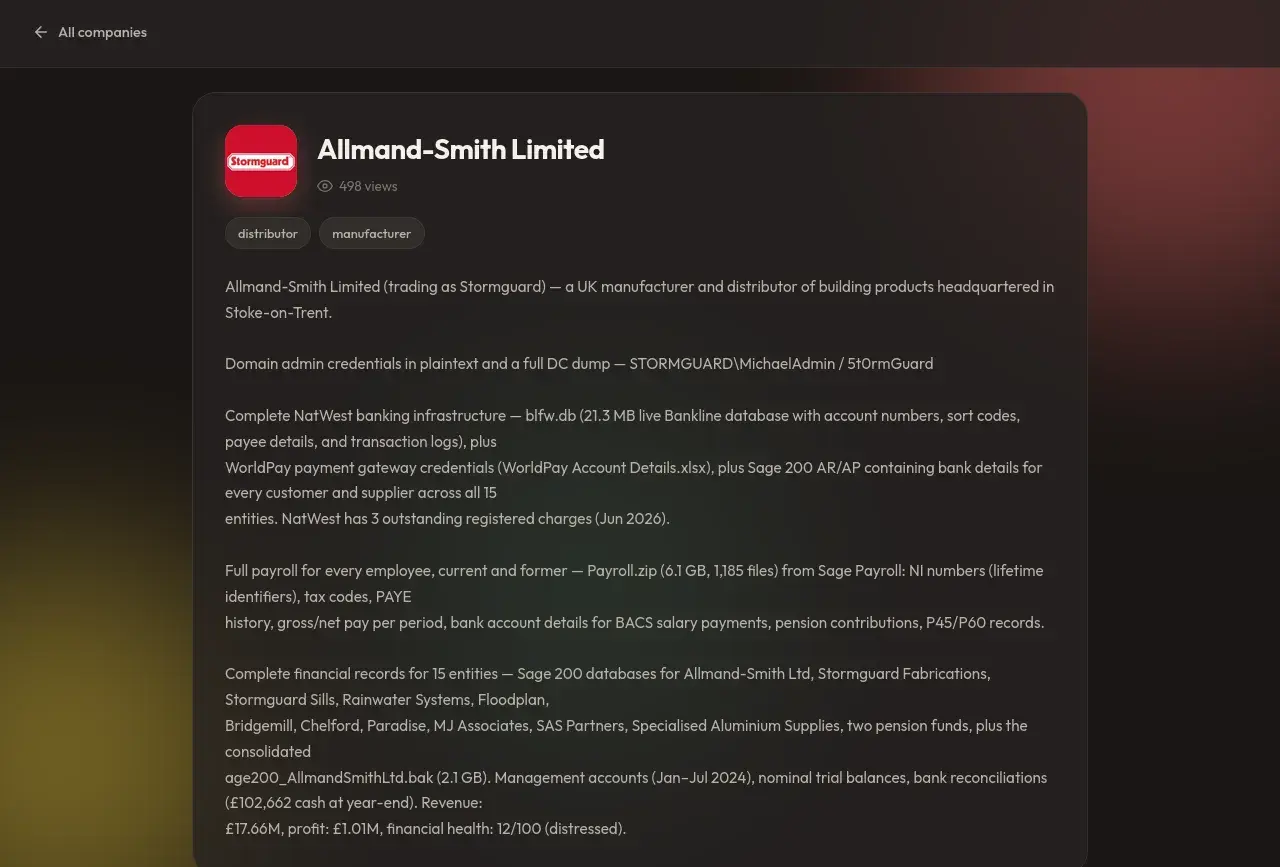
🚨New ransom group blog posts!🚨

Group name: aurora
Post title: Allmand-Smith Limited
Location: 🇬🇧 GB
Sector: Manufacturing
Info: https://cti.fyi/#disclosure/aurora/Allmand-Smith%20Limited

Group name: Ethics
Post title: Guarantee
Location: 🇺🇸 US
Info: https://cti.fyi/#disclosure/Ethics/Guarantee

Group name: Ethics
Post title: Support
Organization: Ethics Showcase
Location: 🇺🇸 US
Sector: Technology
Info: https://cti.fyi/#disclosure/Ethics/Support

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

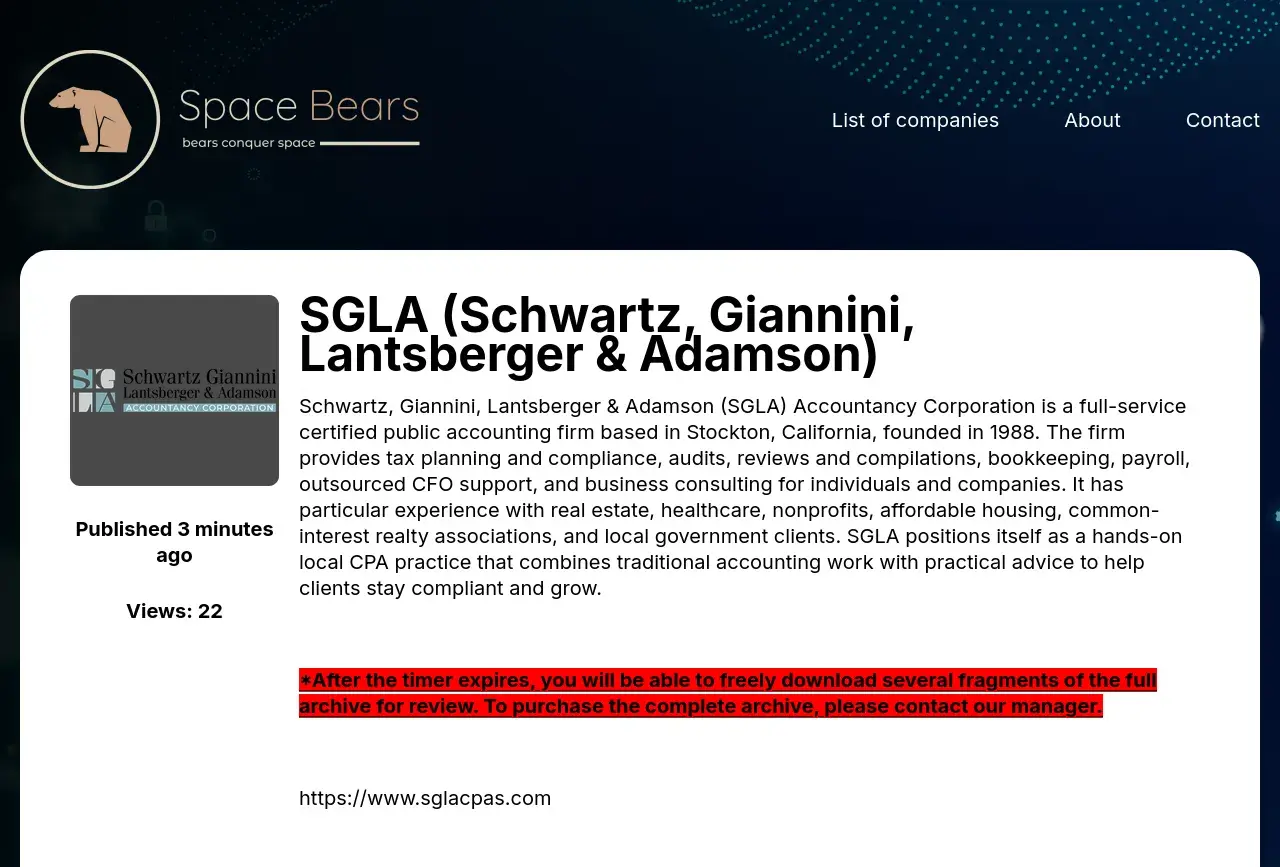
🚨New ransom group blog post!🚨

Group name: spacebears
Post title: SGLA (Schwartz, Giannini, Lantsberger & Adamson)
Organization: Schwartz, Giannini, Lantsberger & Adamson
Location: 🇺🇸 US
Sector: Professional Services
Info: https://cti.fyi/#disclosure/spacebears/SGLA%20%28Schwartz%2C%20Giannini%2C%20Lantsberger%20%26%20Adamson%29

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

If you run GitLab, you've handled some bad vulns recently, so what's one more? Perfect 10 patched today.

https://ifin.network/t/cve-2026-110264-integer-overflow-in-gitlab-regex-compiler/920

#ThreatIntel #ThreatIntelligence #IFIN

IFINCVE-2026-110264: Integer Overflow in Gitlab Regex CompilerLast Updated: 2026-10-21T23:33:33Z (UTC) CVSSv3: 10.0 GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary code on the GitLab server due to integer overflow when compiling a specially crafted regular expression. Another perfect 10 for GitLab, seemingly the same issue as the previous one from last week. The issue affe
↩ Reply ♡ 0 · ↻ 0 ↗ Original

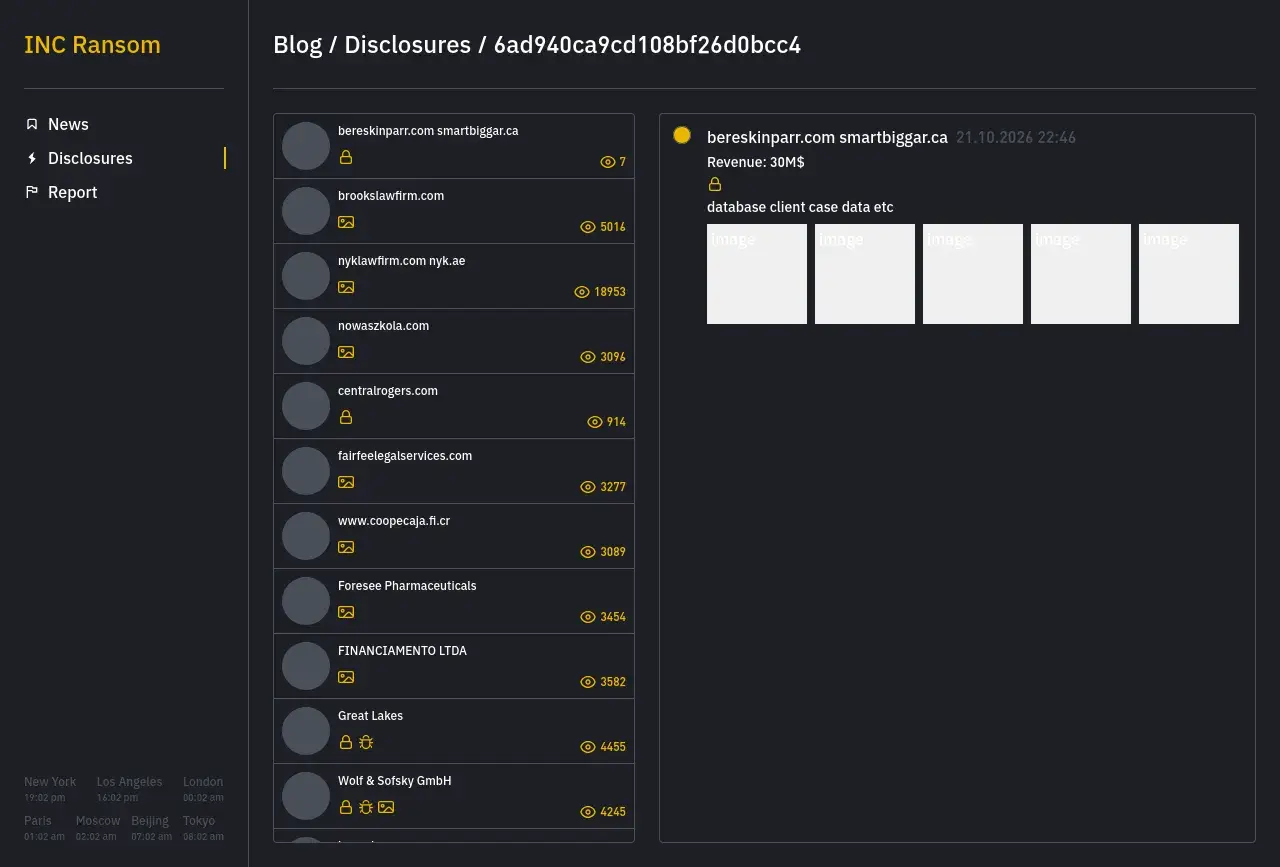
🚨New ransom group blog post!🚨

Group name: incransom
Post title: bereskinparr.com smartbiggar.ca
Organization: Smart Biggar LLP
Location: 🇨🇦 CA
Sector: Professional Services
Info: https://cti.fyi/#disclosure/incransom/bereskinparr.com%20smartbiggar.ca

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

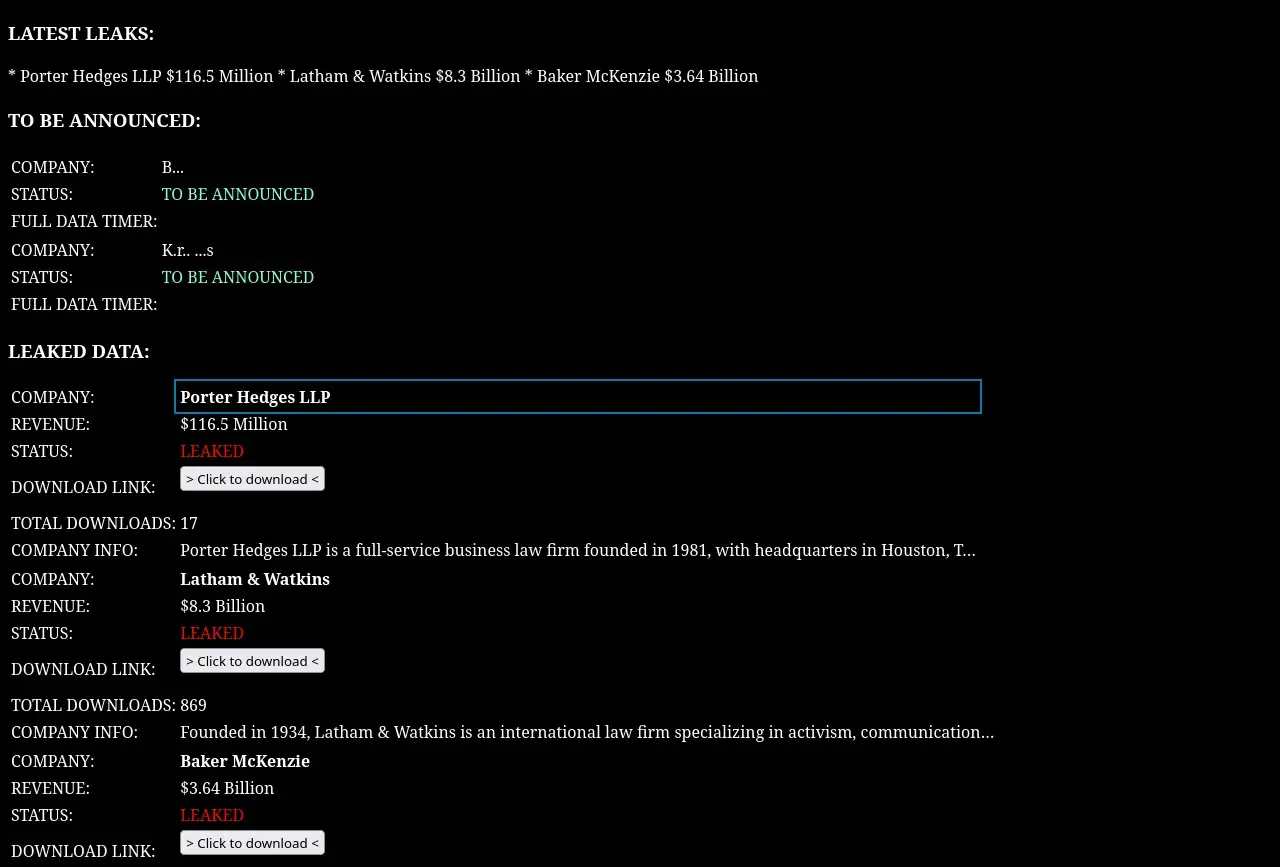
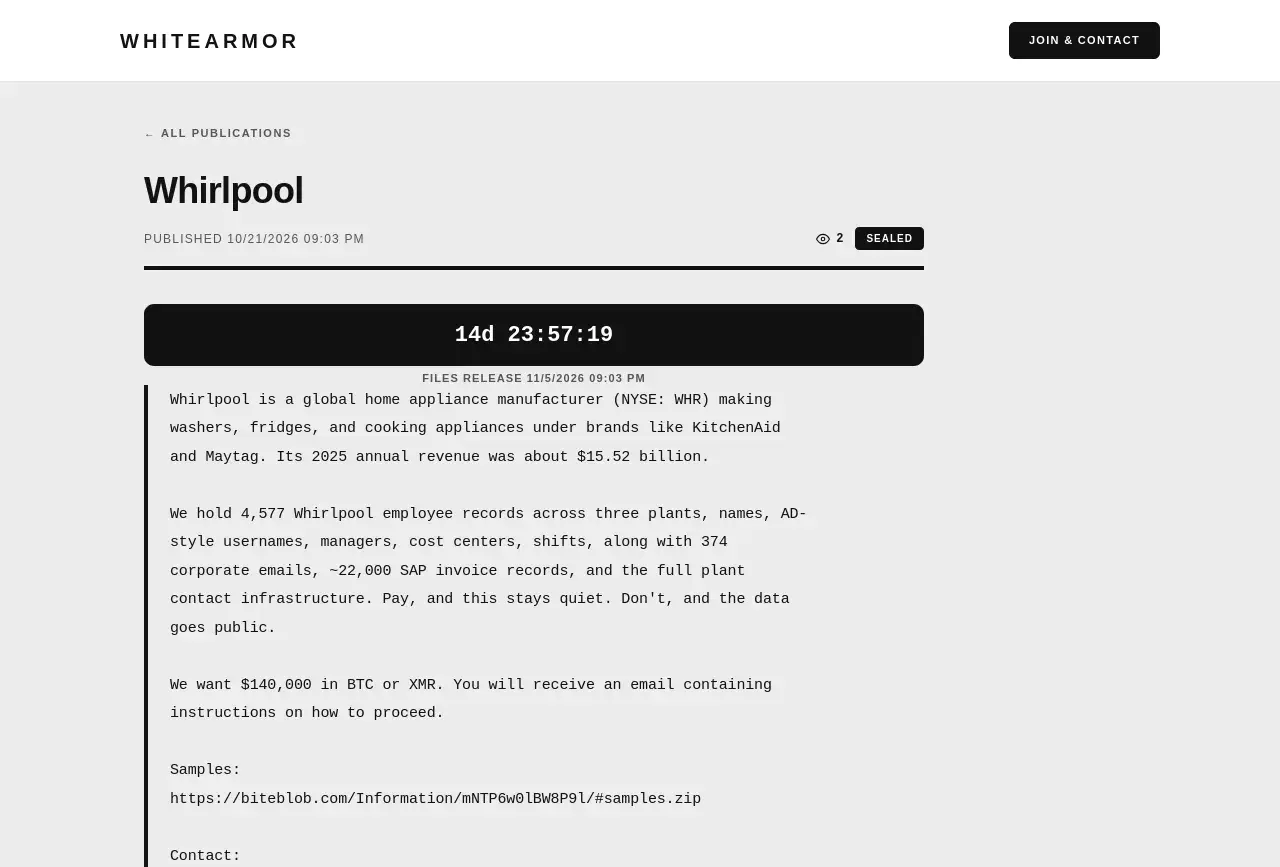
🚨New ransom group blog posts!🚨

Group name: SilentRansomGroup
Post title: Porter Hedges LLP
Location: 🇺🇸 US
Sector: Professional Services
Info: https://cti.fyi/#disclosure/SilentRansomGroup/Porter%20Hedges%20LLP

Group name: Whitearmor
Post title: Whirlpool
Location: 🇺🇸 US
Sector: Manufacturing
Info: https://cti.fyi/#disclosure/Whitearmor/Whirlpool

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

While you were patching PHP, LiteLLM went and get compromised again.

https://ifin.network/t/litellm-compromised-again-credential-stealer-and-backdoor/919

#ThreatIntel #ThreatIntelligence #IFIN

IFINLiteLLM Compromised Again: Credential Stealer and BackdoorLast Updated: 2026-10-21T18:41:47Z (UTC) What’s Happening LiteLLM has been compromised again. litellM 1.107.0 on PyPI has a credential stealer and a backdoor. The official litellM 1.107.0 Docker image is also affected. Both of these run when any python process is ran, regardless of if they import litellm or not. Versions 1.106.2, 1.107.0rc1, and 1.107.0rc2 are not compromised, nor are the pinne
↩ Reply ♡ 0 · ↻ 0 ↗ Original

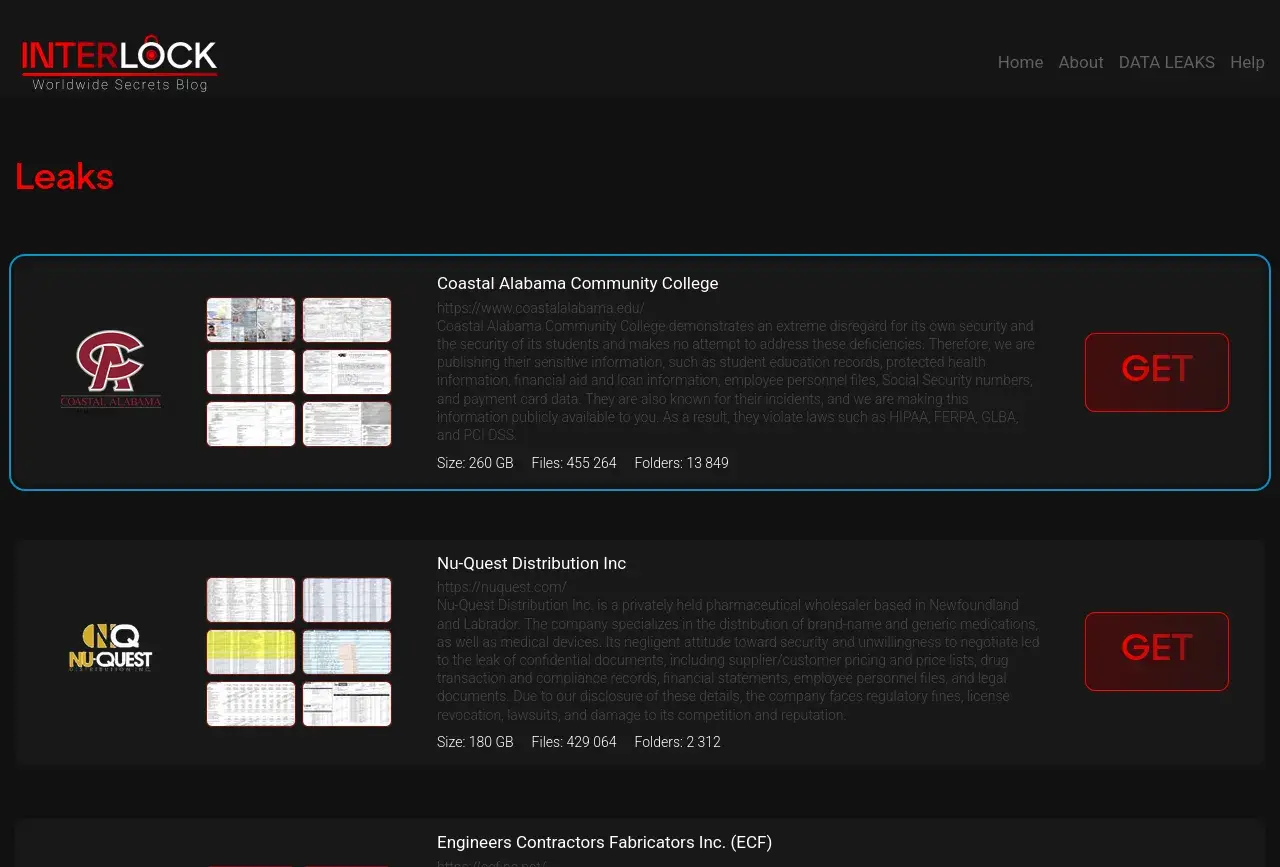
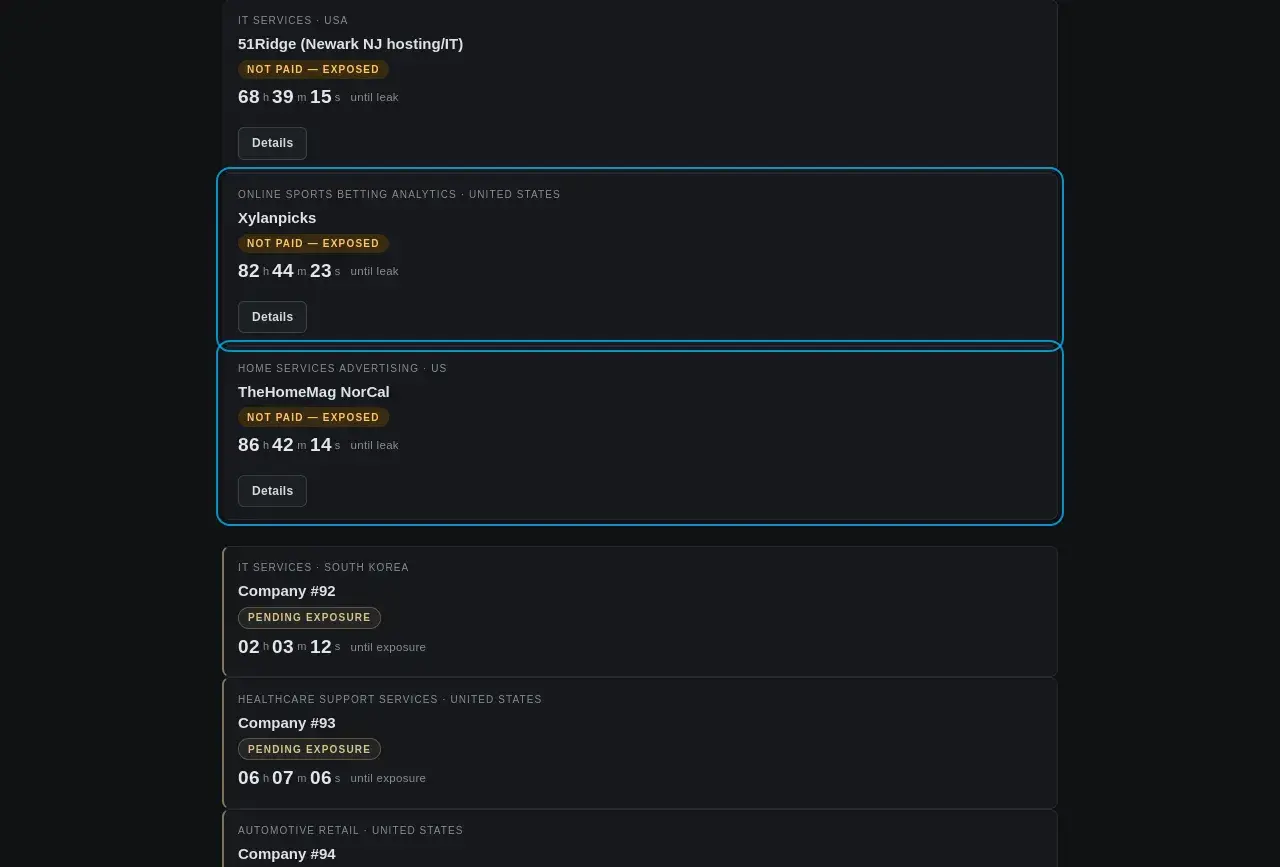
🚨New ransom group blog posts!🚨

Group name: interlock
Post title: Coastal Alabama Community College
Location: 🇺🇸 US
Sector: Education
Info: https://cti.fyi/#disclosure/interlock/Coastal%20Alabama%20Community%20College

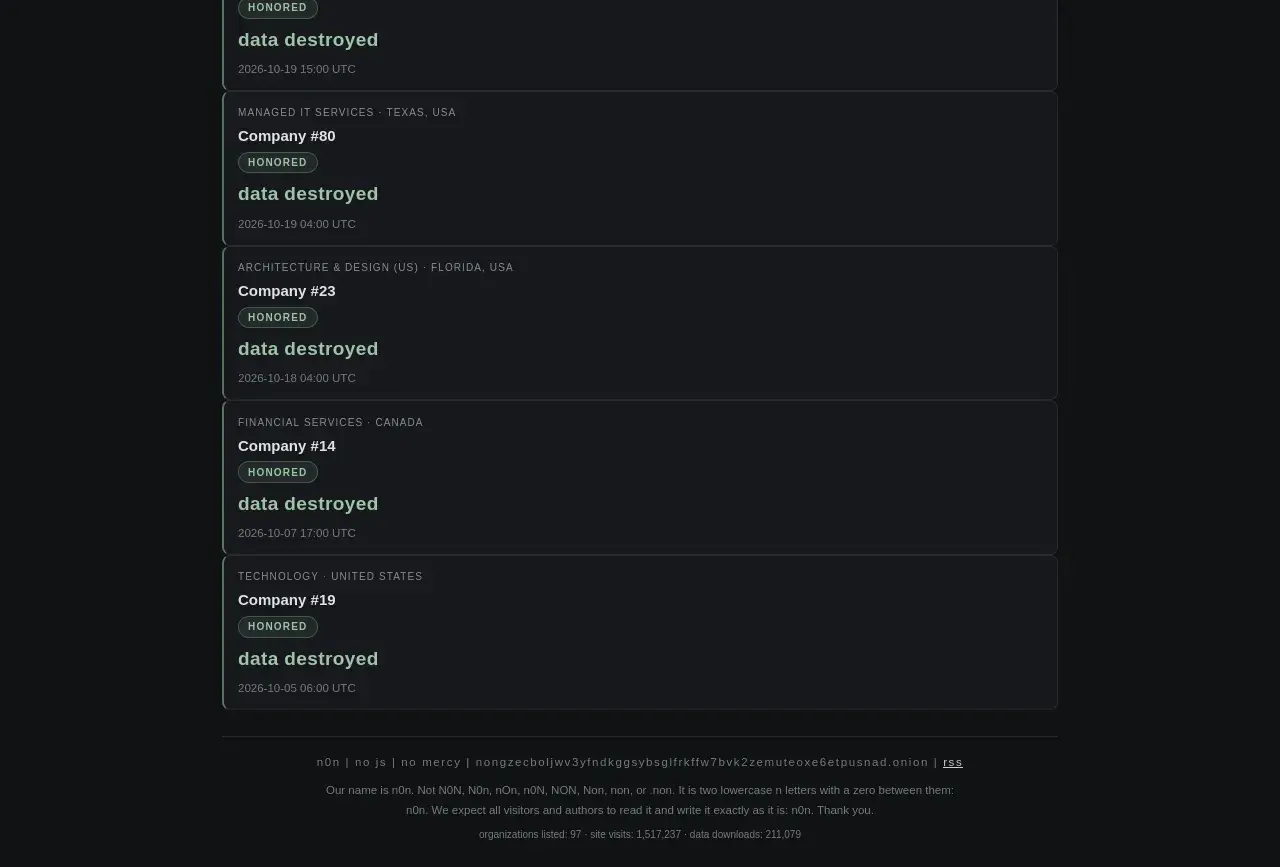
Group name: N0n
Post title: Xylanpicks
Location: 🇺🇸 US
Sector: Technology
Info: https://cti.fyi/#disclosure/N0n/Xylanpicks

Group name: N0n
Post title: TheHomeMag NorCal
Location: 🇺🇸 US
Sector: Professional Services
Info: https://cti.fyi/#disclosure/N0n/TheHomeMag%20NorCal

Group name: N0n
Post title: Company #99
Info: https://cti.fyi/#disclosure/N0n/Company%20%2399

Group name: N0n
Post title: Company #100
Info: https://cti.fyi/#disclosure/N0n/Company%20%23100

Group name: N0n
Post title: Company #101
Info: https://cti.fyi/#disclosure/N0n/Company%20%23101

Group name: N0n
Post title: Company #102
Info: https://cti.fyi/#disclosure/N0n/Company%20%23102

Group name: N0n
Post title: Company #103
Info: https://cti.fyi/#disclosure/N0n/Company%20%23103

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachmentMedia attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

New.

Very reassuring: "Notable among the observed TTPs is the exploitation of vulnerabilities in network devices such as FortiGate Firewalls and Palo Alto GlobalProtect to gain initial access."

"Group-IB and NyxLab expose threat actor k0t's large-scale campaign exploiting FortiGate, FortiWeb, and Palo Alto GlobalProtect edge devices to harvest credentials, establish persistent access and exfiltrate data."

Group-IB: Stray Cat, Open Doors: How k0t Wanders Through the Network Edge https://www.group-ib.com/blog/stray-cat-network-edge/ #infosec #vulnerability #Fortinet #cybercrime #threatintel #threatintelligence

Group-IBStray Cat, Open Doors: How k0t Wanders Through the Network EdgeGroup-IB and NyxLab expose threat actor k0t's large-scale campaign exploiting FortiGate, FortiWeb, and Palo Alto GlobalProtect edge devices to harvest credentials, establish persistent access and exfiltrate data
↩ Reply ♡ 0 · ↻ 0 ↗ Original

The official advisory and patches have been released. We are continue to track emergence of proofs-of-concept and exploits.

https://ifin.network/t/cve-2026-109618-cve-2026-109619-remote-code-execution-in-php/914

#PHP2Shell #ThreatIntelligence #ThreatIntel #IFIN

IFINCVE-2026-109618, CVE-2026-109619: Remote Code Execution in PHPCVSSv3: 9.2 Last Updated: 2026-10-21T14:06:57Z (UTC) What’s Happening On 2026-10-21T07:00:00Z (UTC), PHP published an advisory about two critical vulnerabilities in PHP. The GitHub security issue has also now been published. Earlier unsubstantiated reports put the CVSS at 10.0, and claimed that versions back to PHP 5 (8.5 is current) would be impacted. Researcher and Sigma rule creator Flor
↩ Reply ♡ 0 · ↻ 0 ↗ Original
J

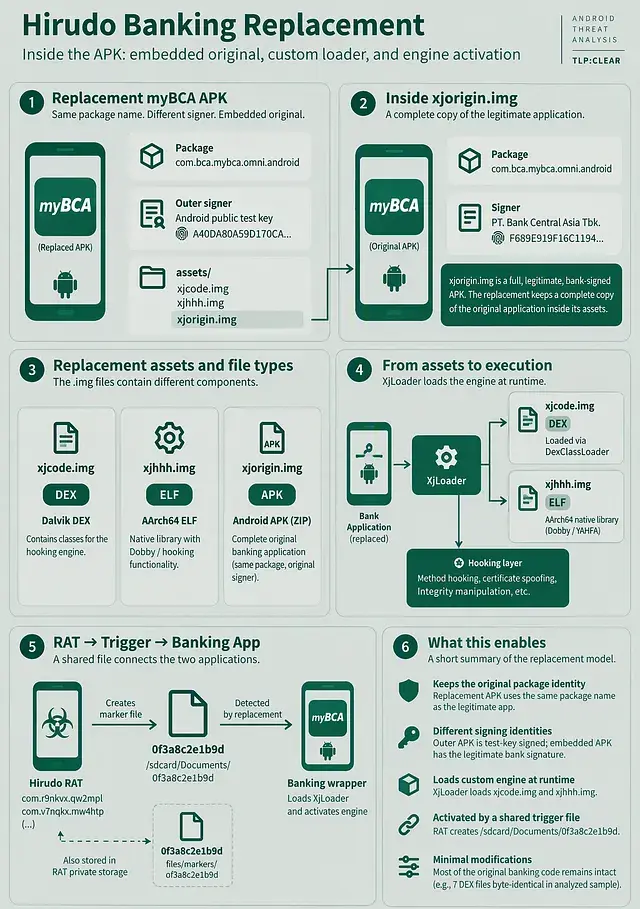
I’ve published an independent technical investigation into Hirudo, an Android banking RAT, focusing on its Indonesian banking-app replacement workflow, recovered APK artifacts, and associated infrastructure. This independent investigation was inspired by the research published by ThreatFabric. Motivated by their findings, I conducted a separate static reverse-engineering investigation focusing on Indonesian banking-app replacement artifacts, MQTT-based RAT communications, and additional infrastructure indicators. Sharing these findings with the cybersecurity community Cyber Defense Indonesia & Surabaya Hacker Link, to contribute to technical knowledge-sharing and further research into Android banking malware.

LINK:https://jeffanzos.medium.com/reverse-engineering-hirudo-indonesian-banking-targets-apk-replacement-and-rat-infrastructure-2b2890f0e4ca

Findings include: Banking app replacement (Recovered samples) associated with m-BCA, myBCA, BNI, BRI, BTN, Livin, JakOne, and BSI.

RAT infrastructure: Hardcoded C2 references and MQTT broker configurations recovered from DEX code, including 134[.]122.153[.]8:18085 and 134[.]122.153[.]8:1884.

APK internals: Hooking-engine artifacts, shared trigger-file mechanisms, certificate-substitution evidence, and embedded development paths.

Infrastructure pivots: Additional API endpoints, APK-processing panels, and certificate/DNS correlations for further investigation. The analysis is based primarily on static reverse engineering and supporting OSINT evidence. Live infrastructure behavior, several suspected relationships, and threat-actor attribution remain unverified. The objective is to document reproducible technical evidence and provide additional pivots for malware researchers, threat hunters, and incident responders.

#CyberSecurity #ThreatIntelligence #MalwareAnalysis #ReverseEngineering #DFIR #ThreatHunting #AndroidSecurity #DigitalForensics #InfoSec #InformationSecurity #CyberDefense #FinancialSecurity

Media attachment
MediumReverse-Engineering Hirudo: Indonesian Banking Targets, APK Replacement, and RAT InfrastructureAn independent technical investigation into Hirudo, focusing on Indonesian banking-app replacement workflows, artifacts recovered from…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

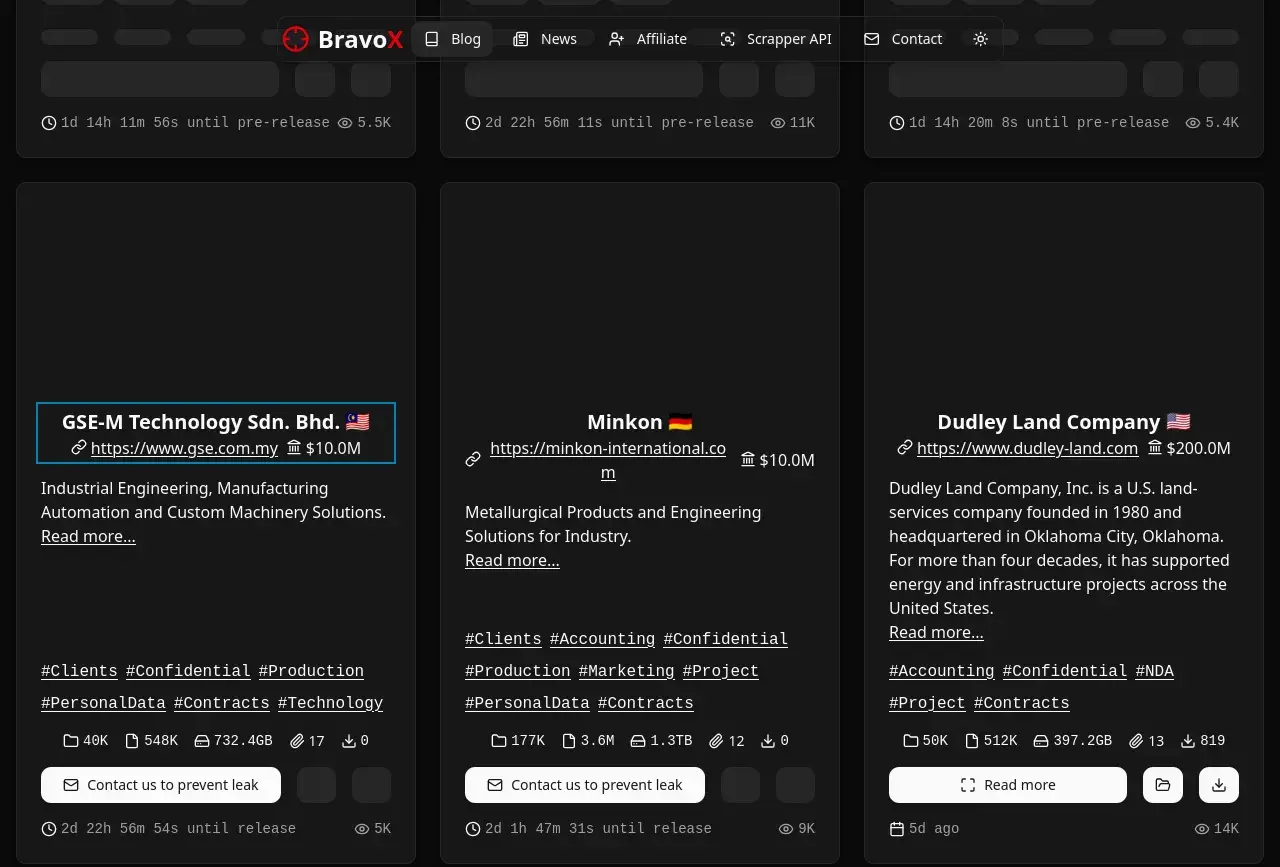
🚨New ransom group blog posts!🚨

Group name: bravox
Post title: GSE-M Technology Sdn. Bhd. 🇲🇾
Organization: GSE-M Technology Sdn. Bhd.
Location: 🇲🇾 MY
Sector: Technology
Info: https://cti.fyi/#disclosure/bravox/GSE-M%20Technology%20Sdn.%20Bhd.%20%F0%9F%87%B2%F0%9F%87%BE

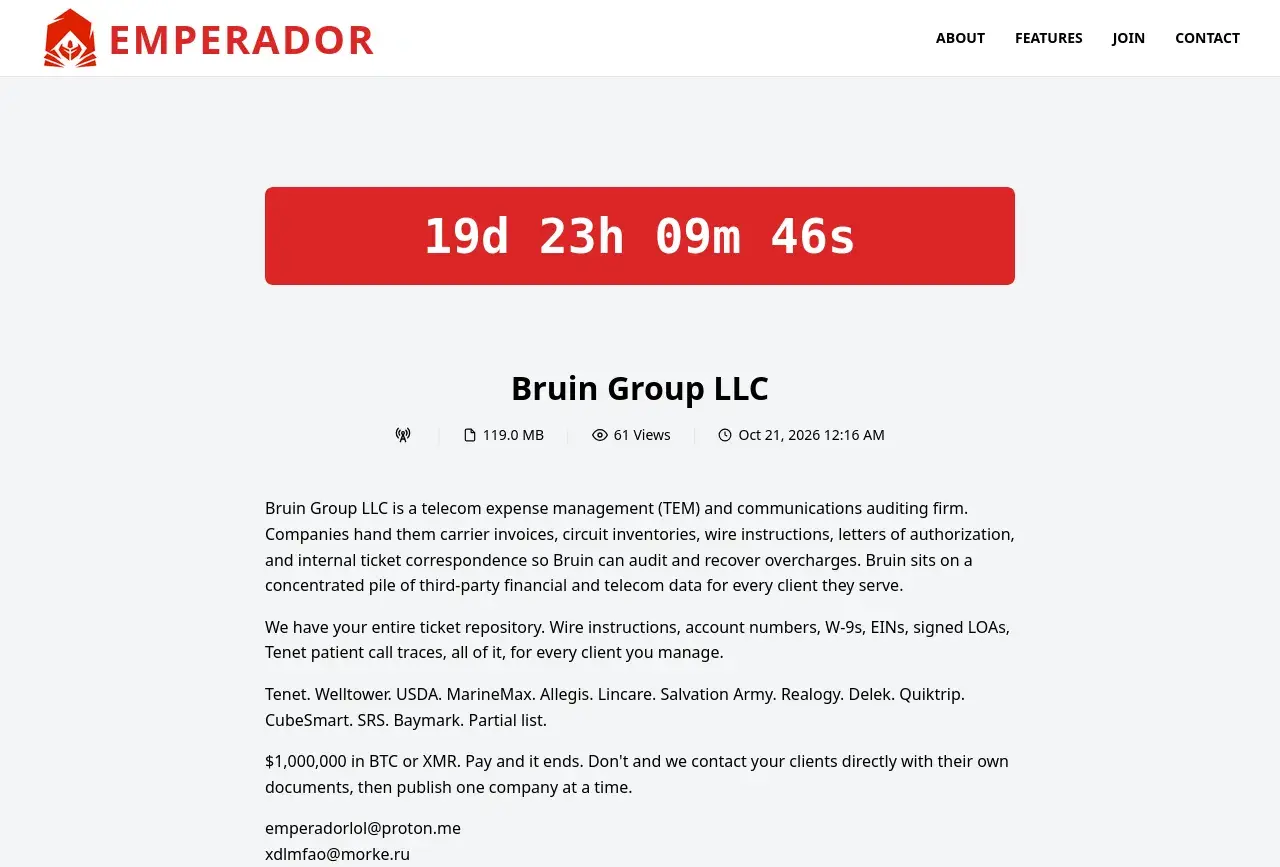
Group name: Emperador
Post title: Bruin Group LLC
Location: 🇺🇸 US
Sector: Construction
Info: https://cti.fyi/#disclosure/Emperador/Bruin%20Group%20LLC

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

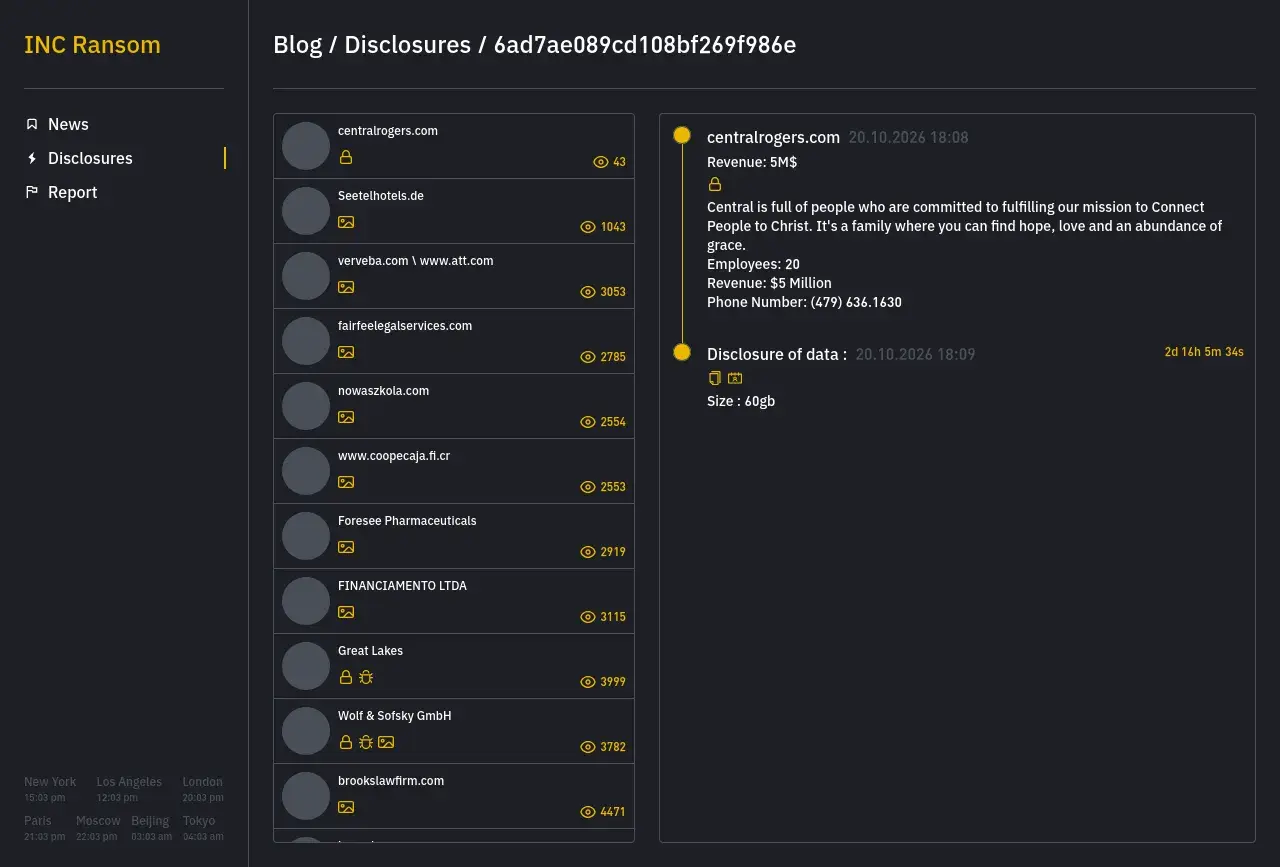
🚨New ransom group blog posts!🚨

Group name: incransom
Post title: centralrogers.com
Organization: Central
Location: 🇺🇸 US
Sector: Professional Services
Info: https://cti.fyi/#disclosure/incransom/centralrogers.com

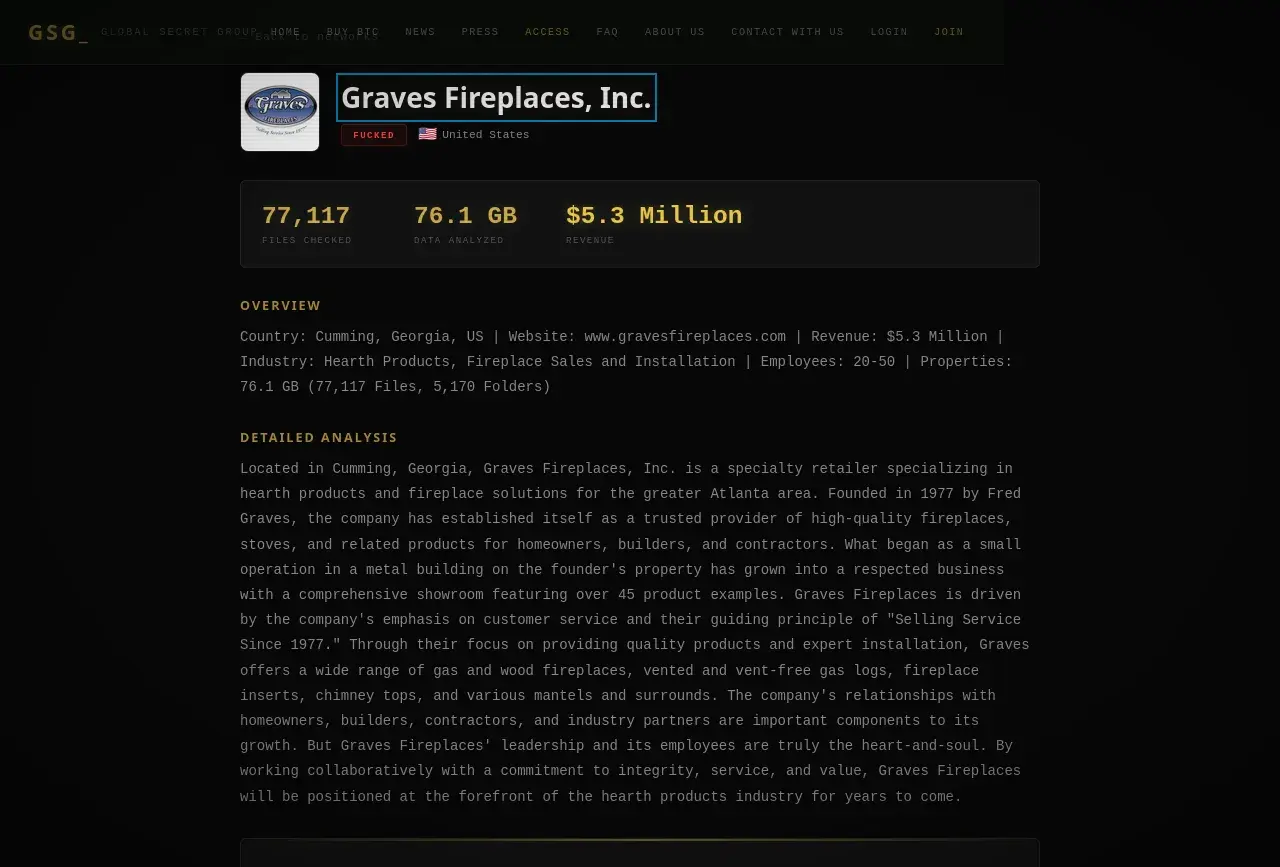
Group name: Global Secret Group
Post title: Graves Fireplaces, Inc.
Location: 🇺🇸 US
Sector: Manufacturing
Info: https://cti.fyi/#disclosure/Global%20Secret%20Group/Graves%20Fireplaces%2C%20Inc.

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🚨New ransom group blog posts!🚨

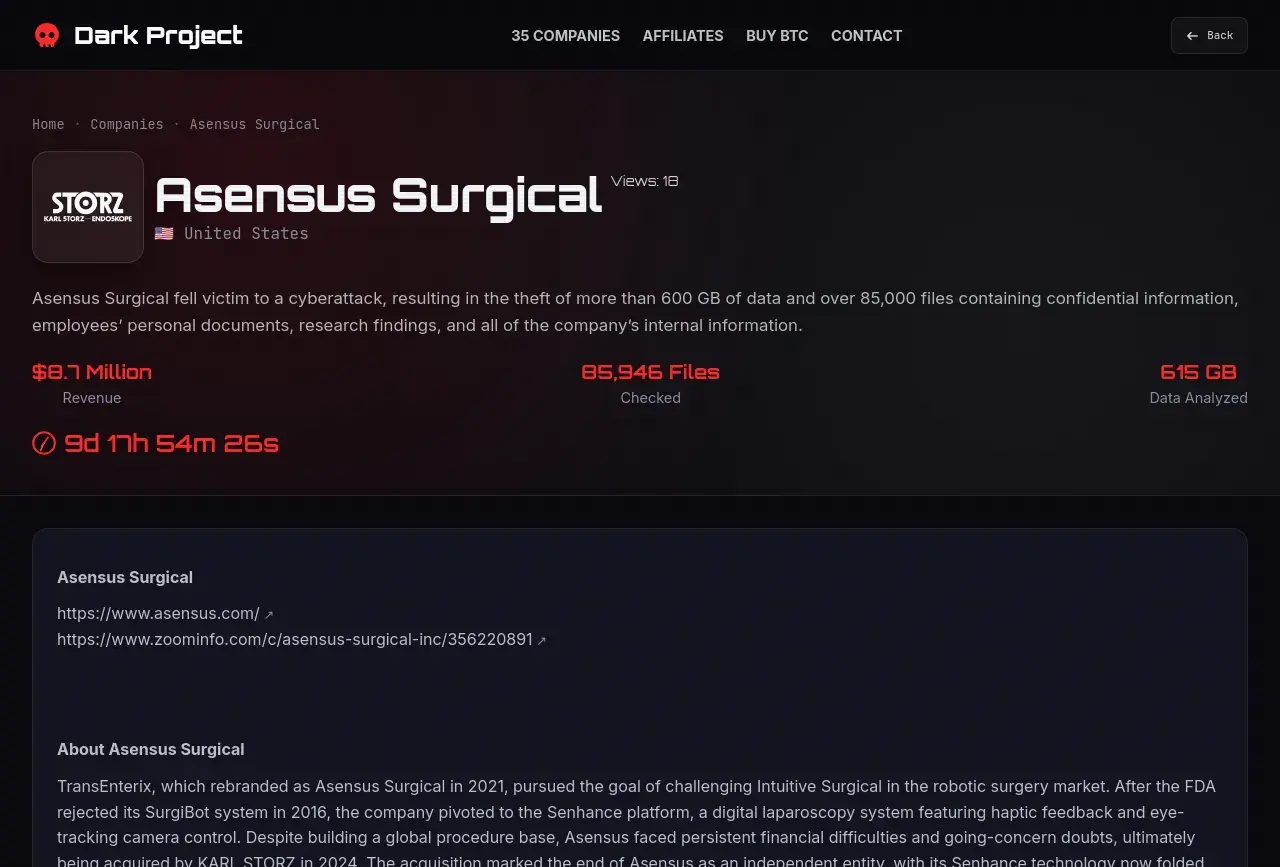
Group name: Dark Project
Post title: Asensus Surgical
Location: 🇺🇸 US
Sector: Manufacturing
Info: https://cti.fyi/#disclosure/Dark%20Project/Asensus%20Surgical

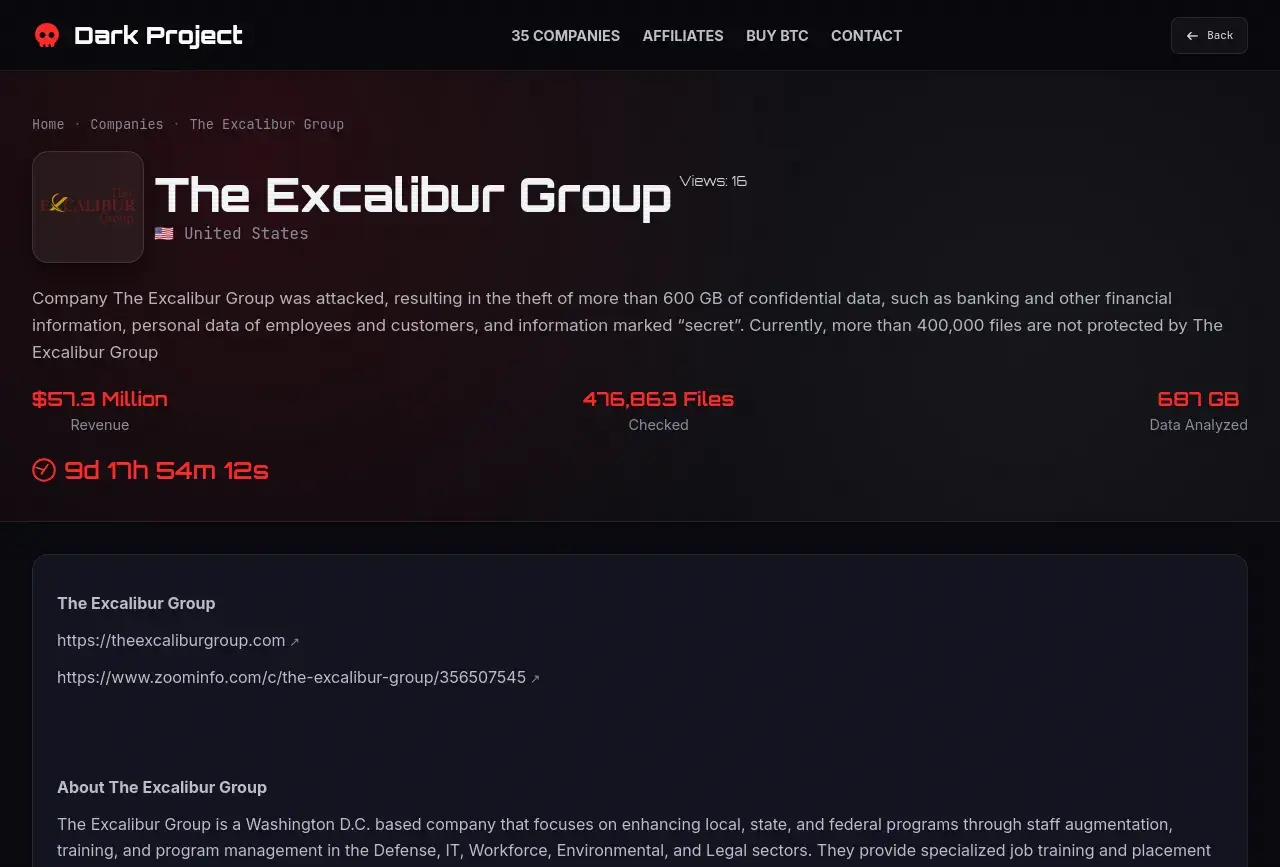
Group name: Dark Project
Post title: The Excalibur Group
Sector: Financial Services
Info: https://cti.fyi/#disclosure/Dark%20Project/The%20Excalibur%20Group

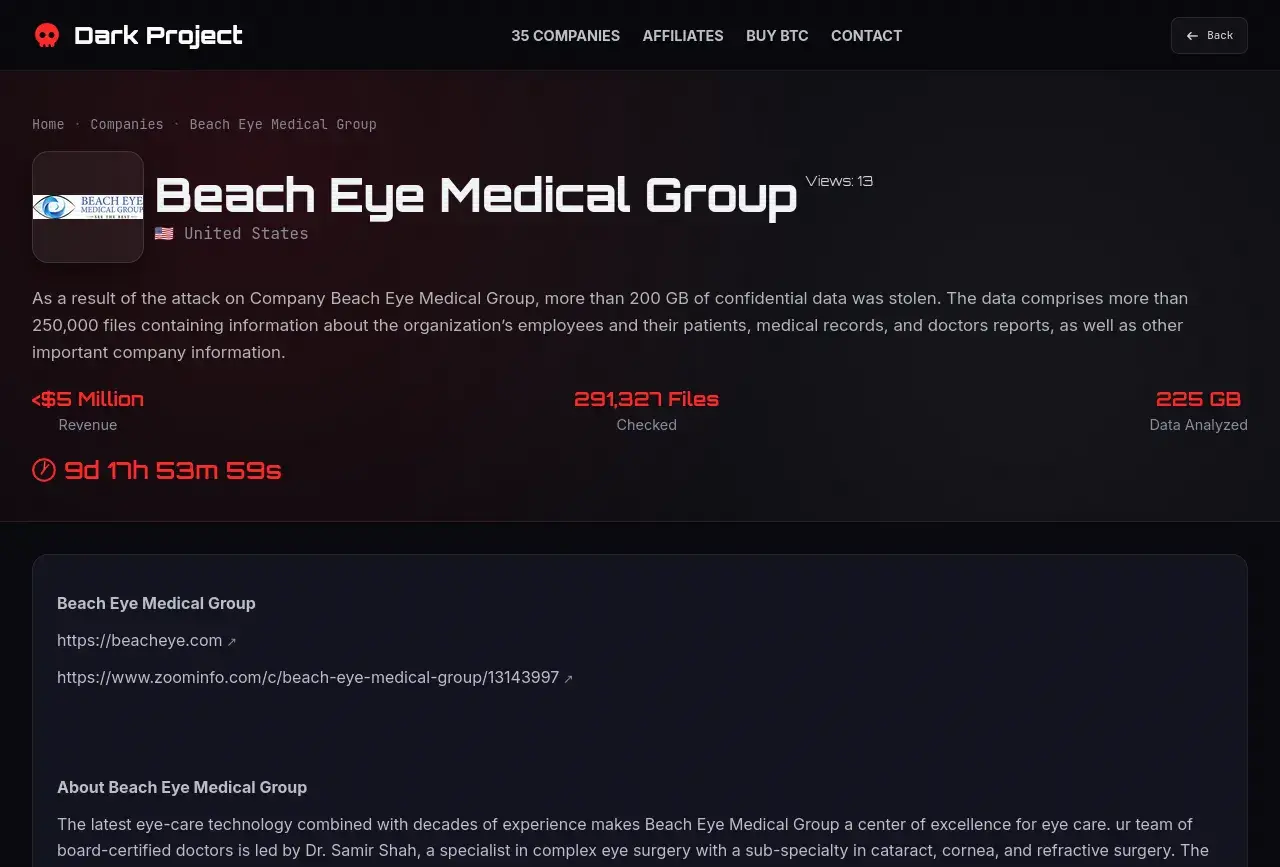
Group name: Dark Project
Post title: Beach Eye Medical Group
Sector: Healthcare
Info: https://cti.fyi/#disclosure/Dark%20Project/Beach%20Eye%20Medical%20Group

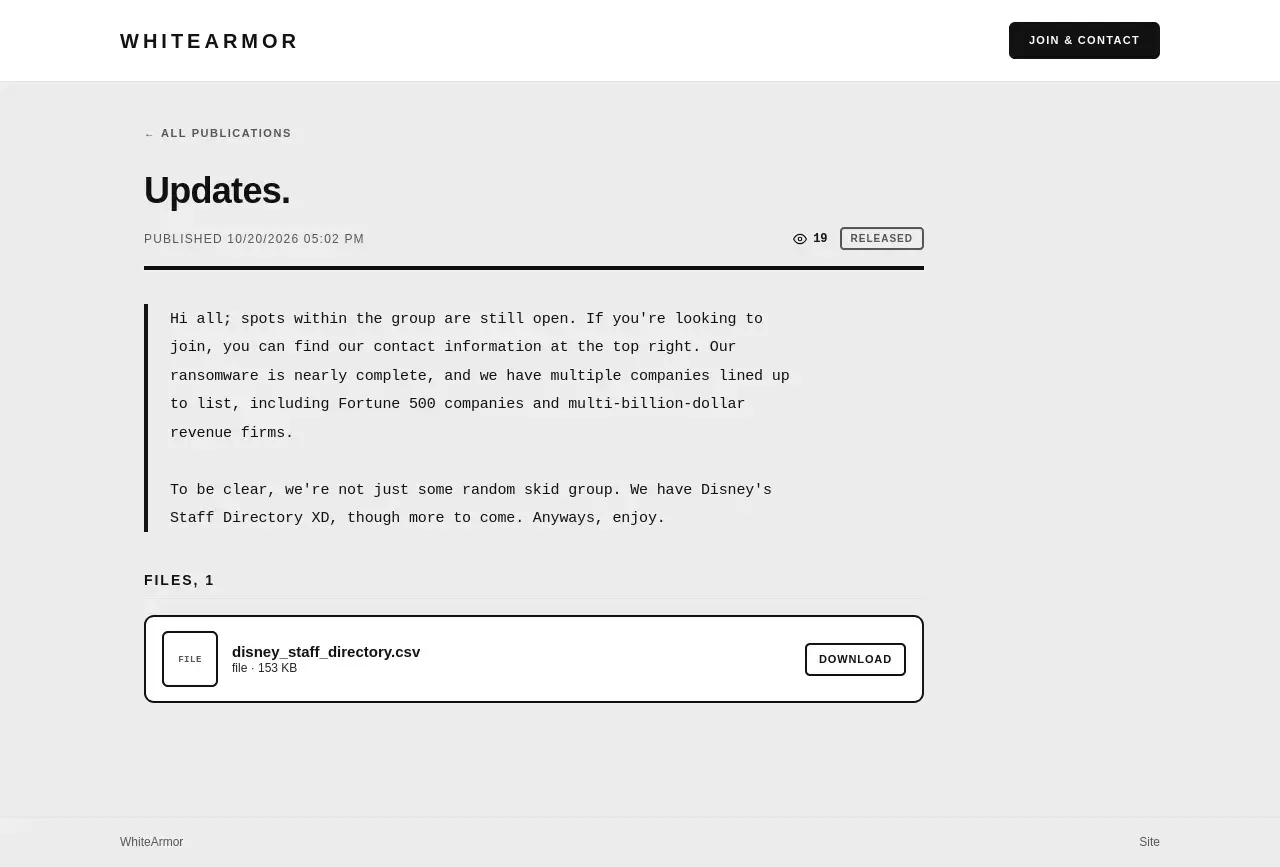
Group name: Whitearmor
Post title: Updates.
Organization: The Walt Disney Company
Location: 🇺🇸 US
Sector: Media & Entertainment
Info: https://cti.fyi/#disclosure/Whitearmor/Updates.

Group name: Whitearmor
Post title: W.A
Info: https://cti.fyi/#disclosure/Whitearmor/W.A

Group name: Mimori
Post title: OpenText
Location: 🇨🇦 CA
Sector: Technology
Info: https://cti.fyi/#disclosure/Mimori/OpenText

Group name: Mimori
Post title: Aveva
Location: 🇬🇧 GB
Sector: Technology
Info: https://cti.fyi/#disclosure/Mimori/Aveva

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachmentMedia attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Eight intermediate certificates used by eMudhra/Emsign have been compromised. These certificates are in multiple trust stores. This will require significant manual action to remediate, including the updates of several packages/

https://ifin.network/t/emudhra-intermediate-certificates-compromised/909

#ThreatIntel #ThreatIntelligence #IFIN

IFINeMudhra Intermediate Certificates CompromisedLast Updated: 2026-10-20T14:45:34Z (UTC) What’s Happening At 2026-10-20T13:01:00Z (UTC), Mozilla Cryptography Team member Dennis Jackson reported to the Mozilla Google Group about a compromised intermediate certificate authority (CA) belonging to eMudhra. Eight separate private keys belonging to the CA were compromised, according to the notice. Jackson reported further on the issue on a dedicat
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🚨New ransom group blog post!🚨

Group name: N0n
Post title: 51Ridge (Newark NJ hosting/IT)
Organization: 51Ridge
Location: 🇺🇸 US
Sector: Technology
Info: https://cti.fyi/#disclosure/N0n/51Ridge%20%28Newark%20NJ%20hosting%2FIT%29

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

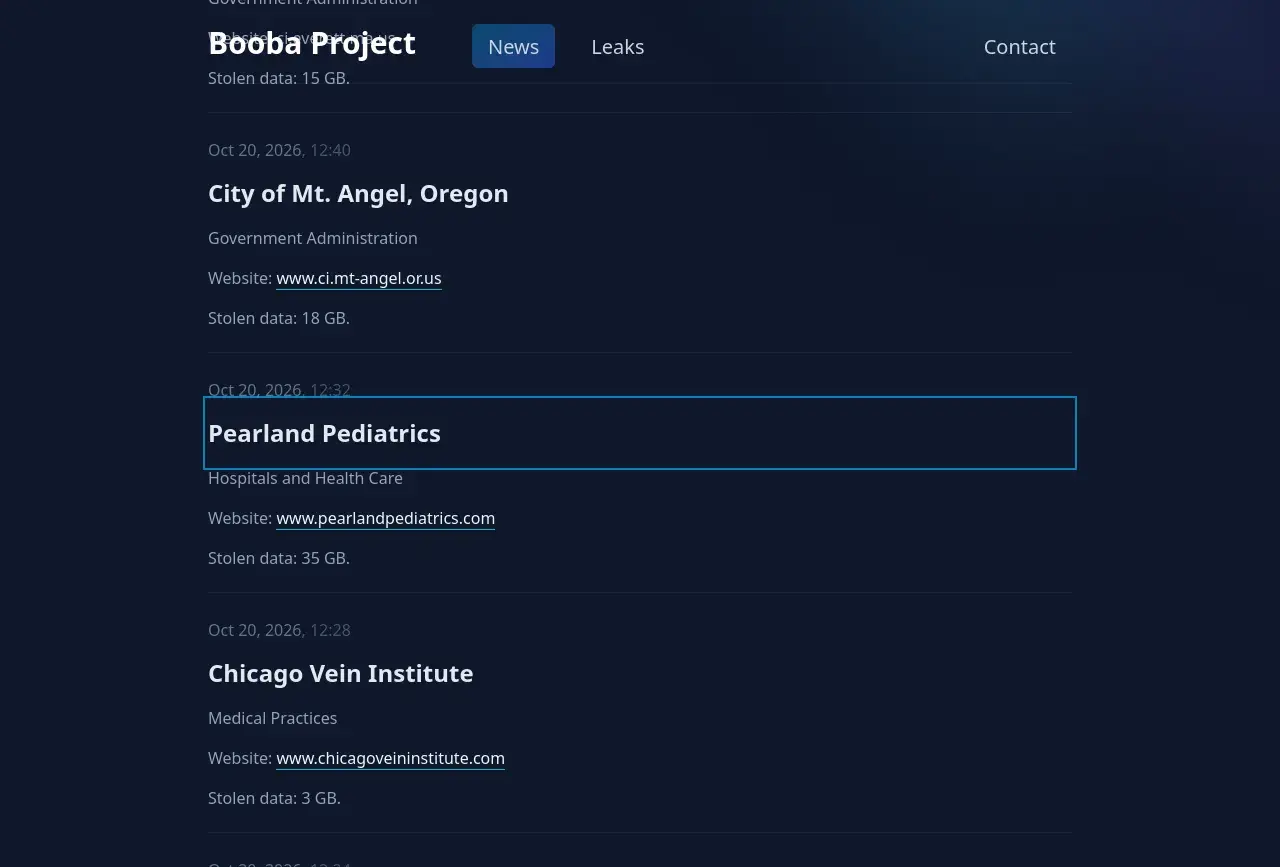
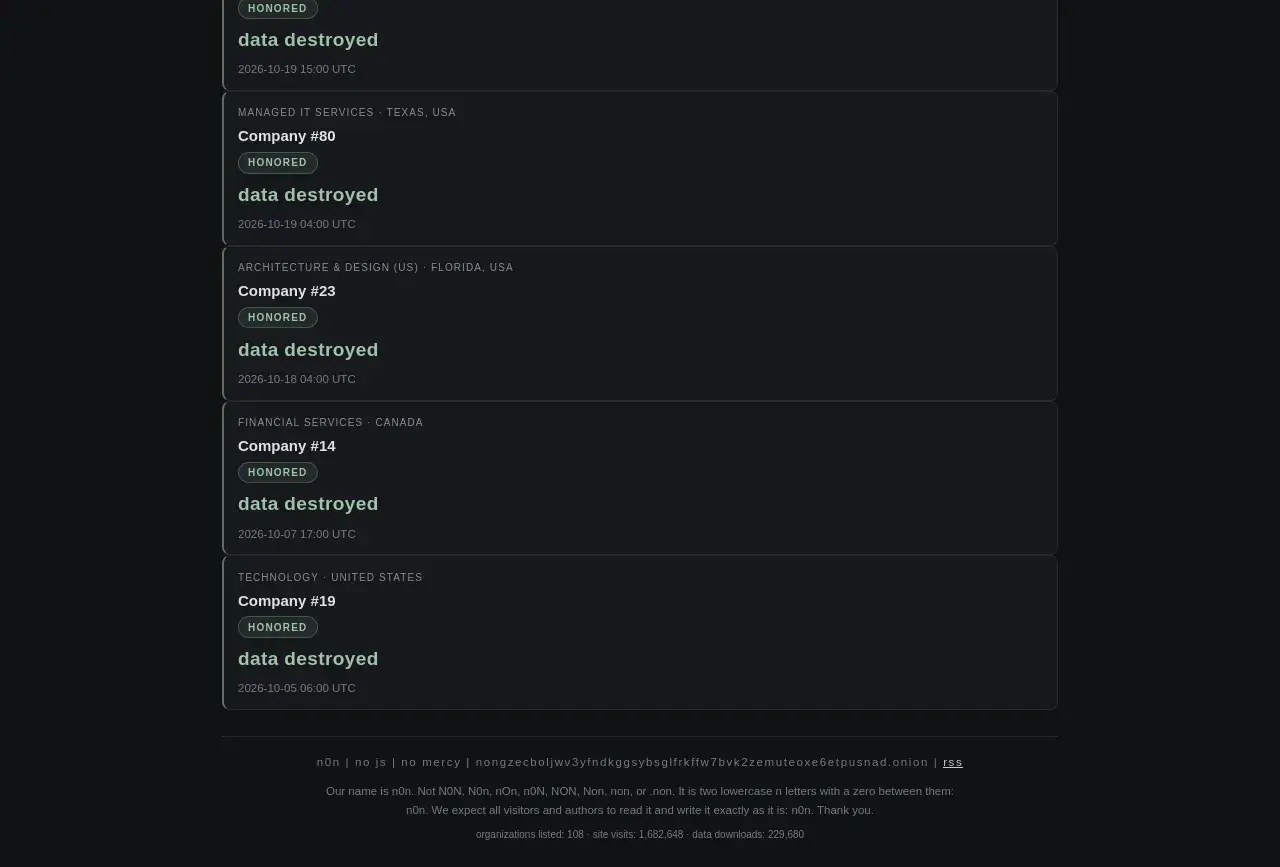
🚨New ransom group blog posts!🚨

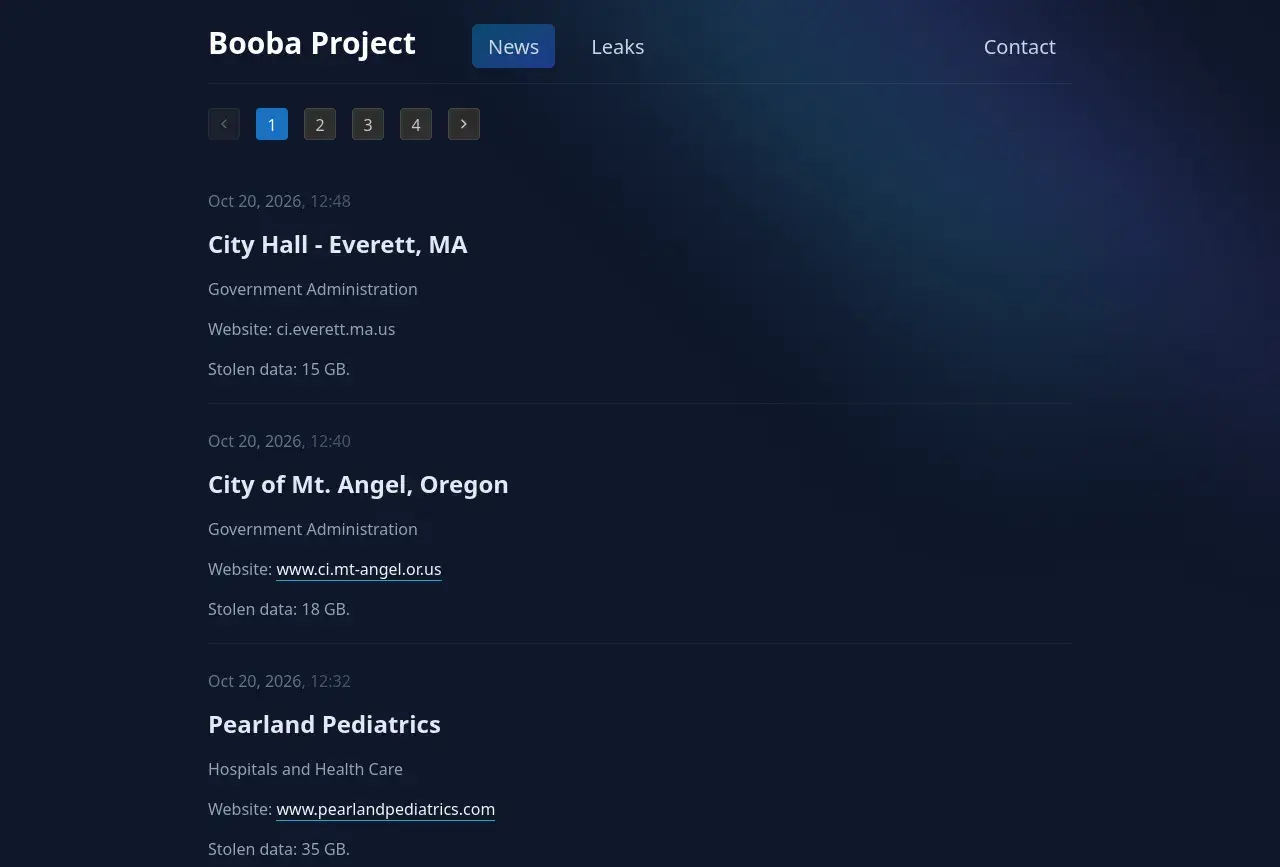
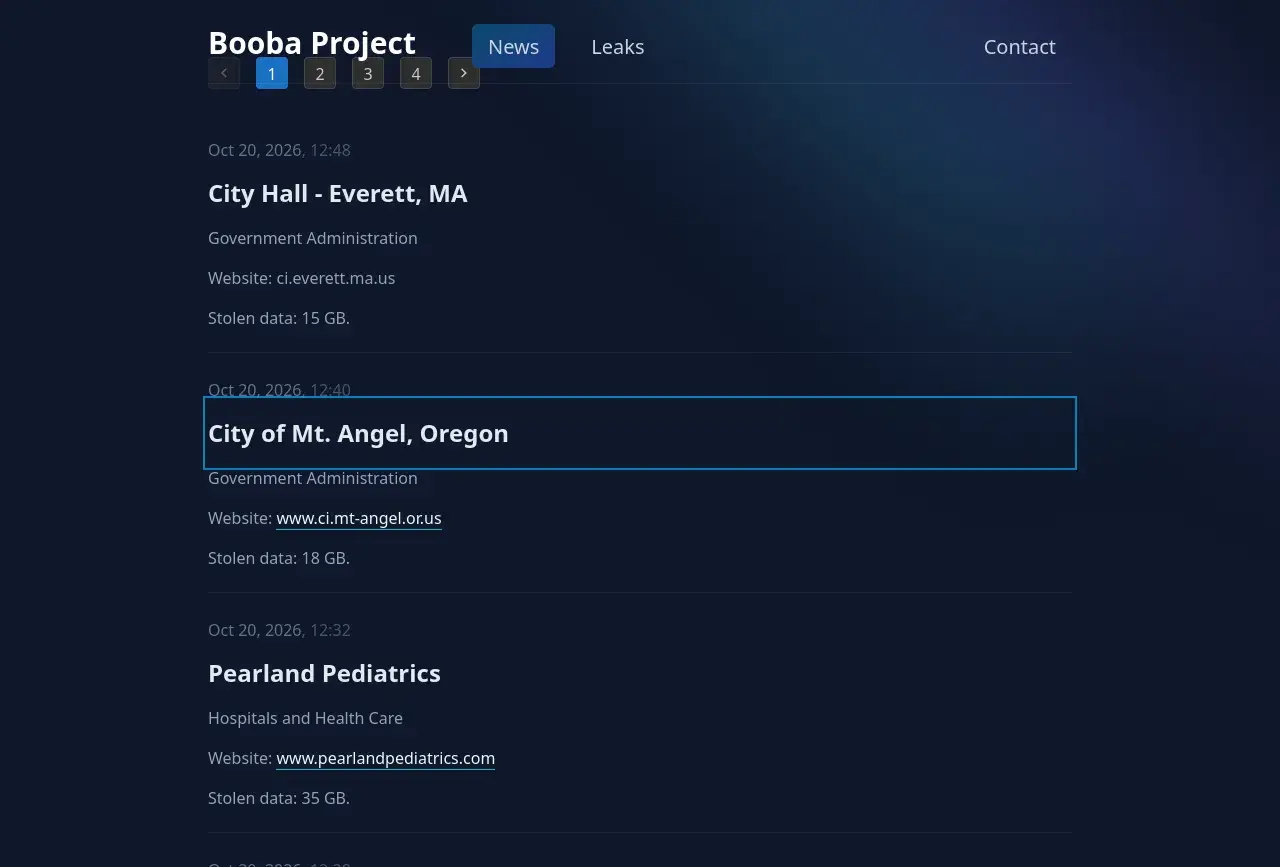
Group name: Booba Project
Post title: City Hall - Everett, MA
Organization: Everett City Hall
Location: 🇺🇸 US
Sector: Government & Public Sector
Info: https://cti.fyi/#disclosure/Booba%20Project/City%20Hall%20-%20Everett%2C%20MA

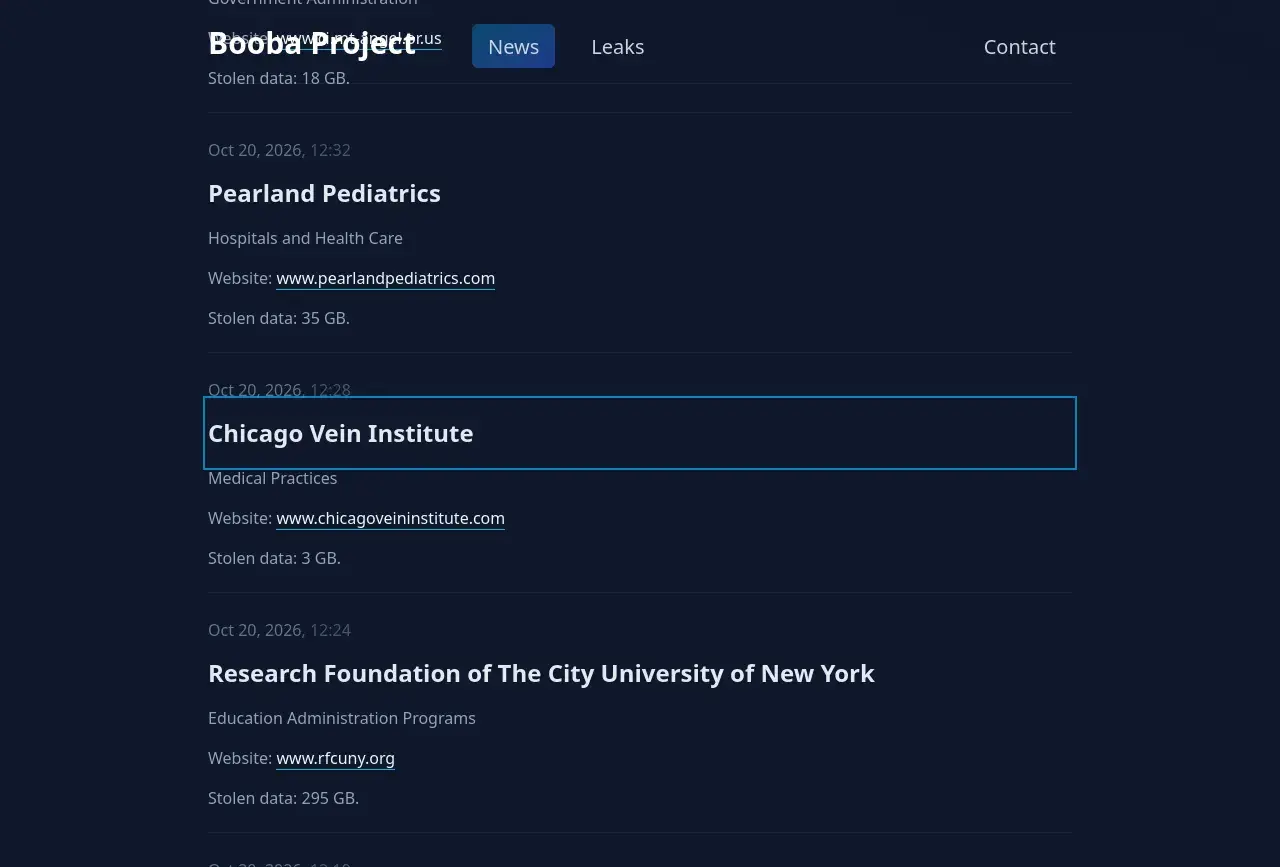
Group name: Booba Project
Post title: City of Mt. Angel, Oregon
Organization: City of Mt. Angel
Location: 🇺🇸 US
Sector: Government & Public Sector
Info: https://cti.fyi/#disclosure/Booba%20Project/City%20of%20Mt.%20Angel%2C%20Oregon

Group name: Booba Project
Post title: Pearland Pediatrics
Location: 🇺🇸 US
Sector: Healthcare
Info: https://cti.fyi/#disclosure/Booba%20Project/Pearland%20Pediatrics

Group name: Booba Project
Post title: Chicago Vein Institute
Location: 🇺🇸 US
Sector: Healthcare
Info: https://cti.fyi/#disclosure/Booba%20Project/Chicago%20Vein%20Institute

Group name: Booba Project
Post title: Research Foundation of The City University of New York
Location: 🇺🇸 US
Sector: Education
Info: https://cti.fyi/#disclosure/Booba%20Project/Research%20Foundation%20of%20The%20City%20University%20of%20New%20York

Group name: Booba Project
Post title: COASTAL CAROLINA NEUROPSYCHIATRIC CENTER, PA
Organization: COASTAL CAROLINA NEUROPSYCHIATRIC CENTER
Location: 🇺🇸 US
Sector: Healthcare
Info: https://cti.fyi/#disclosure/Booba%20Project/COASTAL%20CAROLINA%20NEUROPSYCHIATRIC%20CENTER%2C%20PA

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachmentMedia attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

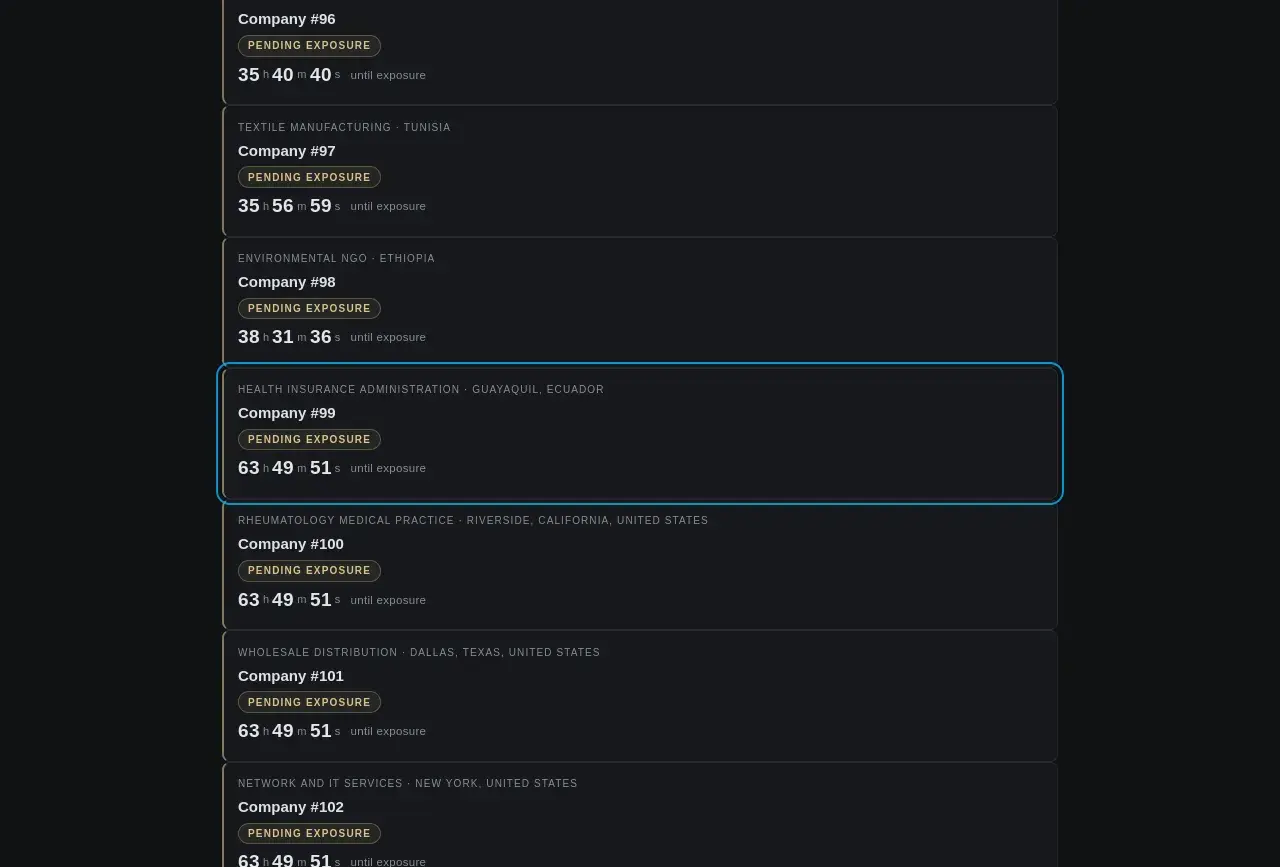
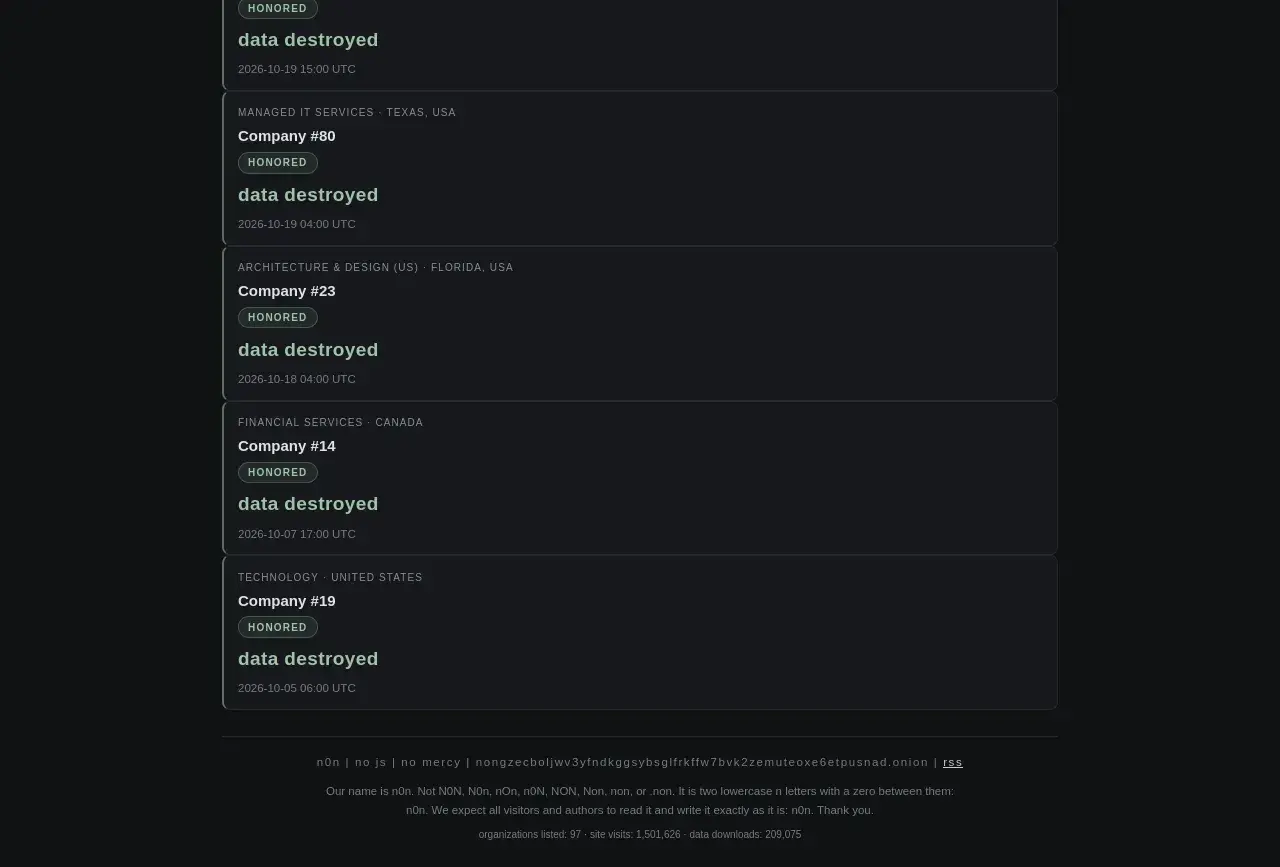
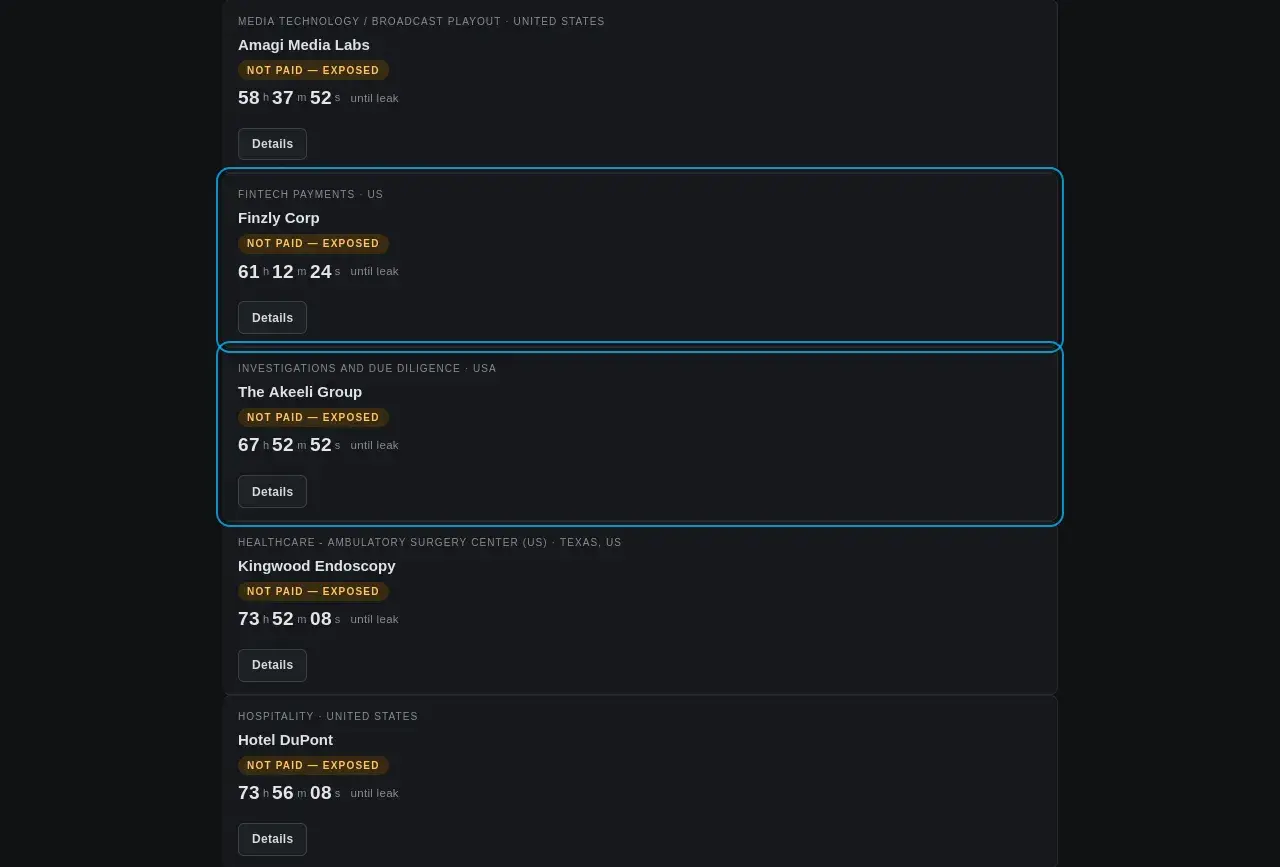
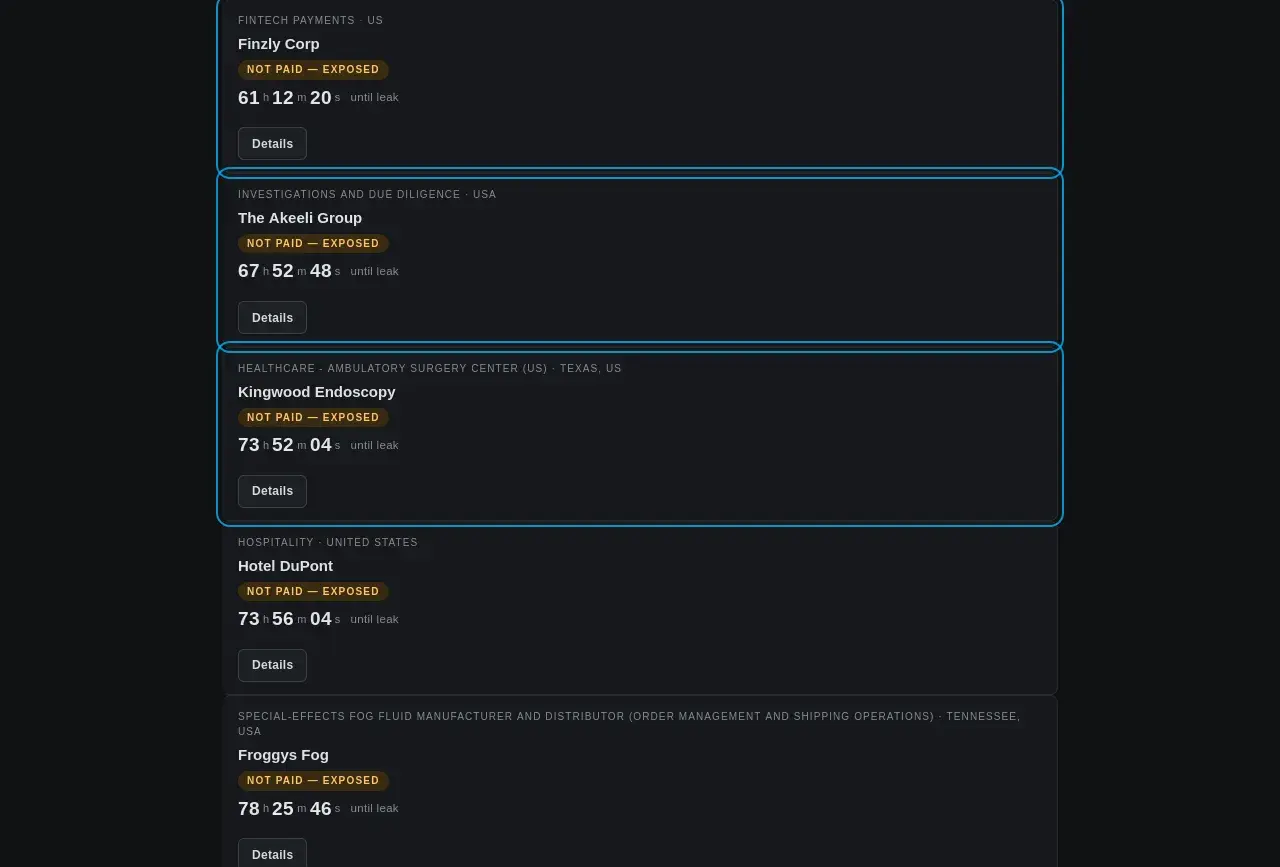
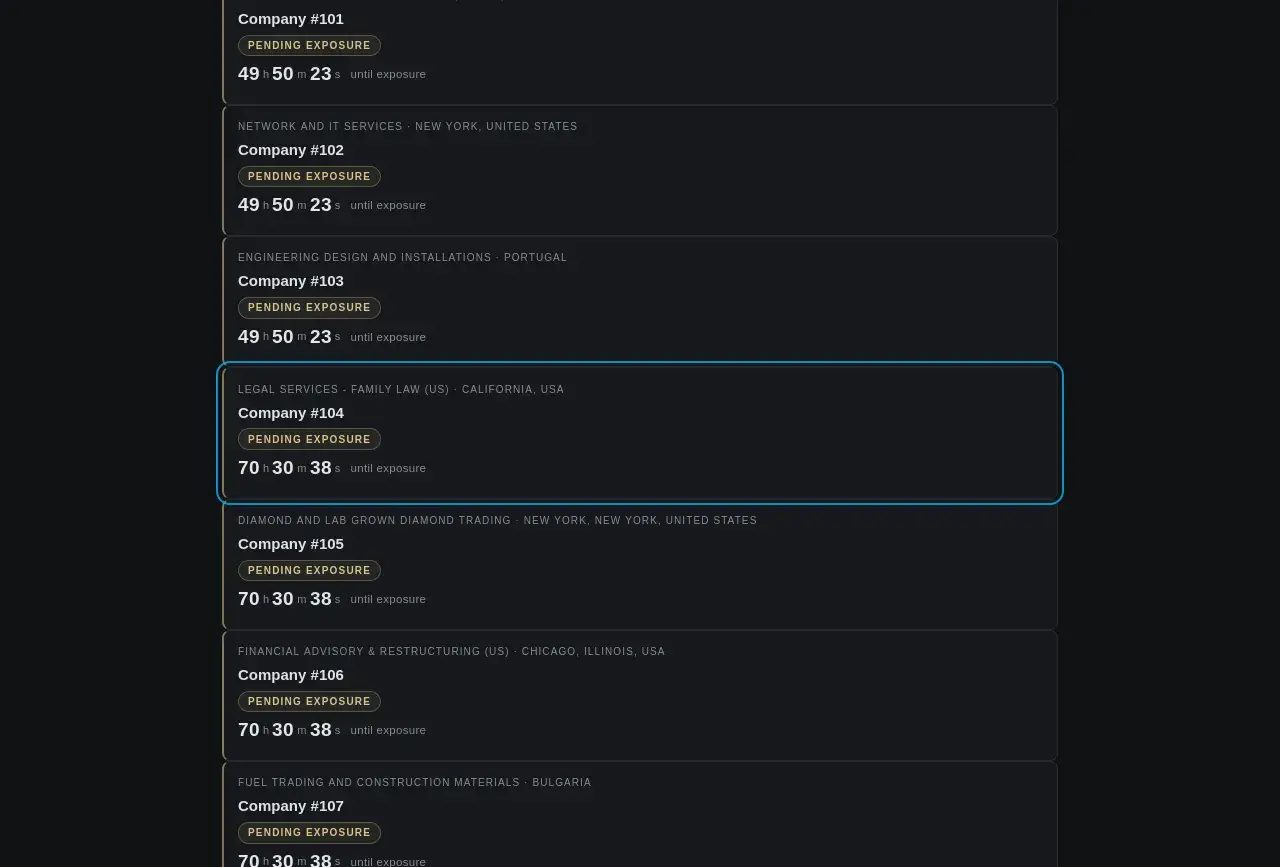
🚨New ransom group blog posts!🚨

Group name: N0n
Post title: Finzly Corp
Location: 🇺🇸 US
Sector: Financial Services
Info: https://cti.fyi/#disclosure/N0n/Finzly%20Corp

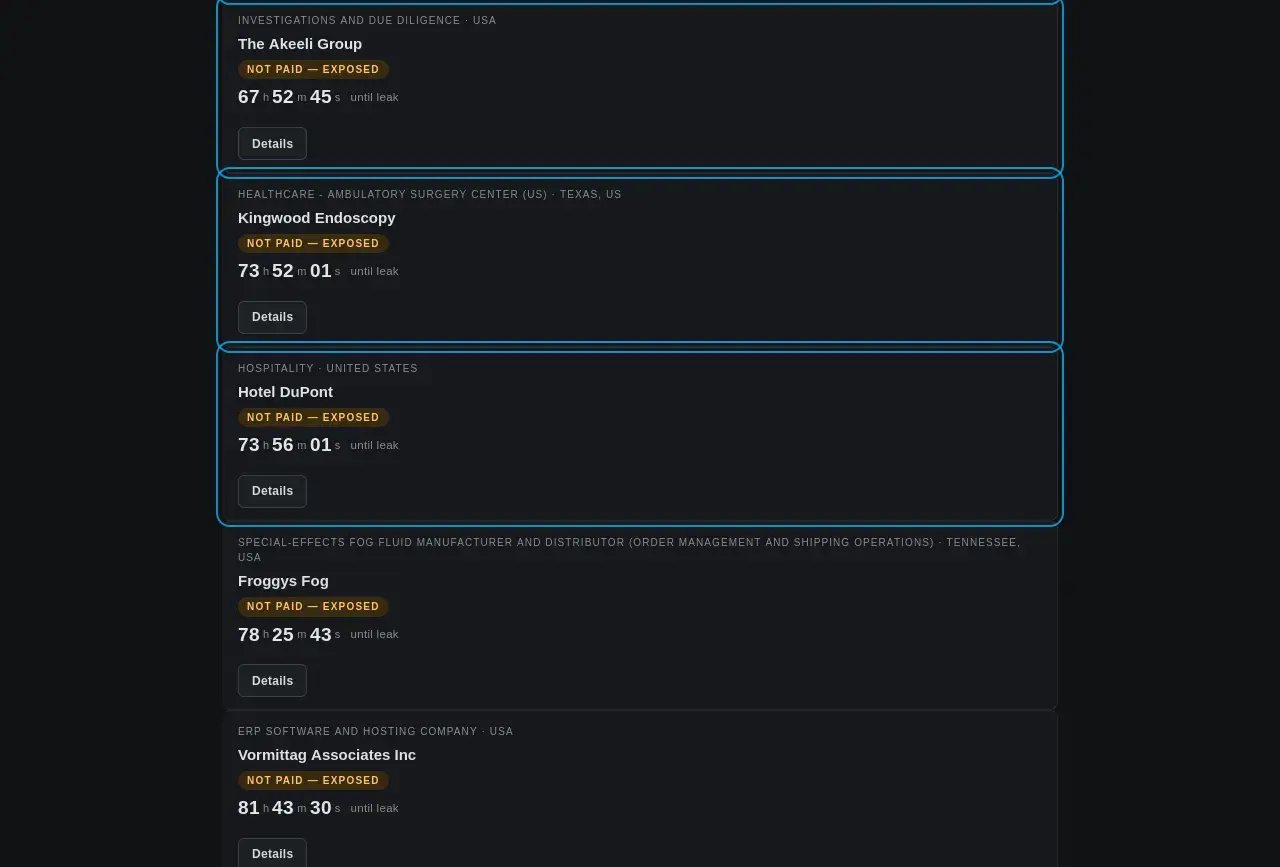
Group name: N0n
Post title: The Akeeli Group
Location: 🇺🇸 US
Sector: Professional Services
Info: https://cti.fyi/#disclosure/N0n/The%20Akeeli%20Group

Group name: N0n
Post title: Kingwood Endoscopy
Location: 🇺🇸 US
Sector: Healthcare
Info: https://cti.fyi/#disclosure/N0n/Kingwood%20Endoscopy

Group name: N0n
Post title: Hotel DuPont
Location: 🇺🇸 US
Sector: Hospitality & Tourism
Info: https://cti.fyi/#disclosure/N0n/Hotel%20DuPont

Group name: N0n
Post title: Froggys Fog
Location: 🇺🇸 US
Sector: Manufacturing
Info: https://cti.fyi/#disclosure/N0n/Froggys%20Fog

Group name: N0n
Post title: Vormittag Associates Inc
Location: 🇺🇸 US
Sector: Technology
Info: https://cti.fyi/#disclosure/N0n/Vormittag%20Associates%20Inc

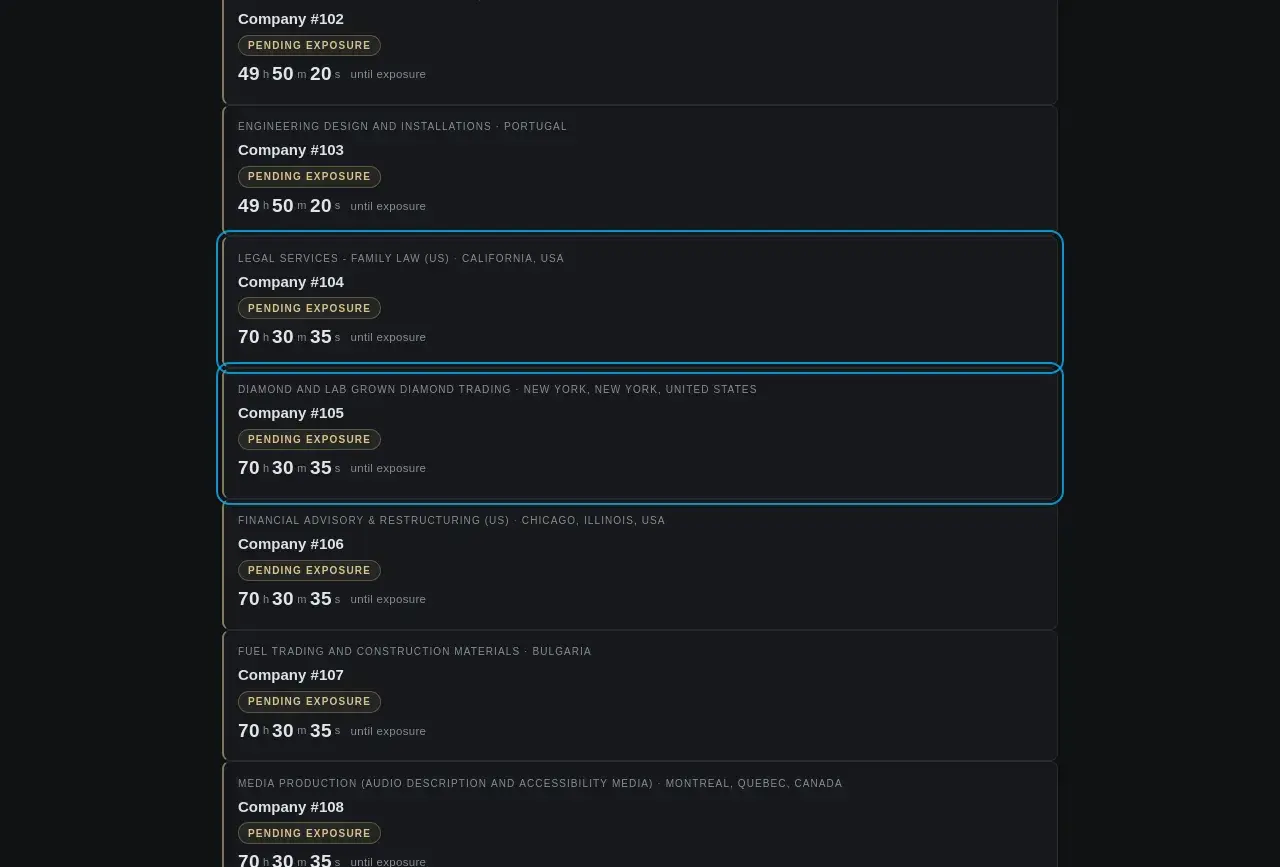
Group name: N0n
Post title: Company #93
Info: https://cti.fyi/#disclosure/N0n/Company%20%2393

Group name: N0n
Post title: Company #94
Info: https://cti.fyi/#disclosure/N0n/Company%20%2394

Group name: N0n
Post title: Company #95
Info: https://cti.fyi/#disclosure/N0n/Company%20%2395

Group name: N0n
Post title: Company #96
Info: https://cti.fyi/#disclosure/N0n/Company%20%2396

Group name: N0n
Post title: Company #97
Info: https://cti.fyi/#disclosure/N0n/Company%20%2397

Group name: N0n
Post title: Company #98
Info: https://cti.fyi/#disclosure/N0n/Company%20%2398

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachmentMedia attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

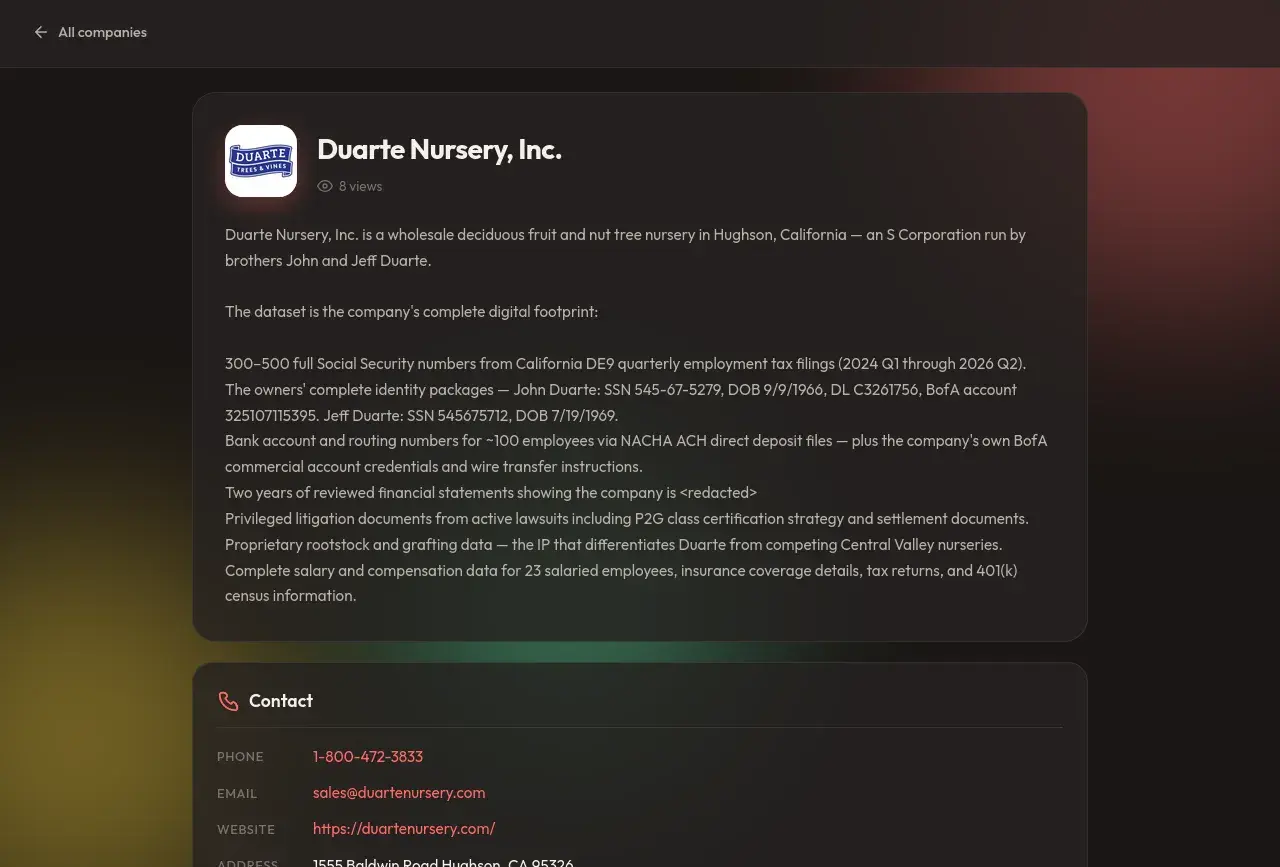
🚨New ransom group blog post!🚨

Group name: aurora
Post title: Duarte Nursery, Inc.
Location: 🇺🇸 US
Sector: Agriculture & Food
Info: https://cti.fyi/#disclosure/aurora/Duarte%20Nursery%2C%20Inc.

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original