X XFediYour place in the Fediverse
XFEDI

#devsecops

ActivityPub

Public posts with this hashtag.

Critical PHP RCEs Turn Patch Timing Into an Application Security Test

Two critical PHP RCEs reportedly turn emergency patching into an application security evidence test.

https://securstack.io/blog/en/critical-php-rces-turn-patch-timing-into-an-application-security-test

#applicationsecurity #phpsecurity #vulnerabilitymanagement #devsecops #sca

securstack.ioCritical PHP RCEs Turn Patch Timing Into an Application Security TestTwo critical PHP RCEs reportedly turn emergency patching into an application security evidence test.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Modern connected-device regulations like the EU CRA, FDA guidance, and IEC 62443 all rest on a single baseline: knowing exactly what is inside your product. When supplier manifests are incomplete, binary analysis fills the gap. 🧩

Read Finite State's technical guide to learn how to generate binary-derived component inventories that stand up to regulatory scrutiny.

Big thanks to Finite State for supporting AppSec Village as a Silver Sponsor; we appreciate you!

Download the guide: https://finitestate.io/resources/firmware-binary-analysis-guide

#AppSec #CyberResilience #SupplyChainSecurity #DevSecOps

Media attachment
finitestate.ioFirmware Binary Analysis: The Complete GuideA source manifest lists what a developer meant to build. The shipped image is what you have to defend. A practitioner's guide to reading firmware from the binary up.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Brigade 0.30.0 is out. It's my open source tool for tracking and verifying work across coding agents, and as of this release the agents can message each other through one hub.

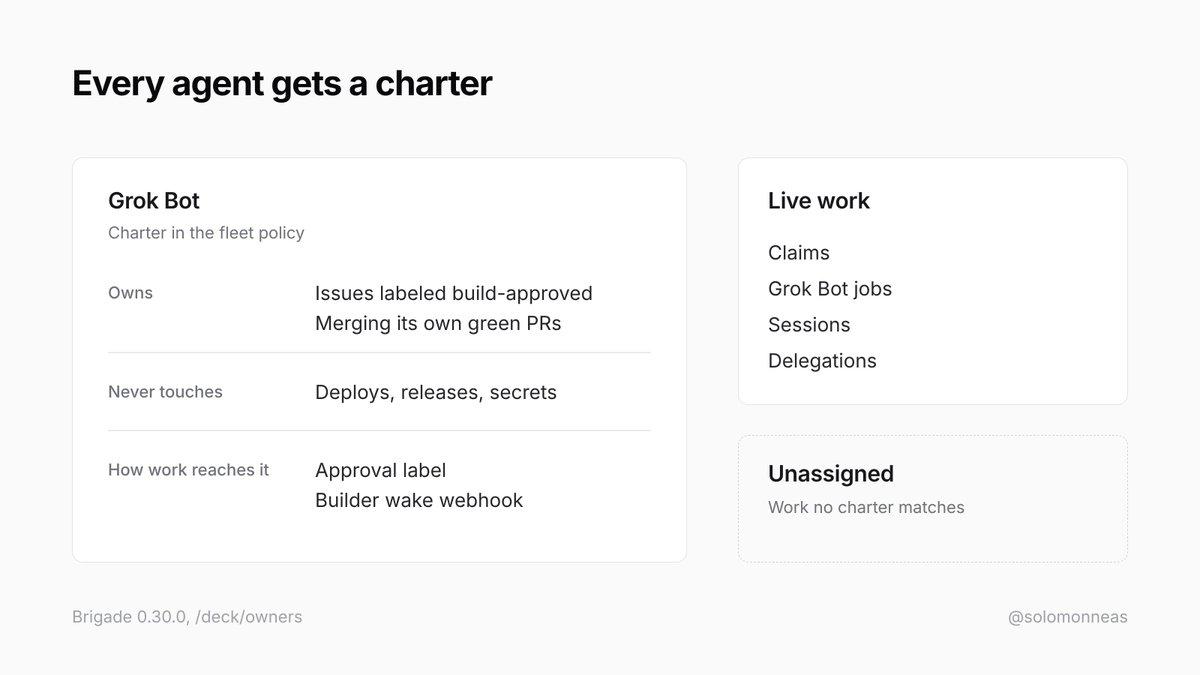
If you let agents touch real repos: each one can now get a charter saying what it owns, what it must never touch, and how work reaches it. An owners page shows each charter beside its live claims and sessions. Work no charter matches lands in Unassigned.

https://git.brigade.tools

#OpenSource #AIAgents #DevSecOps

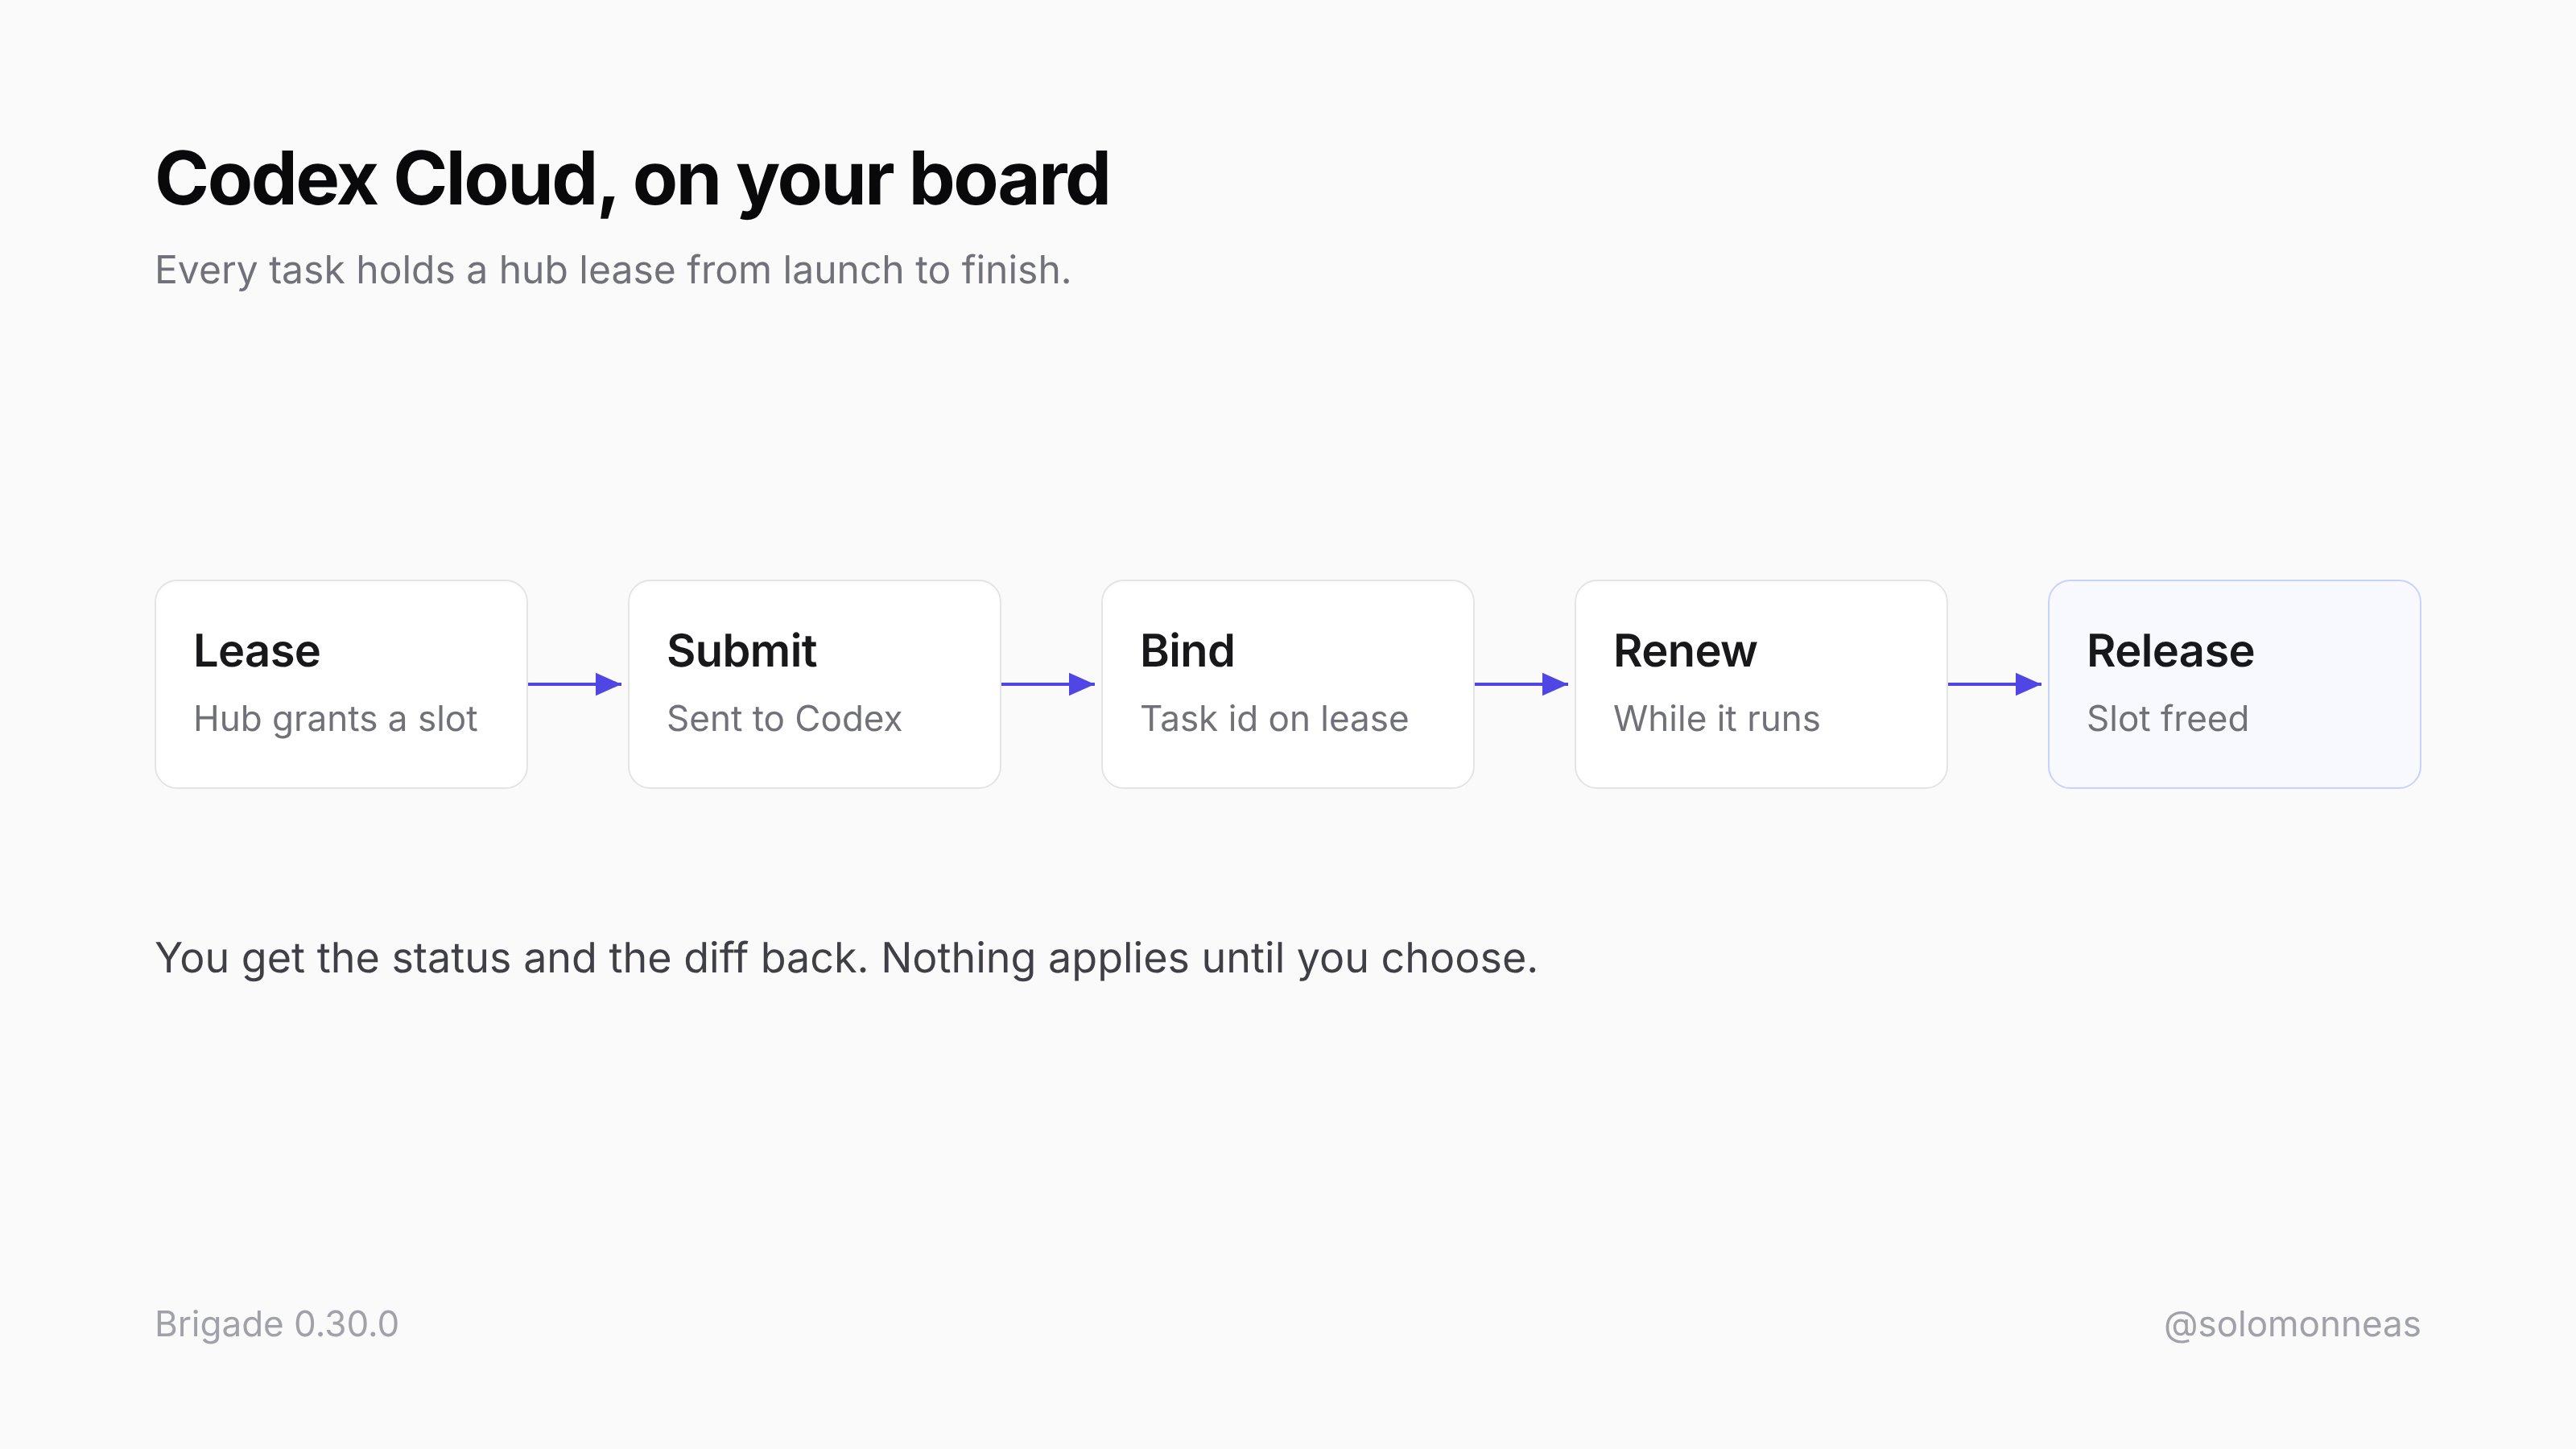
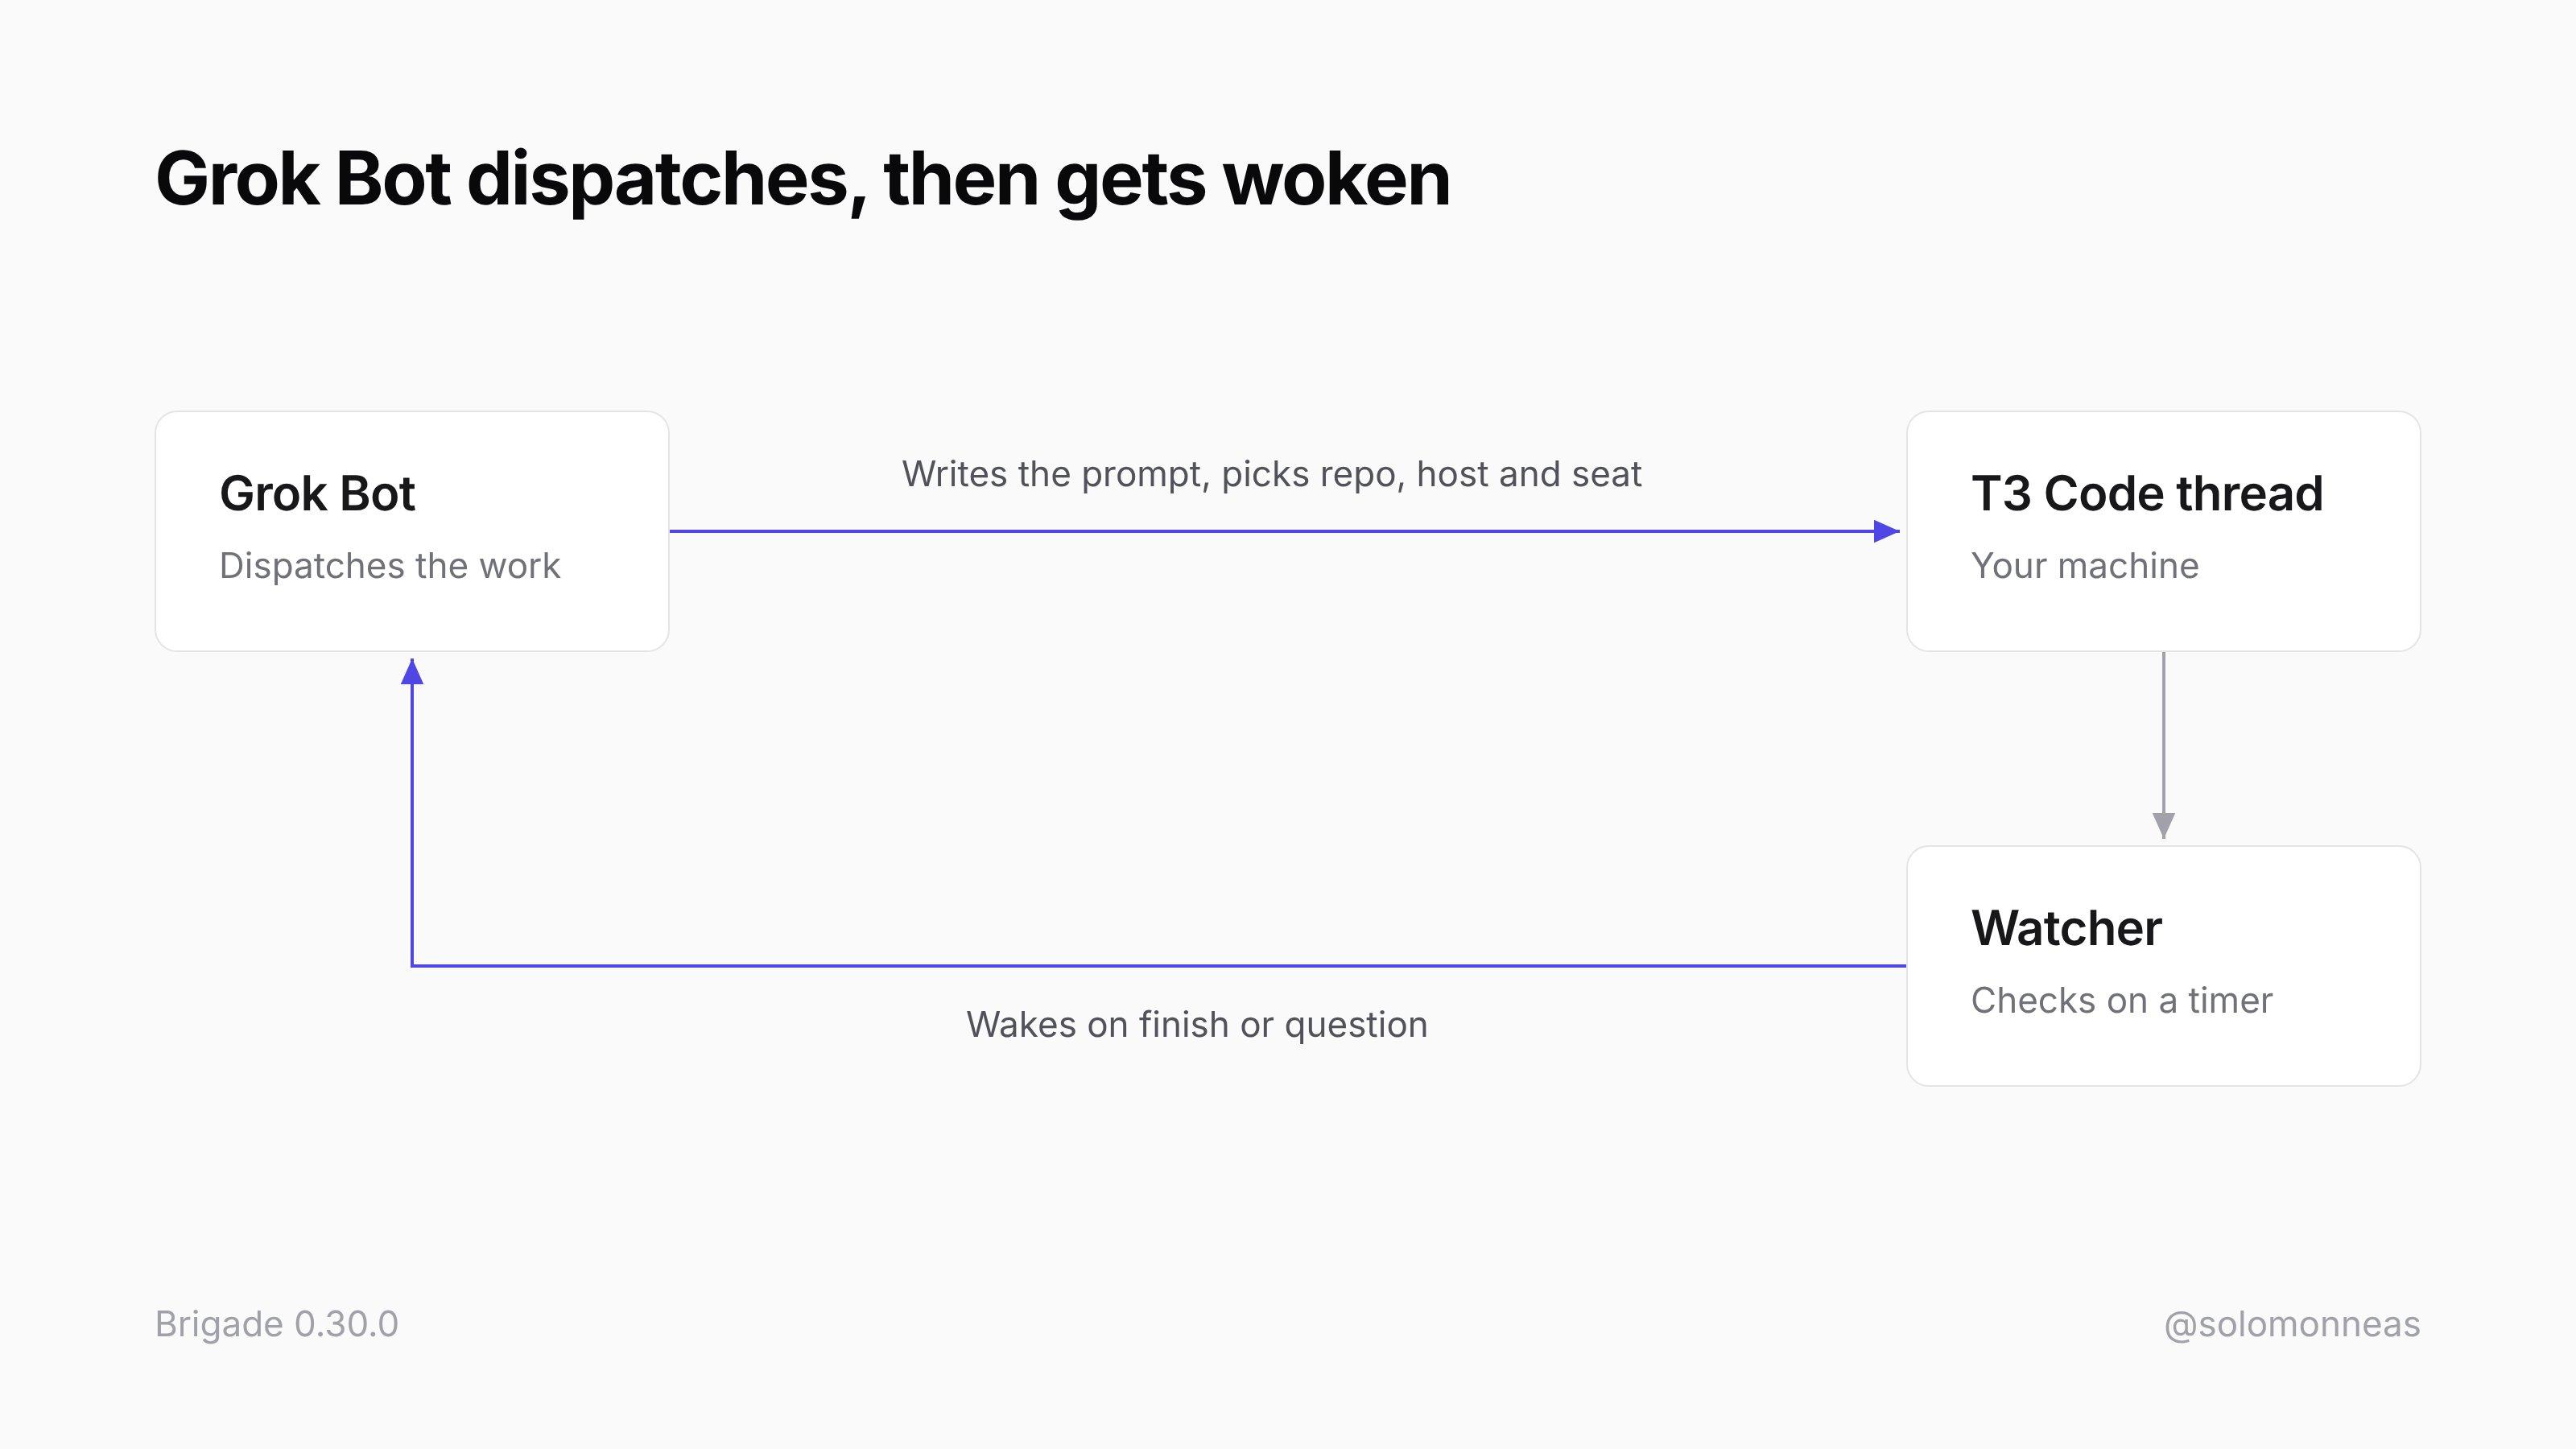
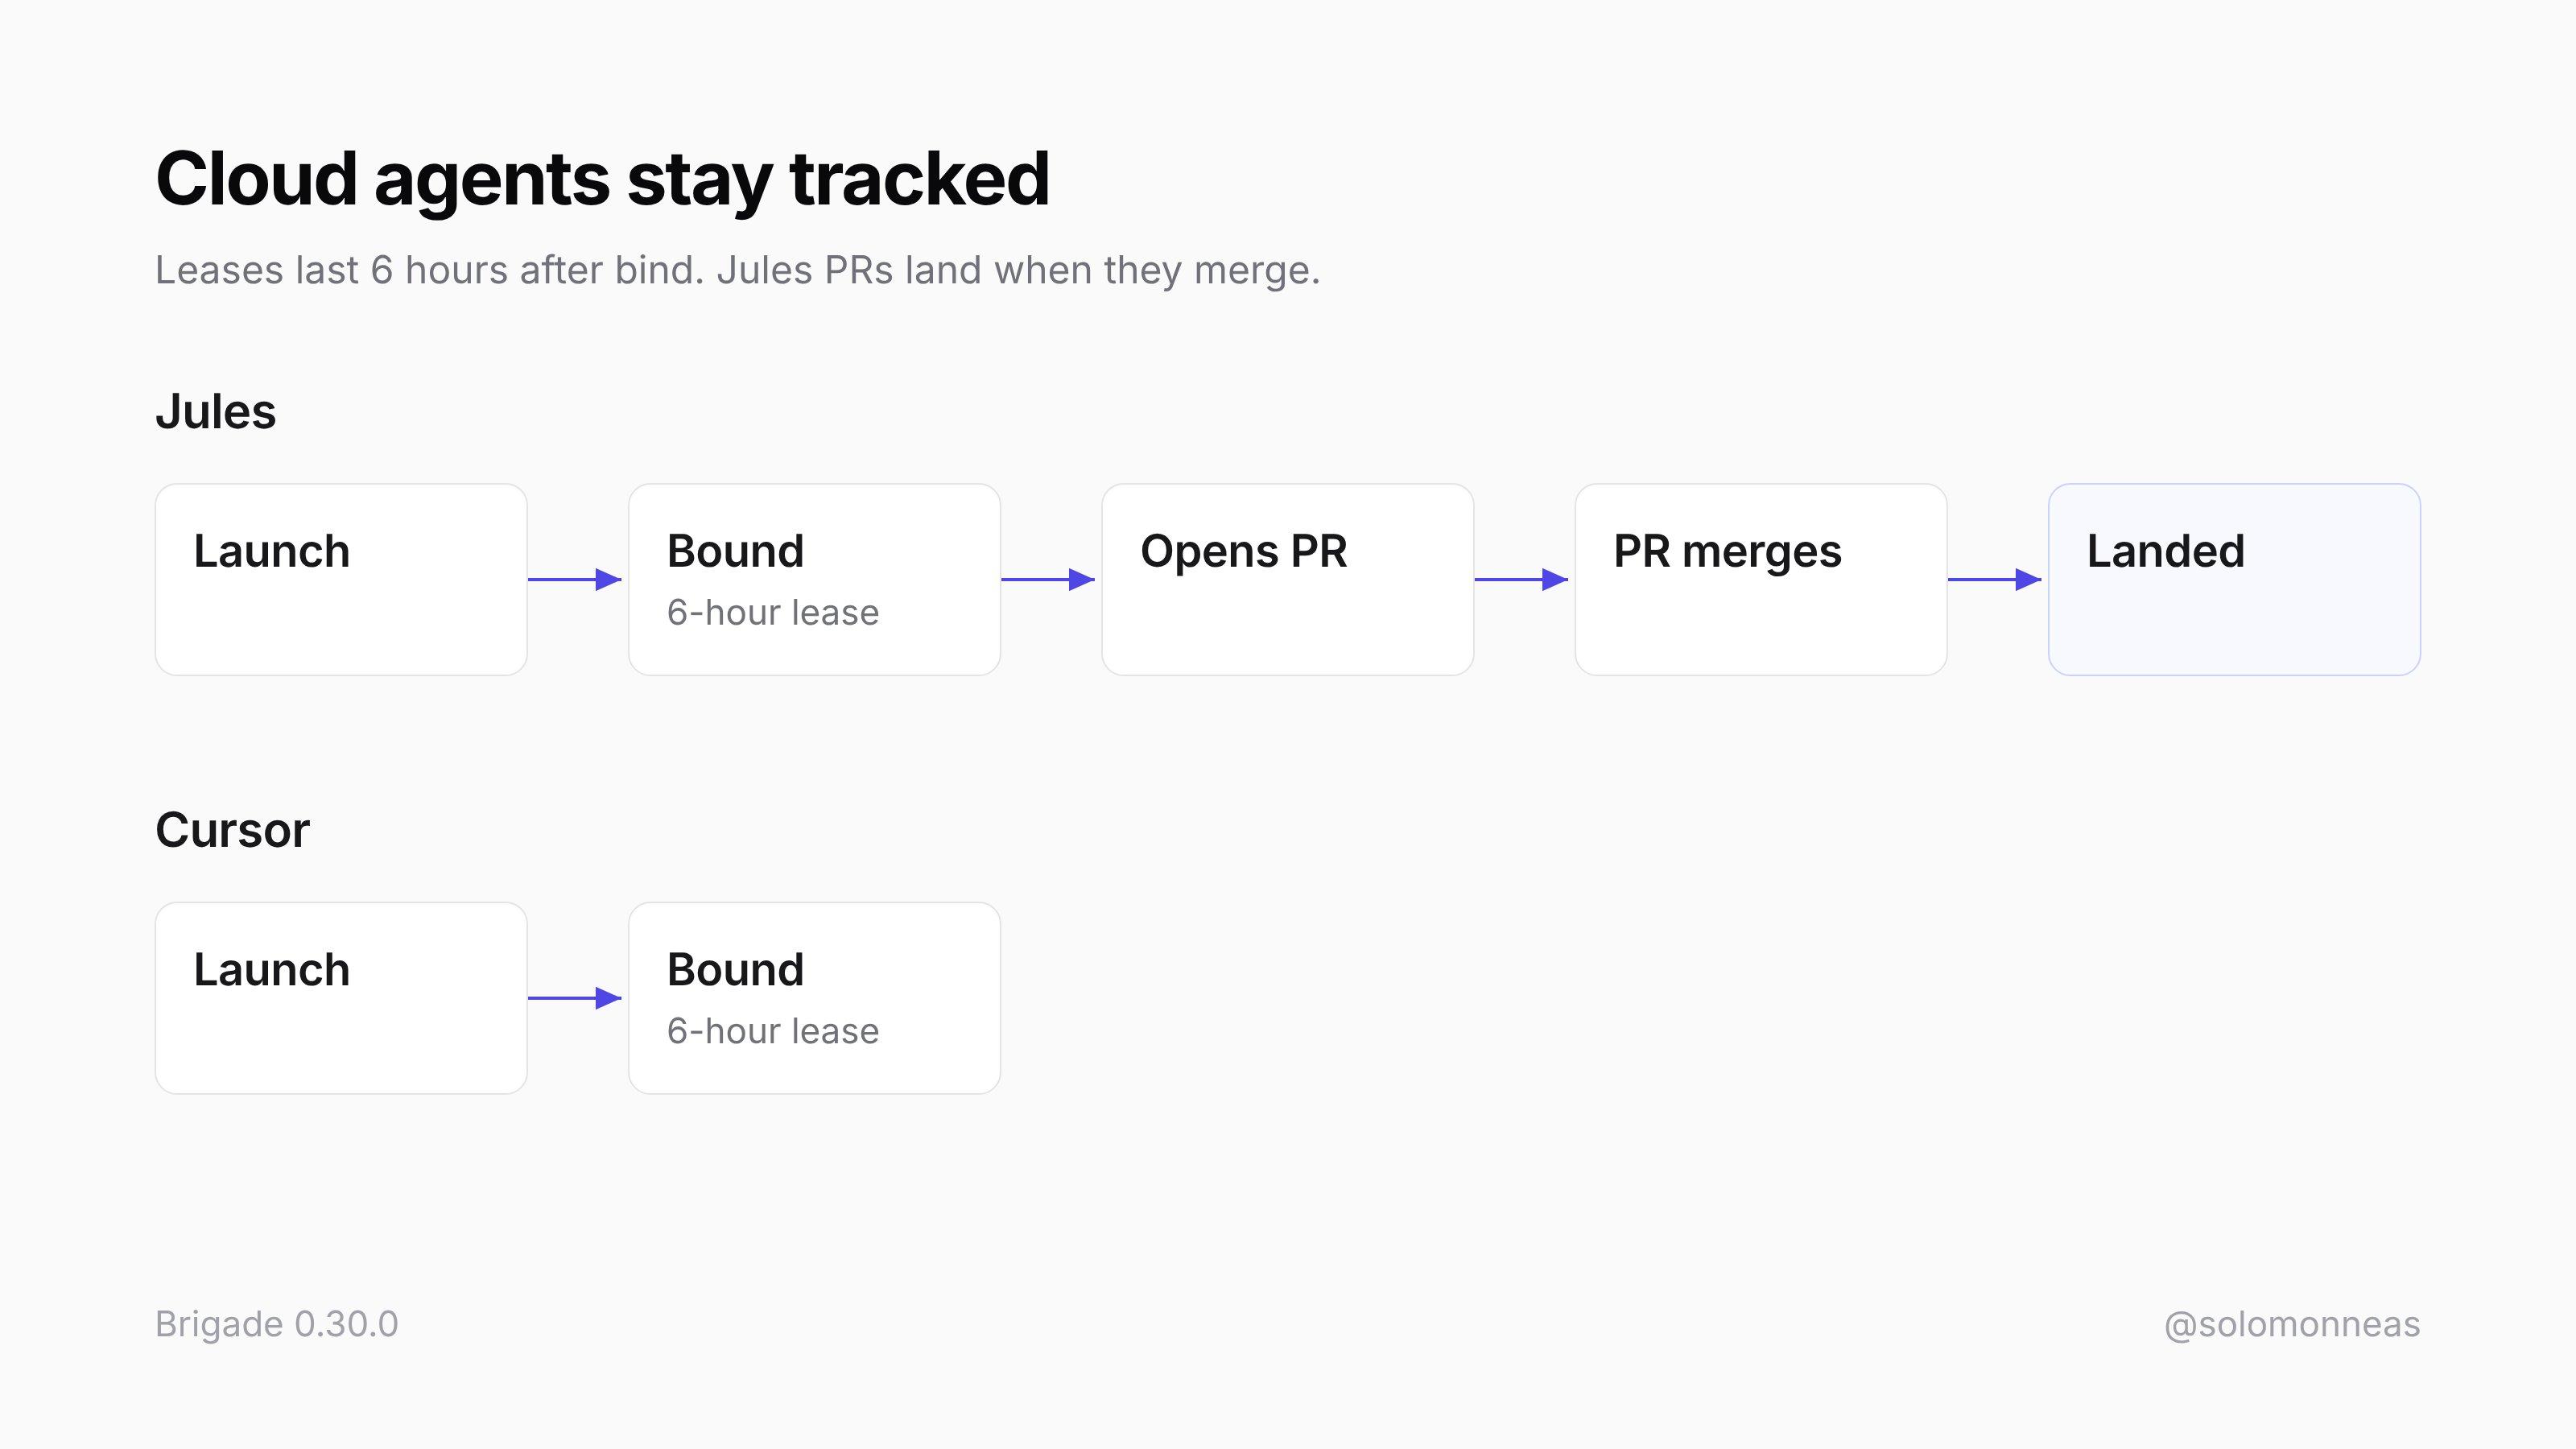
Slide titled "Every agent gets a charter." A card for Grok Bot, labeled as a charter in the fleet policy. Owns: issues labeled build-approved, and merging its own green PRs. Never touches: deploys, releases, secrets. How work reaches it: an approval label and a builder wake webhook. Beside it, a Live work card lists claims, Grok Bot jobs, sessions, and delegations. A dashed card below reads "Unassigned: work no charter matches." Footer: Brigade 0.30.0, /deck/owners.Slide titled "Codex Cloud, on your board," subtitled "Every task holds a hub lease from launch to finish." Five steps left to right: Lease (hub grants a slot), Submit (sent to Codex), Bind (task id on lease), Renew (while it runs), Release (slot freed). Below: "You get the status and the diff back. Nothing applies until you choose."Diagram titled "Grok Bot dispatches, then gets woken." An arrow from Grok Bot (dispatches the work) to a T3 Code thread on your machine is labeled "Writes the prompt, picks repo, host and seat." The thread feeds a Watcher that checks on a timer, and an arrow from the Watcher back to Grok Bot is labeled "Wakes on finish or question."Slide titled "Cloud agents stay tracked," subtitled "Leases last 6 hours after bind. Jules PRs land when they merge." Jules row: Launch, Bound with a 6-hour lease, Opens PR, PR merges, Landed. Cursor row: Launch, Bound with a 6-hour lease.
GitHubGitHub - escoffier-labs/brigade: Track work, verify results, carry memory, and sync tools across coding agents. Local files, no daemon.Track work, verify results, carry memory, and sync tools across coding agents. Local files, no daemon. - escoffier-labs/brigade
↩ Reply ♡ 0 · ↻ 0 ↗ Original