X XFediYour place in the Fediverse
XFEDI

#intelligence

ActivityPub

Public posts with this hashtag.

IC Brief Morning — 2026-10-24

Iranian and Russian intelligence services are escalating lethal and sabotage operations against Western personnel and allied territory. Advanced Iranian assassination plots against U.S. personnel drove Middle East embassy drawdowns; the State Department will likely order reductions at additional posts by early November. High confidence reflects an authenticated DNI memo. Putin personally ordered sabotage against NATO, a shift from earlier GRU-level reporting; a NATO government is unlikely to publicly attribute a new attack to Russian state services by late November. Russia will very likely expel at least one Austrian diplomat within 30 days.

Taiwanese prosecutors will very likely announce criminal charges tied to Chinese election interference before the November 28 vote, as Beijing's traceable inducements give investigators actionable cases. Moderate confidence rests on the NSB director's statements and a related indictment. A confirmed breach through the PHP2Shell flaws will likely surface by November 7; operators on end-of-life PHP have no patch path.

Federal grand juries will likely indict CIA contractor Brinksman on Espionage Act charges by late November, and will likely indict former FBI official Floris or Benavides on false-statement charges by the same date. High confidence in both reflects documentary records, though the Floris-Benavides affidavit omits quoted testimony for one allegation and was filed days before midterms.

https://icbrief.org/icbrief/

#Intelligence #OSINT #NationalSecurity

IC BriefIC BriefIranian and Russian intelligence services are escalating lethal and sabotage operations against Western personnel and allied territory. Advanced Iranian...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

IC Brief Morning — 2026-10-23

Adversary intelligence campaigns against Western elections, exercises, and defense personnel are outpacing countermeasures, as previously assessed. The intelligence community is very unlikely to publicly attribute Russia's Storm-1516 deepfake videos targeting midterm candidates by November 6, leaving campaigns reliant on outside researchers. Moderate confidence rests on lawmaker and private-sector attribution but no official agency comment. PLA operatives intercepted communications at US and South Korean bases 13 times during bilateral exercises, and Taiwan indicted four for leaking military secrets to Chinese contacts.

Western sanctions targeting A7's Sadovod brokers and offshore intermediaries are unlikely by late November, leaving bank de-risking as the primary disruption tool. Another US prisoner release from Russia is unlikely before late December; Hubbard's release was a discrete gesture. High confidence reflects the absence of named prisoners in Russian statements; their appearance would signal active negotiations. The Pentagon's reported sabotage and deep-cover programs lack congressional oversight.

CISA will very likely add the PHP2Shell CVEs to its Known Exploited Vulnerabilities catalog by November 6, triggering mandatory federal remediation; unsupported PHP deployments have no patch path. High confidence reflects joint CISA-NSA advisories and millions of exploitation attempts. Canada's Bill C-22 will likely receive Royal Assent by year's end. Low confidence reflects thin Senate sourcing; passage would force encrypted-communications providers into exit decisions.

https://icbrief.org/icbrief/

#Intelligence #OSINT #NationalSecurity

IC BriefIC BriefIranian and Russian intelligence services are escalating lethal and sabotage operations against Western personnel and allied territory. Advanced Iranian...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

https://medwinpublishers.com/article/OAJCIJ/10.23880/oajcij-16000135/full

https://doi.org/10.23880/oajcij-16000135

Research paper has already been published and is already live.

Medwin Publishers Thanks for helping me publish my article.

#Research #Nihilistic #Extremism #Intelligence #OSINT #CounterTerrorism #Terrorism #CyberSec #CyberSecurity #InfoSec #InformationSecurity #OpenSourceIntelligence #Investigation

Media attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original

IC Brief Morning — 2026-10-22

Adversary operations against Western targets are intensifying while US election security mechanisms remain degraded. UK authorities will likely charge at least one suspect in the IRGC Fairford plot by November 12, reversing the previous edition's judgment; Germany's conviction of two Iranian operatives reinforces European counterpressure. Low confidence reflects thin evidence: police recovered petrol but no explosives, and rearrests may reflect political pressure. ODNI is very unlikely to deliver the statutory 30-day election threat assessment by November 3, leaving state officials without a federal threat picture. Moderate confidence rests on missed deadlines and agency non-response.

Beijing is sustaining military and cyber pressure on allies. Japan's Joint Staff will likely report additional scrambles against Chinese drones near the southwest islands before Keen Sword 27 ends on October 29. High confidence reflects five publicly announced drone flights this fiscal year. Taiwan faces 2.6 million daily cyberattacks ahead of November 28 elections, targeting government and defense networks.

Russia is recruiting disposable agents through Telegram for kinetic targeting and defense-sector espionage. Denmark charged two young Ukrainian migrants with photographing a drone-detection firm; a third suspect is unlikely to be arrested by November 12, suggesting the handler operates abroad. A third arrest would signal a domestic network. The recruitment model will persist near allied defense suppliers.

https://icbrief.org/icbrief/

#Intelligence #OSINT #NationalSecurity

IC BriefIC BriefIranian and Russian intelligence services are escalating lethal and sabotage operations against Western personnel and allied territory. Advanced Iranian...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

IC Brief Morning — 2026-10-21

Foreign influence operations targeting the midterms face no federal counter. Federal attribution to a named state actor is unlikely by November 3, and platform removal of Matryoshka content is unlikely by that date, after the FBI disbanded its Foreign Influence Task Force, ODNI dissolved the Foreign Malign Influence Center, and State closed its counter-disinformation office. Moderate confidence rests on consistent reporting of those closures. A platform or agency takedown before Election Day would alter this assessment.

Russian and Iranian operations against NATO targets span sabotage, espionage, and cyber intrusion. Lithuanian authorities will likely detain a Starlink arson suspect by November 21, the third such attack on Ukrainian communications infrastructure. UK prosecutors are unlikely to charge any RAF Fairford suspect by November 21; espionage re-arrests signal prolonged evidence-building. Swallowtail's sustained access to a NATO shipbuilder, with an unrecovered loader payload, leaves the full GRU compromise unknown.

SafePay will very likely claim a new US critical infrastructure victim within 30 days. High confidence reflects 600 documented victims since August 2024. ProPublica's account that FBI purges killed the Navatek bribery case will likely prompt a congressional inquiry or IG referral within 30 days. Beijing is unlikely to respond to the PAIPA sanctions with a specific countermeasure by November 20.

https://icbrief.org/icbrief/

#Intelligence #OSINT #NationalSecurity

IC BriefIC BriefIranian and Russian intelligence services are escalating lethal and sabotage operations against Western personnel and allied territory. Advanced Iranian...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

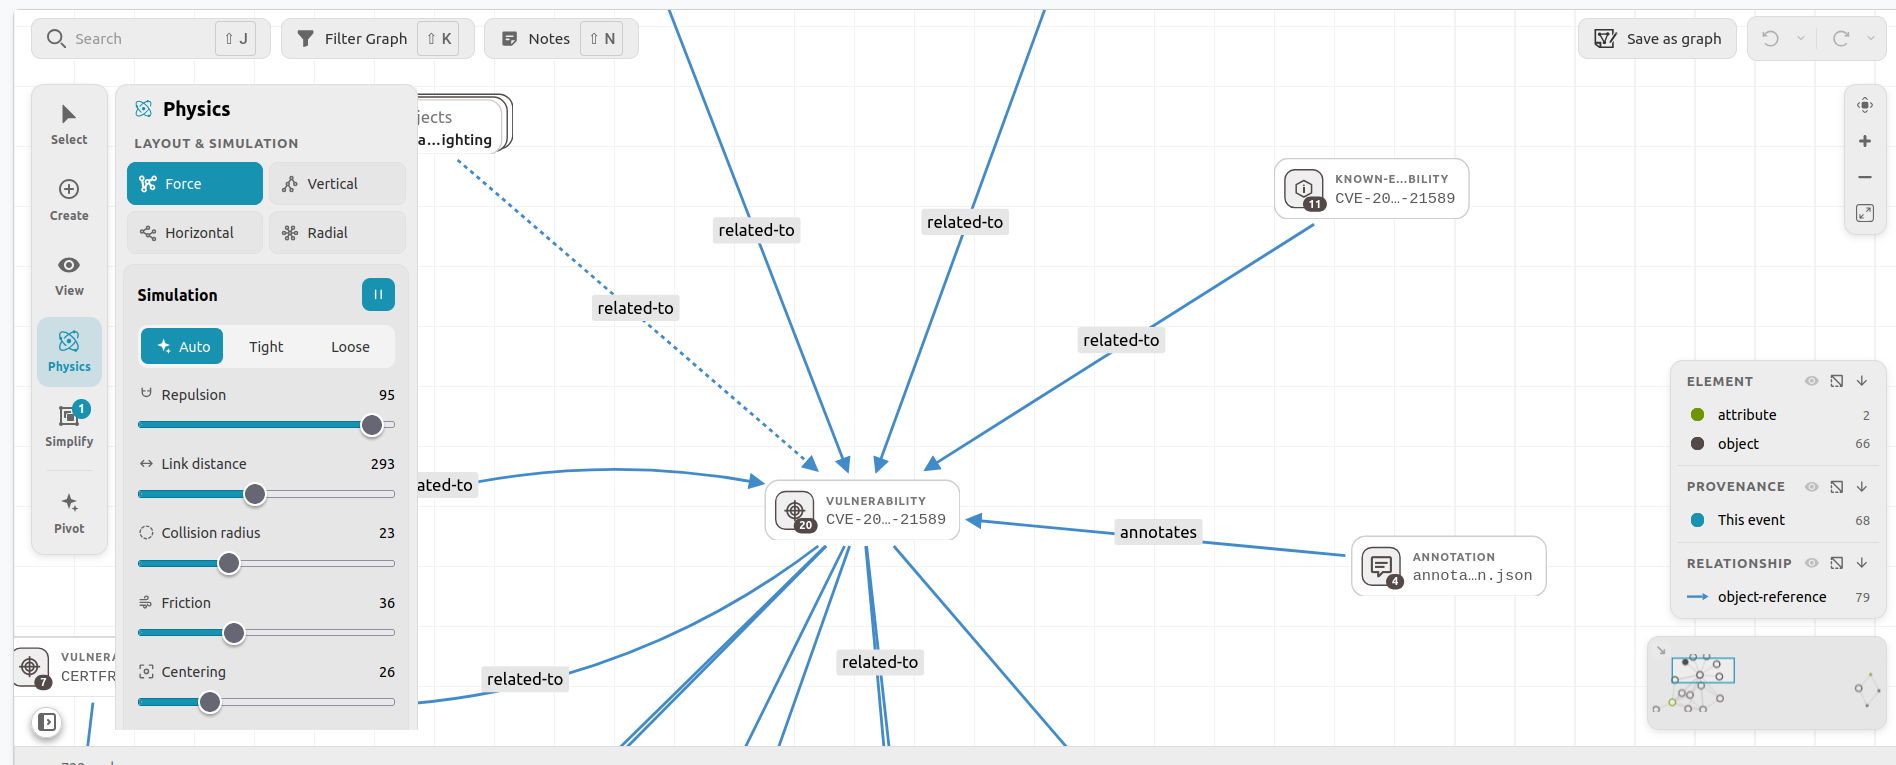
MISP Modules v3.0.13 is a substantial release, bringing a new wave of OSINT and threat intelligence enrichment capabilities, new ways to export indicators into operational security tools, and new workflows for publishing IOCs directly to security platforms.

@misp

🔗 https://github.com/MISP/misp-modules/releases/tag/v3.1.0

#misp #cti #threatintel #intelligence #cybersecurity #osint

vulnerability-lookup expansion modules in MISP 3.0
GitHubRelease MISP Modules v3.1.0 - More pivots, more integrations, more actionable intelligence · MISP/misp-modulesMISP Modules v3.0.13 is a substantial release, bringing a new wave of OSINT and threat intelligence enrichment capabilities, new ways to export indicators into operational security tools, and new w...
↩ Reply ♡ 0 · ↻ 0 ↗ Original