X XFediYour place in the Fediverse
XFEDI

#offensivesecurity

ActivityPub

Public posts with this hashtag.

🚨 If you run PHP (like most of the internet does), this one can’t wait: #PHP2Shell = 2 critical RCE flaws in PHP core leaked before the patch, with live attacks already reported.

Because CVE-2026-109618 & CVE-2026-109619 sit in PHP itself, every app on a vulnerable PHP version is exposed, no matter what runs on top.

That’s why we’re building detection in our Network Scanner + an exploit module in Sniper as you’re reading this. Stay tuned for the launch announcement!

What to do now:

Inventory every PHP install, including control panels, vendor appliances, and Windows software that bundles its own php-cgi.exe
Patch as soon as PHP’s release is out, then restart PHP-FPM or your web server
On PHP 8.1 or older? No fix is coming. Upgrade, or take those systems off the internet
Alert on PHP processes spawning shells, interpreters, or download tools

#OffensiveSecurity #Pentesting #VulnerabilityManagement #EthicalHacking
Media attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Three government programs already. Specter brought proof to every one.

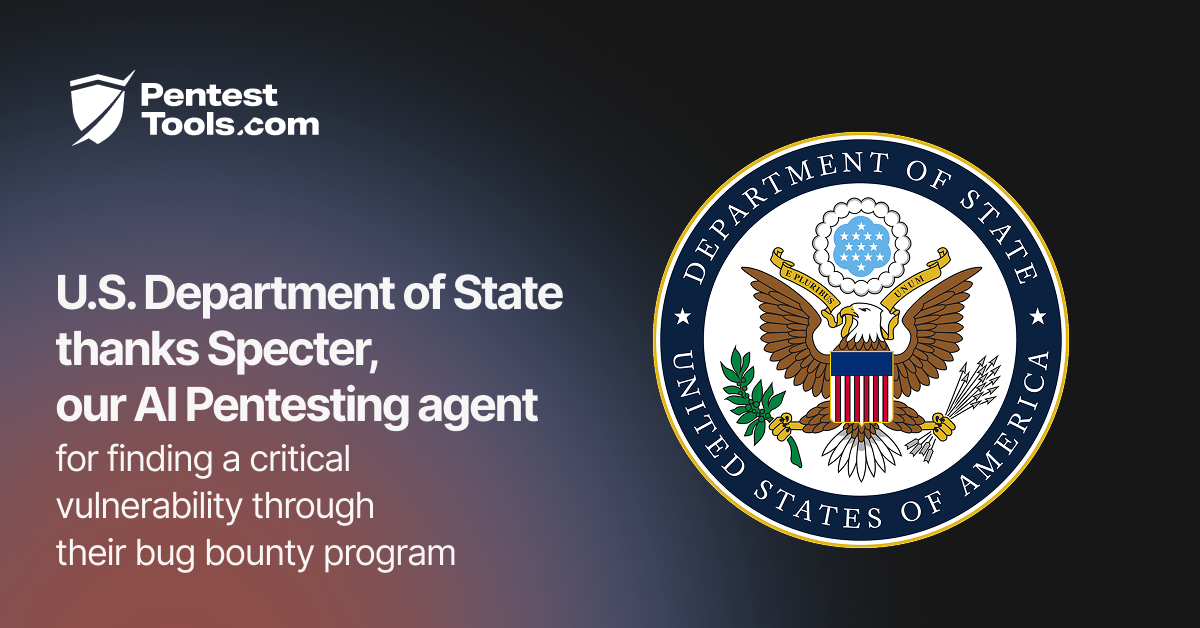
The US Department of State just acknowledged a vulnerability our autonomous pentesting engine reported through its HackerOne disclosure program, following the US Department of Defense and the UK Ministry of Defence.

A maybe doesn’t get fixed. Every finding needs evidence a team can reproduce.

How it works: https://pentest-tools.com/features/ai-pentests
All acknowledgments: https://hackerone.com/pentesttools_specter?type=user

#infosec #offensivesecurity

Media attachment
Pentest-Tools.comAI Pentests - autonomous web application penetration testingSee how AI Pentests autonomously investigate web applications, validate exploitable vulnerabilities, and generate evidence-backed penetration testing reports.
↩ Reply ♡ 0 · ↻ 0 ↗ Original