What detection format would you like to have if you got detections online? (e.g. for a recent attack/vuln wave like php2shell)
#dfir #infosec #cybersecurity #askfedi #incidentresponse #osint #threatintel #threatintelligence #opensourceintelligence
Public posts with this hashtag.
What detection format would you like to have if you got detections online? (e.g. for a recent attack/vuln wave like php2shell)
#dfir #infosec #cybersecurity #askfedi #incidentresponse #osint #threatintel #threatintelligence #opensourceintelligence
----------------
🛠️ Tool: claude-osint ships external recon tradecraft as Claude skills
===================
What it is. claude-osint, built by Sachin Sharma (GenAI Security Research), is a library of eight SKILL.md files for the Claude skills system. Each file primes Claude with a written methodology covering one slice of external recon, aimed at authorized red-team and bug-bounty engagements. The bulk is structured markdown, about 10,000 lines total, plus two small Python scripts.
Core skills.
• osint-methodology (515 lines): strategy and discipline; asset-graph management, a severity rubric, time budgeting, identity-fabric mapping, deliverable templates.
• offensive-osint (4,555 lines): the tactical layer; probe paths, regexes, payloads, scoring rules, curl one-liners, plus 80 secret patterns, 80+ dorks, 9 read-only credential validators, and 27 attack-path templates.
Org-scale skills. Six additional skills, per the README:
• org-attack-surface: maps a legal entity to its owned footprint using GLEIF org-trees, org-first RIR netblock recall, and an ASN hyperscaler-scope guard; discovery only.
• email-domain-security: composite spoofability verdict separating envelope from header-From; explicit note that SPF -all alone does not make a domain spoof-proof; SPF supply-chain analysis.
• exposure-risk-quantification: FAIR-based 0-100 and A-F score, dollar-denominated loss model, board one-pager, and honesty caps on ownership/proof claims.
• continuous-exposure-monitoring: rescan/diff loop, CTI and ransomware chatter checks, finding-lifecycle false-positive discipline, durable alert outbox.
• cloud-saas-exposure: ownership-gated bucket severity, offline AWS account-ID decoding, dependency-confusion confirmation, K8s/CI fingerprinting.
• identity-provider-recon: tenant and federation mapping, pre-auth user-enumeration oracle, name×pattern login synthesis, with a "hard enumeration boundary".
Scripts. secret_scan.py is a stdlib-only 80-pattern secret scanner; h1_reference.py acts as a reference agent over disclosed HackerOne reports.
Use cases. The recon phase of authorized engagements: entity-to-footprint mapping, per-domain spoofability triage, and exposure scoring for client or board reporting. The files also read as standalone reference documents.
Limitations. The evaluation figures (56/56 pass on a 56-prompt self-evaluation, zero fabrications, ~85-90% practitioner coverage) are self-reported by the author and not independently verified. Structurally these are prompt files, not enforcement code: scope controls such as the enumeration boundary live in the instructions themselves, so scope discipline depends on the operator. The README bills the package as "god-mode" recon; the substance is closer to a well-ordered methodology library, which is the more useful framing anyway.
References. Repo: claude-osint on GitHub, author profile under Sachin Sharma; Claude skills documentation.
🔹 tool #OSINT #ClaudeSkills #RedTeam #BugBounty
Next speaker for #OSINT Collective Oct'26: Syed Hafidz, "Automate the Boring Stuff, Not the Analysis" (15:00 GMT, Sat 31 Oct).
Build a pipeline that collects, normalises, enriches, deduplicates and exports data from several sources; decide what to automate and what stays with an analyst; ship findings with provenance, confidence levels, and verification flags.
Free and online: https://osintverse.com/collective/oct26
IC Brief Morning — 2026-10-23
Adversary intelligence campaigns against Western elections, exercises, and defense personnel are outpacing countermeasures, as previously assessed. The intelligence community is very unlikely to publicly attribute Russia's Storm-1516 deepfake videos targeting midterm candidates by November 6, leaving campaigns reliant on outside researchers. Moderate confidence rests on lawmaker and private-sector attribution but no official agency comment. PLA operatives intercepted communications at US and South Korean bases 13 times during bilateral exercises, and Taiwan indicted four for leaking military secrets to Chinese contacts.
Western sanctions targeting A7's Sadovod brokers and offshore intermediaries are unlikely by late November, leaving bank de-risking as the primary disruption tool. Another US prisoner release from Russia is unlikely before late December; Hubbard's release was a discrete gesture. High confidence reflects the absence of named prisoners in Russian statements; their appearance would signal active negotiations. The Pentagon's reported sabotage and deep-cover programs lack congressional oversight.
CISA will very likely add the PHP2Shell CVEs to its Known Exploited Vulnerabilities catalog by November 6, triggering mandatory federal remediation; unsupported PHP deployments have no patch path. High confidence reflects joint CISA-NSA advisories and millions of exploitation attempts. Canada's Bill C-22 will likely receive Royal Assent by year's end. Low confidence reflects thin Senate sourcing; passage would force encrypted-communications providers into exit decisions.
 IC BriefIC BriefAdversary intelligence campaigns against Western elections, exercises, and defense personnel are outpacing countermeasures, as previously assessed. The...
🔍 Search Party Sponsor: @epieos
We are proud to have #Epieos supporting the Trace Labs Global OSINT Search Party CTF On October 24th at 12PM EDT/ 4PM UTC!
Epieos turns one email address or phone number into a map of digital footprints across 140+ online platforms - quietly without alerting the target. It's a legit workhorse for investigators - The kind of tool that turns one lead into ten.
Thank you to the Epieos team for powering the people who bring missing people home. 💙
🌐 To learn more, visit: https://epieos.com/
https://medwinpublishers.com/article/OAJCIJ/10.23880/oajcij-16000135/full
https://doi.org/10.23880/oajcij-16000135
Research paper has already been published and is already live.
Medwin Publishers Thanks for helping me publish my article.
#Research #Nihilistic #Extremism #Intelligence #OSINT #CounterTerrorism #Terrorism #CyberSec #CyberSecurity #InfoSec #InformationSecurity #OpenSourceIntelligence #Investigation

IC Brief Morning — 2026-10-22
Adversary operations against Western targets are intensifying while US election security mechanisms remain degraded. UK authorities will likely charge at least one suspect in the IRGC Fairford plot by November 12, reversing the previous edition's judgment; Germany's conviction of two Iranian operatives reinforces European counterpressure. Low confidence reflects thin evidence: police recovered petrol but no explosives, and rearrests may reflect political pressure. ODNI is very unlikely to deliver the statutory 30-day election threat assessment by November 3, leaving state officials without a federal threat picture. Moderate confidence rests on missed deadlines and agency non-response.
Beijing is sustaining military and cyber pressure on allies. Japan's Joint Staff will likely report additional scrambles against Chinese drones near the southwest islands before Keen Sword 27 ends on October 29. High confidence reflects five publicly announced drone flights this fiscal year. Taiwan faces 2.6 million daily cyberattacks ahead of November 28 elections, targeting government and defense networks.
Russia is recruiting disposable agents through Telegram for kinetic targeting and defense-sector espionage. Denmark charged two young Ukrainian migrants with photographing a drone-detection firm; a third suspect is unlikely to be arrested by November 12, suggesting the handler operates abroad. A third arrest would signal a domestic network. The recruitment model will persist near allied defense suppliers.
IC BriefIC BriefAdversary intelligence campaigns against Western elections, exercises, and defense personnel are outpacing countermeasures, as previously assessed. The...
🔍 Search Party Sponsor: SockPuppet!
🌏 Thank you to #SockPuppet for supporting the Trace Labs Global OSINT Search Party CTF on October 24th at 12pm EDT/ 4pm UTC!
Their alias platform gives investigators secure, isolated environments with real geolocated mobile connections - purpose built infrastructure for running online research personas safely.
They have also provided access to their new platform for coaches to use during the CTF! Coaches will have access to ready-to-use accounts on SockPuppets new Software: Scout. 👏
Thank you to the SockPuppet team for equipping the people behind the mission. 💙
To learn more, visit: https://www.sockpuppet.io/
 SockPuppetSimplify OSINT: Digital Identities on Demand | SockPuppetWith our comprehensive digital infrastructure, you can deploy fully operational sockpuppets quickly and securely, all from a single platform.
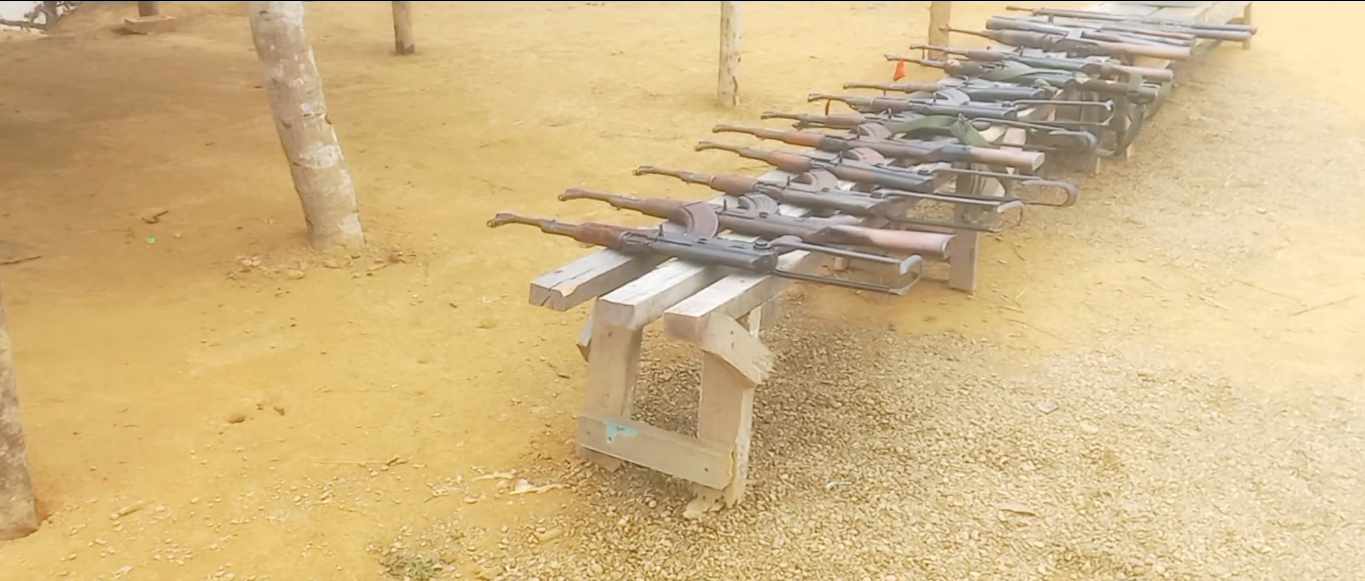
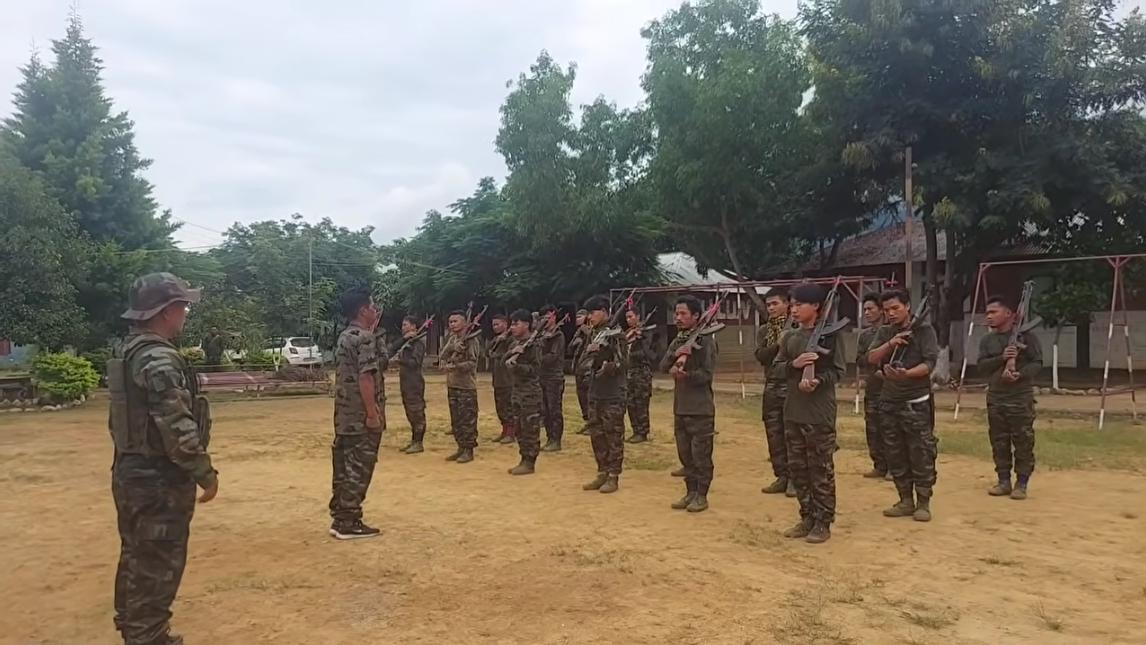
A survey of long term pattern of violations of ceasefire agreement by the Kuki National Army (KNA).
For context, the KNA (India faction) is under ceasefire with the Indian Government. As such, they are prohibited from holding firearms de jure. Despite this, numerous violations can be seen in the agreement across 2 camps.
Eurovision News Spotlight | Fact-Checking & OSINT Network
https://spotlight.ebu.ch/
#factchecking #osint
 spotlight.ebu.chEurovision News Spotlight | Fact-Checking & OSINT Network | SubstackEurovision News Spotlight is a collaborative fact-checking and open-source intelligence (OSINT) network created by the European Broadcasting Union (EBU) in collaboration with public service media members. Click to read Eurovision News Spotlight | Fact-Checking & OSINT Network, a Substack publication.
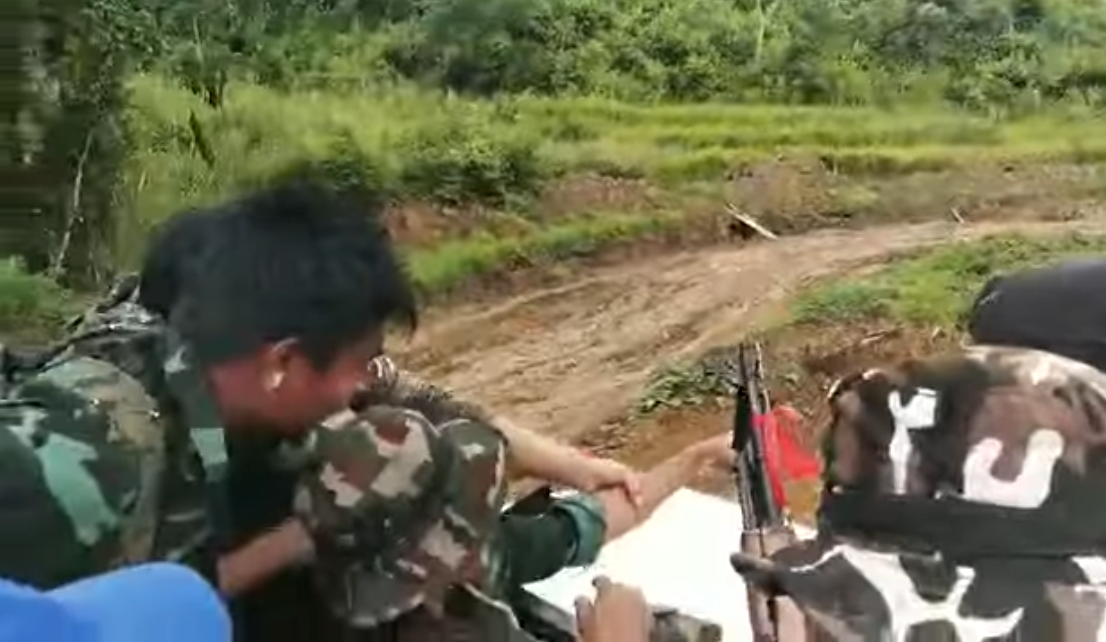
https://manipurosint.mataroa.blog/blog/battalions-kna-likely-alignment/
A survey of the correlation between the usage of certain insignia by the Kuki National Army and militants involved in the recent attacks on Khamenlok in Manipur.
IC Brief Morning — 2026-10-21
Foreign influence operations targeting the midterms face no federal counter. Federal attribution to a named state actor is unlikely by November 3, and platform removal of Matryoshka content is unlikely by that date, after the FBI disbanded its Foreign Influence Task Force, ODNI dissolved the Foreign Malign Influence Center, and State closed its counter-disinformation office. Moderate confidence rests on consistent reporting of those closures. A platform or agency takedown before Election Day would alter this assessment.
Russian and Iranian operations against NATO targets span sabotage, espionage, and cyber intrusion. Lithuanian authorities will likely detain a Starlink arson suspect by November 21, the third such attack on Ukrainian communications infrastructure. UK prosecutors are unlikely to charge any RAF Fairford suspect by November 21; espionage re-arrests signal prolonged evidence-building. Swallowtail's sustained access to a NATO shipbuilder, with an unrecovered loader payload, leaves the full GRU compromise unknown.
SafePay will very likely claim a new US critical infrastructure victim within 30 days. High confidence reflects 600 documented victims since August 2024. ProPublica's account that FBI purges killed the Navatek bribery case will likely prompt a congressional inquiry or IG referral within 30 days. Beijing is unlikely to respond to the PAIPA sanctions with a specific countermeasure by November 20.
IC BriefIC BriefAdversary intelligence campaigns against Western elections, exercises, and defense personnel are outpacing countermeasures, as previously assessed. The...
----------------
🎯 AI
===================
NorForge published an investigation into publicly exposed control panels of AI-driven penetration-testing systems, with Cairn as the central case. The value here is documentation of actual offensive use of autonomous agent stacks, not a threat model on a slide.
Context
In September 2026, Gambit Security reported a criminal intrusion campaign against online marketplaces. The recovered attacker staging server showed AI harnesses in active use: Hermes, Strix, and Cairn. These tools ship with web UIs, and operators keep putting them on the open internet. Shodan and Censys queries surface hosts running various harnesses. Most require authentication. Some do not.
Findings per the source
• More than 20 exposed Cairn panels were assessed as likely associated with malicious activity. Targeting data, language, and task instructions connected several panels to the same actors.
• Panel content is unusually rich. A single open panel can disclose target identity, discovered weaknesses, account secrets, API keys, and whether a compromise already succeeded. One captured task view even showed root access to the attacker's own data drop.
• Legitimate red team operations appear in the same search results, which potentially puts their clients at risk.
• NorForge redacted extracted data aggressively and is withholding panel addresses until takedown. Treat instance-level specifics as unverified until publication.
How Cairn works
• Each task is a project with a defined origin and a predefined goal. The authors position Cairn as a state-based problem-solving engine rather than a dedicated pentest engine.
• Progress cycles through intents and facts. A fact is something an agent discovered. An intent is the next action it decided on.
• Facts go to a project-internal blackboard. Human operators can inject hints onto the same blackboard, and every worker agent reads it.
• The state graph renders visually. In the cited example, an attack against a major US online retailer converged from origin to a stated end of "GOAL MET: Webshell injected into the site."
Attack chain as described
1. Target selection: the operator feeds a target and objective in as a project.
2. Reconnaissance: agents investigate the target and post facts to the blackboard.
3. Exploitation: intents direct probing of weaknesses and break-in attempts.
4. Persistence: the sample run ended with a webshell injected into the site.
Implications, stated plainly:
• Agent-loop observability cuts both ways. The same blackboard that coordinates an attack also logs it for anyone who finds the panel.
• Anyone running agent harnesses should give the web console admin-panel treatment: authentication, network restrictions, and rotation of any keys that passed through it.
• Red teams should inventory their own deployments. Per the source, client exposure is a real risk, which is an uncomfortable finding for the industry.
Attribution remains the researchers' assessment, not confirmed actor identification. The available article text cuts off mid-section, so the full report may add detail on the legitimate operators.
🔹 Cairn #AISecurity #ThreatIntelligence #AutonomousAgents #OSINT
🔗 Source: https://norforge.com/blog/inside_cairn
 NorForgeInside Cairn: Open Windows into massive AI-Driven Cyber Operations - NorForgeNorForge research into publicly exposed Cairn AI pentesting panels: how threat actors select targets, direct autonomous agents, exploit vulnerabilities, and expose their victims' secrets in the process.
MISP Modules v3.0.13 is a substantial release, bringing a new wave of OSINT and threat intelligence enrichment capabilities, new ways to export indicators into operational security tools, and new workflows for publishing IOCs directly to security platforms.
🔍 Search Party Sponsor: @noimosinyosint
We are proud to have #Noimosiny sponsoring the Trace Labs Global OSINT Search Party CTF on October 24th!
Start with one identifier - email, phone, username - and cross reference it across public sources. That's how cases begin and it's what their platform is built for.
Thank you Noimosiny for their continued support in backing the search. 💙
🌐 Learn more: https://noimosiny.com/
 NoimosinyNoimosiny - Unmask Any Digital IdentityPowerful OSINT tools for investigators, analysts, and security professionals. Automate intelligence gathering with our comprehensive OSINT platform.