X XFediYour place in the Fediverse
XFEDI

#threatintelligence

ActivityPub

Public posts with this hashtag.

----------------

🎯 AI
===================

NorForge published an investigation into publicly exposed control panels of AI-driven penetration-testing systems, with Cairn as the central case. The value here is documentation of actual offensive use of autonomous agent stacks, not a threat model on a slide.

Context

In September 2026, Gambit Security reported a criminal intrusion campaign against online marketplaces. The recovered attacker staging server showed AI harnesses in active use: Hermes, Strix, and Cairn. These tools ship with web UIs, and operators keep putting them on the open internet. Shodan and Censys queries surface hosts running various harnesses. Most require authentication. Some do not.

Findings per the source
• More than 20 exposed Cairn panels were assessed as likely associated with malicious activity. Targeting data, language, and task instructions connected several panels to the same actors.
• Panel content is unusually rich. A single open panel can disclose target identity, discovered weaknesses, account secrets, API keys, and whether a compromise already succeeded. One captured task view even showed root access to the attacker's own data drop.
• Legitimate red team operations appear in the same search results, which potentially puts their clients at risk.
• NorForge redacted extracted data aggressively and is withholding panel addresses until takedown. Treat instance-level specifics as unverified until publication.

How Cairn works
• Each task is a project with a defined origin and a predefined goal. The authors position Cairn as a state-based problem-solving engine rather than a dedicated pentest engine.
• Progress cycles through intents and facts. A fact is something an agent discovered. An intent is the next action it decided on.
• Facts go to a project-internal blackboard. Human operators can inject hints onto the same blackboard, and every worker agent reads it.
• The state graph renders visually. In the cited example, an attack against a major US online retailer converged from origin to a stated end of "GOAL MET: Webshell injected into the site."

Attack chain as described

1. Target selection: the operator feeds a target and objective in as a project.
2. Reconnaissance: agents investigate the target and post facts to the blackboard.
3. Exploitation: intents direct probing of weaknesses and break-in attempts.
4. Persistence: the sample run ended with a webshell injected into the site.

Implications, stated plainly:
• Agent-loop observability cuts both ways. The same blackboard that coordinates an attack also logs it for anyone who finds the panel.
• Anyone running agent harnesses should give the web console admin-panel treatment: authentication, network restrictions, and rotation of any keys that passed through it.
• Red teams should inventory their own deployments. Per the source, client exposure is a real risk, which is an uncomfortable finding for the industry.

Attribution remains the researchers' assessment, not confirmed actor identification. The available article text cuts off mid-section, so the full report may add detail on the legitimate operators.

🔹 Cairn #AISecurity #ThreatIntelligence #AutonomousAgents #OSINT

🔗 Source: https://norforge.com/blog/inside_cairn

NorForgeInside Cairn: Open Windows into massive AI-Driven Cyber Operations - NorForgeNorForge research into publicly exposed Cairn AI pentesting panels: how threat actors select targets, direct autonomous agents, exploit vulnerabilities, and expose their victims' secrets in the process.

↩ Reply ♡ 0 · ↻ 0 ↗ Original

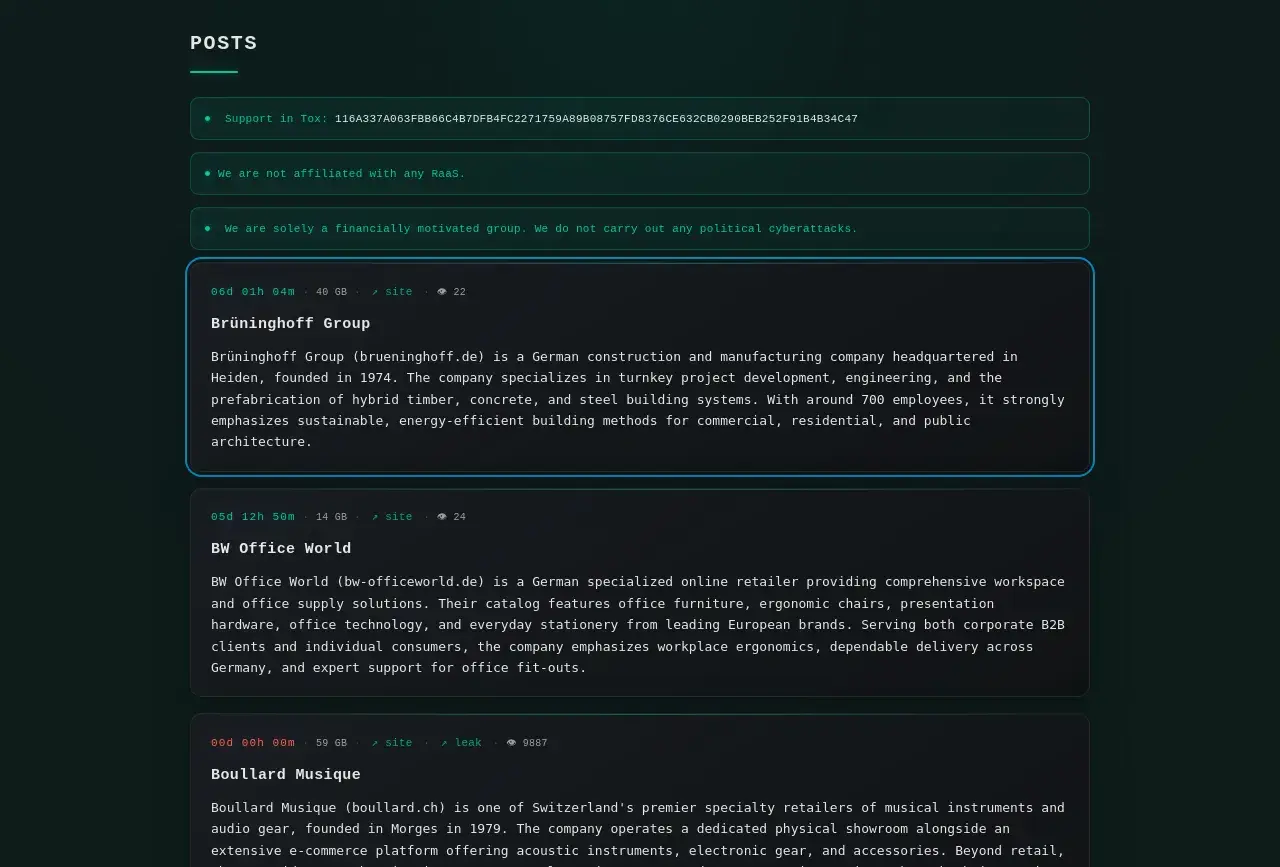
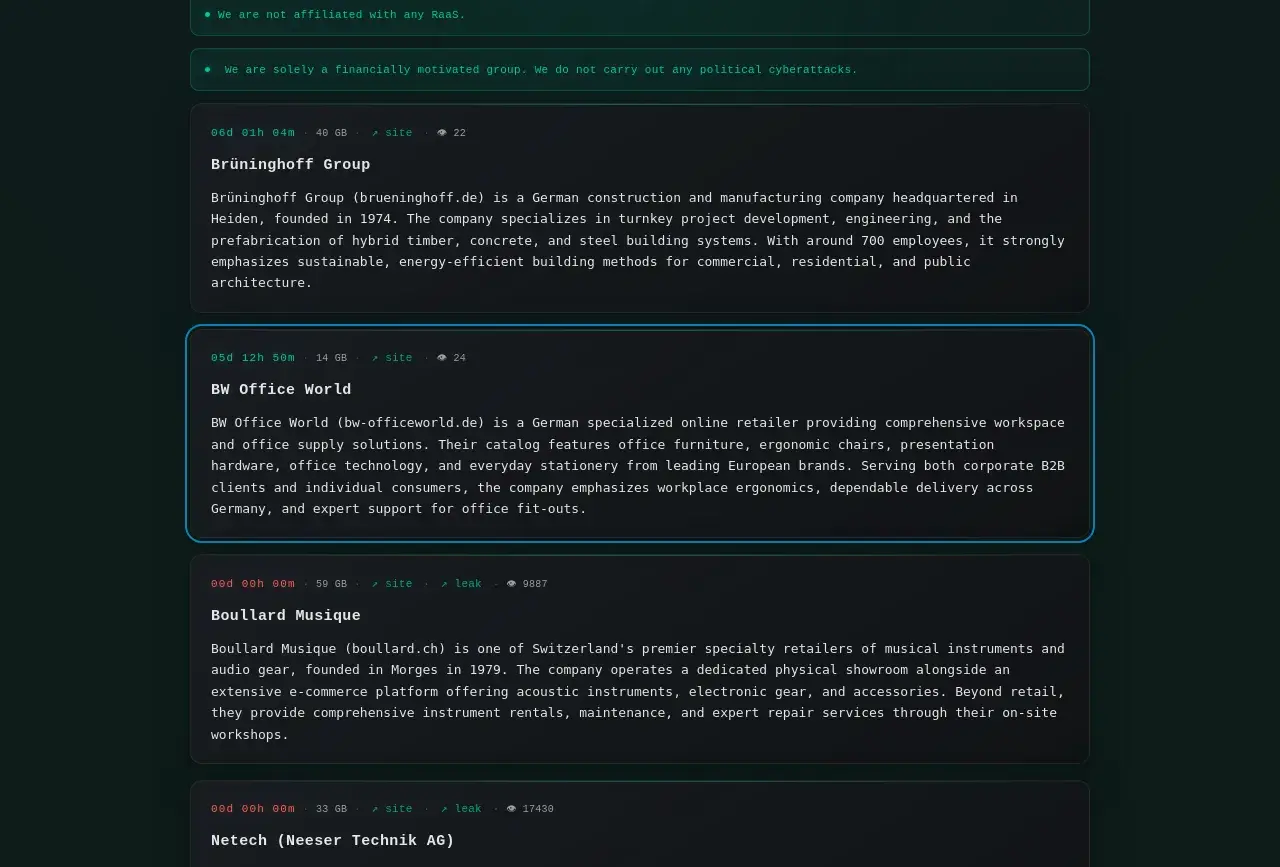
🚨New ransom group blog posts!🚨

Group name: payload
Post title: Brüninghoff Group
Location: 🇩🇪 DE
Sector: Construction
Info: https://cti.fyi/#disclosure/payload/Br%C3%BCninghoff%20Group

Group name: payload
Post title: BW Office World
Location: 🇩🇪 DE
Sector: Other
Info: https://cti.fyi/#disclosure/payload/BW%20Office%20World

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

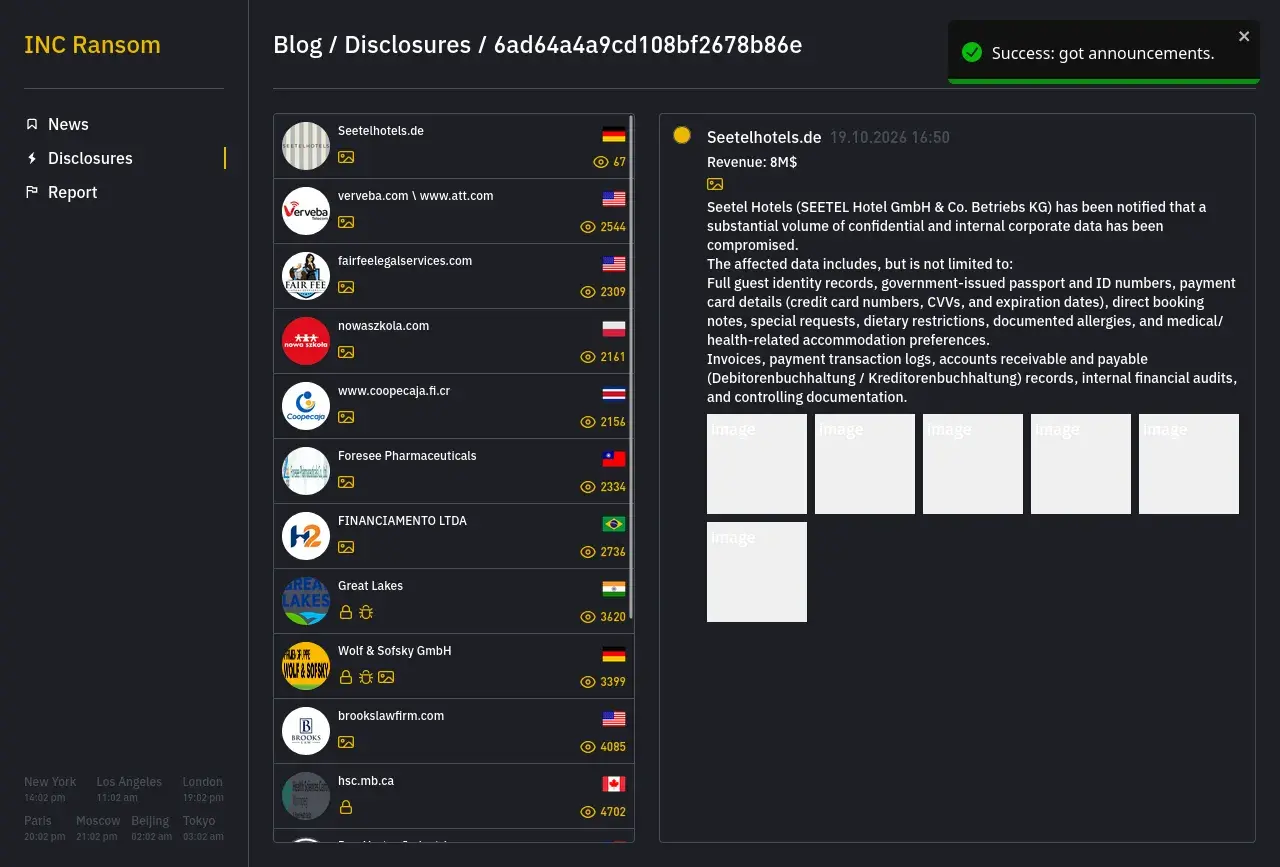
🚨New ransom group blog post!🚨

Group name: incransom
Post title: Seetelhotels.de
Organization: Seetel Hotels
Location: 🇩🇪 DE
Sector: Hospitality & Tourism
Info: https://cti.fyi/#disclosure/incransom/Seetelhotels.de

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

KrebsOnSecurity alleges executives tied to ransomware negotiation services helped operate the ShinyHunters extortion site. Separately, DOJ sentenced a former negotiator in a BlackCat-related extortion case. Both raise integrity risks for third-party incident response. #Ransomware #ShinyHunters #ThreatIntelligence

https://cyberworldops.eu/en/report-alleges-ransomware-negotiation-executives-helped-operate

Report Alleges Ransomware Negotiation Executives Helped Operate ShinyHunters Extortion Site
CyberWorldOpsReport Alleges Negotiators Helped Run ShinyHunters SiteReport says U.S. investigators suspect ransomware negotiators helped run ShinyHunters' Shinywire extortion site, citing anonymous sources.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

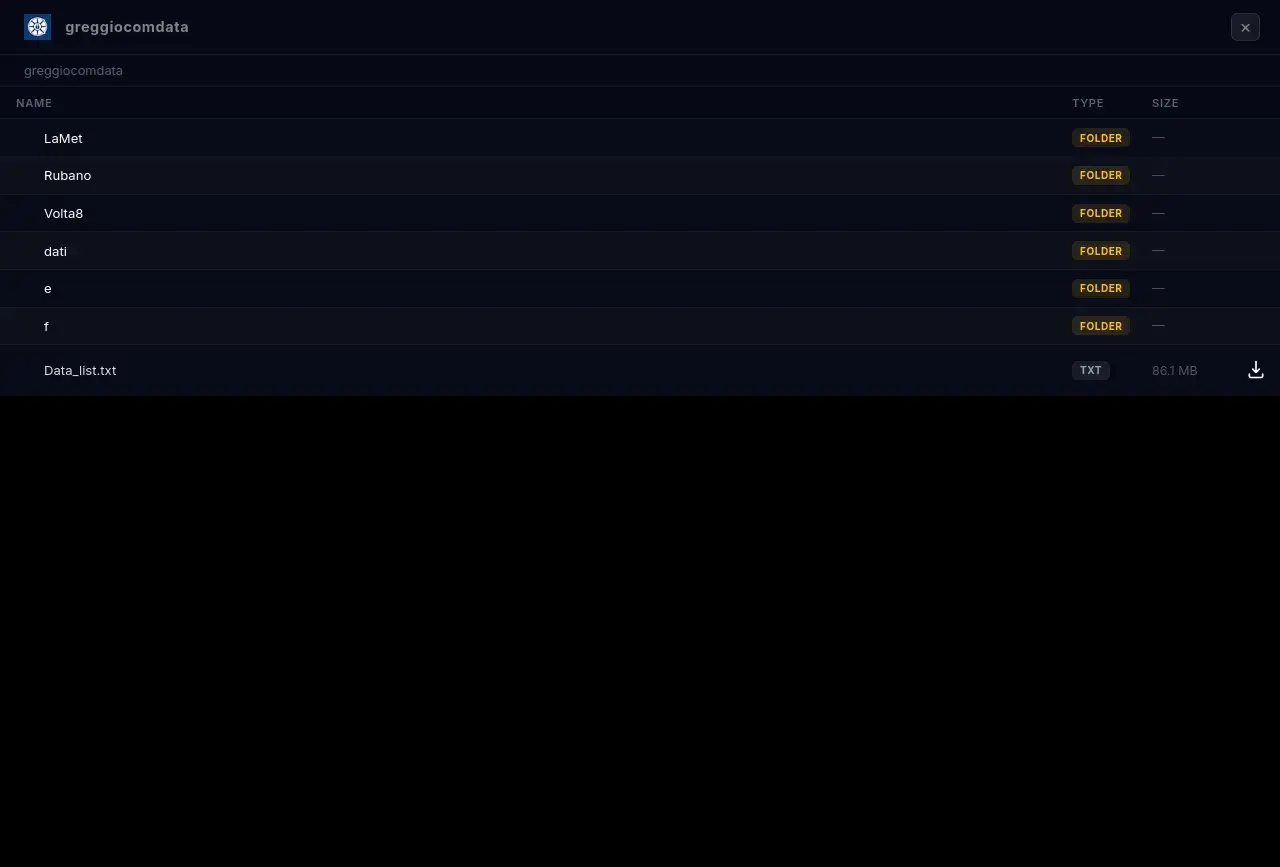
🚨New ransom group blog posts!🚨

Group name: Deadlock
Post title: Greggio Argento
Location: 🇮🇹 IT
Sector: Technology
Info: https://cti.fyi/#disclosure/Deadlock/Greggio%20Argento

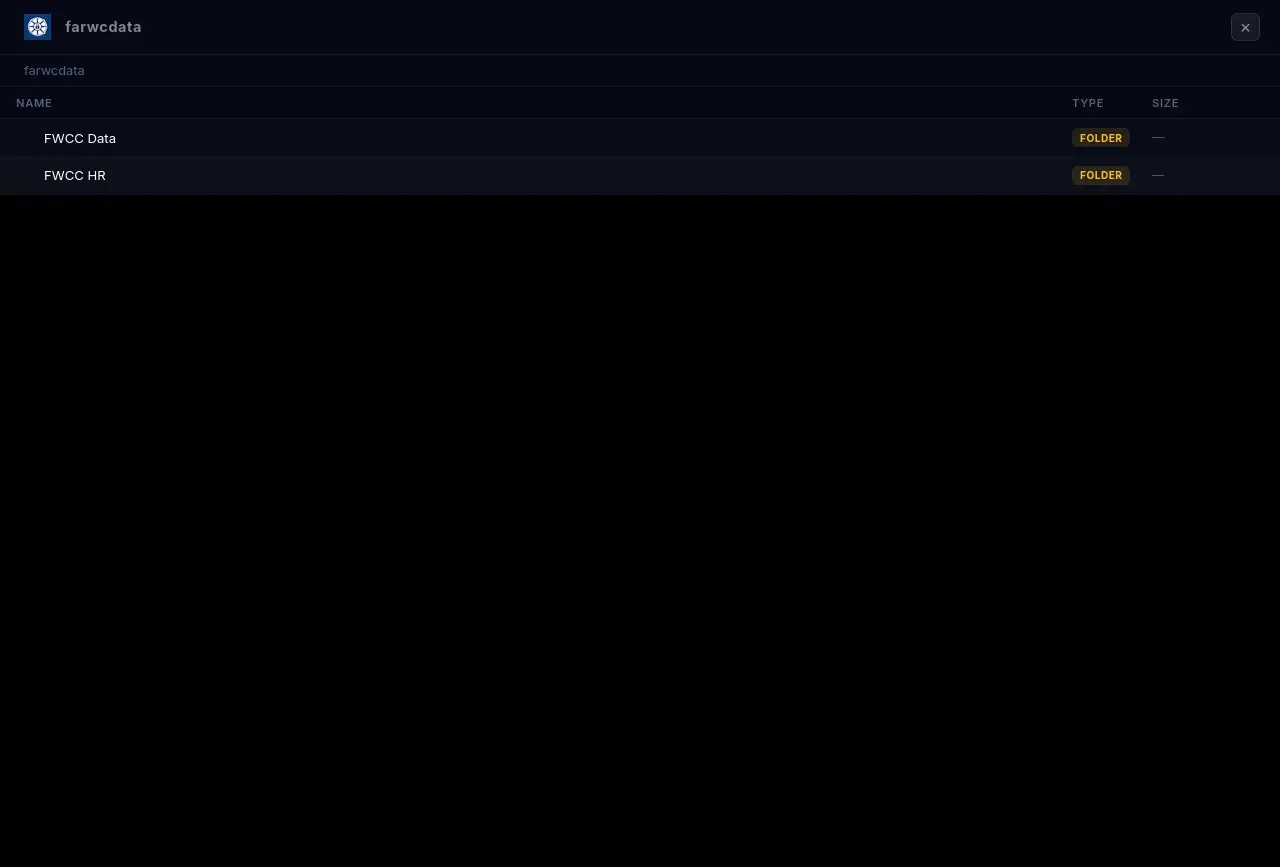
Group name: Deadlock
Post title: Far West Contractors
Sector: Construction
Info: https://cti.fyi/#disclosure/Deadlock/Far%20West%20Contractors

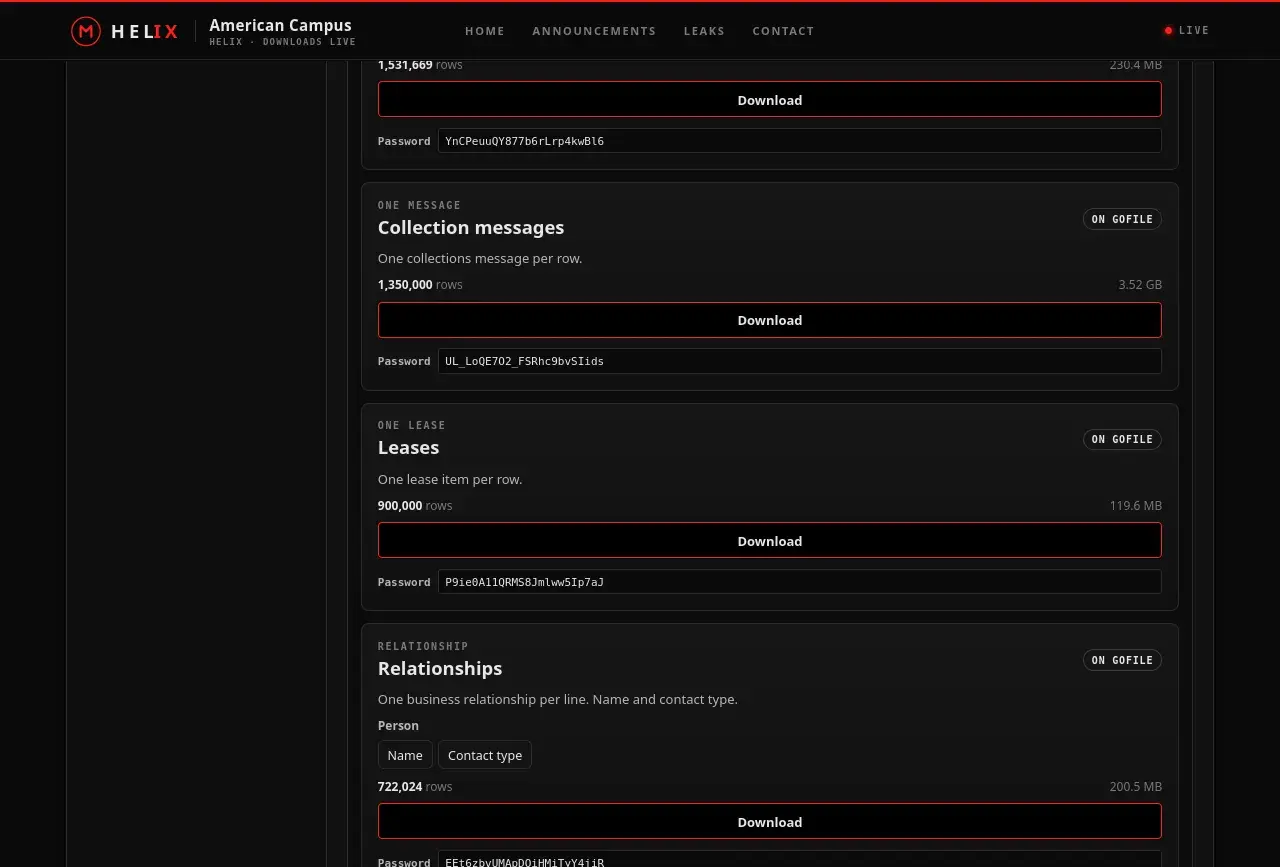
Group name: Helix
Post title: American Campus
Location: 🇺🇸 US
Sector: Education
Info: https://cti.fyi/#disclosure/Helix/American%20Campus

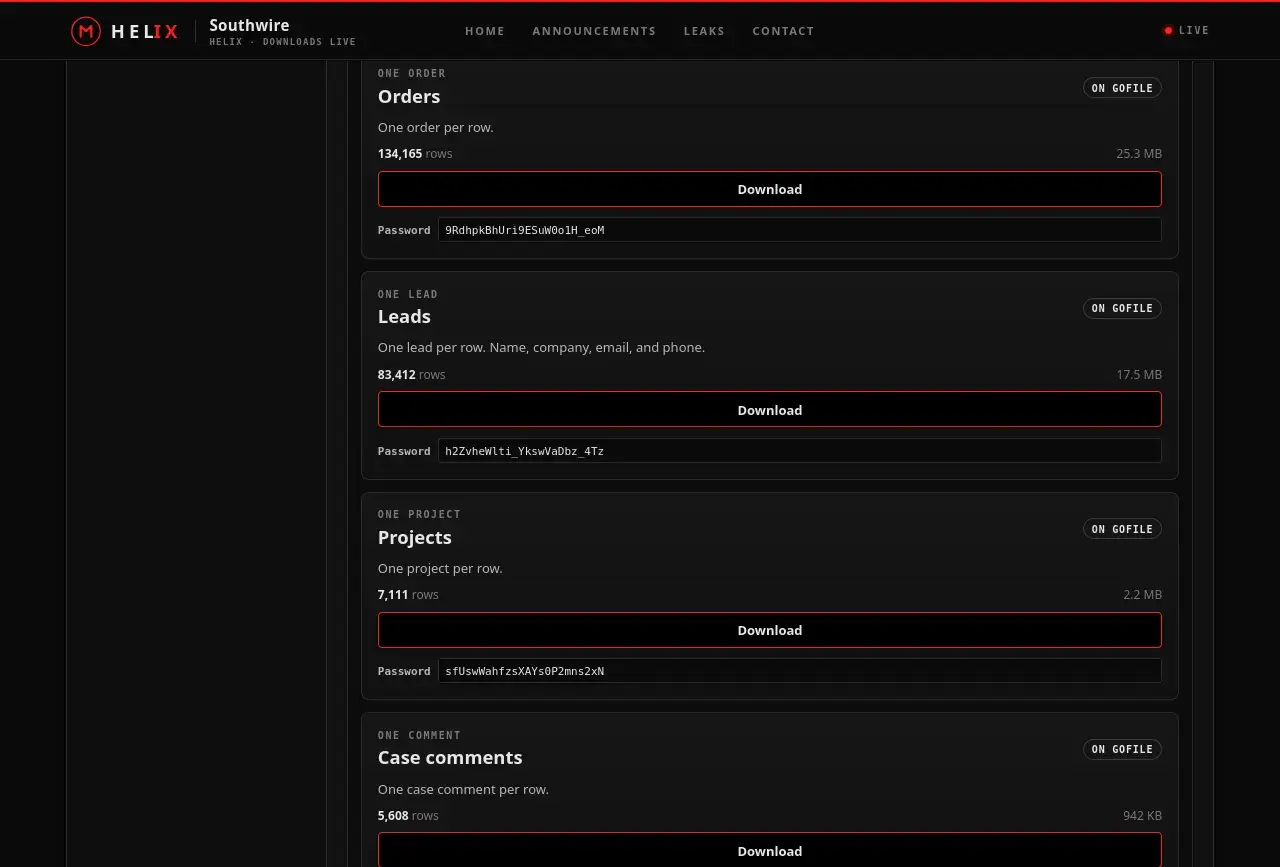
Group name: Helix
Post title: Southwire
Location: 🇺🇸 US
Sector: Manufacturing
Info: https://cti.fyi/#disclosure/Helix/Southwire

Group name: Helix
Post title: Quikrete
Location: 🇺🇸 US
Sector: Construction
Info: https://cti.fyi/#disclosure/Helix/Quikrete

Group name: Helix
Post title: Smith Douglas Homes
Location: 🇺🇸 US
Sector: Construction
Info: https://cti.fyi/#disclosure/Helix/Smith%20Douglas%20Homes

Group name: Helix
Post title: Bay Alarm
Location: 🇺🇸 US
Sector: Technology
Info: https://cti.fyi/#disclosure/Helix/Bay%20Alarm

Group name: Helix
Post title: Personify Health
Location: 🇺🇸 US
Sector: Healthcare
Info: https://cti.fyi/#disclosure/Helix/Personify%20Health

Group name: Helix
Post title: Rheem Global
Location: 🇺🇸 US
Sector: Manufacturing
Info: https://cti.fyi/#disclosure/Helix/Rheem%20Global

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachmentMedia attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original