X XFediYour place in the Fediverse
XFEDI

Remote profile

ActivityPub
Profile banner
Posts

PHP2Shell: two critical PHP RCE vulnerabilities — patches and protection

🔗 https://cybersecurefox.com/en/php2shell-critical-php-rce-vulnerabilities-patches-protection

#PHP2Shell #CVE-2026-109618 #CVE-2026-109619 #PHP #RCE #PHP #vulnerability
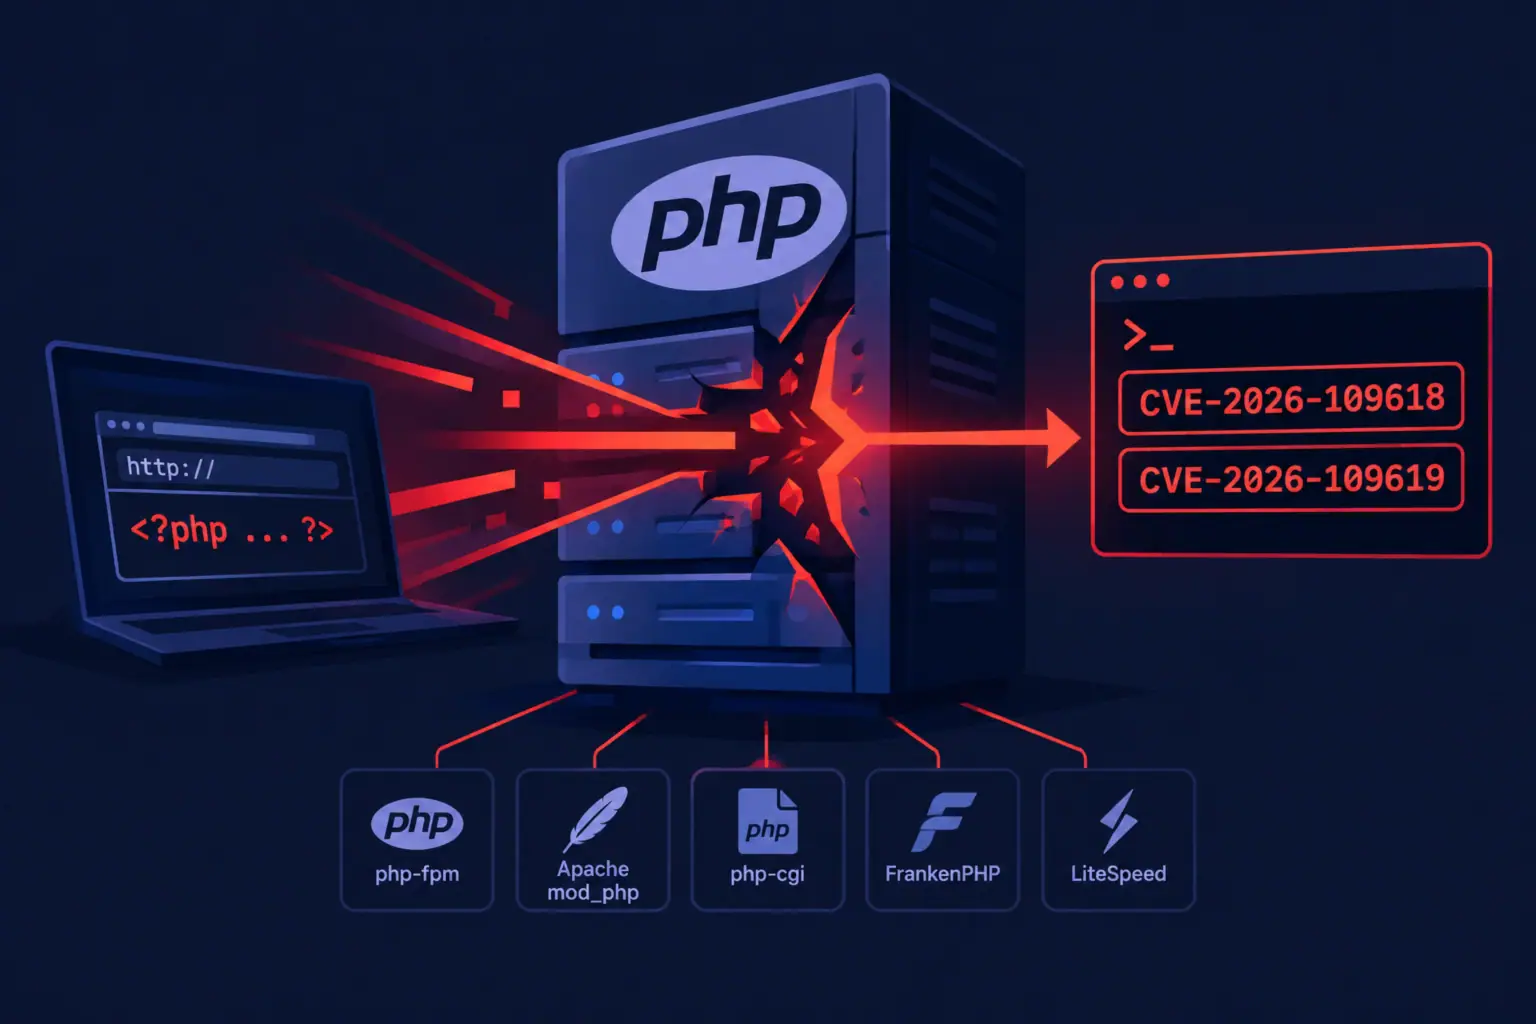
CyberSecureFoxPHP2Shell: Two Critical PHP RCE Vulnerabilities — Patches And ProtectionOn October 21, 2026, the PHP team released emergency updates for two critical remote code execution (RCE) vulnerabilities collectively dubbed PHP2Shell. The
↩ Reply ♡ 0 · ↻ 0 ↗ Original

ChromeOS M-156: 12 critical and dozens of high-severity vulnerabilities

🔗 https://cybersecurefox.com/en/chromeos-m156-12-critical-vulnerabilities-update-october-2026

#ChromeOS #M-156 #Chrome #vulnerabilities #use #after #free #CVE-2026-110151 #CVE-2026-113303

CyberSecureFoxChromeOS M-156: 12 Critical And Dozens Of High-severity VulnerabilitiesOn 20 October 2026, Google released the ChromeOS M-156 update (version 16836.19.0, browser 156.0.8078.42) for the stable channel, according to the official
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Critical PHP RCE vulnerabilities: emergency patch and 884,000 unprotected hosts

🔗 https://cybersecurefox.com/en/php2shell-critical-php-rce-vulnerabilities-emergency-patch

#PHP2Shell #CVE-2026-109618 #CVE-2026-109619 #PHP #RCE #critical #PHP #vulnerability

CyberSecureFoxCritical PHP RCE Vulnerabilities: Emergency Patch And 884,000 Unprotected HostsThe PHP security team has announced two critical vulnerabilities with a CVSS v4.0 score of 9.2 and scheduled an out-of-band security release for 21 October
↩ Reply ♡ 0 · ↻ 0 ↗ Original

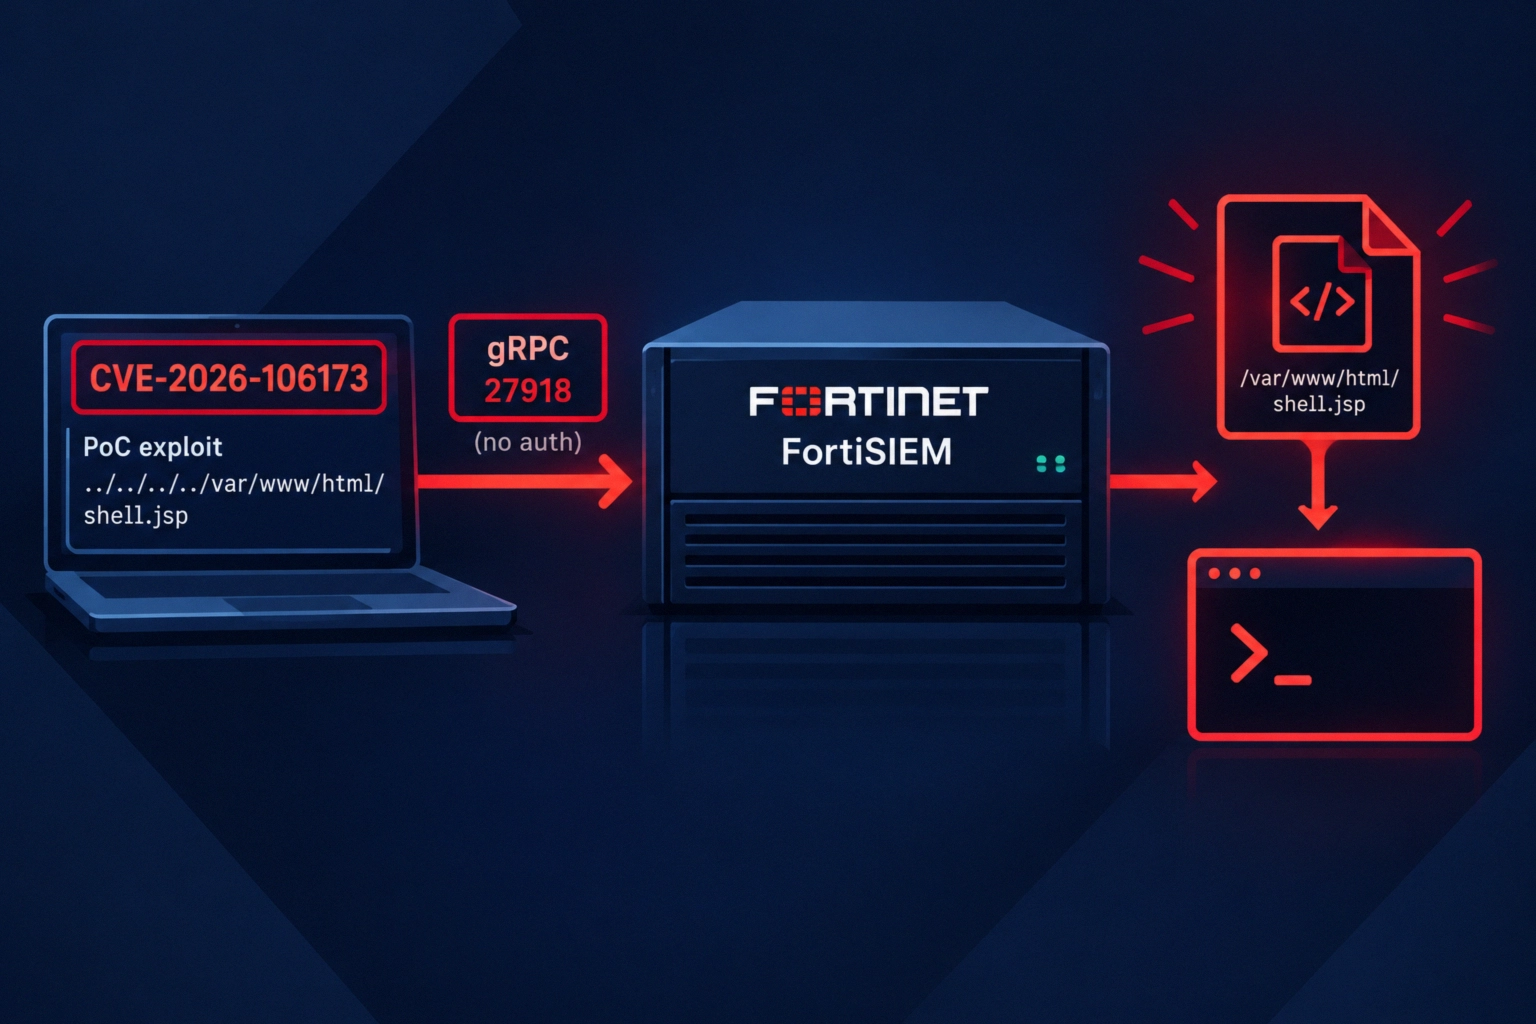
PoC exploit for CVE-2026-106173 in FortiSIEM: unauthenticated remote code execution

🔗 https://cybersecurefox.com/en/cve-2026-106173-fortisiem-poc-exploit-rce

#CVE-2026-106173 #FortiSIEM #Fortinet #gRPC #path #traversal

CyberSecureFoxPoC Exploit For CVE-2026-106173 In FortiSIEM: Unauthenticated Remote Code ExecutionResearchers at Horizon3.ai have released a working PoC exploit for the critical vulnerability CVE-2026-106173 in Fortinet FortiSIEM. This path traversal
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CVE-2026-102764: zero-day vulnerability in BeyondTrust Remote Support

🔗 https://cybersecurefox.com/en/cve-2026-102764-beyondtrust-remote-support-zero-day-armory-castle

#CVE-2026-102764 #BeyondTrust #Remote #Support #Armory #Castle #UNC5221 #zero-day

CyberSecureFoxCVE-2026-102764: Zero-day Vulnerability In BeyondTrust Remote SupportThe critical vulnerability CVE-2026-102764 (CVSSv4 9.3) in BeyondTrust Remote Support was exploited as a zero-day by the Armory Castle group (formerly
↩ Reply ♡ 0 · ↻ 0 ↗ Original

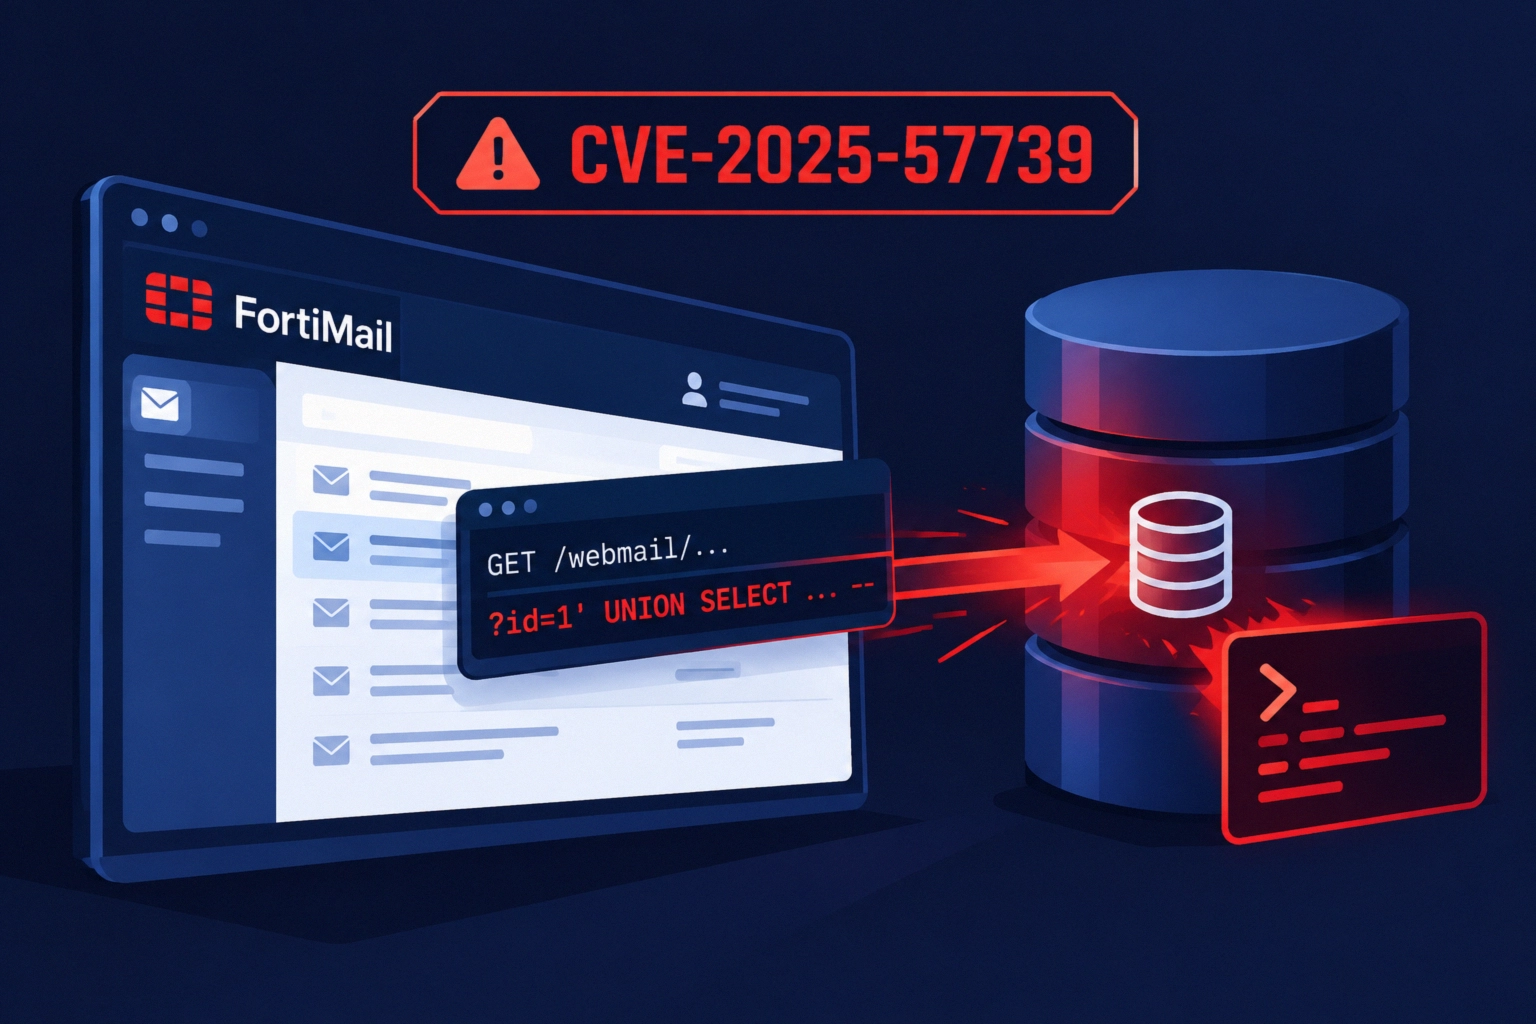
CVE-2025-57739: SQL injection in FortiMail webmail

🔗 https://cybersecurefox.com/en/cve-2025-57739-sql-injection-fortimail-webmail

#CVE-2025-57739 #FortiMail #SQL #injection #Fortinet #CWE-89

CyberSecureFoxCVE-2025-57739: SQL Injection In FortiMail WebmailOn October 13, 2026, Fortinet published security advisory FG-IR-26-184, disclosing an SQL injection vulnerability (CVE-2025-57739) in the web interface of the
↩ Reply ♡ 0 · ↻ 0 ↗ Original

SQL injections in FortiAnalyzer and FortiManager: CVSSv3 up to 8.8

🔗 https://cybersecurefox.com/en/fg-ir-26-178-sql-injection-fortianalyzer-fortimanager

#FortiAnalyzer #FortiManager #SQL #injection #FG-IR-26-178 #CVE-2026-23705

CyberSecureFoxSQL Injections In FortiAnalyzer And FortiManager: CVSSv3 Up To 8.8On 13 October 2026, Fortinet published advisory FG-IR-26-178 describing SQL injection (CWE-89) vulnerabilities in FortiAnalyzer, FortiManager and their cloud
↩ Reply ♡ 0 · ↻ 0 ↗ Original