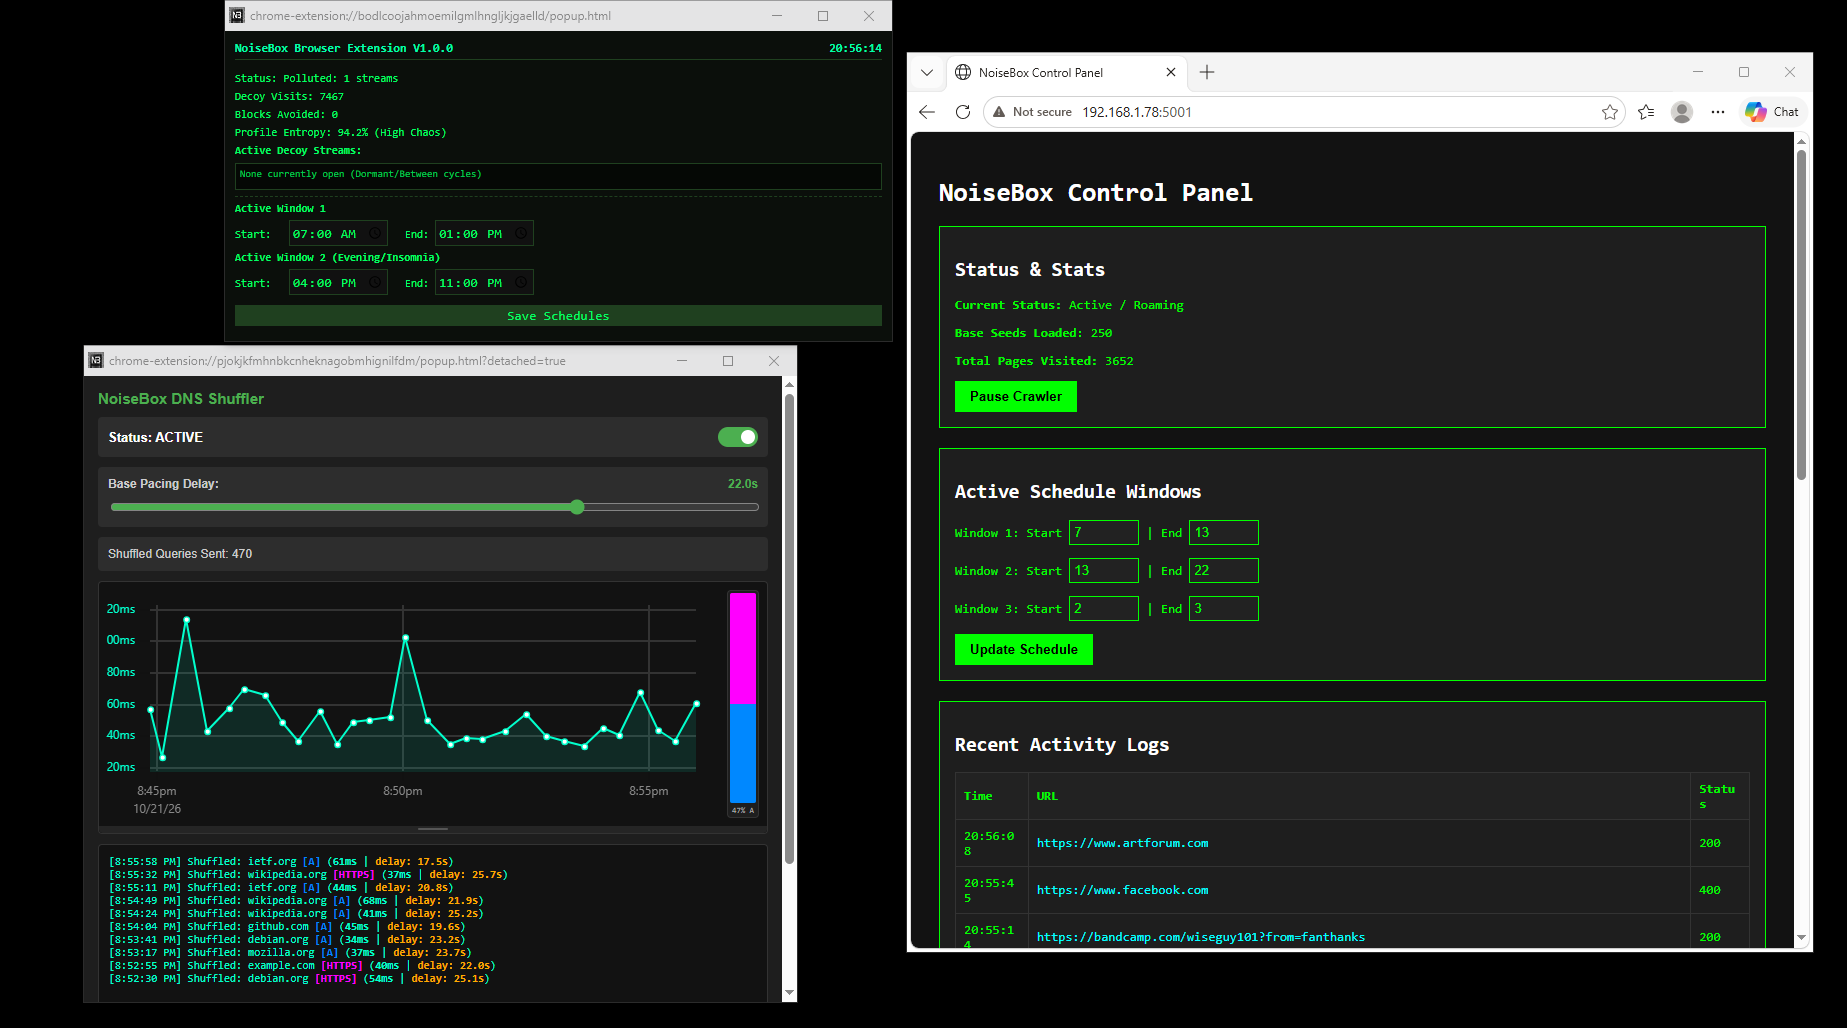
A screen full of data poison! Clockwise from top: NoiseBox Chrome Based Crawler Extension, NoiseBox router-level Wyse Crawler, and the new NoiseBox DNS Shuffler (coming soon). All working hard to obliterate our browsing patterns. All free, open source at Codeberg.org/NoiseBoxWorks
https://www.youtube.com/channel/UCi2cOT9eW575Fw-qoPB4seg
#Privacy #OpenSource #Infosec #DataPrivacy #BrowserExtension
Remote profile

NoiseBox- Poison Your Data
Drowning out network surveillance with decoy traffic.
NoiseBox is a FOSS network privacy tool that generates automated background traffic to disassociate your online footprint and obfuscate ISP/metadata profiling.
Python Crawler | Browser Extension
Code & Docs: https://codeberg.org/NoiseBoxWorks
A new repository is now live at Codeberg.org/NoiseBoxWorks/WyseCrawler. All the stuff you need to make a Dell Wyse 3040 Thin Client into a stand-alone router-based data obfuscater.
Stand up to Big Data! Poison your data with NoiseBox.
https://youtu.be/PmEvlzuw-JQ?si=X3fiZHm0hZQYqsqC
#NoiseBox #Privacy #DataPrivacy #OpenSource #SelfHosted #Homelab #Infosec #DellWyse #Wyse3040 #ThinClient #Linux #Python
This has been infuriating. We've developed a nifty NoiseBox crawler that works right in Windows but when we tested it by downloading it from our development repo and extracted it, our own Windows computer unilaterally decided it was a horrible threat and deleted the executable.
Tried setting it as safe in Windows Defender and restored it but then the file was corrupted. Same thing happened over and over.
How can we make this file not trigger this issue on people's computers when we go public?
