X XFediYour place in the Fediverse
XFEDI

Remote profile

ActivityPub
Profile banner

Dark Web Informer :verified_paw:

@[email protected]

Website: https://darkwebinformer.com
Website Pricing (Crypto payments are fully automated): https://darkwebinformer.com/pricing
Socials: https://darkwebinformer.com/socials
API Access: https://darkwebinformer.com/api-details
About Dark Web Informer: https://darkwebinformer.com/about-dark-web-informer
X: https://x.com/DarkWebInformer
Updated: 2026-07-20

Open remote profile ↗
Posts

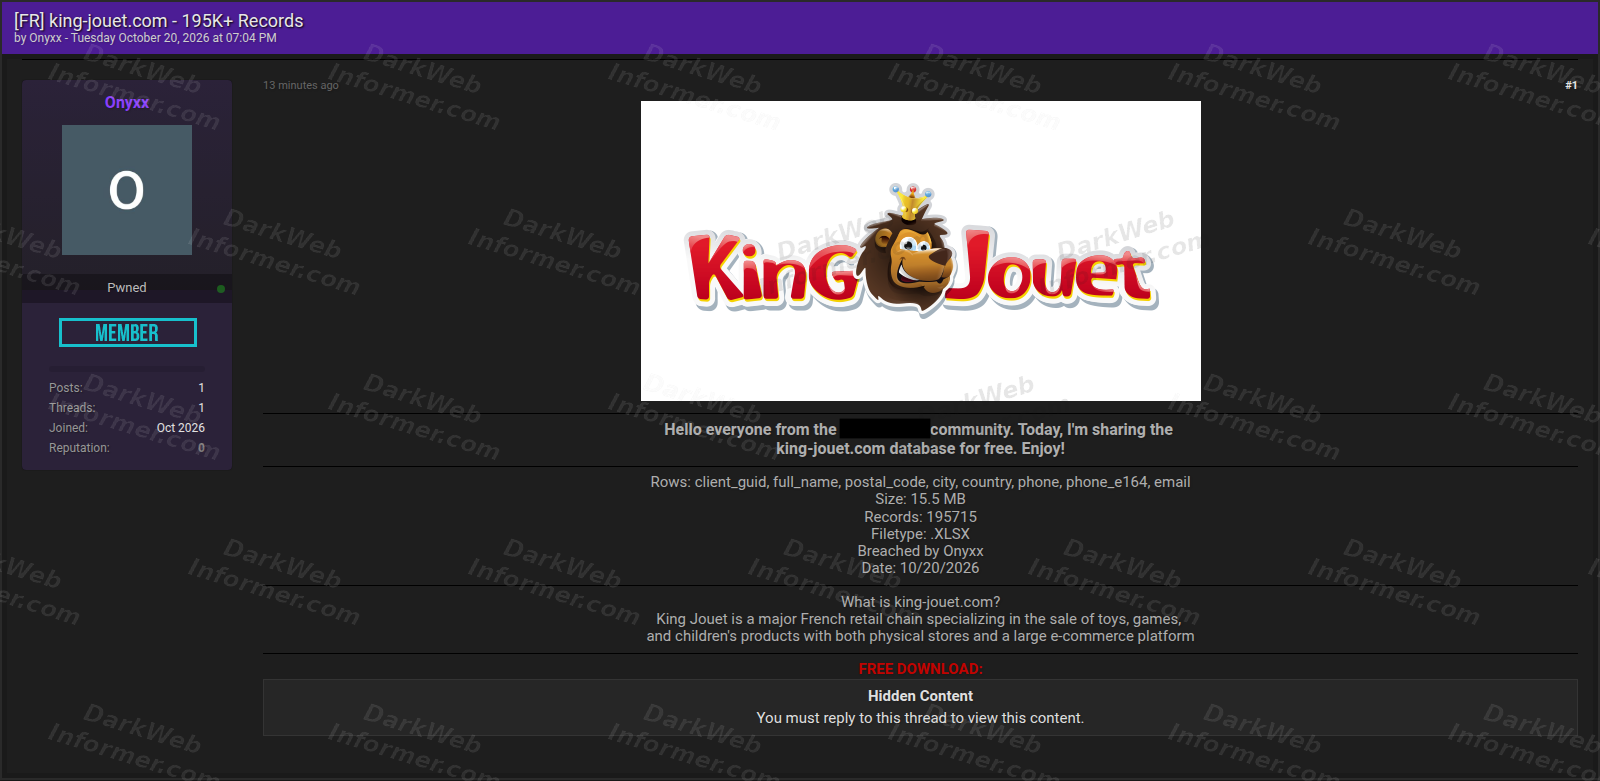
🚨🇫🇷 King Jouet customer dataset containing over 195,000 records allegedly leaked

King Jouet, a major French toy retailer with physical stores and an online shopping platform, has been targeted in an alleged data breach.

The actor "Onyxx" claims to have obtained 195,715 customer records containing full names, email addresses, phone numbers, cities, countries, and postal codes.

The 15.5 MB dataset has been released for free in XLSX format. Claim is currently unverified.

💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Media attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original

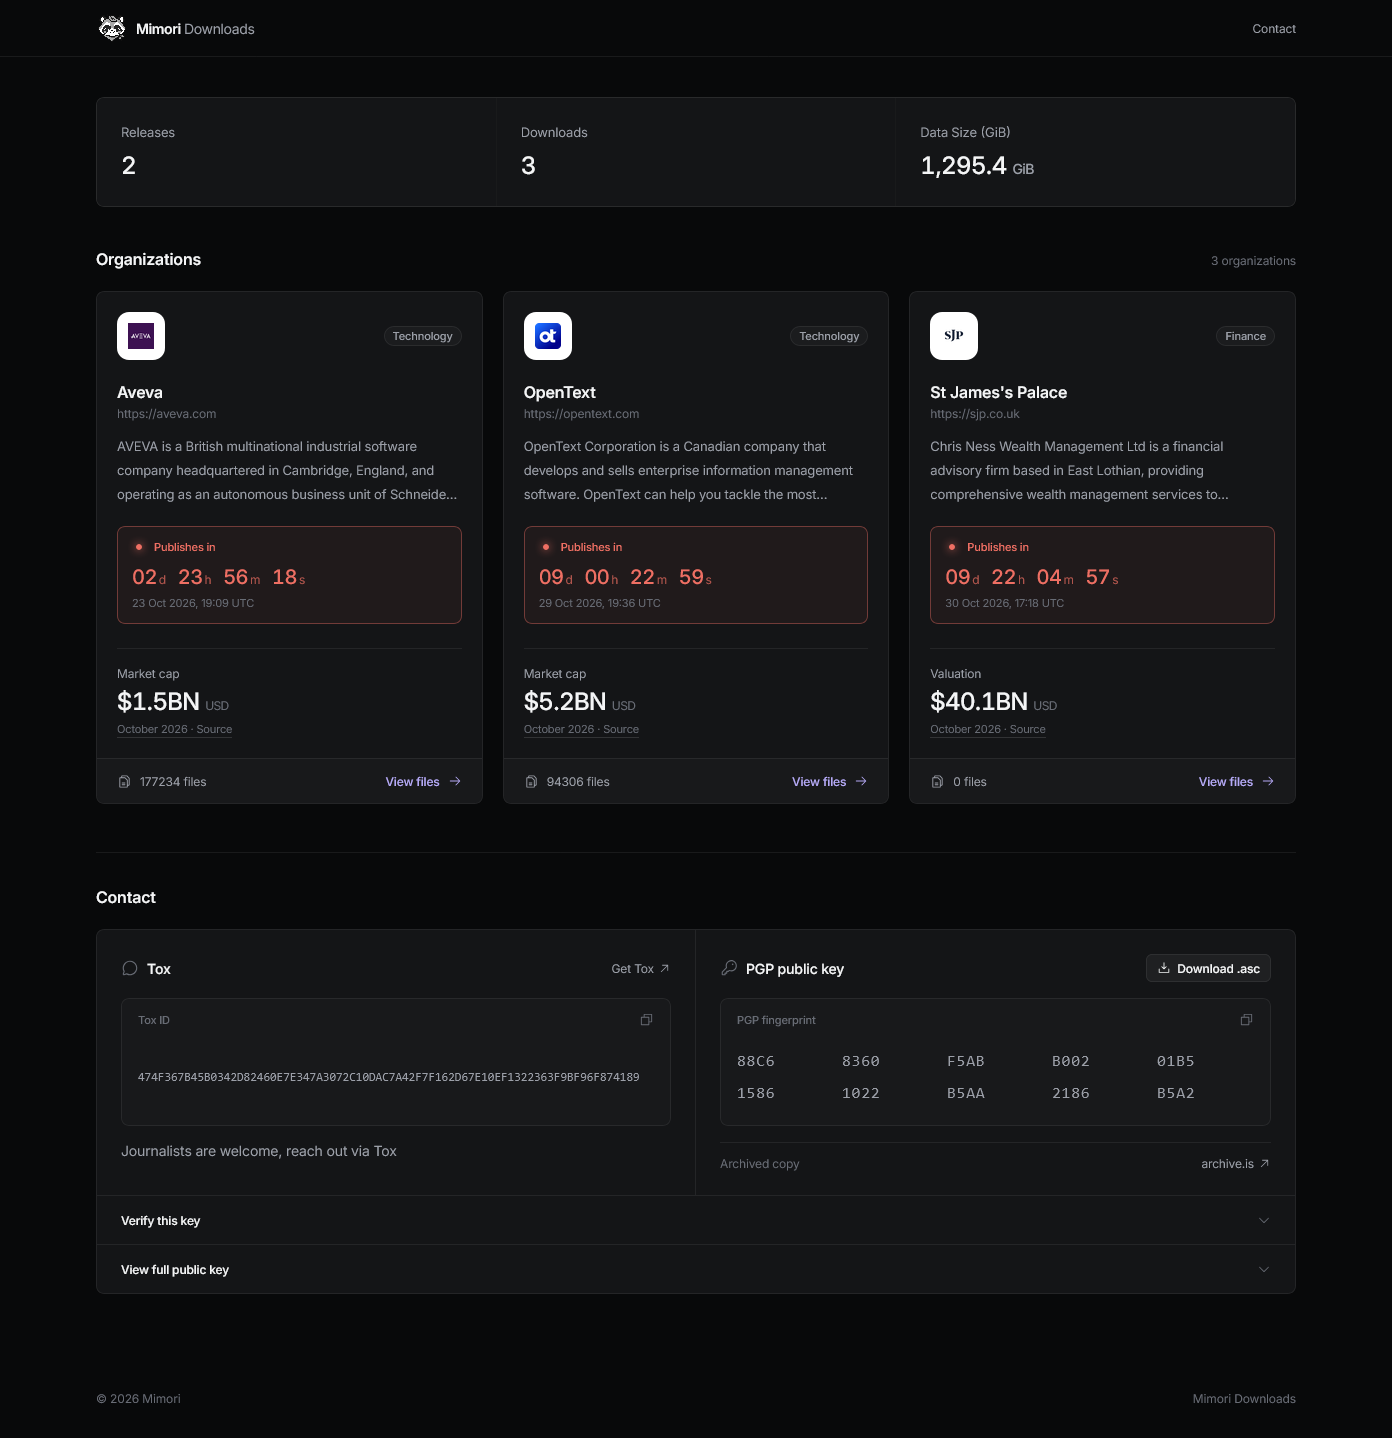
🚨🇧🇪 AFPadel member records allegedly leaked, exposing over 10,000 entries

AFPadel, the governing body for padel players in Belgium's Wallonia-Brussels Federation, has been named in a data leak involving 10,226 records.

The actor "Syrv4x" shared a 5 MB dataset containing player names, email addresses, age categories, nationalities, club affiliations, license details, rankings, and account information.

The dataset has been released for free. Claim is currently unverified.

💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Media attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original

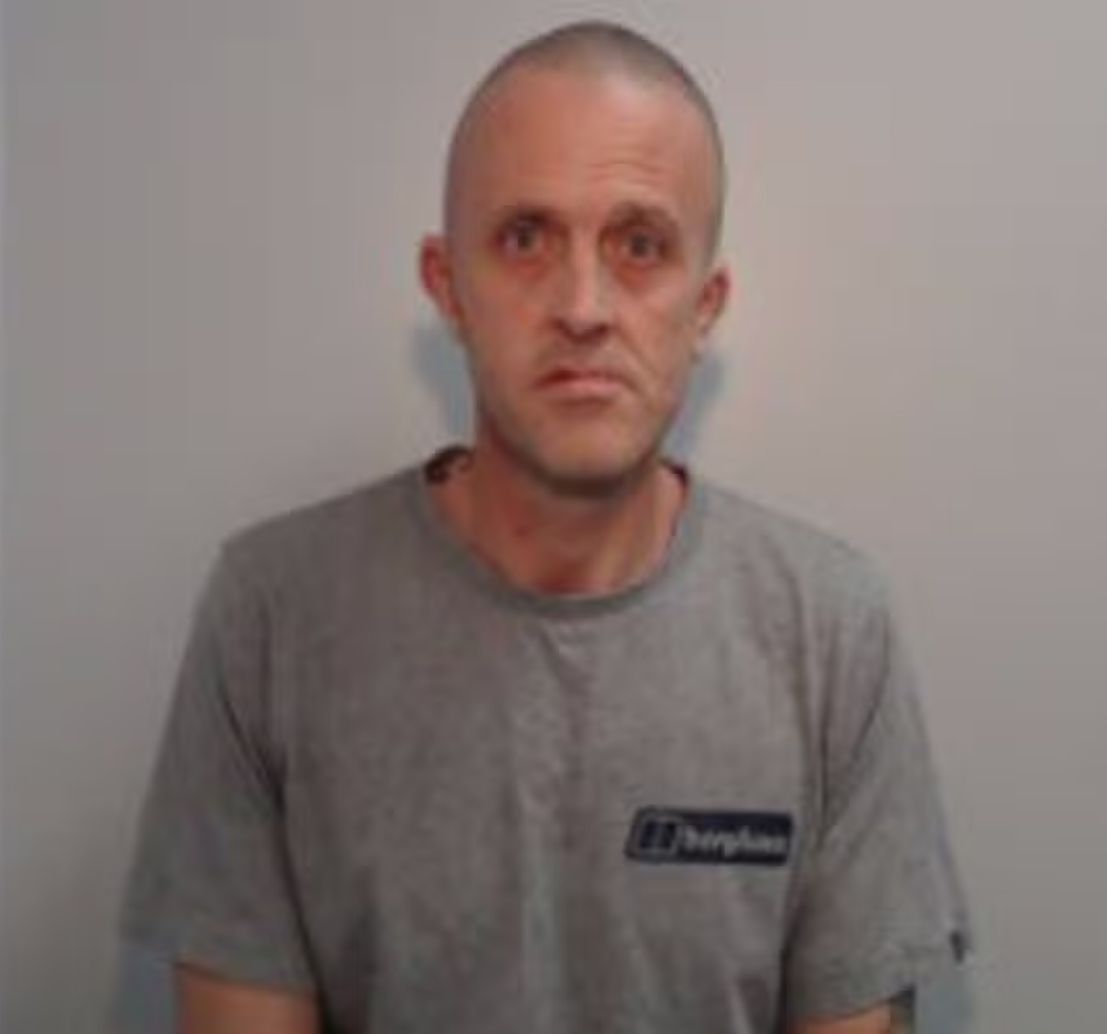
🚨🇬🇧 Dark web child r*pist identified through lingerie photos and images of his hands jailed for 23 years

Darren Welsby, 48, was convicted of r*ping and sexually abusing children, some as young as six, and recording and distributing the abuse online.
⠀
Investigators traced Welsby after the username “wellhnug,” used to upload child sexual abuse material on the dark web, was also used on an adult website where he posted photographs of himself wearing women’s lingerie.
⠀
A forensic anthropologist then matched his hands and knuckles to those visible in the abuse images, while digital experts established that the material was captured using one of his phones.

A search uncovered more than 30,000 abusive images across 10 devices. Welsby was sentenced to 23 years in prison and will serve a further five years on extended licence.

Source: https://www.cps.gov.uk/national-news/news/man-jailed-landmark-conviction-rape-and-child-sexual-abuse

Media attachment
www.cps.gov.ukMan jailed in landmark conviction for rape and child sexual abuse | The Crown Prosecution Service
↩ Reply ♡ 0 · ↻ 0 ↗ Original

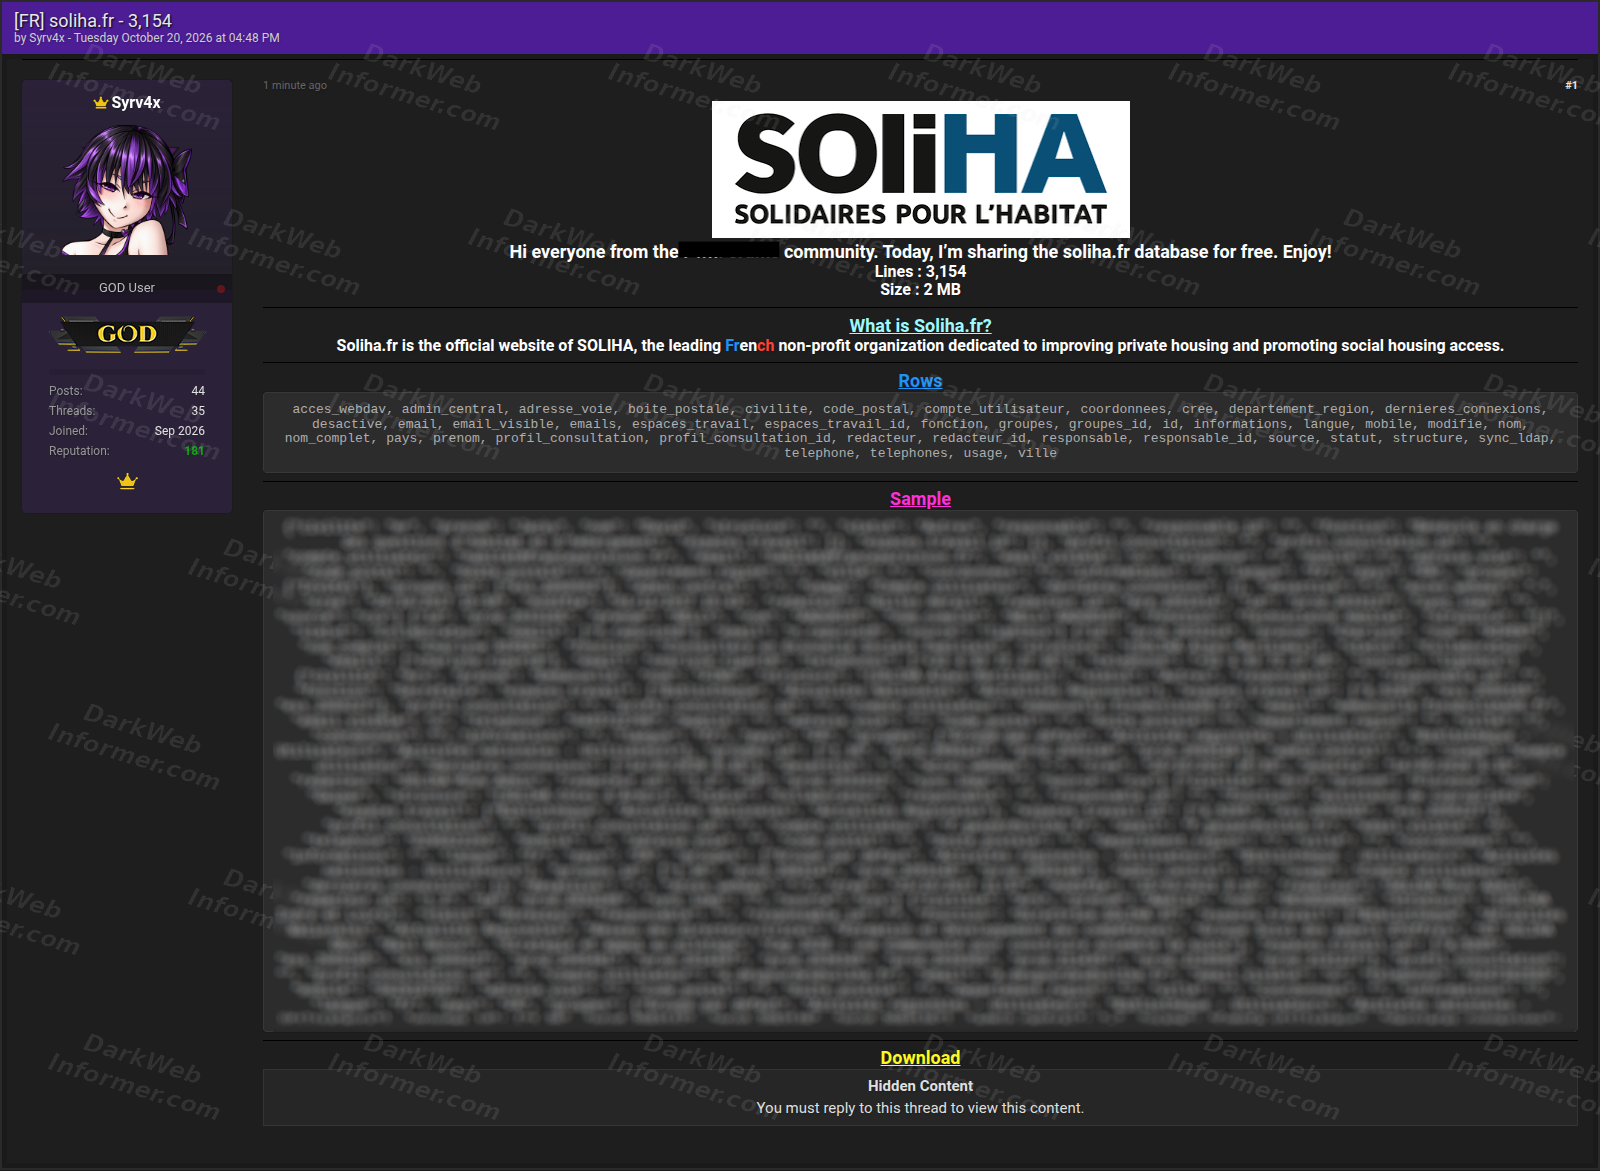
🚨🇫🇷 SOLIHA dataset containing over 3,100 records leaked

SOLIHA, a French nonprofit organization focused on improving housing conditions and access to affordable housing, has been named in a data leak involving 3,154 records.

The actor "Syrv4x" has shared a 2 MB dataset containing names, email addresses, phone numbers, staff roles, organizational affiliations, account information, and internal user details.

Claim is currently unverified.

💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Media attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original

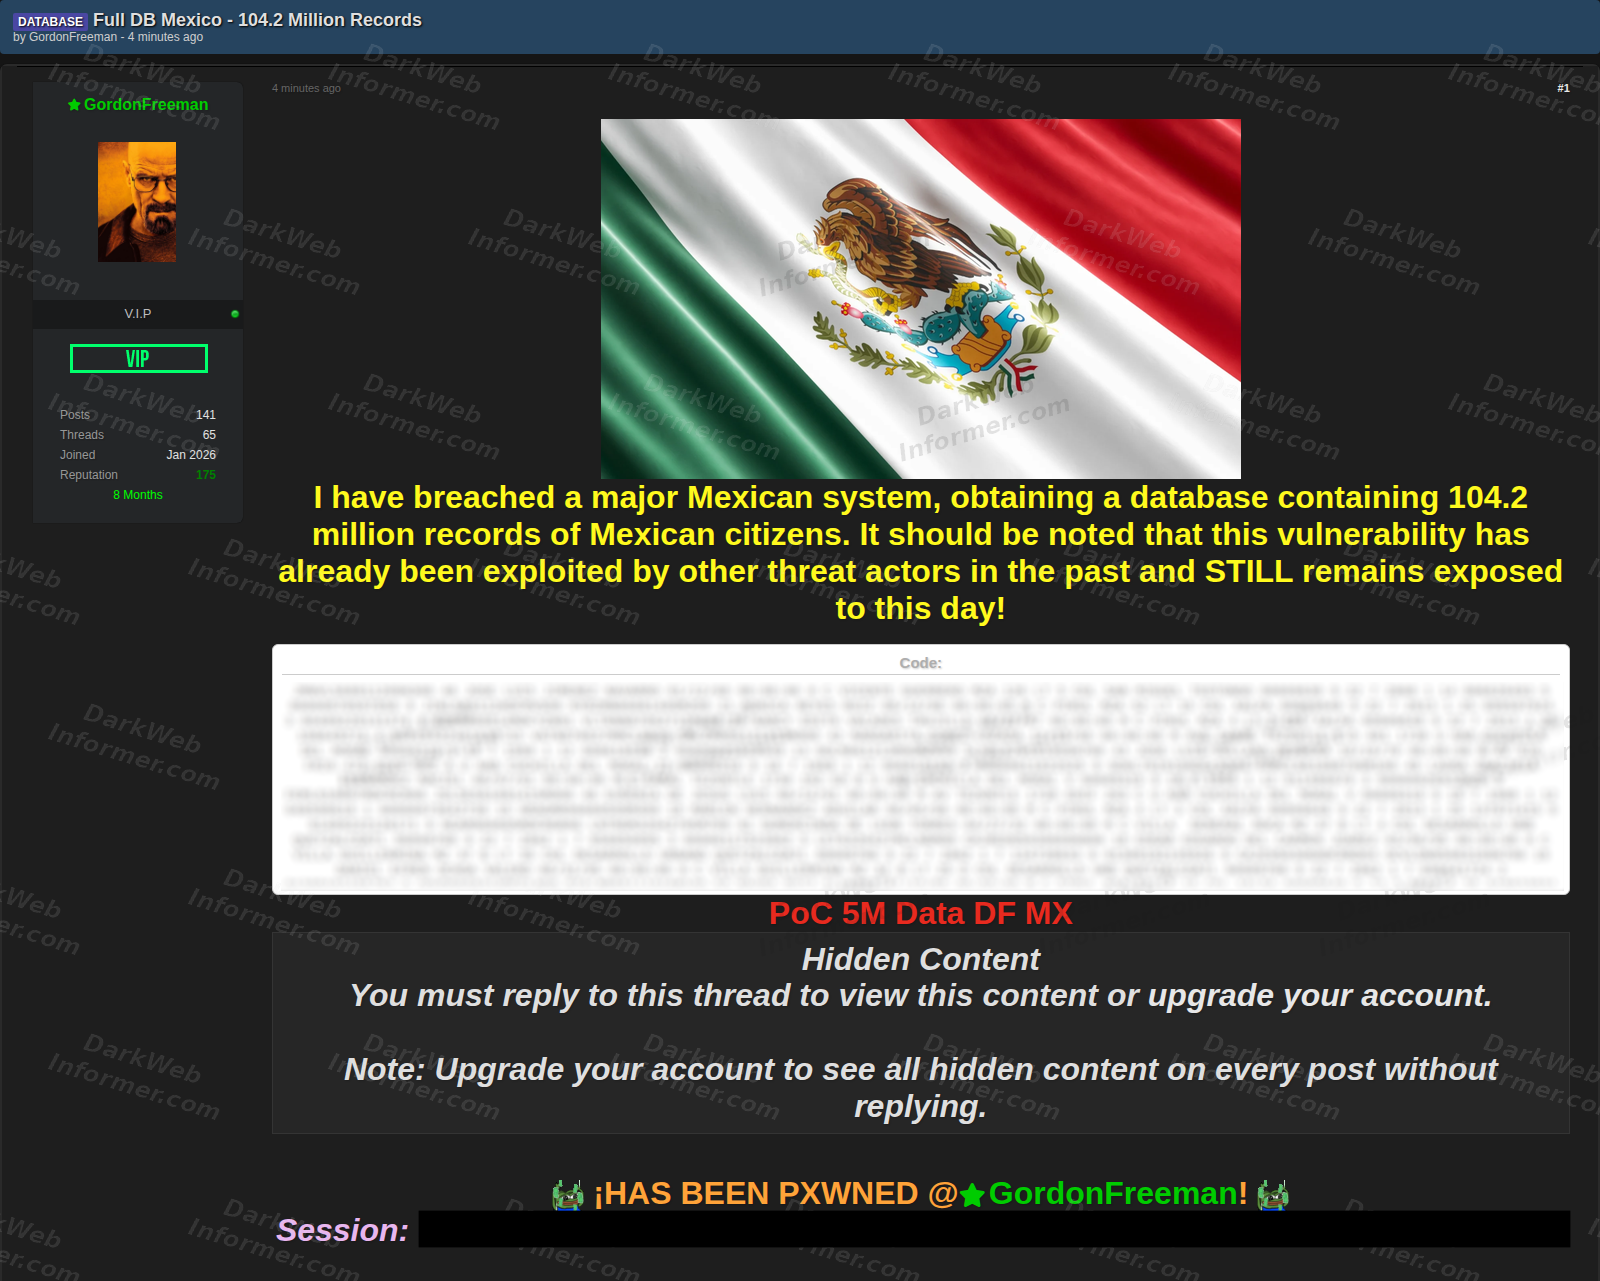
👀🚨🇲🇽 Actor claims to have breached Mexican government system, exposing a MASSIVE 104.2 million records

An actor known as "GordonFreeman" claims to have compromised a major Mexican system and obtained a dataset containing 104.2 million records belonging to Mexican citizens.

The actor published a sample containing names, dates of birth, identification numbers, and residential addresses, along with a claimed 5 million-record proof-of-concept dataset.

The actor also claims the vulnerability has been exploited by others and remains unpatched. The affected system has not been identified.

Claim is currently unverified.

💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Media attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original

‼️ New Dark Web Informer Blog Post!

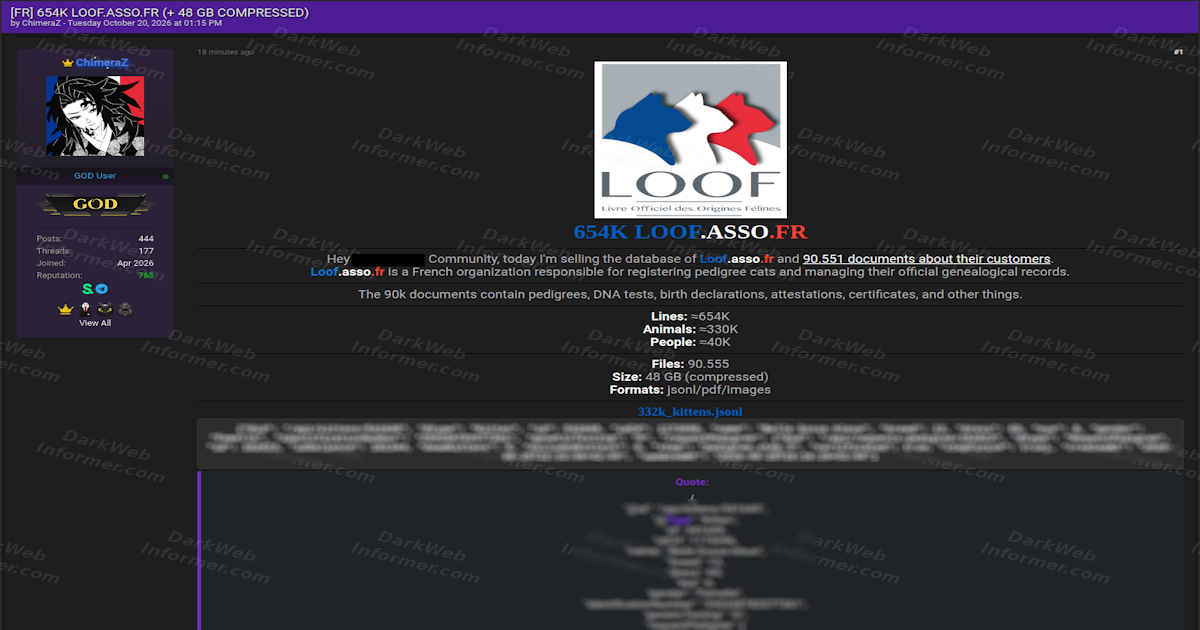
Title: LOOF Data Sale Claim Includes 654K Records and 90,555 Documents in 48 GB Archive

Link: https://darkwebinformer.com/loof-data-sale-claim-includes-654k-records-and-90-555-documents-in-48-gb-archive/

💥 Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing

Dark Web InformerLOOF Data Sale Claim Includes 654K Records and 90,555 Documents in 48 GB ArchiveAn actor using the handle "ChimeraZ" claims to be selling a LOOF dataset. LOOF, the Livre Officiel des Origines Félines, is described in the listing as the French organization responsible for registering pedigree cats and maintaining official feline genealogical records.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

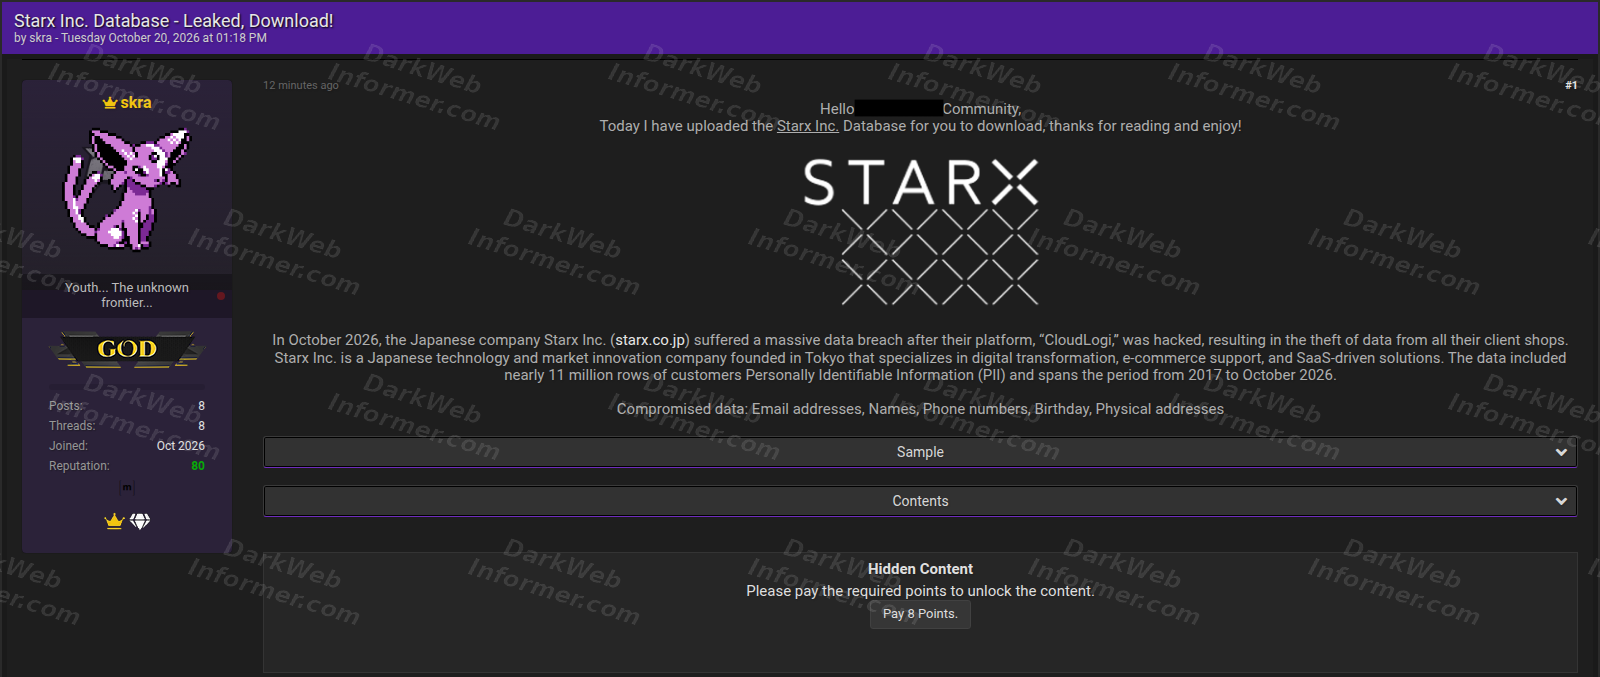
🚨🇯🇵 Starx Inc. allegedly breached, with nearly 11 million customer records exposed

Starx Inc., a Japanese technology company specializing in digital transformation, e-commerce, and SaaS solutions, has been named in a data breach claim involving nearly 11 million records.
⠀
The actor "skra" claims the company's CloudLogi platform was compromised, exposing customer information from its client shops dating from 2017 to October 2026.
⠀
The dataset reportedly contains names, email addresses, phone numbers, dates of birth, and residential addresses.
⠀
Claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Media attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original

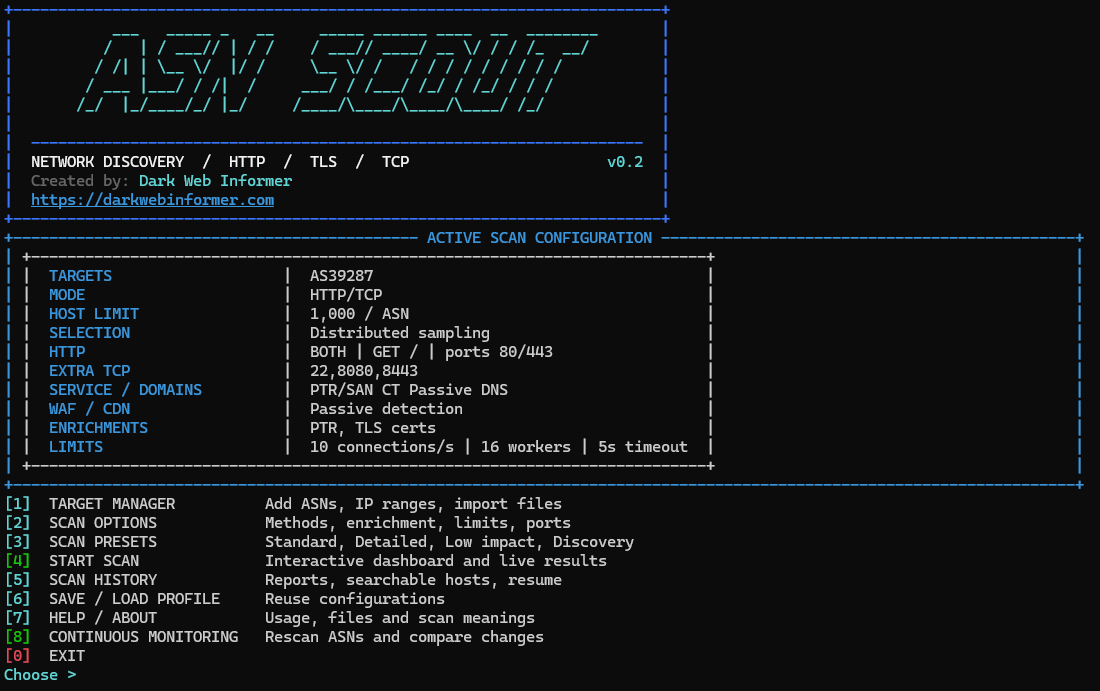
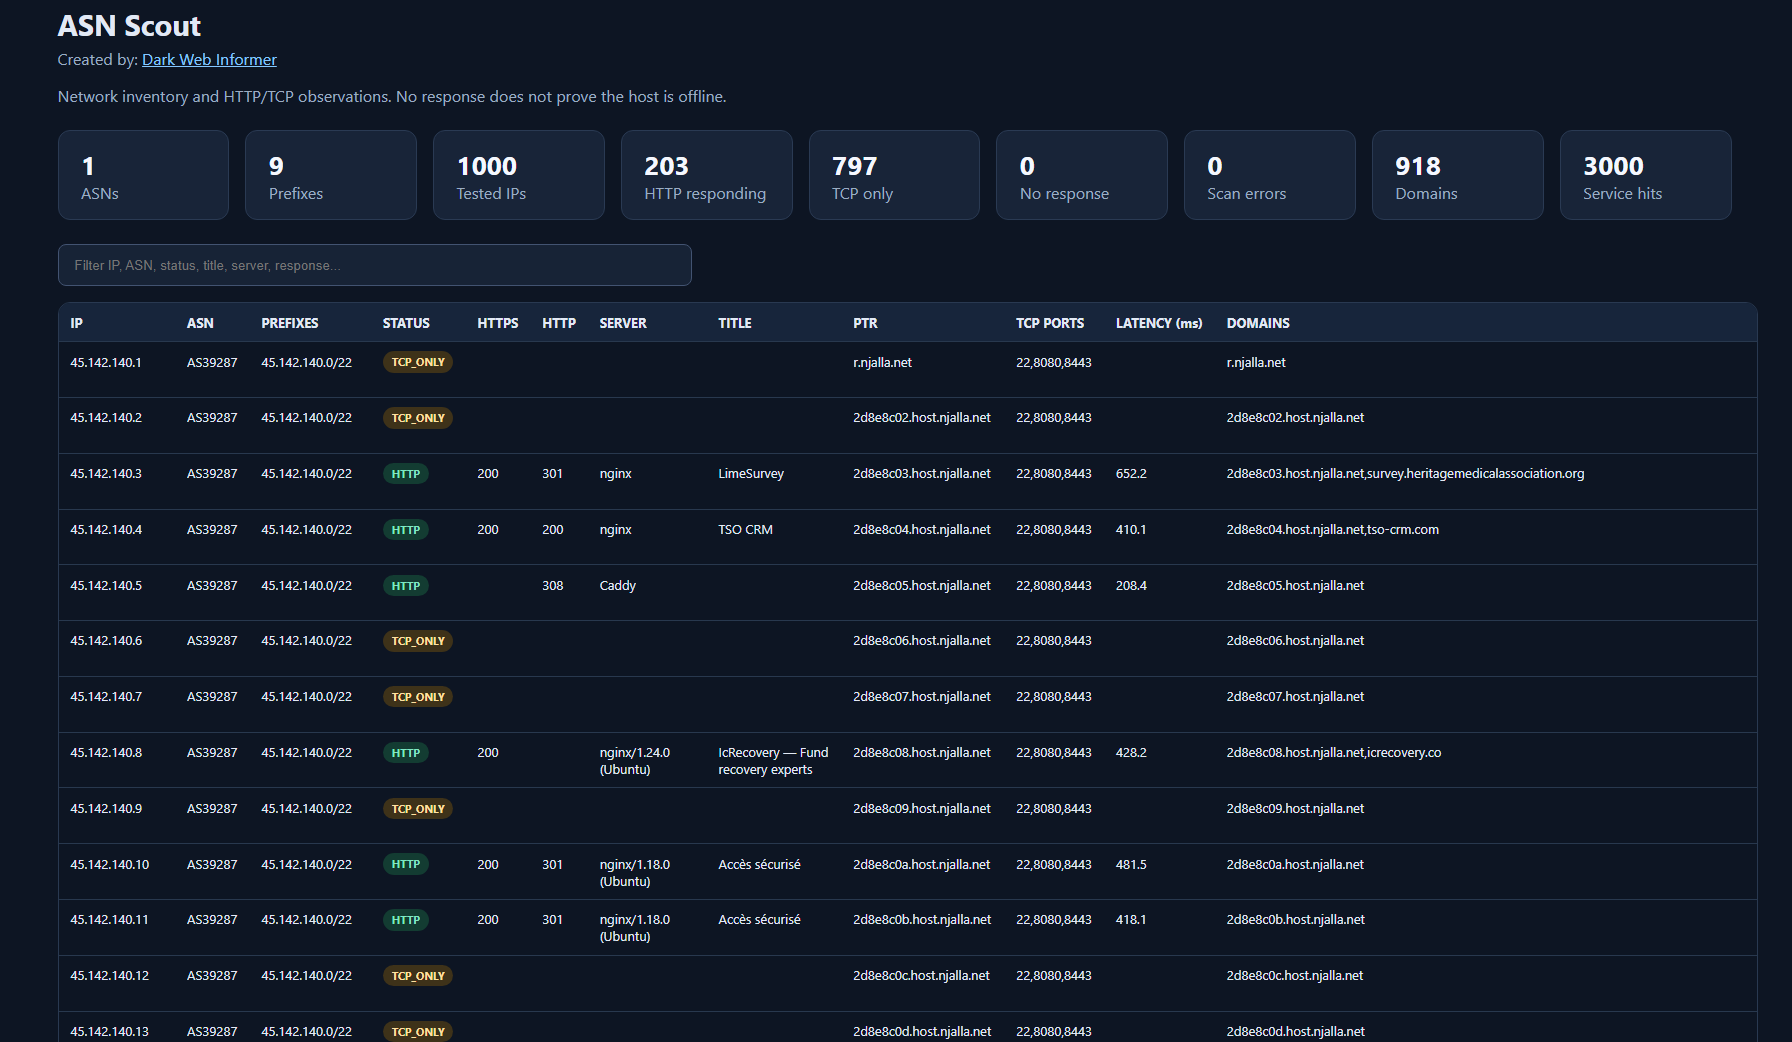
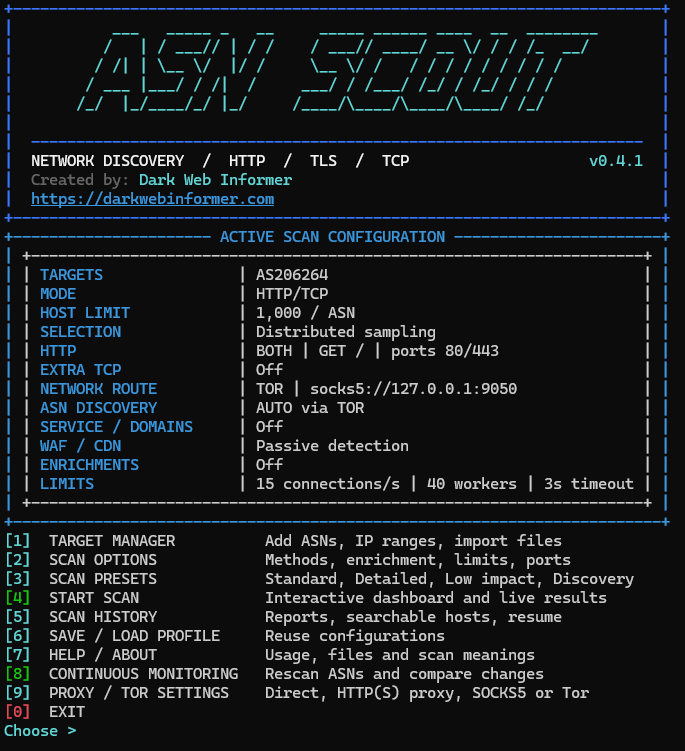
ASN Scout is a Python-based network discovery, service inspection, and infrastructure monitoring utility created by Dark Web Informer.

https://git.darkwebinformer.com/DarkWebInformer/asn_scout

It discovers IP prefixes originated by an autonomous system (ASN), selects addresses for controlled probing, collects HTTP/HTTPS and TCP observations, and generates searchable reports.

Media attachment
Forgejo: Beyond coding. We Forge.asn_scoutASN and IP network intelligence from your terminal.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

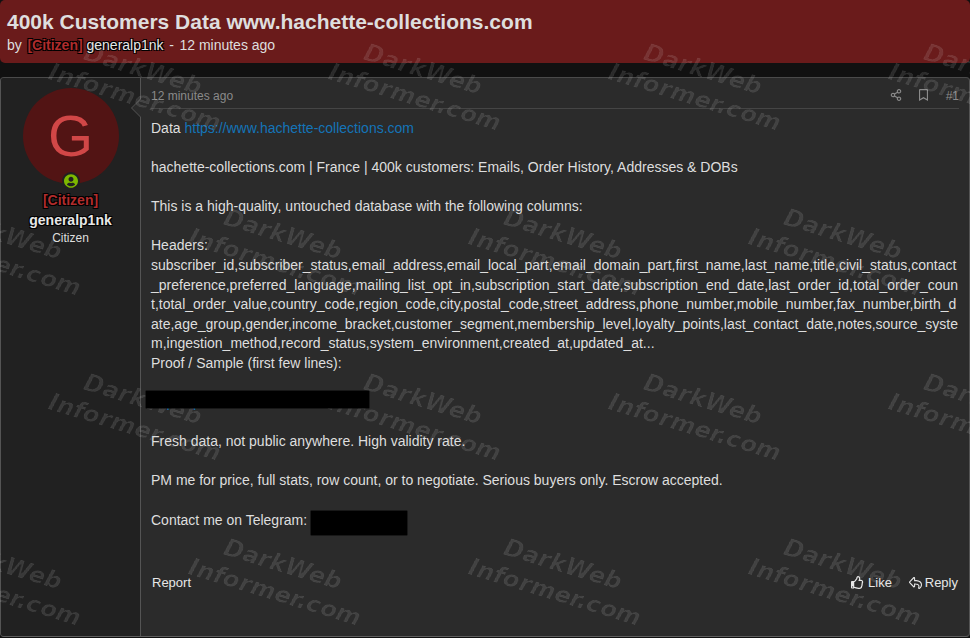
🚨🇫🇷 Hachette Collections customer dataset containing 400,000 records allegedly stolen

Hachette Collections, a French publisher specializing in collectible series and subscription-based products, has been named in a data breach claim involving approximately 400,000 customers.
⠀
The actor "generalp1nk" claims the dataset contains customer names, email addresses, phone numbers, residential addresses, dates of birth, order histories, subscription details, and loyalty information.
⠀
The actor has published a sample and is offering the dataset for sale. Claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Media attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original

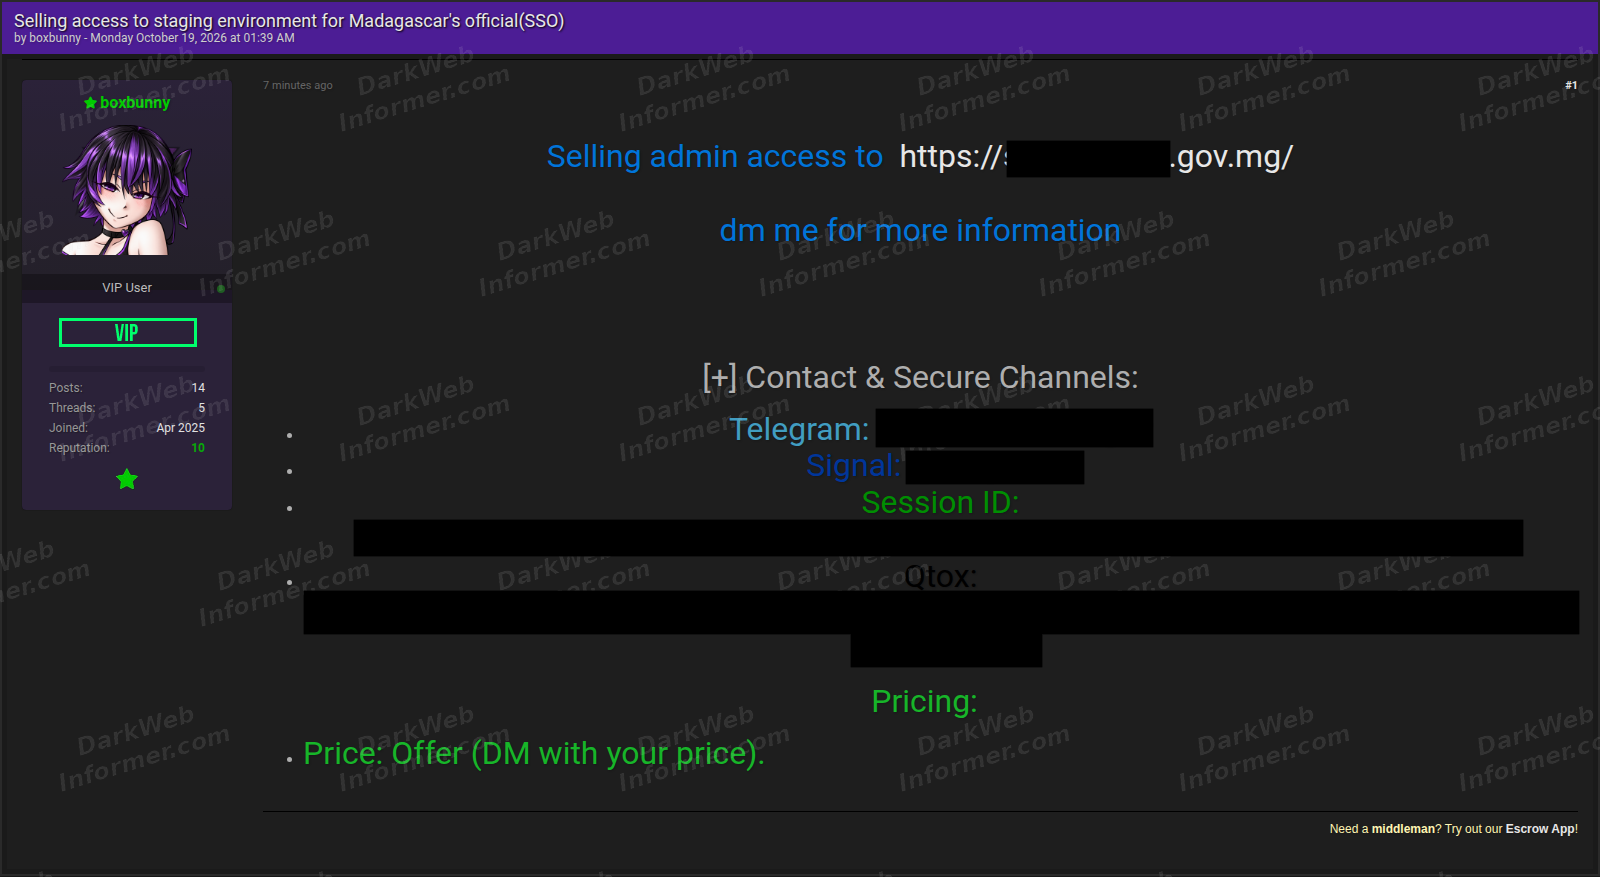
🚨🇲🇬 Initial Access: Madagascar Government SSO

A threat actor is advertising admin access to the staging environment of Madagascar’s government SSO infrastructure.

This claim is currently unverified.

💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Media attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original

The Kid Who Hacked America

This is the story of Kevin Mitnick, one of the most notorious hackers in history. Portrayed by the media as a dangerous cybercriminal, pursued relentlessly by federal authorities, and feared for his extraordinary ability to infiltrate computer systems.

This video draws heavily from Kevin Mitnick's autobiography, "Ghost in the Wires."

RIP 🩵

Video Credit: youtube.com/@fern-tv

↩ Reply ♡ 0 · ↻ 0 ↗ Original

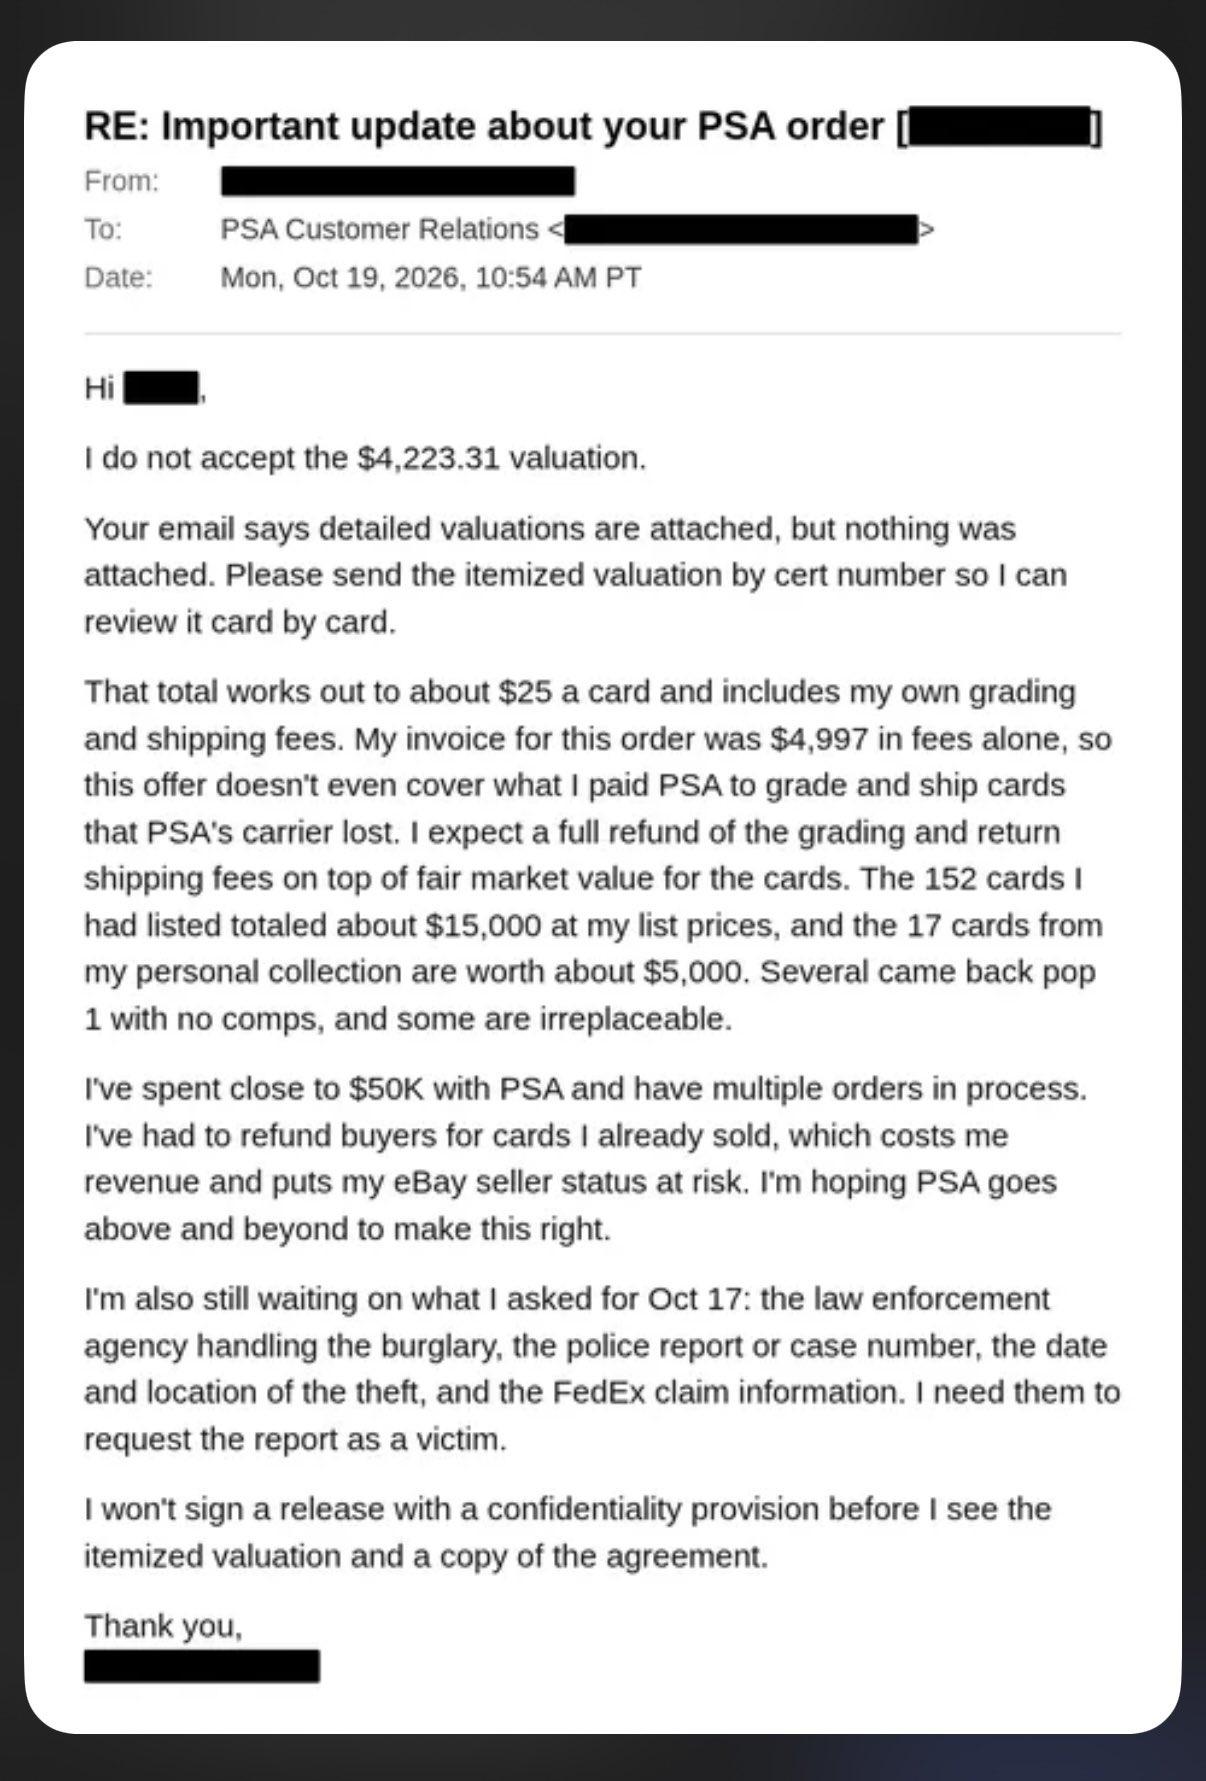
🚨🇺🇸 WILD... PSA-graded trading cards stolen in FedEx vehicle burglary

A FedEx vehicle carrying completed PSA orders was burglarized after leaving the company’s Southern California facility, with multiple collectors reporting that their cards were stolen.
⠀
One collector said a 104-card shipment worth more than $100,000 was taken. Other reported losses include sports, Pokémon, Magic: The Gathering and Yu-Gi-Oh! cards.
⠀
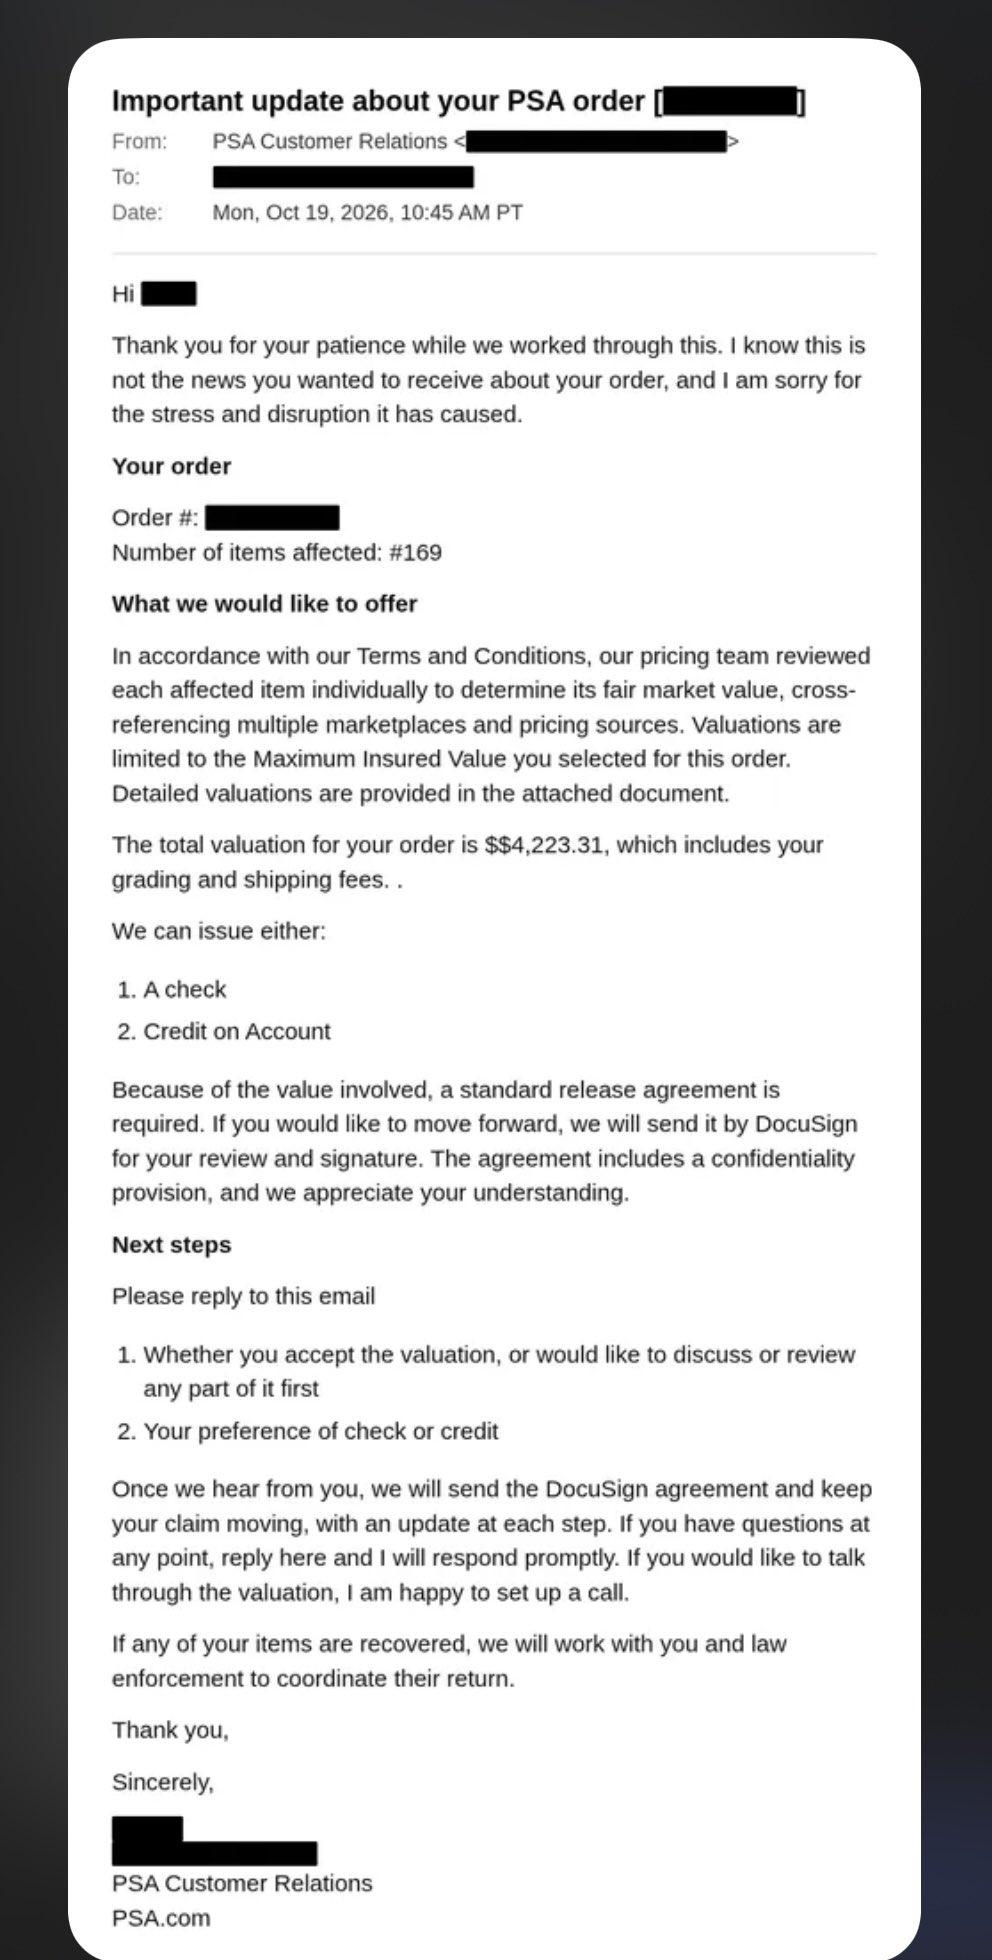
PSA confirmed the theft, deactivated certification numbers linked to the stolen cards and alerted marketplaces to watch for rare and serialized items.

The company is working with FedEx and law enforcement and says affected customers will receive compensation based on fair market value, which I have attached to this post.

The total number and value of stolen cards remain unknown.

Media attachmentMedia attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original

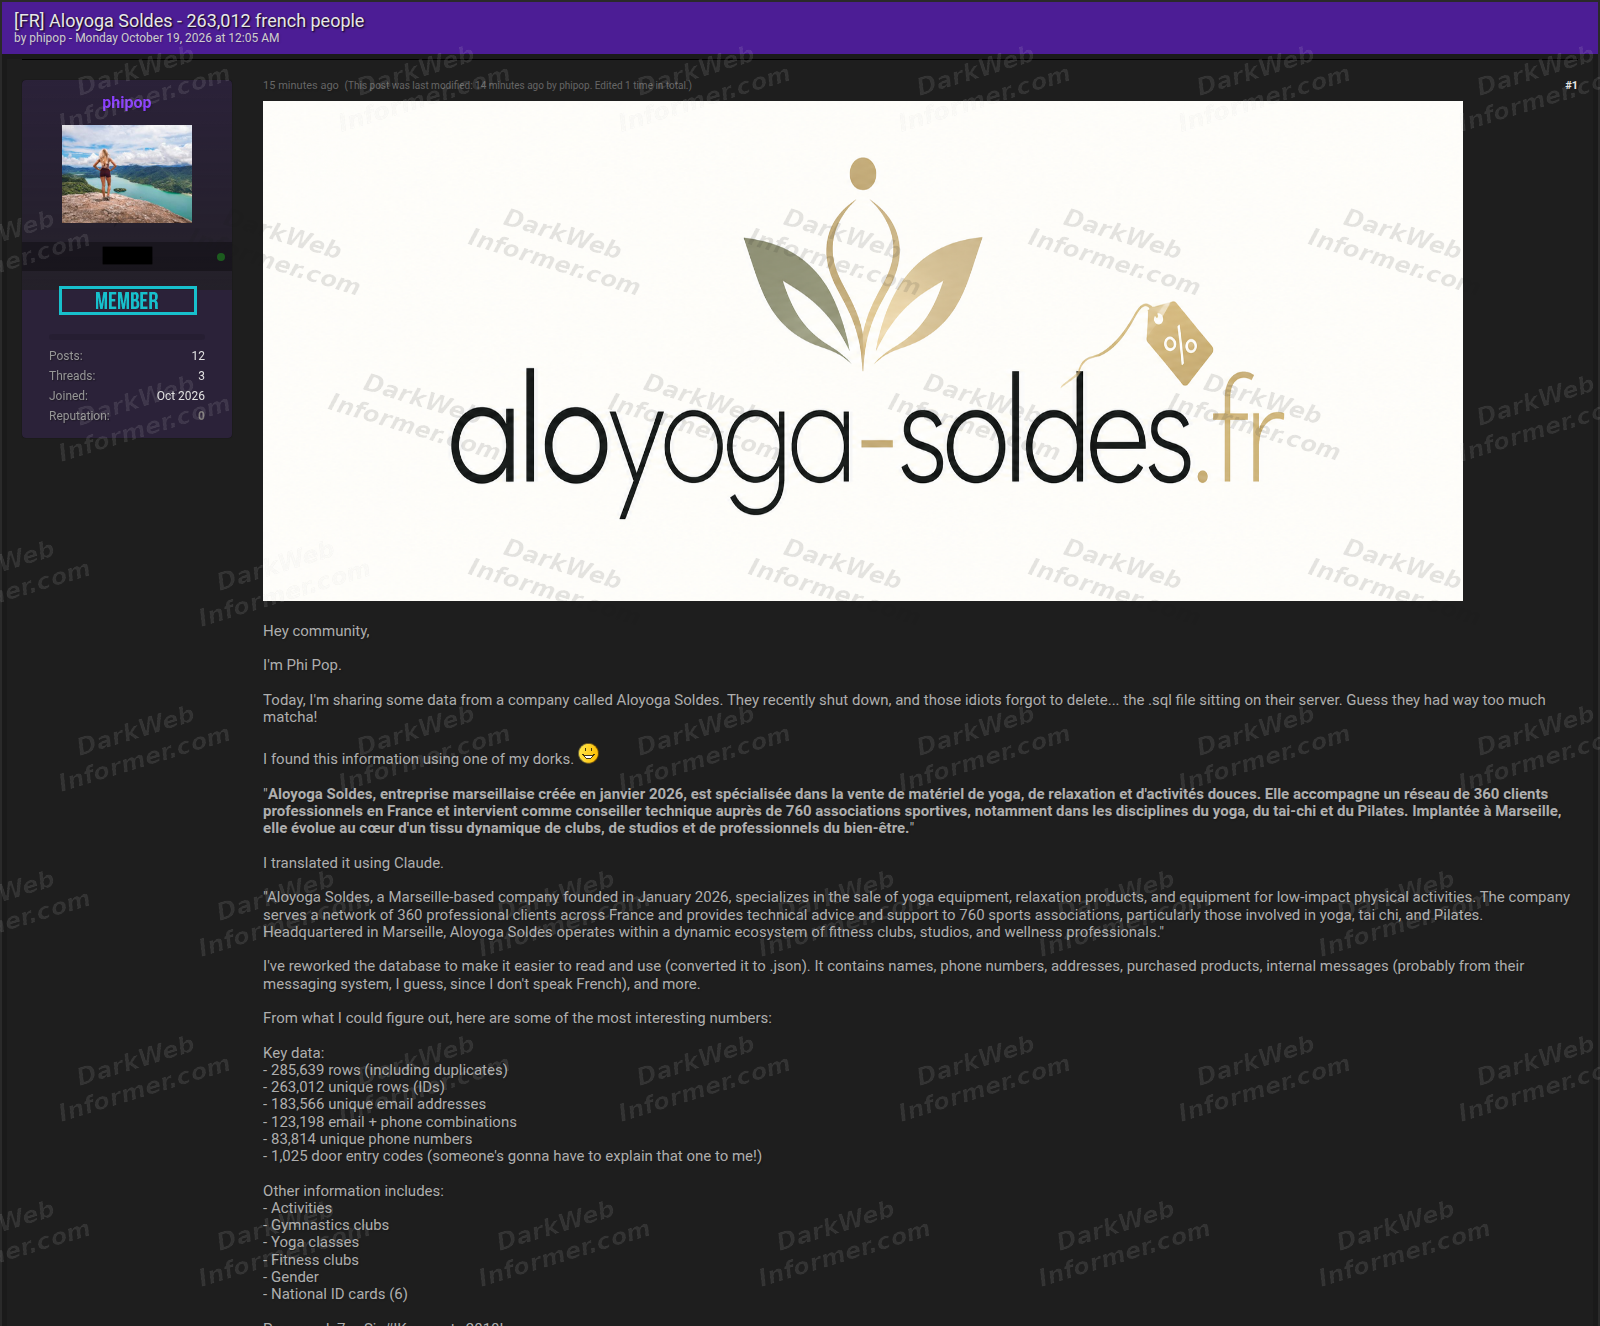
🚨🇫🇷 Aloyoga Soldes dataset containing over 263,000 records leaked

Aloyoga Soldes, a French company specializing in yoga and fitness equipment, has been named in a data leak involving 263,012 unique records.
⠀
The actor "phipop" claims to have discovered an exposed SQL database belonging to the company, which reportedly recently shut down.
⠀
The dataset contains 183,566 unique email addresses, 83,814 phone numbers, customer addresses, purchase information, internal messages, and 1,025 door entry codes.
⠀
The actor has published samples and is offering the dataset for download. Claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Media attachmentMedia attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original

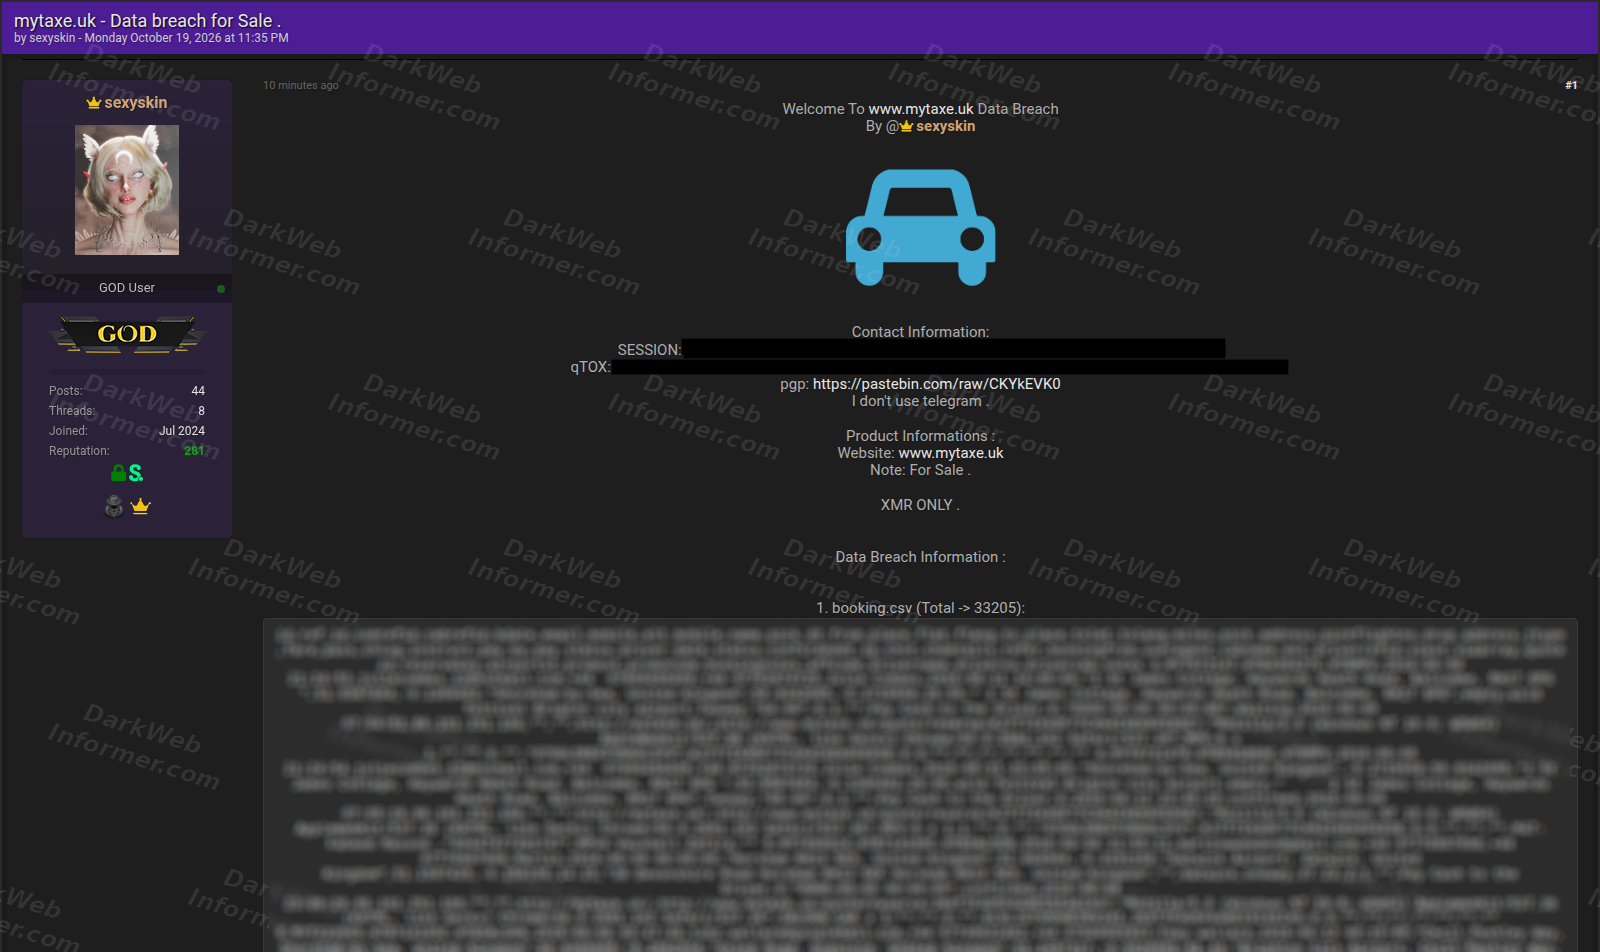
🚨🇬🇧 MyTaxe customer and driver records allegedly leaked, with over 555,000 entries offered for sale

MyTaxe, a UK-based taxi and airport transfer booking service, has been named in a data breach claim involving five CSV files containing approximately 555,000 entries.
⠀
The actor "sexyskin" claims the dataset includes customer names, email addresses, phone numbers, booking histories, pickup and drop-off locations, payment information, and driver records.
⠀
The seller has published samples covering bookings, quotations, driver information, notifications, and member accounts.

The alleged breach and authenticity of the data remain unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Media attachmentMedia attachmentMedia attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original

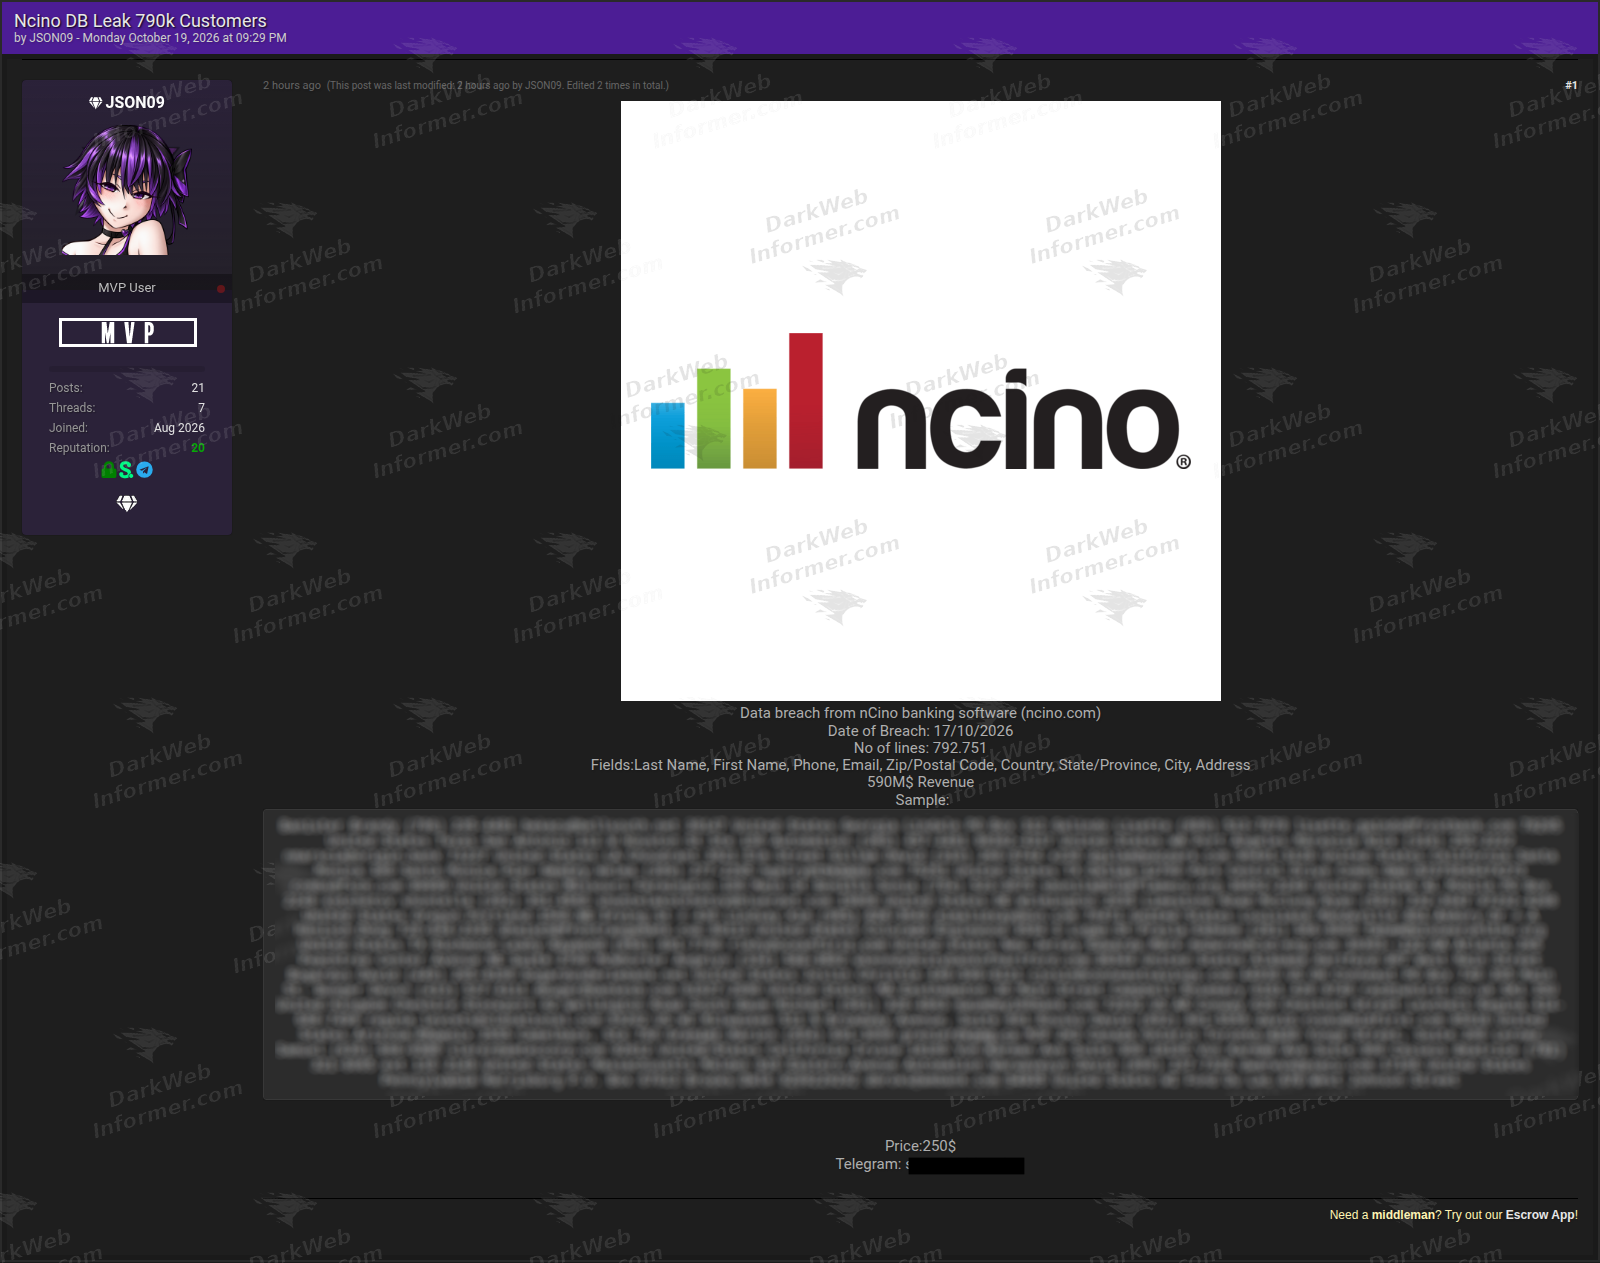
🚨🇺🇸 nCino customer dataset containing nearly 793,000 records allegedly leaked

nCino, a U.S.-based company providing cloud banking software to financial institutions, has been named in a data breach claim involving 792,751 records.
⠀
The actor "JSON09" claims the dataset contains customer names, phone numbers, email addresses, residential addresses, postal codes, and location information.
⠀
The seller has published sample records and is offering the dataset for $250. The alleged breach and origin of the information remain unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Media attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original

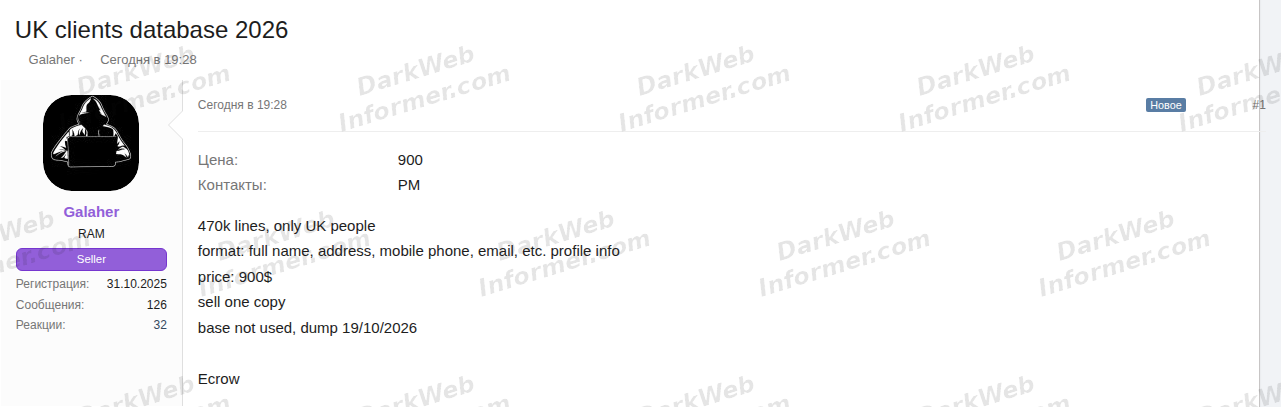
🚨🇬🇧 Dataset containing 470,000 UK customer records advertised for $900
⠀
The records reportedly include full names, residential addresses, mobile phone numbers, email addresses, and other profile information.
⠀
The seller claims the dataset is previously unused, dated October 19, 2026, and will be sold to only one buyer for $900.

The authenticity and origin of the records remain unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Media attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original

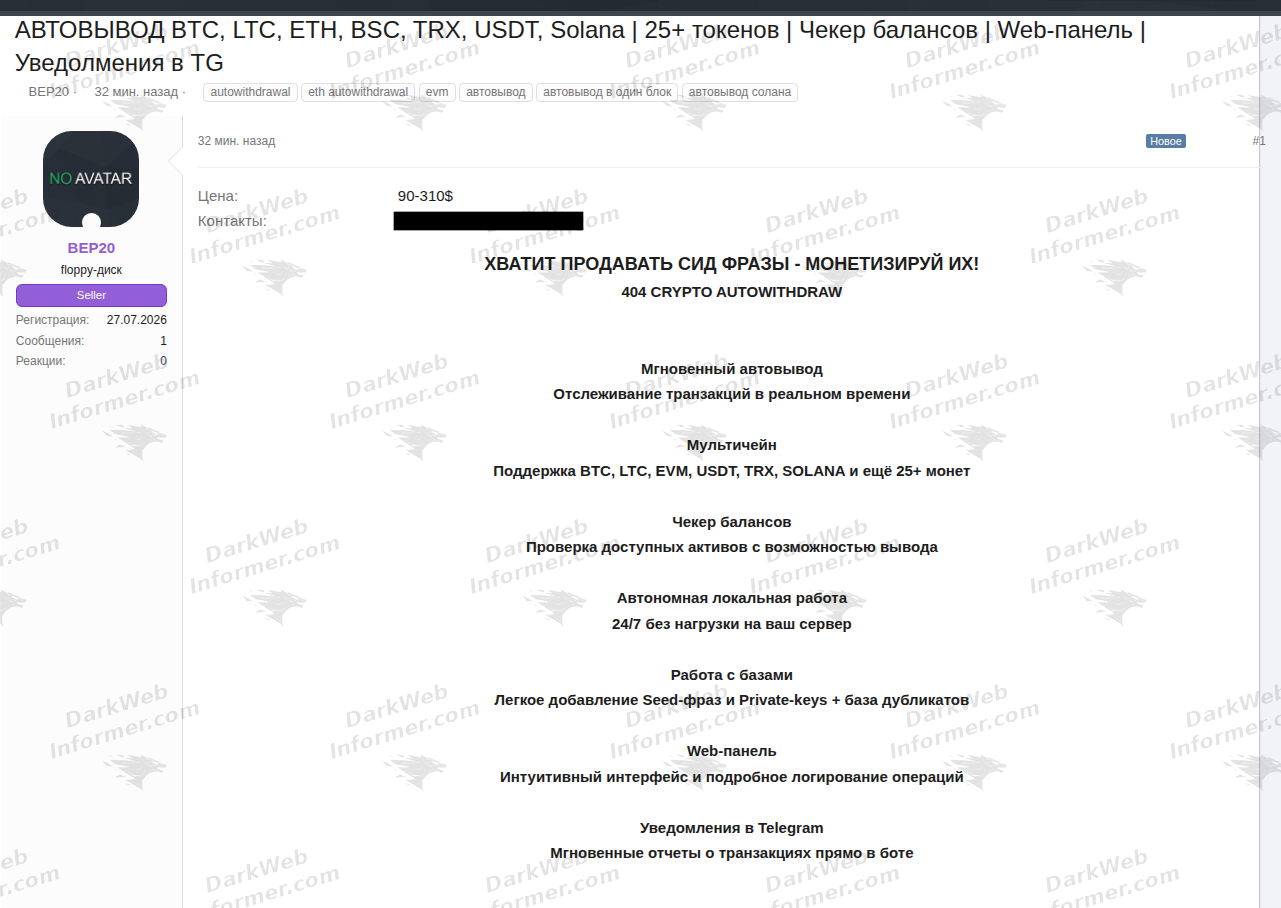
🚨 Cryptocurrency theft tool advertised for $90 to $310, supports automatic withdrawals across 25+ cryptocurrencies

An actor known as "BEP20" is advertising "404 Crypto AutoWithdraw," a tool designed to automatically drain cryptocurrency wallets using stolen seed phrases and private keys.
⠀
The software reportedly supports Bitcoin, Ethereum, Litecoin, Solana, TRON, USDT, and more than 25 cryptocurrencies. It includes wallet balance checking, automatic withdrawals, real-time transaction monitoring, and Telegram notifications.
⠀
The seller also advertises a web dashboard and the ability to import large collections of compromised wallet credentials. The tool's advertised capabilities remain unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Media attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🚨 Malicious Rank Math PRO update delivered a self-restoring WordPress backdoor

Copies of Rank Math PRO 3.0.123 downloaded or installed through updates between October 15 at 20:02 UTC and October 16 at 07:12 UTC contained malware.
⠀
Activated copies could create persistent backdoors, administrator accounts, scheduled tasks and other malicious files. Credentials, database passwords and API keys accessible to compromised sites may also have been exposed.
⠀
Tracked as CVE-2026-111862, the incident carries a CVSS score of 9.8.

Rank Math released a clean version, 3.0.124, but updating alone does not remove backdoors already planted elsewhere. Affected websites should be treated as compromised and restored from a clean backup where possible.

The free Rank Math plugin available through WordPress.org was not affected.

Media attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original

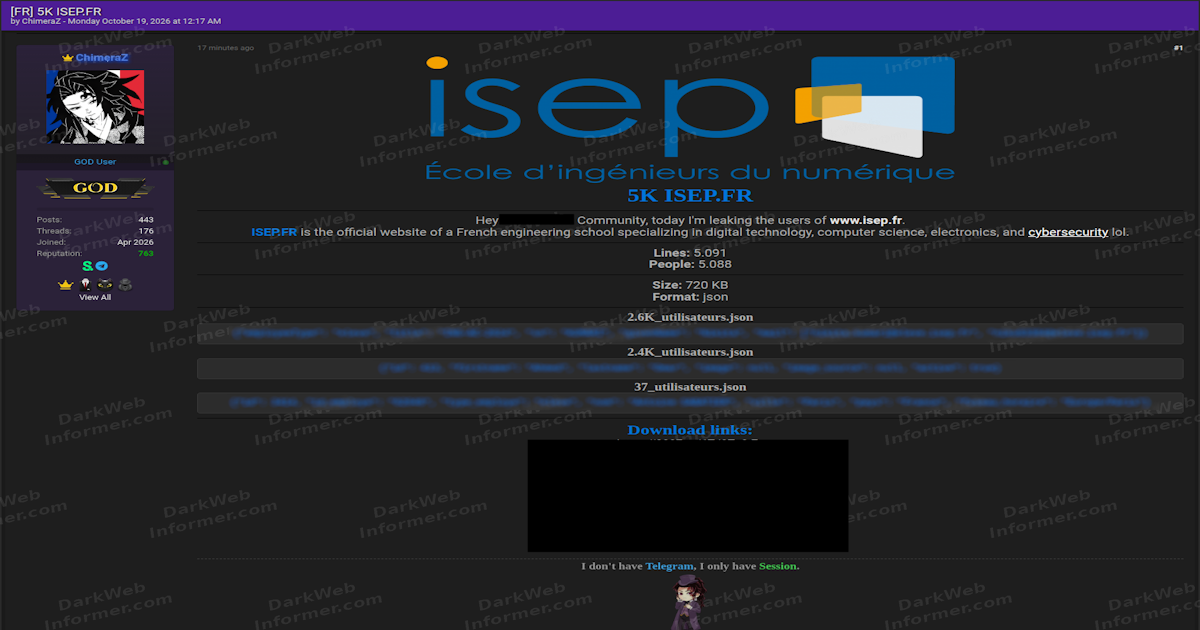
‼️ New Dark Web Informer Blog Post!

Title: ISEP France User Database Leak Claim Lists 5,088 People Across 5,091 JSON Records

Link: https://darkwebinformer.com/isep-france-user-database-leak-claim-lists-5-088-people-across-5-091-json-records/

💥 Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing

Dark Web InformerISEP France User Database Leak Claim Lists 5,088 People Across 5,091 JSON RecordsAn actor using the handle "ChimeraZ" claims to have leaked a user dataset associated with ISEP, a French engineering school specializing in digital technology, computer science, electronics and cybersecurity.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

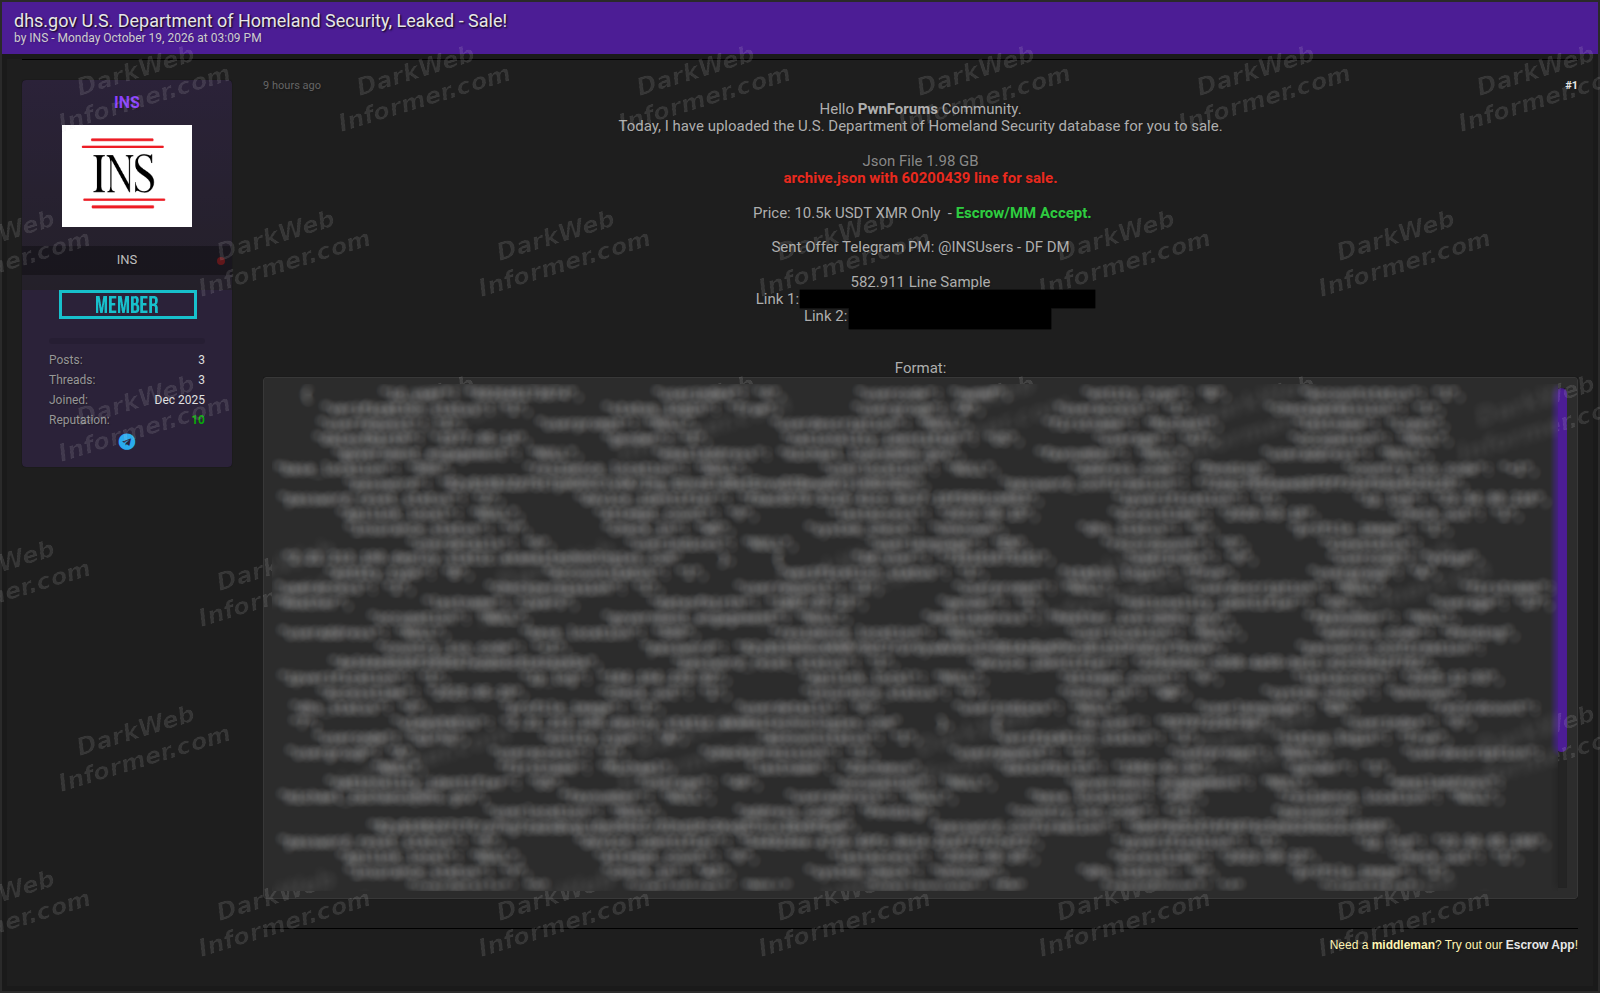
🚨🇺🇸 U.S. Department of Homeland Security dataset containing over 6 million records advertised for $10,500

An actor known as "INS" claims to have obtained a 1.98 GB dataset linked to the U.S. Department of Homeland Security (DHS), containing approximately 6.02 million records.
⠀
The published sample includes names, dates of birth, government email addresses, password hashes, IP addresses, and account verification details.
⠀
The actor has released a sample containing 582,911 records and is offering the full dataset for $10,500. The alleged DHS compromise and authenticity of the records remain unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Media attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original