X XFediYour place in the Fediverse
XFEDI

Remote profile

ActivityPub
Profile banner

Infoblox Threat Intel

@[email protected]

This account is shared by Infoblox Threat Intel researchers including Axur research team. We analyze data and create algorithms to find malicious and suspicious domains and IPs, using DNS.

Open remote profile ↗
Posts

During our research into Help TDS, we called into the tech support scam they are driving victims to. In the call, the scammer directed us to download the free remote access tool UltraViewer. That sparked a side quest: what made UltraViewer the remote desktop tool of choice? Pulling on that thread exposed a broader ecosystem of abuse...

https://www.infoblox.com/blog/threat-intelligence/the-ultra-trail-from-viewer-to-mailer/
#techsupportscam #UltraViewer #UltraMailer #threatintel #rat #malware #infoblox

Infoblox BlogInvestigating Abuse of Remote Desktop and Bulk Mailing AppsHow DNS analysis linked the use of UltraViewer and UltraMailer to tech support scams, QuickBooks lookalike domains, and trojanized installers delivering njRAT.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Illegal gambling operators have a reputation problem. Threat actors found a workaround: borrow someone else's.

In our latest report, we examine how threat actors shadowed government and education domains, including schools and an Indian state government, and turned them into launchpads for parasitic SEO. By hiding gambling-related content under trusted institutions, they inherit the authority those domains have earned with search engines.

Borrowed reputation. Real abuse.

https://www.infoblox.com/blog/threat-intelligence/borrowed-reputation-domain-shadowing-and-gambling-seo/

#DNS #ThreatIntel #CyberSecurity #InfoSec #DomainShadowing #SEO #HiddenHawk #Infoblox

Infoblox BlogDomain Shadowing: Attackers Abuse Institutional DomainsRead how threat actors have gained access to high reputation domains, including ones from government and schools, to steal reputation for illegal gambling SEO.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Seasonal Offer: Free Streaming and TV Services in Exchange for Remote Access to your Device

A cluster involved in the distribution of RATs through paid ads, tracked by our team as Nova YuanKong, has been intensifying its presence in Latin America and the United States.

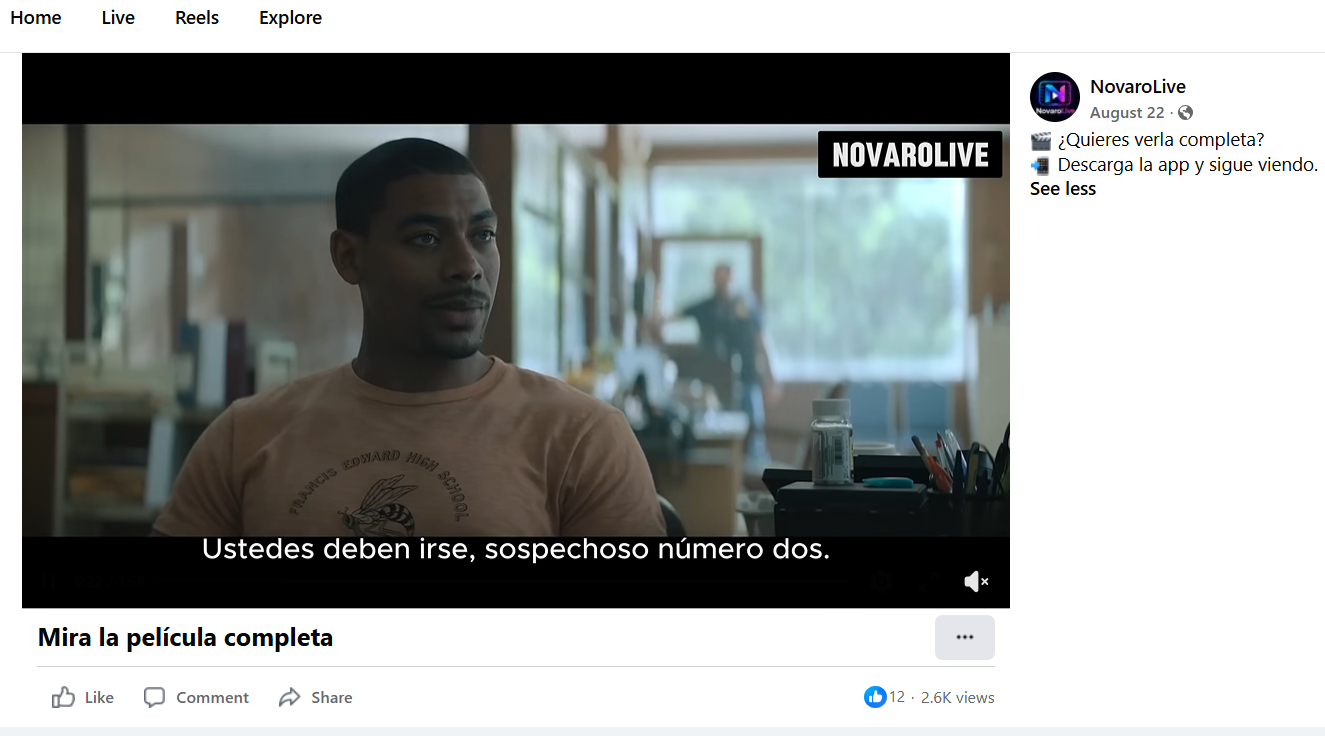
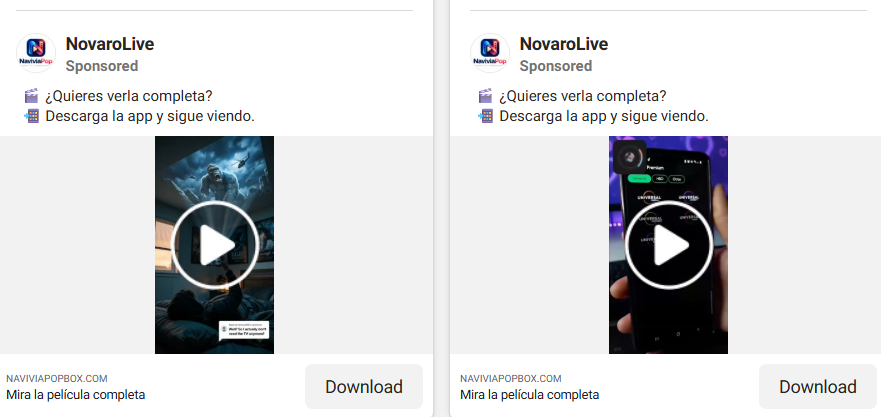
These ads, initially published on platforms such as Meta Ads, offer users the chance to access free streaming and TV services through suspicious websites.

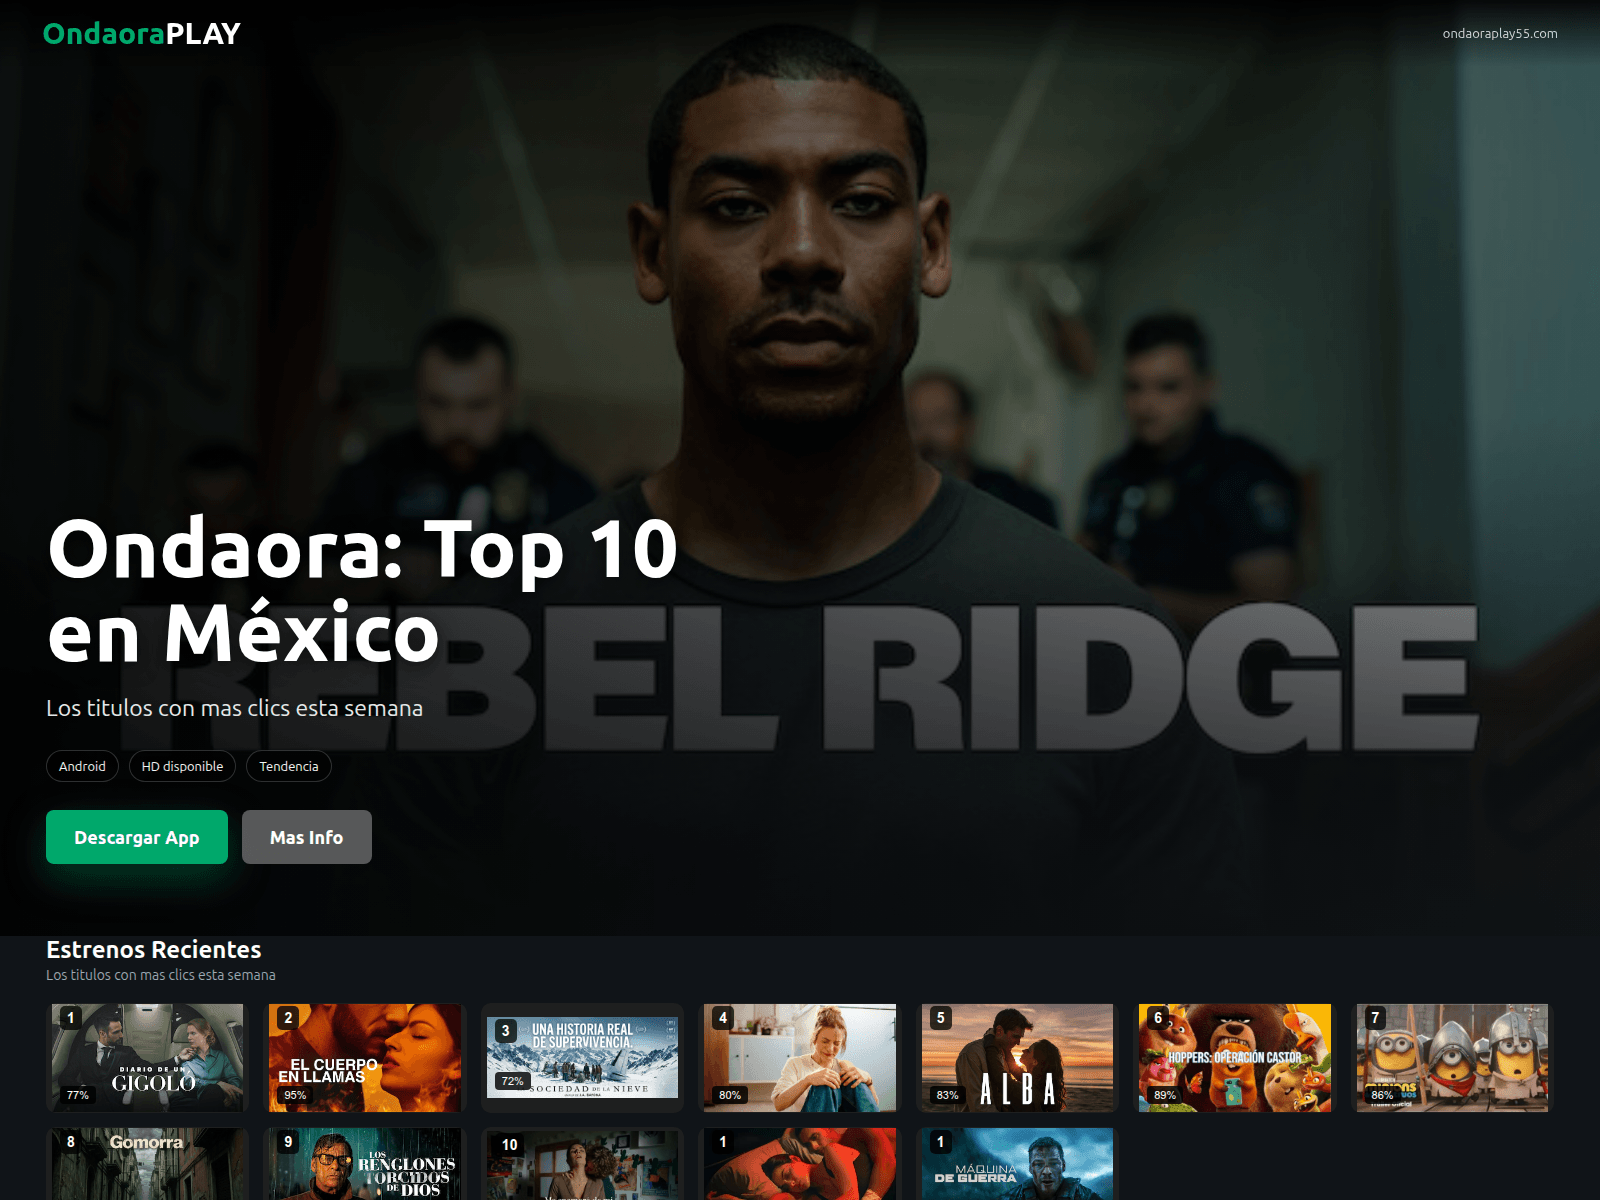
Once users access the advertised websites, they are tricked into downloading an .APK file, supposedly to gain access to the free streaming and TV service.

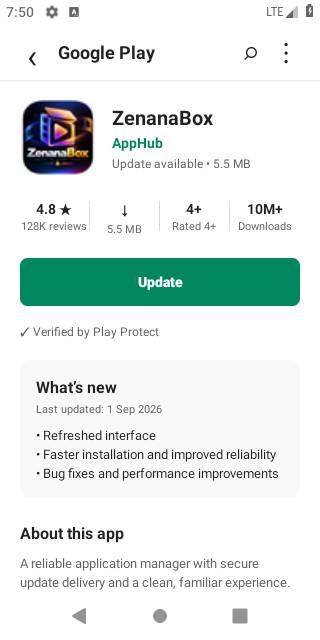
The app, initially intended for viewing multimedia content, turns out to be a dropper/loader. Its job is to look like a legitimate app, evade antivirus software, and, above all, install the RAT without raising suspicion. It impersonates apps from well-known brands, such as Netflix, or from banks based throughout the Americas, and is installed via a fake screen that mimics a Google Play update. Once the primary .APK is installed, it decrypts an encrypted vault containing the child file (child.apk), which then installs the RAT.

The RAT requests accessibility permissions, and once it has the required access—through a wireless debugging step that it automates on its own—the operator gains nearly everything they need, such as screen monitoring, data capture, etc.

Websites related to the cluster use names that follow the pattern "brand + app|play|box|hub|media|live|now|pop" under TLDs such as .com, .xyz, .net, .click, or .site.

C2:
ktxapp[.]com - Primary C2
ktx123[.]net - Backup C2
ktx789[.]com - Associated domain
ktx456[.]com - Associated domain
apppanda[.]xyz - Legacy C2
206.82.1[.]14 - C2 IP

墨影 V2 Panel
cctvv3[.]com
cctvv7[.]com
topasd[.]com
g8688808[.]com
baozi1[.]com

#malvertising #rat #malware #dns
Media attachmentMedia attachmentMedia attachmentMedia attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Oh... turns out we never posted our research released last week. That work unmasked the affiliate program behind Help TDS and how it works.

Perhaps more interesting was how one of our data scientists was able to detect the C2 domains an average of a week in advance. These ran on Cloudflare Pages and the actor used about a dozen domain generation algorithms... a combination that creates a formidable problem.

https://www.infoblox.com/blog/threat-intelligence/inside-help-tds-hotejka-cloudflare-pages-and-predictive-detection/

#malware #phishing #scam #techsupportScam #wordpress #malware #dga

Infoblox BlogInside Help TDS: Hotejka and Cloudflare AbuseInfoblox attributes Help TDS to Hotejka and detects 16,000 malicious Cloudflare Pages before they are used to direct users to tech support scam call centers.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

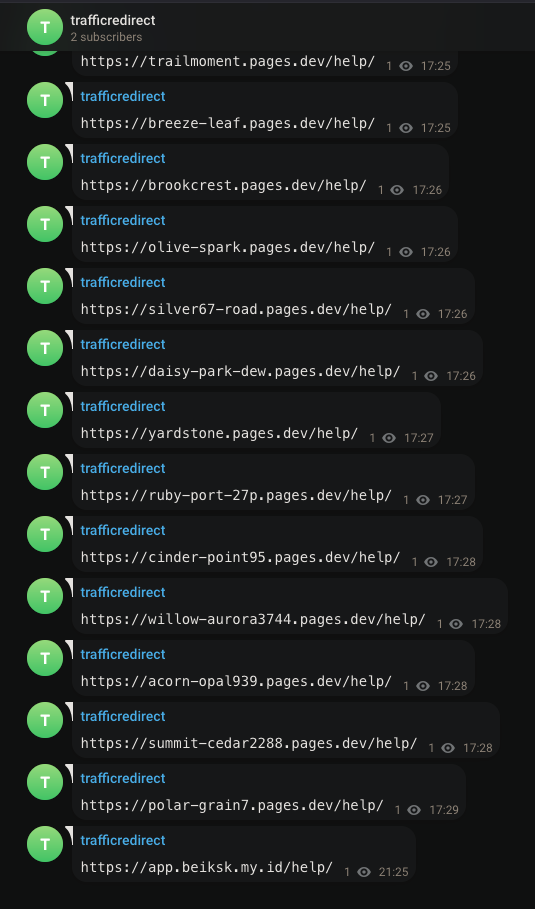
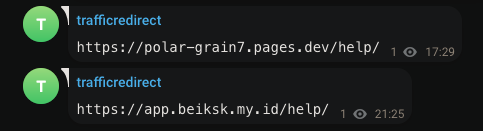
Hotejka's Help TDS had a bit of kernel panic thrashing today. Posting new C2 domains to their Telegram channel every minute instead of normal 5 minute cadence. After months of living off Pages, they seem to have given up and gone back to my.id domains. yes, hosted on cloudflare CDN still but not on Cloudflare Pages.

Very long story short..these guys run a tech support scam operation, cloaked with Keitaro and driving victims to call centers where they are led to download remote access software (ultraviewer).

They run an affiliate program which has some of most prolific actors... #balada #dollyway #detourdog and more...

here's some domains to block as we're quite sure they'll be forced to stay on my.id until they figure something else out.

satesailiki[.]my[.]id
sateiliki[.]my[.]id
jendareok[.]my[.]id
tytmemiliki[.]my[.]id
jenggfdlirrcok[.]my[.]id
feemiliki[.]my[.]id
je5neelirrcok[.]my[.]id
jenggfdetemiliki[.]my[.]id
effectsden[.]my[.]id
dadarethk[.]my[.]id
effdeectsden[.]my[.]id
library1library[.]my[.]id
pkgm620[.]my[.]id
jeneelif3rrcok[.]my[.]id
beiksk[.]my[.]id
jenggfdetearrcok[.]my[.]id
jeneelirrcok[.]my[.]id
hteermemiliki[.]my[.]id
jenggecok[.]my[.]id
satesfaailiki[.]my[.]id
my22library[.]my[.]id
hafcocok[.]my[.]id
jeniscouuutok[.]my[.]id
mydomlibrary[.]my[.]id
jenggfdetecok[.]my[.]id
lawyetteiki[.]my[.]id
reeelirrcok[.]my[.]id
jenggetecok[.]my[.]id
belirryercok[.]my[.]id
fedmy22library[.]my[.]id

link to our latest research on these losers.

https://www.infoblox.com/blog/threat-intelligence/inside-help-tds-hotejka-cloudflare-pages-and-predictive-detection/

#malware #phishing #scam #techsupportScam #wordpress #malware

Media attachmentMedia attachment
Infoblox BlogInside Help TDS: Hotejka and Cloudflare AbuseInfoblox attributes Help TDS to Hotejka and detects 16,000 malicious Cloudflare Pages before they are used to direct users to tech support scam call centers.
↩ Reply ♡ 0 · ↻ 0 ↗ Original