X XFediYour place in the Fediverse
XFEDI

Remote profile

ActivityPub
Profile banner

BeyondMachines :verified:

@[email protected]

Enabling Good Cybersecurity for Everyone:
Automated cybersecurity tools, learning and expert guidance for individuals and companies of all sizes.
Because cybersecurity shouldn't be an enterprise feature.
Sometimes a bot, sometimes not.

Open remote profile ↗
Posts

OpenCode Console Breach Exposes AI Provider API Keys in Distillation-Linked Attack

OpenCode disclosed a breach affecting its cloud-based Console after attackers accessed a legacy system, potentially exposing AI provider API keys belonging to approximately 1.4% of Console users. The company linked the incident to a large-scale model distillation attack and is working with OpenAI, Anthropic, and Google to revoke compromised credentials and address unauthorized charges.

****
#cybersecurity #infosec #incident #databreach
https://beyondmachines.net/event_details/opencode-console-breach-exposes-ai-provider-api-keys-after-legacy-system-compromise-c-6-0-f-4/gD2P6Ple2L
BeyondMachinesOpenCode Console Breach Exposes AI Provider API Keys in Distillation-Linked AttackOpenCode disclosed a breach affecting its cloud-based Console after attackers accessed a legacy system, potentially exposing AI provider API keys belonging to approximately 1.4% of Console users. The company linked the incident to a large-scale model distillation attack and is working with OpenAI, Anthropic, and Google to revoke compromised credentials and address unauthorized charges.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

State of (in)security - Week 42, 2026

In week 42 of 2026 (Oct. 12–19), incidents rose to 39 from 25 while advisories fell to 15 from 22. Known impacted individuals more than doubled to about 26.7 million. Highest breach was BK Japan's 11.18 million-record breach. Unauthorized access (12) and ransomware/malware (9) were the main causes of incidents. Healthcare (8) and tech (7) were the most-hit sectors. Actively exploited flaws reported in Ivanti, Palo Alto PAN-OS, Citrix NetScaler, Cisco, BeyondTrust, SonicWall and Zimbra, plus a Microsoft zero-day.

**Update Chrome to version 155.0.8059.79 or later, and any other Chromium-based browser you use (Edge, Brave, Opera, Vivaldi), and restart it ASAP. A malicious website, PDF, or even an ad on a trusted news site can take over your browser without a click, so keep automatic updates on for your browser, phone, computer and apps (on Android, include "Android System WebView") and add a trusted ad-blocker like uBlock Origin.**
#cybersecurity #infosec #knowledge #weeklyreport
https://beyondmachines.net/event_details/state-of-in-security-week-42-2026-s-g-o-m-1/gD2P6Ple2L

BeyondMachinesState of (in)security - Week 42, 2026In week 42 of 2026 (Oct. 12–19), incidents rose to 39 from 25 while advisories fell to 15 from 22. Known impacted individuals more than doubled to about 26.7 million. Highest breach was BK Japan's 11.18 million-record breach. Unauthorized access (12) and ransomware/malware (9) were the main causes of incidents. Healthcare (8) and tech (7) were the most-hit sectors. Actively exploited flaws reporte
↩ Reply ♡ 0 · ↻ 0 ↗ Original

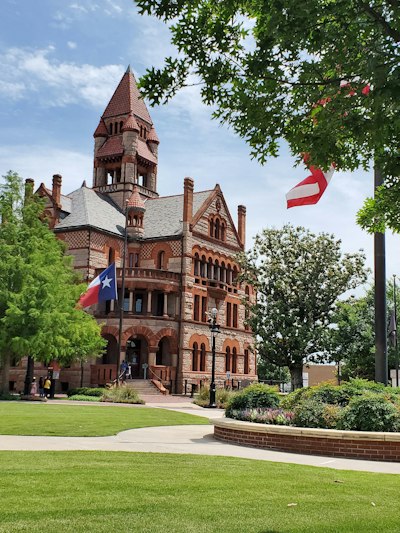
NightSpire Ransomware Claim Follows Colorado County System Disruption

Colorado County, Texas, reported a disruption affecting government systems and potentially threatening essential public services. The NightSpire ransomware group claimed responsibility for the disruption

****
#cybersecurity #infosec #incident #ransomware
https://beyondmachines.net/event_details/nightspire-ransomware-claim-follows-colorado-county-system-disruption-o-d-n-s-s/gD2P6Ple2L

BeyondMachinesNightSpire Ransomware Claim Follows Colorado County System DisruptionColorado County, Texas, reported a disruption affecting government systems and potentially threatening essential public services. The NightSpire ransomware group claimed responsibility for the disruption
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Frazer LLP Discloses 2025 Qilin Ransomware Attack and Data Theft

Frazer LLP, a California accounting firm, confirmed a ransomware attack which occurred in March 2025 claimed by the Qilin group. The firm is offering identity protection services to affected clients.

****
#cybersecurity #infosec #incident #ransomware
https://beyondmachines.net/event_details/frazer-llp-discloses-2025-qilin-ransomware-attack-and-data-theft-k-z-7-2-i/gD2P6Ple2L

BeyondMachinesFrazer LLP Discloses 2025 Qilin Ransomware Attack and Data TheftFrazer LLP, a California accounting firm, confirmed a ransomware attack which occurred in March 2025 claimed by the Qilin group. The firm is offering identity protection services to affected clients.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

F5 Issues Emergency Patches for Critical NGINX Code Execution Flaws

F5 released emergency patches for three critical NGINX vulnerabilities (CVE-2026-15176, CVE-2026-97205, and CVE-2026-93479) that allow unauthenticated remote code execution and denial-of-service attacks.

**If you run NGINX in any form (open-source web server, NGINX Plus, Ingress Controller, Gateway Fabric, or the NGINX WAF/App Protect products), install F5's latest security patches ASAP. If you can't patch, turn off Server Side Includes and asynchronous file I/O, and have your team remove alias directives that use $request_filename and switch regex maps to named captures until the patch is in.**
#cybersecurity #infosec #advisory #vulnerability
https://beyondmachines.net/event_details/f5-issues-emergency-patches-for-critical-nginx-code-execution-flaws-p-9-m-u-w/gD2P6Ple2L

BeyondMachinesF5 Issues Emergency Patches for Critical NGINX Code Execution FlawsF5 released emergency patches for three critical NGINX vulnerabilities (CVE-2026-15176, CVE-2026-97205, and CVE-2026-93479) that allow unauthenticated remote code execution and denial-of-service attacks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original