X XFediYour place in the Fediverse
XFEDI

Remote profile

ActivityPub
Posts

SlowMist traces Qubic wallet theft to weak randomness in seed generation

SlowMist has traced the Qubic wallet theft to weak randomness in seed generation, which undermined the keys protecting user wallets, Crypto Briefing reports. The finding is the root-cause follow-up to the October 18 incident in which an attacker drained 1,404 Qubic wallets and the network paused its mainnet. https://cryptobriefing.com/slowmist-qubic-wallet-key-recovery-flaw/
Crypto BriefingSlowMist traces Qubic wallet theft to weak randomness in seed generationSlowMist says Qubic Wallet used Math.random() for seeds, enabling key recovery tied to the theft of 2.94 trillion QU from 1,404 wallets.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Cybercriminals favor Microsoft over Apple and Google in brand phishing attacks

Microsoft accounted for 33% of brand impersonation attempts tracked by Check Point Research in the third quarter of 2026, up from 23% in the previous quarter, Help Net Security reports. That share is roughly four times that of any other brand in phishing attacks. https://www.helpnetsecurity.com/2026/10/19/check-point-brand-impersonation-scams-q3-2026-report/

Help Net SecurityCybercriminals favor Microsoft over Apple and Google in brand phishing attacks - Help Net SecurityMicrosoft led Q3 2026 brand impersonation scams as attackers used fake AI services and software updates to access victims’ devices.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

OnlyFans Copyright Takedowns Expose Compromised Websites

Copyright takedown requests tied to OnlyFans and other adult content creators are revealing how attackers exploit vulnerable university and government websites to manipulate search results, Dark Reading reports. UpGuard’s Greg Pollock explains what universities, government websites and security teams should take from the pattern. https://www.darkreading.com/vulnerabilities-threats/onlyfans-copyright-takedowns-expose-compromised-websites

www.darkreading.comOnlyFans Copyright Takedowns Expose Compromised WebsitesCopyright takedown requests tied to OnlyFans creators are revealing how attackers exploit vulnerable university and government websites.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

GMO Cybersecurity links Chinese AI tool ARTEX to breaches at Japanese firms

Tokyo-based GMO Cybersecurity by Ierae said on October 19 that it confirmed traces of ARTEX, a Chinese-developed AI penetration-testing tool, on servers used to attack around 20 Japanese companies, Crypto Briefing reports. Eight firms reported data breaches between September and October 2026, and CrowdStrike previously tied the same tool to attacks on South Korean banks in late September. https://cryptobriefing.com/gmo-cybersecurity-artex-ai-tool-japan-breaches/

Crypto BriefingGMO Cybersecurity links Chinese AI tool ARTEX to breaches at Japanese firmsGMO Cybersecurity says Chinese AI pen-testing tool ARTEX was used against about 20 Japanese firms, echoing South Korean bank attacks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

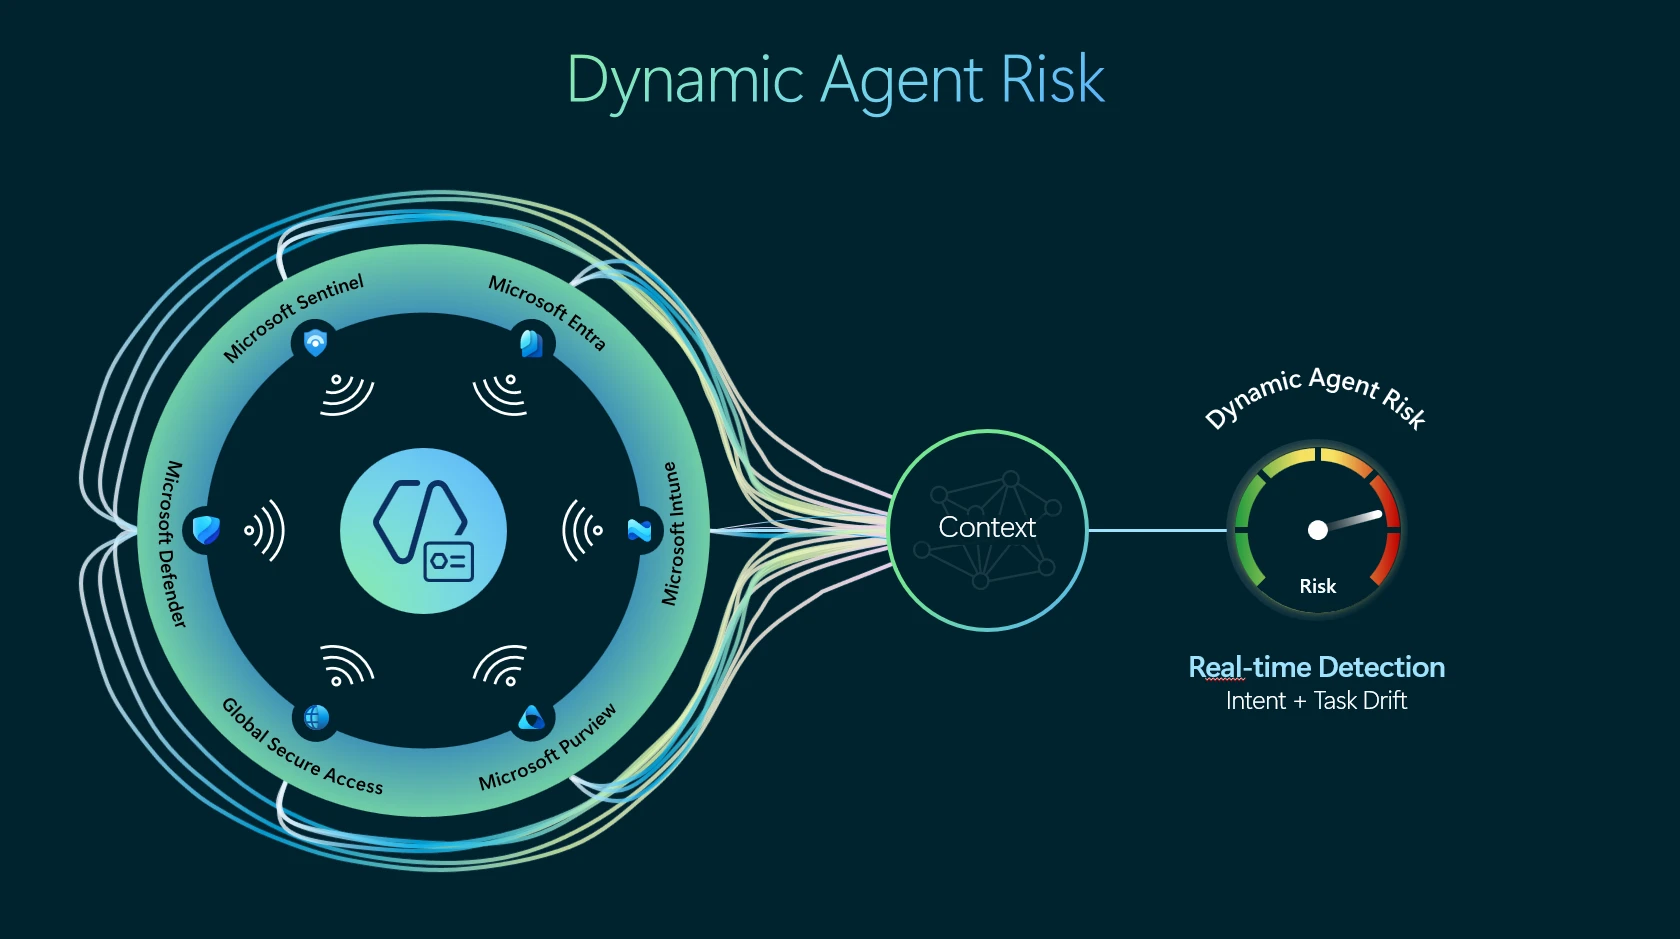
Microsoft Treats AI Agents as Insider Threats in New Security Framework

Microsoft urges organizations to secure AI agents as insider threats, using dynamic permissions, continuous risk monitoring and automated containment, Security Affairs reports. The company published detailed guidance explaining how organizations should secure agents as their access and autonomy grow. SiliconANGLE’s version of the same announcement was dropped as a duplicate. https://securityaffairs.com/201336/ai/microsoft-treats-ai-agents-as-insider-threats-in-new-security-framework.html

Security AffairsMicrosoft Treats AI Agents as Insider Threats in New Security FrameworkMicrosoft urges orgs to secure AI Agents as insider threats, using dynamic permissions, continuous risk monitoring and automated containment.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Your frontline workers have a workaround for that MFA prompt

Frontline workers in healthcare and manufacturing are getting around slow, unreliable logins by staying signed in, sharing credentials and trying to bypass multifactor authentication, Help Net Security reports. In a Sapio Research survey of 700 IT and security decision-makers in August, 95% said they had seen frontline workers using such workarounds. https://www.helpnetsecurity.com/2026/10/20/frontline-worker-authentication-passwordless/

Help Net SecurityYour frontline workers have a workaround for that MFA prompt - Help Net SecurityFrontline worker authentication friction drives credential sharing and MFA bypass attempts as attackers target account resets, survey finds.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Meta wants to scrape your website to train its AI, and you can’t say no

Meta plans to change its commercial terms at the end of the month in a way that would let it scrape websites for AI training, Security Affairs reports. The new language would apply to companies advertising or selling through Meta’s platforms, including business accounts. https://securityaffairs.com/201300/ai/meta-wants-to-scrape-your-website-to-train-its-ai-and-you-cant-say-no.html

Security AffairsMeta wants to scrape your website to train its AI, and you can't say noMeta 's new terms let it scrape business websites for AI training from October 30, raising concerns over copyright, consent and robots.txt.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

MITRE ATT&CK v20 Catalogs AI Abuse, MFA Bypass, Water Utility Attacks

MITRE ATT&CK version 20 catalogues techniques including AI abuse, MFA bypass and water utility attacks, SecurityWeek reports. The release gives defenders 15 new detection strategies, six for Enterprise and nine for ICS, backed by 38 analytics. https://www.securityweek.com/mitre-attck-v20-catalogs-ai-abuse-mfa-bypass-water-utility-attacks/

SecurityWeekMITRE ATT&CK v20 Catalogs AI Abuse, MFA Bypass, Water Utility AttacksMITRE released ATT&CK v20 with new techniques covering AI prompt injection, MFA bypass, and water utility breaches across Enterprise and OT.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Bullhorn takes staffing platform offline to contain cyberattack

Staffing software company Bullhorn has disabled access to its platform to contain a cyberattack that caused a system-wide outage, BleepingComputer reports. Bullhorn says it has isolated the issue and eradicated the immediate threat, is restoring services with help from CrowdStrike specialists, and has not yet determined whether customer data was exfiltrated. https://www.bleepingcomputer.com/news/security/bullhorn-takes-staffing-platform-offline-to-contain-cyberattack/

BleepingComputerBullhorn takes staffing platform offline to contain cyberattackStaffing software company Bullhorn has disabled access to its platform to contain a cyberattack that caused a system-wide outage.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Hackers hijack AOMEI update servers to secretly spread malware

Hackers reportedly compromised AOMEI’s servers to distribute malware through a built-in promotional feature in its backup software, BleepingComputer reports. The attackers briefly tampered with configuration files before restoring them to their original state to hide the activity, and Malwarebytes reports the tampered update system delivered malware that could give attackers remote access to users' PCs. https://www.bleepingcomputer.com/news/security/hackers-hijack-aomei-update-servers-to-secretly-spread-malware/

BleepingComputerHackers hijack AOMEI update servers to secretly spread malwareHackers reportedly compromised AOMEI's servers to distribute malware through a built-in promotional feature in its backup software, briefly tampering with configuration files before restoring them to their original state to hide the attacks.a
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Nikkei discloses third data breach in a month, 1.8M records exposed

Nikkei Inc. has disclosed a data breach, its third in about a month, exposing 1.83 million personal information records after hackers used stolen credentials to access a development system on October 7, BleepingComputer reports. About 150,000 records contained identifying details such as names, email addresses, physical addresses, telephone numbers and dates of birth, and Nikkei says it has no evidence the data was misused or leaked online. https://www.bleepingcomputer.com/news/security/nikkei-discloses-third-data-breach-in-a-month-18m-records-exposed/

BleepingComputerNikkei discloses third data breach in a month, 1.8M records exposedNikkei Inc. disclosed a new data breach, the third in about a month, that exposed 1.83 million personal information records.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Grocery giant Ahold Delhaize confirms cyberattack forced US and European systems offline

Ahold Delhaize has confirmed that a cyberattack led it to take IT systems, including websites and apps, offline across most of its US and European brands, The Register reports. The company says its stores remain open and that its investigation has so far found no evidence that sensitive customer, associate, or partner data was stolen. https://www.theregister.com/security/2026/10/19/grocery-giant-ahold-delhaize-confirms-cyberattack-forced-us-and-european-systems-offline/5303970

theregisterGrocery giant Ahold Delhaize confirms cyberattack forced US and European systems offlineSecond security snafu in two years
↩ Reply ♡ 0 · ↻ 0 ↗ Original

ICANN testing tech to let law enforcement access non-public WHOIS info

ICANN is testing SAML-based authentication that would let law enforcement agencies file urgent requests for non-public WHOIS data through its Registration Data Request Service, The Register reports. The mechanism is aimed at cases involving imminent threats to life, critical infrastructure, or child exploitation, with registrars given 24 to 72 hours to respond or deny requests that do not meet the urgency threshold. https://www.theregister.com/networks/2026/10/20/icann-testing-tech-to-let-law-enforcement-access-non-public-whois-info/5304036

theregisterICANN testing tech to let law enforcement access non-public WHOIS infoSingle sign-on to help address imminent threats to life, critical infrastructure, or kids
↩ Reply ♡ 0 · ↻ 0 ↗ Original

DeepSeek deep-sixed at all US federal civilian agencies

The US Department of Homeland Security has ordered federal civilian agencies to stop using DeepSeek products and remove existing implementations, The Register reports. The order also covers third-party products and services developed using DeepSeek, which security experts quoted in the piece say is too vague to verify in practice. https://www.theregister.com/security/2026/10/20/deepseek-deep-sixed-at-all-us-federal-civilian-agencies/5304010

theregisterDeepSeek deep-sixed at all US federal civilian agenciesOrder disallowing use of Chinese AI service is unhelpfully vague and broad
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Glassworm Hacks OVH Clouds CLI tool

Attackers using a GitHub account hijacked from an OVHcloud contributor replaced the release binaries of five versions of OVHcloud’s official CLI tool with a secret-stealing build on October 19, OpenSourceMalware reports. The tampered files were available for about 94 minutes before a downstream user’s checksum check caught them, and OVHcloud deleted them and shipped a clean release. https://opensourcemalware.com/blog/glassworm-hacks-ovh-clouds-cli-tool

opensourcemalware.comGlassworm Hacks OVH Clouds CLI toolOn 2026-10-19, the official OVHcloud CLI tool was compromised by the Glassworm threat actors who published five malicious versions to GitHub and Brew
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Threat Brief: Active Exploitation of PAN-OS CVE-2026-0257

Ransomware operators including Qilin and Inc are actively exploiting CVE-2026-0257, a GlobalProtect authentication bypass in Palo Alto Networks PAN-OS, Unit 42 reports in an October 19 update. Attackers use the flaw to establish VPN sessions that bypass MFA, and in one case moved from the gateway to the victim’s vCenter to dump domain credentials from a virtual disk. https://unit42.paloaltonetworks.com/active-exploitation-of-pan-os-cve-2026-0257/

Unit 42Threat Brief: Active Exploitation of PAN-OS CVE-2026-0257 (Updated October 19)Ransomware operators including Spikey Scorpius (aka Qilin) and Tarnished Scorpius (aka Inc) are exploiting PAN-OS vulnerability CVE-2026-0257.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Popular WordPress SEO Plugin Rank Math PRO Hijacked to Deliver Self-Restoring Backdoor

Copies of the paid Rank Math PRO WordPress plugin downloaded from rankmath.com or delivered as updates between October 15 and 16 contained malware that installs a self-restoring backdoor, The Hacker News reports. Rank Math has released a clean version, but Wordfence warns that updating alone does not remove backdoor files, administrator accounts, or scheduled tasks the malware may have left behind. https://thehackernews.com/2026/10/popular-wordpress-seo-plugin-rank-math.html

The Hacker NewsPopular WordPress SEO Plugin Rank Math PRO Hijacked to Deliver Self-Restoring BackdoorRank Math PRO distributed malware for 11 hours, exposing WordPress sites that activated affected builds to persistent backdoors.
↩ Reply ♡ 0 · ↻ 0 ↗ Original