X XFediYour place in the Fediverse
XFEDI

Remote profile

ActivityPub
Profile banner

eShard

@[email protected]

Beyond testing tools, solutions that deliver expertise.

Open remote profile ↗
Posts

Next in our drone security series: having the right security mechanisms doesn't always mean they'll withstand a physical attack.

From encryption to secure boot and readout protection, we explore why testing the actual implementation matters.

https://www.eshard.com/blog/drone-security-physical-attack-testing

#drone #drones #cybersecurity #hardware #embedded #embeddedsystems #firmware
www.eshard.comWhen Secure Drone Designs Meet Physical Attacks | #4 | eShardEncryption and secure boot aren't enough on their own. Discover why drone security needs physical attack testing to validate its protections.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

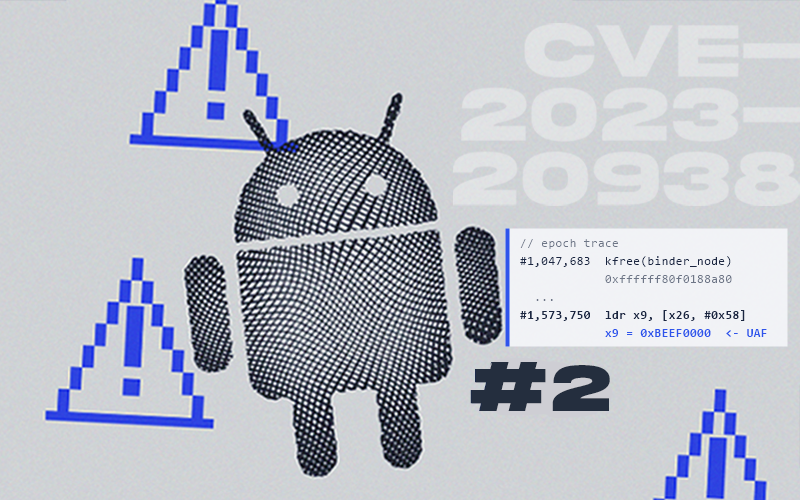
Part 2 of our Android kernel exploit chain (CVE-2023-20938): the stale read returns garbage until you control what reclaims the freed slot.

Land the right object there and it hands back a live kernel pointer instead. That’s your KASLR bypass.

https://www.eshard.com/blog/kernel-uaf-2-leak

www.eshard.comKernel UaF to Root #2: Making the Freed Slot Hand Back an Address We Chose | eShardPart 2 of our Android Binder exploit series: reclaiming a freed slot to leak a kernel address and defeat KASLR, traced step by step with Epoch.
↩ Reply ♡ 0 · ↻ 0 ↗ Original