LiveOverflow explains how he used AI to create a working php2shell exploit https://www.youtube.com/watch?v=SP7y1h0laN0
XFEDI
ActivityPubRemote profile


Ivan Ožić Bebek
:hacker_h: :hacker_a: :hacker_c: :hacker_k: :hacker_e: :hacker_r: :hacker_m: :hacker_a: :hacker_n:
Open remote profile ↗Posts
The wording implies they've seen php2shell being exploited in the wild, because they observed agentic post-exploitation activity? Also, their IOC's are not specific to these vulnerabilities. https://unit42.paloaltonetworks.com/cve-2026-109618-cve-2026-109619/
 Unit 42Threat Brief: Critical Vulnerabilities in PHP: CVE-2026-109618, CVE-2026-109619 (Updated October 23)CVE-2026-109618 and CVE-2026-109619 are Critical vulnerabilities in PHP, a scripting language used globally for web servers and CMS systems.
Signed, Sealed, and Relayed, NTLM-style: Bypassing LDAP Signing Through Reauthentication https://specterops.io/blog/2026/10/23/ldap-signing-bypass-ntlm-relay/
 SpecterOpsSigned, Sealed, and Relayed, NTLM-style: Bypassing LDAP Signing Through ReauthenticationAn LDAP signing bypass let attackers relay NTLM to domain controllers even with signing required. Why the October 2026 patch matters.
Defeating enforced SMB signing https://blackfield.ch/blog/defeating-enforced-smb-signing/
 blackfieldDefeating enforced SMB signing: a noteA documented SMB2/3 re-authentication behavior that keeps a reflected authentication working against a signing-required target.
Assetnote published php2shell scanner https://github.com/assetnote/php2shell-scanner
Hiding a DLL from the PEB Loader List (And Why Process Explorer Still Sees It) https://trainsec.net/library/windows-internals/hiding-a-dll-from-the-peb-loader-list-and-why-process-explorer-still-sees-it/
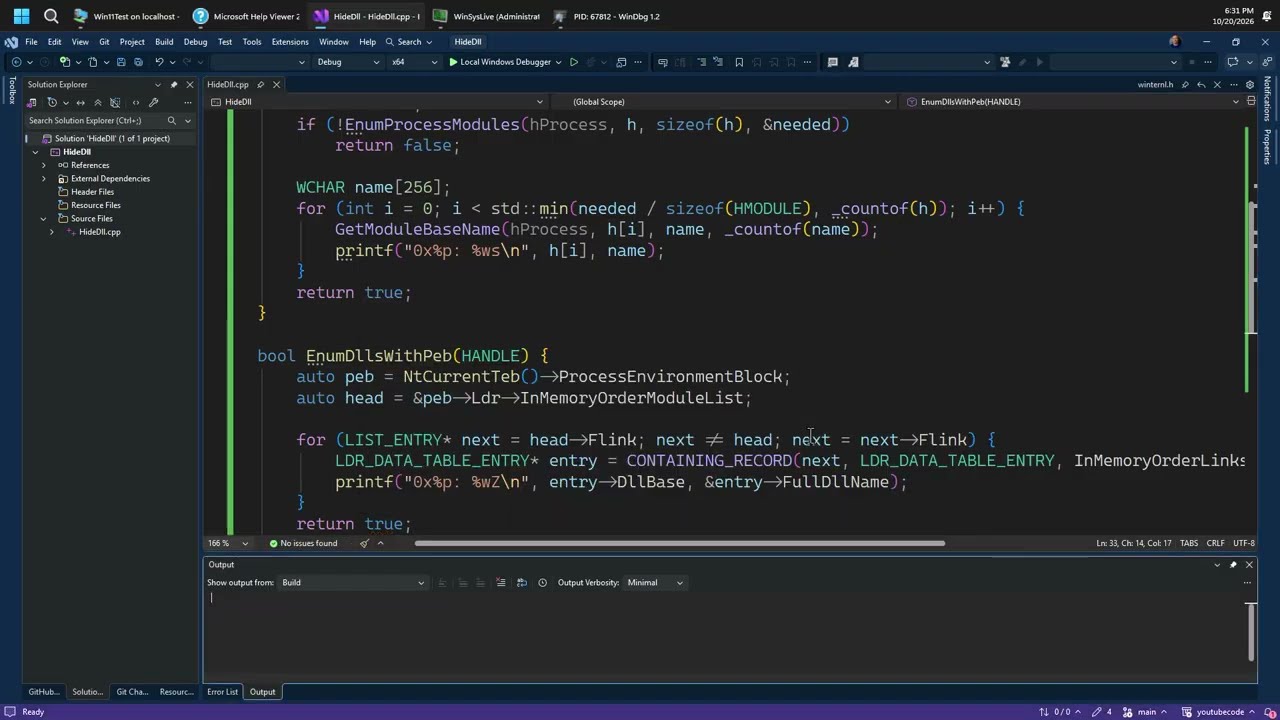 TrainSec - CyberSecurity online trainingHiding a DLL from the PEB Loader List (And Why Process Explorer Still Sees It) » TrainSecPavel Yosifovich unlinks a DLL from the PEB's loader module list, compares it to EnumProcessModules, and shows why Process Explorer and WinDbg's lm still find it.
Another PoC for CVE-2026-109618/109619 PHP session.upload_progress https://github.com/ikow/php2shell-poc
Content discovery and fuzzing with HTTP/3 support (100k requests per second) https://github.com/assetnote/h3fuzz