"Maintain an awareness for contribution -- to your schedule, your project,
our company."
-- A Group of Employees
XFEDI
ActivityPubFederated
HELLO, FEDIVERSE
Good conversations travel.
Public updates from xsukax and this corner of the network.
Sign In to your accountPublic posts known to this server, including selected instances.


Any #FreeBSD folks using vm-bhyve with NAT? It appears that the built-in support was removed in 2016 and never reintroduced. It's not clear to me how to set up the NAT between the bridged interface that vm-bhyve creates and the host network interface. I've found a bunch of articles that claim to cover this and either use the command that hasn't existed for 10 years or skip over network configuration.
The U.S. Department of Commerce’s National Institute of Standards and Technology (NIST) has announced its support for the White House Office of Science and Technology Policy’s Science: A New Golden Ag https://pigeonreporter.com/2026/10/15/nist-supports-white-house-initiative-for-new-golden-age-of-science
 PigeonReporterNIST Supports White House Initiative for 'New Golden Age of Science' - PigeonReporterNIST Supports White House Initiative for 'New Golden Age of Science'

Windows Server 2025 QMR arrives with the October update, letting WinRE fetch fixes from Microsoft after boot failures.
#WindowsServer2025 #QMR #QuickMachineRecovery #WinRE #Microsoft #GroupPolicy #SysAdmin #Windows11
https://securityonline.info/windows-server-2025-qmr/?utm_source=mastodon&utm_medium=jetpack_social
🥤#RedBull, optimistă înainte de cursa de F1 din #Austin: „Lui 🏎️#Verstappen îi place acum mașina”.
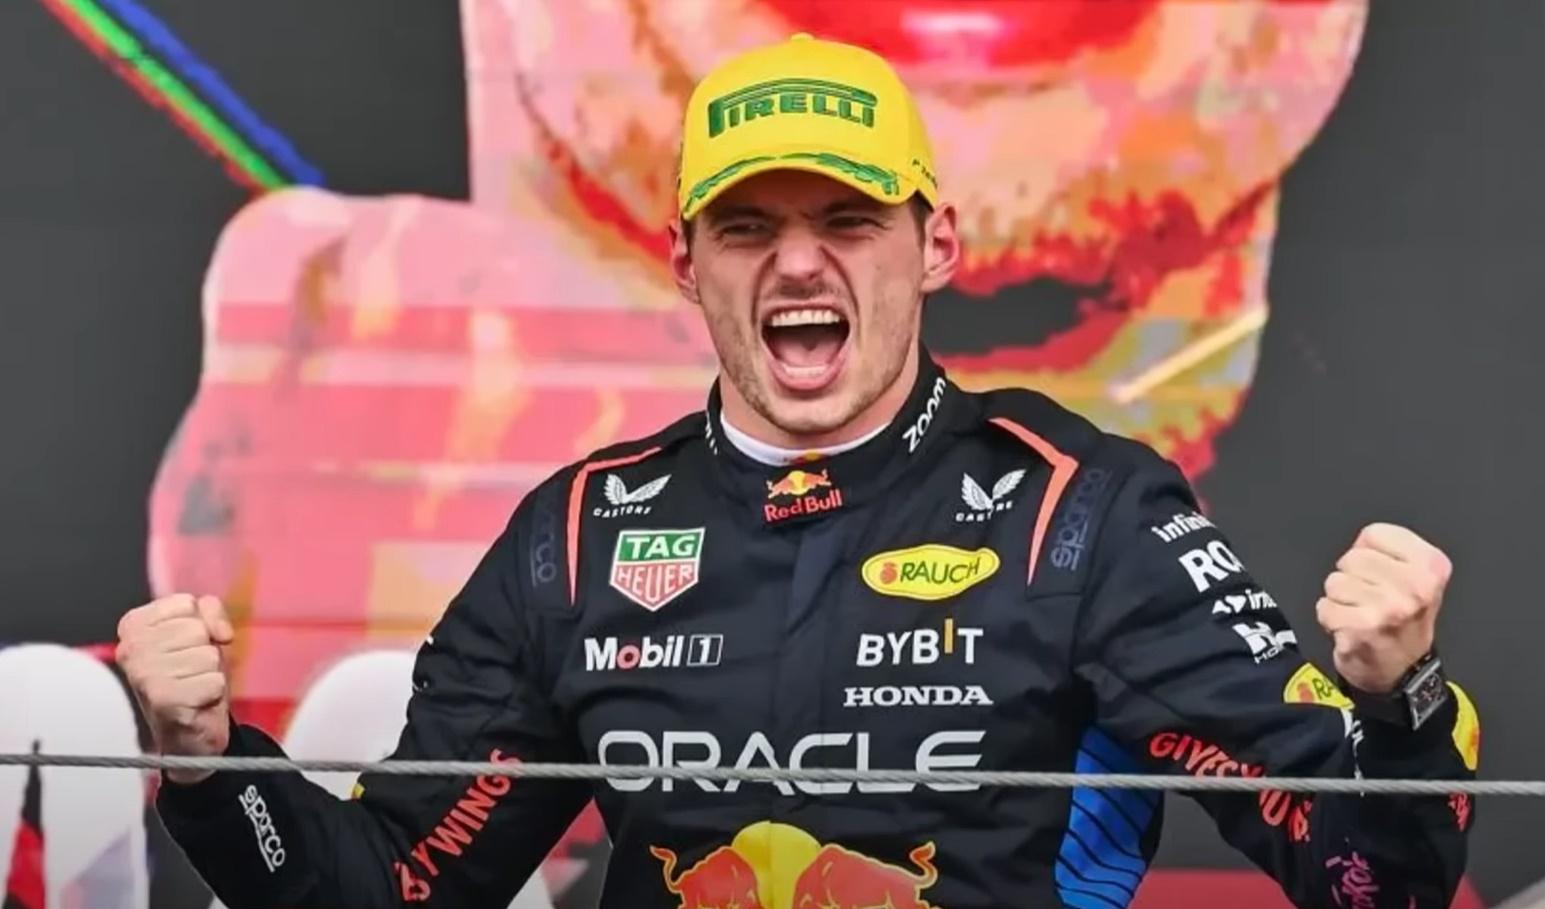
 G4Media.roRedBull, pe val înainte de cursa de F1 din AustinMax Verstappen a câștigat ultimele două Mari Premii din Formula 1, iar RedBull privește încrezătoare către cursa din Austin.
Legends Project Trailer
Microsoft published guidance on Oct 19 reframing AI agents as insider risk requiring external, adaptive controls. It extends Zero Trust to agent identities with least privilege and continuous verification, which matters for scoping access and monitoring autonomous workflows. #AiSecurity #ZeroTrust #IdentitySecurity
https://cyberworldops.eu/en/microsoft-recasts-ai-agents-as-insiders-requiring-external-adaptive
 CyberWorldOpsMicrosoft Treats AI Agents as Insider Security RiskMicrosoft outlines a framework treating AI agents as insider risks, urging external identity, containment and adaptive controls for agent access.
Türkiye'de 6 Gün Sonra Hava Yeniden Değişiyor! Kuvvetli Yağış İçin Tarih Verildi!
https://abcgazetesi.com.tr/turkiye/turkiyede-6-gun-sonra-hava-yeniden-degisiyor-kuvvetli-yagis-icin-tarih-verildi-874673?_unique_id=6ad731a202d30
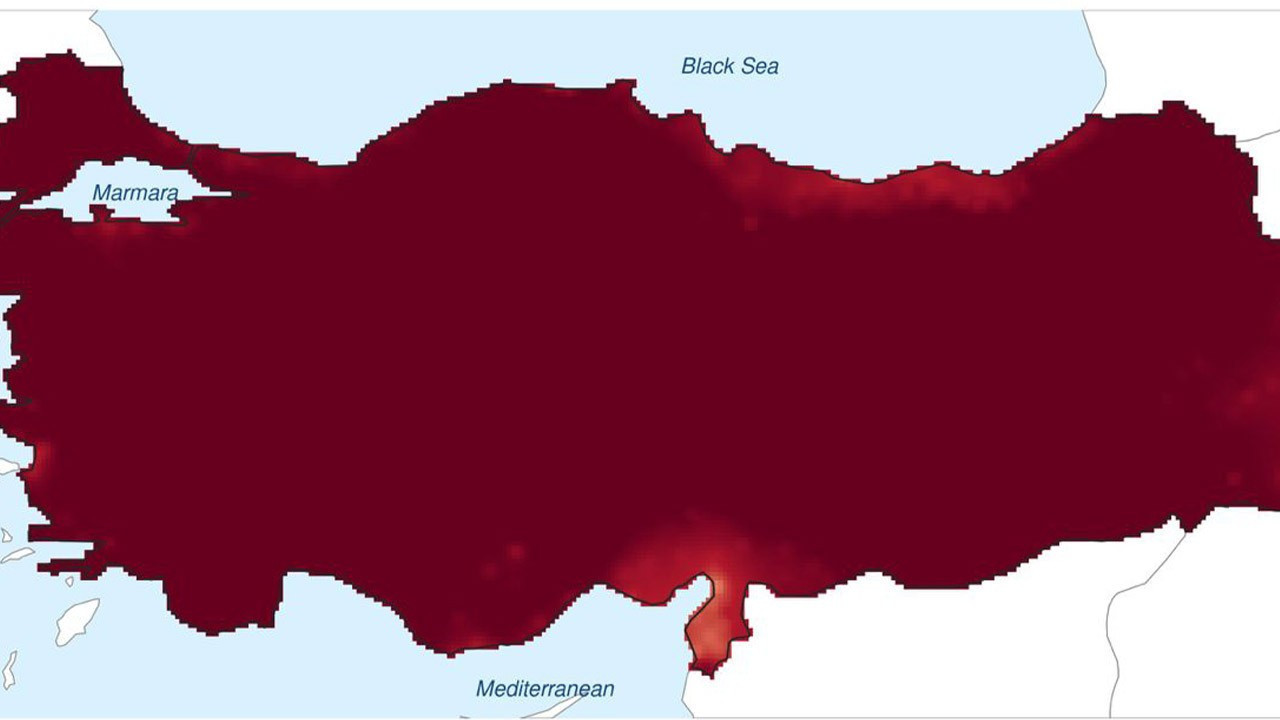 ABC HaberTürkiye'de 6 Gün Sonra Hava Yeniden Değişiyor! Kuvvetli Yağış İçin Tarih Verildi!Türkiye genelinde önümüzdeki 5 gün boyunca mevsim normallerinin üzerinde, güneşli ve ılık bir hava beklenirken meteorolojik tahminlerde yeni bir değişim günde..
Während die Stockholmer Nacht zum Leben erwacht, pulsiert #Silvester durch die glamourösen Clubs am legendären Stureplan – wo bis 05:00 Uhr getanzt wird und der Jahreswechsel zur magischen Feier wird. 🎉 Die skandinavische Hauptstadt verzaubert mit #Schweden-Flair in Berns, Biblioteket Live und Under Bron, wo #Partynacht und nordisches Lebensgefühl verschmelzen. Sichert euch die Tickets frühzeitig und spürt den #Fernweh, wenn die Mitternacht mit ...
 Europa Veranstaltungskalender 2026-2027 – Festivals, Konzerte & EventsSilvesterpartys Stockholm 2026/2027 | Clubs & DiskoSilvesterpartys in Stockholm 2026/2027: Clubs am Stureplan, Biblioteket Live, Berns, Spy Bar und mehr. Tickets, Zeiten und Tipps für die Partynacht.

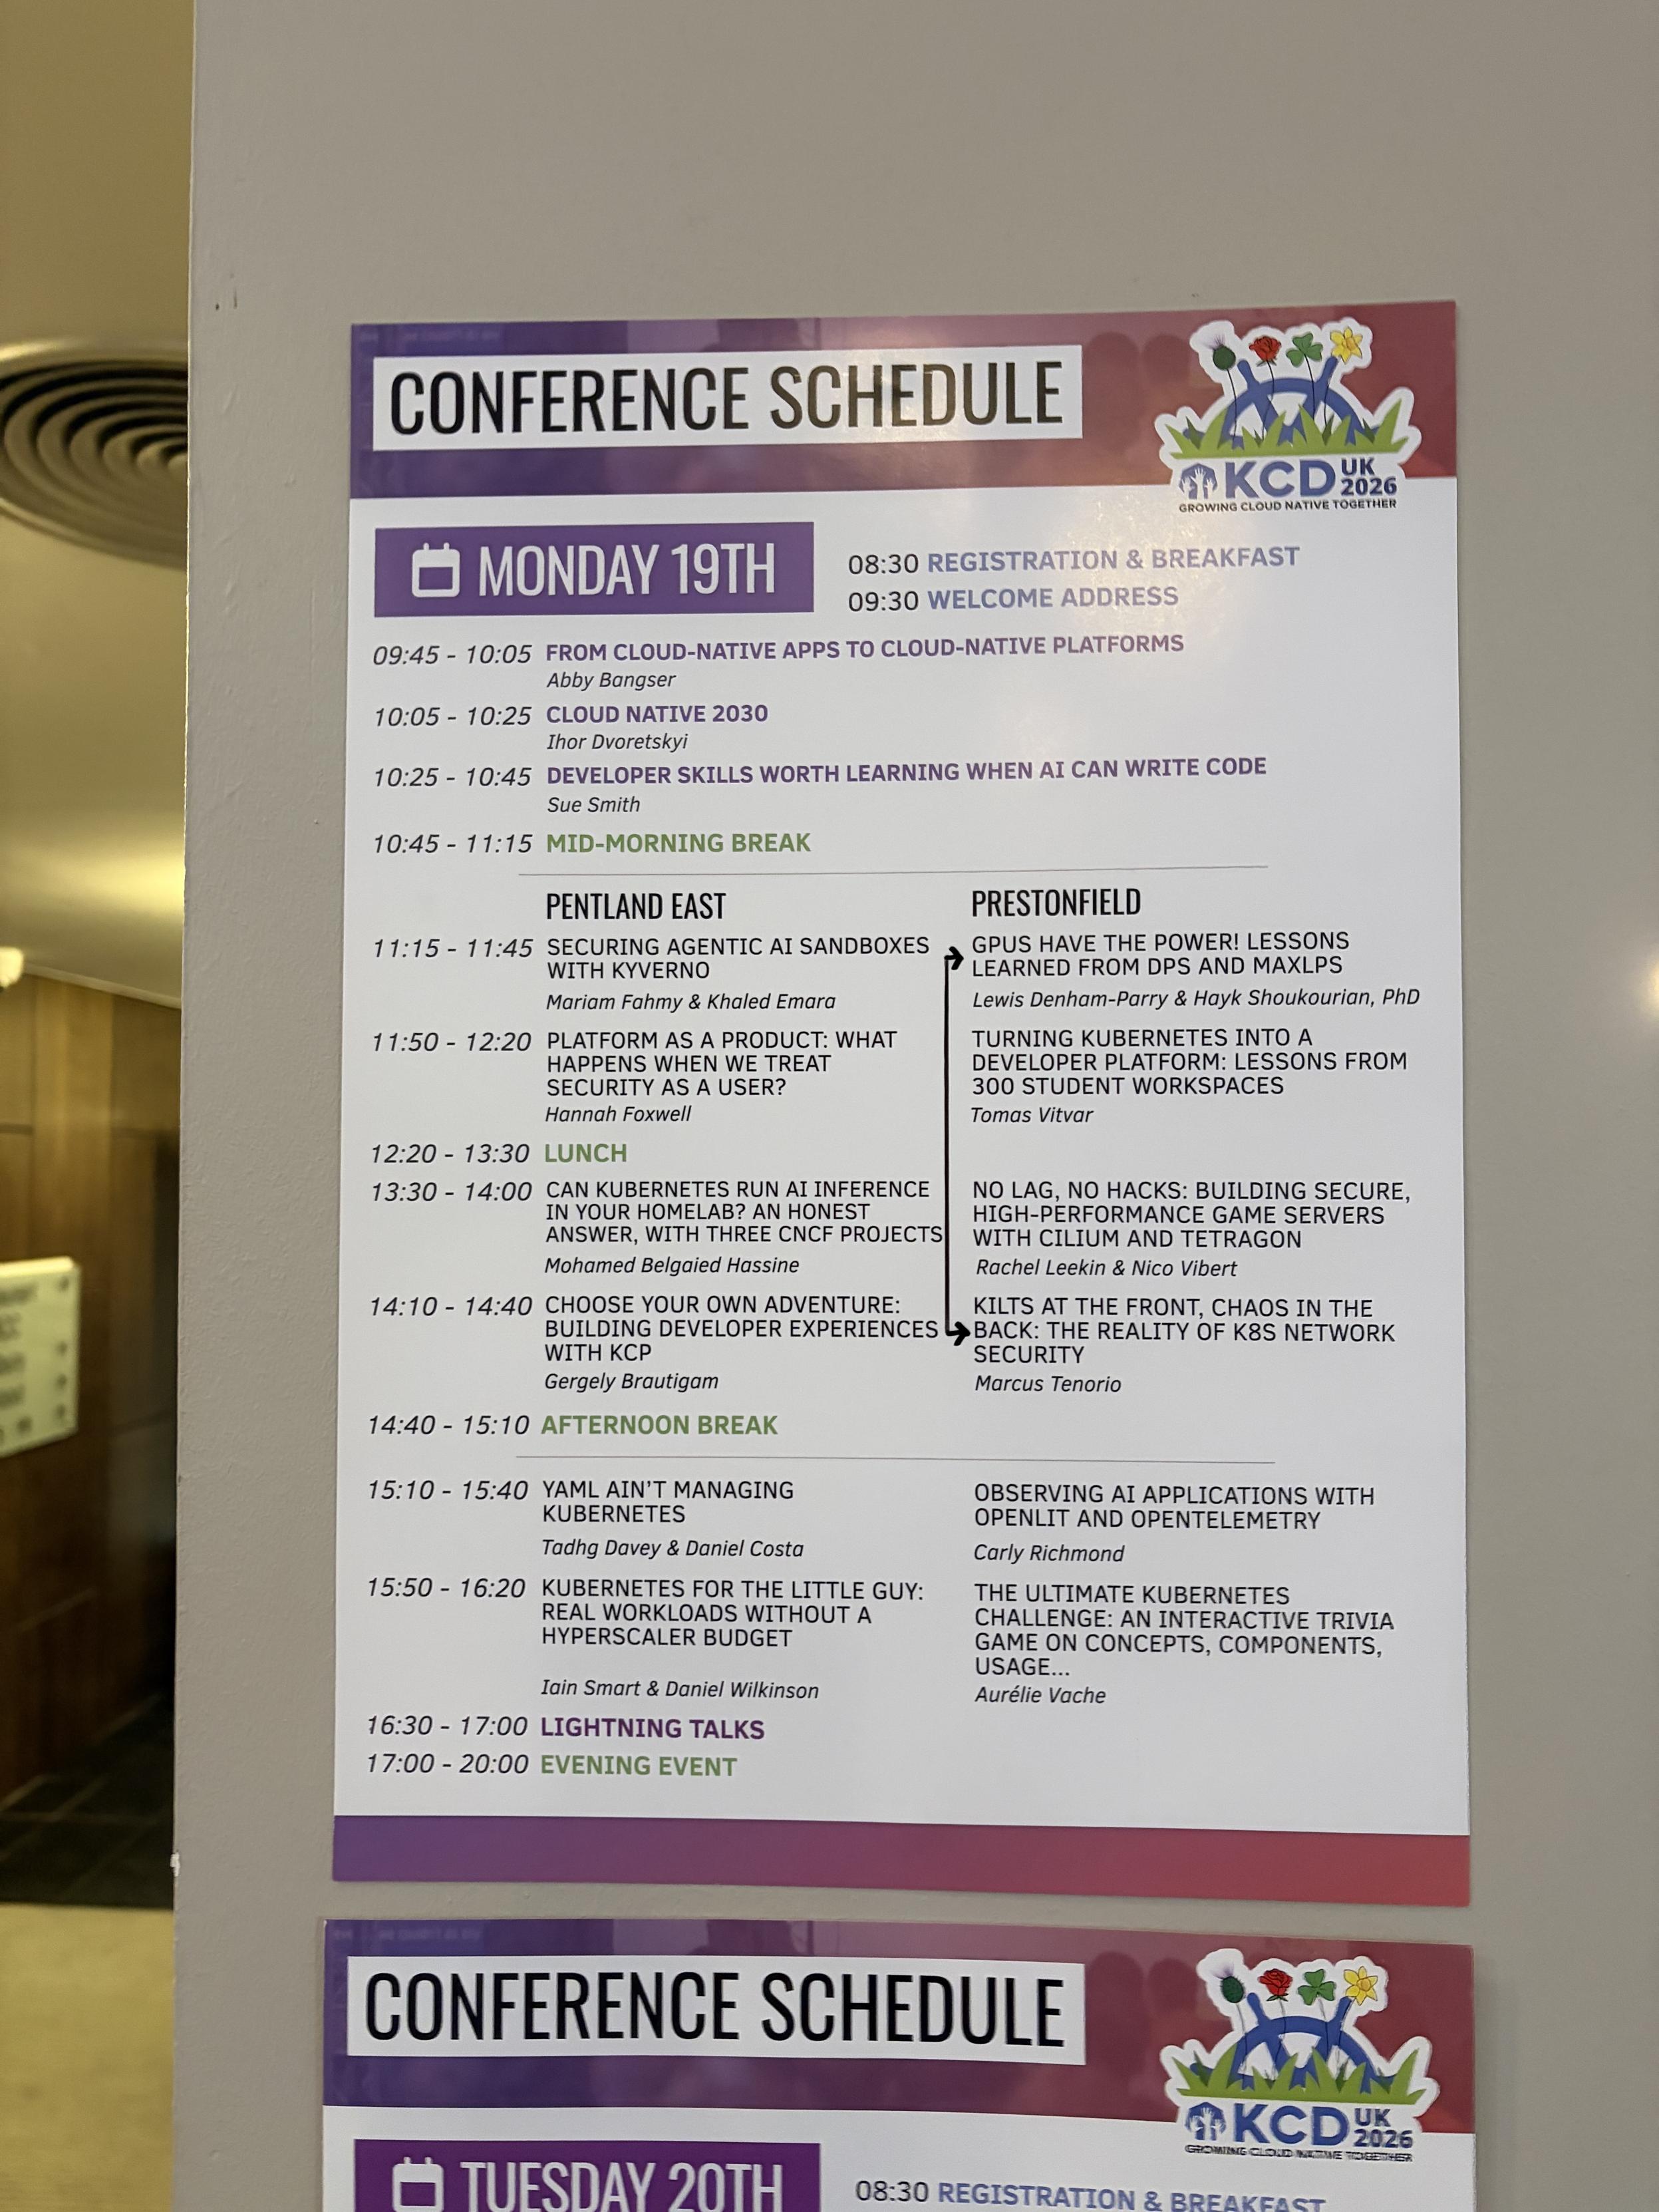
Day 2 of #KCDUK with more #cloudnative fun!

Auch in ihrem Fall schrieb uns eine Gefängnisbeamtin und bat uns um ihren Freikauf zum nächsten Freedom Day. Das ist in 90% der Freikäufe so: Der Staat sperrt Menschen wegen Busfahrkarten ein und wendet sich dann (über JVA-Beamt:innen) an den Freiheitsfonds und bittet um Freikauf…


— ‘A series of Green council groups who share power with Labour have already rejected the motion, including Lewes, Warwick, Rother and Havant. Among other groups to have disowned the policy are the Greens in Southwark, who did so to maintain a coalition with the Liberal Democrats.
Ramsay said such groups “have been brave in speaking out about such a contentious motion”.
He said: “They have supported the Green party’s strong position of calling out the ethnic cleansing and war crimes in Gaza and how this must be combined with upholding the right of both Palestinians and Israelis to statehood and self-determination. Calling out a genocide is more important than debating definitions of Zionism.”’
 the GuardianEx-Greens co-leader urges council groups to reject Zionism policyExclusive: Adrian Ramsay calls conference motion a distraction and says councillors should maintain coalitions where possible

🌐 ■ Se queda: Alberta vota en referéndum a favor de seguir en Canadá, según las primeras proyecciones ■ "El 19 de octubre, los habitantes de Alberta tomaron una decisión clara. Eligieron la unidad", indicó el primer ministro canadiense, Mark Carney. Un 76 % frente a un 23%, bastante claro.
https://www.huffingtonpost.es/global/se-queda-alberta-vota-referendum-favor-seguir-canada-primeras-proyecciones-f202610.html?int=MASTODON_WORLD

[2171483] [SRU] Support Broadcom Corp 58200 0x5884-0x5887
Bug bounty : visez l'impact, pas le volume. Priorisez les surfaces d'attaque oubliées : sous-domaines legacy, API v1 dépréciées, endpoints d'upload. Testez les IDOR avec ffuf en variant les IDs. Un low critique > dix self-XSS. Labs pratiques pour s'entraîner : https://bug404found.com/?utm_source=mastodon&utm_medium=social&utm_campaign=awareness&utm_content=fr
#cybersec #infosec #securite #bugbounty #pentest #websecurity
 Bug404foundBug404found?= — Cybersécurité & IALabs 3D pour prouver tes compétences cyber/dev et te connecter aux entreprises, + audit de sécurité et développement IA automatisés pour PME/ETI.

Inside PH4NTXM: #57 PH4NTXM Session Guard
Your session identity should stay consistent throughout your session.
Session Guard checks generated identity consistency and protection readiness every 10 seconds. If it detects a mismatch, a protection failure, or a monitored MAC change, it warns you and shows what changed.
Monitoring is optional. Enabling or disabling it requires your session password, and closing the window keeps monitoring running.
You stay in control. Review the findings and choose whether to enable Lockdown. Session Guard never activates it automatically.
#ph4ntxm #linux #debian #os #live #privacy #security #opsec #infosec #research #tech #technology
 RansomnewsRAMP admin Stallman: 10 BTC for the XSS admin’s identityRAMP's administrator ran its escrow, bought US network access daily and offered LockBit the XSS admin's identity for 10 BTC. Dancho Danchev reads the record.
Why did RealMLP make two financial ML ensembles despite modest standalone scores? A case study in model selection, validation, and ensemble design. https://hackernoon.com/revisiting-ml-model-selection-with-an-external-realmlp-challenger #realmlp
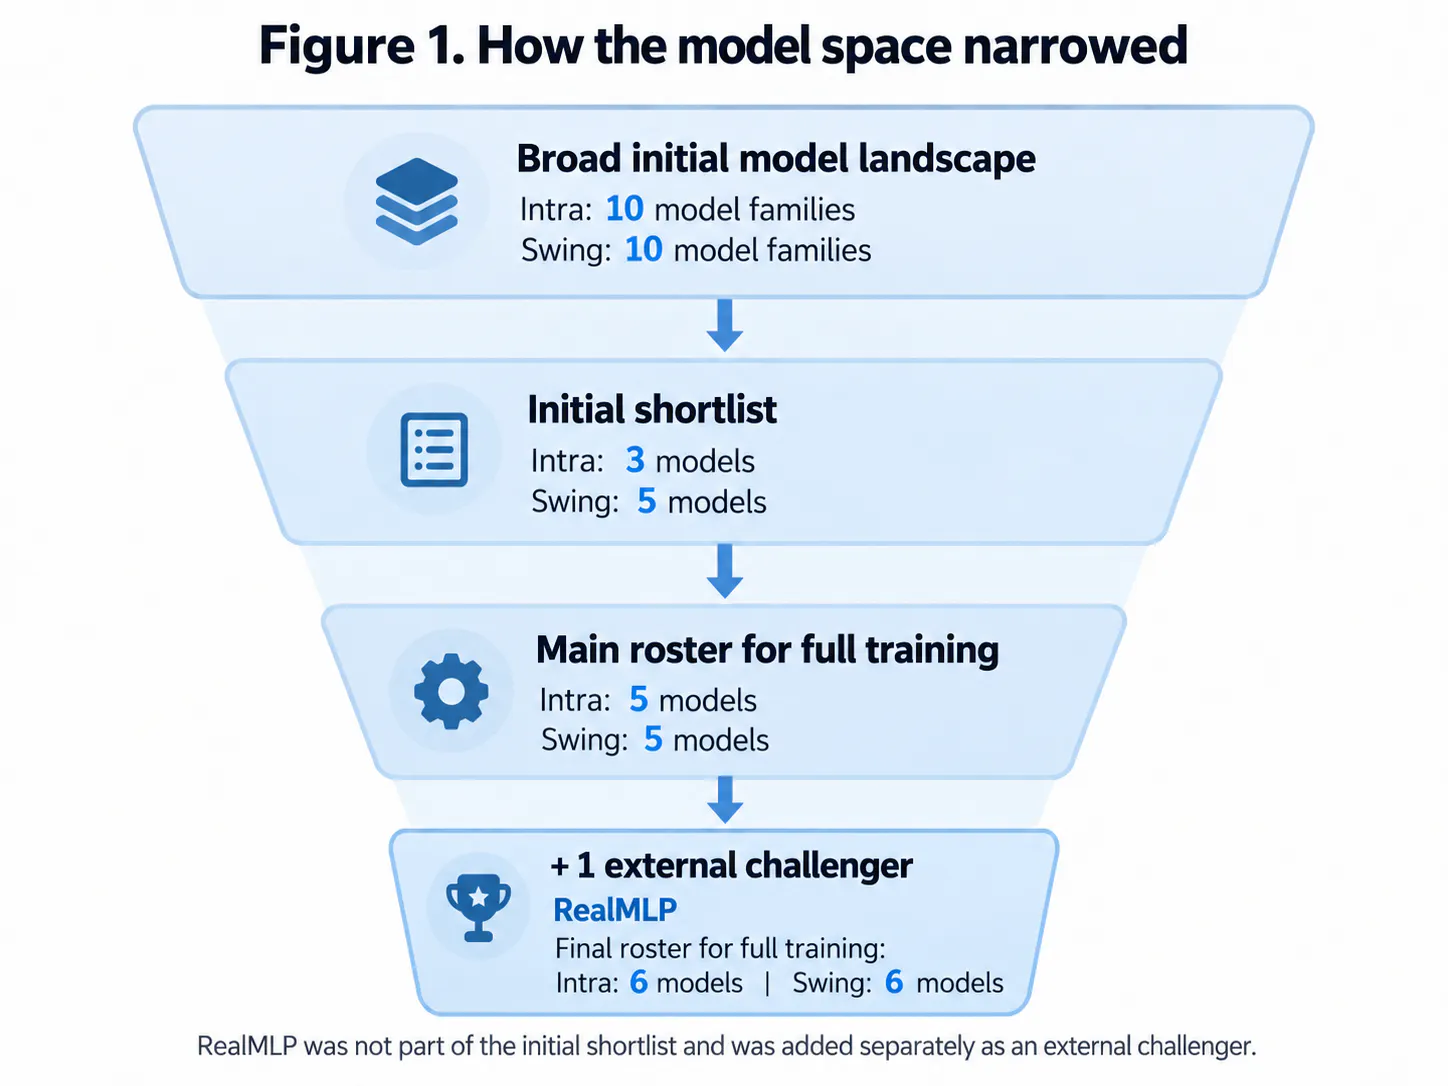 hackernoon.comRevisiting ML Model Selection With an External RealMLP Challenger | HackerNoonWhy did RealMLP make two financial ML ensembles despite modest standalone scores? A case study in model selection, validation, and ensemble design.
Hätten wir die 24-jährige Frau S. nicht freigekauft, hätte sie die gesamte bisherige Amtszeit von Friedrich Merz im Knast gesessen (fürs Fahren ohne Ticket).
Wann wird die Ticket-Haft endlich gestrichen?!

SlowMist traces Qubic wallet theft to weak randomness in seed generation
SlowMist has traced the Qubic wallet theft to weak randomness in seed generation, which undermined the keys protecting user wallets, Crypto Briefing reports. The finding is the root-cause follow-up to the October 18 incident in which an attacker drained 1,404 Qubic wallets and the network paused its mainnet. https://cryptobriefing.com/slowmist-qubic-wallet-key-recovery-flaw/
 Crypto BriefingSlowMist traces Qubic wallet theft to weak randomness in seed generationSlowMist says Qubic Wallet used Math.random() for seeds, enabling key recovery tied to the theft of 2.94 trillion QU from 1,404 wallets.
— ‘Drivers will get a guaranteed five minutes to decide whether to park and 10 minutes to leave after their parking session ends before they face a fine under new rules for private car parks that Andy Burnham said were designed to outlaw “rip-off” charges.
In the latest in a series of “everyday fixes” to ease the cost of living and give consumers a “fairer” deal, the prime minister said a new official code of practice for the industry meant motorists in England, Scotland and Wales would enjoy a range of new rights.
The consumer body Which? said the “long overdue” rules appeared to fall well short of what was needed to help drivers fight back against private parking “cowboys”, however.’
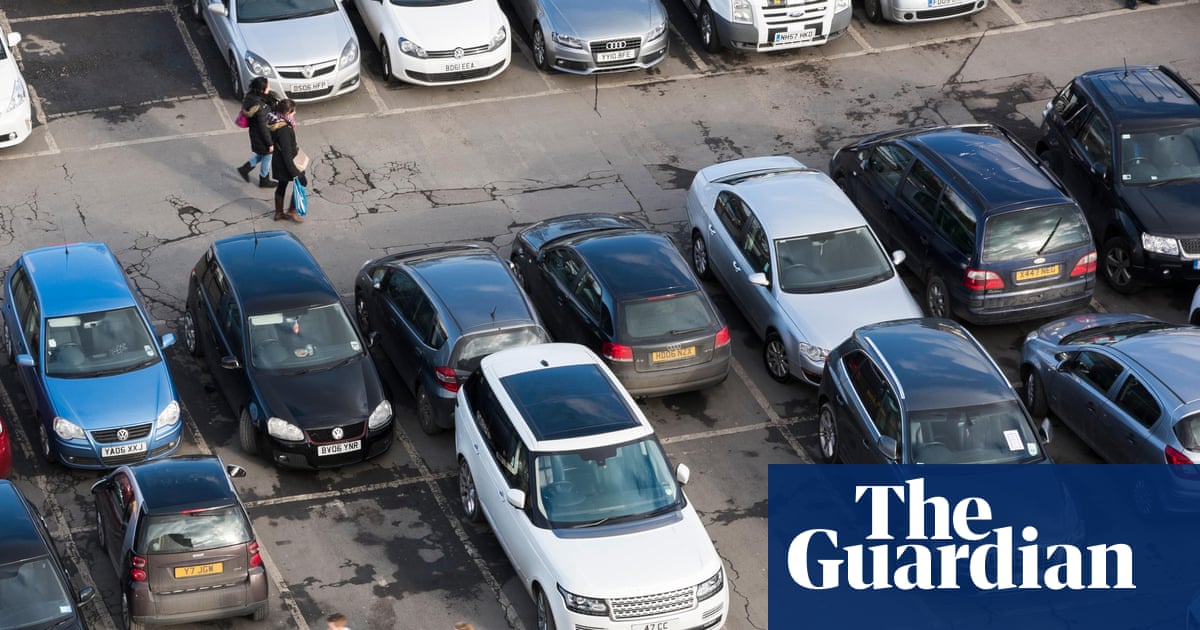 the GuardianAndy Burnham outlines new rules to outlaw ‘rip-off’ private parking finesDrivers to get five minutes to decide whether to park and 10 minutes to leave after their session ends
Cybercriminals favor Microsoft over Apple and Google in brand phishing attacks
Microsoft accounted for 33% of brand impersonation attempts tracked by Check Point Research in the third quarter of 2026, up from 23% in the previous quarter, Help Net Security reports. That share is roughly four times that of any other brand in phishing attacks. https://www.helpnetsecurity.com/2026/10/19/check-point-brand-impersonation-scams-q3-2026-report/
 Help Net SecurityCybercriminals favor Microsoft over Apple and Google in brand phishing attacks - Help Net SecurityMicrosoft led Q3 2026 brand impersonation scams as attackers used fake AI services and software updates to access victims’ devices.
Kommunismus ist Sowjetmacht plus Elektrifizierung
Bündnis 90 Die Grünen ist Kommunismus ohne Arbeiterlieder (nur Kritik und Selbstkritik ist übrig geblieben)
OnlyFans Copyright Takedowns Expose Compromised Websites
Copyright takedown requests tied to OnlyFans and other adult content creators are revealing how attackers exploit vulnerable university and government websites to manipulate search results, Dark Reading reports. UpGuard’s Greg Pollock explains what universities, government websites and security teams should take from the pattern. https://www.darkreading.com/vulnerabilities-threats/onlyfans-copyright-takedowns-expose-compromised-websites
 www.darkreading.comOnlyFans Copyright Takedowns Expose Compromised WebsitesCopyright takedown requests tied to OnlyFans creators are revealing how attackers exploit vulnerable university and government websites.

One Hash Bloom Filters
https://calabro.io/ohbf

The Evolving Cybersecurity Lexicon: Vulnerability Discovery to Resilience https://www.darkreading.com/vulnerabilities-threats/cybersecurity-lexicon-vulnerability-discovery-resilience
 Dark ReadingThe Evolving Cybersecurity LexiconAn industry-wide laser focus on vulnerabilities has left cybersecurity teams without enough room to strategize for resilience.

Tehnična in druga pomoč 20. 10. 2026 11:01
Radovljica
https://spin3.sos112.si/javno/zemljevid/473185
GMO Cybersecurity links Chinese AI tool ARTEX to breaches at Japanese firms
Tokyo-based GMO Cybersecurity by Ierae said on October 19 that it confirmed traces of ARTEX, a Chinese-developed AI penetration-testing tool, on servers used to attack around 20 Japanese companies, Crypto Briefing reports. Eight firms reported data breaches between September and October 2026, and CrowdStrike previously tied the same tool to attacks on South Korean banks in late September. https://cryptobriefing.com/gmo-cybersecurity-artex-ai-tool-japan-breaches/
 Crypto BriefingGMO Cybersecurity links Chinese AI tool ARTEX to breaches at Japanese firmsGMO Cybersecurity says Chinese AI pen-testing tool ARTEX was used against about 20 Japanese firms, echoing South Korean bank attacks.

#90DayCountdownToChristmasDay
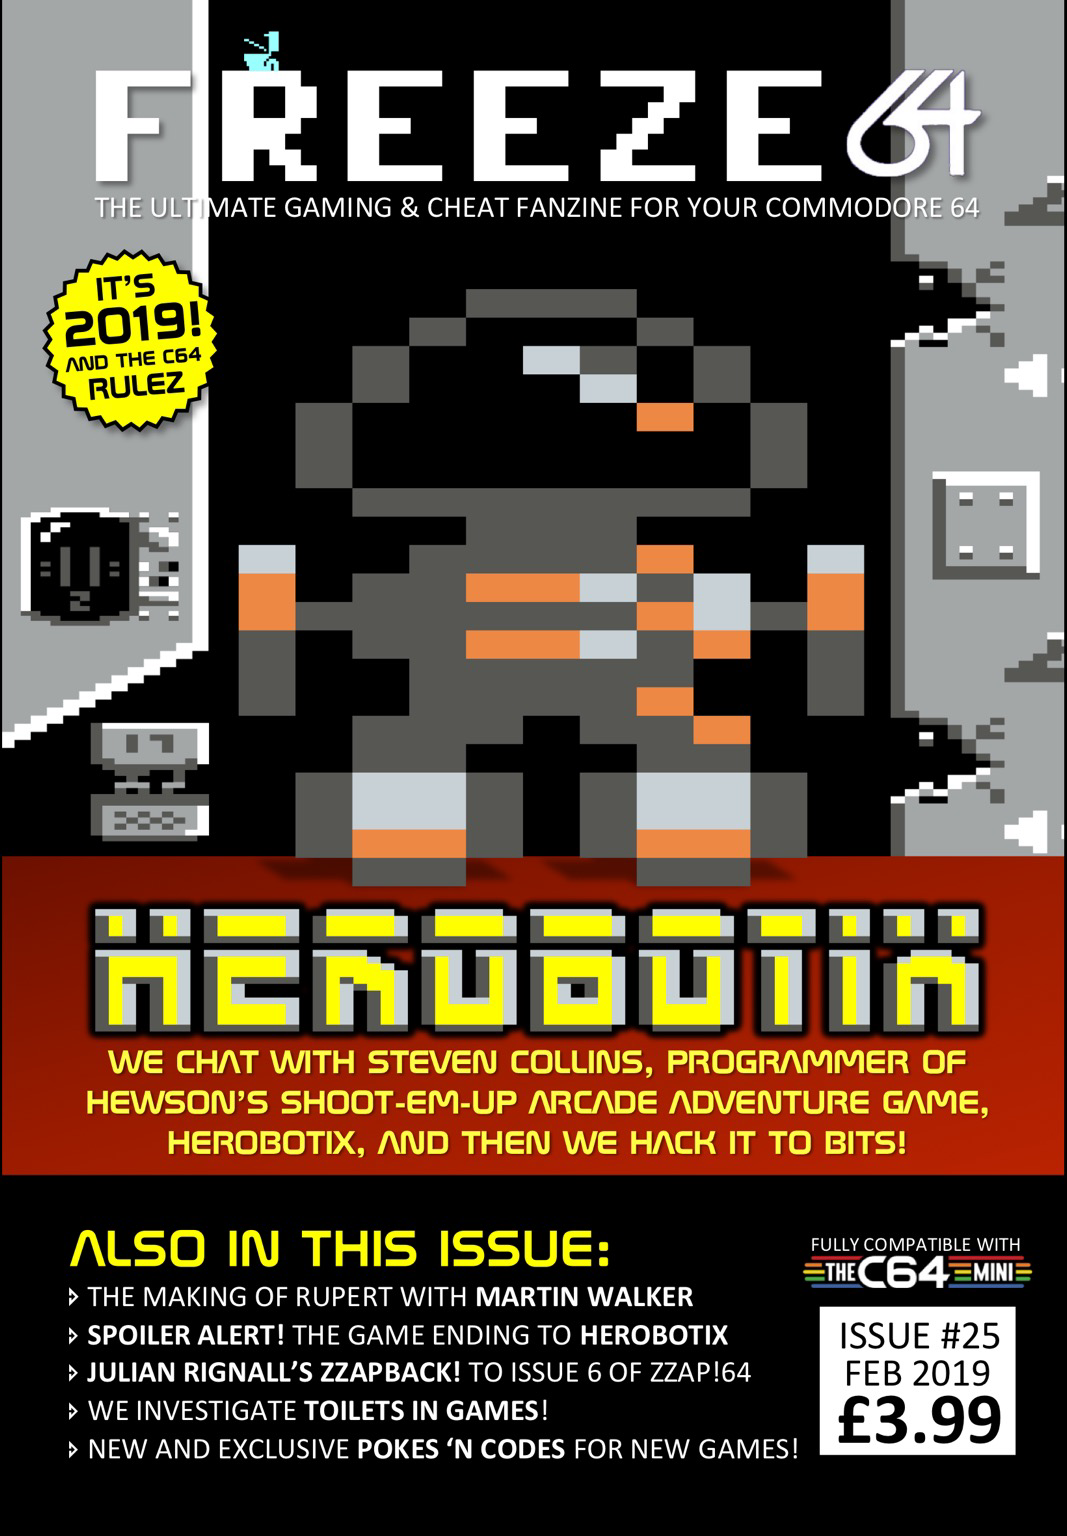
- one issue of FREEZE64 per day…
DAY 25: FREEZE64 issue 25
The issue features game development interviews with Steven Collins who chats about his #C64 games, and also Martin Walker on Rupert Bear.
Buy now: freeze64.com/freeze64-issue-24
#Commodore64 #C64