XFEDI
ActivityPubFederated
HELLO, FEDIVERSE
Good conversations travel.
Public updates from xsukax and this corner of the network.
Sign In to your accountPublic posts known to this server, including selected instances.
After several failed attempts, I've finally managed to get a viable Opencode loop working with a local model: Qwen3.8-27b (Q4_K_M).
Tool calling is much more stable than configuration that I tested before (OK, Ling-3.0-tiny, one of the more recent Chinese models with 8b parameters, was also quite stable).
This is certainly less performant than commercial services, e.g., Copilot with a model like Gemini, but pushing the limit is part of the fun, isn't it?
I've upgraded my inference machine (11th gen Core i7, 32GB RAM, fast storage), installed Incus (Zabbly stable) and use a Debian 13 container as the Opencode sandbox; llama-swap has learned a few new tricks, too. My two RTX 3060 are humming along, crunching numbers.
#homelab #Qwen38 #rtx3060

Hex-Rays has completed its acquisition of HexAI. The HexAI team has joined Hex-Rays to bring IDA technology into its agentic platform for cybersecurity research.
Read more: https://hex-rays.com/blog/hex-rays-completes-acquisition-of-hexai
 hex-rays.comHex-Rays Completes Acquisition of HexAI to Expand Its Agentic Platform Offering for Cybersecurity ResearchHex-Rays has completed its acquisition of HexAI, uniting teams to bring IDA technology into its agentic platform for cybersecurity research, launching early 2027.
Banks Are Struggling to Protect Customers From Their Own AI Agents https://www.motherjones.com/politics/2026/10/banks-ai-axios-agents-rogue-financial-decisions-security/?utm_source=dlvr.it&utm_medium=mastodon via @MotherJones
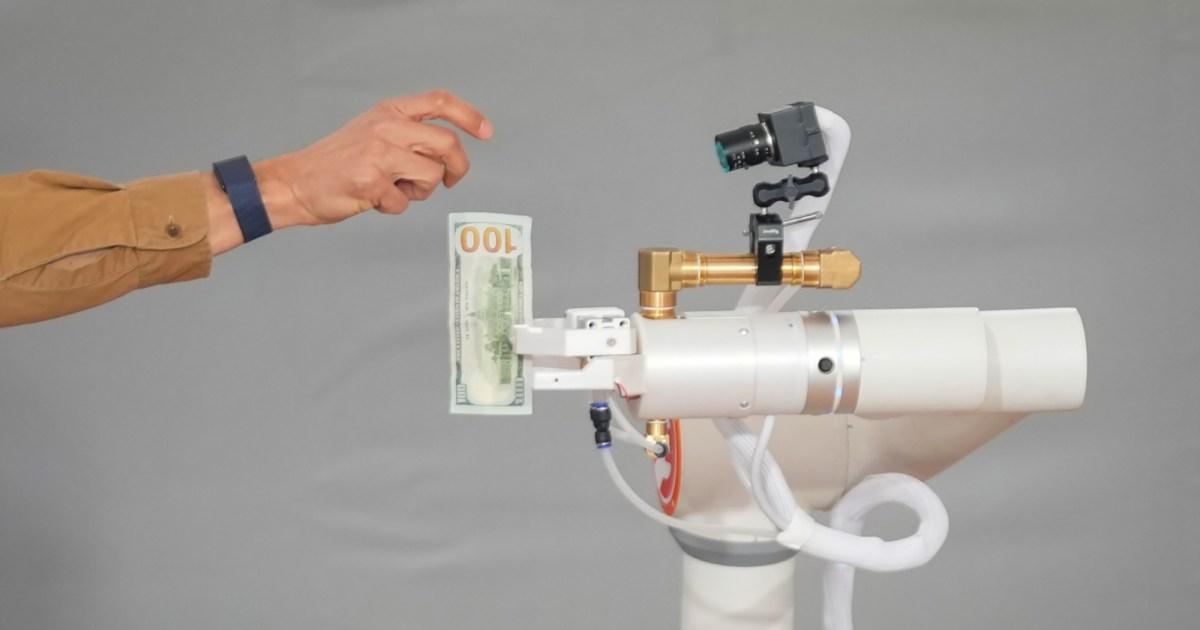
 Mother JonesBanks are struggling to protect customers from their own AI agentsSome AI tools now make financial decisions on their own, bankers say—raising frightening security risks.

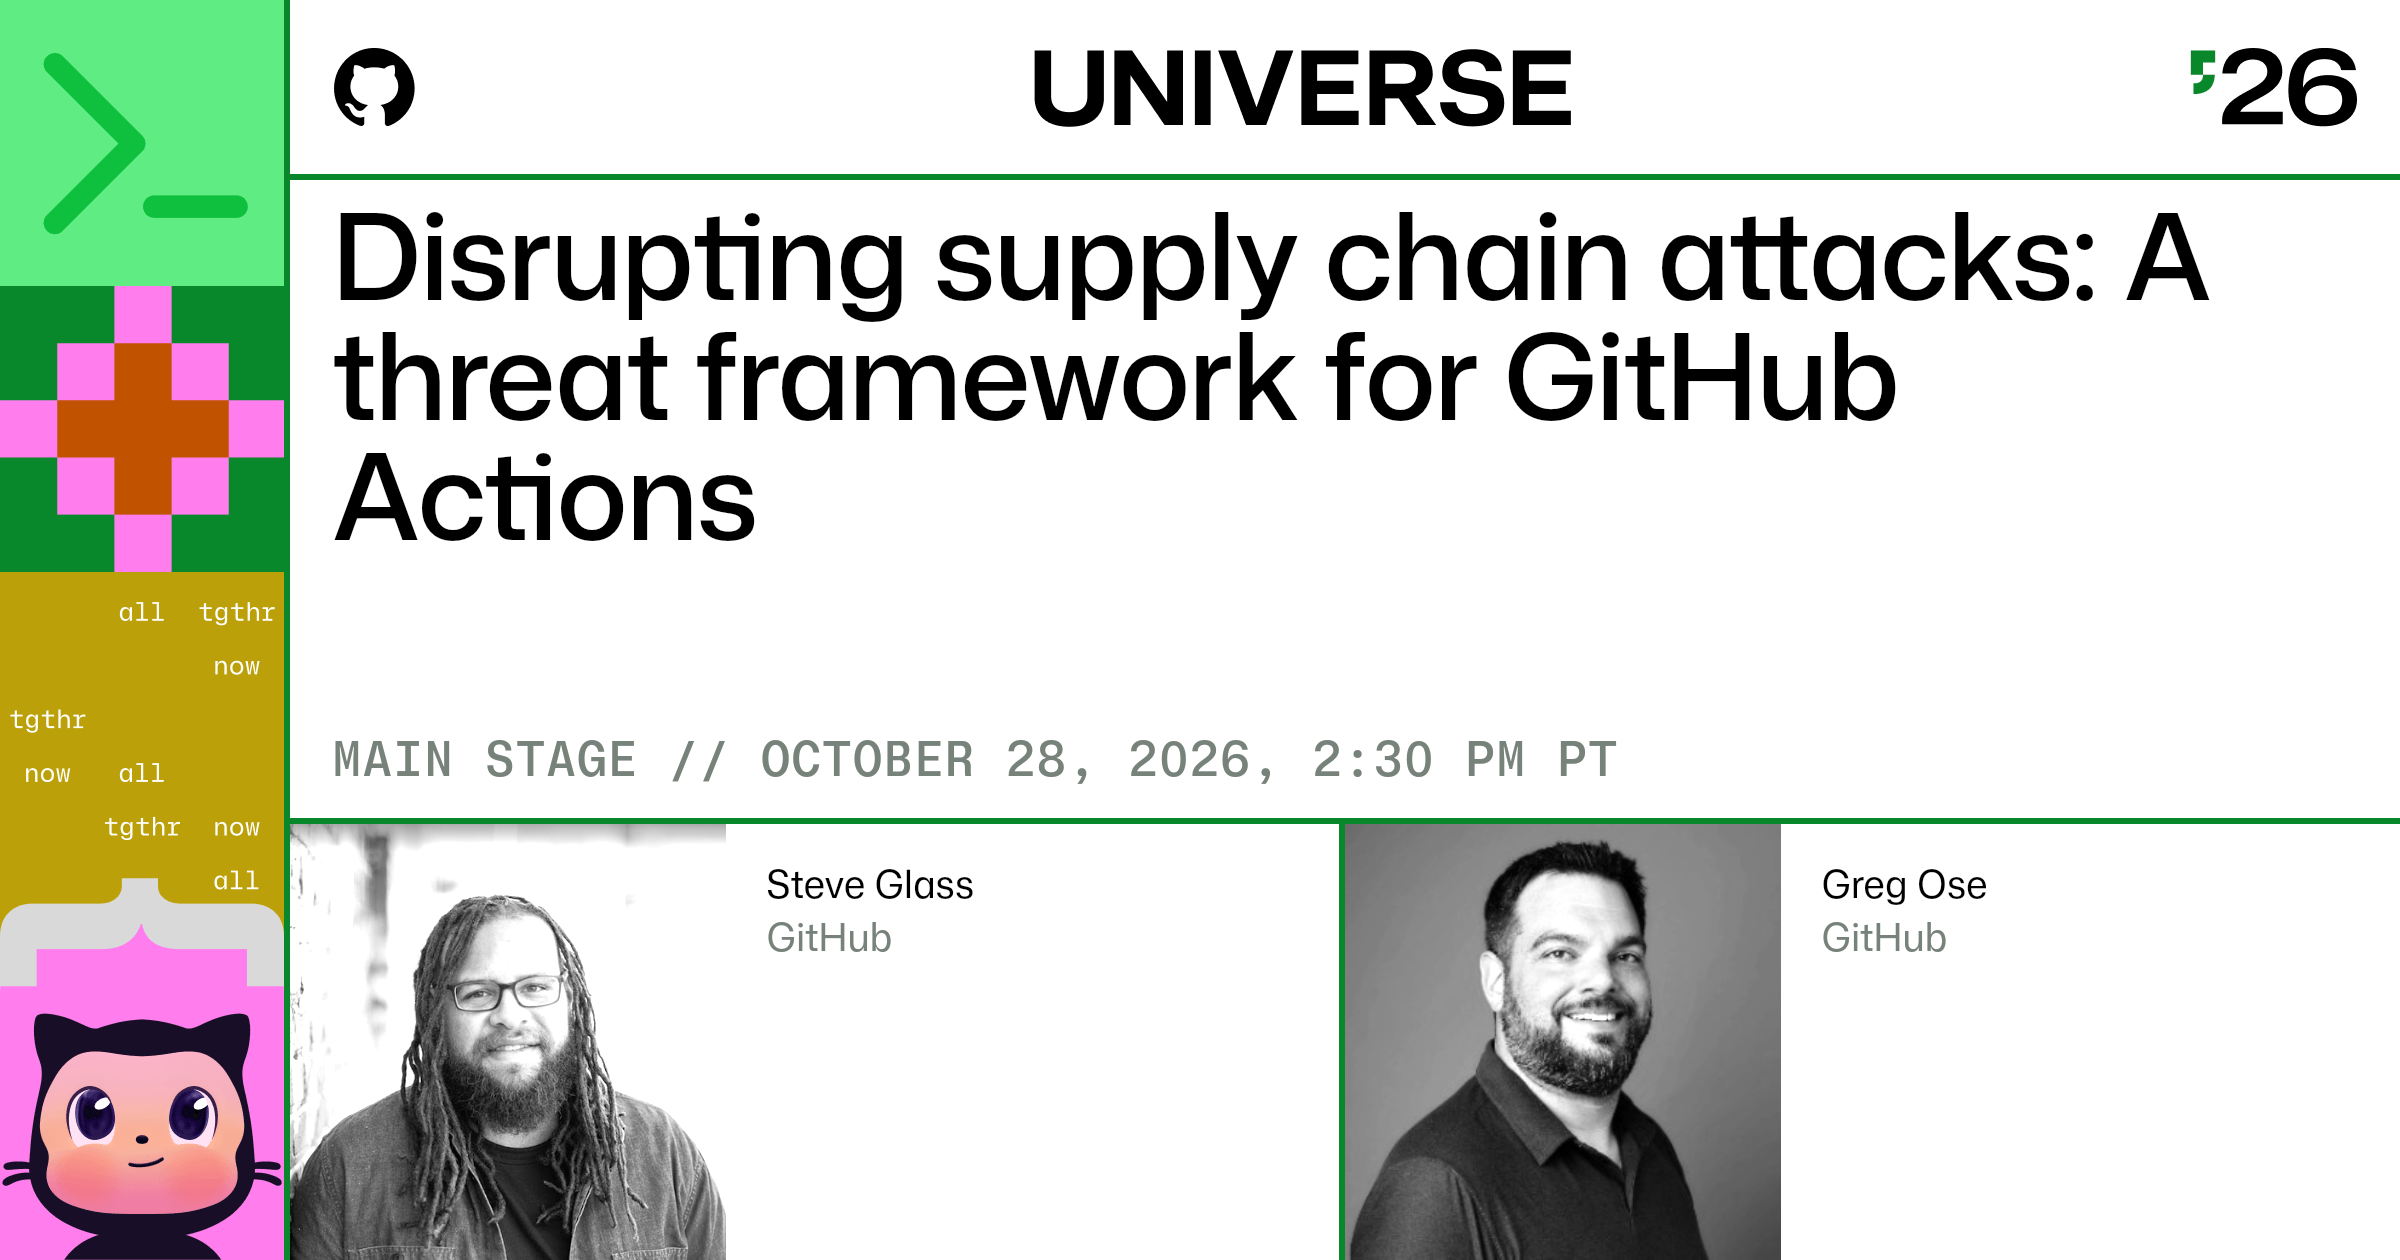
“Disrupting supply chain attacks: A threat framework for GitHub Actions” — Steve Glass and @gregose share an in-depth look at supply chain attacks across the Actions ecosystem and what we shipped to disrupt them. If you maintain open source or CI/CD pipelines, this is one to add to your agenda.
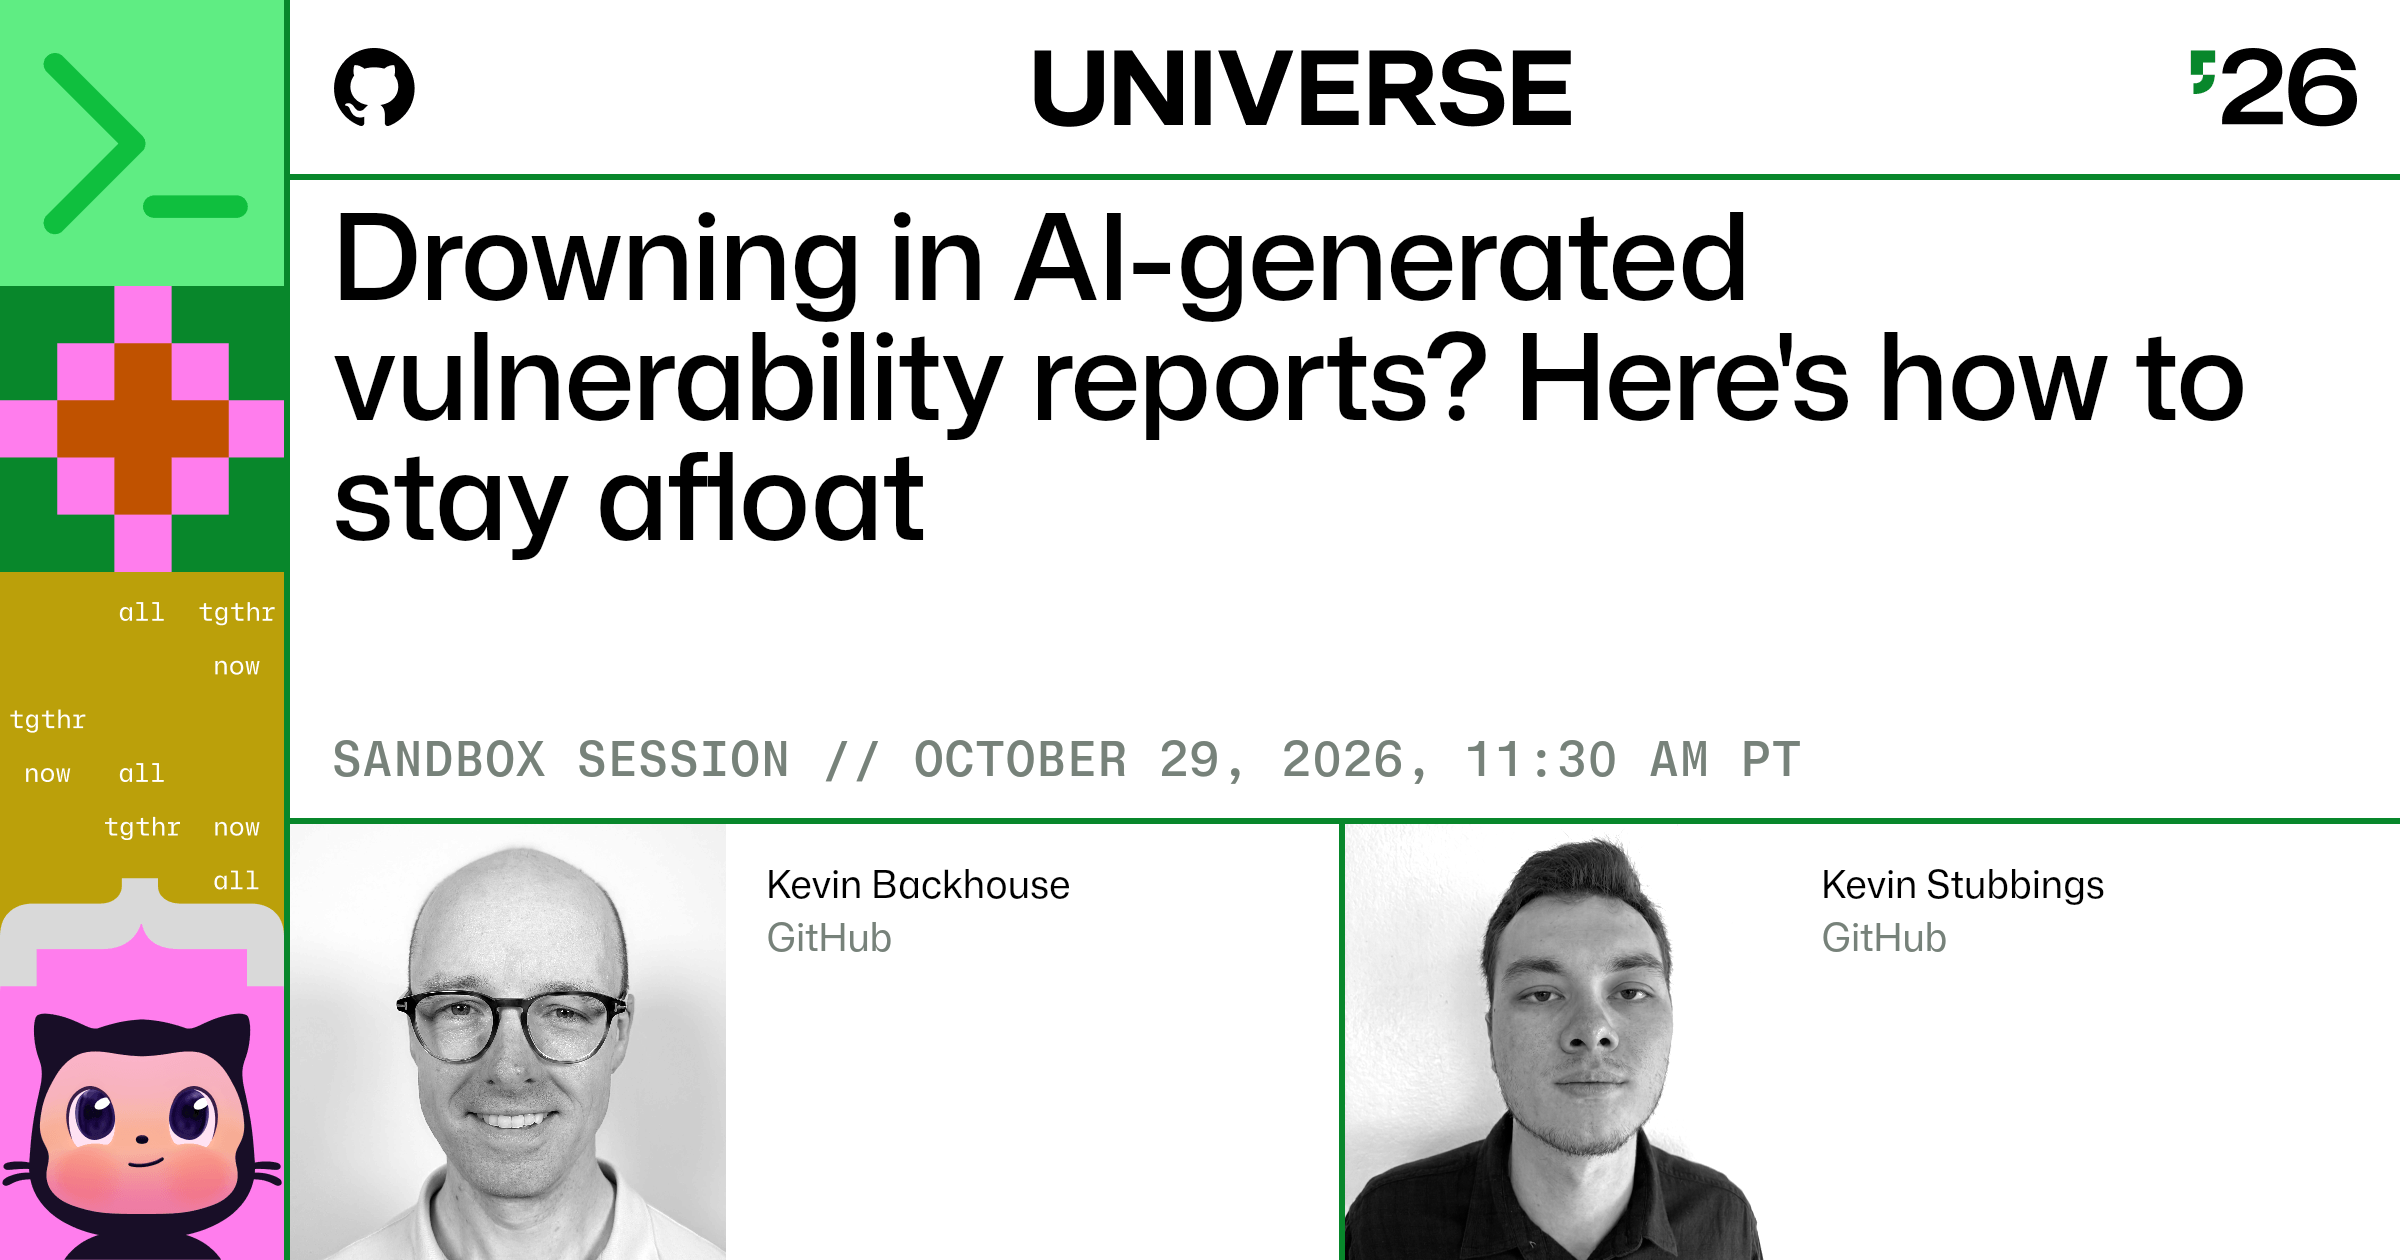
"Drowning in AI-generated vulnerability reports? Here's how to stay afloat.” Grab a paddle and join the two Kevins @kevinbackhouse and Kevin Stubbings as they navigate the creek. You'll practice handling security reports and learn best practices and techniques for triaging low value or invalid reports.
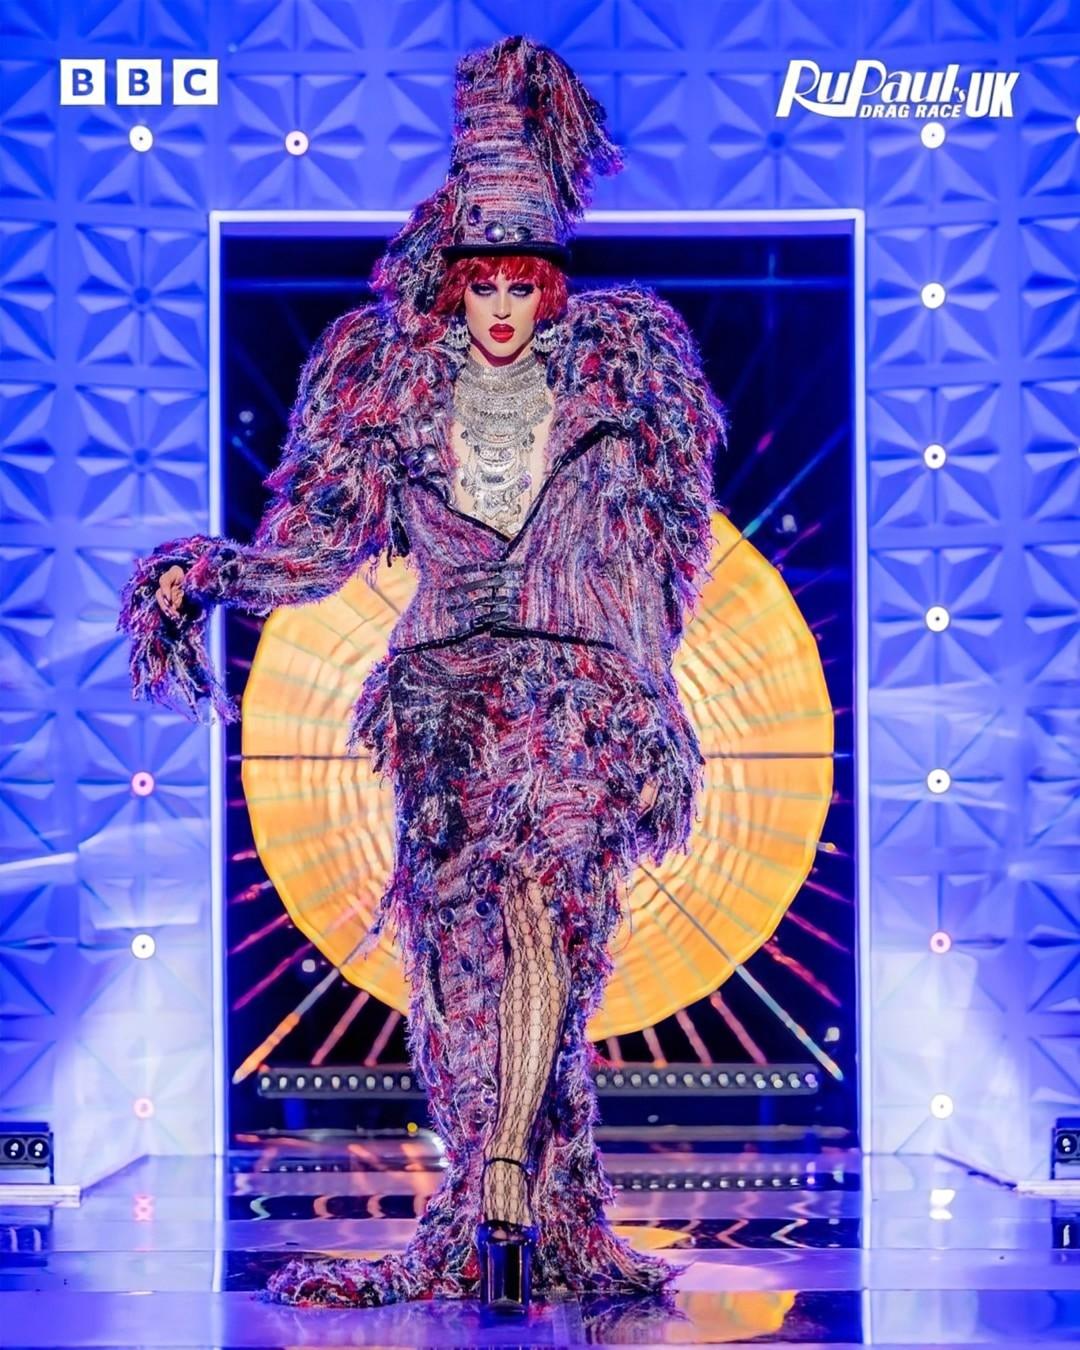
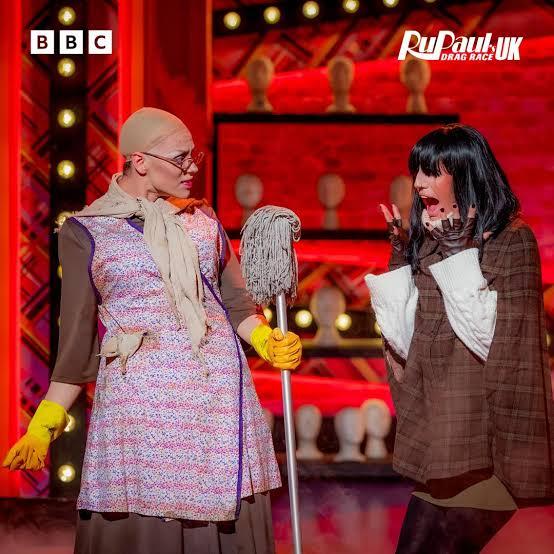
Drag Race UK 8 ep 7
• "Maureengate" was unnecessary
• But Ghost Hunties ended up being great 👻
• I think Flesh should have been in the top - besides crushing the challenge, her "Torn This Way" runway look was absolutely stunning!
• Hello Kadiff Kirwin 😍
#dragraceuk
Core team member Jake Howard has security tips for protecting your Wagtail sites from compromised eMudhra certificates. An important read! ⚠️ 🔐
Check out his blog: https://wagtail.org/blog/wagtail-emudhra-ca-compromise/
 Wagtail CMSWagtail and the eMudhra CA key compromise | Wagtail CMS8 CA certificates were compromised this week. What does that mean for you and your Wagtail sites?

📻 ■ Los 40 music awardsVuelve a ver el programa especial de nominados de LOS40 Music Awards Santander 2026 ■
https://los40.com/2026/10/22/vuelve-a-ver-el-programa-especial-de-nominados-de-los40-music-awards-santander-2026/?int=MASTODON_WORLD
 LOS40Vuelve a ver el programa especial de nominados de LOS40 Music Awards Santander 2026 | LOS40Ya puedes volver a verlo y descubrir quiénes son los artistas que aspiran a uno de los galardones más importantes de la música en España
Rus Ordusu’ndan Arktik’te Tatbikat: Kuzeyden Gelebilecek Saldırılar Simüle Edildi!
https://abcgazetesi.com.tr/dunya/rus-ordusundan-arktikte-tatbikat-kuzeyden-gelebilecek-saldirilar-simule-edildi-875052?_unique_id=6ada6232425a4
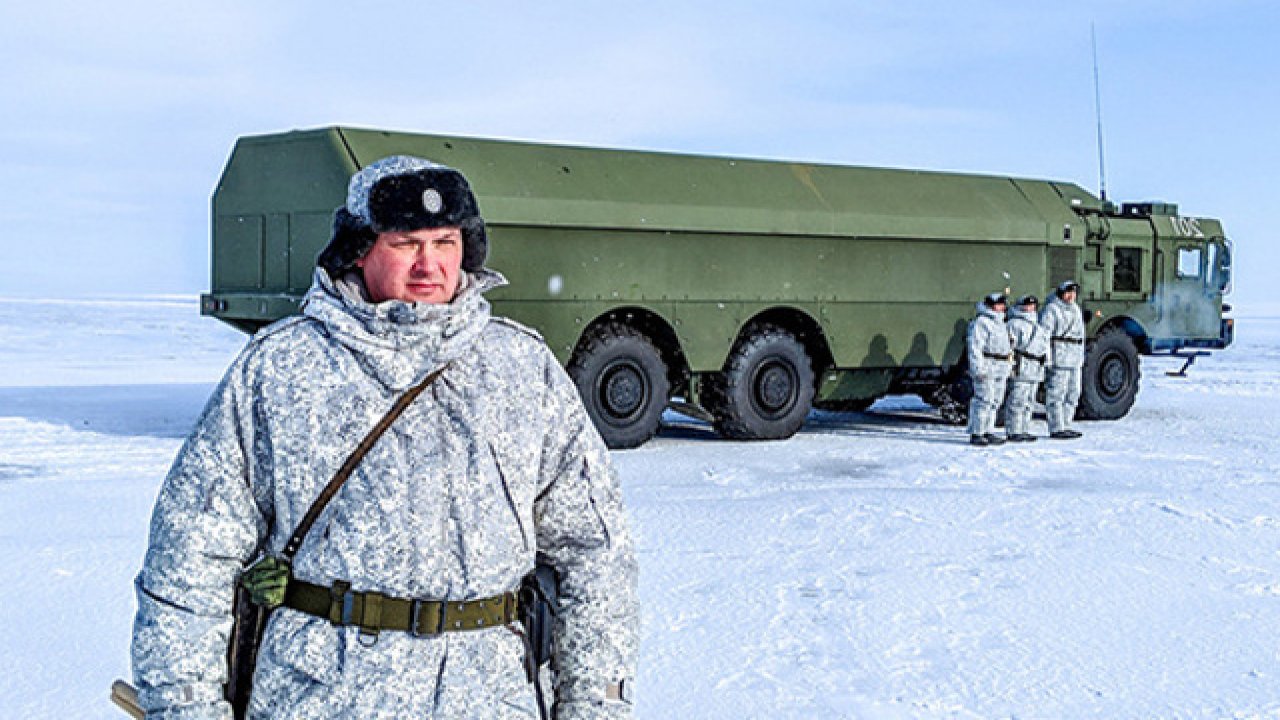 ABC HaberRus Ordusu’ndan Arktik’te Tatbikat: Kuzeyden Gelebilecek Saldırılar Simüle Edildi!Rusya, Avrupa ve NATO ülkeleriyle gerilimin tırmandığı bir dönemde Franz Josef Land takımadalarında askeri tatbikat gerçekleştirdi. Kuzey Filosu’nun düzenledi..
what the christ does a dentistry app have loyalty points for
Anyone else having trouble with band.codes? Every time I try to create a new release, I get, "Network error while creating release". Tried multiple machines, networks, browsers but all get the same error.

The mech, the crystal, and now Monkey King? I bet you anything that keeping him suppressed is taking every ounce of strength she's got!

No. It is simple. You failed, Administrator. And the Emperor will hear of it.
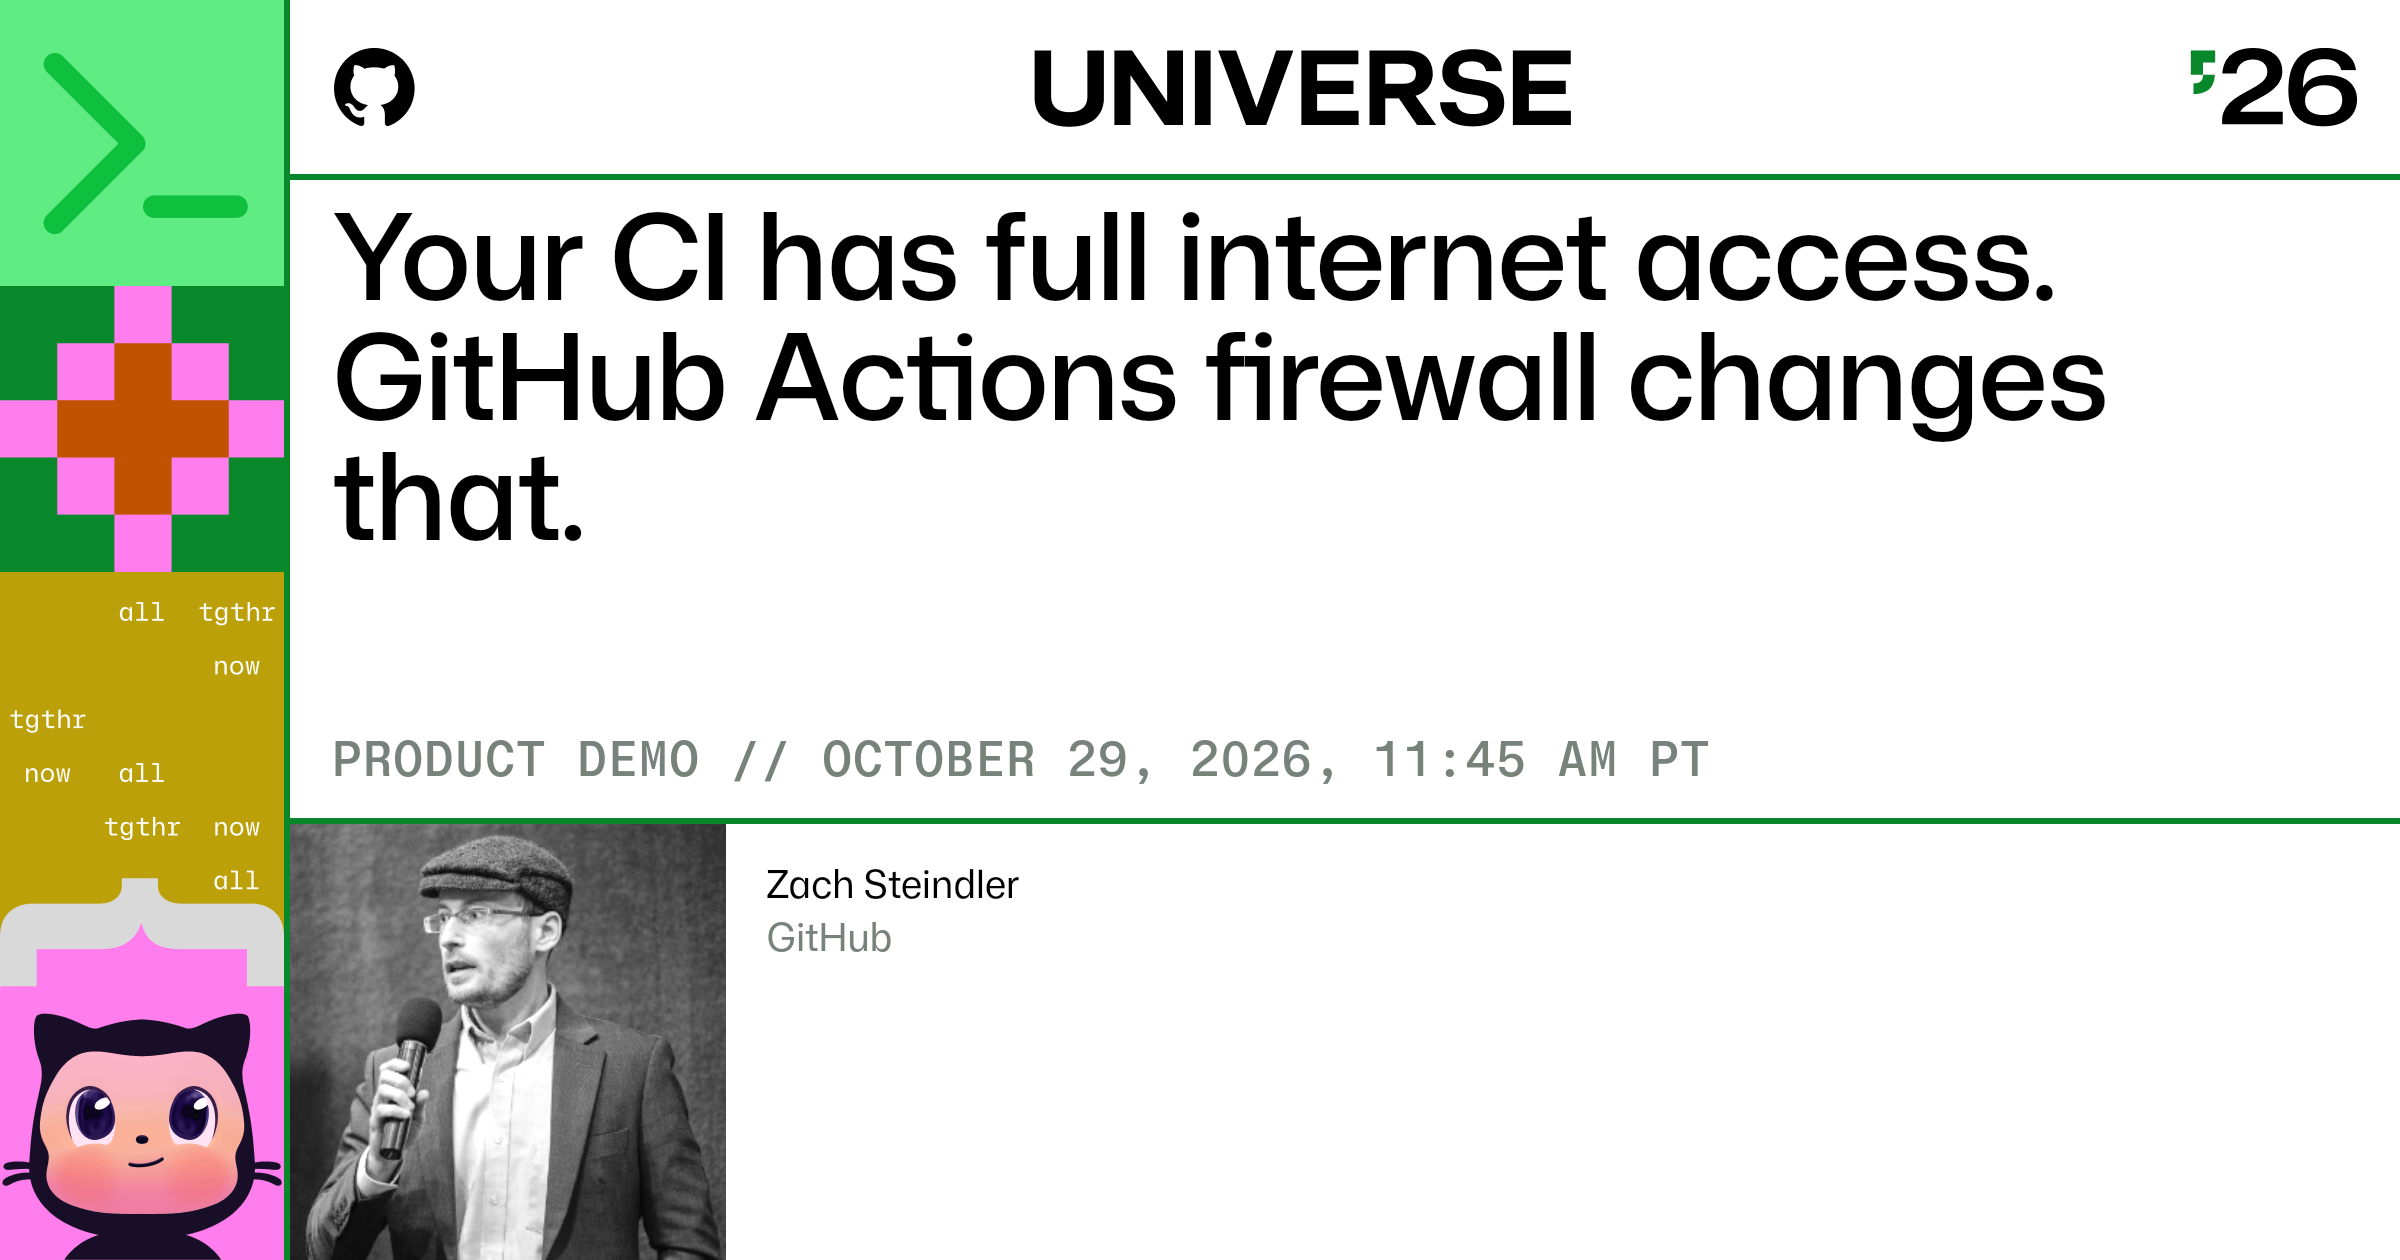
“Your CI has full internet access. GitHub Actions firewall changes that.” Join @steiza for a demo of outbound request visibility and allowlists—and practical ways to limit what your workflows can reach.

What are you doing, Padmé? We're supposed to be undercover.

This is Fungal Weevil
The Monsters Among Us
 www.thebulwark.comThe Monsters Among UsThere is a morbid phenomenon in our politics, apparent both domestically and abroad.
【ご案内】
マジカルミライ2026にて
先行販売 させていただきました新商品が受注開始♪
(https://movic.jp/shop/pages/HatsuneMiku_Series.aspx) movic.jp/shop/pages/HatsuneM…
※一部数量に限りがございますので、
お早めにご購入ください。
 初音ミクシリーズ グッズ通販ページ | ムービック(movic)初音ミクシリーズ グッズ通販ページ | ムービック(movic)初音ミクシリーズのグッズ通販ページです。ご購入はこちらから!
Also discussed: Thinking "betimes" frequently but never saying it out loud. (Ep.350)
The same suspicious installer appeared in two unrelated client environments. Antivirus quarantined it, but I still needed to understand how it arrived.
I wrote up the case for fellow MSPs and defenders: where browser history helped, where my collector fell short, and what remained unresolved. Client details are anonymized.
https://www.kylereddoch.me/blog/client-case-study-tracing-a-suspicious-download-after-quarantine/
 CybersecKyleClient Case Study: Investigating a Quarantined MSIX DownloadAn anonymized case from my client work, with practical lessons for MSPs and defenders on tracing a suspicious download, checking collection gaps, and reporting what the evidence supports.
Protestul camionagiilor italieni a paralizat producția de mozzarella de bivoliță.
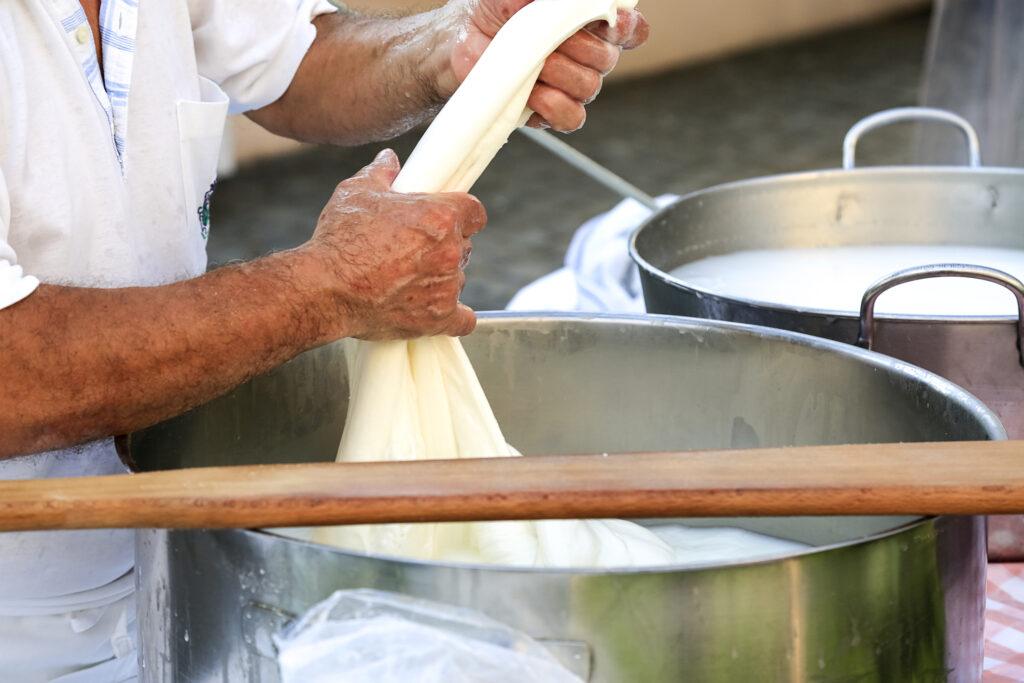
 G4Media.roProtestul camionagiilor italieni a paralizat producţia de mozzarella de bivoliţăProtestul transportatorilor italieni, care durează de aproximativ o săptămână şi care a dus la blocarea livrărilor de produse de bază către supermarketuri
“How GitHub secures open source” — join @anticomputer and @xcorail for seven years of lessons from GitHub Security Lab: make security simple to adopt, build it with community, and understand what AI means for open source. Take ideas straight back to your project.

Am I the only one who thinks we need to either change the way vulns are scored or just have a much larger range say CVSS 1-100 so we can tamp down on the overhyping of Vulns?
It is obvious to me that even if we had real risk scores vulns would be used for FUD.
Hartley's First Law:
You can lead a horse to water, but if you can get him to float
on his back, you've got something.
Buddhism AND sexual orientation? In this economy?
Mastodon.socialIn This Economy? (@[email protected])Buddhism AND sexual orientation? In this economy?
共產黨是不想讓本人獲取範理麗的視角信息,所以要切斷關係。所以不會是本人的視角信息,應該給範理麗找男人。應該是她本來的命格來講,或者根本不講命理,裝出無能為力的樣子,推動關係發展,或者讓範理麗自己努力,實際為自己賣命。假如本人獲取了範理麗的視角信息,那麼這個漏洞就無法填補。
我的兄弟,我的猜測八九不離十吧?
Vendor:
Hewlett Packard Enterprise (HPE)
Products: Unknown product
CVE-2026-79844 - https://www.cve.org/CVERecord?id=CVE-2026-79844
CVE-2026-79846 - https://www.cve.org/CVERecord?id=CVE-2026-79846
CVE-2026-79847 - https://www.cve.org/CVERecord?id=CVE-2026-79847
CVE-2026-79848 - https://www.cve.org/CVERecord?id=CVE-2026-79848
CVE-2026-79849 - https://www.cve.org/CVERecord?id=CVE-2026-79849
CVE-2026-79850 - https://www.cve.org/CVERecord?id=CVE-2026-79850
CVE-2026-79851 - https://www.cve.org/CVERecord?id=CVE-2026-79851
... a perfect 10. you know who else is a 10? :neobot_blush_hide:
Fantastic premise, setup, and punchline.
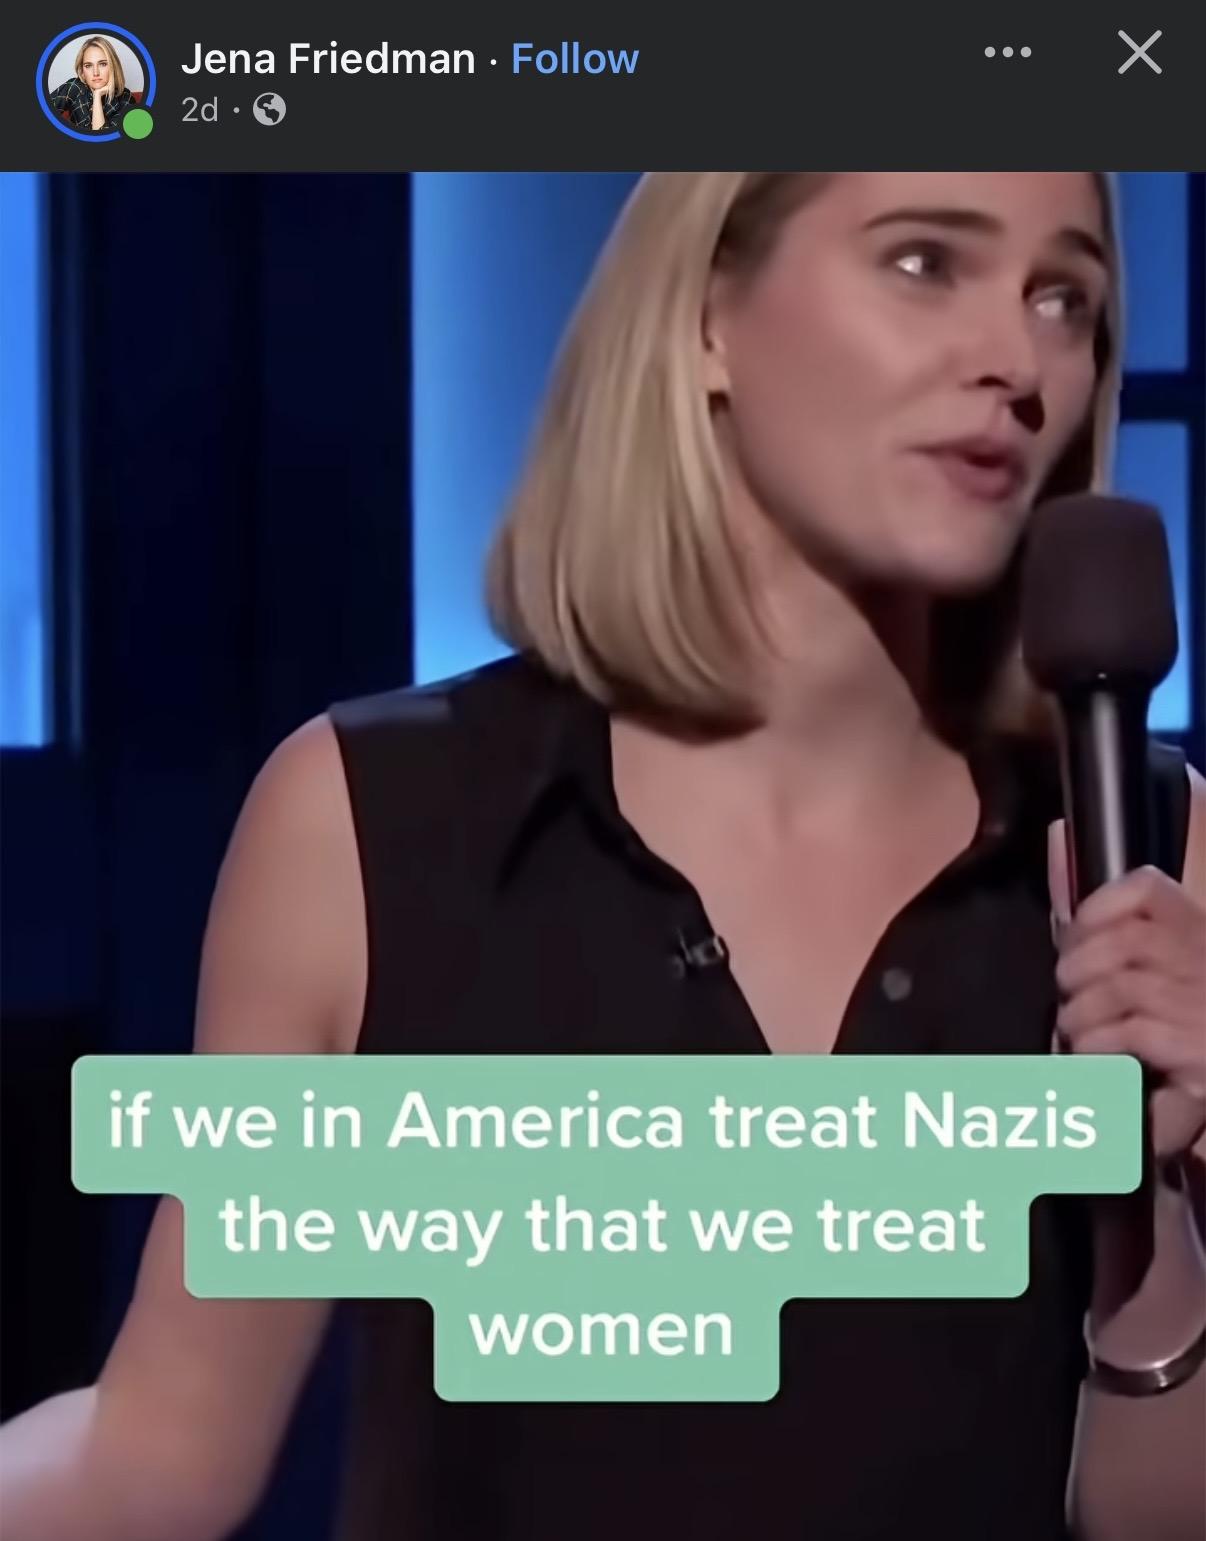
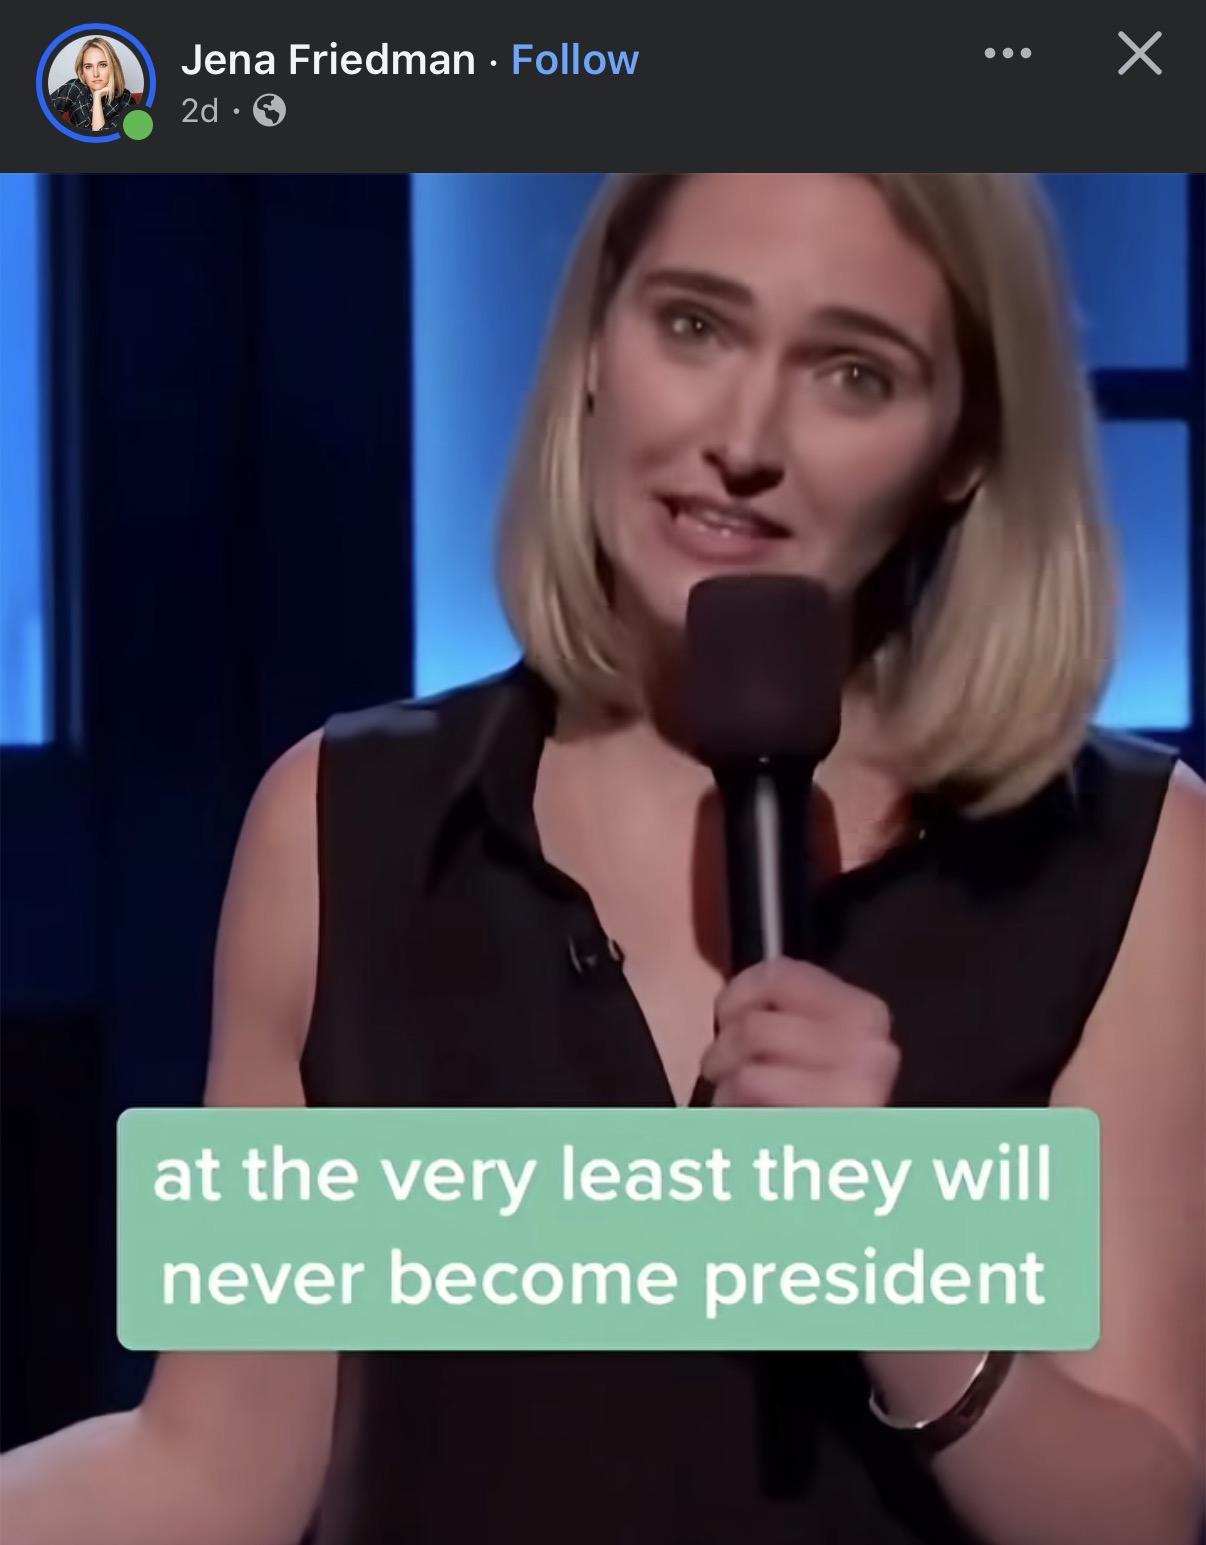
Nereden nereye! "Yakışıklı Mısırcı" 6,5 milyon TL'lik reklam anlaşmasına imza attı
https://abcgazetesi.com.tr/magazin/nereden-nereye-yakisikli-misirci-65-milyon-tllik-reklam-anlasmasina-imza-atti-875051?_unique_id=6ada610d6617d
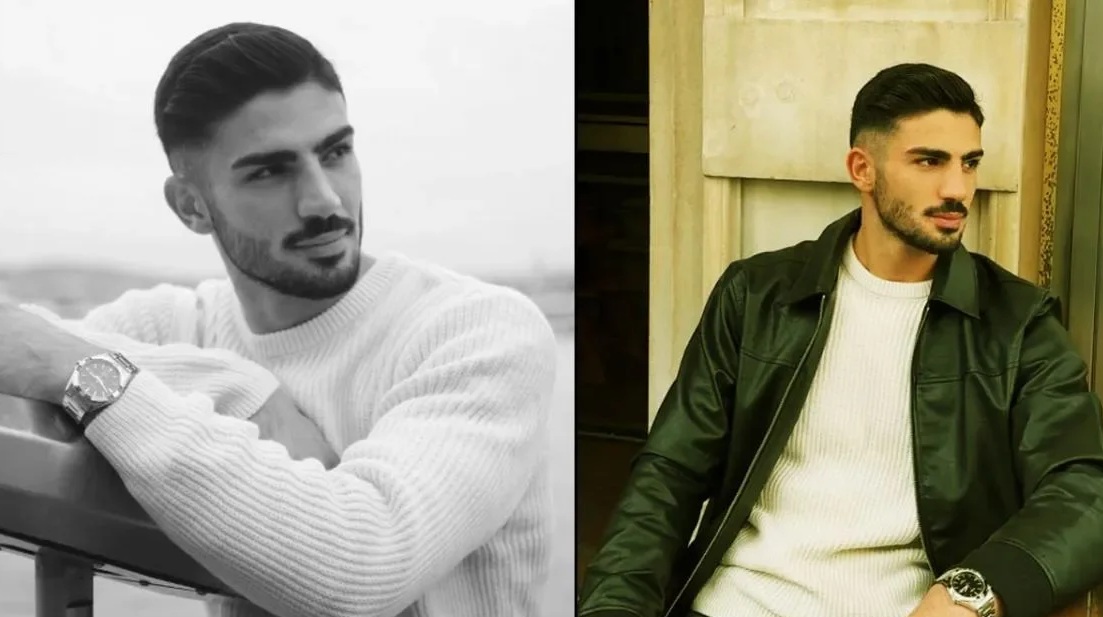 ABC HaberNereden nereye! "Yakışıklı Mısırcı" 6,5 milyon TL'lik reklam anlaşmasına imza a..Karaköy’de mısır ve kestane satarken çekilen görüntüleriyle tanınan Alper Temel, bu kez 6,5 milyon TL’lik reklam anlaşması iddiasıyla gündeme geldi. “Yakışıkl..