X XFediYour place in the Fediverse
XFEDI

Conversation

ActivityPub
↳ In reply to a post

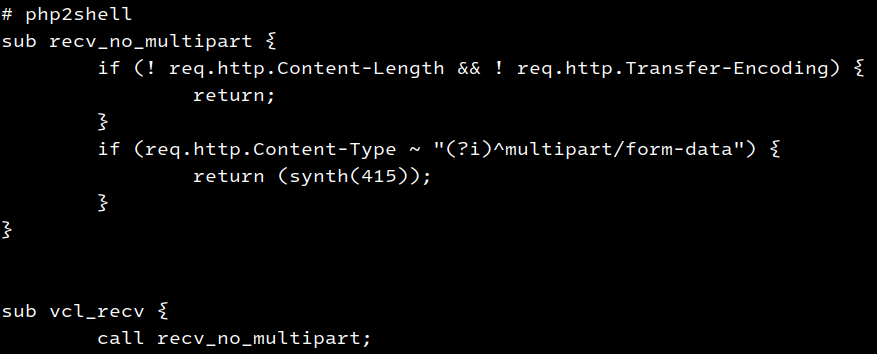
Thanks to a client, I looked at CVE-2026-109618 / CVE-2026-109619 a bit longer:

The most relevant OOM vector seems to be request body processing, and, more specifically, multipart/form-data / rfc7578 processing.

https://github.com/php/php-src/security/advisories/GHSA-w8hw-w9fx-j79w
https://github.com/php/php-src/security/advisories/GHSA-6wmf-4rv5-p3rp
GitHubRCE via OOM corruption## Summary PHP uses `longjmp()` for out-of-memory (OOM) errors to exit the current context and abort handling of the request. In some contexts, request memory is temporarily reachable before it ...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Oct 21, 2026 · 20:29 UTC

Replies