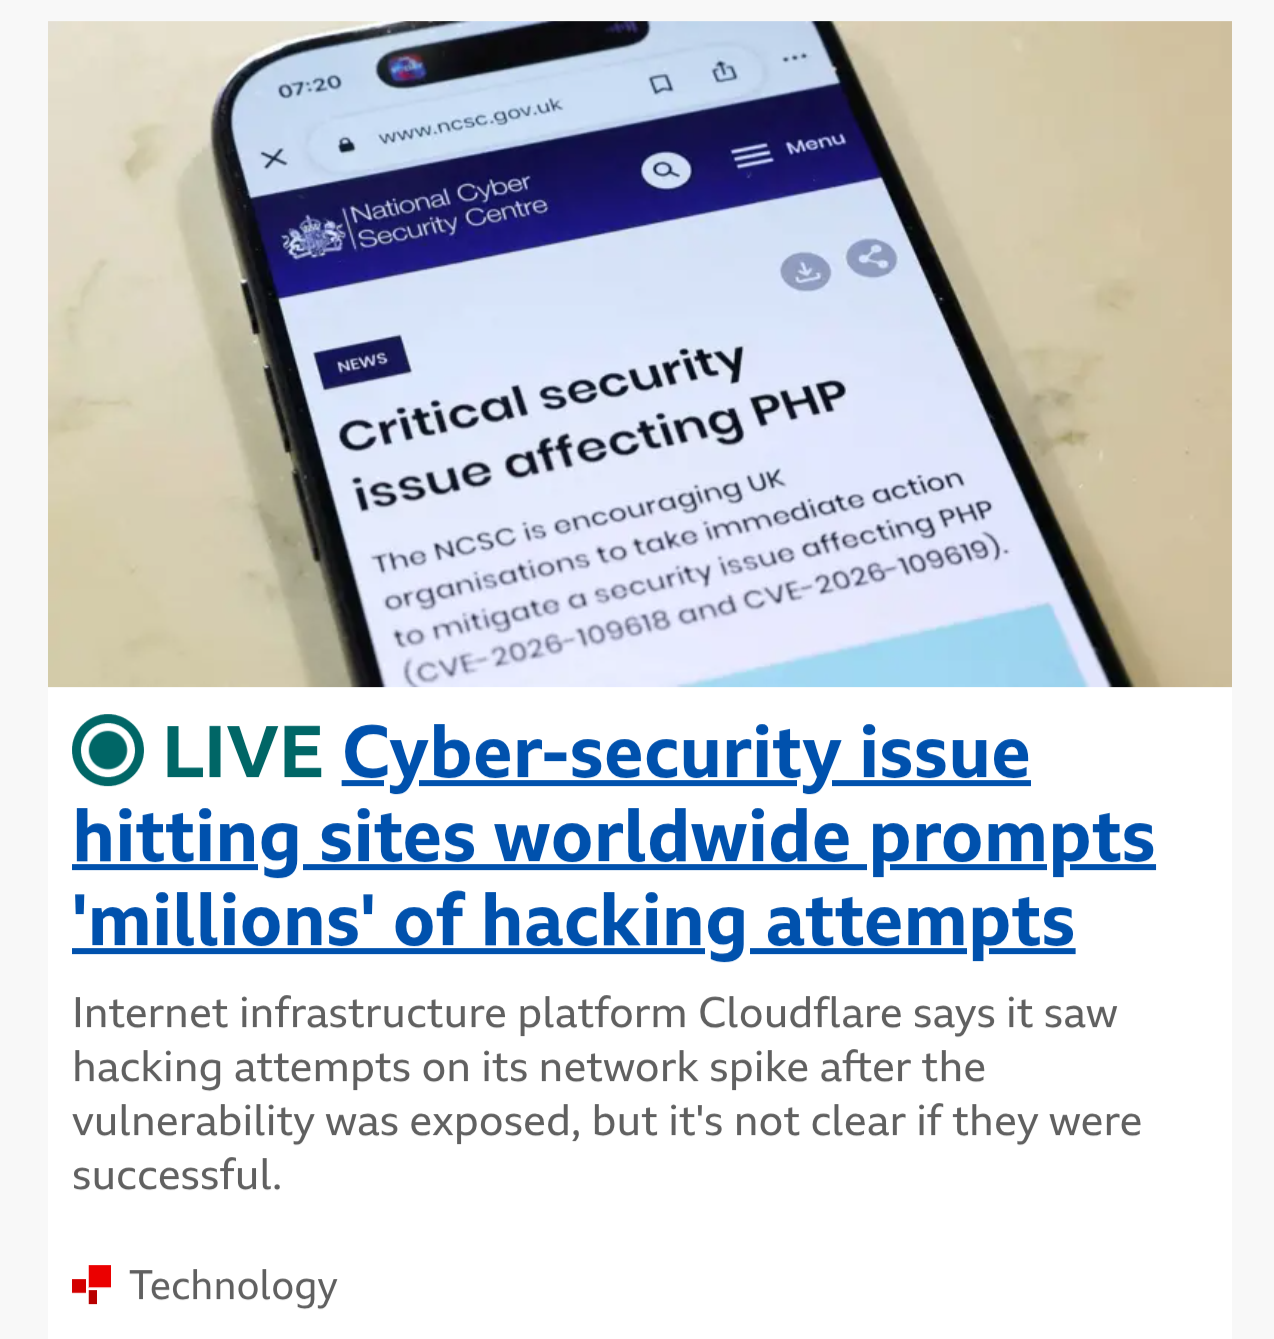
This is normal activity for any publicly exploited vulnerability, especially in web stack, edge device or protocol.
Yes, this PHP vuln is bad and allot of IoT/OT/embedded devices, EoL kit is not going to get patched (CCTV, access control, moxas, plcs etc) but allot of that shouldn't be directly accessible from the internet.
There are also going to be a large number of container images that will probably never get updated as they are orphaned/abandoned.
1/2