🚨 Rapid Response: Four vulnerabilities in Plex Media Server can be chained to achieve unauthenticated remote code execution. Plex reports compromised servers being used to run cryptocurrency miners and proxy software.
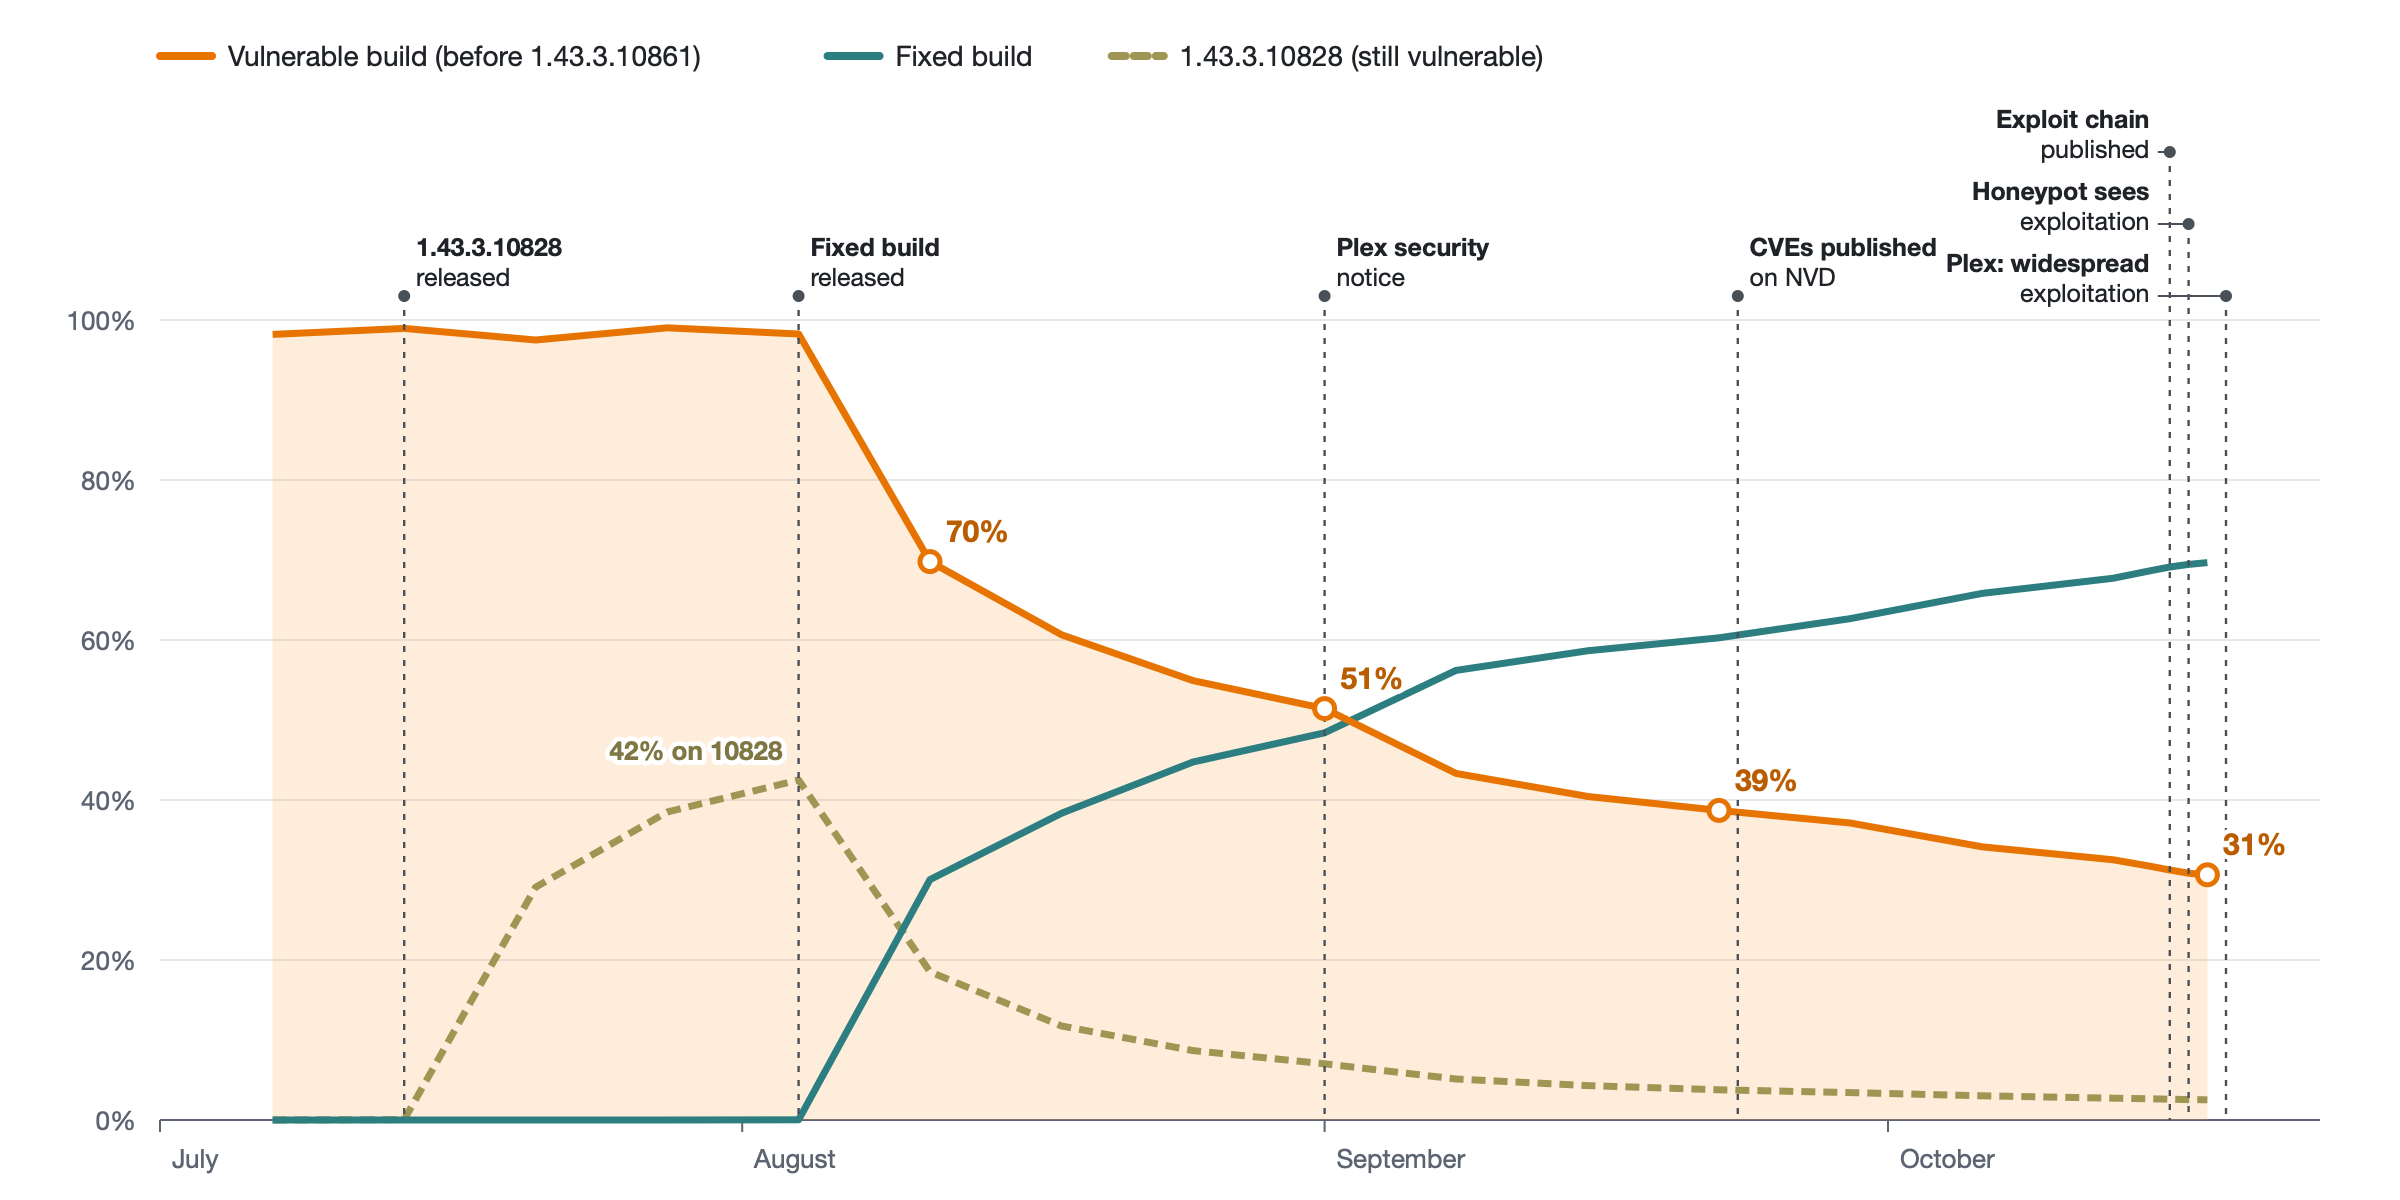
Censys ARC observes ~340,000 Internet-exposed Plex Media Server hosts. Roughly 30% run a vulnerable build, and nearly 8,000 run an early build that may be mistaken for patched.
Despite publication of the exploit chain and reports of exploitation, fewer than 2% of still-vulnerable hosts upgraded in the following three days.
Plex advises that previously exposed, unpatched servers may already be compromised and require additional remediation beyond patching.
Full Censys ARC advisory: https://censys.com/advisory/cve-2026-96652-cve-2026-96654-cve-2026-96655-cve-2026-96656/
#CensysARC #Cybersecurity #VulnerabilityManagement #Plex #InfoSec
 CensysOctober 20 Advisory: Plex Media Server Remote Code Execution Chain [CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, CVE-2026-96656] - CensysCVE-2026-96652, CVE-2026-96654, CVE-2026-96655, and CVE-2026-96656 are four flaws in Plex Media Server before build 1.43.3.10861.