
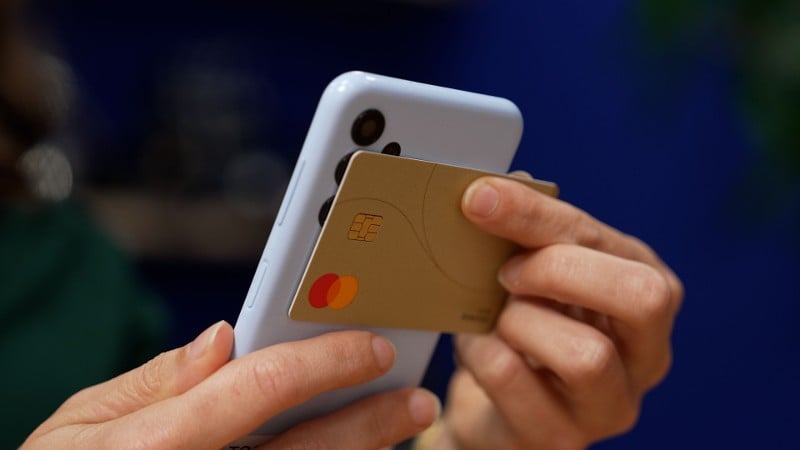
170 customers of Dutch banks fell victim to a social engineering attack that used relaying of NFC communication to their contactless bank card: victims were tricked to install a malicious app on their phone and hold their contactless bank card to it so that the criminals, pretending to be from the bank's helpdesk, could do an NFC relay attack to a payment terminal or ATM https://www.politie.nl/nieuws/2026/oktober/20/07-twee-verdachten-aangehouden-in-onderzoek-naar-nieuwe-vorm-van-bankhelpdeskfraude.html This type of attack has happened before on Czech banks in 2023, but I think it's the first time it happened in the Netherlands.
Already over 10 years ago in master thesis research of Jordi van den Breekel https://www.linkedin.com/in/jbreekel we were surprised to find that contactless terminals had very long time-outs, sometimes over 50 seconds, which makes relay attacks less tricky that one would hope.
 www.politie.nlTwee verdachten aangehouden in onderzoek naar nieuwe vorm van bankhelpdeskfraude380.000 euro schade bij zo'n 170 slachtoffers. Dat waren de cijfers waarmee het Rotterdamse Team Cybercrime werd geconfronteerd in de drie weken die het onderzoeksteam zicht had op de servers van een crimineel samenwerkingsverband. Die criminelen hielden zich bezig met een nieuwe vorm van bankhelpdeskfraude, waarbij slachtoffers de bankpas moesten scannen met hun mobiele telefoon – waarbij op afst