Mitigating CVE-2026-111943 on #Debian:
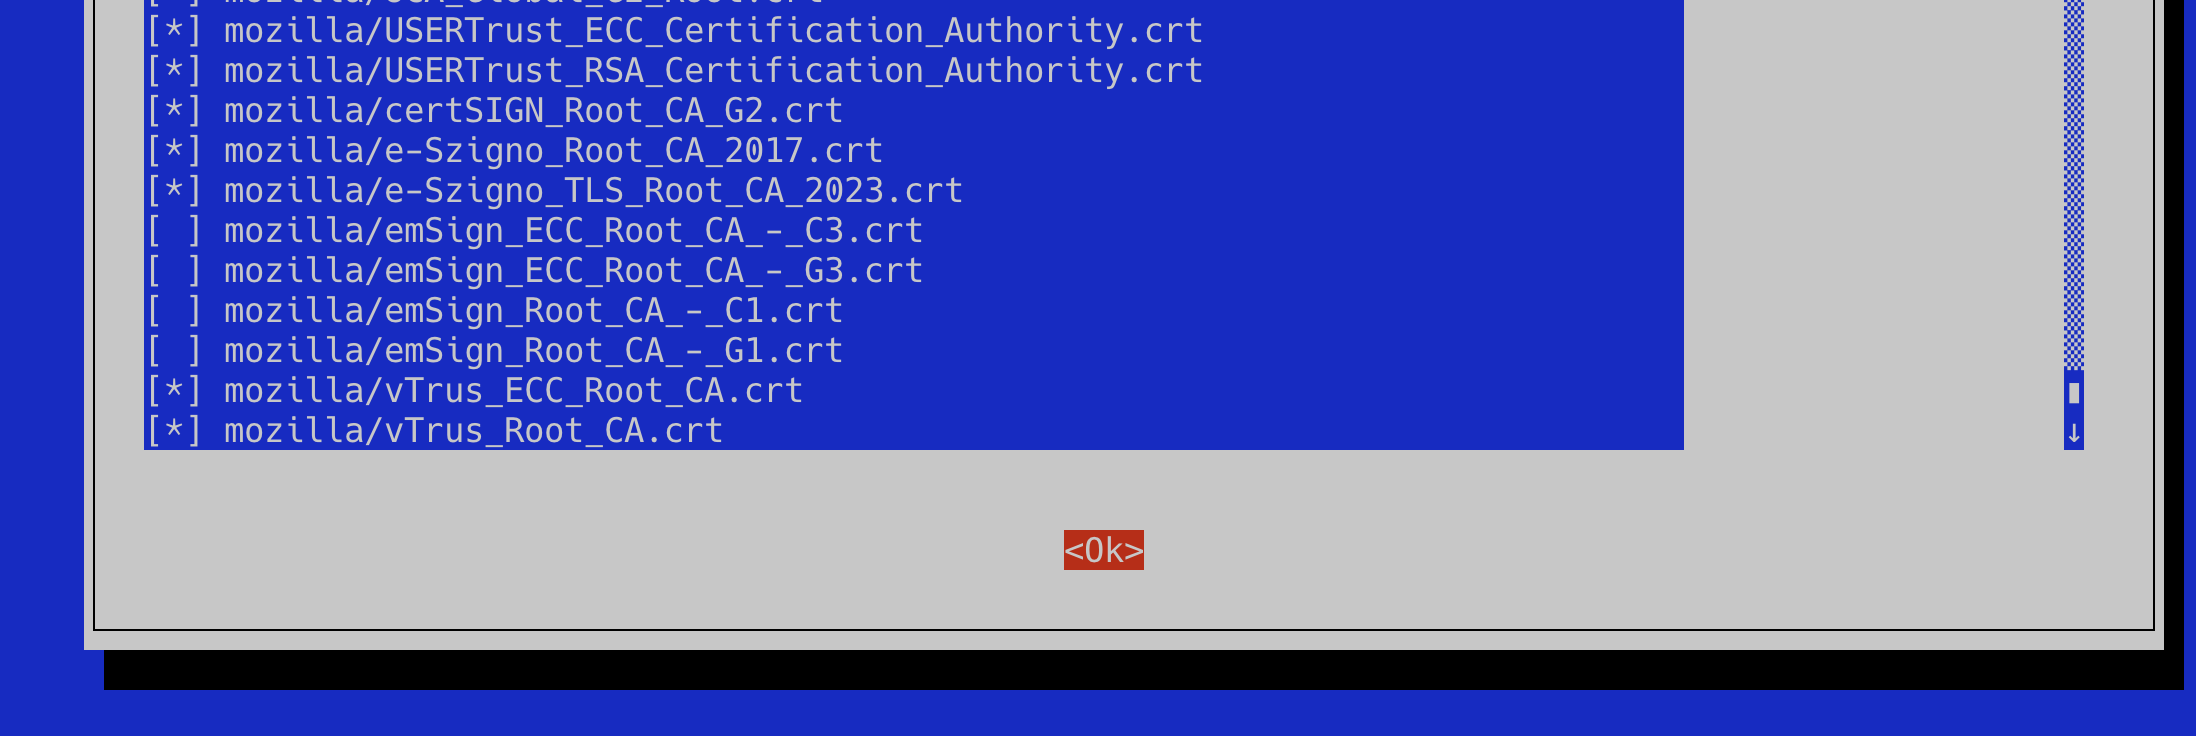
- sudo dpkg-reconfigure ca-certificates
- Select "ask" and deselect the following entries:
mozilla/emSign_ECC_Root_CA_-_C3.crt
mozilla/emSign_ECC_Root_CA_-_G3.crt
mozilla/emSign_Root_CA_-_C1.crt
mozilla/emSign_Root_CA_-_G1.crt
- Hit <Ok>
Alternatively you can edit /etc/ca-certificates.conf manually and add the specific entries:
!mozilla/emSign_ECC_Root_CA_-_C3.crt
!mozilla/emSign_ECC_Root_CA_-_G3.crt
!mozilla/emSign_Root_CA_-_C1.crt
!mozilla/emSign_Root_CA_-_G1.crt
...and sudo update-ca-certificates