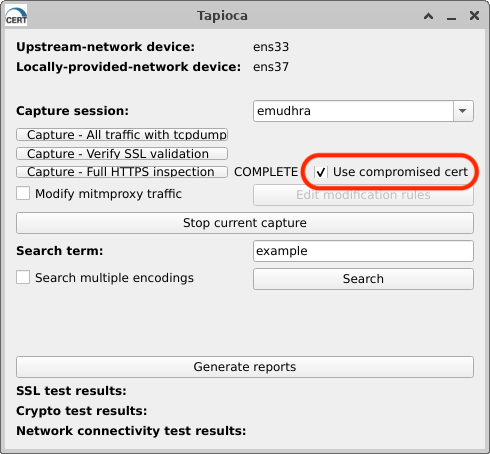
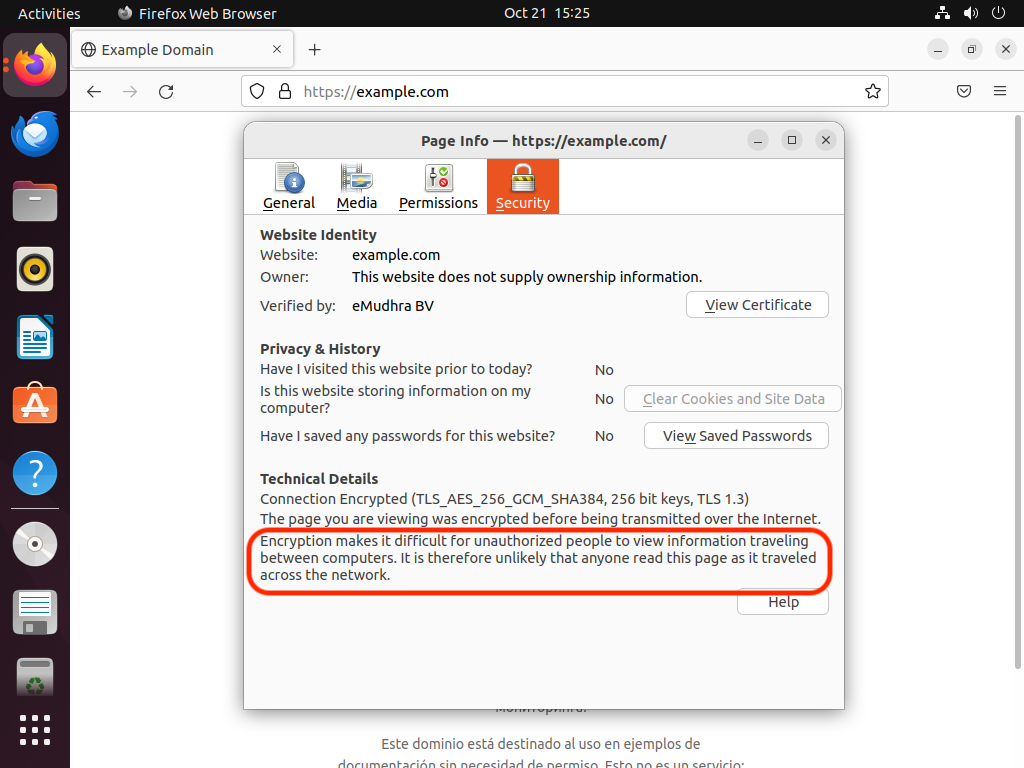
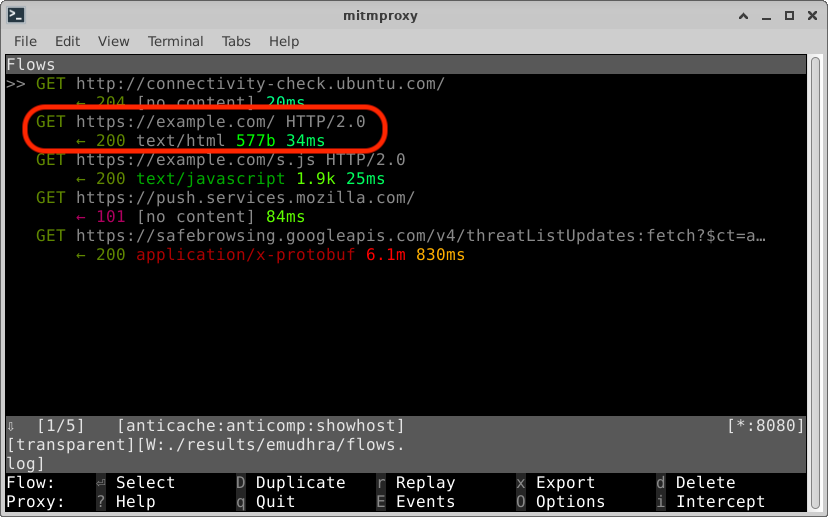
Just for the lulz, I've updated tapioca to support the use of a compromised eMudhra certificate, rather than a self-signed certificate.
If you've ever wanted to intercept HTTPS traffic of <thing>, but <thing> lacks the ability to import self-signed certificates to be trusted, this could be your day!
For some reason Windows and Ubuntu both stopped trusting something in the eMudhra certificate chain a couple of years ago. But plenty of other platforms should allow their HTTPS traffic to be intercepted. So go ahead and see what your TV or smoker or whatever is doing!