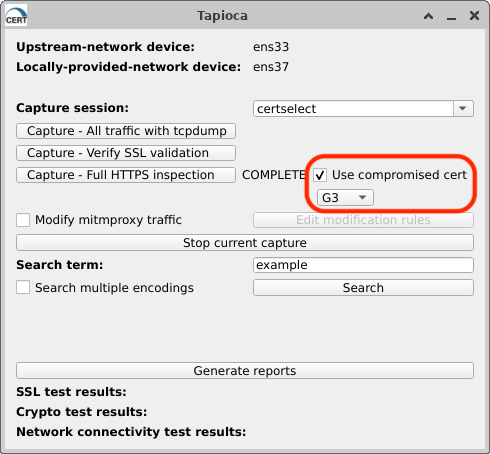
Just to test this out, I've tried a few things out with this compromised eMudhra cert. And in doing so, I realized that there were some differences between what accepts an eMudhra intermediate with a root in emSign Root TLS CA - G3 vs. one with a root in AAA Certificate Services. As such, I've added a drop-down to allow you to pick which one you want in tapioca.
For example, both RHEL (Rocky) 10.1 and Mint 22.3 allow (if you're not fully up to date to pick up this October fun) the G3 root, but not the AAA root.
Some of the physical devices I've tested:
- Old Pixel 3 : ❌
- Alfred Camera : ❌
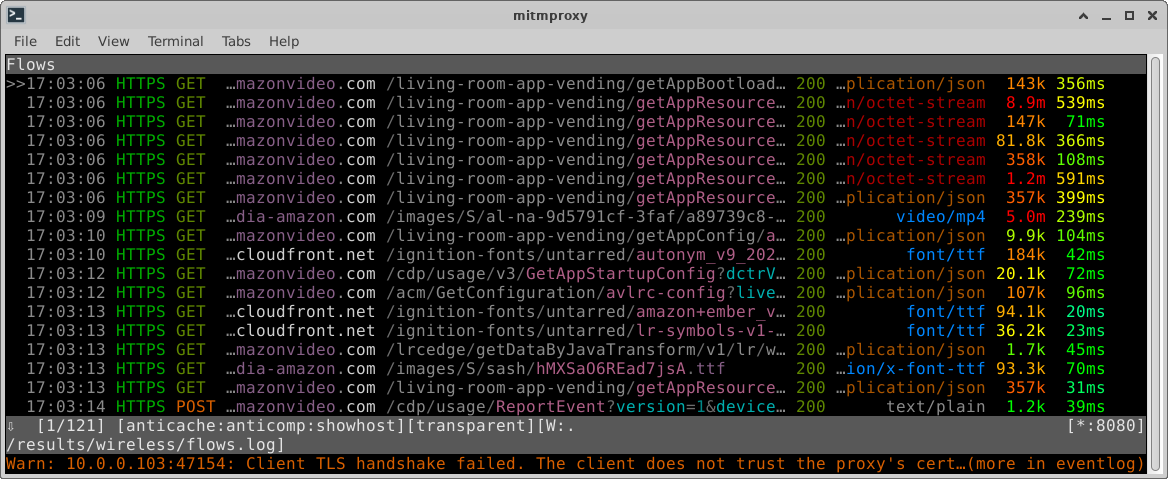
- Old Amazon Fire TV Stick: ✅
So, it's not a magic bullet. It seems that some systems didn't support eMudhra certs even before this month's fun. And supported systems that are getting updates will surely drop support for this cert if it had it before.
BUT, at least with this small sample set, I'd bet that this will open up the ability to see some traffic contents that were previously unavailable on some systems.