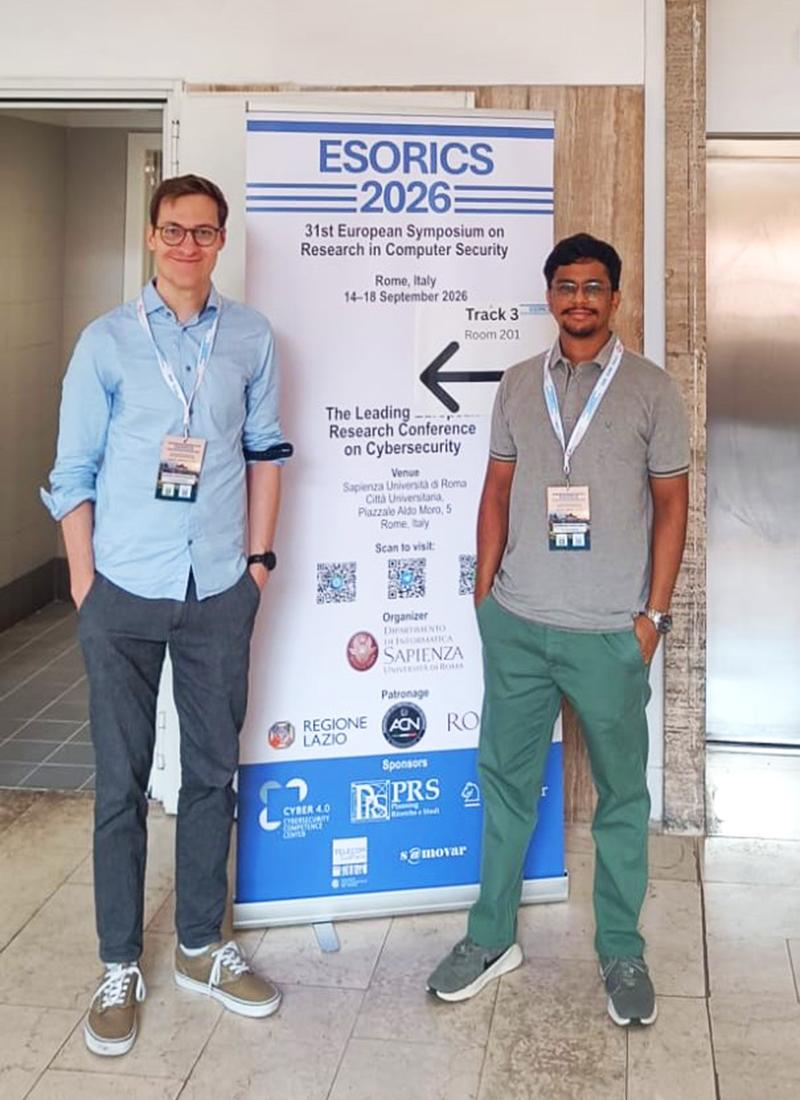
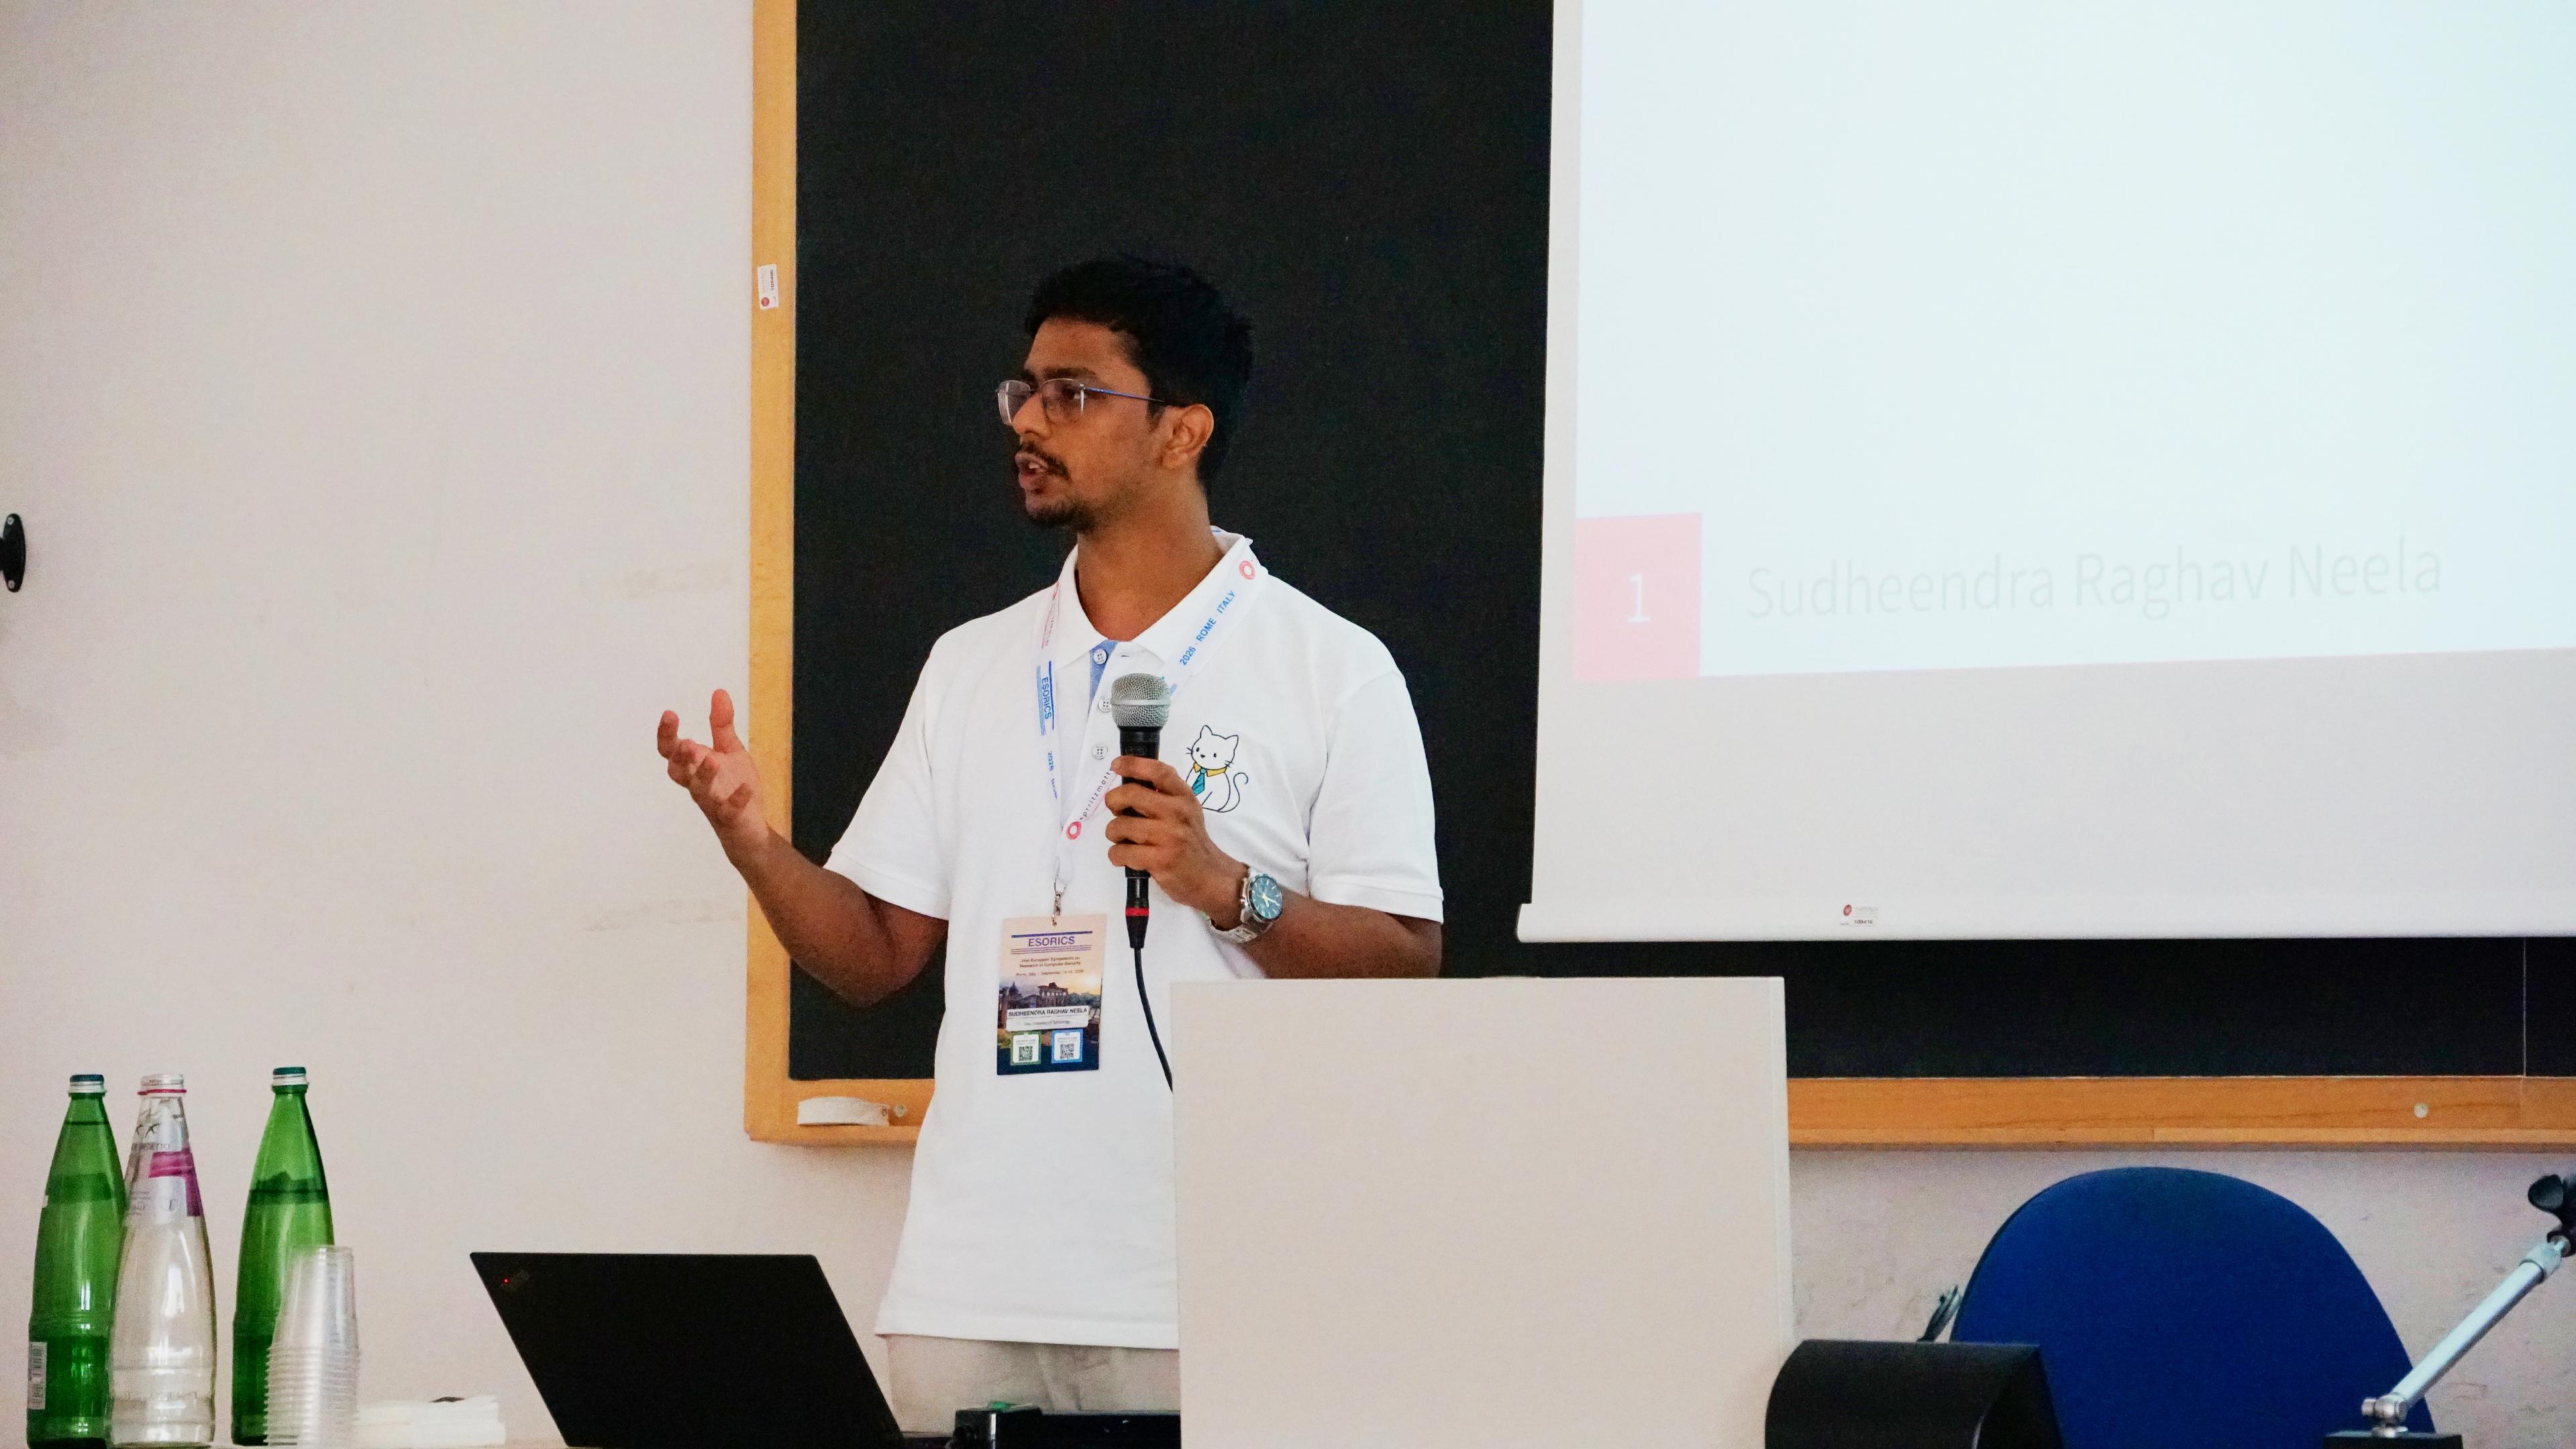
ISEC Researchers Florian Draschbacher and Sudheendra Raghav Neela went to ESORICS 2026 in Rome, Italy, to present their research!
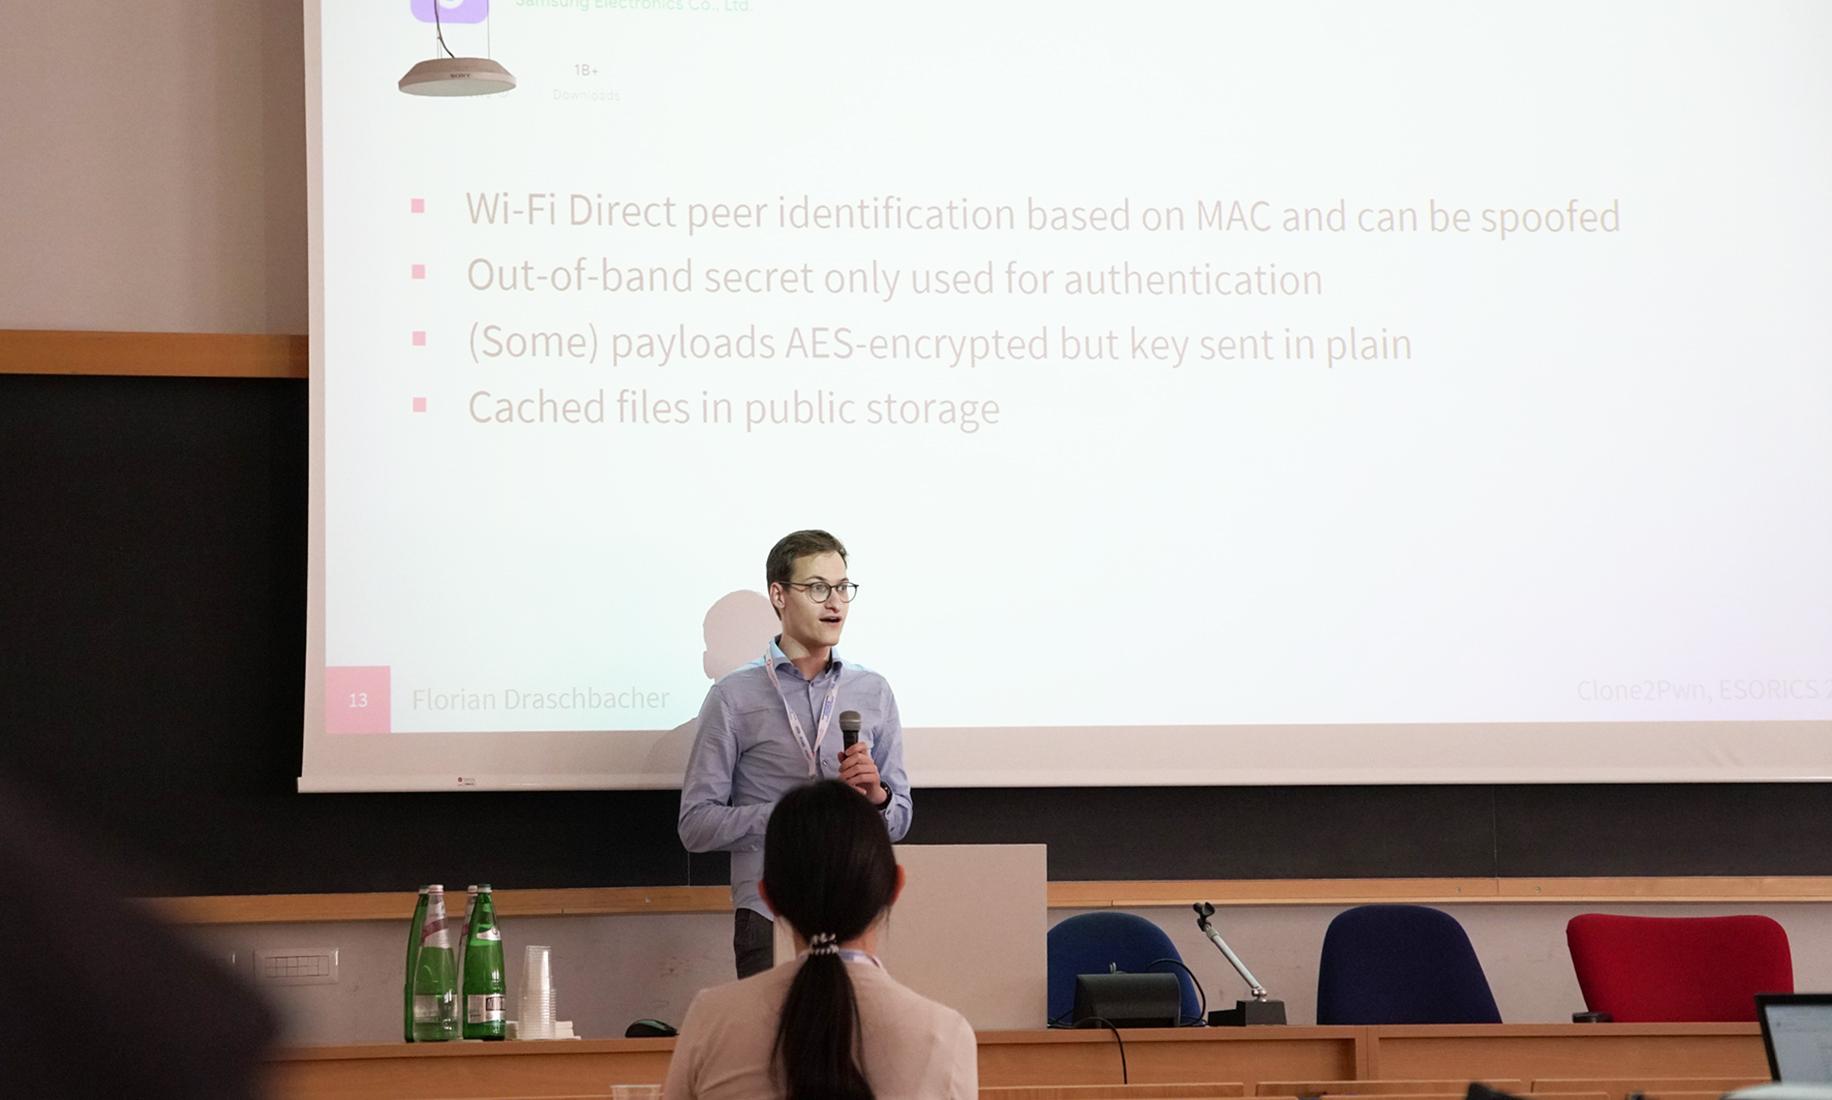
Florian presented "Clone2Pwn: A Systematic Security Analysis of Data Migration Tools in the Android Ecosystem", in which they found severe security flaws in phone data migration tools from 7 major Android vendors (12B+ downloads), letting nearby attackers eavesdrop on (or even inject) sensitive user data during transfers. 8 CVEs (so far!) and 5 high-severity.
📑 Clone2Pwn: A Systematic Security Analysis of Data Migration Tools in the Android Ecosystem:
https://floriandraschbacher.com/papers/esorics26-clone2pwn.pdf
Sudheendra presented "A Systematic Look at Quality-of-Service Feature Effects on Side Channels in AMD SEV-SNP", showing that AMD's QoS resource-control extensions (meant to isolate "noisy neighbor" workloads) create new side channels on AMD SEV-SNP confidential VMs, mounting RSA attacks and keystroke-timing attacks, website fingerprinting, and an amplified cache covert channel with a malicious hypervisor.
📑A Systematic Look at Quality-of-Service Feature Effects on Side Channels in AMD SEV-SNP:
https://snee.la/posts/amd-qos-side-channels/
 sneelaA Cat with an MBA: How AMD QoS Features Enable Side Channels on SEV-SNPForeword This blog post is a summarized and introductory write up of our paper recently accepted at ESORICS 2026 to be presented in Rome, Italy between September 14-16, 2026: “A Systematic Look at Quality-of-Service Feature Effects on Side Channels in AMD SEV-SNP”. Not all the scientific details are mentioned in this blog post. If you’re interested, there’s a full paper with more rigorous, peer-re