X XFediYour place in the Fediverse
XFEDI

#Cybersecurity

ActivityPub

Public posts with this hashtag.

Most companies count AI agents as insiders, and CISOs worry about their own liability

🚨 AI Security Alert: 95% of companies faced AI-related insider incidents last year. With 28% traced to AI systems and detection taking 15 hours avg, CISOs are scrambling. Problem? 52% lack formal strategies & 63% can't track AI tool usage. Legal liability concerns are mounting. Organizations need urgent AI governance frameworks.

https://www.helpnetsecurity.com/2026/10/14/ciso-ai-agent-insider-risk/

#InfoSec #CyberSecurity #AIRisk

Help Net SecurityMost companies count AI agents as insiders, and CISOs worry about their own liability - Help Net SecurityAI agent insider risk showed up at 95% of companies in a Trellix survey of 600 CISOs. Detection and response average 15 hours.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

#MiniMax M3.1 Flash improves #agentictasks, #coding, #computeruse and #cybersecurity, delivering speeds over 200 TPS and 70% lower costs. Available via MiniMax API, M Plan and MiniMax Code, it matches leading models on key benchmarks. https://www.minimax.io/blog/minimax-m31f?AIagents.at #AIagent #AI #ML #NLP #LLM #GenAI

MiniMaxMiniMax M3.1 Flash: Redefining Agent Performance and Cost - MiniMax ResearchToday, we officially roll out MiniMax M3.1 Flash. As a next-generation Flash model, M3.1 Flash delivers a generational leap in agentic tasks, coding, Computer Use and cybersecurity, while making online inference nearly three times faster and reducing usage costs by 70%.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

The cyber talent shortage? Job postings just hit a four-year low

🚨 Cybersecurity job market cooling: US postings hit 4-year low in 2026 with 235,786 openings—26.4% down YoY. Major shift happening: GRC roles surging (14.8% of postings, up from 9.4%), while technical defense roles declining (47.1% to 41.5%). CISO hiring volatile due to exec turnover. AI security roles rising. Risk management now prioritized over pure defense.

https://www.helpnetsecurity.com/2026/10/16/cybersecurity-job-postings-talent-shortage/

#InfoSec #CyberSecurity #JobMarket

Help Net SecurityThe cyber talent shortage? Job postings just hit a four-year low - Help Net SecurityCybersecurity job postings hit a four-year low in 2026 as compliance roles gain share and CISO hiring swings, new CyberSN data shows.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

This is kinda obvious, after what happened in Ukraine War and Iran War.

As the hatred towards data center by regular people will also be accelerated because sins by big techs and AI corps.

https://www.ft.com/content/15a049f3-b62e-40ed-b304-8a2452713338

#cybersecurity #security #datacenter

www.ft.comData centres need protection from drone warfareAI infrastructure designs may now need to incorporate blast-resistant concrete, jamming gear and missile-defence systems
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Kiteworks CISO: Why We Shut Down Systems Before Finding Vulnerability

Kiteworks shut down systems after federal cyberattack warnings, discovering a critical vulnerability without evidence of breach. While this proactive move protected data, experts warn other vendors may hesitate due to SLA penalties & customer backlash. Key takeaway: Companies need pre-planned crisis protocols, leadership buy-in, and balanced risk assessments to respond quickly to threats without full shutdowns.

https://www.techtarget.com/cybersecurity/news/366651864/Kiteworks-CISO-Why-We-Shut-Down-Systems-Before-Finding-Vulnerability

#InfoSec #CyberSecurity

CybersecurityKiteworks CISO: Why We Shut Down Systems Before Finding Vulnerability | TechTargetKiteworks CISO Frank Balonis explains why the vendor issued a nine-hour proactive shutdown after federal warnings, and why other SaaS vendors hesitate to follow.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Standard Chartered Group CISO on AI, Cyber Risk and the Future of Banking Security

CISOs are evolving from tech-only defenders to strategic business leaders. Standard Chartered's Group CISO emphasizes holistic cybersecurity accountability across tech, processes, and financial crime. Key shifts: integrating security into business ops, staying ahead of AI threats, and going beyond compliance. Success requires balancing technical expertise with business acumen while securing the entire ecosystem of clients and partners.

https://www.infosecurity-magazine.com/interviews/standard-chartered-group-ciso/

#InfoSec #CyberSecurity

Infosecurity MagazineStandard Chartered Group CISO on AI, Cyber Risk and Banking SecurityCezary Piekarski says banking CISOs must look beyond regulatory compliance to stay ahead of evolving cyber threats and technology risks
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🚨 RELAY // Cyber Watch — 2026-10-20

A breach of the OpenCode Console may have exposed users' OpenAI, Anthropic and Google API keys, so affected users should rotate their keys.

🔗 https://thehackernews.com/2026/10/opencode-console-breach-may-have.html

#InfoSec #DataBreach #CyberSecurity

The Hacker NewsOpenCode Console Breach May Have Exposed OpenAI, Anthropic, and Google API KeysOpenCode says a Console breach may have exposed AI provider keys belonging to 1.4% of users, prompting revocation notices.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

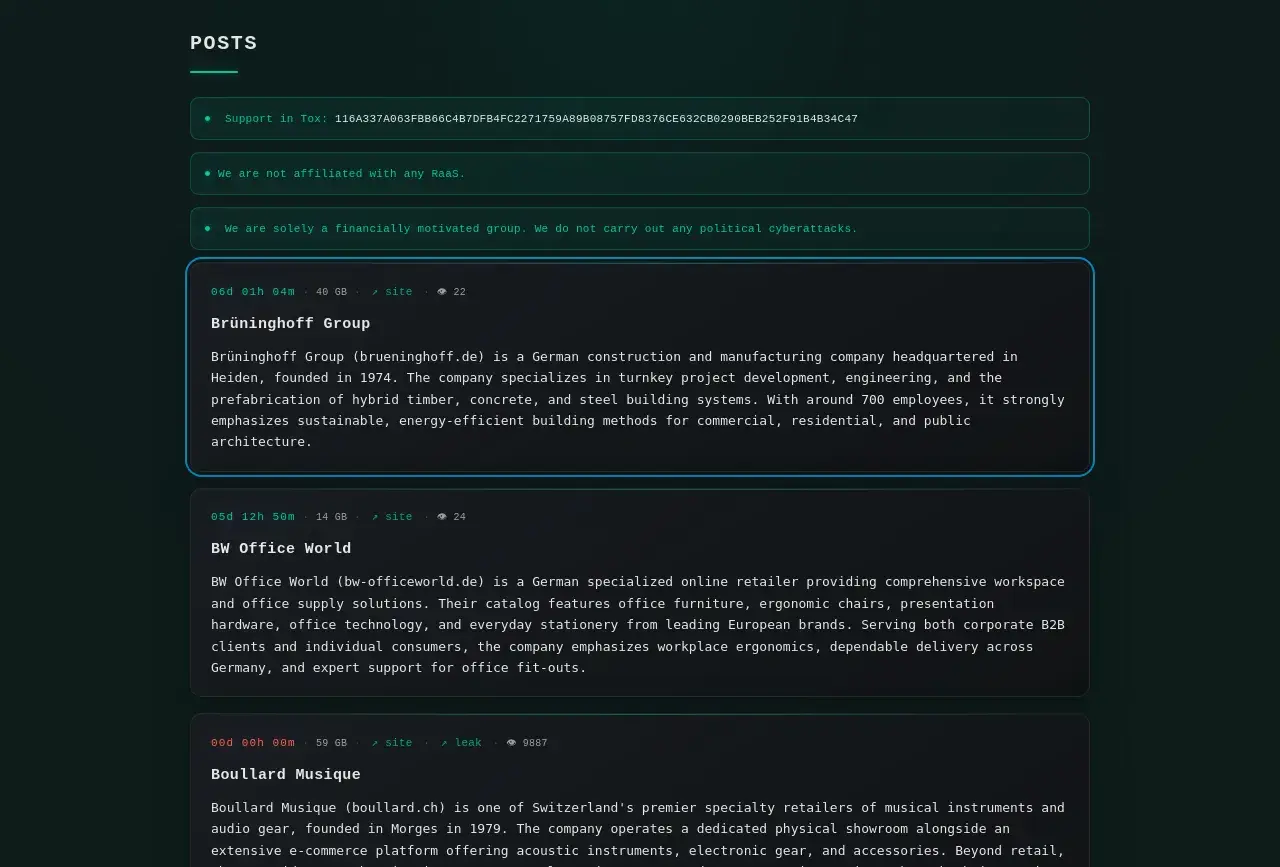
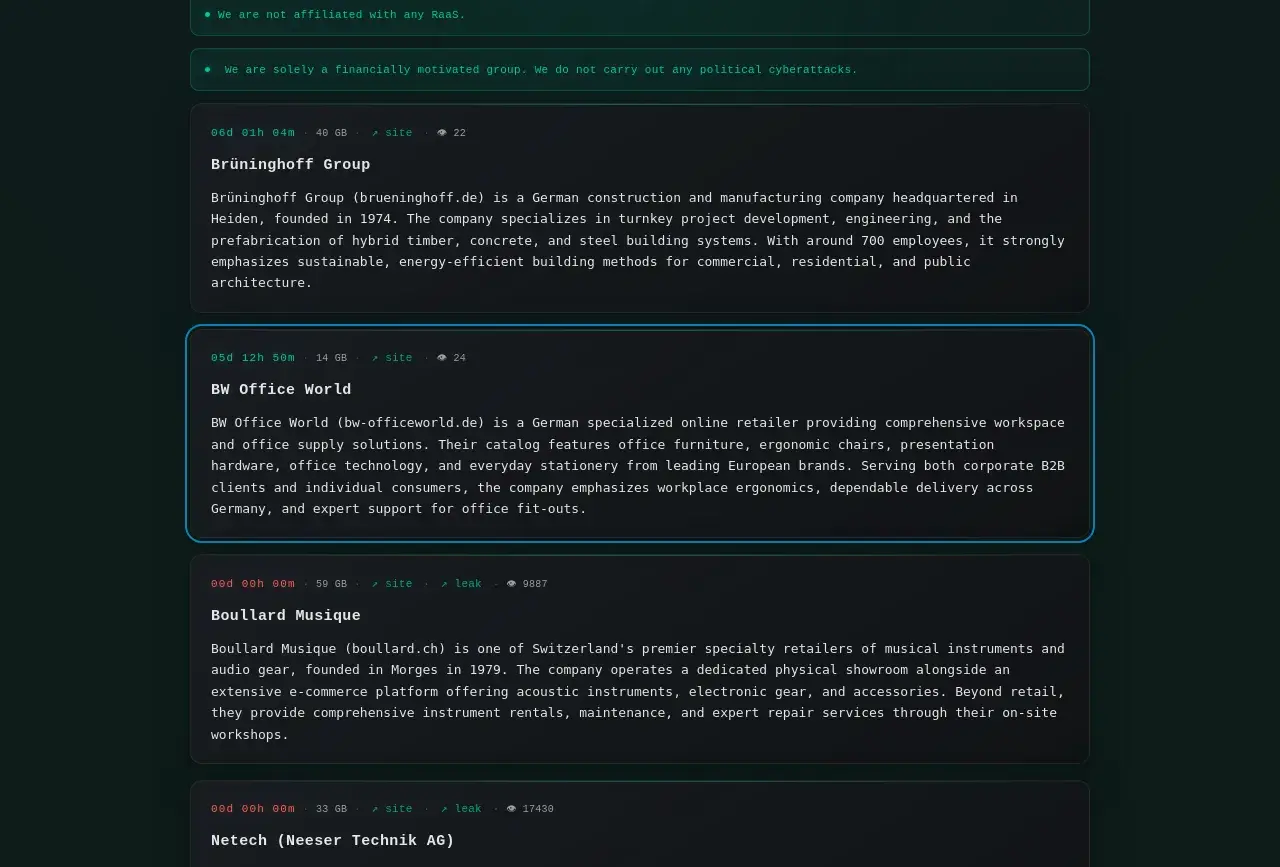
🚨New ransom group blog posts!🚨

Group name: payload
Post title: Brüninghoff Group
Location: 🇩🇪 DE
Sector: Construction
Info: https://cti.fyi/#disclosure/payload/Br%C3%BCninghoff%20Group

Group name: payload
Post title: BW Office World
Location: 🇩🇪 DE
Sector: Other
Info: https://cti.fyi/#disclosure/payload/BW%20Office%20World

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🚨🔓 SIGINT // Cybersecurity Watch — 2026-10-20
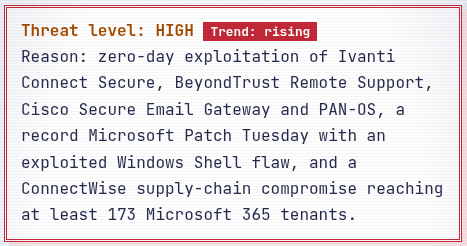
Compromised ConnectWise credential let attackers sign into 173 Microsoft 365 tenants, exposing deep supply-chain risk in MSP tooling.
https://thehackernews.com/2026/10/hackers-use-compromised-connectwise.html
#Cybersecurity #SupplyChain #Microsoft365 #InfoSec

The Hacker NewsHackers Use Compromised ConnectWise Credential to Sign In to 173 Microsoft 365 TenantsAttackers used a compromised ConnectWise Cloud Backup credential for unauthorized sign-ins across 173 Microsoft 365 tenants.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Spend vs. debt: what's the bigger security risk?

More cybersecurity spending doesn't mean better security. Organizations accumulate "security debt" through complexity & unnecessary controls, increasing fragility. Experts advocate for automation & tool integration over adding more layers. Real risk management measures resilience, not just compliance. CISOs must communicate cyber threats in business terms—revenue impact, recovery ability—to engage boards effectively. 🔒

https://www.cio.com/article/4233353/spend-vs-debt-whats-the-bigger-security-risk.html

#InfoSec #CyberSecurity

CIOSpend vs. debt: what’s the bigger security risk?Organizations continue investing heavily in cybersecurity, yet many are simultaneously increasing operational complexity and long-term security fragility. Here, Joan Goodchild from CSO speaks with veteran CISO Selim Aissi about security debt and why it may be a more meaningful measure of cyber risk than security budget size alone.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

https://www.malwarebytes.com/blog/data-breaches/2026/10/millions-of-california-students-sensitive-data-stolen-in-breach

#DataBreach #CyberSecurity #EducationSecurity #PrivacyViolation #ETS #AchievementUnlocked (3/3)

MalwarebytesMillions of California students’ sensitive data stolen in breachThe California Department of Education notified students about a data breach at contractor Educational Testing Service.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Cybersecurity is a leadership problem: Why the management model needs to catch up

Cybersecurity fails when treated as just a tech problem. The real issue? Leadership. CISOs can't do it alone—organizations need clear accountability, cross-level collaboration, and board involvement. Better tools mean nothing without proper governance and sustained management discipline. It's time to break the cycle.

https://www.csoonline.com/article/4234532/cybersecurity-is-a-leadership-problem-why-the-management-model-needs-to-catch-up.html

#InfoSec #CyberSecurity #Leadership

CSO OnlineCybersecurity is a leadership problem: Why the management model needs to catch upWe keep buying better security tech, but the real gaps are ownership and follow-through, so cybersecurity can’t stay the CISO’s problem alone.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Plex shipped fixes in 1.43.3 by Sep 1, yet one researcher's honeypot running a vulnerable version was exploited on Oct 17, a day after the Plex2Shell chain (CVE-2026-96652, -96654, -96655, -96656) went public. He saw an XMRig miner and a proxy tool dropped. Plex's Sep 1 notice listed no CVEs, and Plex did not immediately respond to Ars Technica.

https://www.boredhackerblog.info/2026/10/plex-vulnerabilities-being-exploited-in.html

#Plex #Homelab #Malware #Cybersecurity

www.boredhackerblog.infoPlex vulnerabilities being exploited in the wild to drop a cryptominerIntro: (No AI was involved in writing, research, etc...) If you see weird fonts and spacing, blame Blogger.  Skip to "In the wild exploitati...
↩ Reply ♡ 0 · ↻ 0 ↗ Original