X XFediYour place in the Fediverse
XFEDI

#InfoSEC

ActivityPub

Public posts with this hashtag.

T

🚨 Microsoft Azure: three CVSS 10.0s published Oct 22. All fully mitigated server-side. No patch. No affected version. No date the flaw existed.

CVE-2026-83938 — AKS Config Service (CWE-306, 10.0)
CVE-2026-97785 — AAD App Proxy (CWE-287, 10.0)
CVE-2026-110063 — VM Inspector (CWE-59, 10.0)

"Fully mitigated, no action" ends the remediation story. It doesn't answer: was my tenant touched before the fix landed?

No exposure window = unauditable.

Also in the batch: CVE-2026-105014, Azure Pipelines, CWE-77 command injection, 9.1 — customer-actionable. Don't let three unpatchable 10.0s crowd it out.

https://threataft.com/articles/microsoft-azure-double-10-cve-2026-83938-97785

#CVE #AzureSecurity #VulnerabilityManagement #Infosec

ThreatAftAzure Double 10.0: No Patch, No Action, No Date | ThreatAftMicrosoft's Azure double 10.0 (CVE-2026-83938, CVE-2026-97785) has no patch and no action. Why 'fully mitigated' still needs verification.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Anyone going to @BSidesPDX Friday? I'm planning on being there at the beginning of the day. I'm going to try and make it through the whole time.

I go by Wolf (some of you may already know that). I'll be wearing a black and grey Glitch skull hat. I'll have a brightly colored Timbuk2 messenger bag as well.

If you see me, please feel free to say hello. It'd be cool to catch up with some of you I already know, and meet new people as well. Hope to see you there!

#BSides #PDX #infosec

↩ Reply ♡ 0 · ↻ 0 ↗ Original
T

Oracle October 2026 CPU — the numbers that actually matter:

1,295 patches / 1,209 CVEs (not 1,283 — that's the wrong figure)
~590 patches for unauthenticated flaws
Six CVSS 10.0s, all unauth

The 9.8 to patch first: CVE-2026-101767 — EBS SQL injection with a published Horizon3 chain that bypasses the default URL firewall and reaches a shell via the Concurrent Manager.

CVE-2026-35273 (PeopleSoft, KEV): ShinyHunters / UNC6240 are URL-encoding the PSEMHUB path to bypass WAF blocks. Patch, don't WAF.

https://threataft.com/articles/oracle-october-2026-cpu-1209-cves-six-cvss-10

#Oracle #EBS #PeopleSoft #infosec #vulnerability

ThreatAftOracle October 2026 CPU: 1,209 CVEs, Six 10.0s | ThreatAftOracle's October 2026 CPU fixes 1,209 CVEs across 33 families, including six CVSS 10.0 flaws. Patch Fusion Middleware, EBS and PeopleSoft first.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
T

Craft CMS 8-CVE patch batch — the one to prioritise:

CVE-2026-112776 (9.8): unauthenticated GraphQL site-scope bypass. Cross-site data access on multi-tenant installs with no credentials.

Plus five Twig sandbox escapes and a verification-code ATO flaw that chains into them.

Craft 5.x → 5.11.0 | Craft 4.x → 4.18.8

https://threataft.com/articles/craft-cms-cve-2026-112776-graphql-twig-sandbox-rce

#CraftCMS #Vulnerability #AppSec #infosec

ThreatAftCraft CMS 9.8 GraphQL Bypass + 7 Twig RCEs | ThreatAftCraft CMS 5.x/4.x: 8 CVEs incl. 9.8 GraphQL site-scope bypass and five Twig sandbox RCEs. Fixed in 5.11.0 / 4.18.8.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Capcom says attackers accessed 11.7 million CAPCOM ID accounts used for its web services and some online games. With centralized game identities, credential stuffing and targeted phishing are the main secondary risks. #Capcom #DataBreach #InfoSec

https://cyberworldops.eu/en/capcom-says-intruders-reached-117-million-capcom-id-accounts

Capcom says intruders reached 11.7 million CAPCOM ID accounts
CyberWorldOpsCapcom Confirms Breach Affecting 11.7M CAPCOM ID AccountsCapcom says intruders reached 11.7M CAPCOM ID accounts, exposing emails and login details. Most passwords and payment data were unaffected.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Kiloview E3 firmware (<1.30) hit by CVE-2026-107861: CRITICAL command injection (CWE-78). Authenticated users can execute OS commands as root — full device compromise possible. Patch unavailable. Restrict access & monitor now. https://radar.offseq.com/threat/cve-2026-107861-cwe-78-in-kiloview-e3-firmware-23f97073d04a678f #OffSeq #Infosec #Vuln

Critical threat: CVE-2026-107861: CWE-78 in Kiloview E3 Firmware
OffSeq Threat RadarCVE-2026-107861: CWE-78 in Kiloview E3 Firmware | Threat RadarCVE-2026-107861 is a critical command injection vulnerability in Kiloview E3 NDI encoder firmware. The system control service improperly handles the hostname…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

2026-10-22 RDP #Honeypot IOCs - 908 scans
Thread with top 3 features in each category and links to the full dataset
#DFIR #InfoSec

Top IPs:
221.6.237.66 - 90
82.223.10.125 - 70
82.223.17.218 - 68

Top ASNs:
AS8560 - 340
AS4837 - 90
AS8075 - 80

Top Accounts:
142.93.8.59 - 770
hello - 84
Administr - 10

Top ISPs:
arsys.es - 284
CNC Group CHINA169 Jiangsu Province Network - 90
Speed NET Internet Banda Larga Ltda - 68

Top Clients:
Unknown - 908

Top Software:
Unknown - 908

Top Keyboards:
Unknown - 908

Top IP Classification:
hosting - 486
Unknown - 318
mobile - 66

Pastebin links with full 24-hr RDP Honeypot IOC Lists:
Bad API request, invalid api_dev_key

#CyberSec #SOC #Blueteam #SecOps #Security

↩ Reply ♡ 0 · ↻ 0 ↗ Original

2026-10-22 RDP #Honeypot IOCs - 454 scans
Thread with top 3 features in each category and links to the full dataset
#DFIR #InfoSec

Top IPs:
221.6.237.66 - 45
82.223.10.125 - 35
82.223.17.218 - 34

Top ASNs:
AS8560 - 170
AS4837 - 45
AS8075 - 40

Top Accounts:
142.93.8.59 - 385
hello - 42
Administr - 5

Top ISPs:
arsys.es - 142
CNC Group CHINA169 Jiangsu Province Network - 45
Speed NET Internet Banda Larga Ltda - 34

Top Clients:
Unknown - 454

Top Software:
Unknown - 454

Top Keyboards:
Unknown - 454

Top IP Classification:
hosting - 243
Unknown - 159
mobile - 33

Pastebin links with full 24-hr RDP Honeypot IOC Lists:
Bad API request, invalid api_dev_key

#CyberSec #SOC #Blueteam #SecOps #Security

↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE POLAR 2026 SPONSOR : TRENDAI
La prochaine édition de POLAR ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous TrendAI, qui est notre partenaire BAR!
Pour en savoir plus sur la mission de cette compagnie, visiter leur site web : https://wiz.io/
—--
Our 4th edition of POLAR would not be possible without our sponsors. And this year, we are happy to have TrendAI, a BAR sponsor!
If you want to learn more about this company’s mission, visit their website https://www.trendmicro.com/
#CISO #infosec #polar #hf2026 #cybersecurity

Media attachment
wiz.ioWiz: AI Cybersecurity for All Your Cloud and AI ApplicationsWiz connects code, cloud, and runtime into one agentic cybersecurity platform. Prevent risk, detect threats, and start secure – across every cloud and AI layer.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE POLAR 2026 SPONSOR : WIZ
La prochaine édition de POLAR ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous Wiz, qui est notre partenaire DINER!
Pour en savoir plus sur la mission de cette compagnie, visiter leur site web : https://wiz.io/
—--
Our 4th edition of POLAR would not be possible without our sponsors. And this year, we are happy to have Wiz, a DINNER sponsor!
If you want to learn more about this company’s mission, visit their website https://www.trendmicro.com/
#CISO #infosec #polar #hf2026 #cybersecurity

Media attachment
wiz.ioWiz: AI Cybersecurity for All Your Cloud and AI ApplicationsWiz connects code, cloud, and runtime into one agentic cybersecurity platform. Prevent risk, detect threats, and start secure – across every cloud and AI layer.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE POLAR 2026 SPONSOR : MICROLOGIC
La prochaine édition de POLAR ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous Micrologic, qui est notre partenaire COCKTAIL!
Pour en savoir plus sur la mission de cette compagnie, visiter leur site web : https://micrologic.ca/
—--
Our 4th edition of POLAR would not be possible without our sponsors. And this year, we are happy to have Micrologic, a COCKTAIL sponsor!
If you want to learn more about this company’s mission, visit their website https://micrologic.ca/
#CISO #infosec #polar #hf2026 #cybersecurity

Media attachment
MicrologicSolutions infonuagiques souveraines au Canada | MicrologicMicrologic : solutions infonuagiques pour le stockage et la gestion sécurisée des données. Découvrez notre cloud souverain canadien. Contactez-nous !
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE POLAR 2026 SPONSOR : ARISTA
La prochaine édition de POLAR ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous Arista, qui est notre partenaire CAFÉ!
Pour en savoir plus sur la mission de cette compagnie, visiter leur site web : https://www.arista.com/
—--
Our 4th edition of POLAR would not be possible without our sponsors. And this year, we are happy to have Arista, a COFFEE sponsor!
If you want to learn more about this company’s mission, visit their website https://www.arista.com/
#CISO #infosec #polar #hf2026 #cybersecurity

Media attachment
Arista NetworksData-Driven Cloud Networking - AristaArista Networks was founded to pioneer and deliver software-driven cloud networking solutions for large data center storage and computing environments. Arista’s award-winning platforms, ranging in Ethernet speeds from 10 to 100 gigabits per second,
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Possible Phishing 🎣
on: ⚠️hxxps[:]//docs[.]google[.]com/presentation/d/e/2PACX-1vQOQHSX2gL0nCZb9m9gpTQUo0A4tZUVyz7MGEmMYfpdz2n1nqQqQMslPM7oqpgDdxeH9VoRamxpmy5n/pub?start=false&amp;loop=false&amp;delayms=3000
🧬 Analysis at: https://urldna.io/scan/6ada797b3b77500008097931
#cybersecurity #phishing #infosec #urldna #scam #infosec
Media attachment
urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Kiloview E3 Firmware (<1.30) hit by CVE-2026-110243, a CRITICAL command injection (CVSS 9.9). Authenticated users with network config can execute root OS commands. No patch — restrict interface access. Details: https://radar.offseq.com/threat/cve-2026-110243-cwe-78-in-kiloview-e3-firmware-b693a1be0d634280 #OffSeq #Infosec #Kiloview #CVE2026110243

Critical threat: CVE-2026-110243: CWE-78 in Kiloview E3 Firmware
OffSeq Threat RadarCVE-2026-110243: CWE-78 in Kiloview E3 Firmware | Threat RadarCVE-2026-110243 is a critical command injection vulnerability in the Kiloview E3 NDI encoder firmware. The network management service improperly validates the…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

⚠️ RELAY // Cyber Watch — 2026-10-23

Trump's 2027 budget proposal would cut CISA funding again, and officials fear the agency's ability to protect US elections has been weakened.

🔗 https://www.route-fifty.com/cybersecurity/2026/10/cybersecurity-agency-supposed-protect-us-elections-officials-fear-its-been-compromised-trump/416670/?oref=rf-homepage-river

#InfoSec #CyberSecurity #CISA

Route FiftyThis cybersecurity agency is supposed to protect U.S. elections. Officials fear it’s been compromised by Trump.President Donald Trump’s 2027 budget proposal would reduce funding for the Cybersecurity and Infrastructure Security Agency by another $700 million, which could necessitate 900 additional layoffs.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🚨🐛 SIGINT // Cybersecurity Watch — 2026-10-23
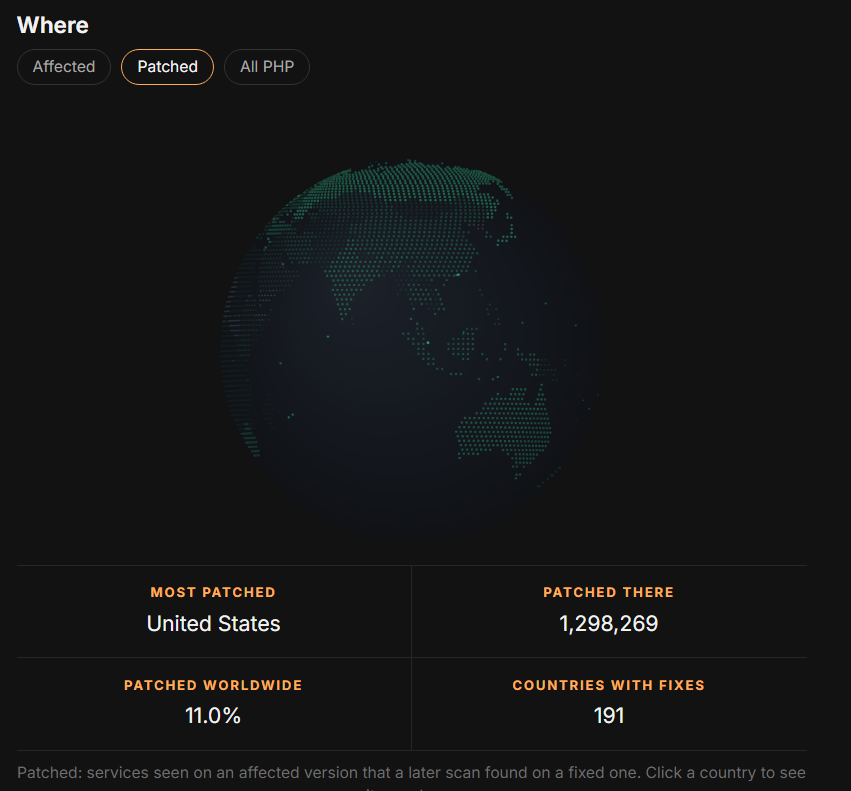
Critical PHP flaws affecting ~70% of websites now under active exploitation—patch immediately as exploit code is public and attacks accelerate.
https://www.securityweek.com/php2shell-mass-exploitation-looms-for-leaked-critical-php-flaws/
#PHP #CVE #InfoSec #Cybersecurity

SecurityWeekPHP2Shell: Mass Exploitation Looms for Leaked Critical PHP FlawsPHP2Shell refers to two critical PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, that could lead to unauthenticated RCE.
↩ Reply ♡ 0 · ↻ 0 ↗ Original