X XFediYour place in the Fediverse
XFEDI

#InfoSEC

ActivityPub

Public posts with this hashtag.

HN user petecooper, who posted the PHP RCE CVE IDs on Oct 20, apologizes, saying a contact told them there was no embargo (their account; contact unnamed). Their post said CVSS 10.0. The PHP Foundation says the leaked IDs carried a wrong time and a wrong 10.0 score (actual 9.2) and names no one. AWS logged an exploit attempt on Oct 17 and calls the actor's source of details unclear.

https://news.ycombinator.com/item?id=50193416

#PHP2Shell #PHP #InfoSec #Cybersecurity

news.ycombinator.comTell HN: I unknowingly broke the PHP RCE embargo. I am sorry. | Hacker News
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🚨 This time the bug isn’t in your code, it’s in PHP itself.

PHP2Shell is two CVEs in the PHP runtime (CVE-2026-109618, CVE-2026-109619) that can lead to unauthenticated RCE.

When something like this lands, the first question is usually: what exactly is affected, and what do I need to patch?

I’d rather answer that from the terminal than from twelve browser tabs.

With the ZEN SecDB CLI:

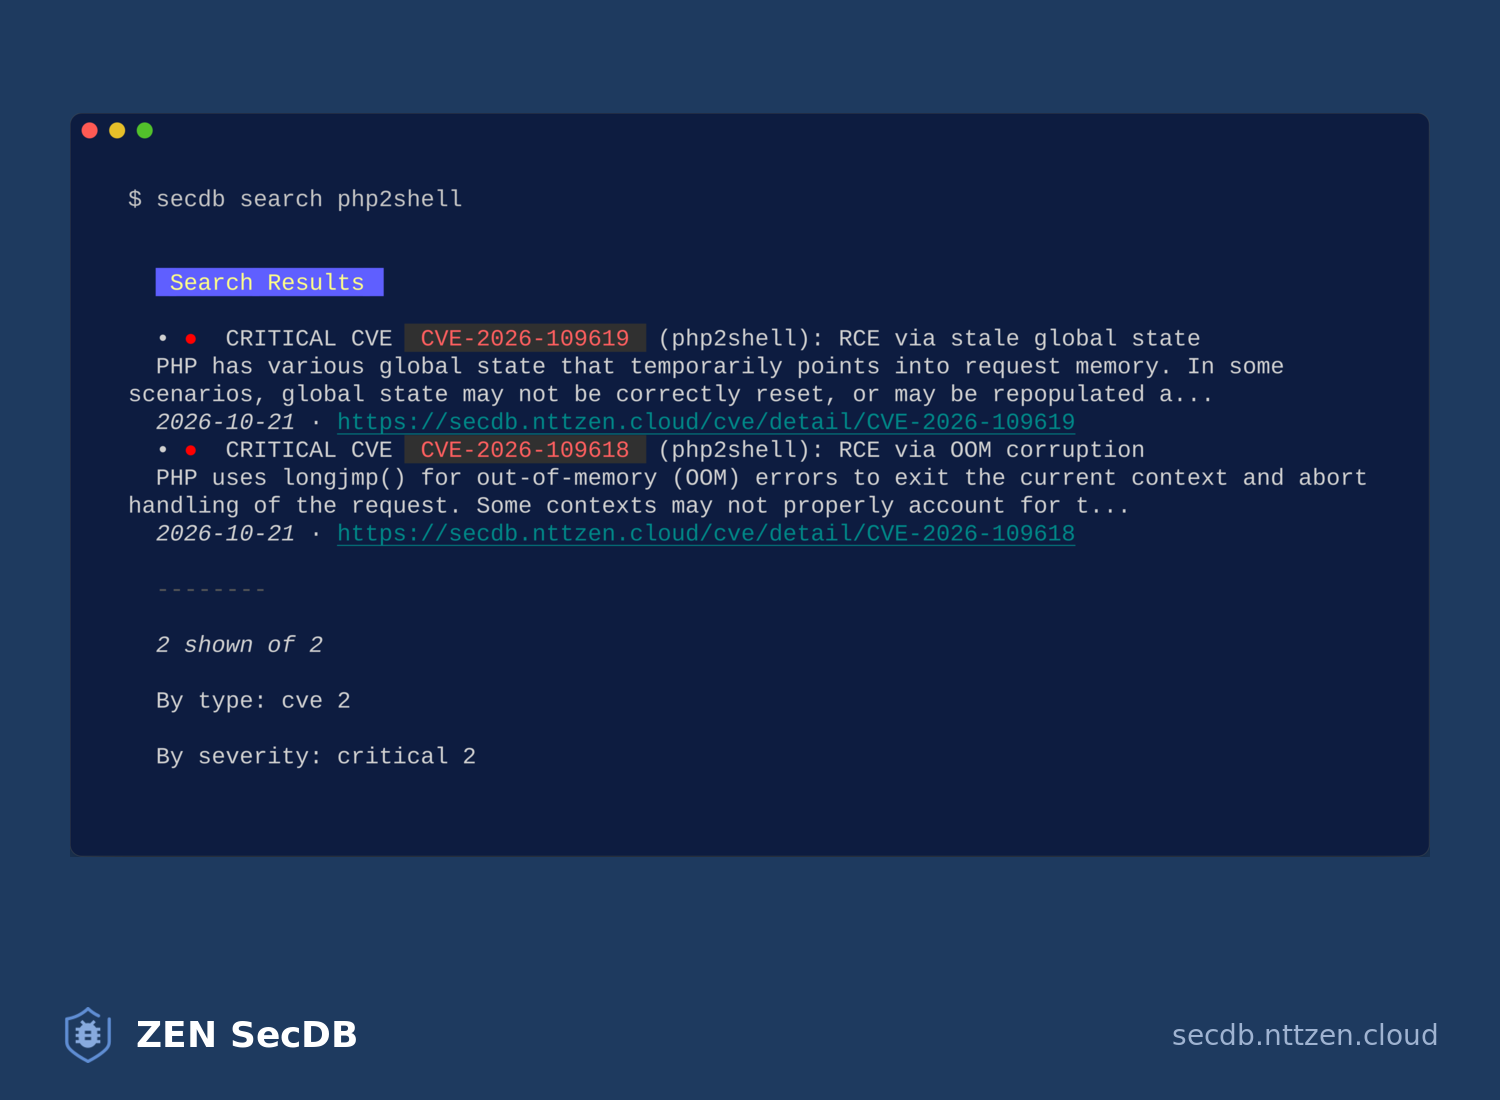
1️⃣ secdb search php2shell

finds both CVEs.

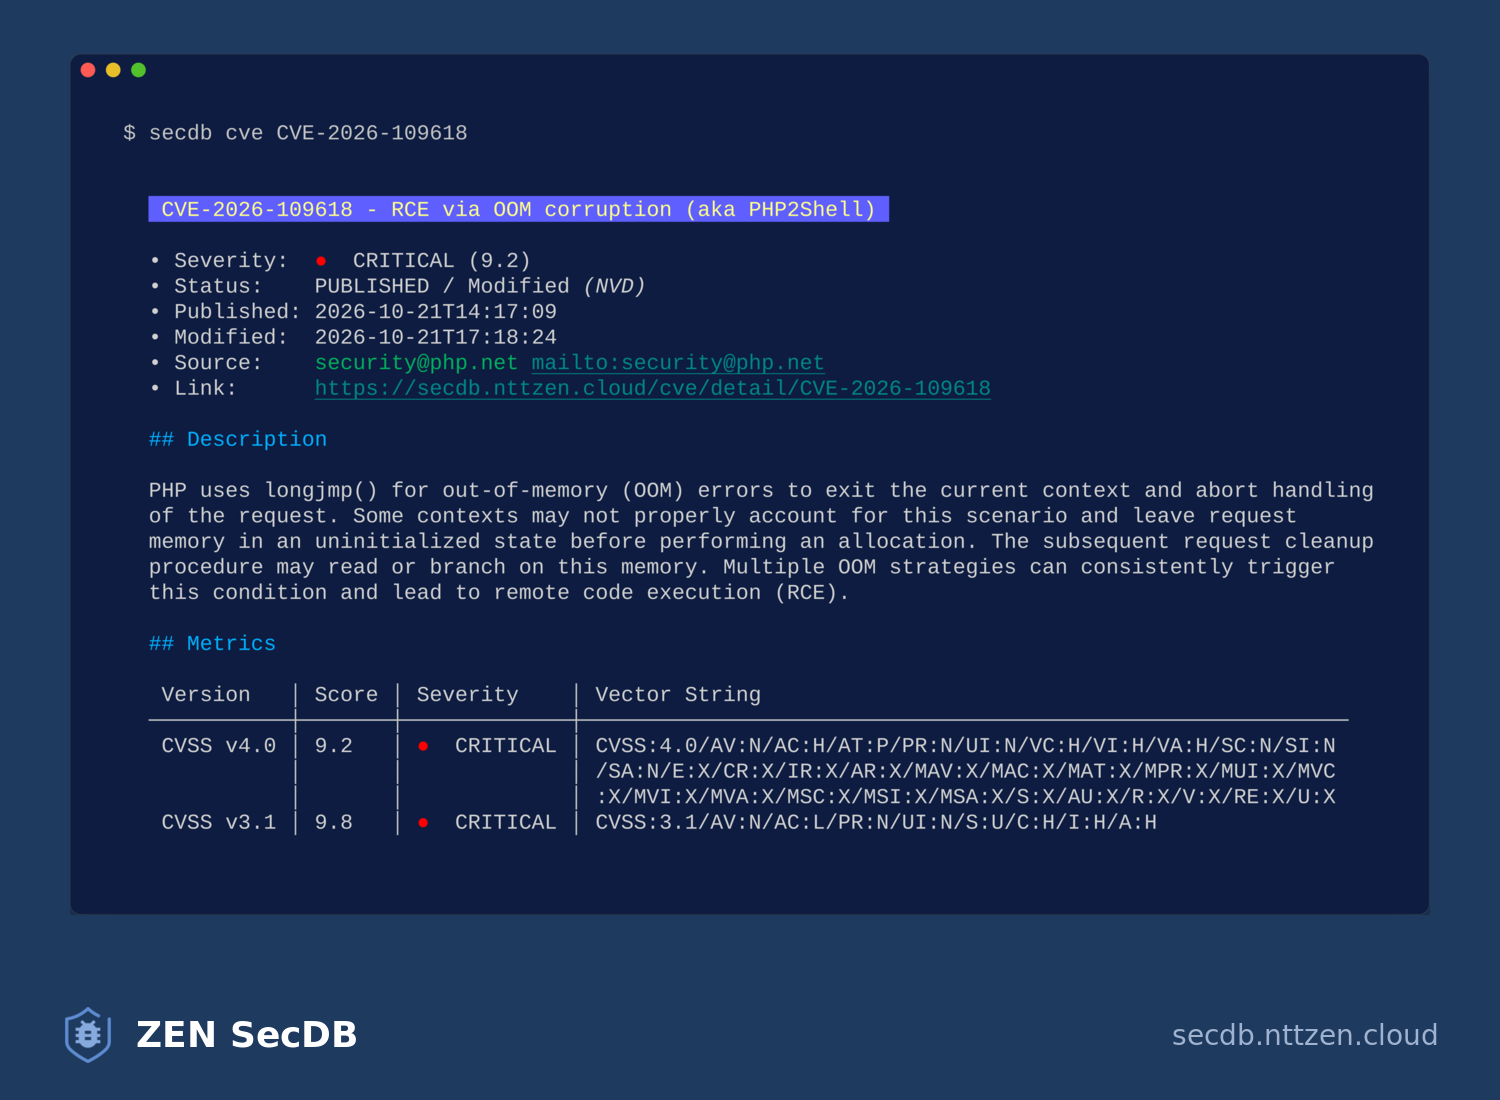
2️⃣ secdb cve CVE-2026-109618

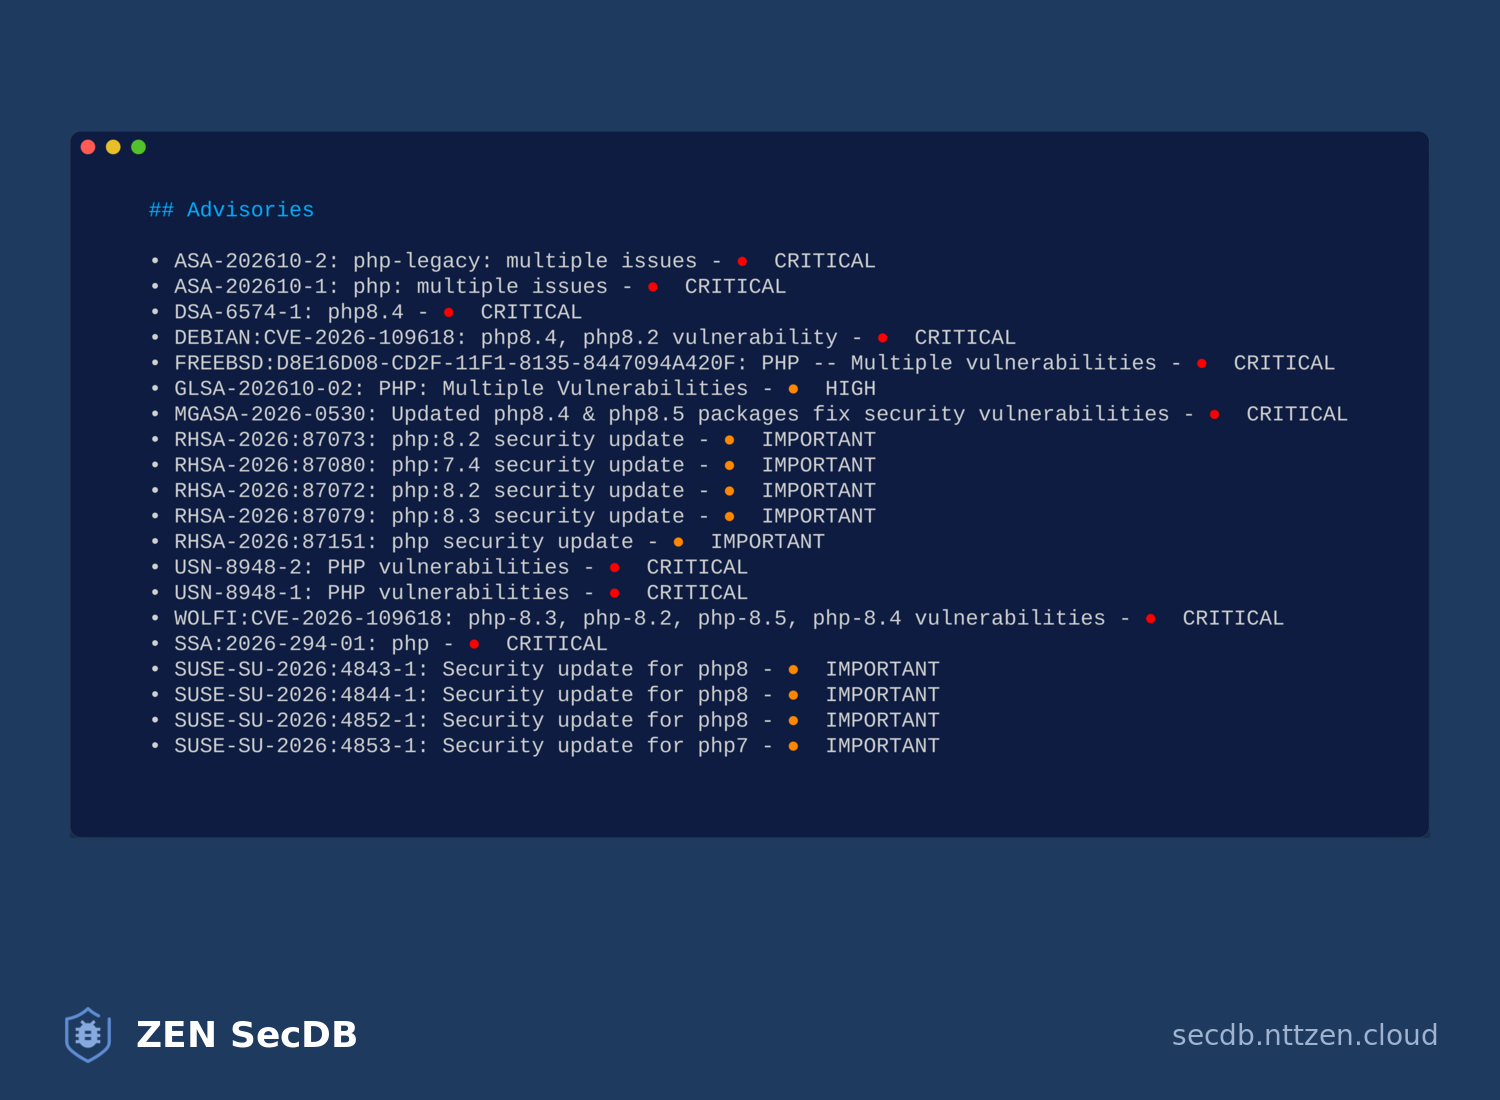
gives the full record: description, CVSS 4.0 at 9.2, CVSS 3.1 at 9.8, vectors, references and vendor advisories from Debian, Red Hat, SUSE, Ubuntu, Arch, Gentoo, FreeBSD and others.

That’s useful because you can quickly check whether your distro already ships a fix, instead of going through each security tracker manually.

If you run PHP, upgrade to 8.5.12, 8.4.27, 8.3.36 or 8.2.35, or use the patched package provided by your distro.

Configuration mitigations may reduce the risk, but they don’t replace patching.

And if the server was exposed, it’s probably worth checking whether it was already compromised.

ZEN SecDB: https://secdb.nttzen.cloud
CLI: https://github.com/giterlizzi/secdb-cli
CVE-2026-109618: https://secdb.nttzen.cloud/cve/detail/CVE-2026-109618

CVE-2026-109619: https://secdb.nttzen.cloud/cve/detail/CVE-2026-109619

#PHP2Shell #PHP #RCE #InfoSec #VulnerabilityManagement #CVE
#NTTDATA #ZENSecDB

secdb search php2shellsecdb cve CVE-2026-109618php2shell advisories
ZEN SecDB PortalHome | ZEN SecDB Portalpowered by YaVS - YaVS Ain't Vulnerability Scanner...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : THALES

Our 18th edition, Hackfest Level Up, would not be possible without our sponsors. And this year, we are happy to have Thales, a KIOSK sponsor!

If you want to learn more about this company’s mission, visit their website https://www.thalesgroup.com/

PS: YOU CAN STILL BUY YOUR TICKET for October 29–31, 2026 at the Convention Center of Québec ;) More info: https://hackfest.ca/en/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
Hackfest 2026Cybersecurity conference in Quebec City, October 29 to 31, 2026 — Hackfest 2026Hackfest 2026, the 18th edition: cybersecurity and hacking conference, October 29 to 31, 2026 at the Quebec City Convention Centre. Talks, trainings, CTFs, villages and POLAR.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : THALES

La prochaine édition du 18e Hackfest Level Up ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous Thales, qui est un partenaire KIOSQUE!

Visiter leur site web : https://www.thalesgroup.com/

PS VOUS POUVEZ TOUJOURS ACHETER VOS BILLETS pour les 29, 30 et 31 octobre 2026 au Centre des congrès de Québec ;) Info sur notre site web : https://hackfest.ca/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
Hackfest 2026Conférence de cybersécurité à Québec, 29 au 31 octobre 2026 — Hackfest 2026Hackfest 2026, 18e édition : conférence de cybersécurité et de hacking du 29 au 31 octobre 2026 au Centre des congrès de Québec. Conférences, formations, CTF, villages et POLAR.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

It's Thursday evening, October 22, 2026. My inbox is full of "urgent" emails and my feed won't stop showing me breaches of 11 million records.

https://theperimetersite.com/report/389

#databreach #infosec

The Perimeter SiteEleven Million Records Gone. The Servers Stay Open. | PerimeterIt's Thursday evening, October 22, 2026. My inbox is full of "urgent" emails and my feed won't stop showing me breaches of 11 million records.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
D

I got curious how risky MCP servers actually are, so I pulled the published tool definitions from 28 of the most popular Python ones and counted. 1,384 tools, all read from public source, nothing run.

Two things jumped out:

14 of the 28 give an agent a tool that ingests untrusted stuff (a URL, a file) and a tool that acts (runs a query, sends a message) in the same context, with nothing flagging either one.

And the tool descriptions themselves are written as orders to the model ("you MUST call X first"). That's the same channel a poisoning attack would use, so a bad one blends right in.

Not calling any of it a vuln. It's just what the surface looks like. Harness is reproducible if you want to check my numbers.

github.com/agentsploit/agentsploit/blob/main/docs/mcp-tool-survey.md

#infosec #AISecurity #MCP

↩ Reply ♡ 0 · ↻ 0 ↗ Original

Two businesses have suffered devastating breaches this week (well, three, if you count the screwup that brought all my sites down and lost data):

Vibe coding platform Zeabur collapses after back-to-back breaches expose 3.2M records:

https://cybernews.com/news/zeabur-cloud-provider-shutdown-two-breaches-3-million-records/

Bengaluru-based eMudhra will exit the global website authentication certificate business after a security flaw left eight intermediate certification authority certificates vulnerable to potential misuse. The company's Indian digital signature and eSign services will continue to operate as usual.: https://www.ndtvprofit.com/technology/emudhra-exits-global-website-security-business-after-weak-keys-found-in-eight-certificates-12221008

@AdrianSanaba

#databreach #infosec

CybernewsZeabur to shut down after two consecutive breaches expose 3.2M recordsVibe coding cloud platform Zeabur is hit with two breaches in just eight weeks, exposing 3.2M records and more than 321,000 accounts. Now Zeabur is shutting down for good.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

The week only keeps getting better... apparently, multiple not yet fixed Linux kernel vulnerabilities were disclosed by accident when they were posted to the public mailing list rather than the private one. Oops.

https://www.phoronix.com/news/LKML-New-Trend-Vulnerabilities

#infosec #cybersecurity

www.phoronix.comSeveral Linux Kernel Vulnerabilities Accidentally Posted To Public Kernel Mailing ListSeemingly as an accident, overnight several new Linux kernel vulnerability reports were posted to the public Linux kernel mailing list rather than the private security mailing list
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : TENABLE

Our 18th edition, Hackfest Level Up, would not be possible without our sponsors. And this year, we are happy to have Tenable, a KIOSK sponsor!

If you want to learn more about this company’s mission, visit their website https://www.tenable.com/

PS: YOU CAN STILL BUY YOUR TICKET for October 29–31, 2026 at the Convention Center of Québec ;) More info: https://hackfest.ca/en/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
Tenable®Vulnerability and exposure management | Cloud and AI security | Tenable®The leader in exposure management and AI security, Tenable cybersecurity solutions reduce cyber risk across IT, OT, cloud, identity & hybrid attack surfaces.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

This dumb password rule is from Canada Revenue Agency.

Password checklist:
- 8 to 16 characters
- At least 1 upper-case character
- At least 1 lower-case character
- At least 1 digit
- No space
- No accented characters
- No special characters except: dot (.), dash (-), underscore (_), and apostrophe (')
- No more than 4 consecutive identical characters

https://dumbpasswordrules.com/sites/canada-revenue-agency/

#password #passwords #infosec #cybersecurity #dumbpasswordrules

dumbpasswordrules.comCanada Revenue Agency - Dumb Password RulesPassword checklist: - 8 to 16 characters - At least 1 upper-case character - At least 1 lower-case character - At least 1 digit - No space - No accented characters - No special characters except: dot (.), dash (-), underscore (_), and apostrophe (') - No more than 4 consecutive identical characters
↩ Reply ♡ 0 · ↻ 0 ↗ Original

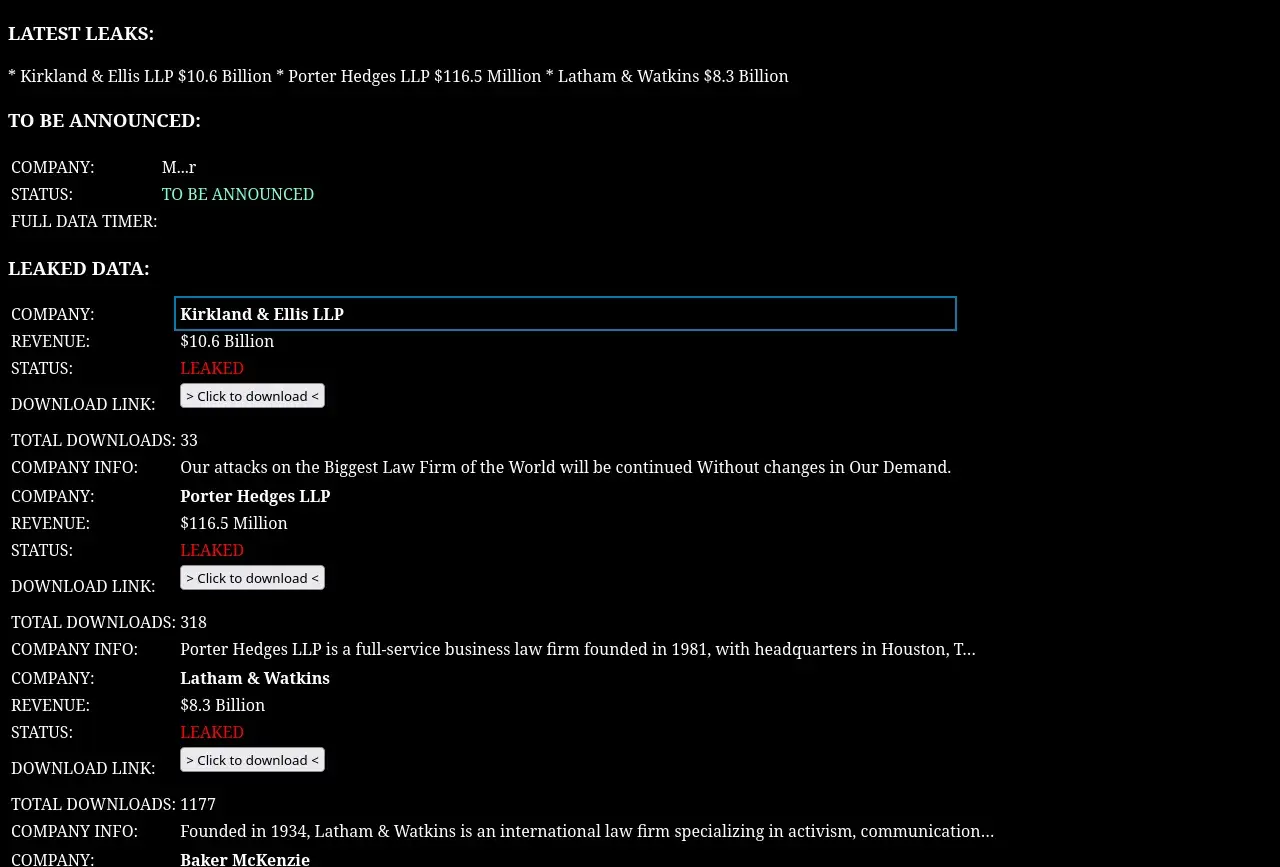
🚨New ransom group blog post!🚨

Group name: SilentRansomGroup
Post title: Kirkland & Ellis LLP
Location: 🇺🇸 US
Sector: Legal
Info: https://cti.fyi/#disclosure/SilentRansomGroup/Kirkland%20%26%20Ellis%20LLP

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Thank you MNP Digital Inc. for sponsoring BSides Edmonton 2026. It was a great event thanks to your support.

We’re excited for 2027, our 10th year!
Secure your spot here: https://bsidesyeg.org/SponsorNextYear

https://mnpdigital.ca/
https://www.linkedin.com/company/mnp-digital/

#BSides #BSidesEdmonton #BSidesYEG #YEG #Infosec #informationsecurity #CyberSec #CyberSecurity

Media attachment
Google DocsBSides Edmonton 2027 Sponsor ApplicationBSides Edmonton is back for it's 10th year! Building on the success of our prior events, we are asking for sponsors to be part of the team to deliver another first-rate cybersecurity conference in Edmonton. Alberta. We are a community-driven, non for profit event. Date: Monday September 13 & Tuesday September 14, 2027 Location: TBA If your organization wants to: Connect directly with the cyber
↩ Reply ♡ 0 · ↻ 0 ↗ Original

OpenAI says its AI found the PHP2Shell bugs before attackers did, and Amazon says it saw hackers trying to use them four days before the rest of us were told they existed. That lead doesn’t last long when the other side has AI too, or when a hint of exposure slips out while the fix is still being developed.

If you run a website, PHP is probably somewhere underneath it. Wiz says it powers about 70% of the web, mostly because WordPress is built on it. The National Security Agency’s advice was blunt: update right away, or take the site offline until you can.

Two things I’d do now:

・ Count your WordPress sites. Then count again. That campaign microsite that marketing launched in 2019 is on that list, and so is the one an agency still hosts for you.

・ Decide today who gets to say “take it down.” Pulling a public site is a business call, and you don’t want to be hunting for that person at 2 a.m. during an active attack.

Patch today, and then go find the sites you forgot you had!

https://arstechnica.com/security/2026/10/hackers-got-a-four-day-head-start-on-epic-php2shell-vulnerability/

#CyberSecurity #WordPress #AI #PHP #security #privacy #cloud #infosec

Ars TechnicaHackers got a four-day head start on epic PHP2Shell vulnerabilityHackers were already probing the bug before defenders were told it existed.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

It's been a rough #InfoSec week. 🫂

Baking can be a great stress-reliever.

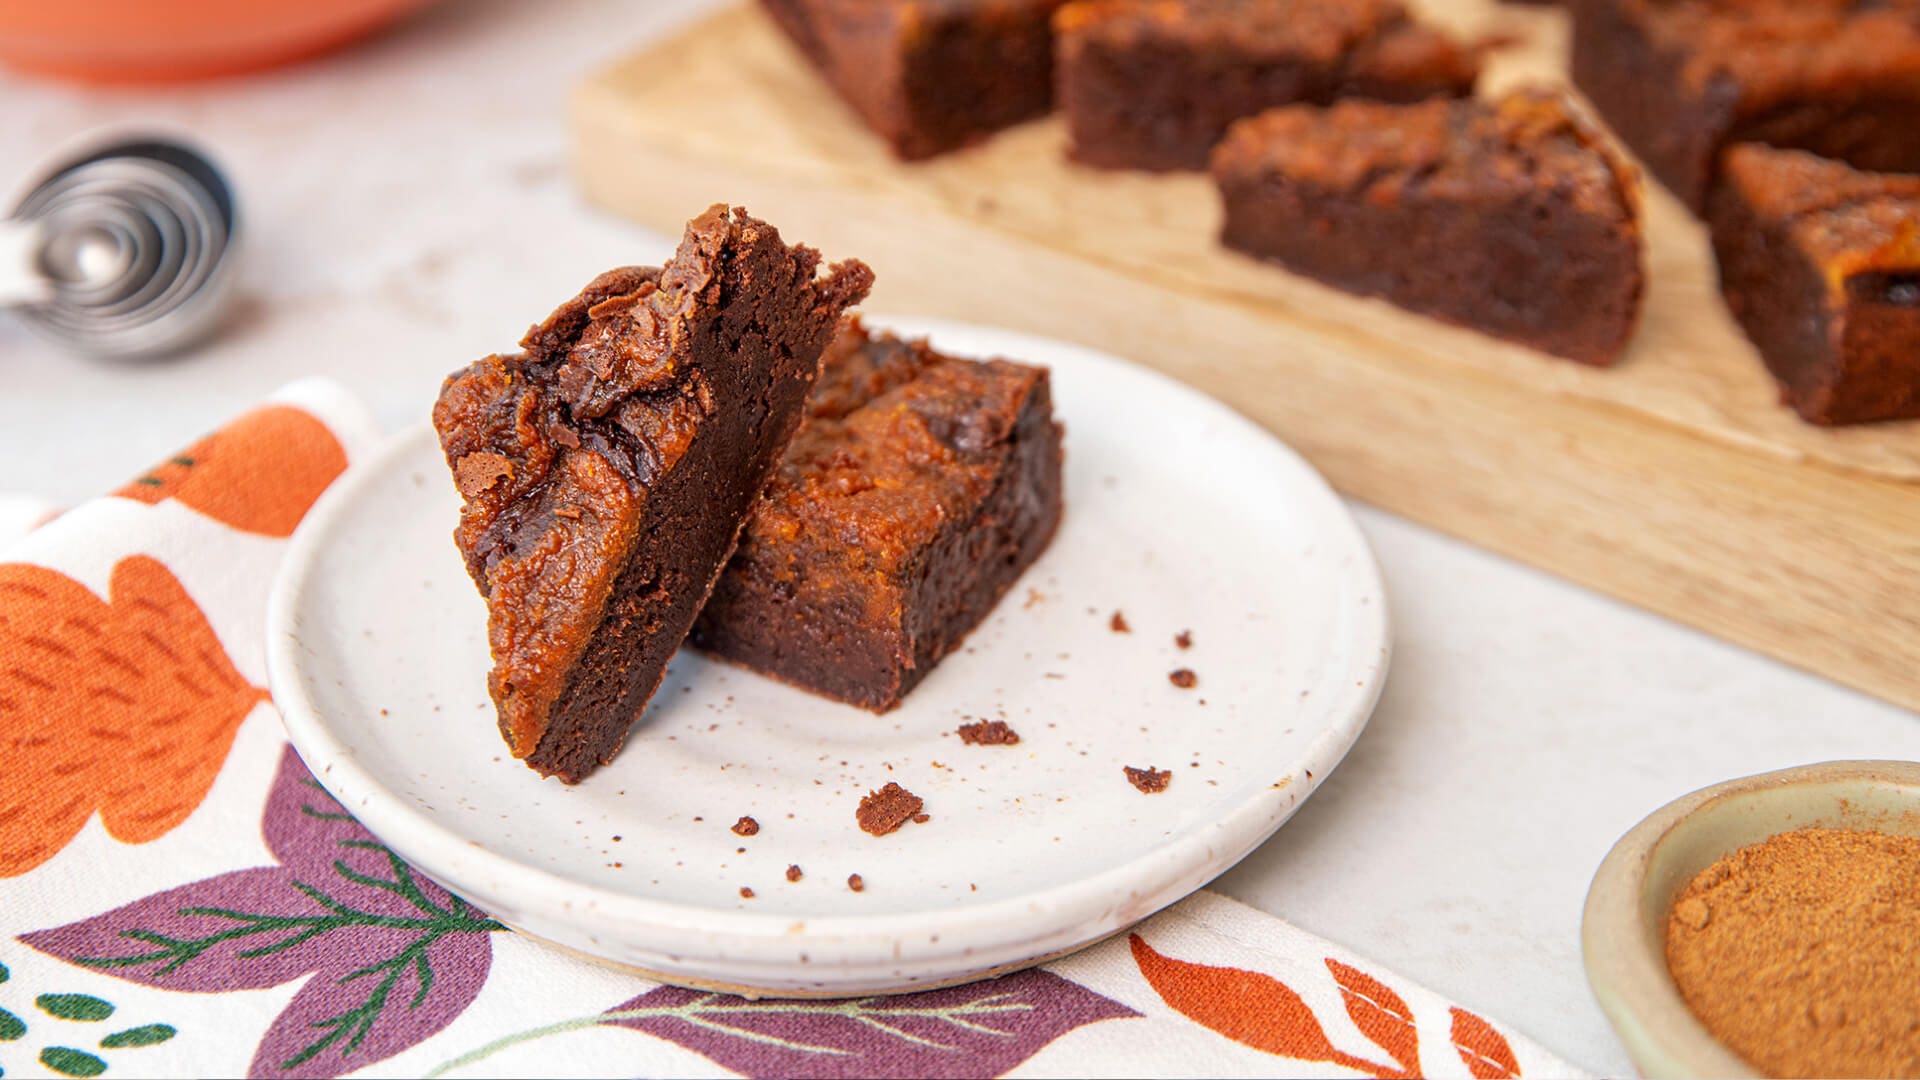
Pumpkin + Chocolate = Delicious. 🎃🍫

Eat them yourself or share.

Just go get that dopamine hit as a respite to all what's going on in the world.

You deserve it. 🫡

#BakingAsAService

https://www.hersheyland.com/stories/easy-chocolate-pumpkin-dessert-recipes-for-fall.html

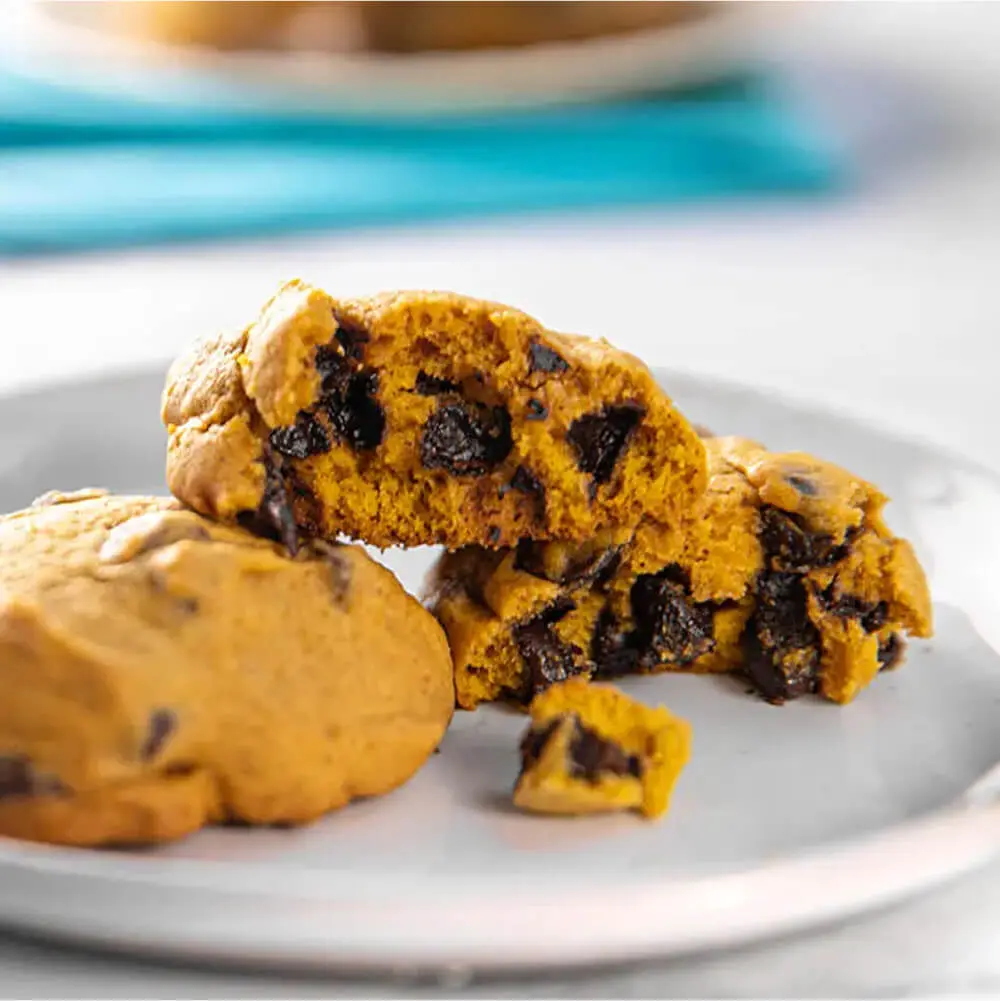
Pumpkin Chocolate Chip cookies. Pumpkin Chocolate Chip Cookies
Whether you’re looking to impress at your next Friendsgiving or just wanting a cozy treat at home, these pumpkin chocolate chip cookies will satisfy for any occasion. With a soft and chewy texture and bursting with warm fall spices and rich chocolate chips, this classic recipe will be a fall favorite.

Don’t let the pumpkin-flavored fun end there. Add this Pumpkin Oatmeal Cookies recipe to your list of fall favorites.
www.hersheyland.com7 Easy Chocolate Pumpkin Dessert Recipes for FallGet cozy with these fall chocolate and pumpkin dessert recipes, like Hershey's twist on the classic pumpkin pie recipe, savory pumpkin brownies, and more!
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PHP2Shell: Critical PHP Flaws Let Attackers Take Over Web Servers Without a Login

PHP maintainers released emergency fixes for two critical flaws, nicknamed PHP2Shell, on October 21 that can let someone with no account and no password take control of a web server by sending it carefully crafted requests. PHP is the software running underneath a large majority of the world's websi...

https://insomnisec.com/posts/2026-10-22-php2shell-cve-2026-109618-109619_insomnisec_v3/

#cybersecurity #infosec

insomnisec.comPHP2Shell: Critical PHP Flaws Let Attackers Take Over Web Servers Without a LoginPHP has released emergency fixes for PHP2Shell, two critical flaws (CVE-2026-109618 and CVE-2026-109619, CVSS 9.2) in the PHP engine itself that can let an unauthenticated attacker run code on a web server. Amazon says attackers were already trying to exploit them on October 17, four days before the fix, and attempts have since climbed into the millions. Update to PHP 8.5.12, 8.4.27, 8.3.36, or 8.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

And ... I was hoping things would look up, but no. Capcom just published an apology for a data breach. This, as you probably can tell, is the translated version:

"It has been found that some of your information has been leaked to the outside world due to unauthorized access by a third party in the online member service 'CAPCOM ID' (*1) operated by our company. We deeply apologize for the inconvenience and concern caused to our customers and related parties" https://www.capcom.co.jp/ir/news/html/261022.html

More:

PC Gamer: Capcom confirms a data breach has affected over 11 million people, with emails, IP addresses, and birthdays caught up in the mix https://www.pcgamer.com/hardware/capcom-confirms-a-data-breach-has-affected-over-11-million-people-with-emails-ip-addresses-and-birthdays-caught-up-in-the-mix/ #infosec #databreach #Capcom

株式会社カプコン |不正アクセスによるお客様情報漏えいのお詫びとお知らせ | プレスリリース | 株式会社カプコンこのたび、当社が運営するオンライン会員サービス「CAPCOM ID」において、第三者による不正アクセスが発生し、お客様情報の一部が外部に漏えいしたことが判明いたしました。お客様ならびに関係者の皆様に多大なるご迷惑とご心配をおかけしておりますことを、深くお詫び申し上げます。
↩ Reply ♡ 0 · ↻ 0 ↗ Original