X XFediYour place in the Fediverse
XFEDI

#InfoSEC

ActivityPub

Public posts with this hashtag.

PHP2Shell: Critical PHP Flaws Let Attackers Take Over Web Servers Without a Login

PHP maintainers released emergency fixes for two critical flaws, nicknamed PHP2Shell, on October 21 that can let someone with no account and no password take control of a web server by sending it carefully crafted requests. PHP is the software running underneath a large majority of the world's websi...

https://insomnisec.com/posts/2026-10-22-php2shell-cve-2026-109618-109619_insomnisec_v3/

#cybersecurity #infosec

insomnisec.comPHP2Shell: Critical PHP Flaws Let Attackers Take Over Web Servers Without a LoginPHP has released emergency fixes for PHP2Shell, two critical flaws (CVE-2026-109618 and CVE-2026-109619, CVSS 9.2) in the PHP engine itself that can let an unauthenticated attacker run code on a web server. Amazon says attackers were already trying to exploit them on October 17, four days before the fix, and attempts have since climbed into the millions. Update to PHP 8.5.12, 8.4.27, 8.3.36, or 8.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

And ... I was hoping things would look up, but no. Capcom just published an apology for a data breach. This, as you probably can tell, is the translated version:

"It has been found that some of your information has been leaked to the outside world due to unauthorized access by a third party in the online member service 'CAPCOM ID' (*1) operated by our company. We deeply apologize for the inconvenience and concern caused to our customers and related parties" https://www.capcom.co.jp/ir/news/html/261022.html

More:

PC Gamer: Capcom confirms a data breach has affected over 11 million people, with emails, IP addresses, and birthdays caught up in the mix https://www.pcgamer.com/hardware/capcom-confirms-a-data-breach-has-affected-over-11-million-people-with-emails-ip-addresses-and-birthdays-caught-up-in-the-mix/ #infosec #databreach #Capcom

株式会社カプコン |不正アクセスによるお客様情報漏えいのお詫びとお知らせ | プレスリリース | 株式会社カプコンこのたび、当社が運営するオンライン会員サービス「CAPCOM ID」において、第三者による不正アクセスが発生し、お客様情報の一部が外部に漏えいしたことが判明いたしました。お客様ならびに関係者の皆様に多大なるご迷惑とご心配をおかけしておりますことを、深くお詫び申し上げます。
↩ Reply ♡ 0 · ↻ 0 ↗ Original
C

🤖 Railway (PaaS) discloses an intrusion into systems storing customer environment variables. Encrypted vars may have been accessed, and in some cases decrypted. A subset of users is urged to rotate credentials and secrets.
🔗 https://thehackernews.com/2026/10/railway-says-intruder-may-have-accessed.html
#DataBreach #InfoSec #CloudSecurity #Secrets

The Hacker NewsRailway Says Intruder May Have Accessed Customer Secrets, Urges Credential RotationRailway says an intruder may have accessed decrypted environment variables for some users, as a researcher reports related cryptocurrency theft.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
T

A QPACK implementation flaw can turn a tiny HTTP/3 request into a serious memory exhaustion problem.

FoxIO’s Header Accordion research reports up to 4,064× memory amplification in Bun.

The key issue: compressed headers on the wire can expand into massive allocations during QPACK decompression.

A deep dive into the attack, affected implementations, CVEs, and mitigations:
https://thecybersecguru.com/exploits/qpack-header-accordion-http3-dos/

#InfoSec #CVE

❞ Quoted postThe CyberSec Guru

Content warning: QPACK Header Accordion attacks exploit HTTP/3 header compression to trigger memory exhaustion. Learn the affected libraries, CVEs, and mitigation steps

The CyberSec GuruQPACK Header Accordion Attack: HTTP/3 DoS Explained | The CyberSec GuruQPACK Header Accordion attacks exploit HTTP/3 header compression to trigger memory exhaustion. Learn the affected libraries, CVEs, and mitigation steps
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🆕 Improved Domain search reliability: wildcard searches of certificate names now run to the end, with a progress notice while they finish

https://scanmalware.com/search-domains?mtm_campaign=social-changelog&mtm_source=mastodon&mtm_medium=social&mtm_kwd=202610221430

#ScanMalware #InfoSec #ThreatIntel

ScanMalware.comDomain search | ScanMalwareList domains by IP address, nameserver or certificate name, including domains that have never been scanned.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Bethany Press International has fallen to a ransomware actor https://ransomware.live/id/QmV0aGFueSBQcmVzcyBJbnRlcm5hdGlvbmFsQGFraXJh

Also:

US: Performance Ford Inc https://ransomware.live/id/UGVyZm9ybWFuY2UgRm9yZCBJbmNATjBu

Heritage Senior Living https://ransomware.live/id/SGVyaXRhZ2UgU2VuaW9yIExpdmluZ0BOMG4

Yesterday:

Germany: FuG-Gruppe https://ransomware.live/id/RnVHLUdydXBwZUBsYW1hc2h0dQ

US: Coastal Alabama Community College https://ransomware.live/id/Q29hc3RhbCBBbGFiYW1hIENvbW11bml0eSBDb2xsZWdlQGludGVybG9jaw

More: https://ransomware.live/ #infosec #ransomware #cybercrime

Ransomware.liveVictim: Bethany Press International – akiraRansomware.live discovered on 2026-10-22 that Bethany Press International has been claimed by Akira ransomware group
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🔒 Security News Digest - 2026-10-22

📊 18 updates from 5 sources:

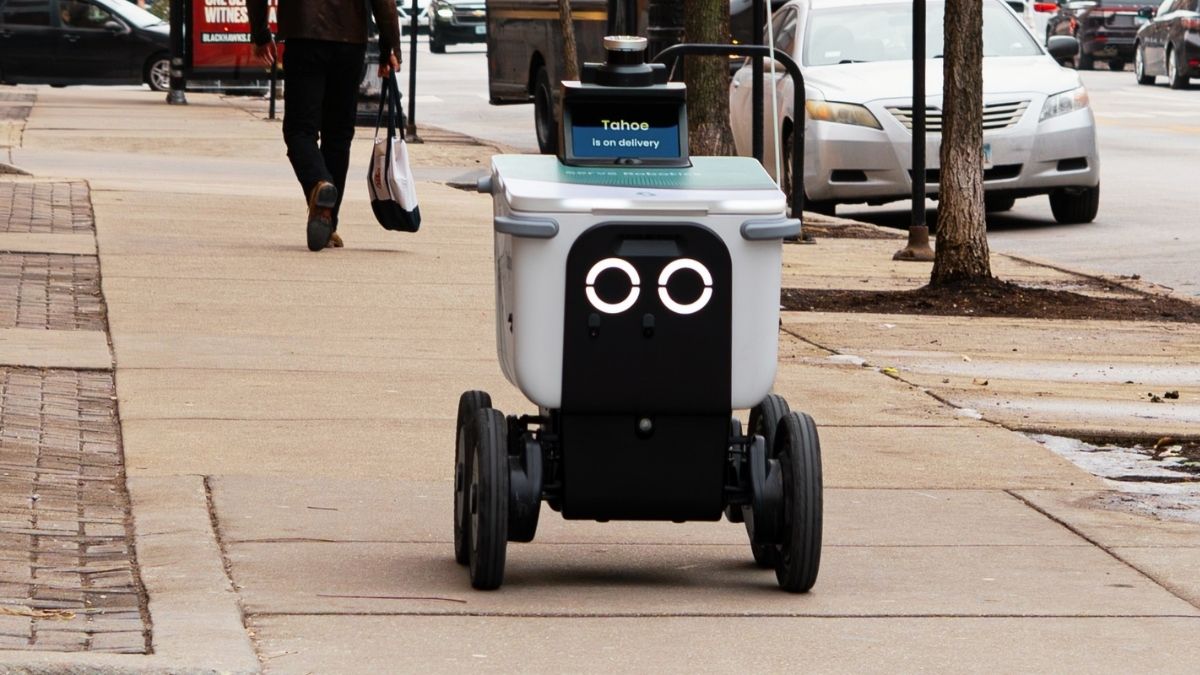
🦠 Malwarebytes: Delivery bots accused of illegally scanning customers
https://www.malwarebytes.com/blog/privacy/2026/10/delivery-bots-accused-of-illegally-scanning-customers

🔹 SecurityWeek: PHP2Shell Exploitation Started Days Before Patches
https://www.securityweek.com/php2shell-exploitation-started-days-before-patches/

🔹 SecurityWeek: Cisco Patches 34 Vulnerabilities Across Multiple Products
https://www.securityweek.com/cisco-patches-34-vulnerabilities-across-multiple-products/

🔹 The Hacker News: OpenCode Flaw Lets Malicious MCP Servers Execute Code During Sign-In on Windows and WSL
https://thehackernews.com/2026/10/opencode-flaw-lets-malicious-mcp.html

🔹 SecurityWeek: Splunk, SolarWinds Release Fresh Security Updates
https://www.securityweek.com/splunk-solarwinds-release-fresh-security-updates/

🔹 The Hacker News: Railway Says Intruder May Have Accessed Customer Secrets, Urges Credential Rotation
https://thehackernews.com/2026/10/railway-says-intruder-may-have-accessed.html

🦠 Malwarebytes: Woman faces years in prison over a Cash App account she says she never opened
https://www.malwarebytes.com/blog/news/2026/10/woman-faces-years-in-prison-over-a-cash-app-account-she-says-she-never-opened

🔹 The Hacker News: The AI Agent Nobody Owns: Watch Expert Webinar On Your Newest Insider Threat
https://thehackernews.com/2026/10/the-ai-agent-nobody-owns-watch-expert.html

🔹 The Record from Recorded Future News: South Carolina officials offer assistance after state capital hit with cyberattack
https://therecord.media/south-carolina-officials-offer-assistance-cyber-incident

🔹 SecurityWeek: Tech and Security Companies Respond to PHP2Shell Vulnerabilities
https://www.securityweek.com/tech-and-security-companies-respond-to-php2shell-vulnerabilities/

🔹 SecurityWeek: Signal Vulnerability Lets Malicious Callers Block Hang-Ups
https://www.securityweek.com/signal-vulnerability-lets-malicious-callers-block-hang-ups/

🔹 SecurityWeek: Indurex Raises $8 Million to Expand Industrial Cybersecurity Platform
https://www.securityweek.com/indurex-raises-8-million-to-expand-industrial-cybersecurity-platform/

🔹 The Record from Recorded Future News: Cybercrime crackdown across Africa leads to 1,462 arrests, $105 million seized
https://therecord.media/africa-cybercrime-interpol-arrests

🔹 The Hacker News: INTERPOL Arrests 1,462 Suspects, Disrupts 10,909 Cybercrime Networks in Global Crackdown
https://thehackernews.com/2026/10/interpol-arrests-1462-suspects-disrupts.html

🔹 Security News | TechCrunch: Developer platform Railway urges ‘all users’ to revoke secret keys after cyberattack
https://techcrunch.com/2026/10/22/developer-platform-railway-urges-all-users-to-revoke-secret-keys-after-cyberattack/

🦠 Malwarebytes: Scammers are finding new ways to target your phone. Here are 5 ways to protect yourself
https://www.malwarebytes.com/blog/scams/2026/10/scammers-are-finding-new-ways-to-target-your-phone-here-are-5-ways-to-protect-yourself

🔹 SecurityWeek: Hacker Conversations: Corey Thuen and the Evil Bit
https://www.securityweek.com/hacker-conversations-corey-thuen-and-the-evil-bit/

🔹 The Hacker News: Meta Ordered to Pay $25 Billion After Court Finds 43 Million Privacy Violations
https://thehackernews.com/2026/10/meta-ordered-to-pay-25-billion-after.html

#InfoSec #SecurityNews

MalwarebytesDelivery bots accused of illegally scanning customersTwo lawsuits allege delivery robots scanned customers’ faces without consent, linked scans to names and addresses, and used them to train AI.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Skoro @lacze dalej nie potrafi odpuścić i publikuje kolejne wielostronicowe elaboraty, czas napisać to jasno i definitywnie. Twierdzisz, że "działasz bez parcia na szkło" i "nie dla ego", a właśnie napisałeś esej w obronie własnego wizerunku, przy okazji publicznie przyznając, że to Ty pierwszy napisałeś do mnie na priv, bo mój blog zrobił na Tobie wrażenie. Jeśli to nie jest definicja urażonego ego, to nie wiem, co jest.

Zarzucasz mi hipokryzję w sprawie Brave i Safe Browsing. Po raz kolejny nie zrozumiałeś mojego wpisu. W mojej konfiguracji owszem, wspominam o wyłączeniu Safe Browsing, ale jako o ŚWIADOMYM, OPCJONALNYM KOMPROMISIE. Jeśli ktoś woli ukryć IP przed Google kosztem utraty ochrony, to jego wybór. Różnica polega na tym, że ja prezentuję to jako trade-off, a Ty twierdzisz, że NextDNS to ZAMIENNIK Safe Browsing. To bzdura, bo NextDNS działa tylko na poziomie domen i nie widzi ścieżek URL. Twoja filozofia "prywatność ponad bezpieczeństwo" jest absurdalna. IEEE wprost stwierdza, że bezpieczeństwo jest warunkiem wstępnym prywatności.

Nazywasz mnie kopistą. Owszem, wzorowałem się na dobrych źródłach, bo na tym polega rzetelna kwerenda. Różnica między nami polega na tym, że ja te źródła rozumiem i wyciągam z nich wnioski. Ty natomiast tłumaczysz cudze teksty DeepL-em i nie rozumiesz nawet własnych cytatów.

Zastanawia mnie też Twoja obsesja. Kto normalny stalkuje kogoś z innych kont i trybu incognito, mimo że został zablokowany i olany? Piszesz wielostronicowe dokumenty, bo Twoje kruche ego nie potrafi przyjąć do wiadomości, że ktoś po prostu Cię zignorował.

A na koniec mały dodatek, który pokazuje kwintesencję Twojego "bezpieczeństwa". Pouczasz wszystkich o OPSEC i Zero Trust, a jednocześnie trzymasz "telefon obywatela" z usługami Google, mObywatelem i aplikacjami bankowymi w torbie Faradaya. Wyraźnie nie wiesz, że telefon w torbie nadal zbiera telemetrię offline. Gdy tylko go wyciągniesz, żeby zalogować się do banku, złapie sieć i natychmiast wyśle cały ten bufor do Google. Twój cały wypracowany wizerunek z GrapheneOS pada w tym jednym momencie.

To mój ostatni wpis na ten temat. Zamykam ten rozdział u siebie. Idę robić rzeczy, które mają realną wartość. EOT.

#Cyberbezpieczeństwo #Prywatność #OPSEC #ZeroTrust #InfoSec
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PHP2Shell (CVE-2026-109618/109619): two RCEs in PHP itself. Unauthenticated attackers can run code before any app code runs.

Patched: 8.5.12, 8.4.27, 8.3.36, 8.2.35. PHP 8.1 and older: no fix from the PHP project, ask your distro.

Can't update today? Free, tentative CrowdSec WAF virtual patches:

CVE-2026-109618: https://app.crowdsec.net/hub/author/crowdsecurity/waf-rules/vpatch-CVE-2026-109618
CVE-2026-109619: https://app.crowdsec.net/hub/author/crowdsecurity/waf-rules/vpatch-CVE-2026-109619

A stopgap, not a fix.

#PHP #infosec #CVE #sysadmin
app.crowdsec.netPHP - RCE WAF Rule by crowdsecurity | CrowdSec HubTentative vpatch for CVE-2026-109618 : block requests crafted to exhaust PHP memory during input parsing.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Winning headline of the day, for sure. 😅

It gets funnier:

"New reseller agreement pairs Docker Hardened Images with ActiveState's trusted open source, securing the container and everywhere else open source runs, without slowing developers down."

Yahoo: ActiveState Partners With Docker to Secure the Open Source in Enterprise Containers https://finance.yahoo.com/technology/ai/articles/activestate-partners-docker-secure-open-110700943.html #infosec #Docker #OpenSource

Yahoo FinanceActiveState Partners With Docker to Secure the Open Source in Enterprise ContainersActiveState today announced a reselling partnership with Docker, Inc., the trusted platform for building software in the agentic era. The partnership pairs Docker Hardened Images (DHI), the hardened foundation for enterprise containers, with ActiveState's trusted open source components. The two companies will jointly go to market and resell each other's offerings. Enterprises can source a hardened
↩ Reply ♡ 0 · ↻ 0 ↗ Original

New.

The attacks targeted more than 5,700 accounts across 28 Microsoft 365 tenants in Latin America.

"All 7 successfully compromised accounts were unmanaged functional/service accounts with no prior legitimate login baseline, strongly indicating default or predictable passwords that had never been rotated, with no MFA enforcement."

Proofpoint: Spraying in the Andes: TeamFiltration Returns to Exploit Forgotten Service Accounts https://www.proofpoint.com/us/blog/threat-insight/Spraying-in-the-Andes-TeamFiltration-Returns #infosec #threatresearch #Microsoft

ProofpointSpraying in the Andes: TeamFiltration Returns to Exploit Forgotten Service Accounts | Proofpoint USKey Takeaways Proofpoint researchers identified an active TeamFiltration campaign - tracked as UNK_CondorFiltration, that targeted over 5,700 accounts across 28 Microsoft 365 tenants in
↩ Reply ♡ 0 · ↻ 0 ↗ Original

New.

"Curiously, the file inst.exe does not contain any malicious strings or embedded blobs. All the files needed to install the malicious payload are inside PVMDIJGKAX2, which makes it harder for incident responders to retrieve the bootkit components."

Kaspersky: How APT41 revived the BlackLotus bootkit to attack diplomatic organizations in Central Asia https://securelist.com/uefi-bootkit-blackx/121539/ @Kaspersky #infosec #threatresearch #malware

SecurelistNew BlackX UEFI bootkit exploiting Baton DropKaspersky GReAT experts discovered a new UEFI bootkit, BlackX. It exploits the Baton Drop vulnerability (CVE-2022-21894) and is similar to the BlackLotus bootkit.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

New. Part research, part marketing, FYI.

Huntress: Unboxing Phishing Kits: Advanced Cred Theft for Entry-Level Hackers https://www.huntress.com/blog/unboxing-phishing-kits @huntress #infosec #threatresearch #phishing #scam

HuntressUnboxing Phishing Kits: Huntress Examines 3 Real Kits | HuntressHuntress examines 3 phishing kits that hand beginner attackers everything they need to steal tokens. See what the attacks look like from the inside.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

New.

ESET: MythicRatatoskr: An Yggdrasil-enabled backdoor deployed in a UAC-0099-Sandworm collaboration https://www.welivesecurity.com/en/eset-research/mythicratatoskr-yggdrasil-enabled-backdoor-deployed-uac0099-sandworm-collaboration/ @ESETresearch #infosec #malware #threatresearch #cyberattack

www.welivesecurity.comMythicRatatoskr: An Yggdrasil-enabled backdoor deployed in a UAC‑0099-Sandworm collaborationESET researchers uncover MythicRatatoskr – a previously unknown Go-based backdoor hiding its C&C server inside the Yggdrasil mesh network – that paved the way for a destructive attack against a Ukrainian grain firm.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

The French courts yesterday handed down an unfavorable ruling against Quad9 in a major case that undermines the transparency and stability of the internet. As a result, Quad9 will no longer be able to offer its free cyberprotection service to users located in France effective November 24.

https://quad9.net/news/blog/au-revoir-france/

#DNS #InternetIntegrity #infosec

‘quad9,’ logo beside a cracked vertical divide and a blue-white-red map of France.
Quad9Quad9 | A public and free DNS service for a better security and privacyA public and free DNS service for a better security and privacy
↩ Reply ♡ 0 · ↻ 0 ↗ Original

"European regulators are investigating whether Booking.com is doing enough to protect travelers from fraudsters who exploit hotel reservations, impersonate property owners, and trick customers into making fraudulent payments."

Bitdefender: Booking.com has a scam problem. The EU wants answers https://www.bitdefender.com/en-us/blog/hotforsecurity/eu-booking-com-phishing-scams-investigation #scam #infosec

Hot for SecurityEU investigates Booking.com over phishing scamsThe EU is investigating Booking.com over fake hotel listings, phishing scams and fraudulent payments. Here's what travelers should know.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : PRIVACY SAFE

Our 18th edition, Hackfest Level Up, would not be possible without our sponsors. And this year, we are happy to have Privacy Safe, a SMB BOOTH sponsor!

If you want to learn more about this company’s mission, visit their website https://privacy-safe.io/

PS: YOU CAN STILL BUY YOUR TICKET for October 29–31, 2026 at the Convention Center of Québec ;) More info: https://hackfest.ca/en/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
Privacy SafePrivacy Safe | Automatisez votre conformité (Loi 25, RGPD) sans complexitéPrivacy Safe est une solution SaaS qui simplifie la gestion des renseignements personnels en conformité avec la Loi 25, le RGPD et le CCPA. Centralisez, sécurisez et automatisez vos obligations sans complexité.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : PRIVACY SAFE

La prochaine édition du 18e Hackfest Level Up ne serait pas possible sans nos partenaires. Nous sommes heureux d’avoir avec nous Privacy Safe, qui est un partenaire KIOSQUE PME!

Visiter leur site web : https://privacy-safe.io/

PS VOUS POUVEZ TOUJOURS ACHETER VOS BILLETS pour les 29, 30 et 31 octobre 2026 au Centre des congrès de Québec ;) Info sur notre site web : https://hackfest.ca/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
Privacy SafePrivacy Safe | Automatisez votre conformité (Loi 25, RGPD) sans complexitéPrivacy Safe est une solution SaaS qui simplifie la gestion des renseignements personnels en conformité avec la Loi 25, le RGPD et le CCPA. Centralisez, sécurisez et automatisez vos obligations sans complexité.
↩ Reply ♡ 0 · ↻ 0 ↗ Original