X XFediYour place in the Fediverse
XFEDI

#InfoSEC

ActivityPub

Public posts with this hashtag.

PARTENAIRE HACKFEST 2026 SPONSOR : PRIVACY SAFE

Our 18th edition, Hackfest Level Up, would not be possible without our sponsors. And this year, we are happy to have Privacy Safe, a SMB BOOTH sponsor!

If you want to learn more about this company’s mission, visit their website https://privacy-safe.io/

PS: YOU CAN STILL BUY YOUR TICKET for October 29–31, 2026 at the Convention Center of Québec ;) More info: https://hackfest.ca/en/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors
#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
Privacy SafePrivacy Safe | Automatisez votre conformité (Loi 25, RGPD) sans complexitéPrivacy Safe est une solution SaaS qui simplifie la gestion des renseignements personnels en conformité avec la Loi 25, le RGPD et le CCPA. Centralisez, sécurisez et automatisez vos obligations sans complexité.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : PRIVACY SAFE

La prochaine édition du 18e Hackfest Level Up ne serait pas possible sans nos partenaires. Nous sommes heureux d’avoir avec nous Privacy Safe, qui est un partenaire KIOSQUE PME!

Visiter leur site web : https://privacy-safe.io/

PS VOUS POUVEZ TOUJOURS ACHETER VOS BILLETS pour les 29, 30 et 31 octobre 2026 au Centre des congrès de Québec ;) Info sur notre site web : https://hackfest.ca/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
Privacy SafePrivacy Safe | Automatisez votre conformité (Loi 25, RGPD) sans complexitéPrivacy Safe est une solution SaaS qui simplifie la gestion des renseignements personnels en conformité avec la Loi 25, le RGPD et le CCPA. Centralisez, sécurisez et automatisez vos obligations sans complexité.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Let's hope this doesn't include targets among allies, such as they are. The unit was created quietly in April.
"The creation of the Technology Support Office signals the Defense Department's intent to ramp up a range of aggressive covert activities abroad."

"TSO as it is called internally, is nearly impossible to find on Pentagon websites, and the agency is mentioned by name only in several previously unreported Defense Department historical records and memoranda."

Politico: The Pentagon is quietly building an elite new tech sabotage agency https://www.politico.com/news/2026/10/22/technology-support-office-dod-tech-spyware-sabotage-01100327 @politico #infosec

POLITICOThe Pentagon is quietly building an elite new tech sabotage agencyThe creation of the Technology Support Office signals the Defense Department's intent to ramp up a range of aggressive covert activities abroad.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

If you missed this yesterday, the platform is called Athena StealthRoute. In addition to phishing on demand, the service includes "a marketplace and link-cloaking capabilities designed to divert security scanners away from malicious destinations."

Infosecurity-Magazine: New PhaaS Platform Uses AI to Craft Phishing Lures and Mask Malicious Activity https://www.infosecurity-magazine.com/news/new-phaas-uses-ai-phishing-lures/ #infosec #phishing #cybercrime

Infosecurity MagazineNew PhaaS Platform Uses AI to Craft Phishing Lures and Mask MaliciousResearchers have uncovered Athena StealthRoute, a phishing-as-a-service platform featuring an AI Studio
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PHP2Shell field report — the attacker-side view.

The first exploit-shaped request hit our Mirage honeypot fleet at 21:57 UTC on 20 Oct, ~16h before the patch embargo lifted. Over the next 48h: 9 source IPs, 7 countries, 2 distinct attack shapes.

Highlights:

One actor swept body size <1KB → 16KB+, 200+ unique payloads in 2 min — live calibration of the OOM trigger
The lead tool stamps ----p2shell<hex> into its multipart boundary: a zero-false-positive detection tell we haven’t seen documented elsewhere
A B8RAT/1.0 actor reaching for the deserialization path (CVE-2026-109619) while others hammer the OOM path (CVE-2026-109618)
Independent confirmation of the pre-disclosure exploitation Amazon & Cloudflare reported, from a second sensor network

Full writeup + IOCs:
https://offseq.com/en/research/php2shell-first-48-hours/

#infosec #PHP2Shell #threatintel #honeypot #PHP #CVE

OffSeqPHP2Shell in the wild: the first 48 hours on a honeypot fleet – OffSeqPHP2Shell leaked before its patch, and the first exploit-shaped request hit OffSeq's Mirage fleet about sixteen hours before the fix shipped.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

"Users who downloaded an unpinned version of LiteLLM between 11:39 a.m. and 1:23 p.m. UTC via pip or used the Docker image v1.107.0, latest, main-latest, or main-stable between 11:46 a.m. and 2:20 p.m. UTC are impacted."

LiteLLM, from yesterday: Contained: Oct 21, 2026 LiteLLM release v1.107.0 Compromised https://docs.litellm.ai/blog/security-incident-oct-21-2026

More:

The Hacker News: LiteLLM Suspects GitHub Token Leak in AI Gateway Logs Behind Malicious Package Release https://thehackernews.com/2026/10/litellm-suspects-github-token-leak-in.html @thehackernews #GitHub #infosec #Docker

docs.litellm.aiContained: Oct 21, 2026 LiteLLM release v1.107.0 Compromised | liteLLMLiteLLM release v1.107.0 was compromised by a malicious actor.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Railway made the disclosure yesterday: https://blog.railway.com/p/security-disclosure-wednesday-october-21st

More:

The Hacker News:

Platform-as-a-Service Provider Railway Says Intruder May Have Accessed Customer Secrets, Urges Credential Rotation https://thehackernews.com/2026/10/railway-says-intruder-may-have-accessed.html @thehackernews #infosec #databreach

Railway BlogSecurity Disclosure: Wednesday October 21st | Railway BlogRailway detected anomalous activity involving systems that store customer environment variables and recommends your immediate attention
↩ Reply ♡ 0 · ↻ 0 ↗ Original

"A pair of Marines filed a class-action lawsuit Tuesday against the Pentagon over a data breach at the Defense Manpower Data Center, or DMDC, arguing it allowed scammers to obtain and use their personally identifiable information, or PII."

Military Times: Pentagon ignored cybersecurity flaws before data breach, Marines’ lawsuit says https://www.militarytimes.com/news/pentagon-congress/2026/10/22/pentagon-ignored-cybersecurity-flaws-before-data-breach-marines-lawsuit-says/ #infosec #scam #databreach

Military TimesPentagon ignored cybersecurity flaws before data breach, Marines’ lawsuit saysA pair of Marines filed a class-action lawsuit Tuesday against the Pentagon over a data breach at the Defense Manpower Data Center.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
T

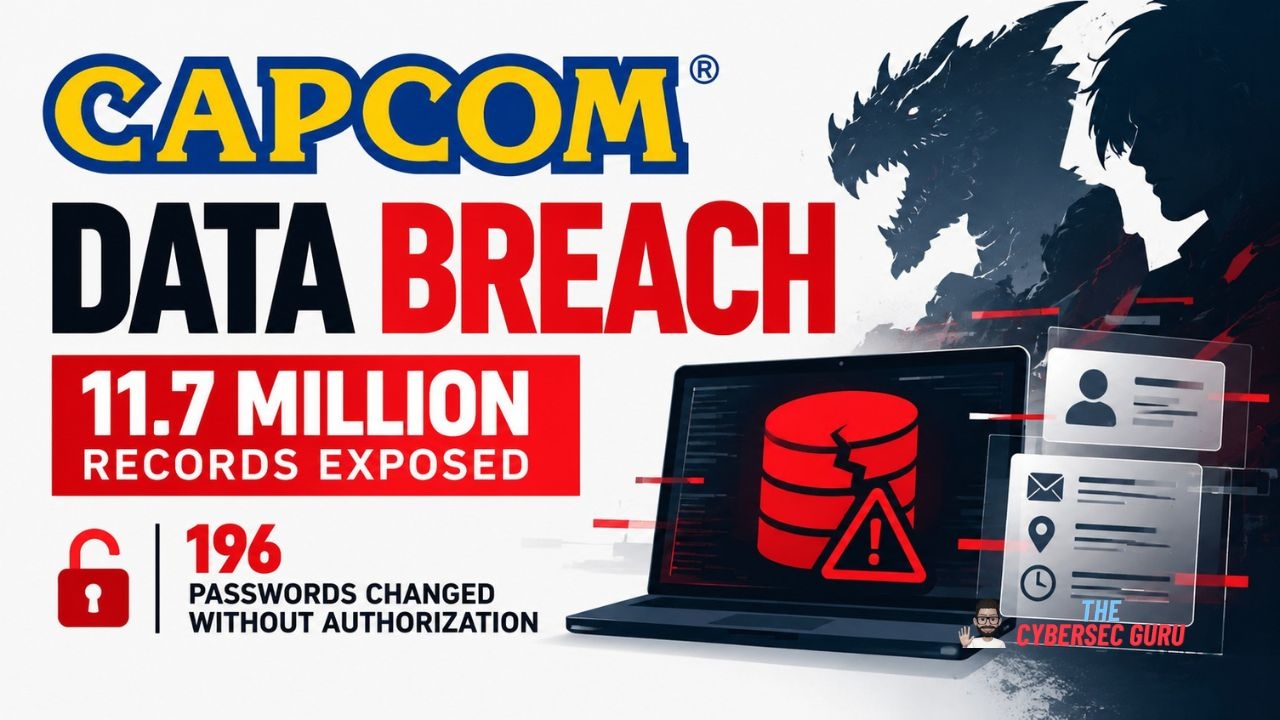
Capcom's CAPCOM ID breach exposed 11.7 Million records.

The part that stands out: 196 accounts had their passwords changed without authorization.

Exposed data includes email addresses, IP addresses, last-login timestamps and login counts.

Capcom says credit card data wasn't involved. It has not confirmed that users' original passwords were compromised.

The bigger concern is what attackers can do with millions of real account records: targeted phishing, account takeover attempts and cross-platform profiling.

The root cause remains unconfirmed. IDOR, session abuse and account recovery flaws are possibilities, not established findings.

Technical breakdown 👇
https://thecybersecguru.com/news/capcom-id-breach-2026/

#InfoSec #CyberSecurity #DataBreach

❞ Quoted postThe CyberSec Guru

Content warning: Capcom confirmed a CAPCOM ID breach exposing 11.8M records and 196 unauthorized password changes. What leaked, how it may have happened, and what to do

The CyberSec GuruCAPCOM ID Breach: 11.7M Exposed, 196 Passwords Changed | The CyberSec GuruCapcom confirmed a CAPCOM ID breach exposing 11.7M records and 196 unauthorized password changes. What leaked, how it may have happened, and what to do
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : GOSECURE

Our 18th edition, Hackfest Level Up, would not be possible without our sponsors. And this year, we are happy to have GoSecure, a DÉPANNEUR sponsor!

If you want to learn more about this company’s mission, visit their website https://gosecure.ai/

PS: YOU CAN STILL BUY YOUR TICKET for October 29–31, 2026 at the Convention Center of Québec ;) More info: https://hackfest.ca/en/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
GoSecure24/7 managed detection, response, and expert cybersecurity services - GoSecureWe provide around-the-clock threat detection and incident response, backed by expert consulting to keep your organization secure.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

📣 Say hello to the Spamhaus Sender Guidelines! These are for anyone running a mail server, from your IT admin to the biggest ESPs...and because DNS is kind of our thing, we've also built a HELO/DNS checker too!

We're really proud of this one, and we hope it makes life easier for senders everywhere. Now, go grab a cup of coffee, have a read and test your setup:

👉️ https://www.spamhaus.org/sender-guidelines/

🇫🇷 If you’re heading to #M3AAWG68 next week, come and tell us what you think!

#EmailSecurity #InfoSec

Media attachment
The Spamhaus ProjectSender Guidelines | SpamhausPractical email sender best practices from Spamhaus — covering infrastructure, authentication, list hygiene, reputation, and ESP requirements.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : GOSECURE

La prochaine édition du 18e Hackfest Level Up ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous GoSecure, qui est un partenaire DÉPANNEUR!

Visiter leur site web : https://gosecure.ai/

PS VOUS POUVEZ TOUJOURS ACHETER VOS BILLETS pour les 29, 30 et 31 octobre 2026 au Centre des congrès de Québec ;) Info sur notre site web : https://hackfest.ca/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
GoSecure24/7 managed detection, response, and expert cybersecurity services - GoSecureWe provide around-the-clock threat detection and incident response, backed by expert consulting to keep your organization secure.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

The number of Certificate Authorities (CA) – which can sign valid certificates for *any site* – that our devices trust by default is kinda ridiculous and outrageous.

It's dozens of entities you've never heard of. Not to pick on anyone in particular, as they might be doing a fine / better job than eMudhra, but do you need to trust the GUANG DONG CERTIFICATE AUTHORITY CO LTD. or XRamp Security Services inc.?

Well you can disable whatever CA your phone trusts.

#infosec #cybersecurity

↩ Reply ♡ 0 · ↻ 0 ↗ Original

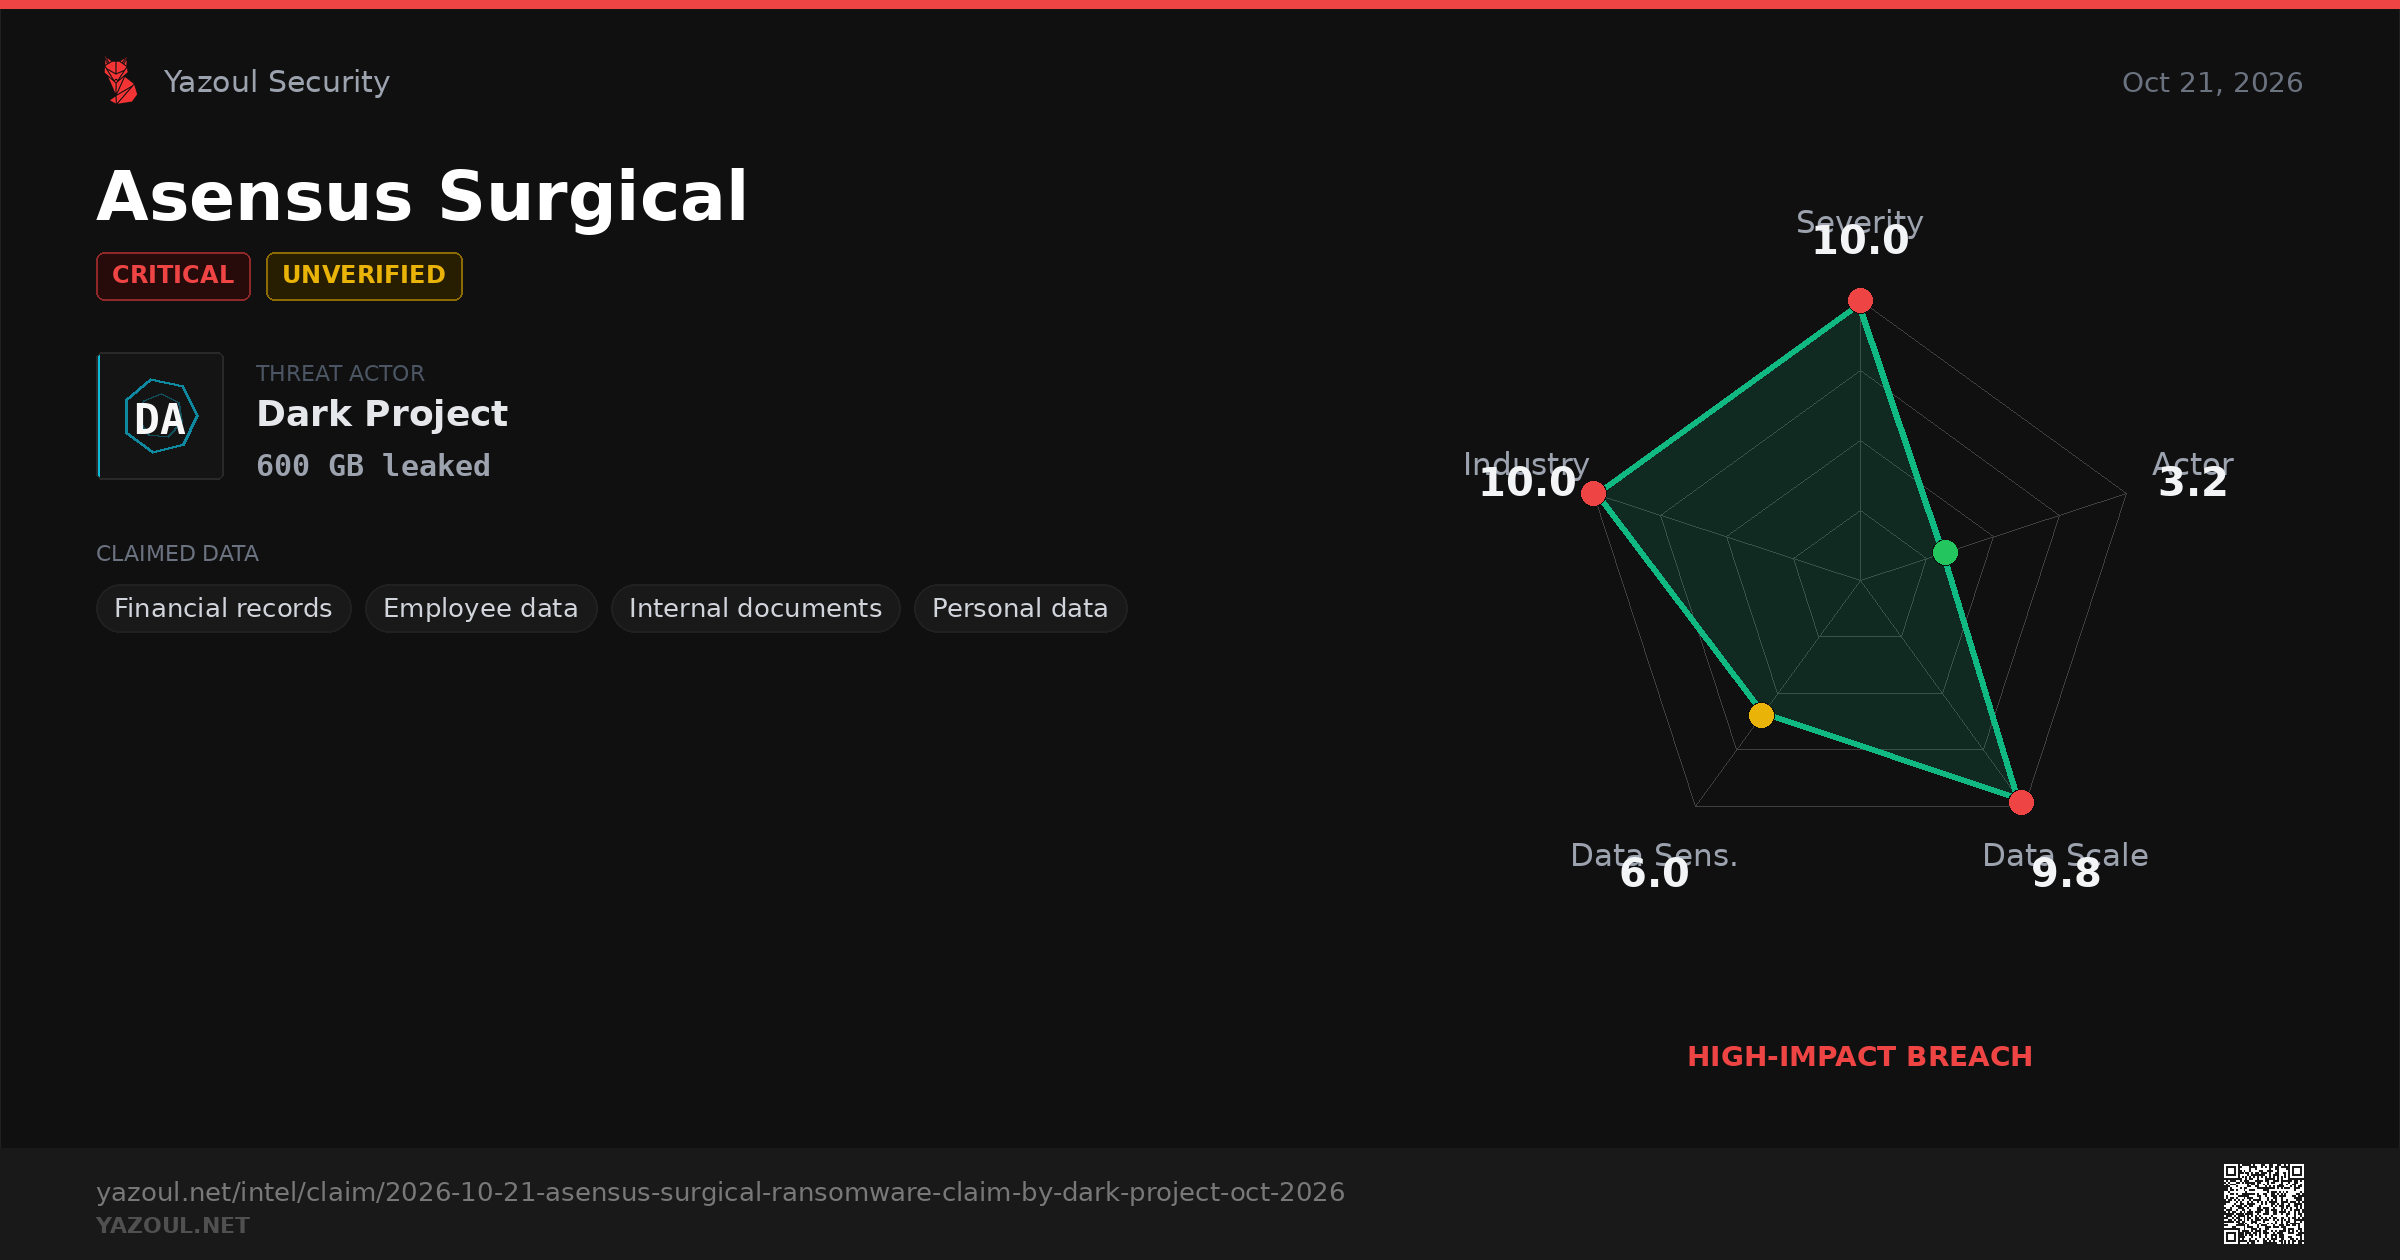
🛡 THREAT INTEL | Asensus Surgical

🔴 Actor "Dark Project" claims 600GB

Allegedly exposed (+1 more)
• Financial records
• Employee data
• Internal documents

⚠️ Unverified claim

https://www.yazoul.net/intel/claim/2026-10-21-asensus-surgical-ransomware-claim-by-dark-project-oct-2026

by Yazoul AI

#DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec

Yazoul SecurityAsensus Surgical Ransomware Claim by Dark Project (Oct 2026)Dark Project allegedly claims 600GB stolen from Asensus Surgical. Unverified leak site data on the healthcare robotics firm. Read our cautious analysis now.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
T

🚨 PingCAP's TiDB Cloud breach raises some serious questions.

FulcrumSec claims it ran a data collection pipeline every 6 hours for 22 days, allegedly stealing massive amounts of customer data.

The confirmed exposure includes customer metadata, SQL editor history, billing records, encrypted API key values and source code.

PingCAP says there's no evidence TiDB production data was impacted. The alleged 10.6 TB haul and the attacker's collection method remain unverified.

The real concern? Your production database can be untouched while the control plane managing it gets compromised.

Full technical breakdown: https://thecybersecguru.com/news/pingcap-data-breach-tidb-cloud/

#InfoSec #CloudSecurity

❞ Quoted postThe CyberSec Guru

Content warning: PingCAP confirmed stolen service account credentials led to a TiDB Cloud breach. See what was taken, what FulcrumSec claims, and which keys to rotate now

The CyberSec GuruPingCAP Data Breach: TiDB Cloud Control Plane Exposed | The CyberSec GuruPingCAP confirmed stolen service account credentials led to a TiDB Cloud breach. See what was taken, what FulcrumSec claims, and which keys to rotate now
↩ Reply ♡ 0 · ↻ 0 ↗ Original

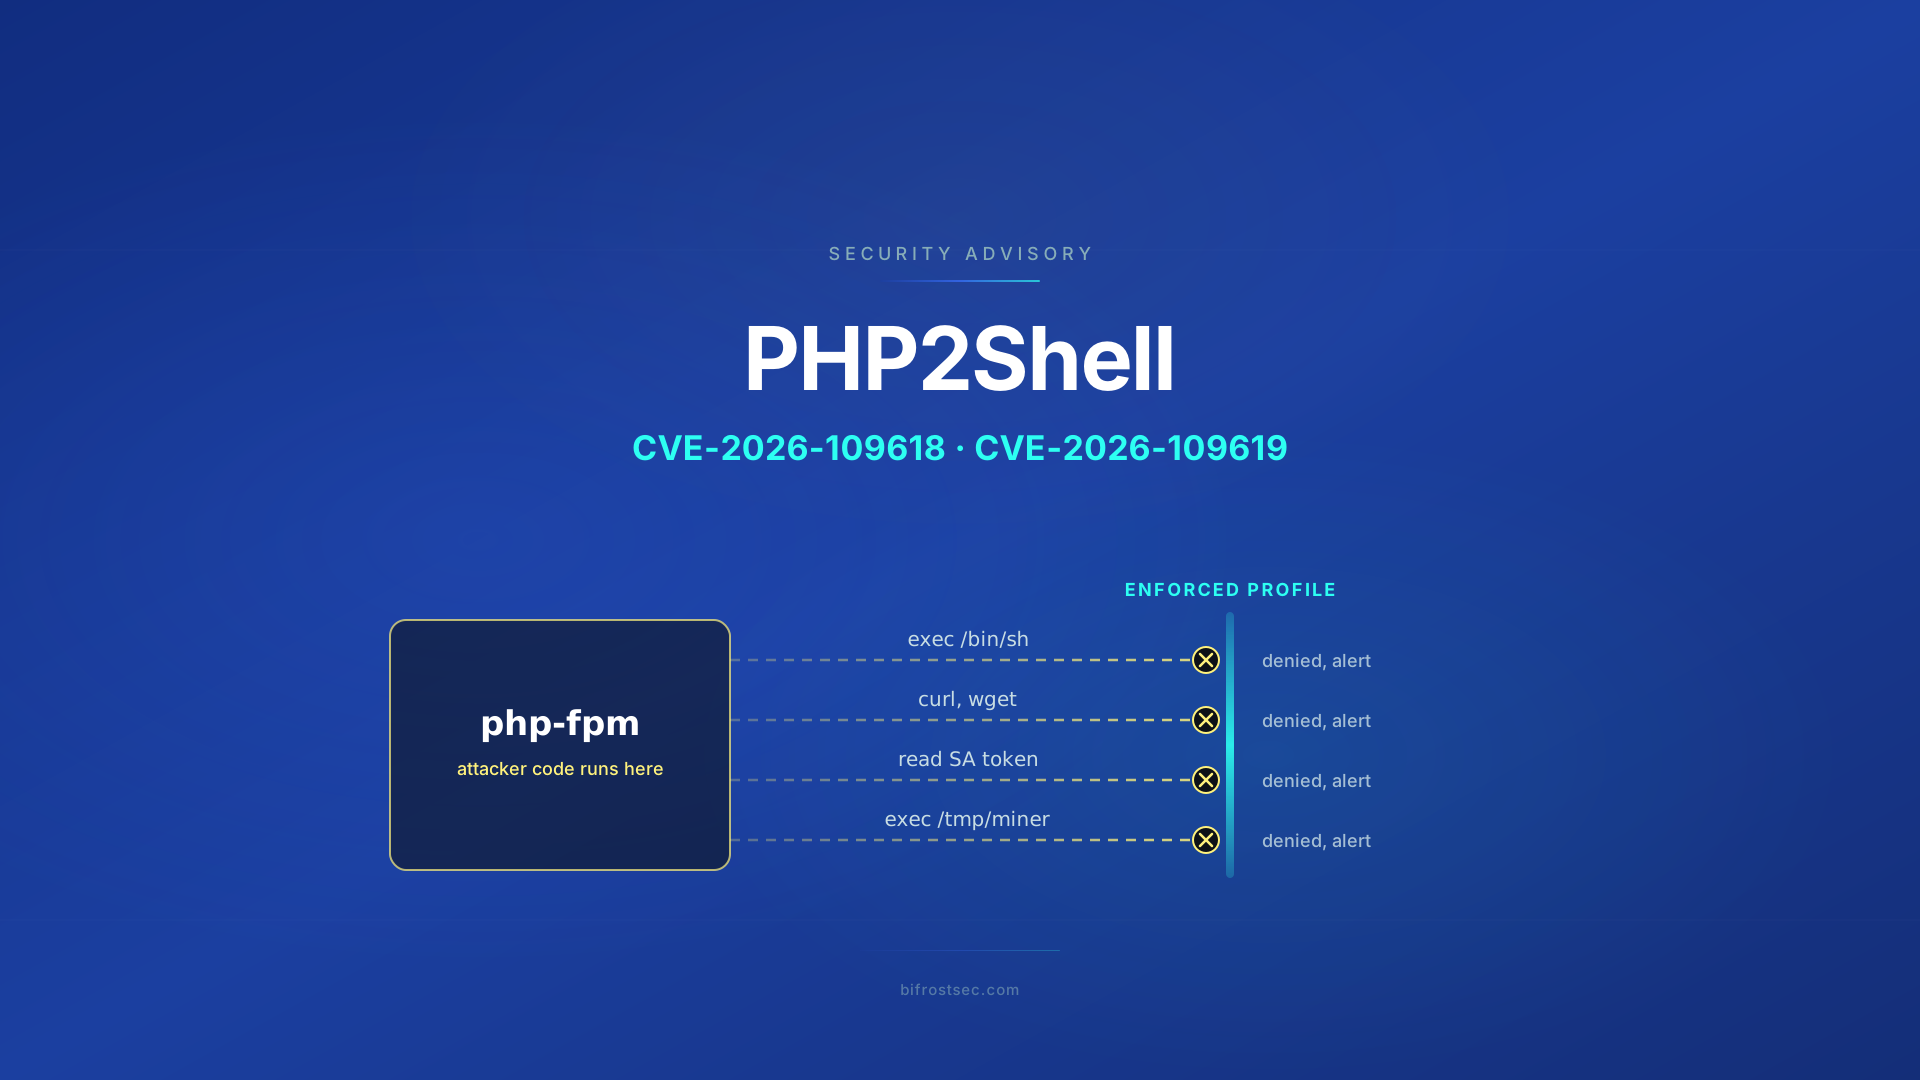
PHP2Shell: patch now. Patching takes days, attacks took hours.

How bifrost security covers the gap:
→ Our CVE prioritisation engine shows every running instance of vulnerable PHP in your clusters
→ Enforced runtime profiles block shells, tool downloads, dropped binaries and credential theft
→ Every blocked attempt is a high-confidence alert

Hardened before the patch.

The deep dive, with what to look for while you patch: https://bifrostsec.com/blog/2026/php2shell-security-advisory/

#PHP2Shell #Kubernetes #infosec #RuntimeSecurity

bifrost securitySecurity advisory: PHP2Shell (CVE-2026-109618, CVE-2026-109619) | bifrost securityTwo critical flaws in the PHP engine, disclosed on 21 October 2026, allow unauthenticated remote code execution and memory disclosure on almost every PHP version since 5.4. In this advisory we look at what is affected, how to patch, and what an enforced AppArmor profile stops until every workload is patched.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CVE-2026-112832 (CRITICAL, CVSS 9.8) in CozyThemes Rootblox <1.0.7 allows unauthenticated remote LFI via improper filename control in PHP. Full system compromise possible. Restrict access & monitor closely. https://radar.offseq.com/threat/cve-2026-112832-improper-control-of-filename-for-includerequire-statement-in-php-program-php-remote-3c455496d4cdf128 #OffSeq #infosec #PHP #LFI

Critical threat: CVE-2026-112832: Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Rem
OffSeq Threat RadarCVE-2026-112832: Improper Control of Filename for… | Threat RadarVulnerability: Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in CozyThemes Rootblox…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Stop staring at your dashboard trying to tell yourself your patching cadence is optimal. It isn't. Most companies treat their vulnerability lists like restaurant menus.

https://theperimetersite.com/report/387

#vulnerability #healthcare #infosec

The Perimeter SiteYour Patching Schedule is a Work of Fiction — The Perimeter SiteStop staring at your dashboard trying to tell yourself your patching cadence is optimal. It isn't. Most companies treat their vulnerability lists like restaurant menus.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

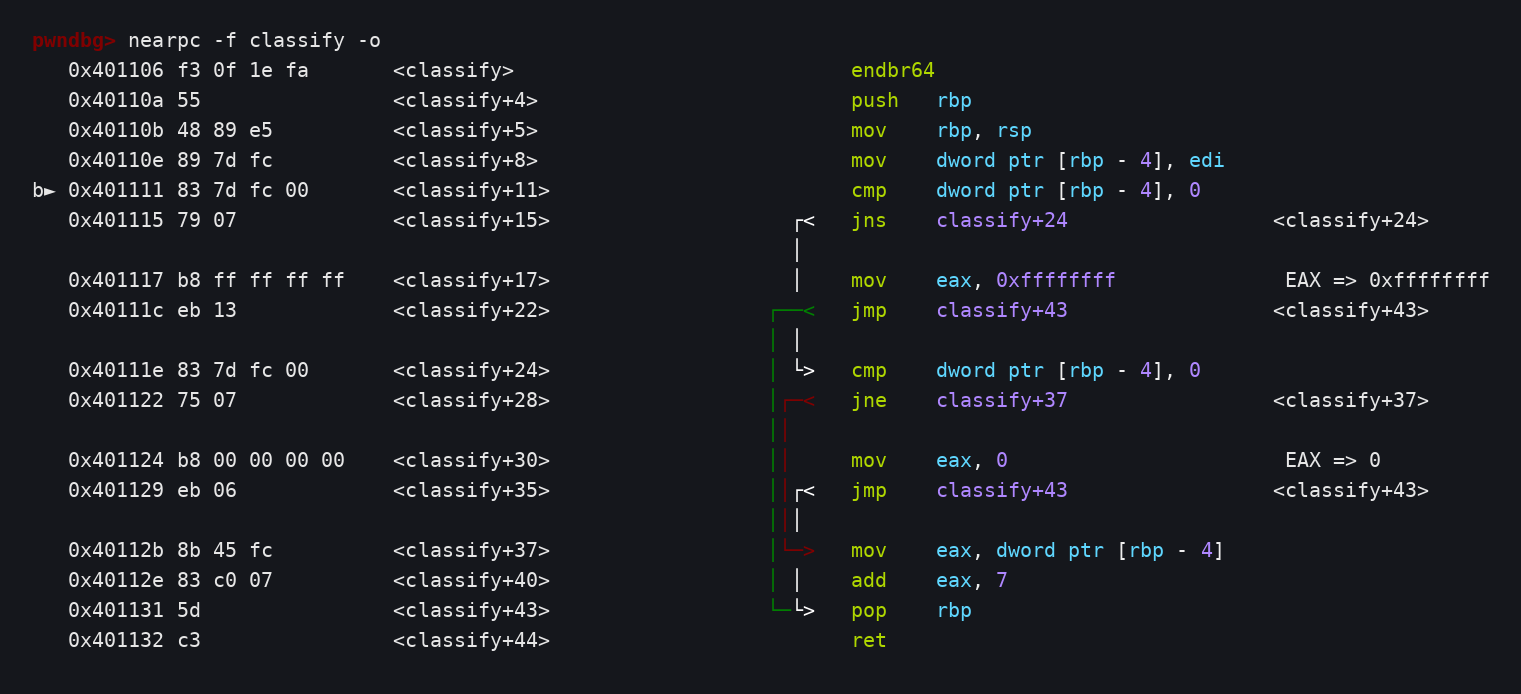
Hi! Welcome a new Pwndbg release: 2026.10.22 !

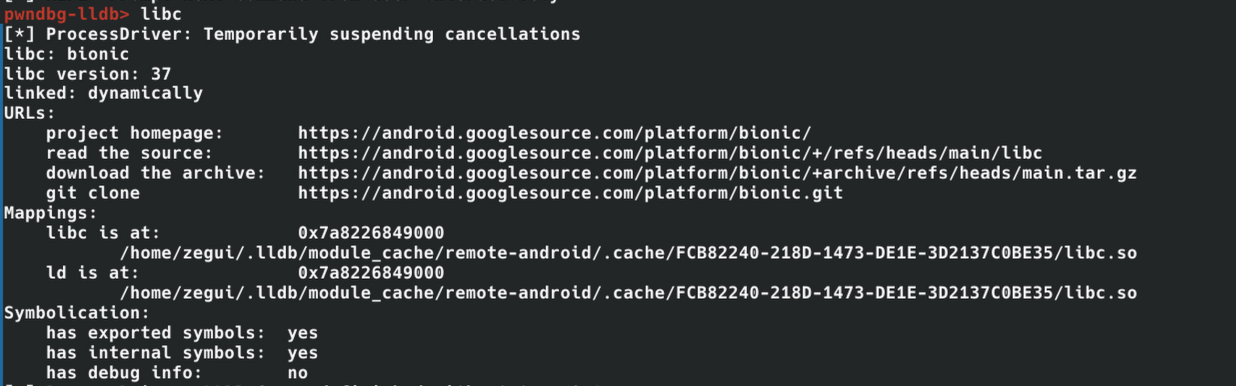
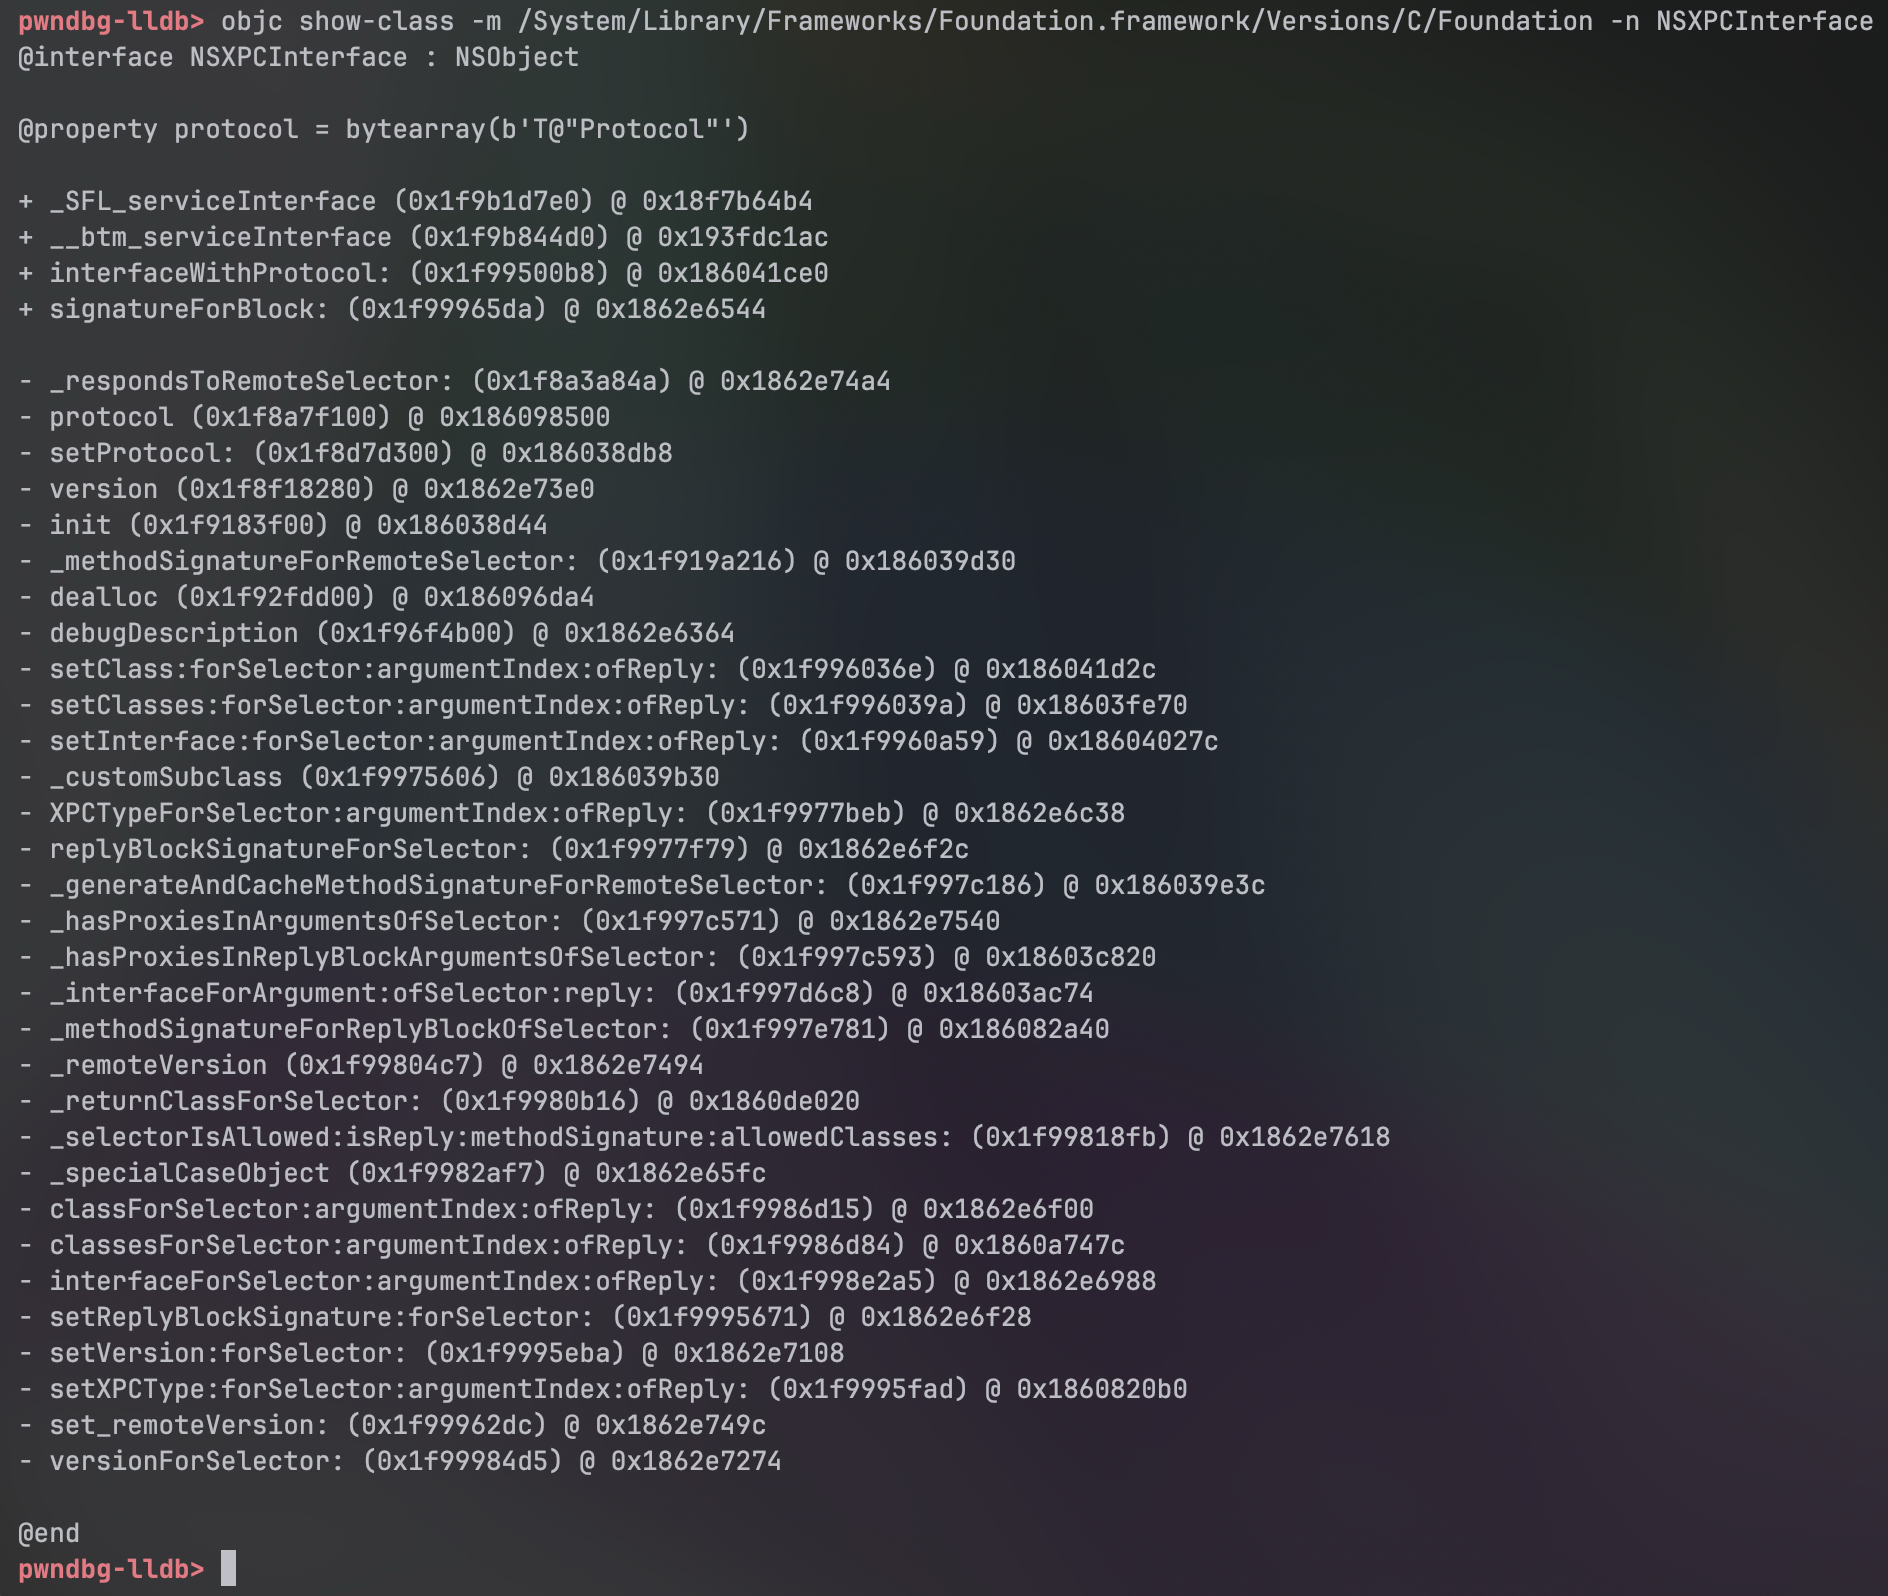
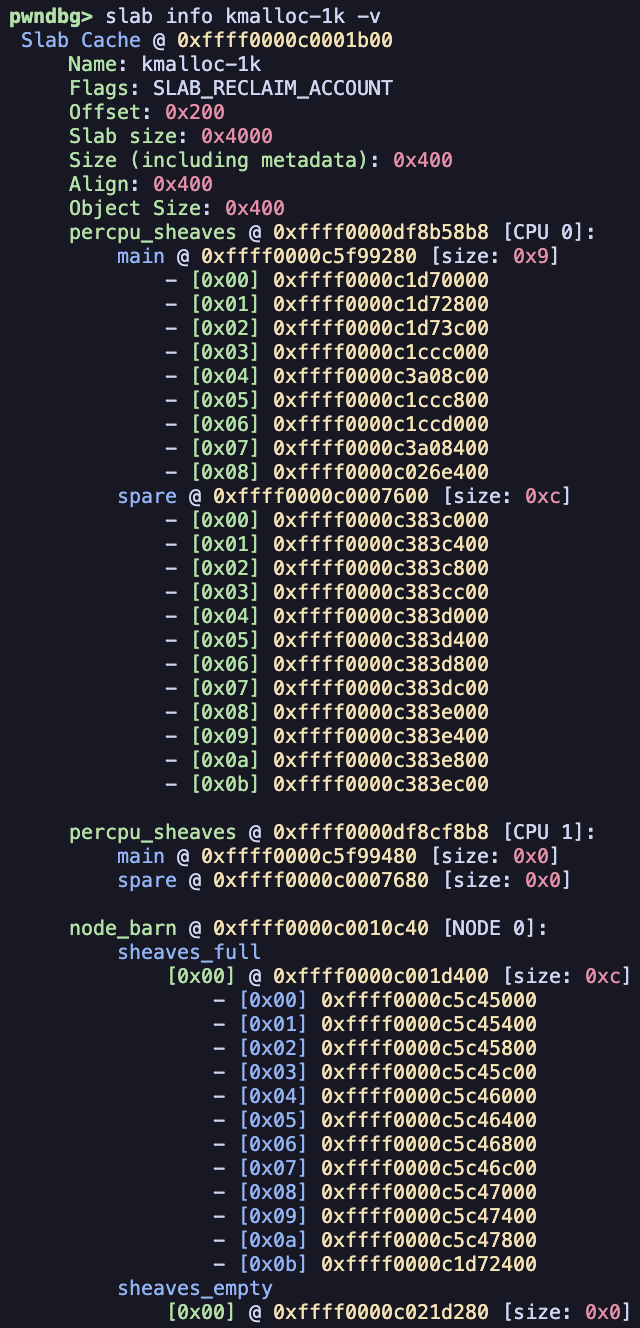
We now support m86k arch, unknown archs, have better C++ support, added tutorials (https://pwndbg.re/dev/tutorials/debugging-cxx/, https://pwndbg.re/dev/tutorials/mangling/, https://pwndbg.re/dev/tutorials/pretty-printing/), `nearpc -o` shows opcode bytes, we have `libcinfo` for Android Bionic libc information, we added Objective-C class inspection commands (`objc show-class` and `objc list-classes`), improved `regs` command (`regs xmm0` and `regs eflags`), have better glibc discovery, added Linux kernel 7+ SLUB sheaf and barn inspection, added `setrlimit` command, improved LLDB support and more (like bug fixes)!

See https://github.com/pwndbg/pwndbg/releases/tag/2026.10.22

Please sponsor us at https://github.com/sponsors/pwndbg !

Thanks to everyone who made it possible!

#pwndbg #gdb #lldb #debugging #security #infosec #pwn #reverseengineering #linux

Media attachmentMedia attachmentMedia attachmentMedia attachment
pwndbg.reDebugging C++ - Documentationpwndbg (/paʊnˈdiˌbʌɡ/) is a GDB plug-in that makes debugging with GDB suck less, with a focus on features needed by low-level software developers, hardware hackers, reverse-engineers and exploit developers.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

We truly can't wait to hear from our fabulous keynote speakers at #osco26! 🤩

⚠️ Stephanie Carstensen will tell us all about "The Day Everything Stops: Preparing for the Cyber Crisis You Hope Never Comes".

🚧 Jahmel Harris will share his insights on "Building a Penetration Testing Lab in 2026".

We believe these topics will inspire great sessions during the open space! Check out the keynote details: https://opensecurityconference.org/conference/keynotes

#osco #Security #CyberSecurity #InfoSec #AppSec #OTSecurity [lisi]

Open Security ConferenceKeynotesWelcome to the Open Security Conference (osco), the people-centred international gathering for everyone interested in cybersecurity. Join us 5-8 November 2026 in Rückersbach, Germany.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Four reports, one week. One conclusion.

Attackers are not breaking AI models. They are walking through the infrastructure.

1,467 MCP servers in one scan. Half the ecosystem repos teach plaintext credential storage. Shadow MCP servers on laptops via Git, Slack, and zip files, never inventoried.

The infrastructure is the attack surface. Screen it.

<https://blog.relayshield.net/attackers-arent-breaking-the-models-theyre-walking-through-the-infrastructure>

#MCP #AISecurity #infosec

blog.relayshield.netAttackers Aren't Breaking the Models. They're Walking Through the Infrastructure. | RelayShieldTrendAI's 1H 2026 State of AI Security report has a finding that should reframe how we think about AI security: attackers are going after the infrastructure around models, not the...
↩ Reply ♡ 0 · ↻ 0 ↗ Original