X XFediYour place in the Fediverse
XFEDI

Remote profile

ActivityPub
Profile banner

Yazoul - Cybersecurity Alerts

@[email protected]

🔐 Yazoul Security — CVE Advisories · Data Breaches · Cyber News
Automated security intelligence: daily CVE alerts, breach reports, correlated news, and learning resources.
🌐 www.yazoul.net
📨 Newsletter: www.yazoul.net/
🔗 @[email protected]
#InfoSec #Cybersecurity #CVE #ThreatIntel #DataBreach

Open remote profile ↗
Posts

🟠 New security advisory:

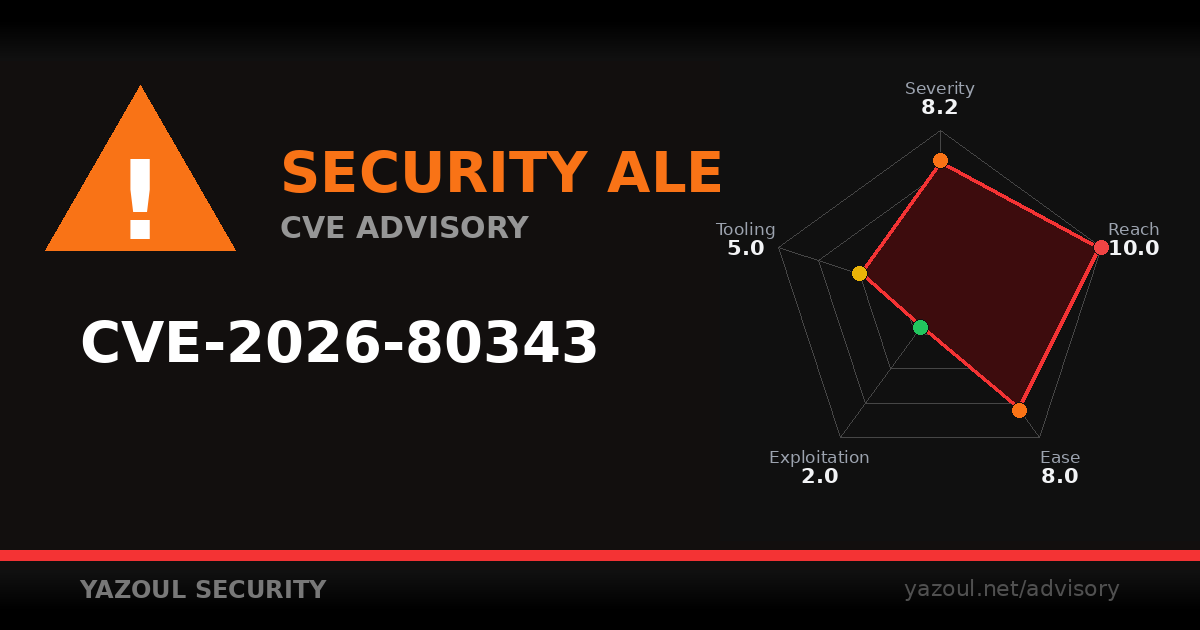
CVE-2026-80343 affects multiple systems.

• Impact: Significant security breach potential
• Risk: Unauthorized access or data exposure
• Mitigation: Apply patches within 24-48 hours

Full breakdown:
https://www.yazoul.net/advisory/cve/cve-2026-80343-camel-netty-http-auth-bypass-exposes-routes-poc

by Yazoul AI
#InfoSec #ZeroDay #ThreatIntel

Yazoul SecurityCamel Netty HTTP auth bypass exposes routes (CVE-2026-80343) [PoC]CVE-2026-80343: Apache Camel 4.0.0-4.22.0 Netty HTTP security constraint bypass lets unauthenticated callers reach protected routes. Upgrade to 4.23.0 or 4.18.5/4.22.1 LTS.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

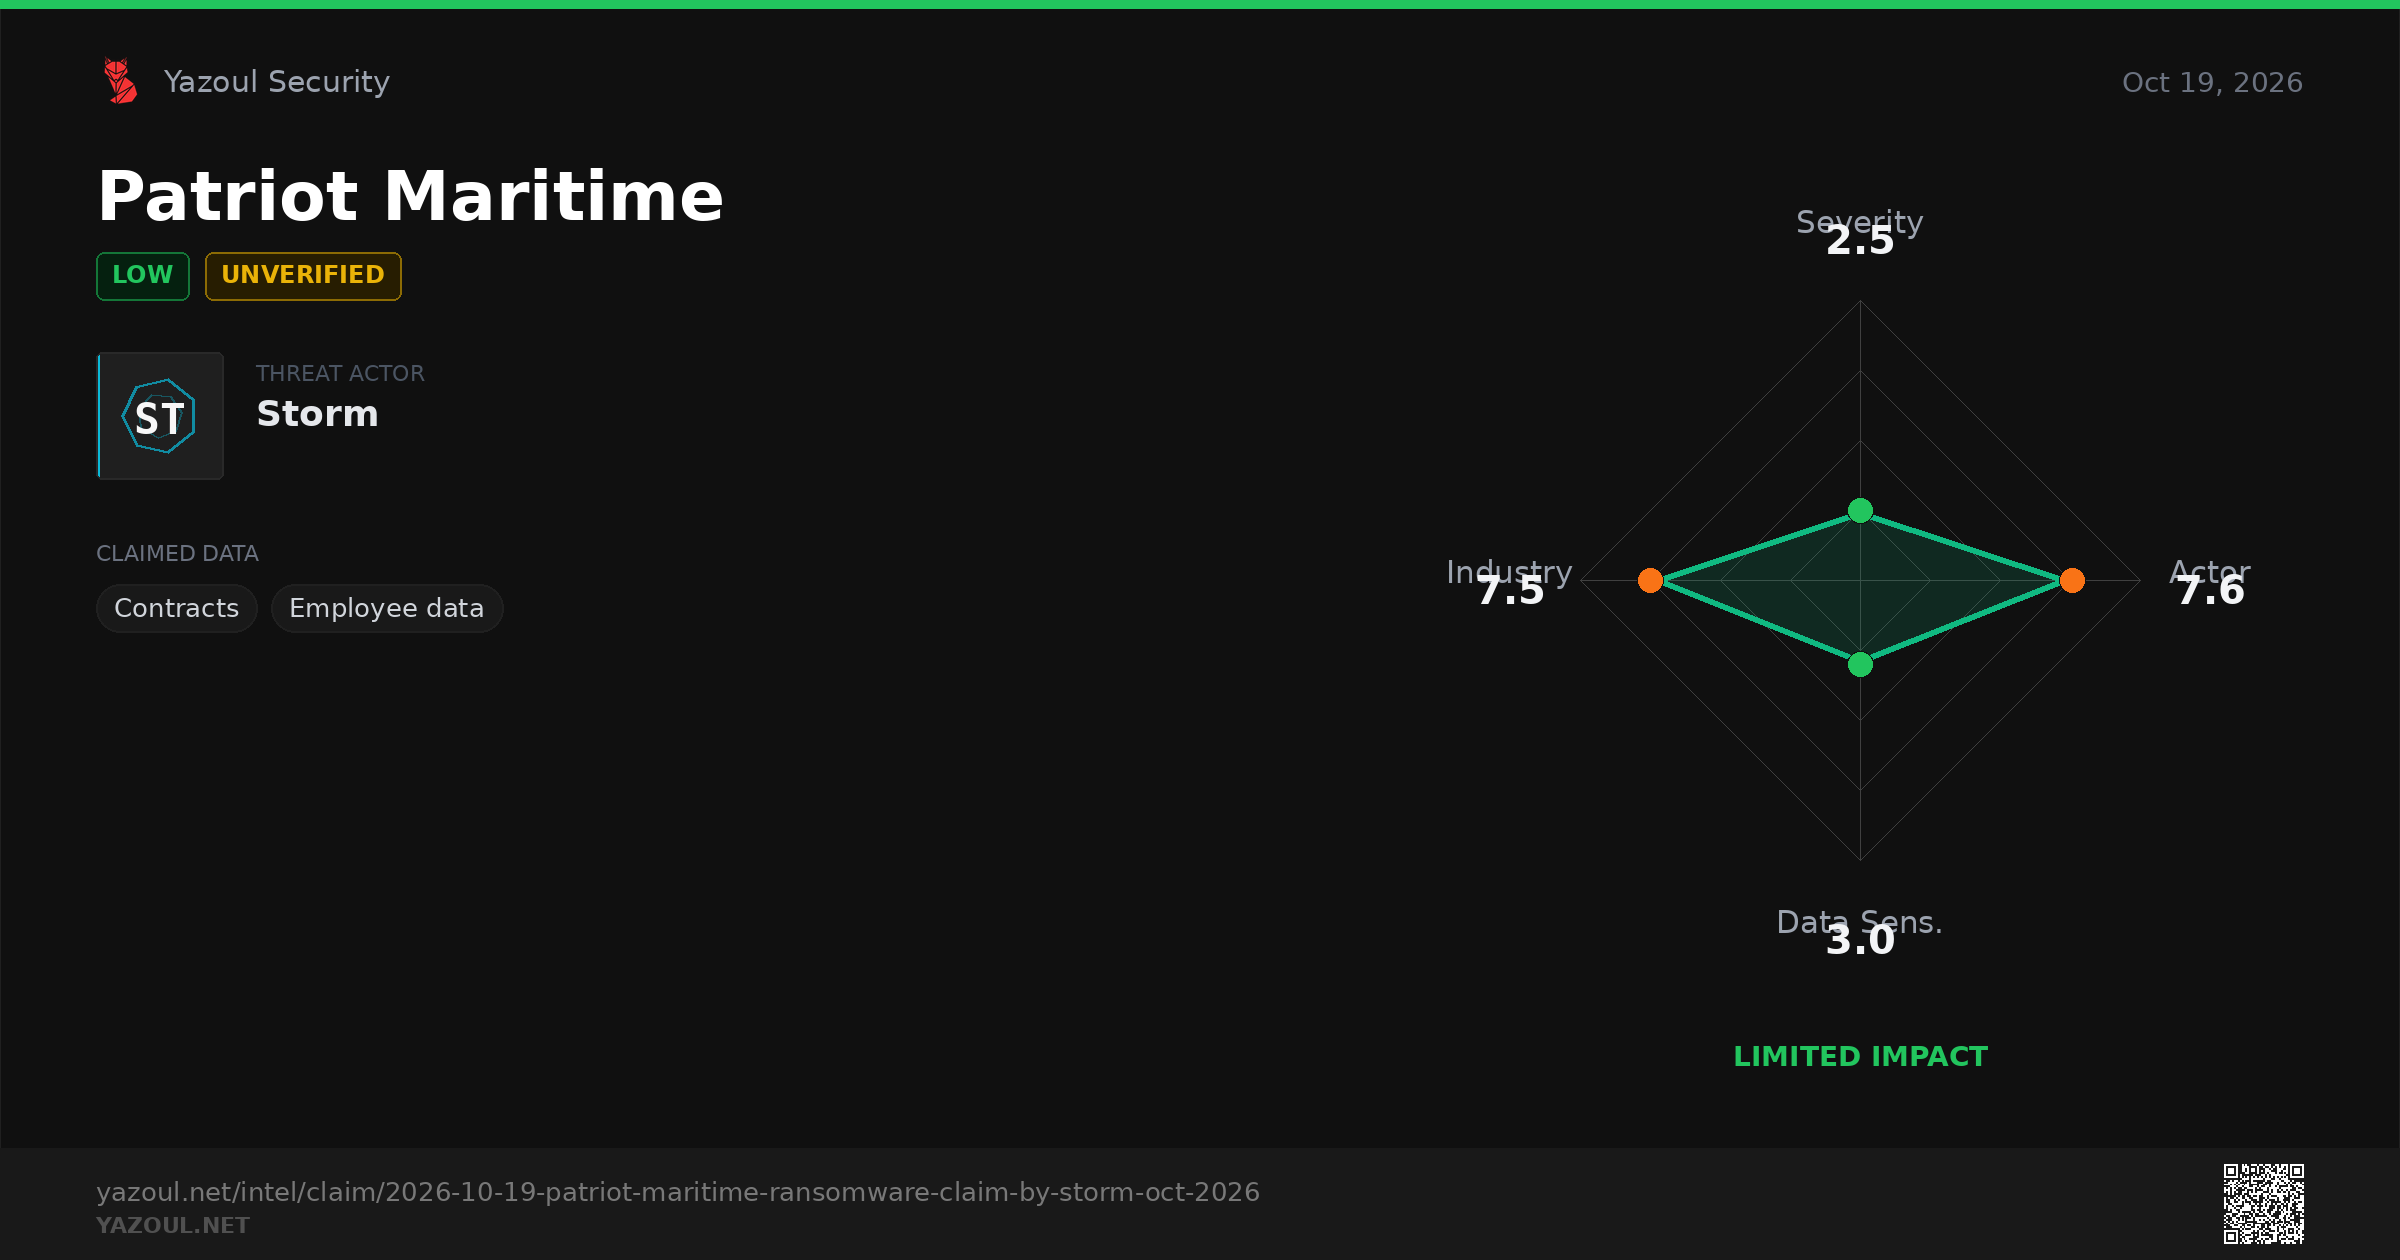
🛡 THREAT INTEL | Patriot Maritime

🟢 Actor "Storm" claims Undisclosed

Allegedly exposed
• Contracts
• Employee data

⚠️ Unverified claim

https://www.yazoul.net/intel/claim/2026-10-19-patriot-maritime-ransomware-claim-by-storm-oct-2026

by Yazoul AI

#DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec

Yazoul SecurityPatriot Maritime Ransomware Claim by Storm (Oct 2026)Storm ransomware group allegedly claims Patriot Maritime as a victim, threatening sensitive maritime contractor data. Read our unverified threat intel analysis now.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

⚠️ New security advisory:

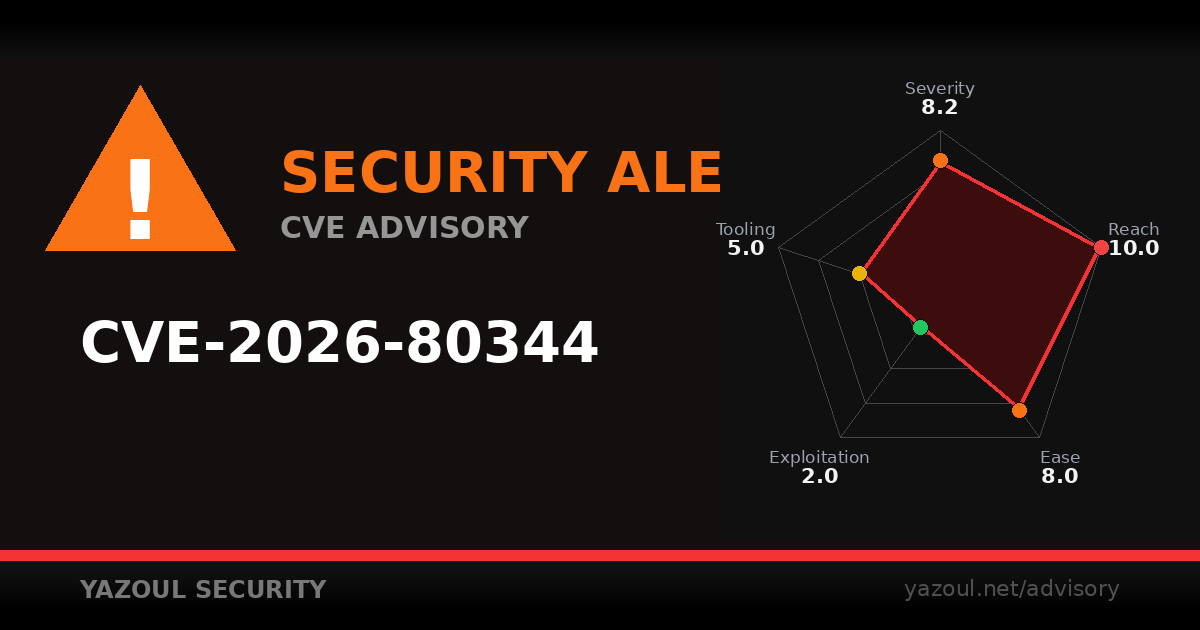
CVE-2026-80344 affects multiple systems.

• Impact: Significant security breach potential
• Risk: Unauthorized access or data exposure
• Mitigation: Apply patches within 24-48 hours

Full breakdown:
https://www.yazoul.net/advisory/cve/cve-2026-80344-apache-camel-as2-ssrf-enables-internal-network-access-poc

by Yazoul AI

#InfoSec #ZeroDay #ThreatIntel

Yazoul SecurityApache Camel AS2 SSRF enables internal network access (CVE-2026-80344) [PoC]CVE-2026-80344: Apache Camel AS2 SSRF (CVSS 8.2) lets remote senders pick the MDN destination host and leak credentials. Update to 4.23.0, 4.18.5, or 4.22.1.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🟠 New security advisory:

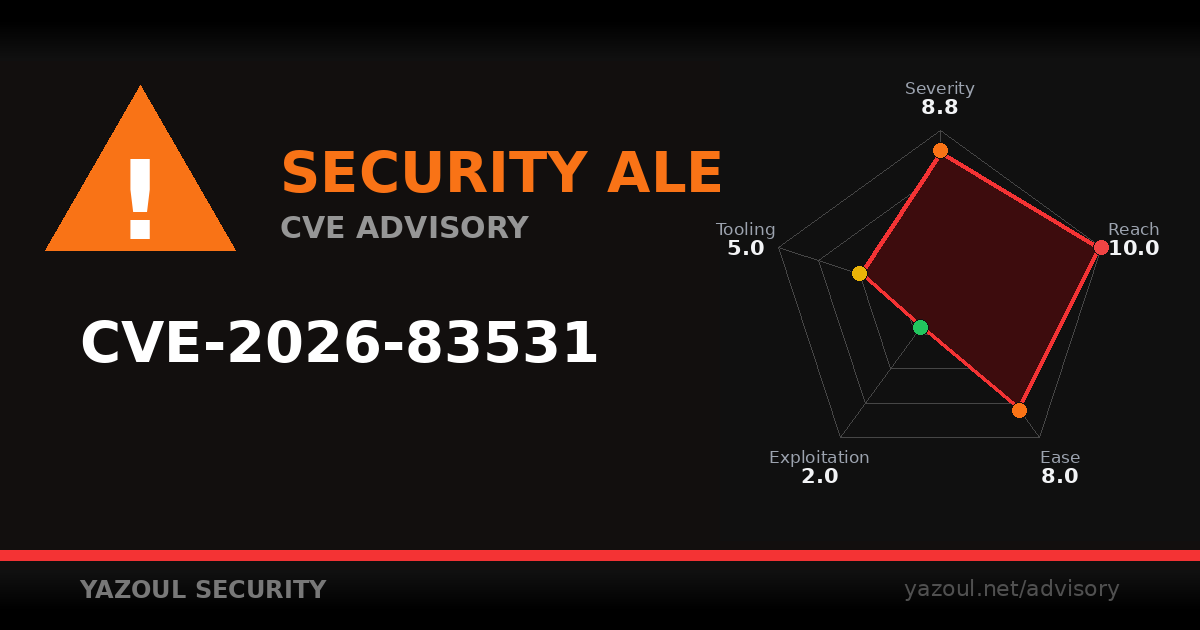
CVE-2026-83531 affects multiple systems.

• Impact: Significant security breach potential
• Risk: Unauthorized access or data exposure
• Mitigation: Apply patches within 24-48 hours

Full breakdown:
https://www.yazoul.net/advisory/cve/cve-2026-83531-apache-camel-code-injection-attacker-controlled-poc

by Yazoul AI

#Cybersecurity #SecurityPatching #HackerNews

Yazoul SecurityApache Camel code injection, attacker-controlled (CVE-2026-83531) [PoC]CVE-2026-83531: Apache Camel 4.4.0-4.18.4 and 4.19.0-4.22.0 lets network senders inject expression language code via dynamic-router-control (CVSS 8.8). Update to 4.23.0, 4.22.1 or 4.18.5.
↩ Reply ♡ 0 · ↻ 0 ↗ Original