X XFediYour place in the Fediverse
XFEDI

#ThreatIntel

ActivityPub

Public posts with this hashtag.

🟠 New security advisory:

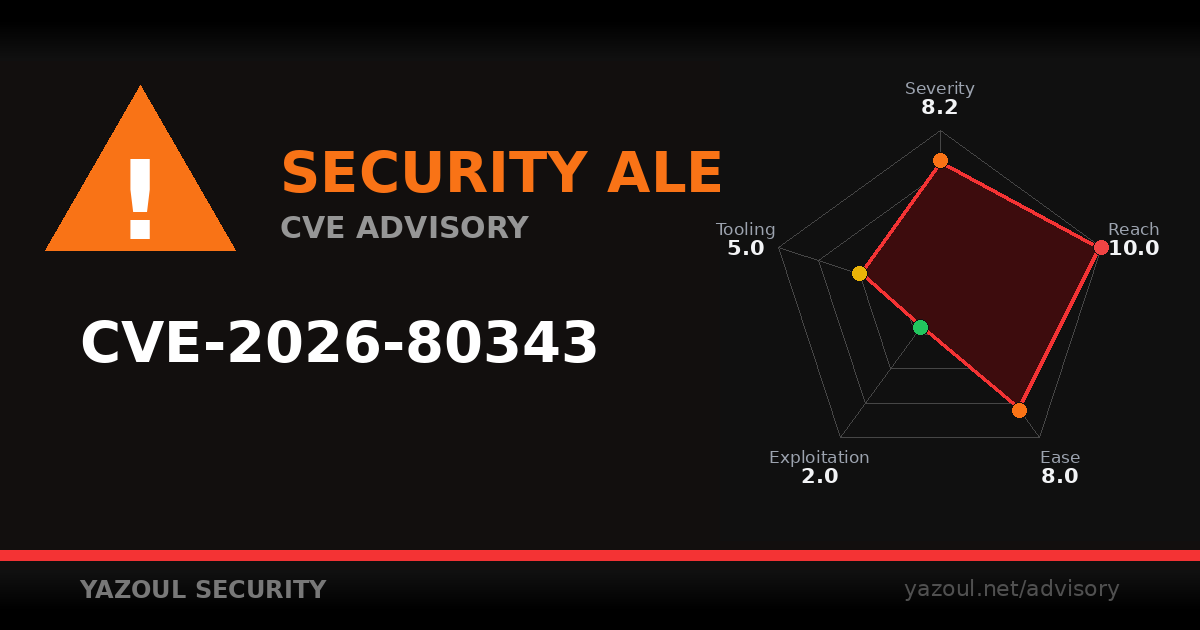
CVE-2026-80343 affects multiple systems.

• Impact: Significant security breach potential
• Risk: Unauthorized access or data exposure
• Mitigation: Apply patches within 24-48 hours

Full breakdown:
https://www.yazoul.net/advisory/cve/cve-2026-80343-camel-netty-http-auth-bypass-exposes-routes-poc

by Yazoul AI
#InfoSec #ZeroDay #ThreatIntel

Yazoul SecurityCamel Netty HTTP auth bypass exposes routes (CVE-2026-80343) [PoC]CVE-2026-80343: Apache Camel 4.0.0-4.22.0 Netty HTTP security constraint bypass lets unauthenticated callers reach protected routes. Upgrade to 4.23.0 or 4.18.5/4.22.1 LTS.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

In Japan, the ransomware name everyone knows is Qilin, thanks to the Asahi attack.

On the leak sites, 2026 belongs to The Gentlemen: 23 Japanese organizations listed this year (ransomware.live), vs 15 for Qilin. Group-IB says it grew out of a Qilin affiliate team, and it hands affiliates compromised FortiGates.

The brand changes; the way in doesn't.

https://japancyberwatch.com/articles/japan-ransomware-groups-2026-the-gentlemen-qilin

#ransomware #infosec #Japan #ThreatIntel

japancyberwatch.comJapan's Ransomware Headlines Say Qilin. The Leak Sites Say The GentlemenQilin became a household name in Japan after the Asahi attack. In 2026, a group that grew out of Qilin's own affiliates, The Gentlemen, has listed more Japanese organizations than any other. What the data shows, and why the name matters less than the way in.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

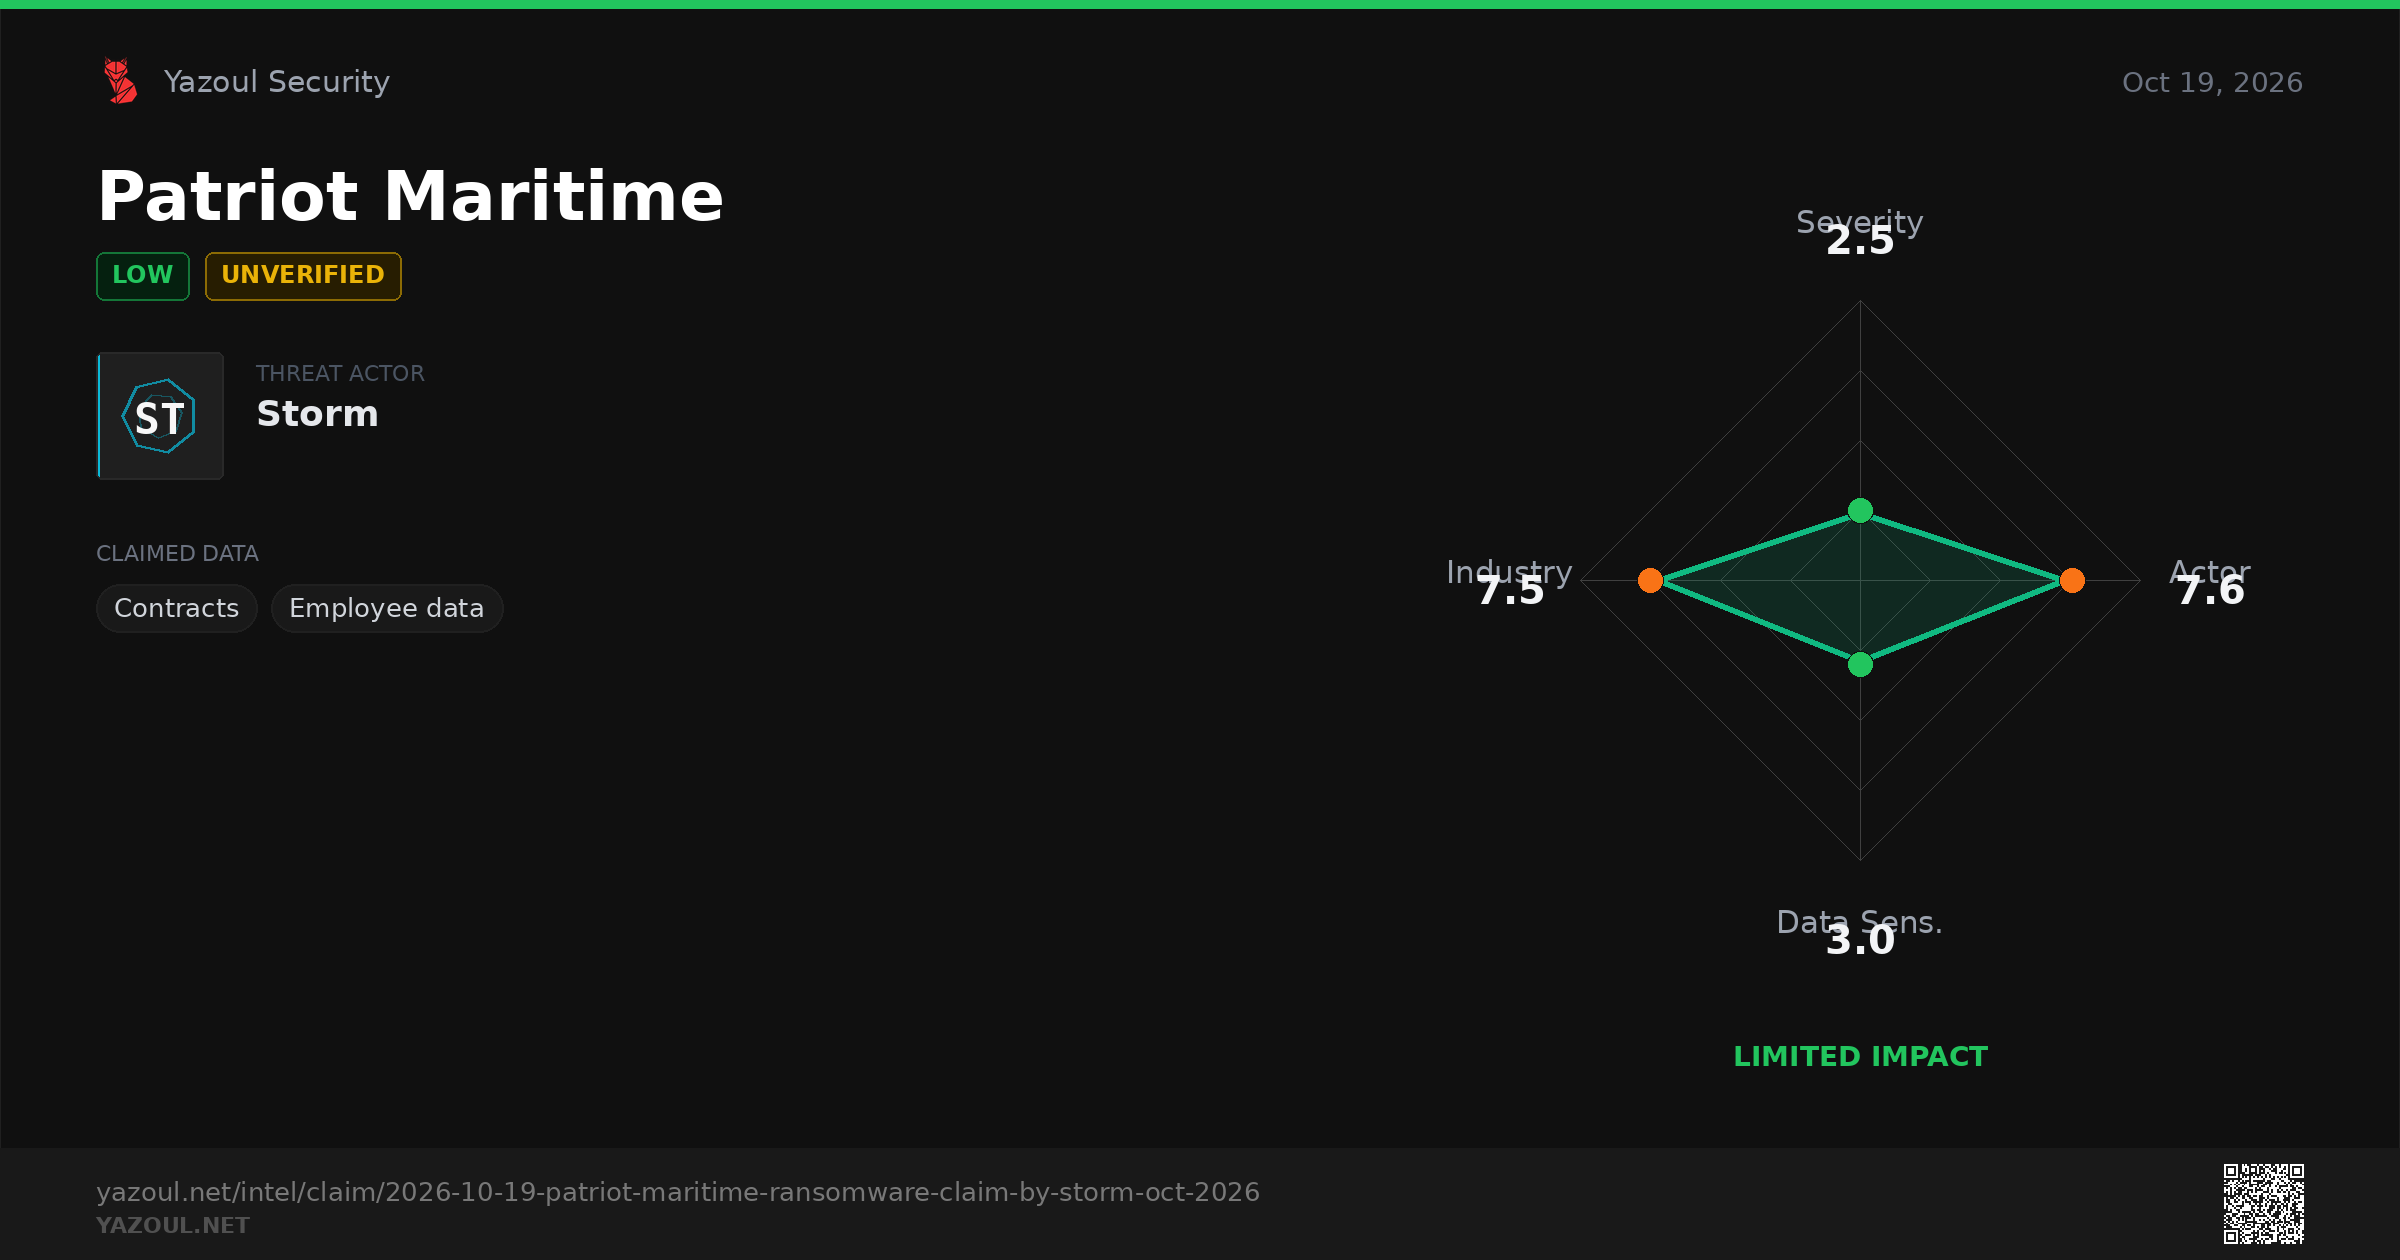
🛡 THREAT INTEL | Patriot Maritime

🟢 Actor "Storm" claims Undisclosed

Allegedly exposed
• Contracts
• Employee data

⚠️ Unverified claim

https://www.yazoul.net/intel/claim/2026-10-19-patriot-maritime-ransomware-claim-by-storm-oct-2026

by Yazoul AI

#DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec

Yazoul SecurityPatriot Maritime Ransomware Claim by Storm (Oct 2026)Storm ransomware group allegedly claims Patriot Maritime as a victim, threatening sensitive maritime contractor data. Read our unverified threat intel analysis now.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

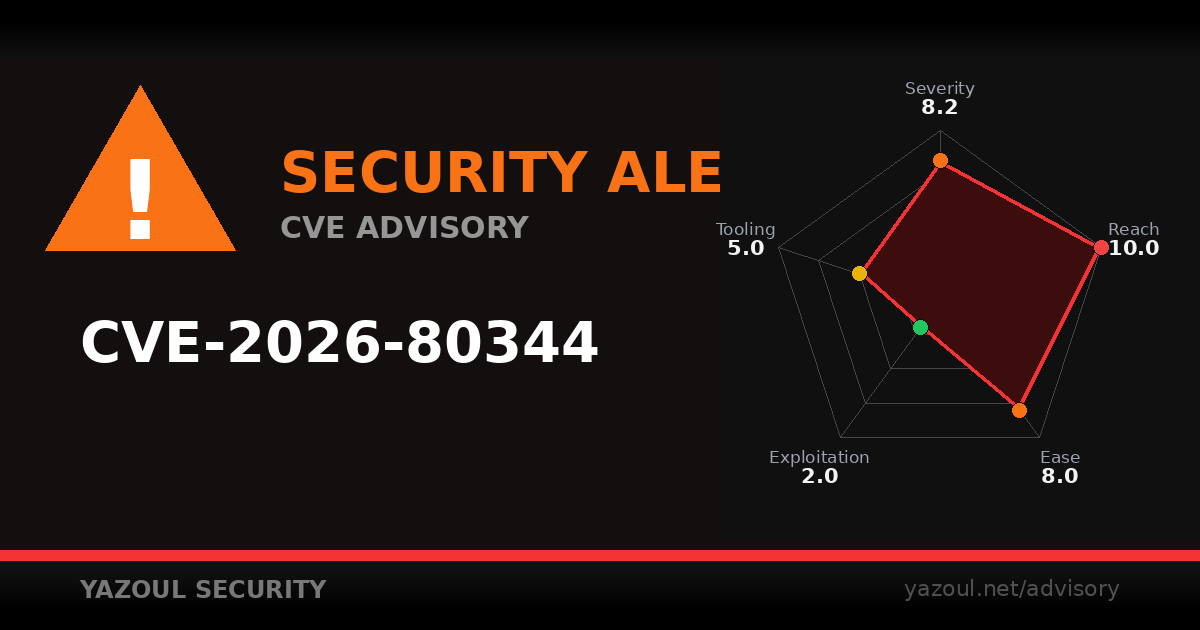
⚠️ New security advisory:

CVE-2026-80344 affects multiple systems.

• Impact: Significant security breach potential
• Risk: Unauthorized access or data exposure
• Mitigation: Apply patches within 24-48 hours

Full breakdown:
https://www.yazoul.net/advisory/cve/cve-2026-80344-apache-camel-as2-ssrf-enables-internal-network-access-poc

by Yazoul AI

#InfoSec #ZeroDay #ThreatIntel

Yazoul SecurityApache Camel AS2 SSRF enables internal network access (CVE-2026-80344) [PoC]CVE-2026-80344: Apache Camel AS2 SSRF (CVSS 8.2) lets remote senders pick the MDN destination host and leak credentials. Update to 4.23.0, 4.18.5, or 4.22.1.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

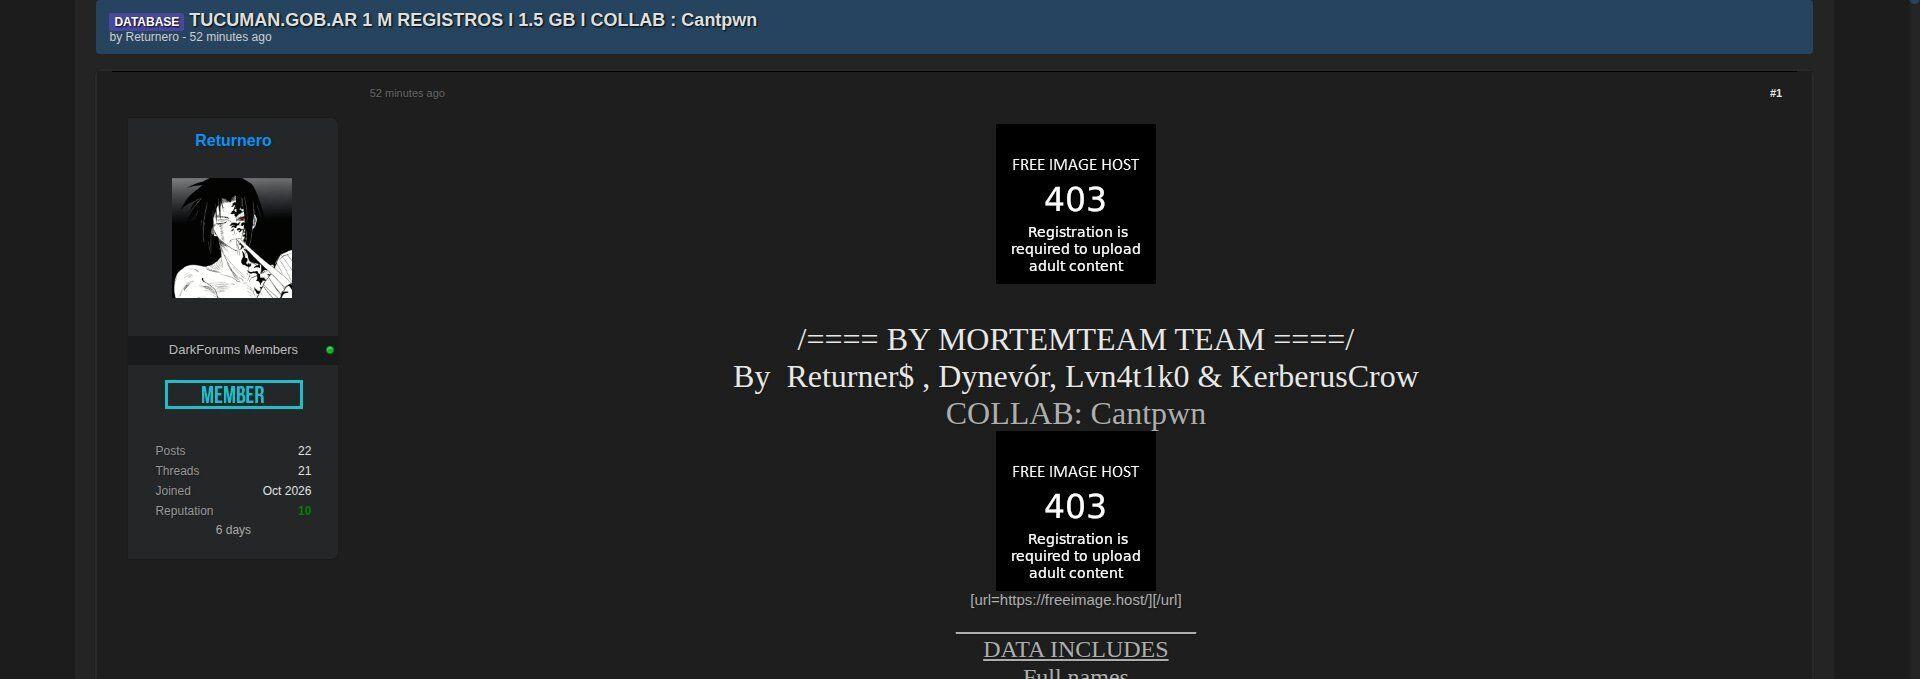
🇦🇷 We tracked a data breach claim by actors identifying as MortemTeam and Cantpwn listing the Government of Tucumán Province in Argentina. They're advertising approximately 1.5 GB containing roughly 1 million records, with samples showing Argentine DNI numbers, names, birth dates, and home addresses of residents. Returnero has been prolific in our tracking, 22 incidents total with 21 logged in the past week. #DataBreach #Government #ThreatIntel

More on this and other incidents → https://go.darkwebsonar.io/returnero-mastodon

Media attachment
darkwebsonar.ioIs Your Business on the Dark Web? Find Out InstantlyDarkWebSonar monitors ransomware, lookalike domains, breach credentials, stealer logs, and executive threat exposure — alerting your team to real threats, in real time. Threat intelligence without the noise.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

For the DoS haters who don't want to patch their Citrix NetScalers: threat actors are chaining CVE-2026-88771 and CVE-2026-88779:

https://www.rapid7.com/blog/post/ra-netscaler-intrusions-chaining-cve-2026-88771-and-cve-2026-88779/

#citrix #netscaler #threatintel #IOC #pitscaler

Rapid7Rapid7In early October 2026, Rapid7 analysts investigated a confirmed compromise of an anonymized Citrix NetScaler ADC appliance. The appliance was running an affected 14.1 build and was exposed to active exploitation targeting NetScaler authentication and SAML deployments. The intrusion achieved root code execution, deployed multiple persistence mechanisms, installed PHP web shells, created outbound c
↩ Reply ♡ 0 · ↻ 0 ↗ Original