X XFediYour place in the Fediverse
XFEDI

#InfoSEC

ActivityPub

Public posts with this hashtag.

CVE-2026-112832 (CRITICAL, CVSS 9.8) in CozyThemes Rootblox <1.0.7 allows unauthenticated remote LFI via improper filename control in PHP. Full system compromise possible. Restrict access & monitor closely. https://radar.offseq.com/threat/cve-2026-112832-improper-control-of-filename-for-includerequire-statement-in-php-program-php-remote-3c455496d4cdf128 #OffSeq #infosec #PHP #LFI

Critical threat: CVE-2026-112832: Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Rem
OffSeq Threat RadarCVE-2026-112832: Improper Control of Filename for… | Threat RadarVulnerability: Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in CozyThemes Rootblox…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Stop staring at your dashboard trying to tell yourself your patching cadence is optimal. It isn't. Most companies treat their vulnerability lists like restaurant menus.

https://theperimetersite.com/report/387

#vulnerability #healthcare #infosec

The Perimeter SiteYour Patching Schedule is a Work of Fiction — The Perimeter SiteStop staring at your dashboard trying to tell yourself your patching cadence is optimal. It isn't. Most companies treat their vulnerability lists like restaurant menus.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

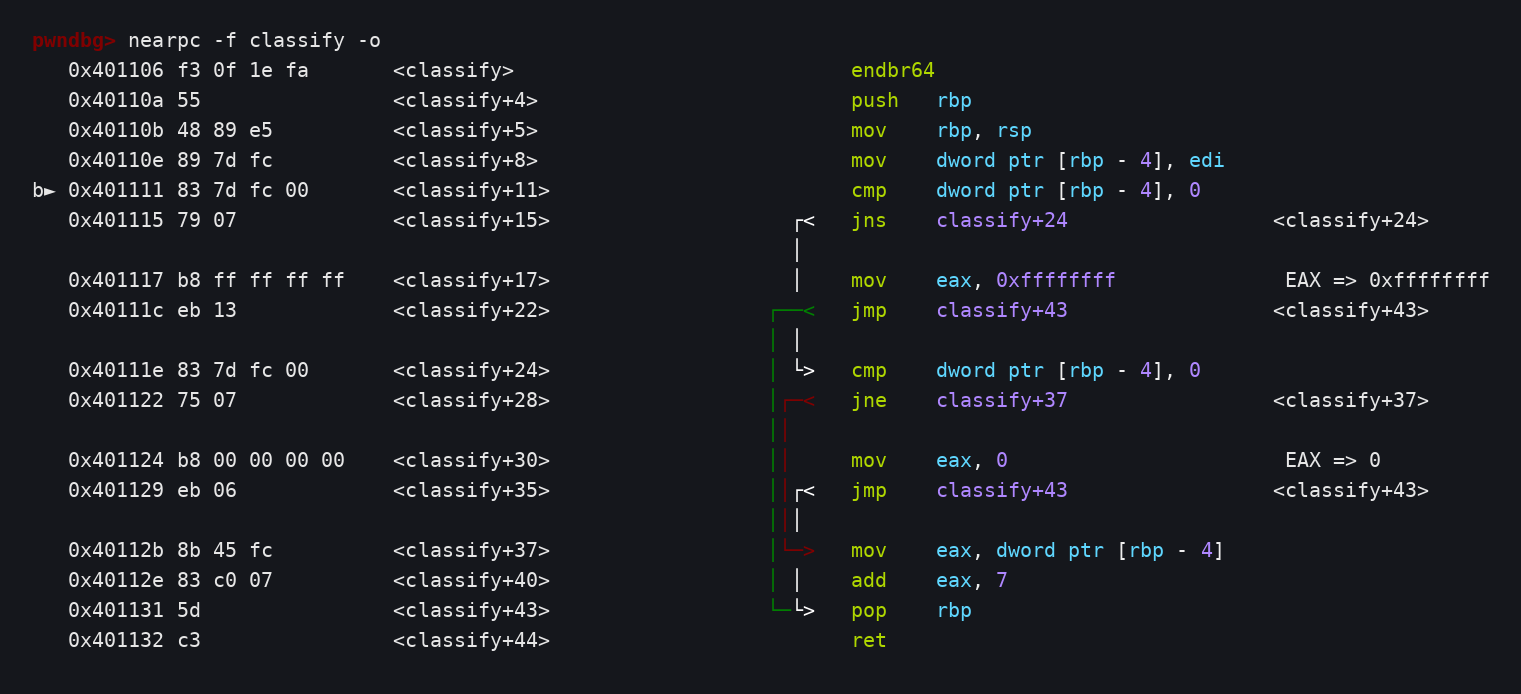
Hi! Welcome a new Pwndbg release: 2026.10.22 !

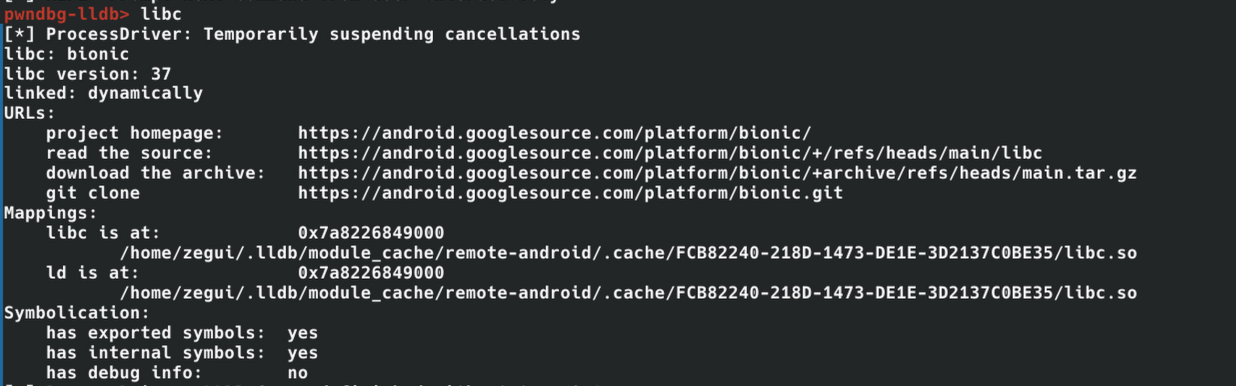
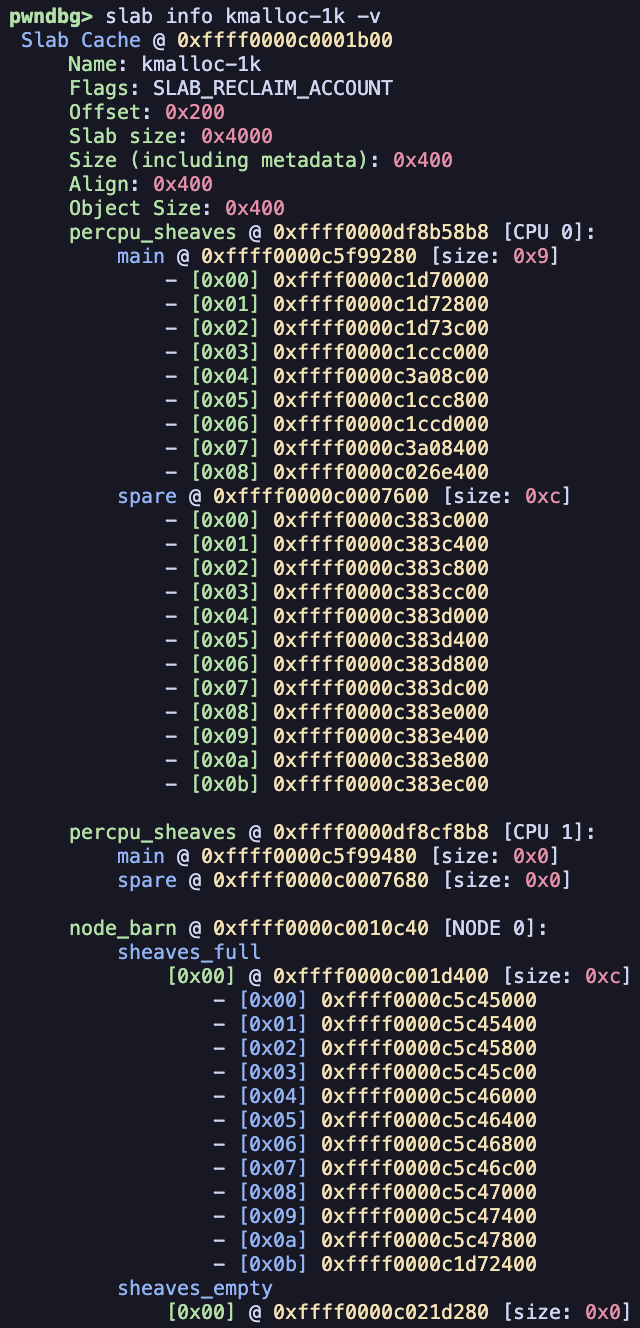
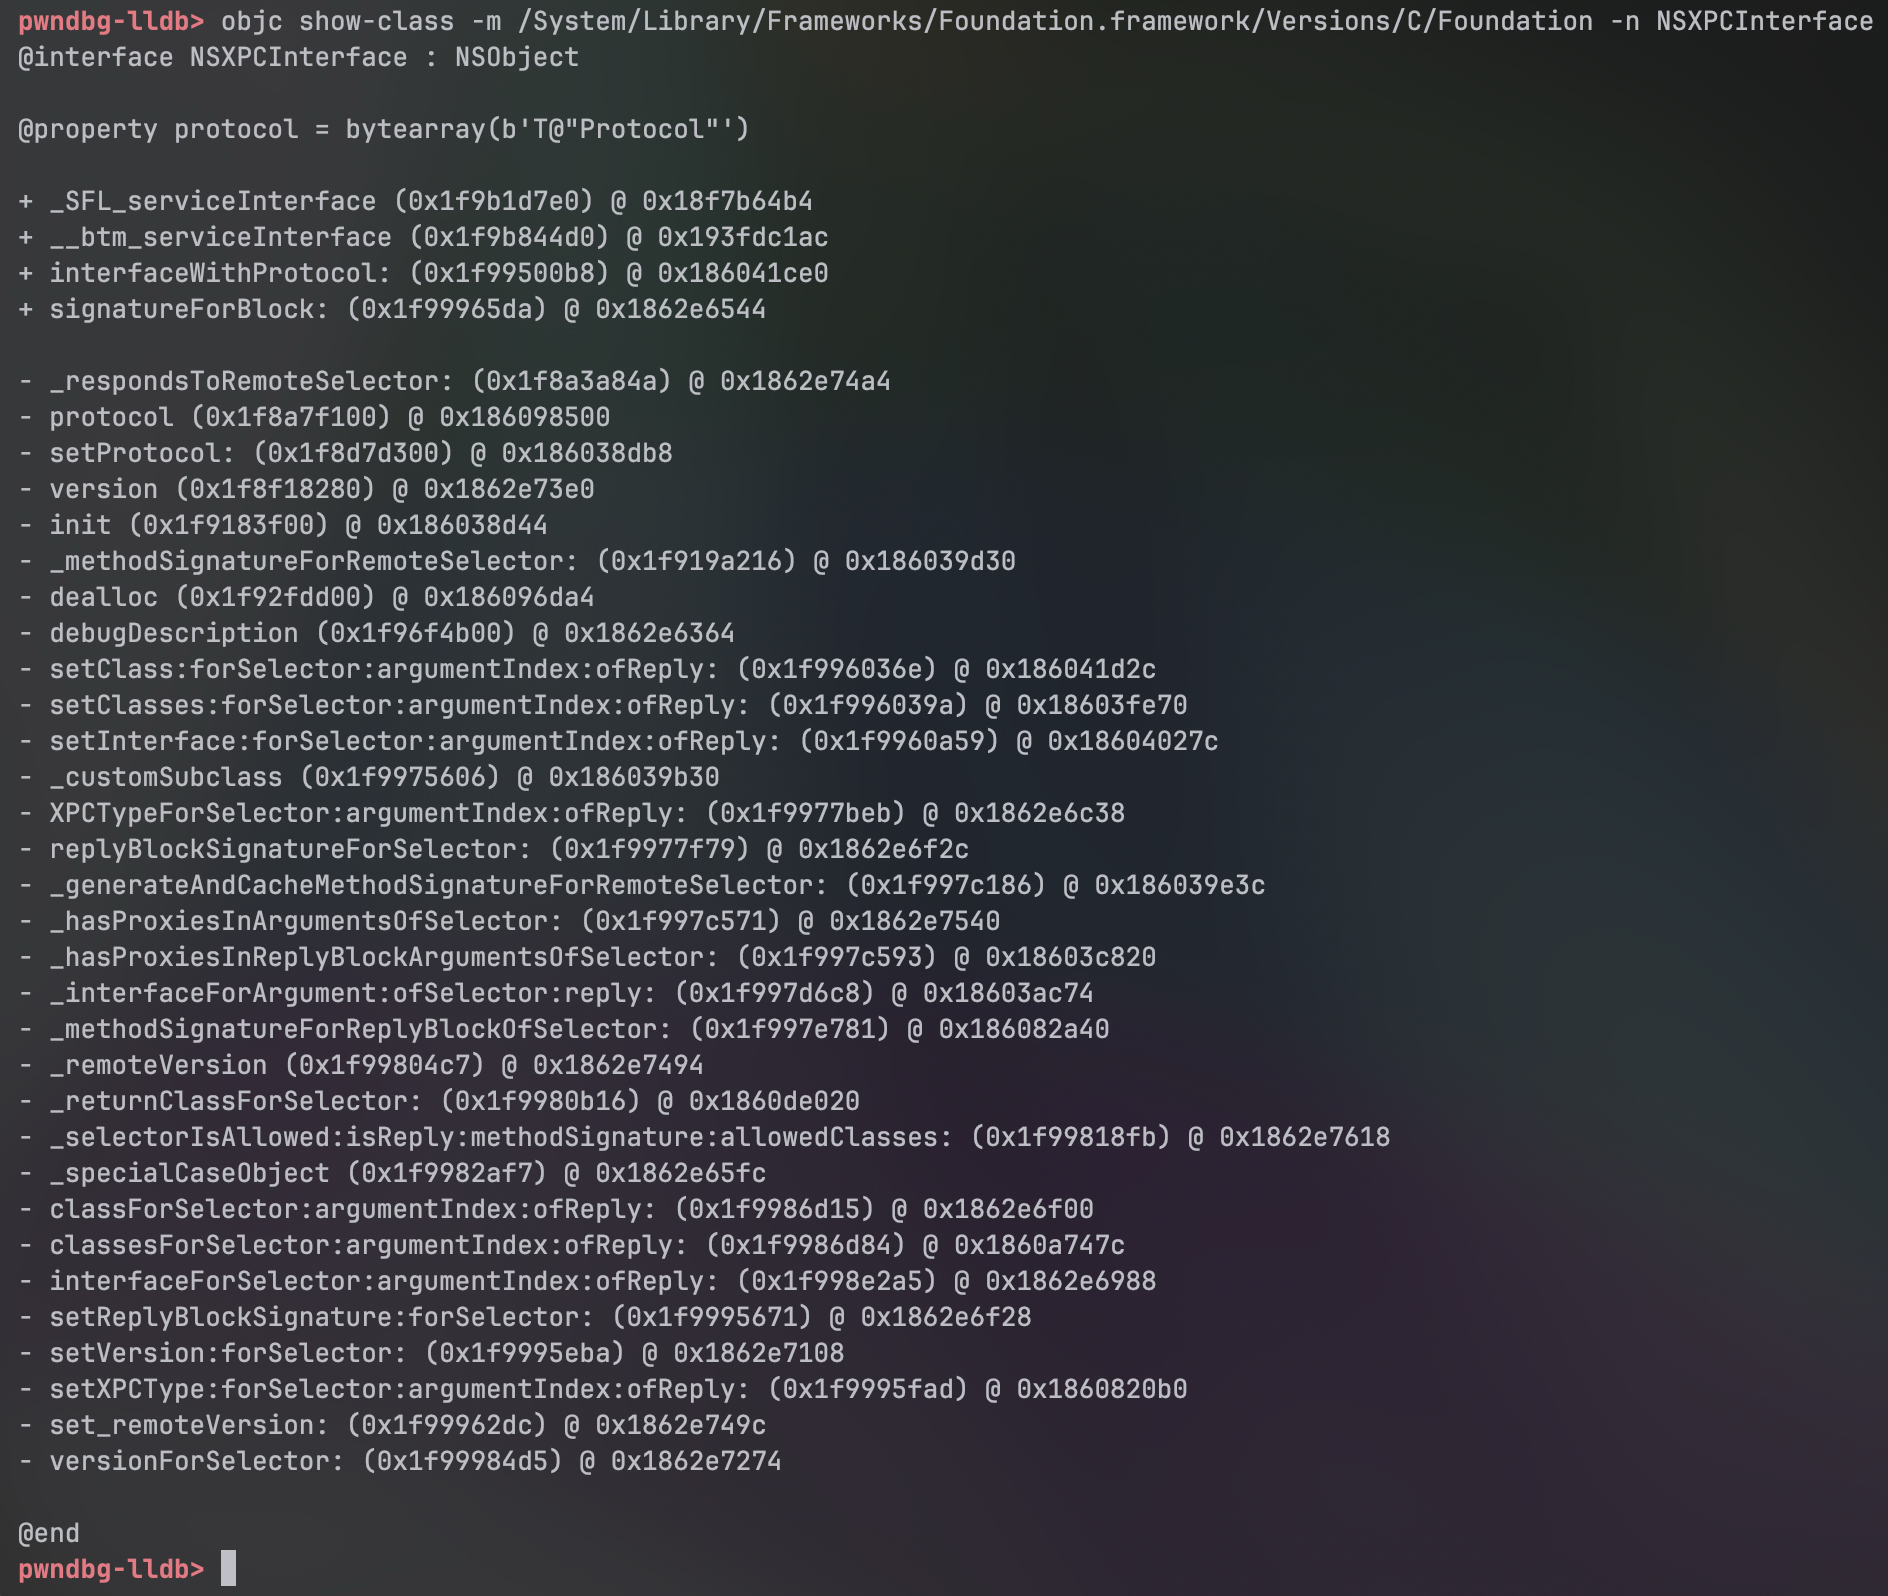
We now support m86k arch, unknown archs, have better C++ support, added tutorials (https://pwndbg.re/dev/tutorials/debugging-cxx/, https://pwndbg.re/dev/tutorials/mangling/, https://pwndbg.re/dev/tutorials/pretty-printing/), `nearpc -o` shows opcode bytes, we have `libcinfo` for Android Bionic libc information, we added Objective-C class inspection commands (`objc show-class` and `objc list-classes`), improved `regs` command (`regs xmm0` and `regs eflags`), have better glibc discovery, added Linux kernel 7+ SLUB sheaf and barn inspection, added `setrlimit` command, improved LLDB support and more (like bug fixes)!

See https://github.com/pwndbg/pwndbg/releases/tag/2026.10.22

Please sponsor us at https://github.com/sponsors/pwndbg !

Thanks to everyone who made it possible!

#pwndbg #gdb #lldb #debugging #security #infosec #pwn #reverseengineering #linux

Media attachmentMedia attachmentMedia attachmentMedia attachment
pwndbg.reDebugging C++ - Documentationpwndbg (/paʊnˈdiˌbʌɡ/) is a GDB plug-in that makes debugging with GDB suck less, with a focus on features needed by low-level software developers, hardware hackers, reverse-engineers and exploit developers.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

We truly can't wait to hear from our fabulous keynote speakers at #osco26! 🤩

⚠️ Stephanie Carstensen will tell us all about "The Day Everything Stops: Preparing for the Cyber Crisis You Hope Never Comes".

🚧 Jahmel Harris will share his insights on "Building a Penetration Testing Lab in 2026".

We believe these topics will inspire great sessions during the open space! Check out the keynote details: https://opensecurityconference.org/conference/keynotes

#osco #Security #CyberSecurity #InfoSec #AppSec #OTSecurity [lisi]

Open Security ConferenceKeynotesWelcome to the Open Security Conference (osco), the people-centred international gathering for everyone interested in cybersecurity. Join us 5-8 November 2026 in Rückersbach, Germany.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Four reports, one week. One conclusion.

Attackers are not breaking AI models. They are walking through the infrastructure.

1,467 MCP servers in one scan. Half the ecosystem repos teach plaintext credential storage. Shadow MCP servers on laptops via Git, Slack, and zip files, never inventoried.

The infrastructure is the attack surface. Screen it.

<https://blog.relayshield.net/attackers-arent-breaking-the-models-theyre-walking-through-the-infrastructure>

#MCP #AISecurity #infosec

blog.relayshield.netAttackers Aren't Breaking the Models. They're Walking Through the Infrastructure. | RelayShieldTrendAI's 1H 2026 State of AI Security report has a finding that should reframe how we think about AI security: attackers are going after the infrastructure around models, not the...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : ARISTA

Our 18th edition, Hackfest Level Up, would not be possible without our sponsors. And this year, we are happy to have Arista, a KIOSK sponsor!

If you want to learn more about this company’s mission, visit their website https://www.arista.com/

PS: YOU CAN STILL BUY YOUR TICKET for October 29–31, 2026 at the Convention Center of Québec ;) More info: https://hackfest.ca/en/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersec

Media attachment
Arista NetworksData-Driven Cloud Networking - AristaArista Networks was founded to pioneer and deliver software-driven cloud networking solutions for large data center storage and computing environments. Arista’s award-winning platforms, ranging in Ethernet speeds from 10 to 100 gigabits per second,
↩ Reply ♡ 0 · ↻ 0 ↗ Original

LiteLLM Supply Chain Attack and Critical Vulnerabilities Expose AI Infrastructure

LiteLLM version 1.107.0 was compromised in a supply chain attack that distributed a credential stealer and a persistent backdoor via stolen GitHub OAuth tokens. The incident exposes cloud credentials, AI provider keys, and sensitive developer secrets across millions of installations.

**If you use LiteLLM (or suspect you use it), this is urgent. Check for installed LiteLLM 1.107.0 or pulled its Docker images (even as "latest") on October 21. If you find any trace of LiteLLM 1.107.0 treat those machines as fully hacked: don't run pip, manually delete cook.pth, cook.py and sitecustomize.py from site-packages, kill the hidden Python process, and rebuild from scratch pinned to version 1.106.2. Then assume all your secrets were stolen and change them, including cloud keys, SSH keys, API keys, tokens and saved passwords, and block litellm.dev on your network.**
#cybersecurity #infosec #attack #activeexploit
https://beyondmachines.net/event_details/litellm-supply-chain-attack-and-critical-vulnerabilities-expose-ai-infrastructure-p-t-8-f-2/gD2P6Ple2L

BeyondMachinesLiteLLM Supply Chain Attack and Critical Vulnerabilities Expose AI InfrastructureLiteLLM version 1.107.0 was compromised in a supply chain attack that distributed a credential stealer and a persistent backdoor via stolen GitHub OAuth tokens. The incident exposes cloud credentials, AI provider keys, and sensitive developer secrets across millions of installations.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🆕 ScanMalware is now listed in ChatGPT's plugin directory, so ChatGPT can submit scans, search the archive and pivot from one phishing page to the rest of its campaign through our MCP server

https://scanmalware.com/changelog?mtm_campaign=social-changelog&mtm_source=mastodon&mtm_medium=social&mtm_kwd=202610220810#2026-10-22T08:10:00Z-ac63c2e0

#ScanMalware #InfoSec #ThreatIntel

ScanMalware.comChangelog - ScanMalware.comRecent changes and updates to ScanMalware.com - URL and website security scanner.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Security Advisory: CVE-2025-71438 - Out-of-Bounds Read in GPAC/MP4Box

Processing a crafted AC-4 stream with an invalid `frame_rate_index` triggers an out-of-bounds read in `gf_odf_ac4_cfg_dsi_v1`, causing MP4Box to crash.

Summary:
The `gf_odf_ac4_cfg_dsi_v1` function in `odf/descriptors.c` uses a stream-supplied `frame_rate_index` to index into fixed-size lookup tables (`AC4_SAMPLE_DELTA_TABLE_48`, `AC4_MEDIA_TIMESCALE_48`). The function does not validate that the index is within bounds before performing the table lookup. A crafted AC-4 file carrying an out-of-range index (e.g., 15) causes an out-of-bounds read, ultimately resulting in a NULL dereference and process crash.

CWE:
CWE-125 - Out-of-bounds Read

Affected Component:
```
odf/descriptors.c:2179
Function: gf_odf_ac4_cfg_dsi_v1()
```

Affected Product:
MP4Box (GPAC Multimedia Open Source Project)

Affected Version:
2.5-DEV-rev1617-g856674b22-master; commit `856674b226d6cbe28a941ad223be38194cbf7d37`. Any codebase equivalent to this commit that has not applied the fix commit is affected.

Attack Conditions:
An attacker supplies a specially crafted AC-4 stream file containing an invalid `frame_rate_index` value. Local access is required; the victim must invoke `MP4Box -dash 100 <crafted_file>` or any equivalent DASH segmentation command that triggers the AC-4 configuration descriptor parsing path.

Impact:
The out-of-bounds read leads to an immediate process crash (SEGV READ at address 0x000000000000), resulting in Denial of Service. No evidence of arbitrary code execution was observed.

Fix / mitigation status:
The issue was fixed in GPAC commit:
```
13eb5b76560aaf7813b865a2ad433258478e2695
```
Users should update to a GPAC build containing this commit or later.

References:

- Issue: https://github.com/gpac/gpac/issues/3303
- PoC: https://github.com/sigdevel/pocs/blob/main/res/gpac/MP4Box/50/50_gf_odf_ac4_cfg_dsi_v1_odf_descriptors_c_2179
- Fix: https://github.com/gpac/gpac/commit/13eb5b76560aaf7813b865a2ad433258478e2695

Credit
Alexander A. Shvedov (@sigdevel)

#fuzzing #infosec #security #afl++ #revers #cybersecurity #bugbounty #vulnerability #opensource #linux #cve #advisory #gpac

GitHub[security] odf/descriptors.c:2179 out-of-bounds read in gf_odf_ac4_cfg_dsi_v1 · Issue #3303 · gpac/gpacodf/descriptors.c:2179 out-of-bounds read in gf_odf_ac4_cfg_dsi_v1 Description: When processing ac-4 streams with invalid frame rate indices, the code fails to validate "frame_rate_index" before ac...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Bezpieczeństwo i prywatność to nie to samo, choć często traktuje się je zamiennie.

W najnowszym wpisie wyjaśniam różnicę między bezpieczeństwem a prywatnością. Pokazuję też, dlaczego to bezpieczeństwo jest fundamentem, na którym dopiero można budować prywatność. Bez niego każda obrona staje się iluzją.

Zapraszam do lektury 👇
https://eteryu.space/blog/2026/10/22/bezpiecze%C5%84stwo-fundamentem-prywatno%C5%9Bci-dlaczego-kolejno%C5%9B%C4%87-ma-znaczenie/

#Bezpieczeństwo #Prywatność #Cyberbezpieczeństwo #Security #Privacy #InfoSec
eteryu.spaceBezpieczeństwo fundamentem prywatności. Dlaczego kolejność ma znaczenie - Eteryu.spacePrywatność bez bezpieczeństwa to iluzja. Wyjaśniam, dlaczego bezpieczeństwo jest warunkiem wstępnym prywatności i jak przełożyć to na codzienne decyzje.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

STM and SAQ Shut Down Websites Following Critical PHP2Shell Disclosure

The Société de transport de Montréal and the Société des alcools du Québec temporarily took their websites offline on October 21, 2026, as a precaution following the disclosure of two critical PHP vulnerabilities known as PHP2Shell. The flaws can allow unauthenticated remote code execution on affected servers, prompting precautionary shutdowns and urgent patching.

****
#cybersecurity #infosec #incident #databreach
https://beyondmachines.net/event_details/stm-and-saq-shut-down-websites-following-critical-php2shell-disclosure-s-g-p-b-q/gD2P6Ple2L

BeyondMachinesSTM and SAQ Shut Down Websites Following Critical PHP2Shell DisclosureThe Société de transport de Montréal and the Société des alcools du Québec temporarily took their websites offline on October 21, 2026, as a precaution following the disclosure of two critical PHP vulnerabilities known as PHP2Shell. The flaws can allow unauthenticated remote code execution on affected servers, prompting precautionary shutdowns and urgent patching.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🎸 Don’t Stop Me Now: MIRE/C³ release 2026.11 is out early.

It seems the world (or at least the attackers and scanners on the Internet) has been searching for AI-proxy config files: the LiteLLM-style proxies people put in front of their AI models, often with the cloud keys sitting right there in the config.

So The MIRE now hands those out too. The AWS key inside is a canary.

4 keys were used in the first 12 hours. The fastest was in use 14 seconds after it was taken. Each key was tried from between 53 and 93 different addresses, one call each: a residential proxy pool doing its job.

The calls tell the story: “who am I?”, then how much email the account may send, whether it can send texts, and which AI models it can run. Spam and free AI, on someone else’s bill.

Only “who am I?” ever worked. Of course!

Also new in 2026.11:
🪤 More bait where attackers actually look: Terraform, Kubernetes, shell history, build scripts, .bak copies
🏢 Every site tells one consistent story
🔐 A login for every SaaS dashboard that was never there
🔎 About 9'400 attacks hidden in query strings since July, now caught

30 different canaries used since 9 October. The full field report is to follow.

https://mire.cc/dont-stop-me-now/

#cybersecurity #AI #MIREC3 #honeypot #infosec #ThreatIntel #LLMjacking #AWS #DeceptionTechnology

MIRE/C³Don’t Stop Me Now · MIRE/C³Analysis of the gaps from researching the logs showed many attackers searching for AI-proxy config files.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Possible Phishing 🎣
on: ⚠️hxxps[:]//www[.]e-serviceparts[.]info/landingpages/daec0dfa-de7a-4f73-9b8e-44fde686ce12/tmjj55gh6lnzatdk9bgovnathsgesa77mnlhuwq-dqq
🧬 Analysis at: https://urldna.io/scan/6ad9b4a53b775000061783af
#cybersecurity #phishing #infosec #urldna #scam #infosec

Media attachment
urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PHP2Shell is now public and already under attack. Two flaws in PHP core, CVE-2026-109618 and 109619, both scored 9.2, give pre-authentication remote code execution on every PHP 7.x and 8.x release, through any reachable endpoint. Patches came a day early after the identifiers and a proof of concept leaked.

Amazon's honeypots saw an exploit attempt on 17 October, four days before disclosure, from an anonymised address. Broader attacks began within hours of release, and CrowdStrike notes they leave almost no log trace. The NCSC and CISA say patch at once or consider taking the system offline.

https://thehackernews.com/2026/10/someone-tried-to-exploit-php2shell-4.html

#CyberSecurity #InfoSec #PHP

The Hacker NewsSomeone Tried to Exploit PHP2Shell 4 Days Before the Vulnerabilities Were Publicly DisclosedAmazon detected a PHP2Shell exploit attempt on October 17, before disclosure, followed by further attempts after patches were released.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

This dumb password rule is from Slovenska sporitelna.

Slovenska sporitelna is the biggest bank in Slovakia. Despite pretty new version of the internet banking (rolled out in 2018), their password policy restricts password to be 16 characters long at most and prohibits any special characters.

https://dumbpasswordrules.com/sites/slovenska-sporitelna/

#password #passwords #infosec #cybersecurity #dumbpasswordrules

dumbpasswordrules.comSlovenska sporitelna - Dumb Password RulesSlovenska sporitelna is the biggest bank in Slovakia. Despite pretty new version of the internet banking (rolled out in 2018), their password policy restricts password to be 16 characters long at most and prohibits any special characters.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

NT OneAPP (≤1.5.22) by NewType Infortech has a CRITICAL hard-coded credentials flaw (CVE-2026-114219, CVSS 9.1). Attackers can decrypt login data & access user creds. No patch yet — restrict access & monitor closely. https://radar.offseq.com/threat/cve-2026-114219-cwe-798-use-of-hard-coded-credentials-in-newtype-infortech-nt-oneapp-d8766d50ef7b2f82 #OffSeq #CVE #infosec #vulnerability

Critical threat: CVE-2026-114219: CWE-798 Use of Hard-coded Credentials in NewType Infortech NT OneAPP
OffSeq Threat RadarCVE-2026-114219: CWE-798 Use of Hard-coded Credentials in… | Threat RadarNT OneAPP by NewType Infortech contains a hard-coded credentials vulnerability (CWE-798) that allows unauthenticated remote attackers to obtain a hard-coded…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

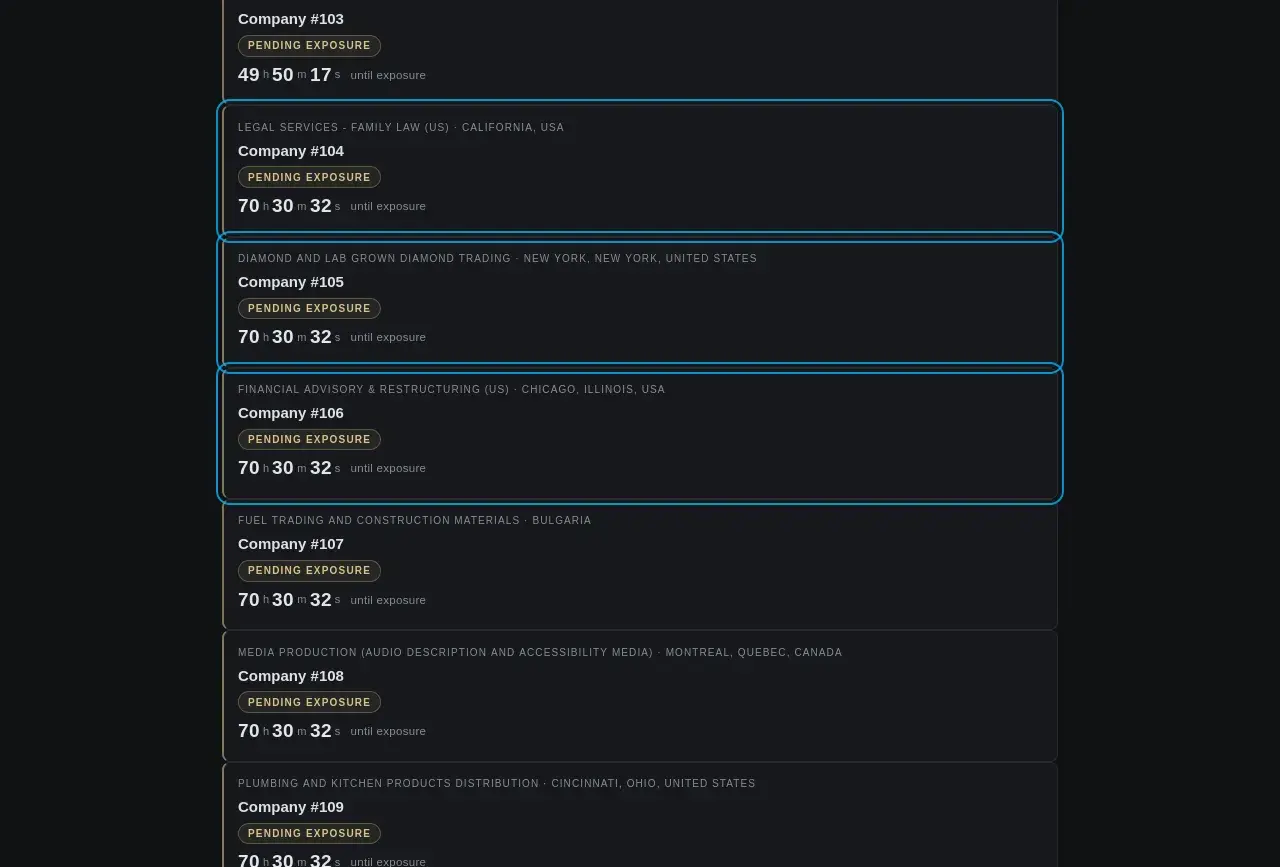
🚨New ransom group blog posts!🚨

Group name: N0n
Post title: Performance Ford Inc
Location: 🇺🇸 US
Sector: Automotive
Info: https://cti.fyi/#disclosure/N0n/Performance%20Ford%20Inc

Group name: N0n
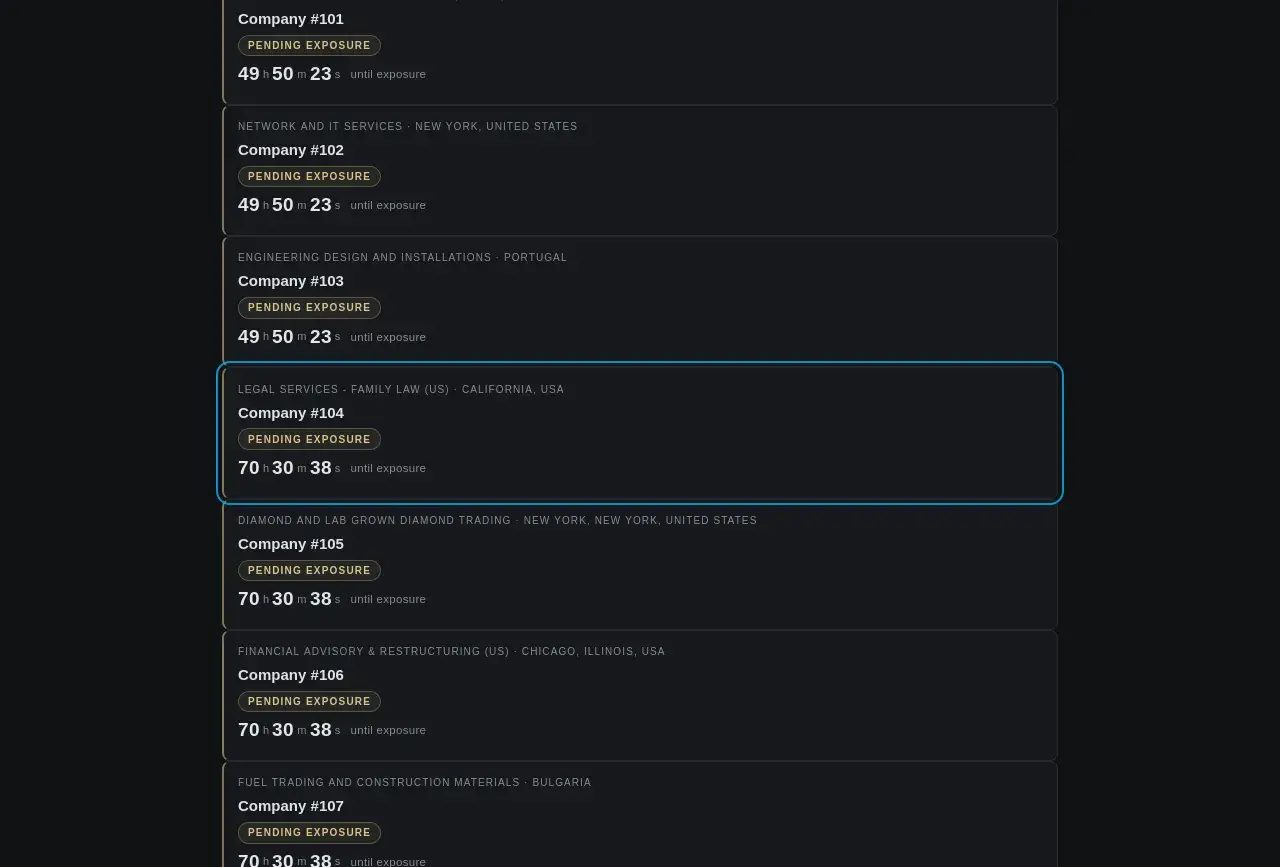
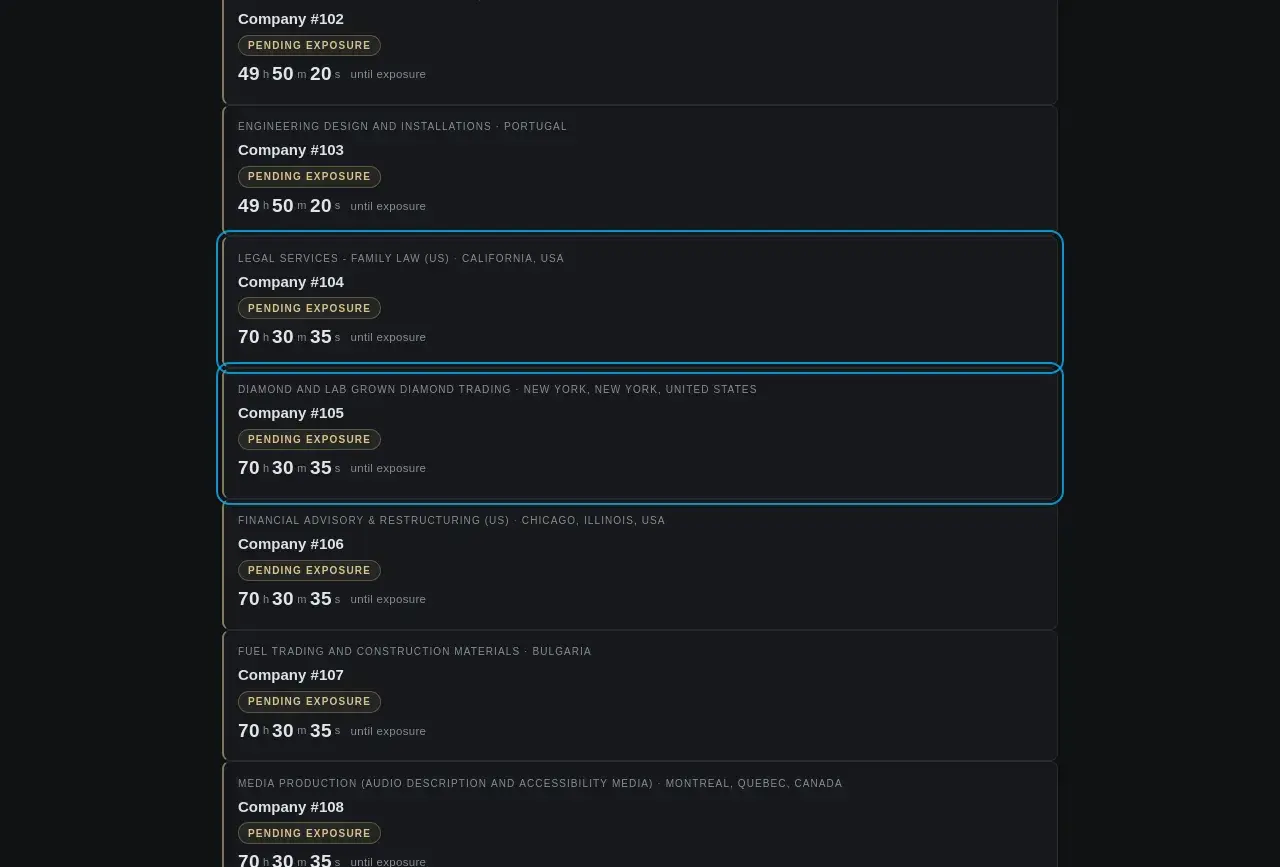
Post title: Company #104
Info: https://cti.fyi/#disclosure/N0n/Company%20%23104

Group name: N0n
Post title: Company #105
Info: https://cti.fyi/#disclosure/N0n/Company%20%23105

Group name: N0n
Post title: Company #106
Info: https://cti.fyi/#disclosure/N0n/Company%20%23106

Group name: N0n
Post title: Company #107
Info: https://cti.fyi/#disclosure/N0n/Company%20%23107

Group name: N0n
Post title: Company #108
Info: https://cti.fyi/#disclosure/N0n/Company%20%23108

Group name: N0n
Post title: Company #109
Info: https://cti.fyi/#disclosure/N0n/Company%20%23109

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachmentMedia attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

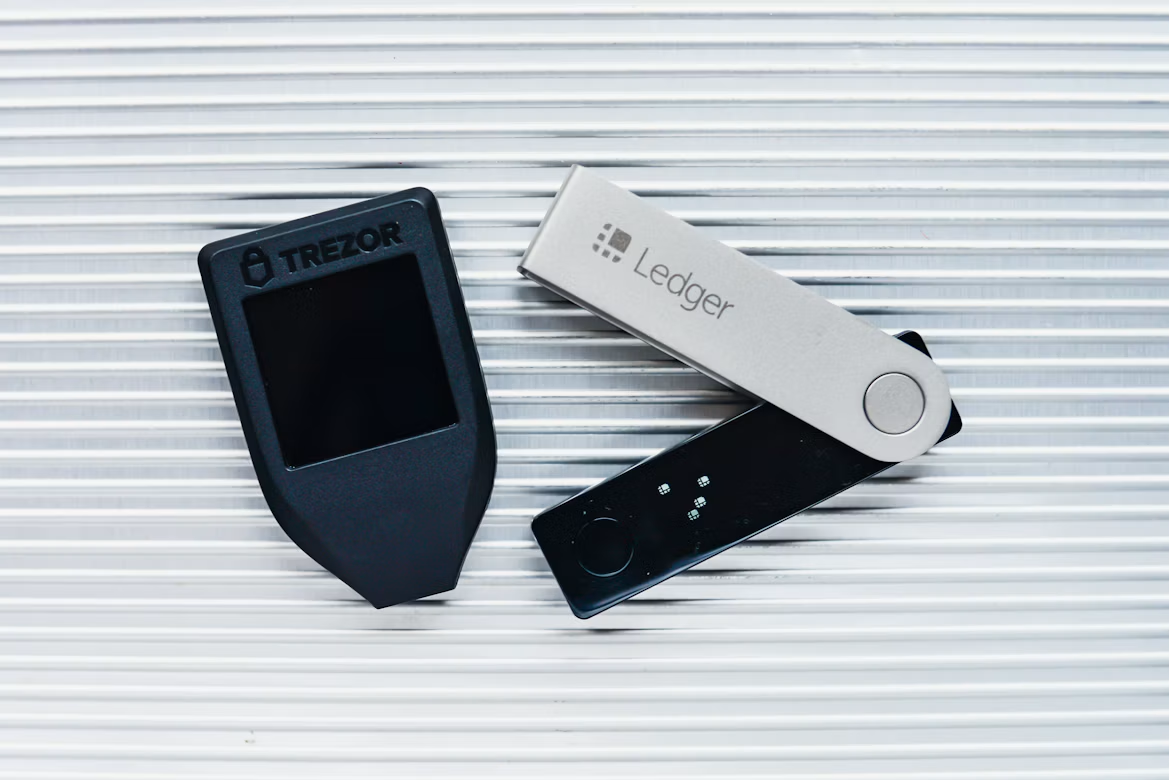
Starting 9 October 2026, hundreds of Ledger users who bought through the reseller CryptoBilis lost an estimated $86 million to over $100 million.

Be careful. Details in the article:
https://hackers-arise.com/cryptocurrency-security-analysis-of-hardware-crypto-wallets/

#tech #cryptocurrency #cybersecurity #infosec

Media attachment
Hackers Arise - EXPERT CYBERSECURITY TRAINING FOR ETHICAL HACKERSCryptocurrency: Security Analysis of Hardware Crypto Wallets - Hackers AriseHardware wallet implants can expose crypto recovery phrases. We showed how to protect your crypto from supply-chain attacks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original