ASN: AS51056
Location: Chisinau, MD
Added: 2026-10-21T07:12
Sensitive media · Show
Public posts with this hashtag.
ASN: AS51056
Location: Chisinau, MD
Added: 2026-10-21T07:12
PHP2Shell is now public and already under attack. Two flaws in PHP core, CVE-2026-109618 and 109619, both scored 9.2, give pre-authentication remote code execution on every PHP 7.x and 8.x release, through any reachable endpoint. Patches came a day early after the identifiers and a proof of concept leaked.
Amazon's honeypots saw an exploit attempt on 17 October, four days before disclosure, from an anonymised address. Broader attacks began within hours of release, and CrowdStrike notes they leave almost no log trace. The NCSC and CISA say patch at once or consider taking the system offline.
https://thehackernews.com/2026/10/someone-tried-to-exploit-php2shell-4.html
 The Hacker NewsSomeone Tried to Exploit PHP2Shell 4 Days Before the Vulnerabilities Were Publicly DisclosedAmazon detected a PHP2Shell exploit attempt on October 17, before disclosure, followed by further attempts after patches were released.
This dumb password rule is from Slovenska sporitelna.
Slovenska sporitelna is the biggest bank in Slovakia. Despite pretty new version of the internet banking (rolled out in 2018), their password policy restricts password to be 16 characters long at most and prohibits any special characters.
https://dumbpasswordrules.com/sites/slovenska-sporitelna/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
 dumbpasswordrules.comSlovenska sporitelna - Dumb Password RulesSlovenska sporitelna is the biggest bank in Slovakia. Despite pretty new version of the internet banking (rolled out in 2018), their password policy restricts password to be 16 characters long at most and prohibits any special characters.
NT OneAPP (≤1.5.22) by NewType Infortech has a CRITICAL hard-coded credentials flaw (CVE-2026-114219, CVSS 9.1). Attackers can decrypt login data & access user creds. No patch yet — restrict access & monitor closely. https://radar.offseq.com/threat/cve-2026-114219-cwe-798-use-of-hard-coded-credentials-in-newtype-infortech-nt-oneapp-d8766d50ef7b2f82 #OffSeq #CVE #infosec #vulnerability
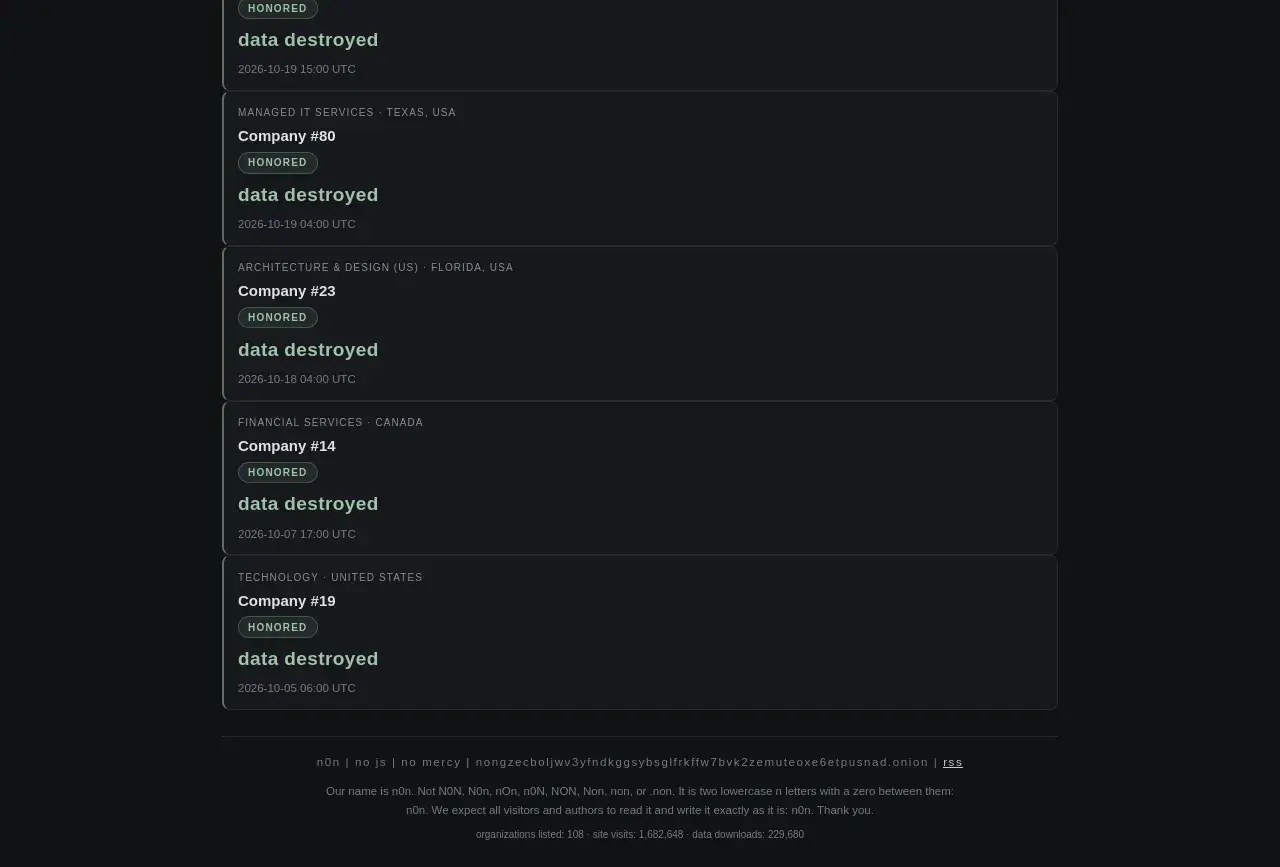
🚨New ransom group blog posts!🚨
Group name: N0n
Post title: Performance Ford Inc
Location: 🇺🇸 US
Sector: Automotive
Info: https://cti.fyi/#disclosure/N0n/Performance%20Ford%20Inc
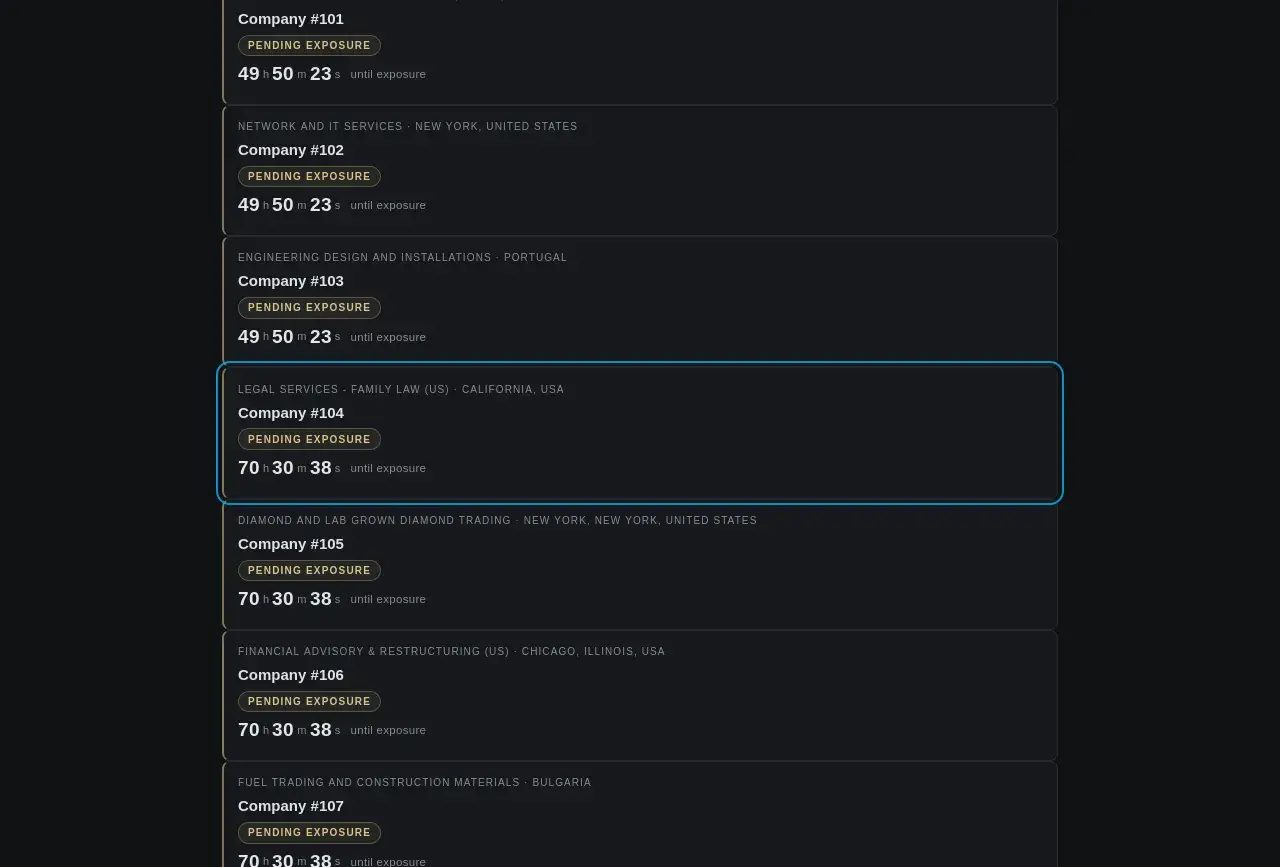
Group name: N0n
Post title: Company #104
Info: https://cti.fyi/#disclosure/N0n/Company%20%23104
Group name: N0n
Post title: Company #105
Info: https://cti.fyi/#disclosure/N0n/Company%20%23105
Group name: N0n
Post title: Company #106
Info: https://cti.fyi/#disclosure/N0n/Company%20%23106
Group name: N0n
Post title: Company #107
Info: https://cti.fyi/#disclosure/N0n/Company%20%23107
Group name: N0n
Post title: Company #108
Info: https://cti.fyi/#disclosure/N0n/Company%20%23108
Group name: N0n
Post title: Company #109
Info: https://cti.fyi/#disclosure/N0n/Company%20%23109
#ransomware #cti #threatintelligence #cybersecurity #infosec
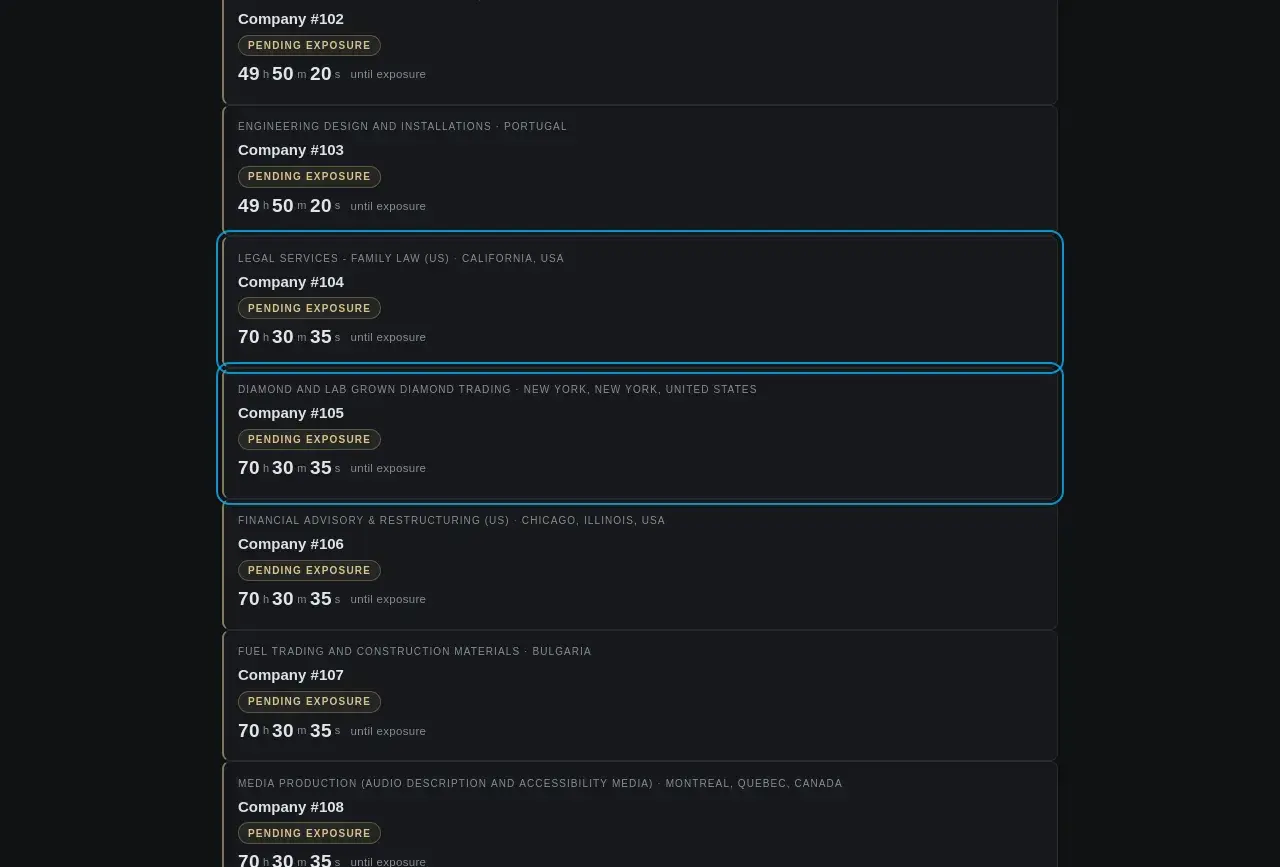
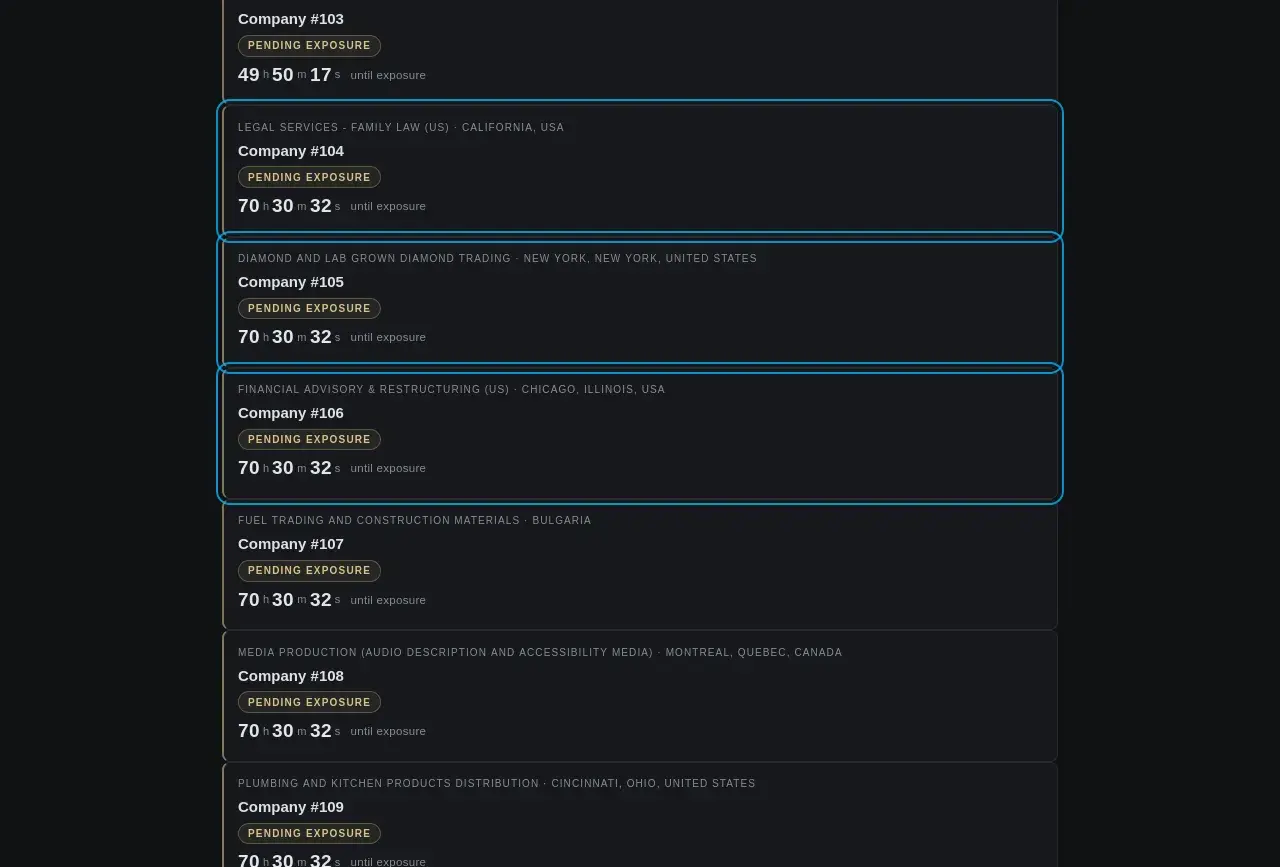
 CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
ASN: AS196968
Location: Martinroda, DE
Added: 2026-10-21T06:30
Id-SIRTII/CC just released (an hour ago) a security advisory regarding php2shell.
You can access the details here:
https://idsirtii.bssn.go.id/publications/advisories/security-advisory-kerentanan-pada-php2shell-cve-2026-109618-cve-2026-109619
#cybersecurity #infosec #indonesia #indonesiaNews #php2shell
Starting 9 October 2026, hundreds of Ledger users who bought through the reseller CryptoBilis lost an estimated $86 million to over $100 million.
Be careful. Details in the article:
https://hackers-arise.com/cryptocurrency-security-analysis-of-hardware-crypto-wallets/
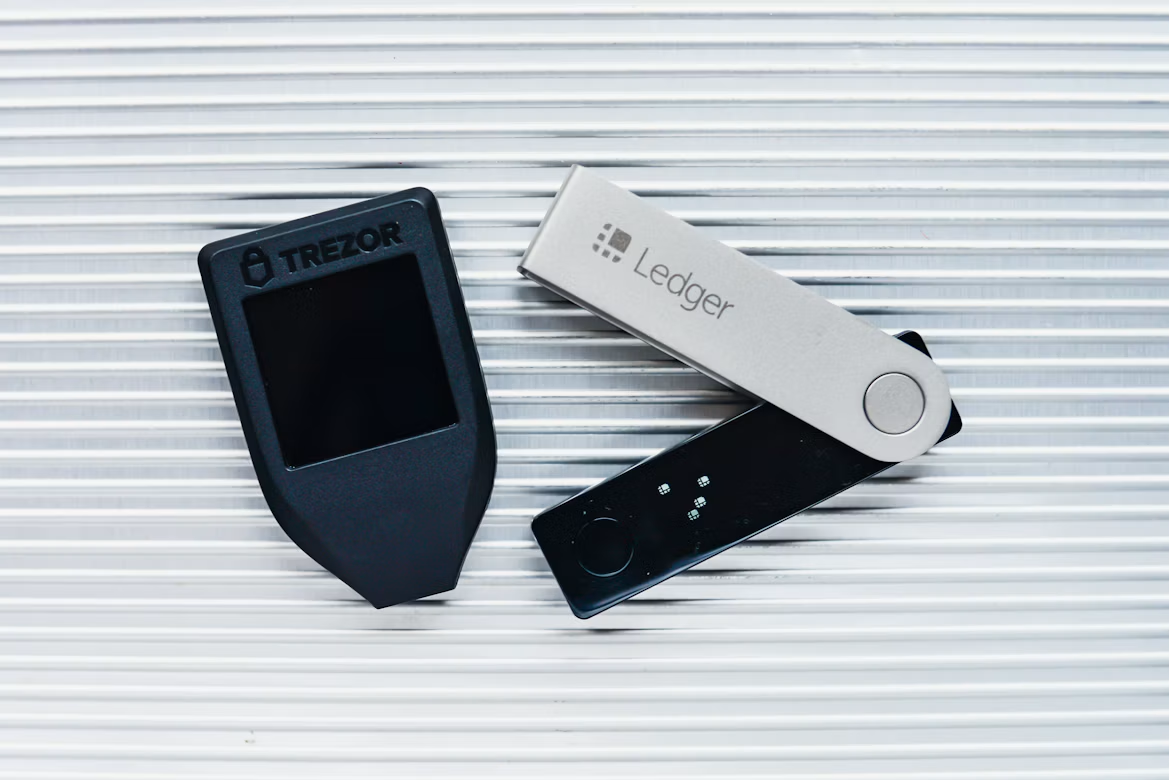
 Hackers Arise - EXPERT CYBERSECURITY TRAINING FOR ETHICAL HACKERSCryptocurrency: Security Analysis of Hardware Crypto Wallets - Hackers AriseHardware wallet implants can expose crypto recovery phrases. We showed how to protect your crypto from supply-chain attacks.
11 million. That's the number you need to focus on this morning. That many customer records just vanished from Burger King Japan.
🤖 CISA: attackers chain four Plex Media Server flaws (≤1.43.2) in "Plex2Shell" — SSRF via any X-Plex-Token value (CVE-2026-96652/96655), encoded URI scheme abuse (96654), then arbitrary file write that executes on load (CVE-2026-96656). All four in KEV, patch due Oct 23.
🔗 https://forums.plex.tv/t/important-security-update-for-plex-media-server-v1-43-2-and-earlier/942319
#CVE #InfoSec #CyberSec
 Plex ForumImportant Security Update for Plex Media Server v1.43.2 and earlierWe recently released Plex Media Server 1.43.3 and Plex Desktop 1.115.0 to address a number of security issues. We recommend all server owners and Desktop users update to the latest version as soon as possible. CVEs have been requested and we’ll reply to this thread with more details once they’re published. If you’re running Plex Media Server on a NAS device, the updated version may not be availab
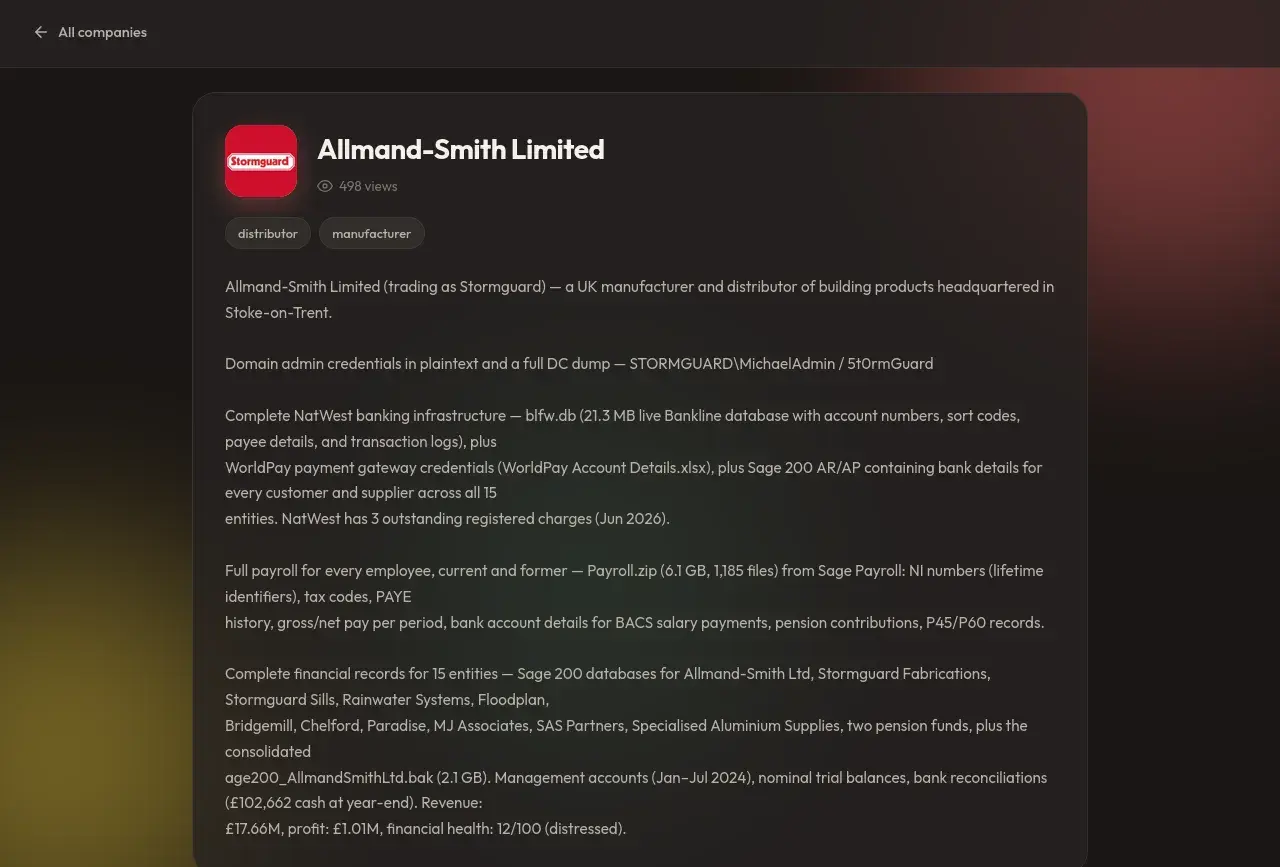
🚨New ransom group blog posts!🚨
Group name: aurora
Post title: Allmand-Smith Limited
Location: 🇬🇧 GB
Sector: Manufacturing
Info: https://cti.fyi/#disclosure/aurora/Allmand-Smith%20Limited
Group name: Ethics
Post title: Guarantee
Location: 🇺🇸 US
Info: https://cti.fyi/#disclosure/Ethics/Guarantee
Group name: Ethics
Post title: Support
Organization: Ethics Showcase
Location: 🇺🇸 US
Sector: Technology
Info: https://cti.fyi/#disclosure/Ethics/Support
#ransomware #cti #threatintelligence #cybersecurity #infosec
 CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
Possible Phishing 🎣
on: ⚠️hxxps[:]//weddtetu[.]weebly[.]com/
🧬 Analysis at: https://urldna.io/scan/6ad913af3b7750000503683e
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
CRITICAL vuln (CVE-2026-114220) in NT OneAPP ≤1.5.22: improper certificate validation lets network-adjacent attackers run MITM attacks, risking data exposure. Patch status unknown. Details: https://radar.offseq.com/threat/cve-2026-114220-cwe-295-improper-certificate-validation-in-newtype-infortech-nt-oneapp-9989fe91f72af746 #OffSeq #infosec #mitm #CVE2026114220
ASN: AS2518
Location: Tokyo, JP
Added: 2026-10-21T06:25
🚨 Railway Security Breach: Customer secrets may be exposed.
Railway disclosed a security incident involving its internal systems for storing environment variables. An unauthorized third party may have accessed encrypted variables and potentially decrypted values.
The bigger concern? You don't need to break AES-256-GCM if you compromise the system authorized to decrypt the secrets.
🔎 Technical breakdown:
• Envelope encryption & Google Cloud KMS
• Potential exposure of OpenAI and Anthropic API keys
• Credential rotation challenges while deployments are paused
• Multi-tenant isolation and cloud secret management risks
If you use Railway, review the official disclosure, rotate affected credentials, and audit provider usage logs for suspicious activity.
Full technical analysis 👇
https://thecybersecguru.com/news/railway-security-breach-environment-variables/
Content warning: Railway disclosed a security breach that may have exposed environment variables, API keys and database credentials. Read the technical analysis and response steps
 The CyberSec GuruRailway Security Breach: API Keys Exposed | The CyberSec GuruRailway disclosed a security breach that may have exposed environment variables, API keys and database credentials. Read the technical analysis and response steps
CVE-2026-114570 is a stored cross-site scripting vulnerability in WordPress Core, caused by insufficient escaping of user display names in Quick Edit.
It affects all versions up to 7.0.2 and requires contributor-level access. No in-the-wild exploitation is confirmed.
WordPress 7.0.3 fixes the issue.
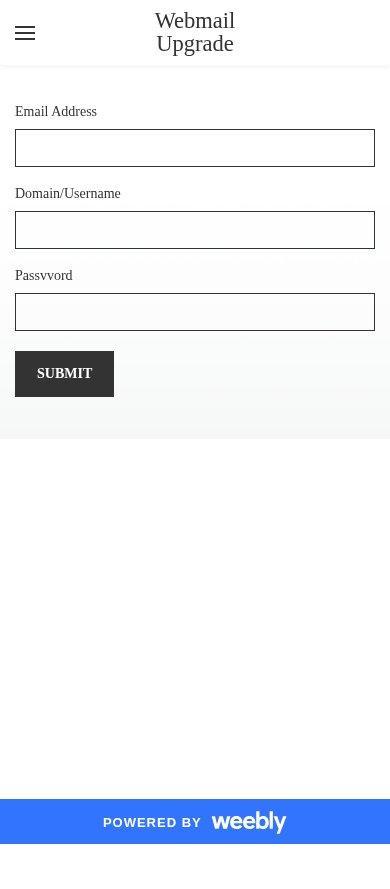
Possible Phishing 🎣
on: ⚠️hxxps[:]//adminhelpdeskunit1[.]weebly[.]com/
🧬 Analysis at: https://urldna.io/scan/6ad913ad3b7750000503683c
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
🚨 GitLab Regex RCE alert: CVE-2026-110264 carries CVSS 10.0.
A 12-year-old integer overflow in the regular expression compiler could enable unauthenticated remote code execution.
🔴 CVSS 10.0
⚠️ No authentication required
🛠️ Multiple GitLab branches have patched releases
Already patched the previous GitLab regex flaw? Don't assume you're covered. CVE-2026-110264 requires a separate version check.
Technical analysis + affected versions:
https://thecybersecguru.com/news/gitlab-regex-rce-cve-2026-110264/
Content warning: GitLab CVE-2026-110264 is a critical regex compiler integer overflow rated CVSS 10.0. Learn about regular expression RCE, affected versions and security patches
 The CyberSec GuruCVE-2026-110264: GitLab Regex Integer Overflow RCE, CVSS 10.0 | The CyberSec GuruGitLab CVE-2026-110264 is a critical regex compiler integer overflow rated CVSS 10.0. Learn about regular expression RCE, affected versions and security patches
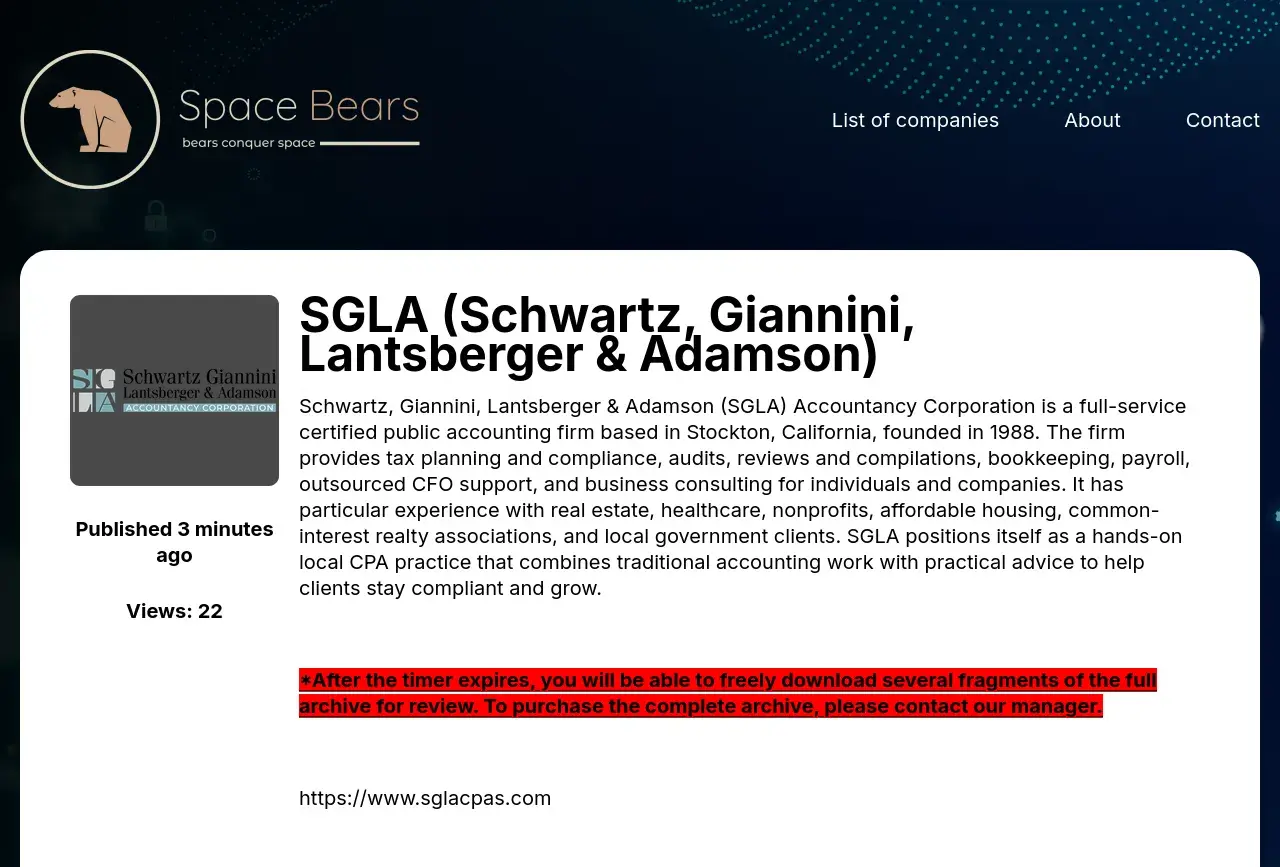
🚨New ransom group blog post!🚨
Group name: spacebears
Post title: SGLA (Schwartz, Giannini, Lantsberger & Adamson)
Organization: Schwartz, Giannini, Lantsberger & Adamson
Location: 🇺🇸 US
Sector: Professional Services
Info: https://cti.fyi/#disclosure/spacebears/SGLA%20%28Schwartz%2C%20Giannini%2C%20Lantsberger%20%26%20Adamson%29
#ransomware #cti #threatintelligence #cybersecurity #infosec
 CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
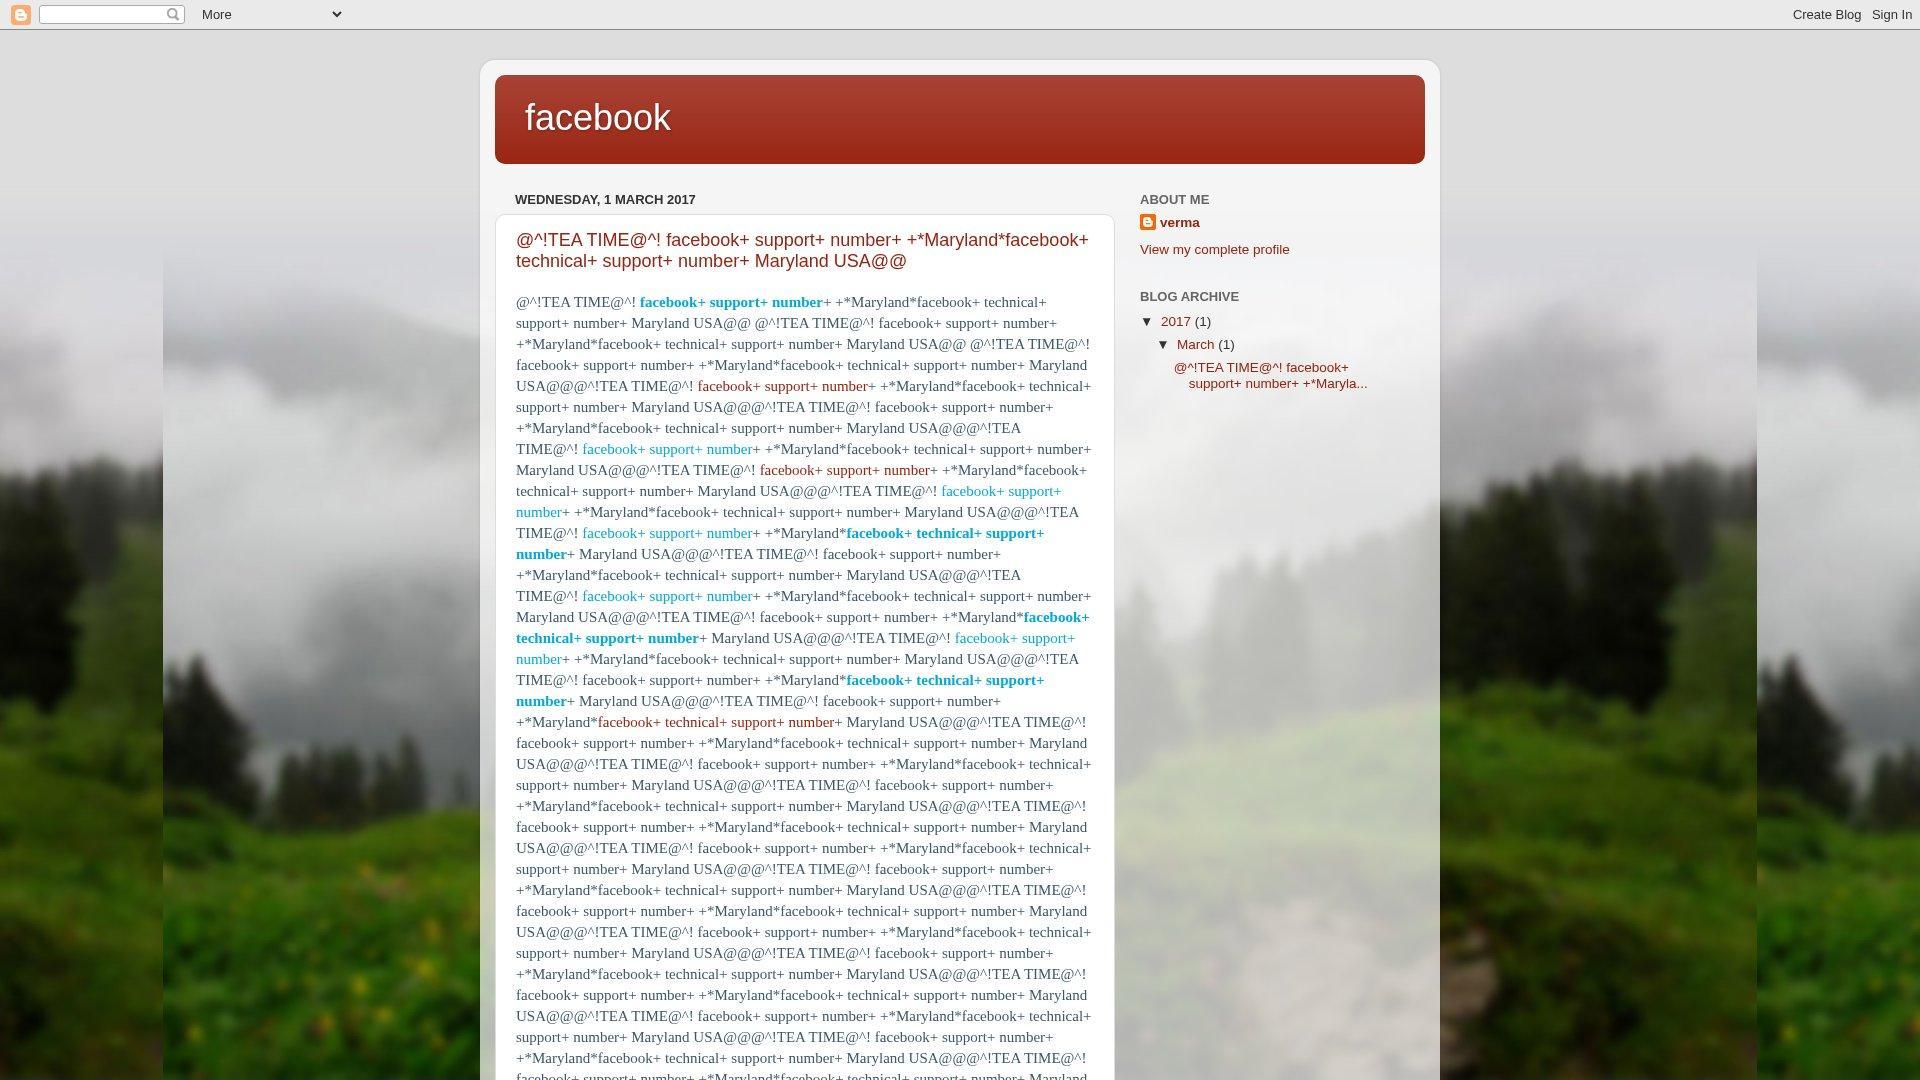
Possible Phishing 🎣
on: ⚠️hxxp[:]//facebookcustomersupportnumber25[.]blogspot[.]com
🧬 Analysis at: https://urldna.io/scan/6ad959e63b7750000486f500
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
Blogger Elias Taylor says public PHP2Shell PoCs fail on vanilla PHP and lean on a file-inclusion bug the target must already have. The top-starred PoC repo's README lists such app-side conditions for chain A and says code for chains D and E is for paid subscribers. PHP's advisory still says RCE was validated against default mod_php (attack complexity high), and Datadog says it reproduced both flaws.
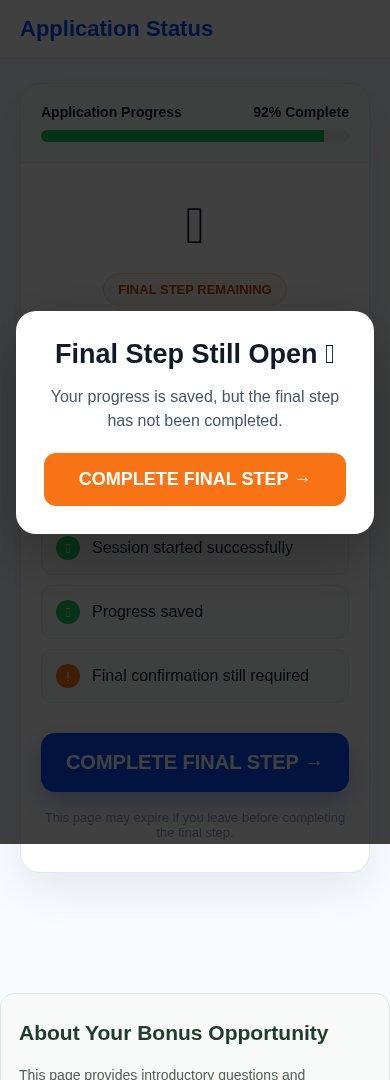
Possible Phishing 🎣
on: ⚠️hxxps[:]//falselection[.]shop/1C06072qc83zmjs-7na7wo07ps0gn2m000012n9c1
🧬 Analysis at: https://urldna.io/scan/6ad9360a3b77500007852ca7
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
CVE-2026-114727 (HIGH): Roundcube Webmail <1.6.20/1.7.5 allows SVG/EPS uploads, risking remote code execution via ImageMagick. Upgrade to 1.6.20+ or 1.7.5+ to mitigate. Details: https://radar.offseq.com/threat/cve-2026-114727-cwe-829-inclusion-of-functionality-from-untrusted-control-sphere-in-roundcube-webmail-0e067a7fe4b46d68 #OffSeq #Vulnerability #Infosec #Roundcube
🤖 GitLab patched a CVSS 10.0 unauth RCE in self-managed servers, affecting every release back to 7.0 (2014). No login needed to run code. The Oct 12 fix only covered 19.2+ — if you patched then, you need this second update.
🔗 https://thehackernews.com/2026/10/critical-gitlab-flaw-cvss-100-could.html
#CVE #GitLab #RCE #InfoSec
 The Hacker NewsCritical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of ReleasesGitLab fixes CVE-2026-110264, a critical flaw that could allow unauthenticated code execution on self-managed versions dating back to 7.0.
Railway says an unauthorized party may have accessed encrypted environment variables and decrypted some, with impact that "may be limited to a subset of users." Yet it tells all users to roll every variable, paused all deployments, and invalidated all API tokens. Its status page showed only an outage until the 22:10 UTC notice, and paused builds blocked applying new keys. Railway gives no count or entry point.
https://blog.railway.com/p/security-disclosure-wednesday-october-21st
 Railway BlogSecurity Disclosure: Wednesday October 21st | Railway BlogRailway detected anomalous activity involving systems that store customer environment variables and recommends your immediate attention
A New Mexico judge ordered Meta to pay $25B for deceiving users, down from $219.5B (43,899,725 jury-found violations at the $5,000 maximum). The court found Facebook promised a full post-Cambridge Analytica investigation but ran 14 forensic audits in three years and notified users about 2 apps. Meta says it will appeal, calling the case a "tax on speech." Injunctive relief is still pending.
https://www.cnbc.com/2026/10/21/meta-new-mexico-cambridge-analytica-penalty.html
 CNBCMeta ordered to pay $25 billion penalty in New Mexico Cambridge Analytica caseMeta to pay $25 billion in penalties related to Cambridge Analytica scandal in New Mexico.
The PHP Foundation says first signs of the flaw behind CVE-2026-109618 appeared in 2024, and the fix then stalled for months: "a structural failure." PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 fix it and CVE-2026-109619, both unauthenticated RCE (CVSS 9.2). It says Chainguard broke the embargo 6+ hours early; Chainguard's CEO told The Register he shipped because vendors reported exploitation. AWS saw a honeypot attempt on Oct 17.
 thephp.foundationToday's PHP Security Release, and How We're Strengthening PHP SecurityDescribing the story behind how critical security vulnerabilities were found and fixed.
Possible Phishing 🎣
on: ⚠️hxxp[:]//jj-facebook[.]blogspot[.]com
🧬 Analysis at: https://urldna.io/scan/6ad9602e3b77500008f5c21e
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
ASN: AS2518
Location: Tokyo, JP
Added: 2026-10-21T08:18
Possible Phishing 🎣
on: ⚠️hxxps[:]//onetimefstip[.]weebly[.]com
🧬 Analysis at: https://urldna.io/scan/6ad967ef3b7750000270920e
#cybersecurity #phishing #infosec #urldna #scam #infosec
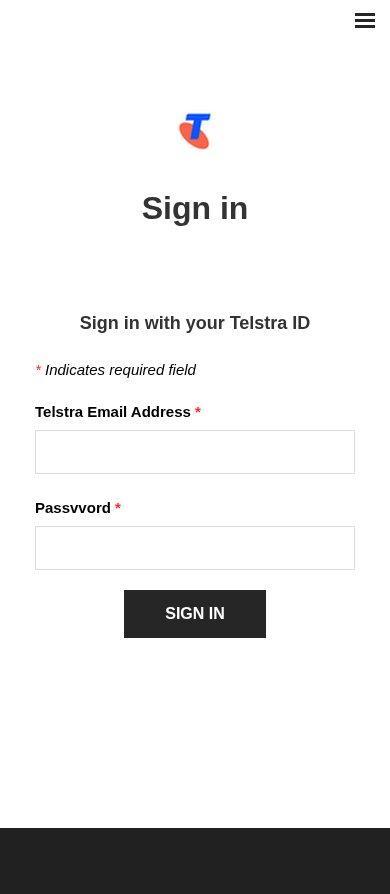 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test