X XFediYour place in the Fediverse
XFEDI

#InfoSEC

ActivityPub

Public posts with this hashtag.

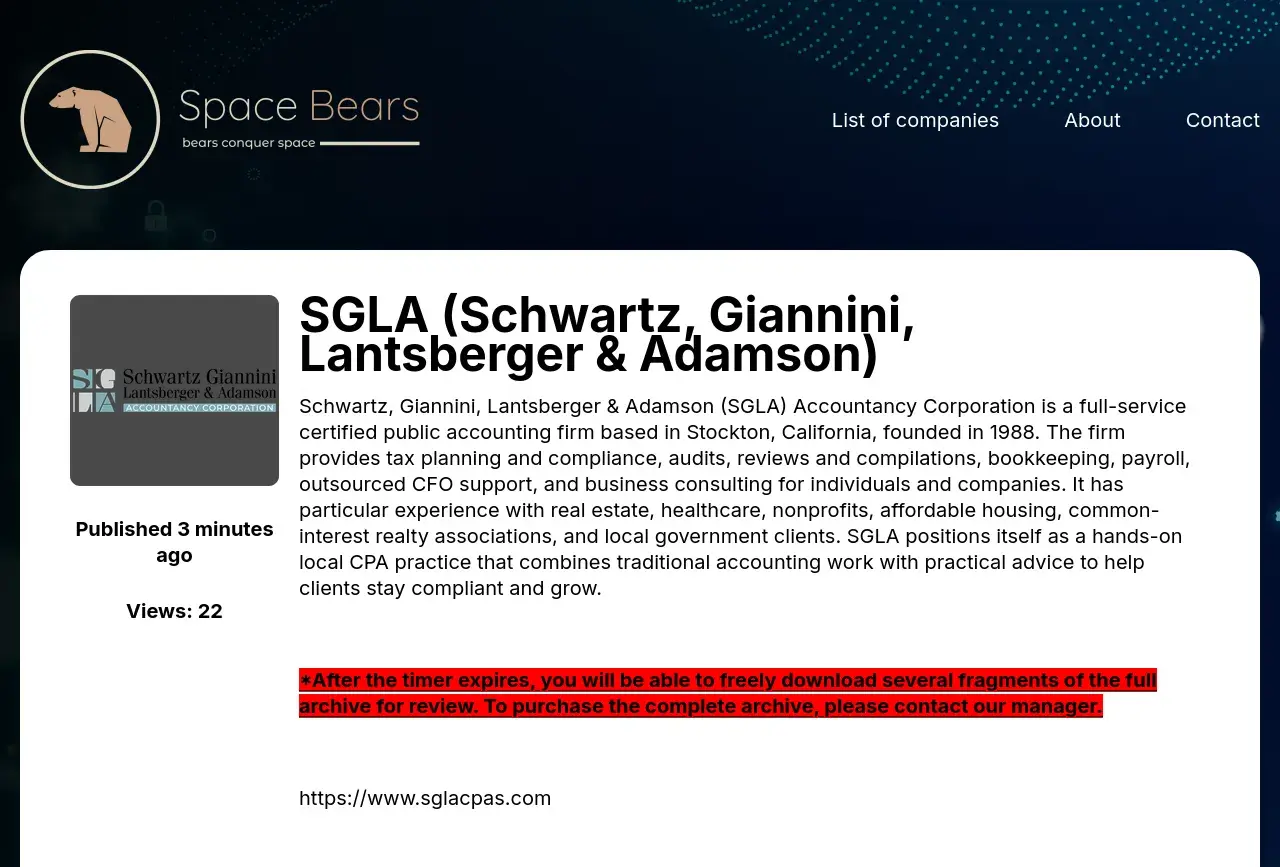
🚨New ransom group blog post!🚨

Group name: spacebears
Post title: SGLA (Schwartz, Giannini, Lantsberger & Adamson)
Organization: Schwartz, Giannini, Lantsberger & Adamson
Location: 🇺🇸 US
Sector: Professional Services
Info: https://cti.fyi/#disclosure/spacebears/SGLA%20%28Schwartz%2C%20Giannini%2C%20Lantsberger%20%26%20Adamson%29

#ransomware #cti #threatintelligence #cybersecurity #infosec
Media attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Blogger Elias Taylor says public PHP2Shell PoCs fail on vanilla PHP and lean on a file-inclusion bug the target must already have. The top-starred PoC repo's README lists such app-side conditions for chain A and says code for chains D and E is for paid subscribers. PHP's advisory still says RCE was validated against default mod_php (attack complexity high), and Datadog says it reproduced both flaws.

https://eliastaylor.com/noexploit/

#PHP2Shell #PHP #InfoSec #Cybersecurity

Elias TaylorThere isn't an easy exploit for this PHP vulnerabilityMass hysteria, or something.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

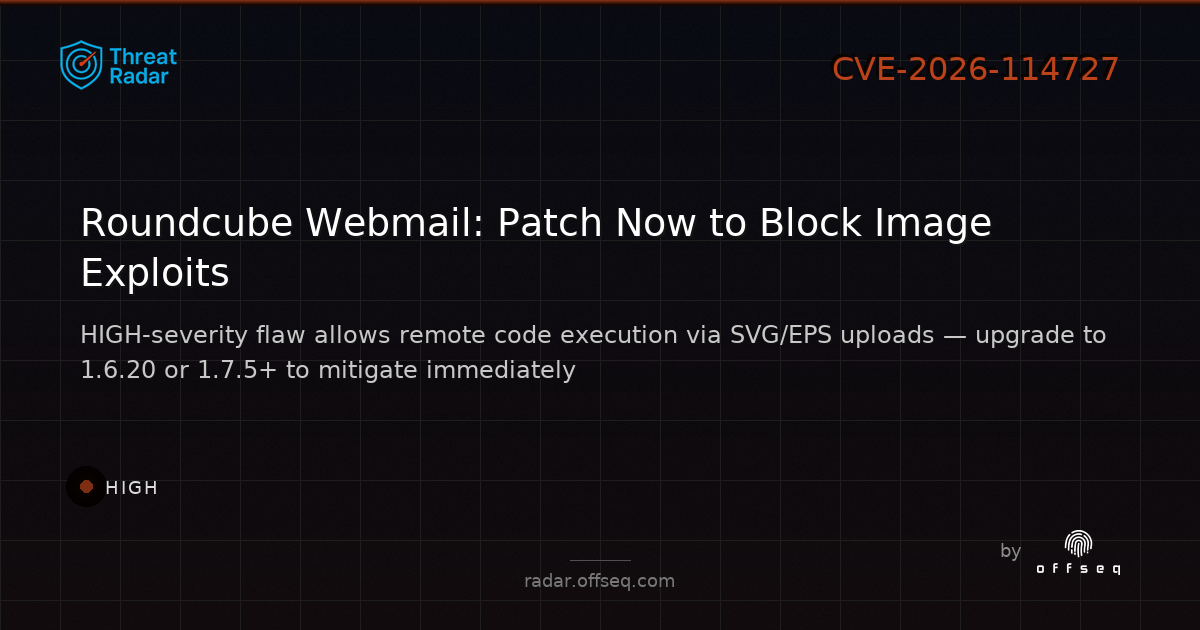
CVE-2026-114727 (HIGH): Roundcube Webmail <1.6.20/1.7.5 allows SVG/EPS uploads, risking remote code execution via ImageMagick. Upgrade to 1.6.20+ or 1.7.5+ to mitigate. Details: https://radar.offseq.com/threat/cve-2026-114727-cwe-829-inclusion-of-functionality-from-untrusted-control-sphere-in-roundcube-webmail-0e067a7fe4b46d68 #OffSeq #Vulnerability #Infosec #Roundcube

High threat: CVE-2026-114727: CWE-829 Inclusion of Functionality from Untrusted Control Sphere in Roundcube Webma
OffSeq Threat RadarCVE-2026-114727: CWE-829 Inclusion of Functionality from… | Threat RadarCVE-2026-114727 is a high-severity vulnerability in Roundcube Webmail before versions 1.6.20 and 1.7.5. The issue involves unsafe handling of SVG and EPS image…
↩ Reply ♡ 0 · ↻ 0 ↗ Original
C

🤖 GitLab patched a CVSS 10.0 unauth RCE in self-managed servers, affecting every release back to 7.0 (2014). No login needed to run code. The Oct 12 fix only covered 19.2+ — if you patched then, you need this second update.
🔗 https://thehackernews.com/2026/10/critical-gitlab-flaw-cvss-100-could.html
#CVE #GitLab #RCE #InfoSec

The Hacker NewsCritical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of ReleasesGitLab fixes CVE-2026-110264, a critical flaw that could allow unauthenticated code execution on self-managed versions dating back to 7.0.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Railway says an unauthorized party may have accessed encrypted environment variables and decrypted some, with impact that "may be limited to a subset of users." Yet it tells all users to roll every variable, paused all deployments, and invalidated all API tokens. Its status page showed only an outage until the 22:10 UTC notice, and paused builds blocked applying new keys. Railway gives no count or entry point.

https://blog.railway.com/p/security-disclosure-wednesday-october-21st

#CloudSecurity #DevOps #InfoSec #Cybersecurity

Railway BlogSecurity Disclosure: Wednesday October 21st | Railway BlogRailway detected anomalous activity involving systems that store customer environment variables and recommends your immediate attention
↩ Reply ♡ 0 · ↻ 0 ↗ Original

A New Mexico judge ordered Meta to pay $25B for deceiving users, down from $219.5B (43,899,725 jury-found violations at the $5,000 maximum). The court found Facebook promised a full post-Cambridge Analytica investigation but ran 14 forensic audits in three years and notified users about 2 apps. Meta says it will appeal, calling the case a "tax on speech." Injunctive relief is still pending.

https://www.cnbc.com/2026/10/21/meta-new-mexico-cambridge-analytica-penalty.html

#Privacy #Facebook #CambridgeAnalytica #InfoSec

CNBCMeta ordered to pay $25 billion penalty in New Mexico Cambridge Analytica caseMeta to pay $25 billion in penalties related to Cambridge Analytica scandal in New Mexico.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

The PHP Foundation says first signs of the flaw behind CVE-2026-109618 appeared in 2024, and the fix then stalled for months: "a structural failure." PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 fix it and CVE-2026-109619, both unauthenticated RCE (CVSS 9.2). It says Chainguard broke the embargo 6+ hours early; Chainguard's CEO told The Register he shipped because vendors reported exploitation. AWS saw a honeypot attempt on Oct 17.

https://thephp.foundation/blog/2026/10/21/todays-php-security-release-and-how-were-strengthening-php-security/

#PHP #InfoSec #Cybersecurity #OpenSource

thephp.foundationToday's PHP Security Release, and How We're Strengthening PHP SecurityDescribing the story behind how critical security vulnerabilities were found and fixed.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

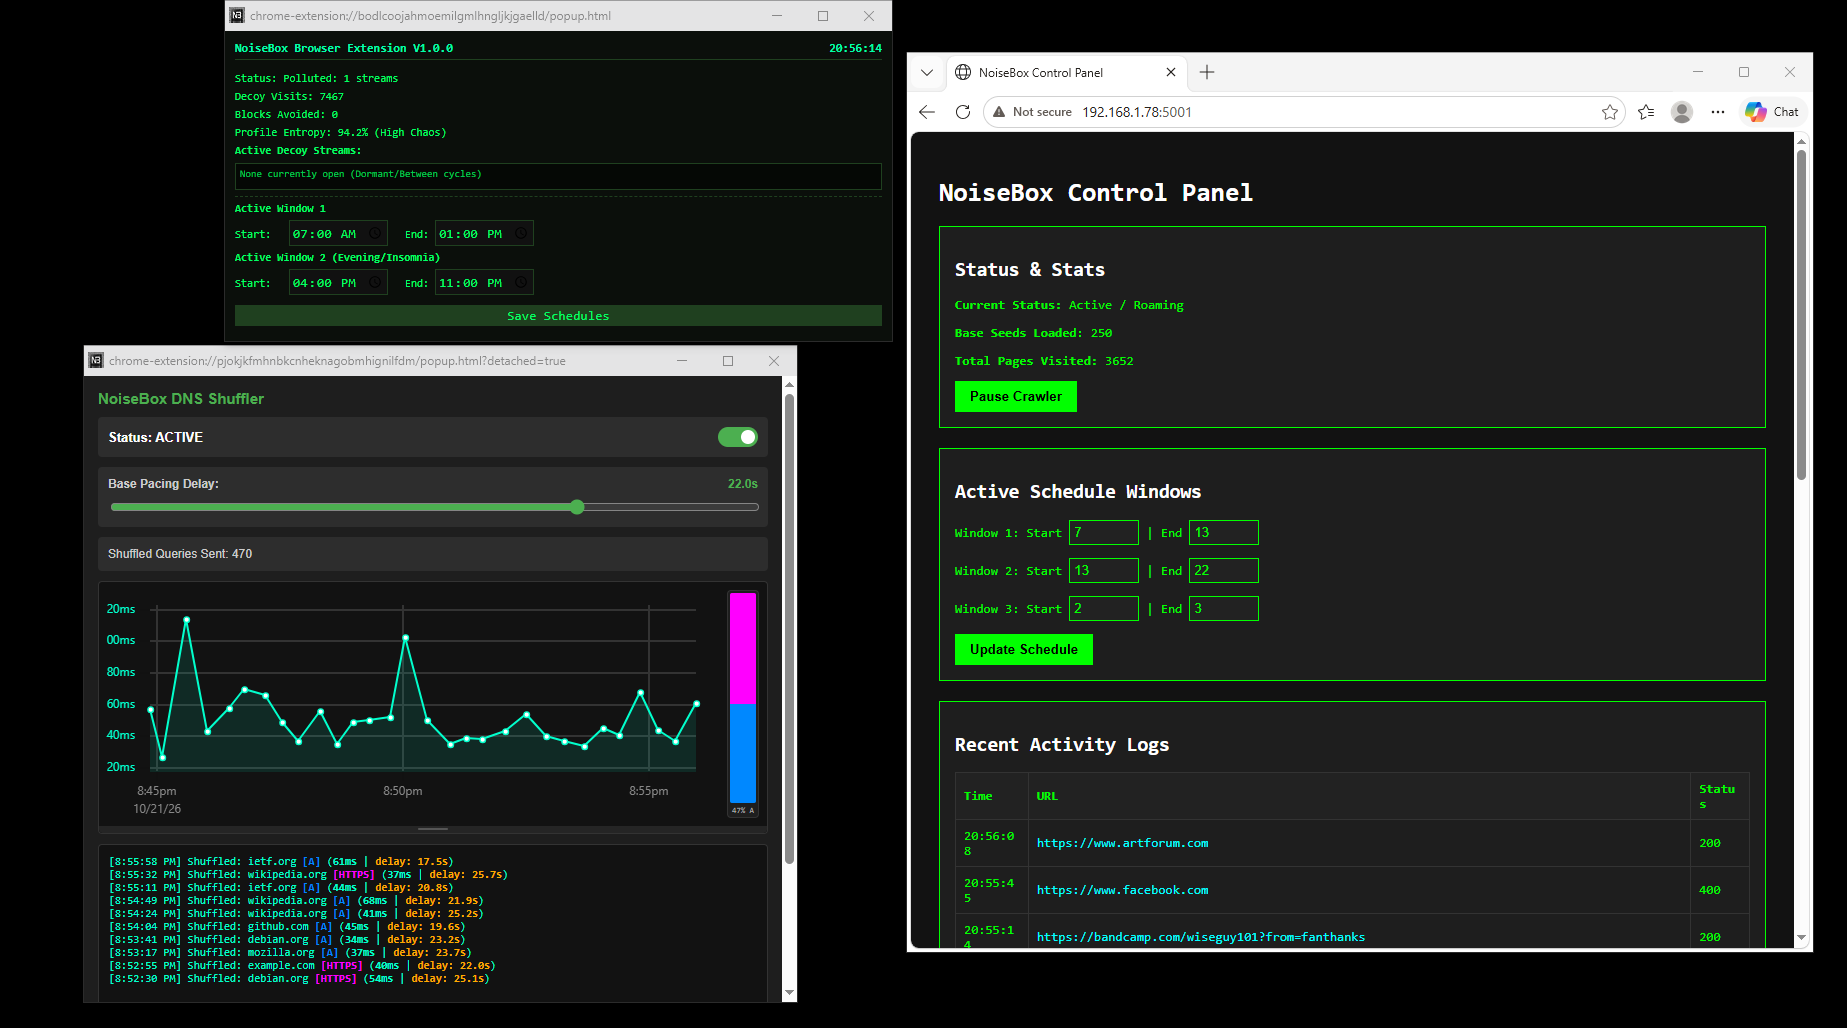
A screen full of data poison! Clockwise from top: NoiseBox Chrome Based Crawler Extension, NoiseBox router-level Wyse Crawler, and the new NoiseBox DNS Shuffler (coming soon). All working hard to obliterate our browsing patterns. All free, open source at Codeberg.org/NoiseBoxWorks
https://www.youtube.com/channel/UCi2cOT9eW575Fw-qoPB4seg
#Privacy #OpenSource #Infosec #DataPrivacy #BrowserExtension

Media attachment
YouTubeNoiseBoxNoiseBox's mission is to create free open source tools to help people preserve their online privacy through active data pollution. Codeberg.org/NoiseBoxWorks
↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

New docker image for HortusFox v6.4 is now live! 😊

A big thanks to @thephpf for working so hard on the PHP patches. And everyone involved building docker images, posting news, supporting maintainers, and updating their own projects. You did an awesome job today!

What a #Spooktober indeed. We all deserve some rest now. 😴

Good night everyone. See y'all tomorrow. 💚

#PHP #FOSS #OpenSource #SelfHosted #SelfHosting #PHP2Shell #InfoSec

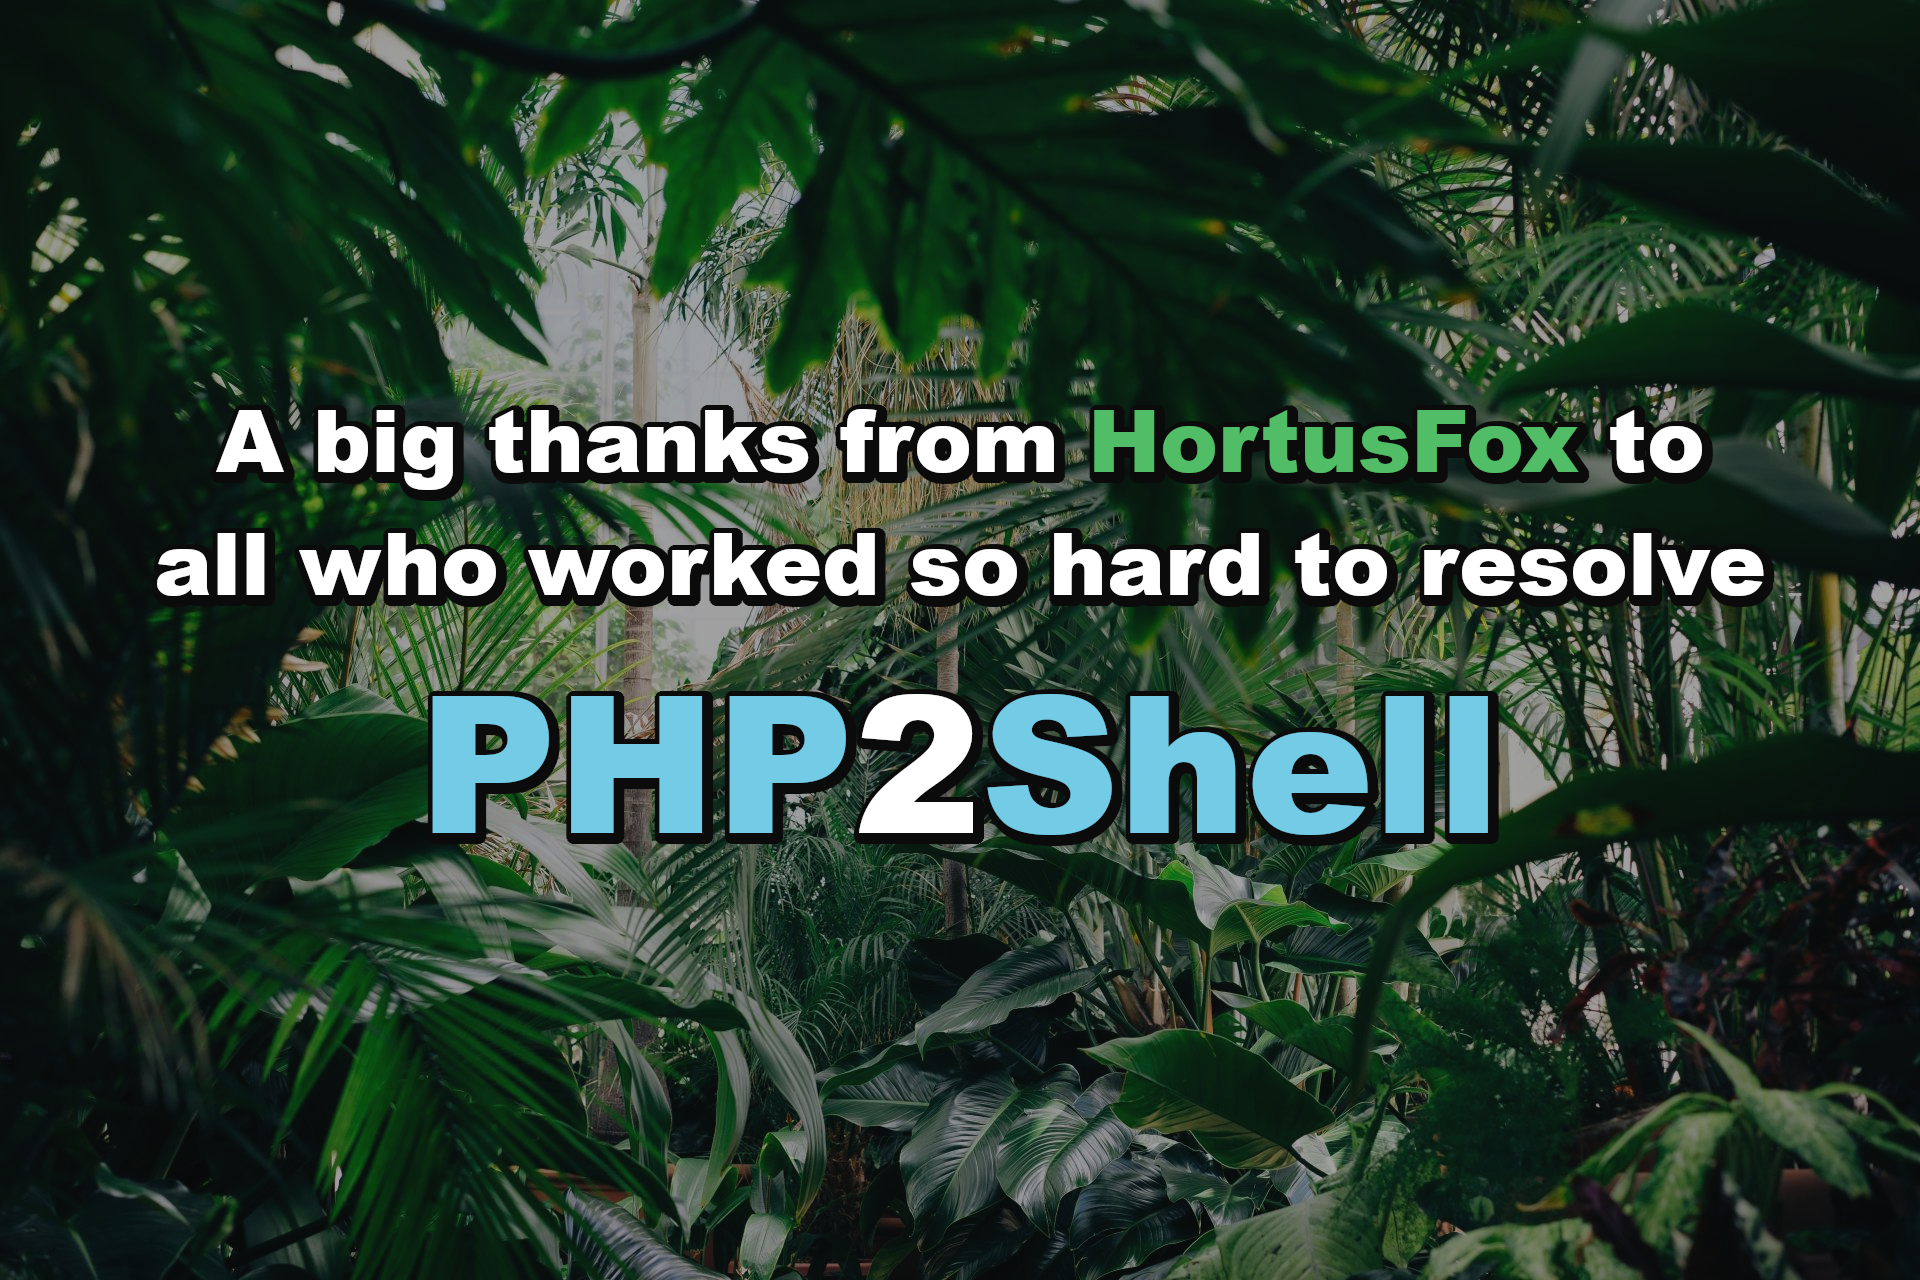
Photo with plants in the background, containing the following text in the front:

A big thanks from HortusFox to all who worked so hard to resolve
PHP2Shell.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

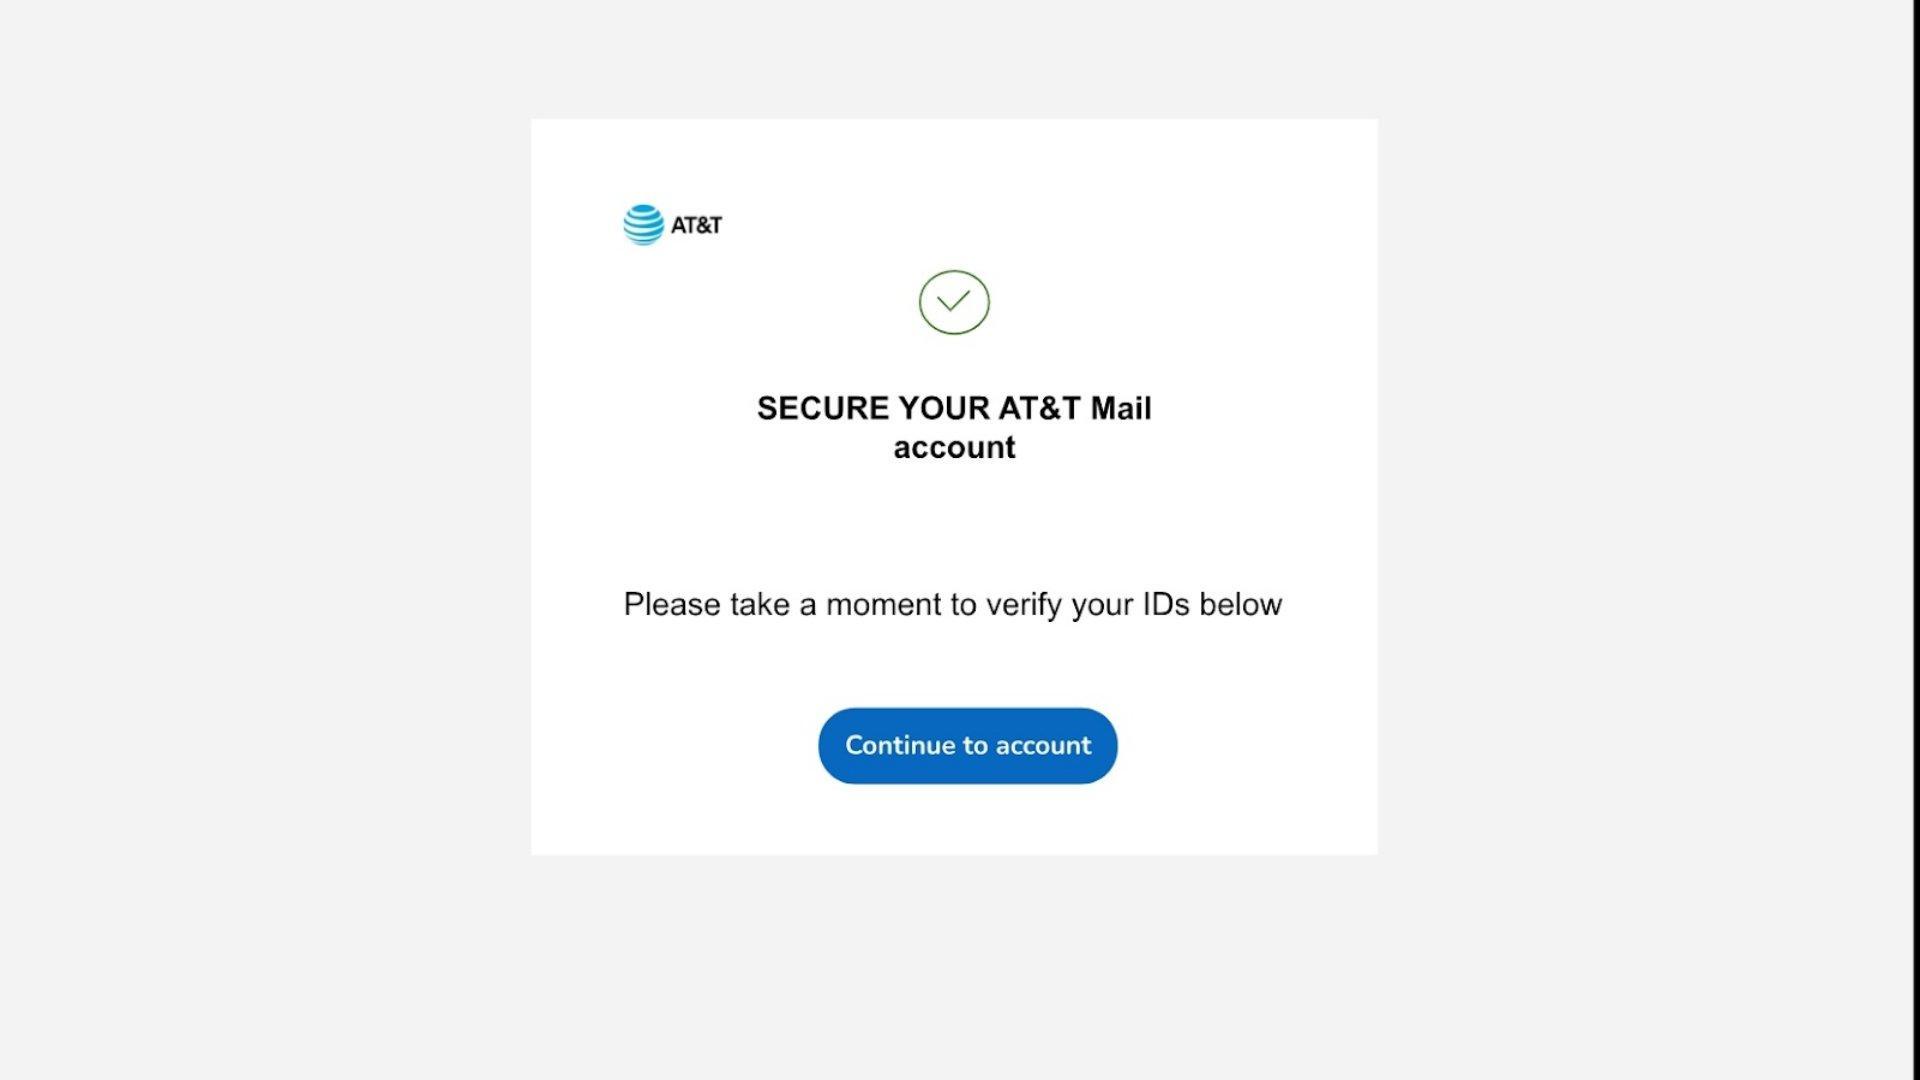
Possible Phishing 🎣
on: ⚠️hxxps[:]//docs[.]google[.]com/presentation/d/e/2PACX-1vRRY_5Lkya4ZoCF3ZLSddZWed9ZSkrF_gw0bqilBkNzJSBxXahIbjvhKBBbPmsnR0NVgbS398sFbQJK/pub?start=false&amp;loop=false&amp;delayms=3000
🧬 Analysis at: https://urldna.io/scan/6ad8fdbe3b775000045e8555
#cybersecurity #phishing #infosec #urldna #scam #infosec

Media attachment
urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE POLAR 2026 SPONSOR : SECUR01
La prochaine édition de POLAR ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous Secur01, qui est notre partenaire LANIÈRES et CAFÉ!
Pour en savoir plus sur la mission de cette compagnie, visiter leur site web : https://www.secur01.com/
—--
Our 4th edition of POLAR would not be possible without our sponsors. And this year, we are happy to have Secur01, a LANYARD & COFFEE sponsor!
If you want to learn more about this company’s mission, visit their website https://www.secur01.com/
#CISO #infosec #polar #hf2026 #cybersecurity

Media attachment
www.secur01.comSecur01 | Solutions complètes de cybersécurité pour entreprisesExpert en cybersécurité offrant des services de protection, détection et réponse aux incidents. Solutions personnalisées pour entreprises de 5 à 1000 employés.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE POLAR 2026 SPONSOR : TENABLE
La prochaine édition de POLAR ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous Tenable, qui est notre partenaire BANNIÈRE!
Pour en savoir plus sur la mission de cette compagnie, visiter leur site web : https://www.tenable.com/
—--
Our 4th edition of POLAR would not be possible without our sponsors. And this year, we are happy to have Tenable, a BANNER sponsor!
If you want to learn more about this company’s mission, visit their website https://www.tenable.com/
#CISO #infosec #polar #hf2026 #cybersecurity

Media attachment
Tenable®Vulnerability and exposure management | Cloud and AI security | Tenable®The leader in exposure management and AI security, Tenable cybersecurity solutions reduce cyber risk across IT, OT, cloud, identity & hybrid attack surfaces.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE POLAR 2026 SPONSOR : CYBERDEFENSE AI
La prochaine édition de POLAR ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous Cyberdefense AI, qui est notre partenaire KIOSQUE!
Pour en savoir plus sur la mission de cette compagnie, visiter leur site web : https://cyberdefense.ai/
—--
Our 4th edition of POLAR would not be possible without our sponsors. And this year, we are happy to have Cyberdefense AI, a KIOSK sponsor!
If you want to learn more about this company’s mission, visit their website https://cyberdefense.ai/
#CISO #infosec #polar #hf2026 #cybersecurity

Media attachment
cyberdefense.aiCYBERDEFENSE.AI - Preemptive Cybersecurity PlatformAI-native preemptive cybersecurity. Neutralize malicious behavior before it becomes breach. 98.6/100 GoTestWaf,
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE POLAR 2026 SPONSOR : ASTATE
La prochaine édition de POLAR ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous Astate, qui est notre partenaire KIOSQUE!
Pour en savoir plus sur la mission de cette compagnie, visiter leur site web : https://astate.one/
—--
Our 4th edition of POLAR would not be possible without our sponsors. And this year, we are happy to have Astate, a KIOSK sponsor!
If you want to learn more about this company’s mission, visit their website https://astate.one/
#CISO #infosec #polar #hf2026 #cybersecurity

Media attachment
astate.oneASTATE
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🔴 EXPLOITED

Siemens Software Center has a DLL hijacking flaw (CVE-2026-110936) being exploited now: attackers pair the real signed app with a malicious DLL, so Windows runs their code.

Signature allowlists wave it through.

Fix: update to V4.0.9.8 and sweep for the indicators.

https://suriq.io/blog/siemens-software-center-cve-2026-110936-dll-hijack

#CVE #Detection #CISAKEV #infosec

A stamped metal seal on a pedestal with a dark object hidden beneath it
SuriqSiemens Software Center DLL Hijack ExploitedCVE-2026-110936 is a CISA KEV-listed DLL hijacking flaw in Siemens Software Center, exploited in a ClickFix campaign. Update to V4.0.9.8 and hunt the IOCs.
↩ Reply ♡ 0 · ↻ 0 ↗ Original