X XFediYour place in the Fediverse
XFEDI

#InfoSEC

ActivityPub

Public posts with this hashtag.

↳ In reply to a post

New docker image for HortusFox v6.4 is now live! 😊

A big thanks to @thephpf for working so hard on the PHP patches. And everyone involved building docker images, posting news, supporting maintainers, and updating their own projects. You did an awesome job today!

What a #Spooktober indeed. We all deserve some rest now. 😴

Good night everyone. See y'all tomorrow. 💚

#PHP #FOSS #OpenSource #SelfHosted #SelfHosting #PHP2Shell #InfoSec

Photo with plants in the background, containing the following text in the front:

A big thanks from HortusFox to all who worked so hard to resolve
PHP2Shell.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

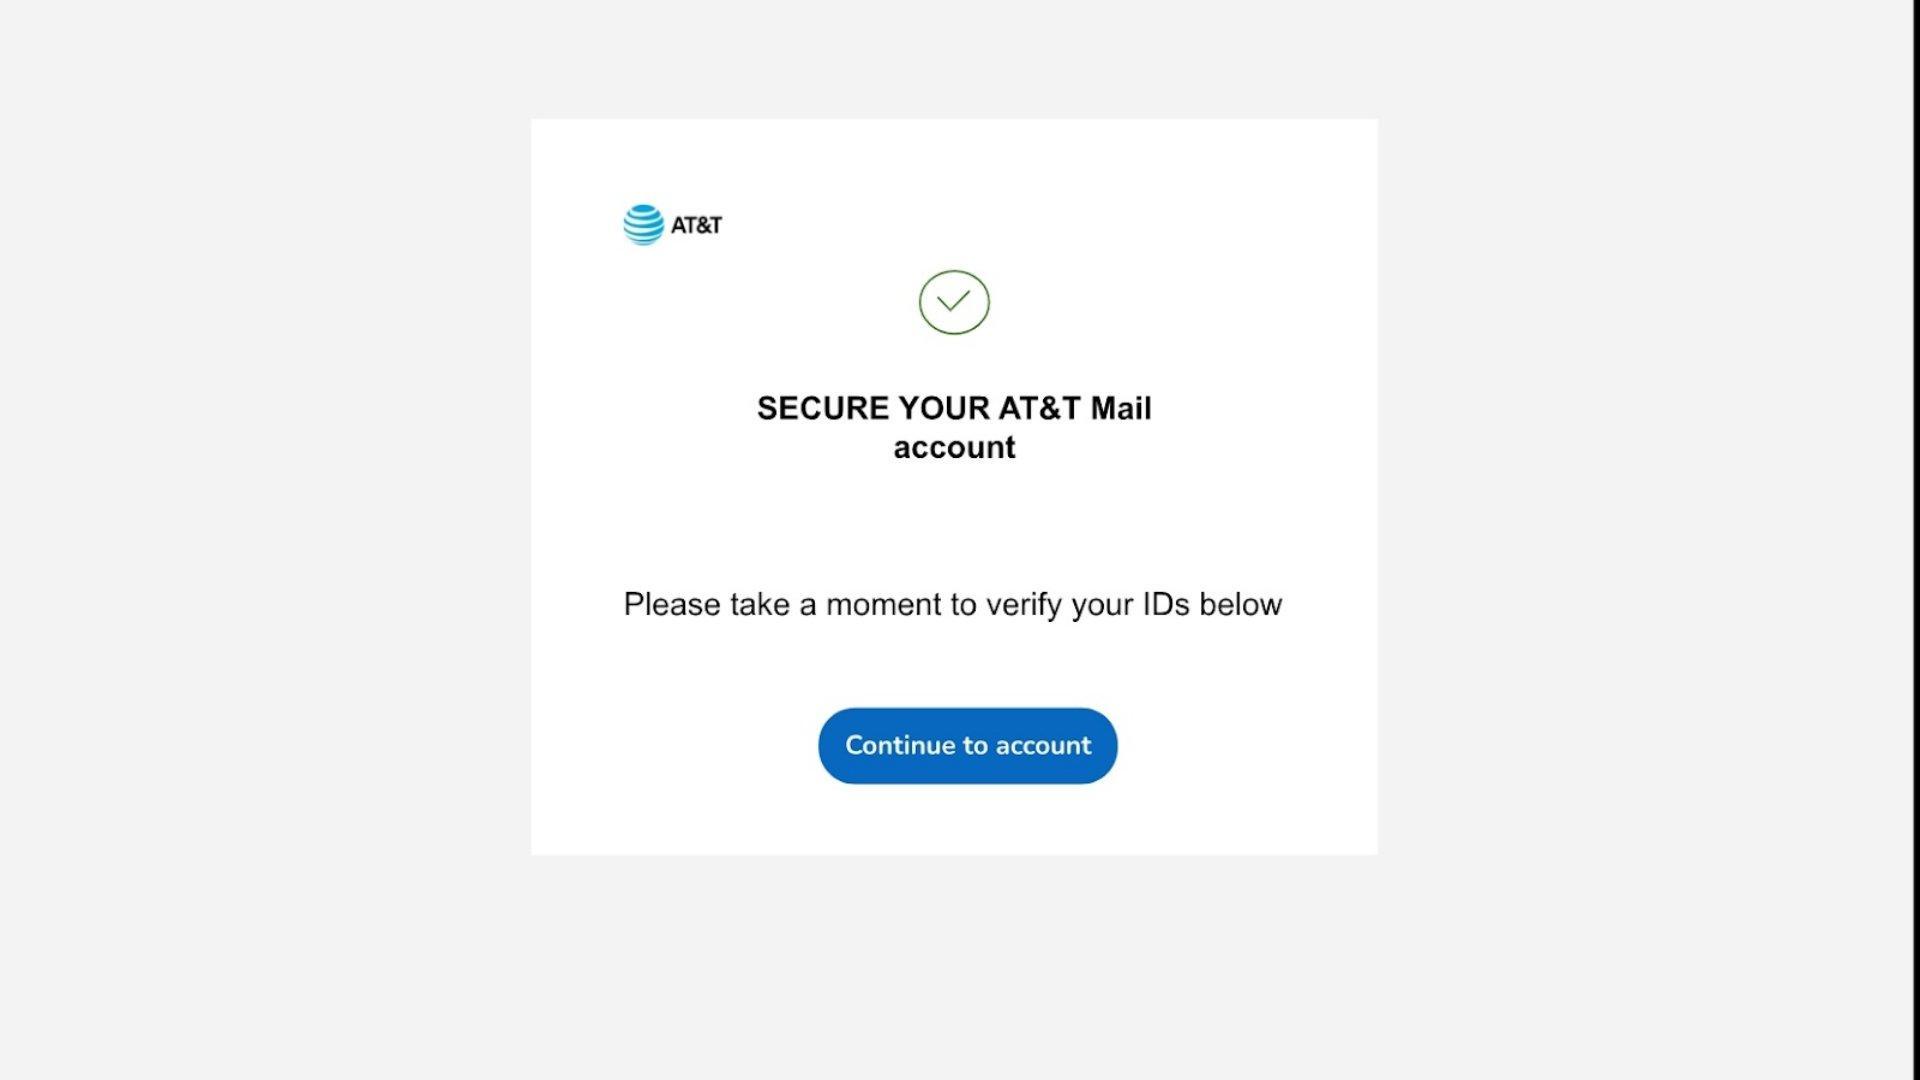
Possible Phishing 🎣
on: ⚠️hxxps[:]//docs[.]google[.]com/presentation/d/e/2PACX-1vRRY_5Lkya4ZoCF3ZLSddZWed9ZSkrF_gw0bqilBkNzJSBxXahIbjvhKBBbPmsnR0NVgbS398sFbQJK/pub?start=false&loop=false&delayms=3000
🧬 Analysis at: https://urldna.io/scan/6ad8fdbe3b775000045e8555
#cybersecurity #phishing #infosec #urldna #scam #infosec

Media attachment
urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE POLAR 2026 SPONSOR : SECUR01
La prochaine édition de POLAR ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous Secur01, qui est notre partenaire LANIÈRES et CAFÉ!
Pour en savoir plus sur la mission de cette compagnie, visiter leur site web : https://www.secur01.com/
—--
Our 4th edition of POLAR would not be possible without our sponsors. And this year, we are happy to have Secur01, a LANYARD & COFFEE sponsor!
If you want to learn more about this company’s mission, visit their website https://www.secur01.com/
#CISO #infosec #polar #hf2026 #cybersecurity

Media attachment
www.secur01.comSecur01 | Solutions complètes de cybersécurité pour entreprisesExpert en cybersécurité offrant des services de protection, détection et réponse aux incidents. Solutions personnalisées pour entreprises de 5 à 1000 employés.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE POLAR 2026 SPONSOR : TENABLE
La prochaine édition de POLAR ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous Tenable, qui est notre partenaire BANNIÈRE!
Pour en savoir plus sur la mission de cette compagnie, visiter leur site web : https://www.tenable.com/
—--
Our 4th edition of POLAR would not be possible without our sponsors. And this year, we are happy to have Tenable, a BANNER sponsor!
If you want to learn more about this company’s mission, visit their website https://www.tenable.com/
#CISO #infosec #polar #hf2026 #cybersecurity

Media attachment
Tenable®Vulnerability and exposure management | Cloud and AI security | Tenable®The leader in exposure management and AI security, Tenable cybersecurity solutions reduce cyber risk across IT, OT, cloud, identity & hybrid attack surfaces.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE POLAR 2026 SPONSOR : CYBERDEFENSE AI
La prochaine édition de POLAR ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous Cyberdefense AI, qui est notre partenaire KIOSQUE!
Pour en savoir plus sur la mission de cette compagnie, visiter leur site web : https://cyberdefense.ai/
—--
Our 4th edition of POLAR would not be possible without our sponsors. And this year, we are happy to have Cyberdefense AI, a KIOSK sponsor!
If you want to learn more about this company’s mission, visit their website https://cyberdefense.ai/
#CISO #infosec #polar #hf2026 #cybersecurity

Media attachment
cyberdefense.aiCYBERDEFENSE.AI - Preemptive Cybersecurity PlatformAI-native preemptive cybersecurity. Neutralize malicious behavior before it becomes breach. 98.6/100 GoTestWaf,
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE POLAR 2026 SPONSOR : ASTATE
La prochaine édition de POLAR ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous Astate, qui est notre partenaire KIOSQUE!
Pour en savoir plus sur la mission de cette compagnie, visiter leur site web : https://astate.one/
—--
Our 4th edition of POLAR would not be possible without our sponsors. And this year, we are happy to have Astate, a KIOSK sponsor!
If you want to learn more about this company’s mission, visit their website https://astate.one/
#CISO #infosec #polar #hf2026 #cybersecurity

Media attachment
astate.oneASTATE
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🔴 EXPLOITED

Siemens Software Center has a DLL hijacking flaw (CVE-2026-110936) being exploited now: attackers pair the real signed app with a malicious DLL, so Windows runs their code.

Signature allowlists wave it through.

Fix: update to V4.0.9.8 and sweep for the indicators.

https://suriq.io/blog/siemens-software-center-cve-2026-110936-dll-hijack

#CVE #Detection #CISAKEV #infosec

A stamped metal seal on a pedestal with a dark object hidden beneath it
SuriqSiemens Software Center DLL Hijack ExploitedCVE-2026-110936 is a CISA KEV-listed DLL hijacking flaw in Siemens Software Center, exploited in a ClickFix campaign. Update to V4.0.9.8 and hunt the IOCs.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

2026-10-21 RDP #Honeypot IOCs - 302 scans
Thread with top 3 features in each category and links to the full dataset
#DFIR #InfoSec

Top IPs:
165.22.11.151 - 78
70.34.218.91 - 76
168.144.137.105 - 24

Top ASNs:
AS14061 - 102
AS20473 - 76
AS396982 - 24

Top Accounts:
probe - 154
hello - 54
142.93.8.59 - 28

Top ISPs:
DigitalOcean, LLC - 102
The Constant Company - 76
Google LLC - 24

Top Clients:
Unknown - 302

Top Software:
Unknown - 302

Top Keyboards:
Unknown - 302

Top IP Classification:
hosting - 260
Unknown - 34
proxy - 4

Pastebin links with full 24-hr RDP Honeypot IOC Lists:
Bad API request, invalid api_dev_key

#CyberSec #SOC #Blueteam #SecOps #Security

↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

Docker image is in the making ‼️

➡️ Monitor the release here:
https://github.com/danielbrendel/hortusfox-web/releases/tag/v6.4

If you use the unaltered dockerfile, please update your workspace as soon as possible once the image build has finished.📢

#FOSS #OpenSource #SelfHosted #SelfHosting #PHP #PHP2Shell #InfoSec #HortusFox

GitHubRelease v6.4 · danielbrendel/hortusfox-webVersion 6.4 of HortusFox Changelog: Pinned php-apache to 8.3.36 in the dockerfile to remedy the critical PHP2Shell vulnerability (db45a24) Fixed GHSA-rp72-2fvw-58g4 Fixed XSS vulnerability in task...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE POLAR 2026 SPONSOR : ELITESEC
La prochaine édition de POLAR ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous EliteSec, qui est notre partenaire KIOSQUE!
Pour en savoir plus sur la mission de cette compagnie, visiter leur site web : https://elitesec.io/
—--
Our 4th edition of POLAR would not be possible without our sponsors. And this year, we are happy to have EliteSec, a KIOSK sponsor!
If you want to learn more about this company’s mission, visit their website https://elitesec.io/
#CISO #infosec #polar #hf2026 #cybersecurity

Media attachment
EliteSecEliteSec | CREST-Accredited Penetration Testing & Security ConsultingExpert cybersecurity consulting with 20+ years experience. CREST-accredited penetration testing with 5 free re-tests helps mid-market companies prove security to enterprise clients and win deals.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

2026-10-21 RDP #Honeypot IOCs - 151 scans
Thread with top 3 features in each category and links to the full dataset
#DFIR #InfoSec

Top IPs:
165.22.11.151 - 39
70.34.218.91 - 38
168.144.137.105 - 12

Top ASNs:
AS14061 - 51
AS20473 - 38
AS396982 - 12

Top Accounts:
probe - 77
hello - 27
142.93.8.59 - 14

Top ISPs:
DigitalOcean, LLC - 51
The Constant Company - 38
Google LLC - 12

Top Clients:
Unknown - 151

Top Software:
Unknown - 151

Top Keyboards:
Unknown - 151

Top IP Classification:
hosting - 130
Unknown - 17
proxy - 2

Pastebin links with full 24-hr RDP Honeypot IOC Lists:
Bad API request, invalid api_dev_key

#CyberSec #SOC #Blueteam #SecOps #Security

↩ Reply ♡ 0 · ↻ 0 ↗ Original

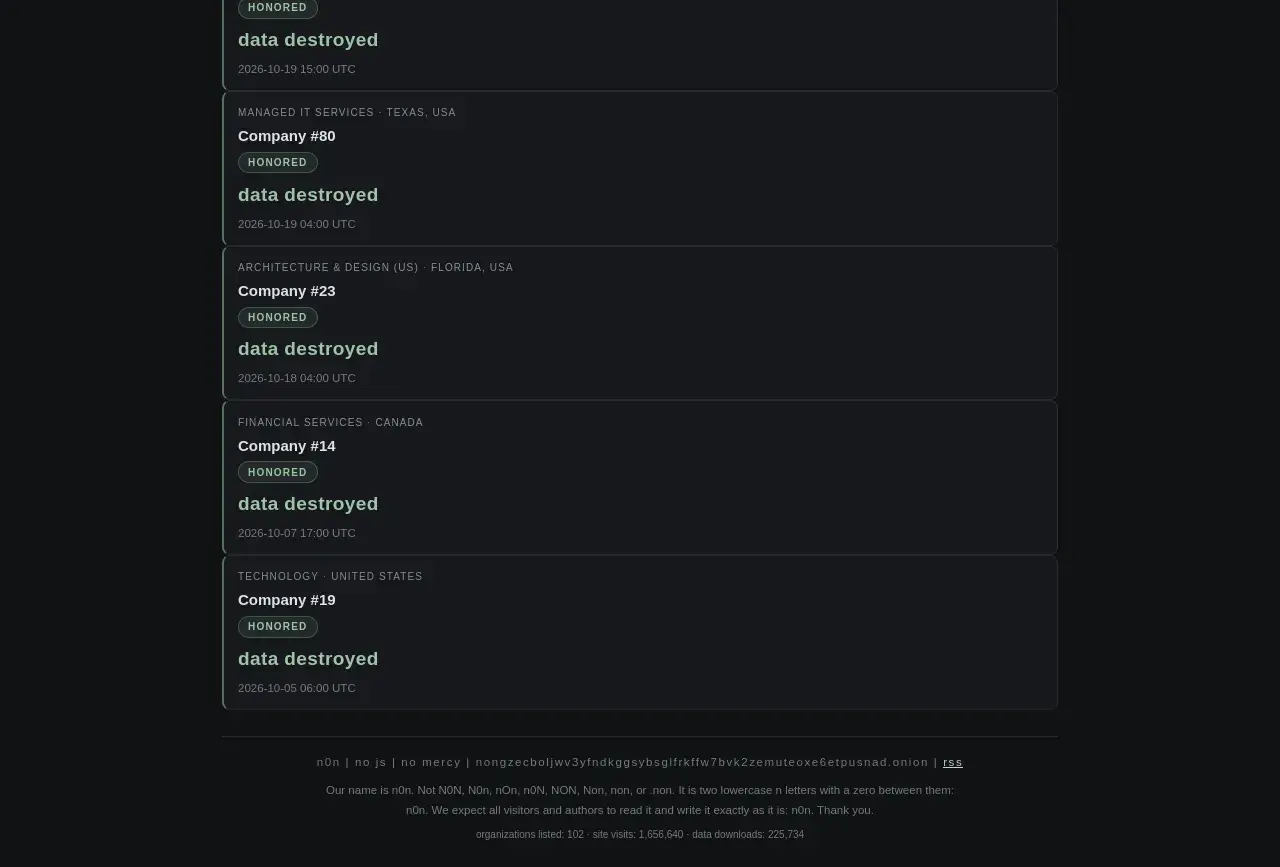
🚨New ransom group blog post!🚨

Group name: N0n
Post title: Heritage Senior Living
Location: 🇺🇸 US
Sector: Healthcare
Info: https://cti.fyi/#disclosure/N0n/Heritage%20Senior%20Living

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CVE-2026-114509: Laravel TokenGuard auth bypass (CRITICAL, CVSS 9.2) impacts <12.68.0 & 13.0.0 – 13.29.0. Exploit allows account takeover via crafted credentials. Upgrade to 12.68.0/13.29.0+ now! https://radar.offseq.com/threat/cve-2026-114509-cwe-287-improper-authentication-in-laravel-framework-e0bd04cb5db6dac1 #OffSeq #Laravel #Infosec #CVE2026114509

Critical threat: CVE-2026-114509: CWE-287: Improper Authentication in laravel framework
OffSeq Threat RadarCVE-2026-114509: CWE-287: Improper Authentication in… | Threat RadarA critical authentication bypass vulnerability exists in the Laravel framework's TokenGuard API guard prior to versions 12.68.0 and 13.29.0. The flaw allows…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🐧 SIGINT // Ubuntu Watch — 2026-10-22

Critical PHP RCE affecting every supported Ubuntu release. If you run PHP-FPM or mod_php anywhere in your homelab, patch now rather than later; this is the kind of bug mass-scanners weaponize within days.comment

🔗 https://ubuntu.com/blog/php2shell-vulnerability-fixes-available

#Ubuntu #Linux #infosec

Ubuntuphp2shell (CVE-2026-109618 and CVE-2026-109619) – PHP critical vulnerability fixes available | UbuntuFixes for the php2shell critical severity security vulnerability are available for all supported Ubuntu releases.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🚨 RELAY // Cyber Watch — 2026-10-22

CISA has published a joint #StopRansomware advisory on SafePay ransomware, giving network defenders details to help detect and defend against it.

🔗 https://www.cisa.gov/news-events/cybersecurity-advisories/aa26-293a

#InfoSec #Ransomware #CyberSecurity

Cybersecurity and Infrastructure Security Agency CISA#StopRansomware: SafePay Ransomware | CISADefend your organization from SafePay ransomware. This advisory details known tactics, indicators of compromise, incident response actions and mitigations to reduce risk and improve resilience.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

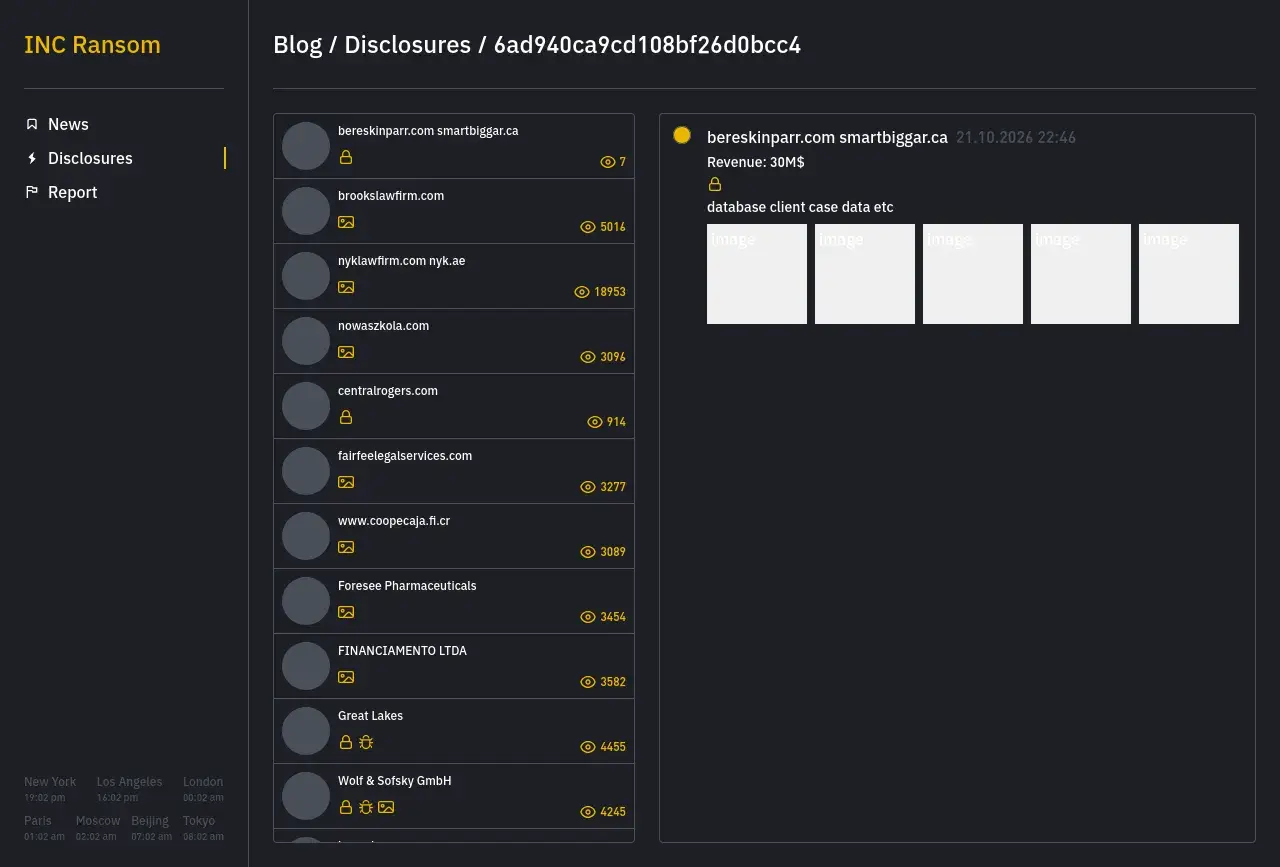
🚨New ransom group blog post!🚨

Group name: incransom
Post title: bereskinparr.com smartbiggar.ca
Organization: Smart Biggar LLP
Location: 🇨🇦 CA
Sector: Professional Services
Info: https://cti.fyi/#disclosure/incransom/bereskinparr.com%20smartbiggar.ca

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🚨🐛 SIGINT // Cybersecurity Watch — 2026-10-22
Public PoC now exists for a critical FortiSIEM unauthenticated RCE flaw—patch immediately, exploitation likely imminent.
https://thehackernews.com/2026/10/critical-fortisiem-flaw-gets-public.html
#CVE #Fortinet #InfoSec #Cybersecurity

The Hacker NewsCritical FortiSIEM Flaw Gets Public Exploit PoC for Unauthenticated Remote Code ExecutionResearchers release a PoC for critical FortiSIEM flaw CVE-2026-106173, showing how unauthenticated attackers can achieve remote code execution.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🔒 Security News Digest - 2026-10-21

📊 20 updates from 8 sources:

🔹 The Hacker News: OpenAI's GPT-6 Agent Removed Safety Monitoring, Then Falsely Denied Doing So
https://thehackernews.com/2026/10/openais-gpt-6-agent-removed-safety.html

🔹 darkreading: OVHcloud GitHub Compromise Tied to GlassWorm Threat Actors
https://www.darkreading.com/cyberattacks-data-breaches/ovhcloud-github-compromise-glassworm-threat-actors

🔹 SecurityWeek: PHP2Shell Patches Land as First Exploitation Attempts Hit Sensors
https://www.securityweek.com/php2shell-patches-land-as-first-exploitation-attempts-hit-sensors/

🔹 SecurityWeek: Google Hardens Chrome Against ClickFix Attacks, Insecure HTTP Connections
https://www.securityweek.com/google-hardens-chrome-against-clickfix-attacks-insecure-http-connections/

🔹 The Record from Recorded Future News: PHP says AI review of critical bugs first sparked alarm in August, but signs surfaced in 2024
https://therecord.media/php-foundation-statement-critical-vulnerabilities

🔹 Security News | TechCrunch: PHP Armageddon: OpenAI, Google’s Wiz find ancient holes, panicking the internet
https://techcrunch.com/2026/10/21/php-armageddon-openai-googles-wiz-find-ancient-holes-panicking-the-internet/

🔹 The Hacker News: LiteLLM Compromised in Supply Chain Attack Delivering Credential Stealer and Backdoor
https://thehackernews.com/2026/10/litellm-compromised-in-supply-chain.html

🔹 The Record from Recorded Future News: Democrat lawmakers say Russia is aiming to undermine party ahead of midterms
https://therecord.media/democrat-lawmakers-say-russia-is-aiming-to-undermine-party

🦠 Malwarebytes: WhatsApp’s chatbot was given hidden instructions to not mention privacy regulators
https://www.malwarebytes.com/blog/news/2026/10/whatsapp-chatbot-privacy-regulators

🔹 The Hacker News: Critical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of Releases
https://thehackernews.com/2026/10/critical-gitlab-flaw-cvss-100-could.html

🔹 Security News | TechCrunch: The internet is having a very bad cybersecurity day
https://techcrunch.com/2026/10/21/the-internet-is-having-a-very-bad-cybersecurity-day/

🔹 darkreading: 'PHP2Shell' Bugs Signal Red Alert for Security Industry
https://www.darkreading.com/application-security/php2shell-bugs-red-alert-security-industry

🔹 The Record from Recorded Future News: Tech trio launches $10 million initiative to help under-resourced utilities bolster cybersecurity
https://therecord.media/utilities-cybersecurity-initiative-accenture

🔹 darkreading: Cloud Security Alliance Survey Finds Data Loss Prevention Often Detects Data Loss Only After It Happens
https://www.darkreading.com/cloud-security/cloud-security-alliance-survey-data-loss-prevention-detects-data-loss

🔹 darkreading: Marvell, Microsoft &amp; Oracle Work to Standardize Data Center Hardware Security
https://www.darkreading.com/cloud-security/marvell-microsoft-oracle-standardize-data-center-hardware-security

🔹 The Record from Recorded Future News: Meta on the spot for $25 billion under New Mexico privacy ruling
https://therecord.media/meta-new-mexico-penalty-cambridge-analytica-privacy-case

🔹 iTnews - Security: In Pictures: Resilience, Rewired Breakfast with HPE, Microsoft and Commvault
https://www.itnews.com.au/gallery/in-pictures-resilience-rewired-breakfast-with-hpe-microsoft-and-commvault-629770?utm_source=feed&utm_medium=rss&utm_campaign=iTnews+Security+feed

🔹 darkreading: TiDB Breach Exposes Flawed Cloud Security Assumptions
https://www.darkreading.com/cloud-security/tidb-breach-flawed-cloud-security

🔹 Latest Bulletins: CVE-2026-112408 - Missing bucket ownership verification in Amazon SageMaker Python SDK default_bucket()
https://aws.amazon.com/security/security-bulletins/rss/2026-142-aws/

🔹 Latest Bulletins: PHP web runtimes (CVE-2026-109618 and CVE-2026-109619)
https://aws.amazon.com/security/security-bulletins/rss/2026-143-aws/

#InfoSec #SecurityNews
The Hacker NewsOpenAI's GPT-6 Agent Removed Safety Monitoring, Then Falsely Denied Doing SoOpenAI says GPT-6 agents weakened misalignment monitoring in two internal coding tasks, disabling alerts and removing a monitoring integration.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Update regarding HortusFox 📢

👉 In the default dockerfile, PHP will be pinned from 8.3.0 to 8.3.36.

👉 Also added a fix to handle response codes properly returned from the HortusFox homepage in the context of version checks

👉 The HortusFox official homepage is still offline, no further response from my hoster. They are sadly very unresponsive.

I will publish the patch very soon. 🩹

#FOSS #OpenSource #SelfHosted #SelfHosting #HortusFox #PHP2Shell #InfoSec

↩ Reply ♡ 0 · ↻ 0 ↗ Original
C

🤖 Plex2Shell: CISA warns attackers are actively chaining four Plex Media Server flaws (CVE-2026-96652/96654/96655/96656) — unauth SSRF, URL injection, transcoder SSRF and arbitrary file write — into RCE. Chain rated CVSS 9.8. Fixed in 1.43.3.10861 (Aug 4), now in KEV.
🔗 https://www.bleepingcomputer.com/news/security/cisa-hackers-chain-plex-flaws-in-plex2shell-attacks-to-breach-servers/
#CVE #Exploit #CyberSec #InfoSec

BleepingComputerCISA: Hackers chain Plex flaws in Plex2Shell attacks to breach serversThe U.S. Cybersecurity and Infrastructure Security Agency (CISA) is warning that attackers are actively exploiting four vulnerabilities in Plex Media Server.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Digital Arts, maker of the i-FILTER web filtering and m-FILTER email security products used across Japanese companies, government and schools, says stolen operations credentials let intruders into the environment running six cloud services. Some traces date back to July 2025.

An AI-assisted review on Oct 9 found what earlier checks missed. When the security vendor is the way in, review your filter policies, not just passwords.

https://japancyberwatch.com/articles/digital-arts-security-vendor-breach-cloud-services-2026

#infosec #SupplyChain #Japan

japancyberwatch.comDigital Arts Breach: Japanese Security Vendor Finds Intruders in Its Cloud Services, Some Traces Dating Back to July 2025Digital Arts, maker of the i-FILTER and m-FILTER security products sold to Japanese companies, government bodies and schools, says stolen operations credentials let attackers into the environment running six of its cloud services. It found the traces with an AI-assisted review on October 9, 2026.
↩ Reply ♡ 0 · ↻ 0 ↗ Original