CVE-2026-112371: CRITICAL code injection in H3C Magic NX15 (CVSS 9.4). Public exploit allows remote code execution via /api/esps. No patch yet — restrict device access. Details: https://radar.offseq.com/threat/cve-2026-112371-code-injection-in-h3c-magic-nx15-047130e6380b2198 #OffSeq #H3C #infosec #vulnerability
#InfoSEC
Public posts with this hashtag.
Possible Phishing 🎣
on: ⚠️hxxps[:]//nugtgsr222[.]weebly[.]com
🧬 Analysis at: https://urldna.io/scan/6ad60e223b77500007bd2ff8
#cybersecurity #phishing #infosec #urldna #scam #infosec
urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
ASN: AS14265
Location: Los Angeles, US
Added: 2026-10-17T12:02
🐧 SIGINT // Ubuntu Watch — 2026-10-20
Kernel escape vuln with real patching urgency. This roundup gives actual check commands and per-distro fix status for Ubuntu, Debian, RHEL, Proxmox - more actionable than the bare CVE entry for patching your fleet tonight.
🔗 https://smartscope.blog/en/blog/cve-2026-99999-pwnescape-linux-kernel-vulnerability-affected-2026/
SmartScopeCVE-2026-99999 (PwnEscape): Am I affected? Fix status for RHEL, Ubuntu, Debian, Amazon Linux and ProxmoxAm I affected by CVE-2026-99999 (PwnEscape)? Check commands and OS fix status for RHEL, Ubuntu, Debian, Amazon Linux, Proxmox VE and SUSE, including confirmed Debian, Amazon Linux and Proxmox kernels, unconfirmed fixes, and host update and reboot steps.
Possible Phishing 🎣
on: ⚠️hxxp[:]//cuddly-disco-alpha[.]vercel[.]app/
🧬 Analysis at: https://urldna.io/scan/6ad63ea43b77500002f4d890
#cybersecurity #phishing #infosec #urldna #scam #infosec
urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
Standard Chartered Group CISO on AI, Cyber Risk and the Future of Banking Security
CISOs are evolving from tech-only defenders to strategic business leaders. Standard Chartered's Group CISO emphasizes holistic cybersecurity accountability across tech, processes, and financial crime. Key shifts: integrating security into business ops, staying ahead of AI threats, and going beyond compliance. Success requires balancing technical expertise with business acumen while securing the entire ecosystem of clients and partners.
https://www.infosecurity-magazine.com/interviews/standard-chartered-group-ciso/
Infosecurity MagazineStandard Chartered Group CISO on AI, Cyber Risk and Banking SecurityCezary Piekarski says banking CISOs must look beyond regulatory compliance to stay ahead of evolving cyber threats and technology risks
🚨 RELAY // Cyber Watch — 2026-10-20
A breach of the OpenCode Console may have exposed users' OpenAI, Anthropic and Google API keys, so affected users should rotate their keys.
🔗 https://thehackernews.com/2026/10/opencode-console-breach-may-have.html
The Hacker NewsOpenCode Console Breach May Have Exposed OpenAI, Anthropic, and Google API KeysOpenCode says a Console breach may have exposed AI provider keys belonging to 1.4% of users, prompting revocation notices.
🔒 Security News Digest - 2026-10-19
📊 8 updates from 4 sources:
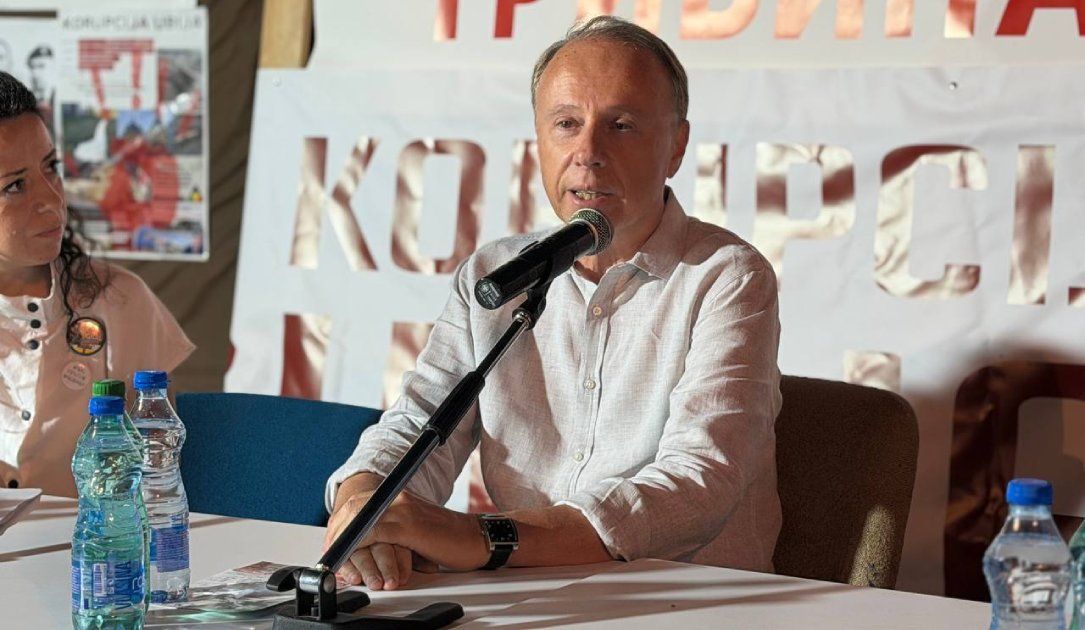
🔹 The Record from Recorded Future News: Two more Serbian opposition figures targeted with spyware, researchers say
https://therecord.media/serbia-spyware-pegasus-elections
🔹 darkreading: ConnectWise Disables Cloud Backups Amid Concerns for Downstream MSPs
https://www.darkreading.com/identity-access-management-security/connectwise-disables-cloud-backups-downstream-msps
🔹 The Record from Recorded Future News: ConnectWise suspends Cloud Backup service after supply chain attack
https://therecord.media/connectwise-suspends-cloud-backup-service-supply-chain-attack
🔹 The Record from Recorded Future News: Judge denies WhatsApp’s bid to hold spyware maker in contempt for allegedly targeting users
https://therecord.media/whatsapp-denied-appeal-alleged-nso-group-violation-injunction
🔹 darkreading: 'AdFection' Turns Ad Impressions Into Zero-Click Spyware Delivery
https://www.darkreading.com/data-privacy/adfection-online-ads-spyware-delivery
🔹 iTnews - Security: Ex-OpenAI employee accused of planting device appears to have Saudi backing
https://www.itnews.com.au/news/ex-openai-employee-accused-of-planting-device-appears-to-have-saudi-backing-629760?utm_source=feed&utm_medium=rss&utm_campaign=iTnews+Security+feed
🔹 darkreading: Researchers Infiltrate Microsoft Tech Support Scam Operation
https://www.darkreading.com/threat-intelligence/microsoft-tech-support-scam-operation
🔹 Unit 42: Threat Brief: Active Exploitation of PAN-OS CVE-2026-0257 (Updated October 19)
https://unit42.paloaltonetworks.com/active-exploitation-of-pan-os-cve-2026-0257/
therecord.mediaTwo more Serbian opposition figures targeted with spyware, researchers sayA phone belonging to the rector of the University of Belgrade was discovered to have been infected with Pegasus spyware, the latest in a series of such discoveries in the lead-up to Serbia's national elections.
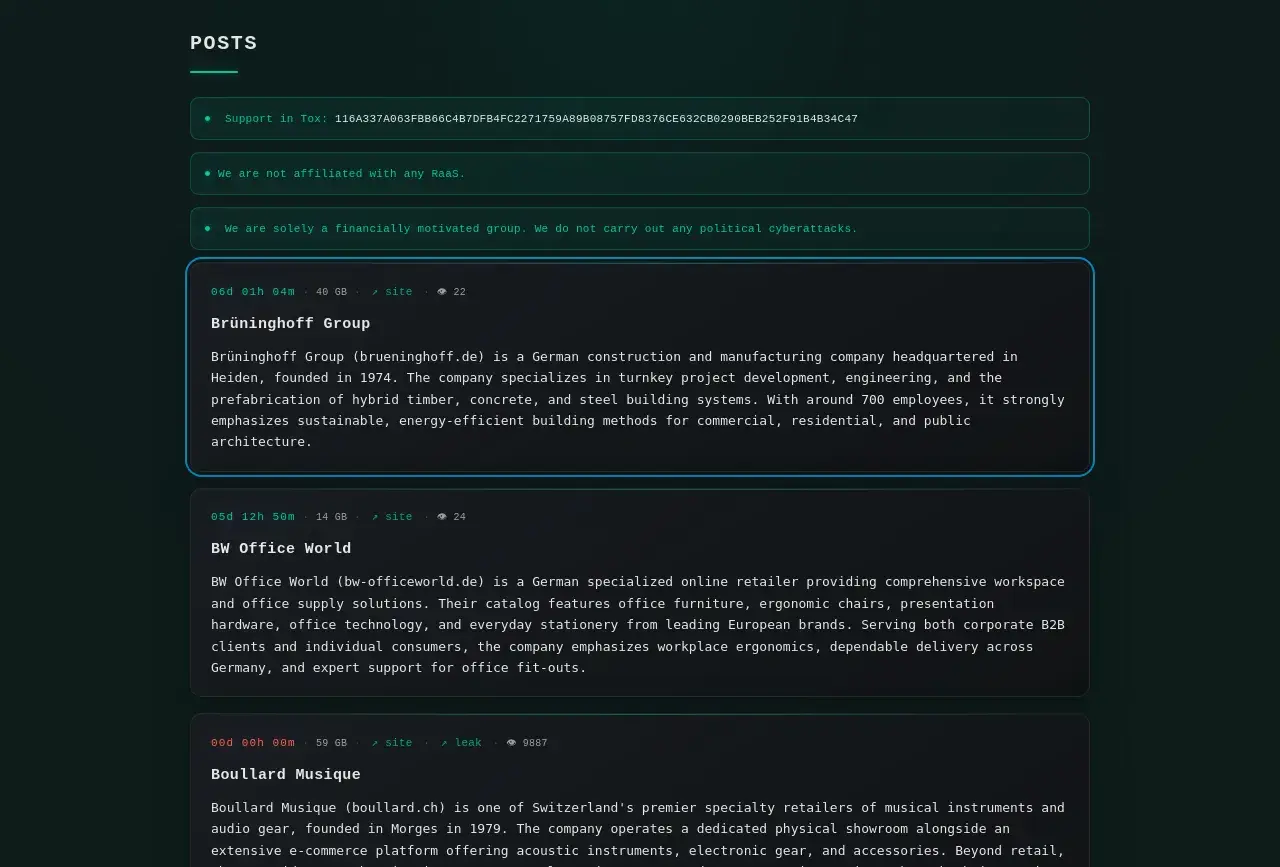
🚨New ransom group blog posts!🚨
Group name: payload
Post title: Brüninghoff Group
Location: 🇩🇪 DE
Sector: Construction
Info: https://cti.fyi/#disclosure/payload/Br%C3%BCninghoff%20Group
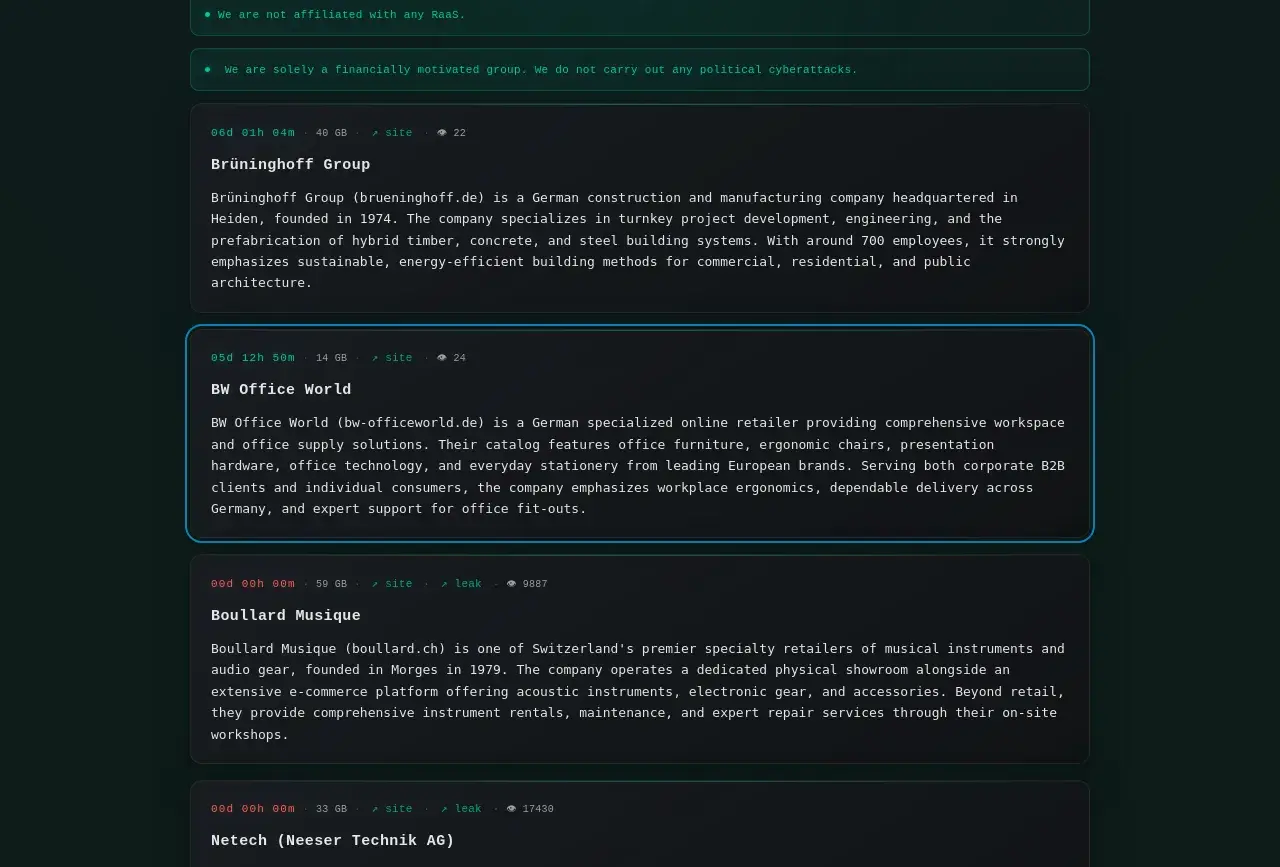
Group name: payload
Post title: BW Office World
Location: 🇩🇪 DE
Sector: Other
Info: https://cti.fyi/#disclosure/payload/BW%20Office%20World
#ransomware #cti #threatintelligence #cybersecurity #infosec
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
🚨🔓 SIGINT // Cybersecurity Watch — 2026-10-20
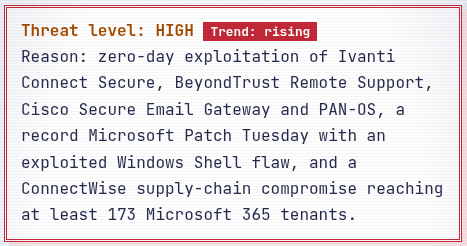
Compromised ConnectWise credential let attackers sign into 173 Microsoft 365 tenants, exposing deep supply-chain risk in MSP tooling.
https://thehackernews.com/2026/10/hackers-use-compromised-connectwise.html
#Cybersecurity #SupplyChain #Microsoft365 #InfoSec
The Hacker NewsHackers Use Compromised ConnectWise Credential to Sign In to 173 Microsoft 365 TenantsAttackers used a compromised ConnectWise Cloud Backup credential for unauthorized sign-ins across 173 Microsoft 365 tenants.
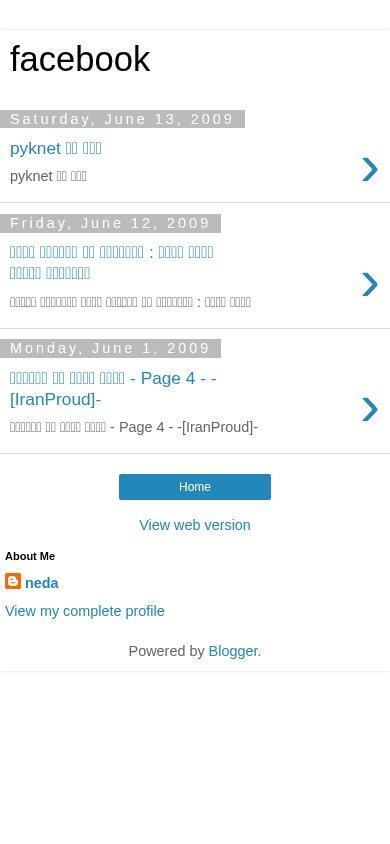
Possible Phishing 🎣
on: ⚠️hxxps[:]//neda-facebook[.]blogspot[.]com
🧬 Analysis at: https://urldna.io/scan/6ad5f8b63b77500006fb743a
#cybersecurity #phishing #infosec #urldna #scam #infosec
urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
Spend vs. debt: what's the bigger security risk?
More cybersecurity spending doesn't mean better security. Organizations accumulate "security debt" through complexity & unnecessary controls, increasing fragility. Experts advocate for automation & tool integration over adding more layers. Real risk management measures resilience, not just compliance. CISOs must communicate cyber threats in business terms—revenue impact, recovery ability—to engage boards effectively. 🔒
https://www.cio.com/article/4233353/spend-vs-debt-whats-the-bigger-security-risk.html
CIOSpend vs. debt: what’s the bigger security risk?Organizations continue investing heavily in cybersecurity, yet many are simultaneously increasing operational complexity and long-term security fragility. Here, Joan Goodchild from CSO speaks with veteran CISO Selim Aissi about security debt and why it may be a more meaningful measure of cyber risk than security budget size alone.
In Japan, the ransomware name everyone knows is Qilin, thanks to the Asahi attack.
On the leak sites, 2026 belongs to The Gentlemen: 23 Japanese organizations listed this year (ransomware.live), vs 15 for Qilin. Group-IB says it grew out of a Qilin affiliate team, and it hands affiliates compromised FortiGates.
The brand changes; the way in doesn't.
https://japancyberwatch.com/articles/japan-ransomware-groups-2026-the-gentlemen-qilin
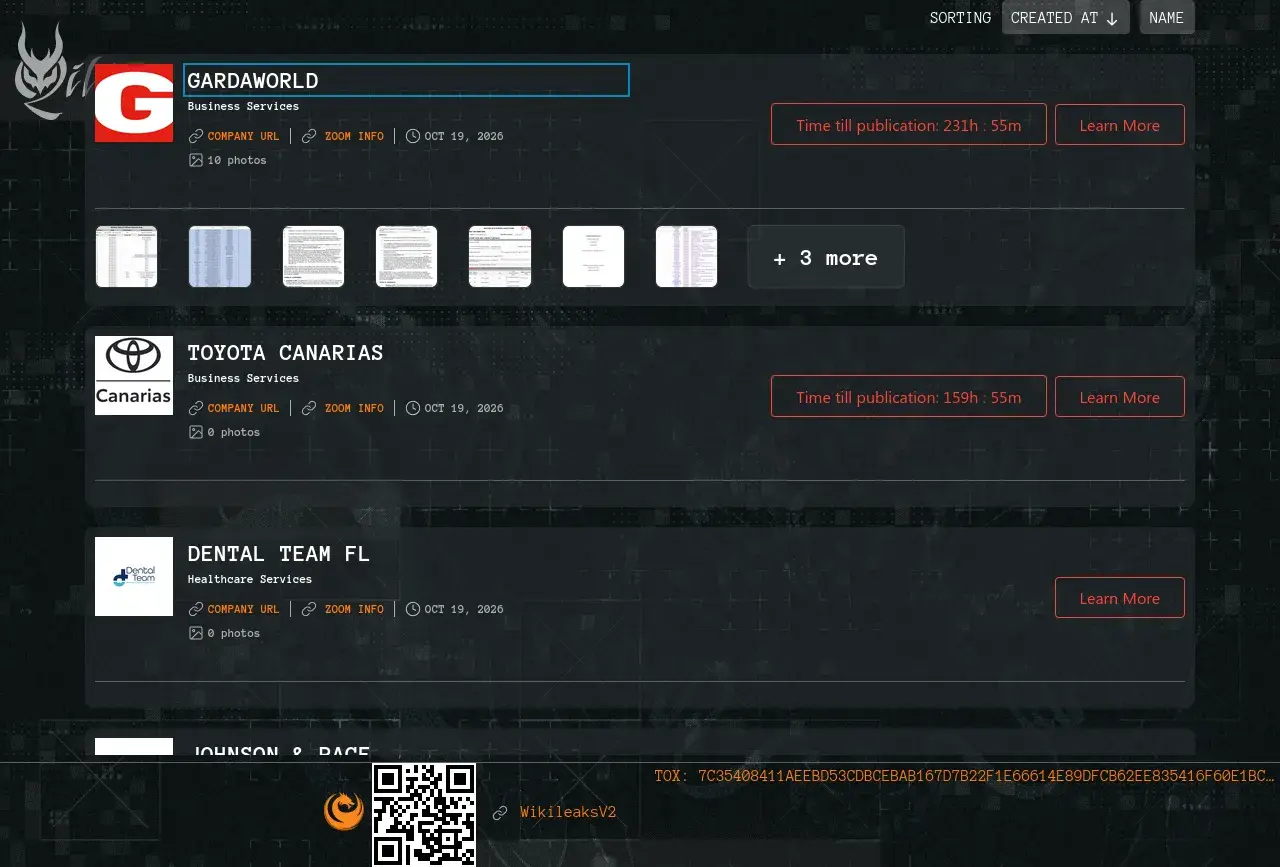
🚨New ransom group blog post!🚨
Group name: qilin
Post title: GardaWorld
Location: 🇨🇦 CA
Sector: Professional Services
Info: https://cti.fyi/#disclosure/qilin/GardaWorld
#ransomware #cti #threatintelligence #cybersecurity #infosec
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
Possible Phishing 🎣
on: ⚠️hxxps[:]//us02webzoomus[.]com/invite[.]php
🧬 Analysis at: https://urldna.io/scan/6ad5ea403b77500004c2bc66
#cybersecurity #phishing #infosec #urldna #scam #infosec
urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
ASN: AS265919
Location: Cotia, BR
Added: 2026-10-17T12:05
CVE-2026-112302 is a path traversal vulnerability in the ZIP extraction function of the kiwilan php-archive PHP library. Versions up to 2.3.02 are affected.

A public exploit is circulating per VulDB. No vendor fix is available, and kiwilan has not responded to the disclosure.
Cybersecurity is a leadership problem: Why the management model needs to catch up
Cybersecurity fails when treated as just a tech problem. The real issue? Leadership. CISOs can't do it alone—organizations need clear accountability, cross-level collaboration, and board involvement. Better tools mean nothing without proper governance and sustained management discipline. It's time to break the cycle.
CSO OnlineCybersecurity is a leadership problem: Why the management model needs to catch upWe keep buying better security tech, but the real gaps are ownership and follow-through, so cybersecurity can’t stay the CISO’s problem alone.
Possible Phishing 🎣
on: ⚠️hxxps[:]//bradesco-validacao[.]digital
🧬 Analysis at: https://urldna.io/scan/6ad64cb13b77500009d2816d
#cybersecurity #phishing #infosec #urldna #scam #infosec
urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
ASN: AS7506
Location: Tokyo, JP
Added: 2026-10-17T11:51
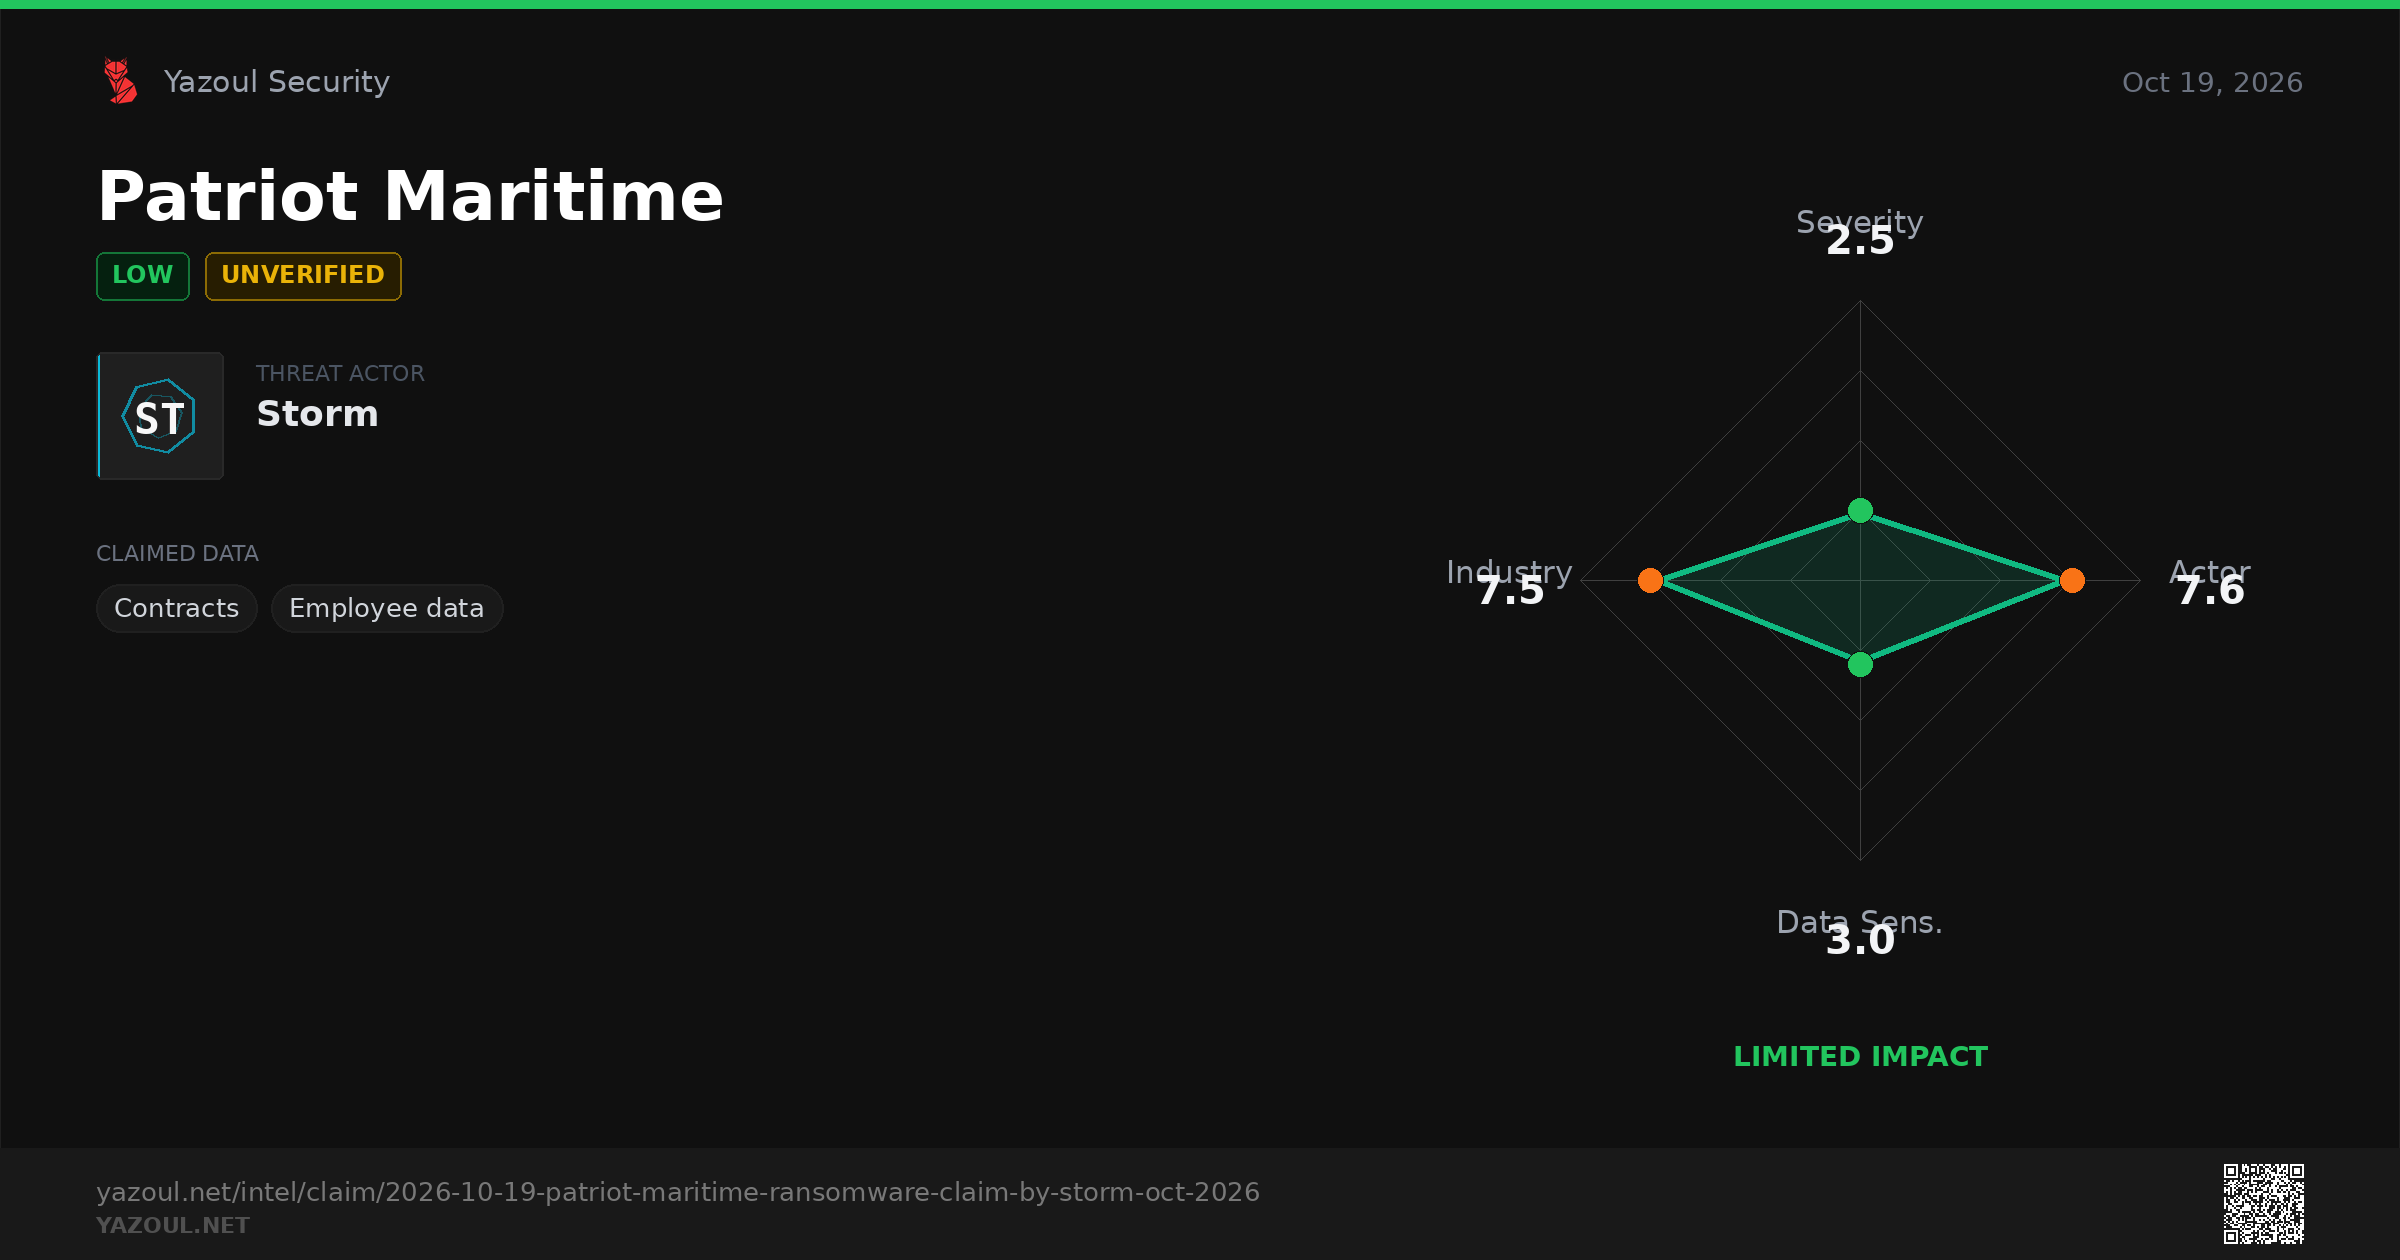
🛡 THREAT INTEL | Patriot Maritime
🟢 Actor "Storm" claims Undisclosed
Allegedly exposed
• Contracts
• Employee data
⚠️ Unverified claim
https://www.yazoul.net/intel/claim/2026-10-19-patriot-maritime-ransomware-claim-by-storm-oct-2026
by Yazoul AI
Yazoul SecurityPatriot Maritime Ransomware Claim by Storm (Oct 2026)Storm ransomware group allegedly claims Patriot Maritime as a victim, threatening sensitive maritime contractor data. Read our unverified threat intel analysis now.
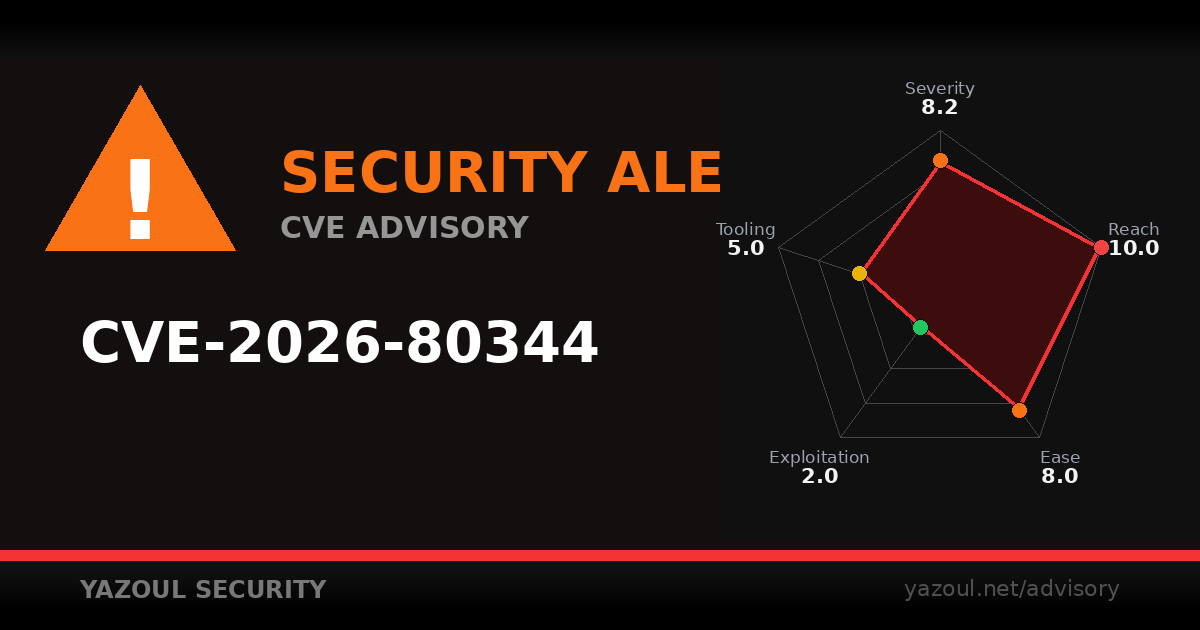
⚠️ New security advisory:
CVE-2026-80344 affects multiple systems.
• Impact: Significant security breach potential
• Risk: Unauthorized access or data exposure
• Mitigation: Apply patches within 24-48 hours
Full breakdown:
https://www.yazoul.net/advisory/cve/cve-2026-80344-apache-camel-as2-ssrf-enables-internal-network-access-poc
by Yazoul AI
Yazoul SecurityApache Camel AS2 SSRF enables internal network access (CVE-2026-80344) [PoC]CVE-2026-80344: Apache Camel AS2 SSRF (CVSS 8.2) lets remote senders pick the MDN destination host and leak credentials. Update to 4.23.0, 4.18.5, or 4.22.1.
🧪 NEW BETA RELEASES 🧪
📱 iOS 27.2 RC (24B115)
📱 iPadOS 27.2 RC (24B115)
💻 macOS 27.2 RC (26B118)
📺 tvOS 27.2 RC (24K120)
🥽 visionOS 27.2 RC (24N118)
⌚ watchOS 27.2 RC (24S116)
🔨 Xcode 27.2 RC (27B48)
Tech took a beating this past week. It was the main target for attackers (ranking #2 out of 12 sectors) with 193 stories hitting the wire.
Possible Phishing 🎣
on: ⚠️hxxps[:]//sites[.]google[.]com/view/webmaillogin09/home
🧬 Analysis at: https://urldna.io/scan/6ad5d5cb3b77500008d7e84e
#cybersecurity #phishing #infosec #urldna #scam #infosec
urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
The 7 biggest issues CISOs and security teams face today
Security leaders face mounting pressure as AI-driven cyberattacks surge. 68% of CISOs report increased stress, with 73% unprepared for major breaches. The shift from prevention to resilience is critical—78% view generative AI as a security risk. Key priorities: close the 95% skills gap, strengthen AI infrastructure security, align programs with org needs, and maintain foundational practices.
CSO OnlineThe 7 biggest issues CISOs and security teams face todayFrom escalating AI-enabled threats to persistent skills gaps, security leaders are reshaping their agendas to address several key long-standing and emerging concerns.
This dumb password rule is from Crédit Agricole Centre-Est.
You have to enter your 6-digit password using this Frenchy keypad.
https://dumbpasswordrules.com/sites/credit-agricole-centre-est/
#password #passwords #infosec #cybersecurity #dumbpasswordrules
dumbpasswordrules.comCrédit Agricole Centre-Est - Dumb Password RulesYou have to enter your 6-digit password using this Frenchy keypad.
ASN: AS3462
Location: Taipei, TW
Added: 2026-10-17T12:02
Possible Phishing 🎣
on: ⚠️hxxp[:]//dempiremanagement[.]com/owa[.]auth[.]logo[.]aspx
🧬 Analysis at: https://urldna.io/scan/6ad63eb33b77500002f4d892
#cybersecurity #phishing #infosec #urldna #scam #infosec
urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test