#Plex
Public posts with this hashtag.

Self-Host Weekly (23 October 2026)
#PHP stuff, software updates and launches, a spotlight on #PatchMon - a #Linux fleet patch monitoring system, and more in this week's #selfhosted recap!
https://selfh.st/weekly/2026-10-23/
#selfhost #selfhosting #opensource #foss #homelab #server #newsletter #ai #plex #jellyfin #homeassistant #smarthome #privacy #fediverse #mastodon #sysadmin #devops #development #strands #puzzle #software #app #apps
 selfh.stSelf-Host Weekly (23 October 2026)Shell shocked

More detail: https://news.ycombinator.com/item?id=50186318

Reward: You've received a Commemorative Unpatched Codecs Directory — filled with someone else's binaries.
https://thehackernews.com/2026/10/hackers-exploit-plex2shell-flaws-to.html
#Plex #CyberSecurity #Ransomware #ZeroDay #CryptoMiner #PatchedOrPerish (3/3)
 The Hacker NewsHackers Exploit Plex2Shell Flaws to Install Crypto Miners and Linux Proxy BackdoorAttackers exploit four Plex Media Server flaws chained as Plex2Shell to deploy XMRig miners and reverse proxy software after PoC release.

📻 ■ Aitana desarrolla una nueva faceta muy influenciada por Plex: “Esto no os lo esperabais” ■
https://los40.com/2026/10/21/aitana-desarrolla-una-nueva-faceta-muy-influenciada-por-plex-esto-no-os-lo-esperabais/?int=MASTODON_WORLD
 LOS40Aitana desarrolla una nueva faceta muy influenciada por Plex: “Esto no os lo esperabais” | Música | LOS40La cantante se encuentra de gira por Latinoamérica y más conectada que nunca
3 vulnerabilities added to CISA's Known Exploited Vulnerabilities catalog:
- #CVE_2026_106931: EG Secure Solutions SiteGuard Server Edition OS Command Injection Vulnerability
- #CVE_2026_96656: Plex Media Server External Control of File Name or Path Vulnerability
- #CVE_2026_96655: Plex Media Server Server-Side Request Forgery (SSRF) Vulnerability
 overflo.wsKnown exploitedEvery vulnerability in CISA's Known Exploited Vulnerabilities catalog, newest first, with EPSS scores and affected products.
🚨 Rapid Response: Four vulnerabilities in Plex Media Server can be chained to achieve unauthenticated remote code execution. Plex reports compromised servers being used to run cryptocurrency miners and proxy software.
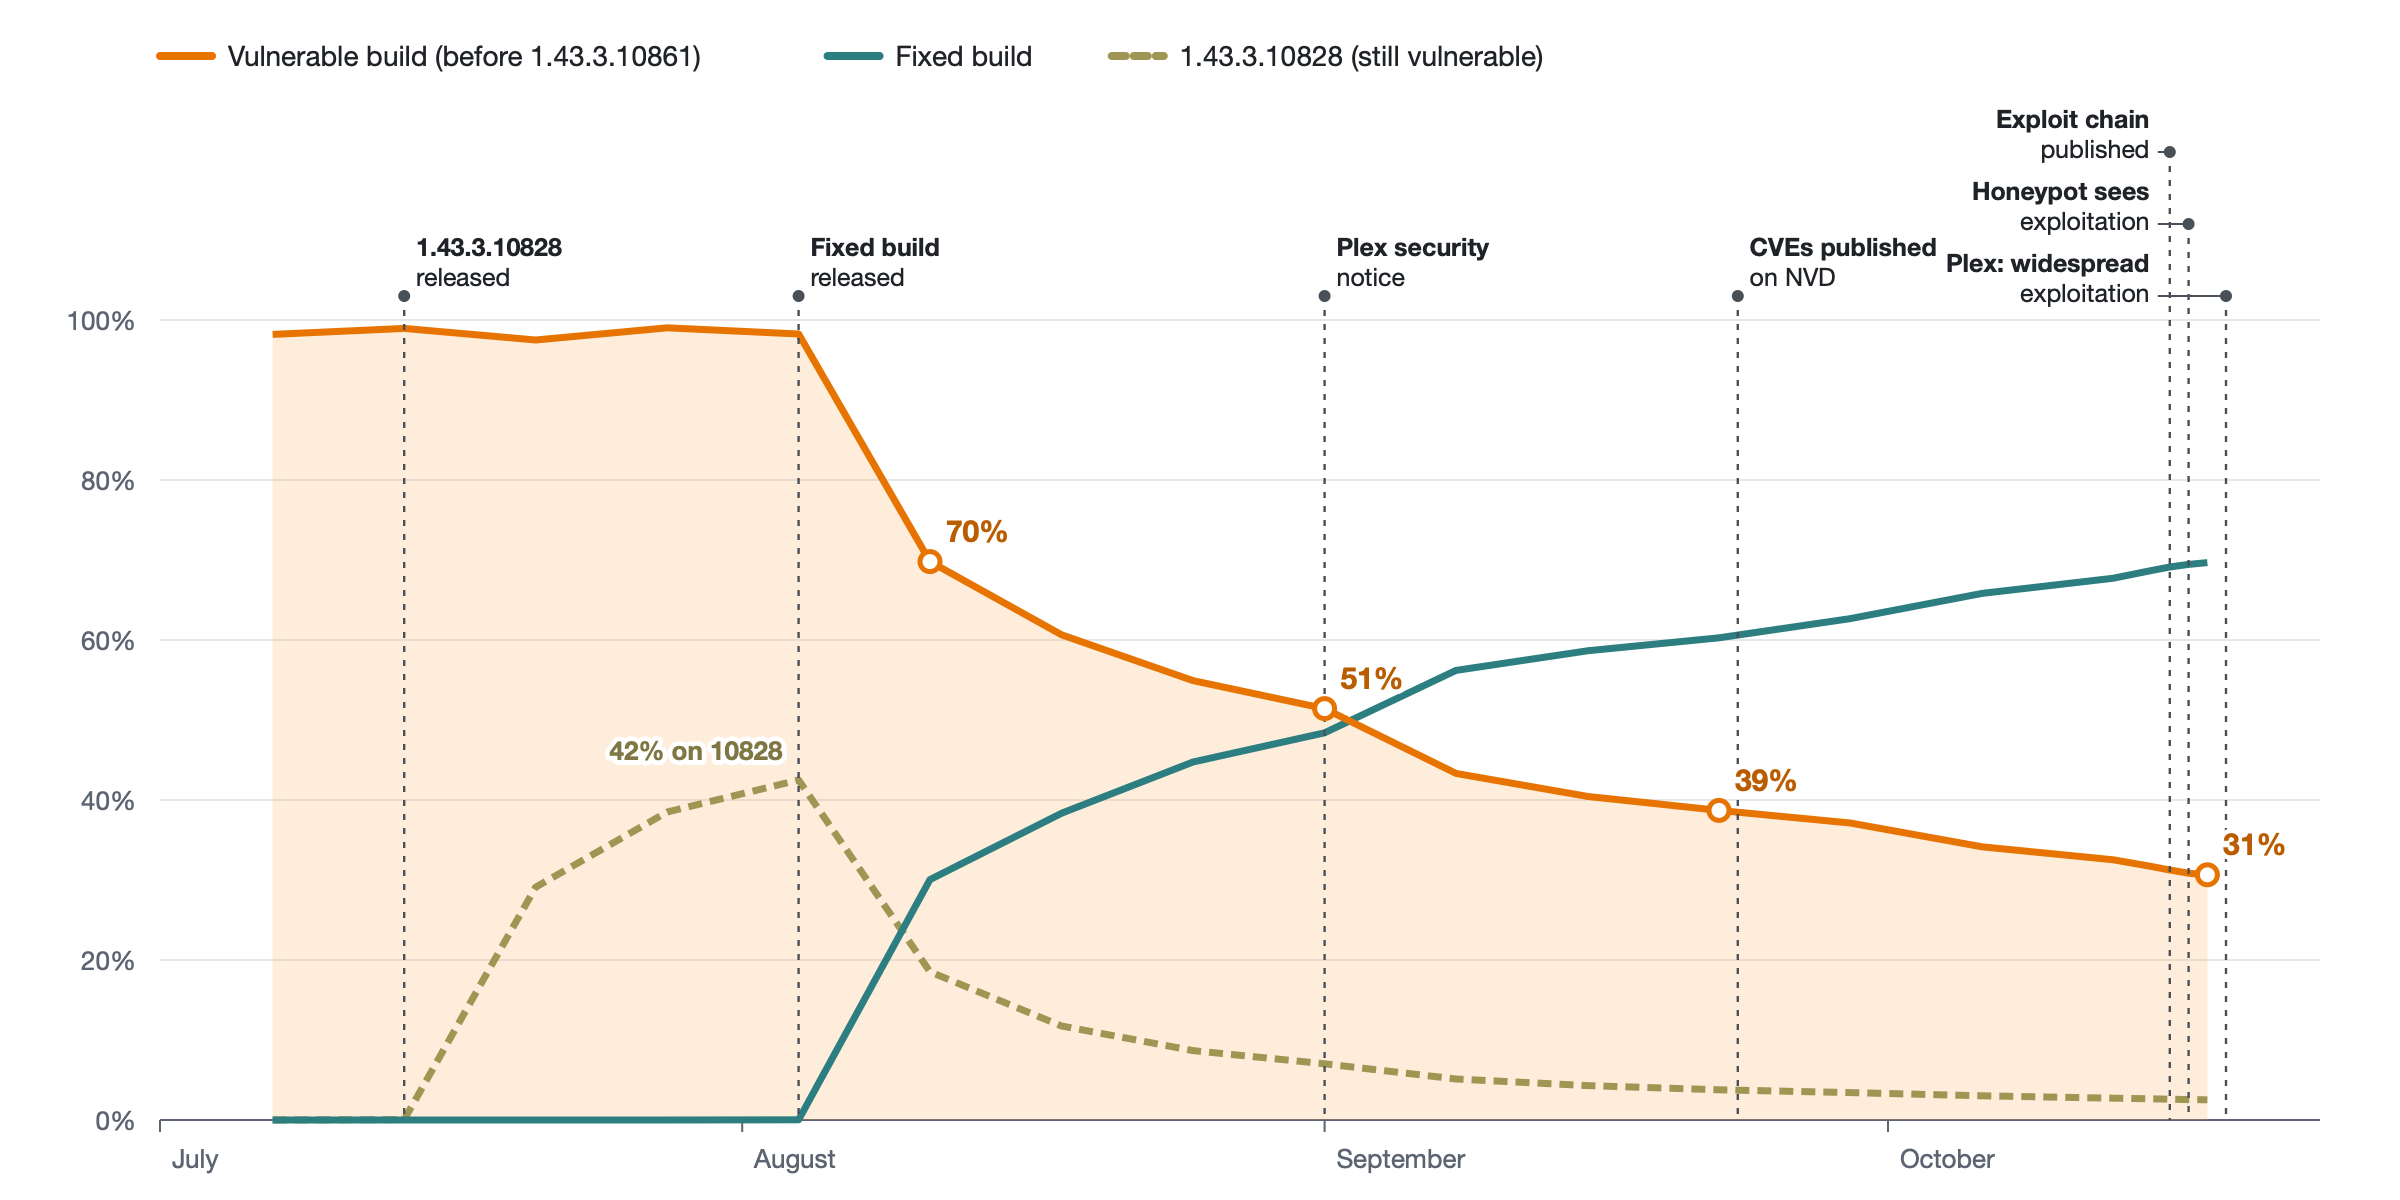
Censys ARC observes ~340,000 Internet-exposed Plex Media Server hosts. Roughly 30% run a vulnerable build, and nearly 8,000 run an early build that may be mistaken for patched.
Despite publication of the exploit chain and reports of exploitation, fewer than 2% of still-vulnerable hosts upgraded in the following three days.
Plex advises that previously exposed, unpatched servers may already be compromised and require additional remediation beyond patching.
Full Censys ARC advisory: https://censys.com/advisory/cve-2026-96652-cve-2026-96654-cve-2026-96655-cve-2026-96656/
#CensysARC #Cybersecurity #VulnerabilityManagement #Plex #InfoSec
 CensysOctober 20 Advisory: Plex Media Server Remote Code Execution Chain [CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, CVE-2026-96656] - CensysCVE-2026-96652, CVE-2026-96654, CVE-2026-96655, and CVE-2026-96656 are four flaws in Plex Media Server before build 1.43.3.10861.
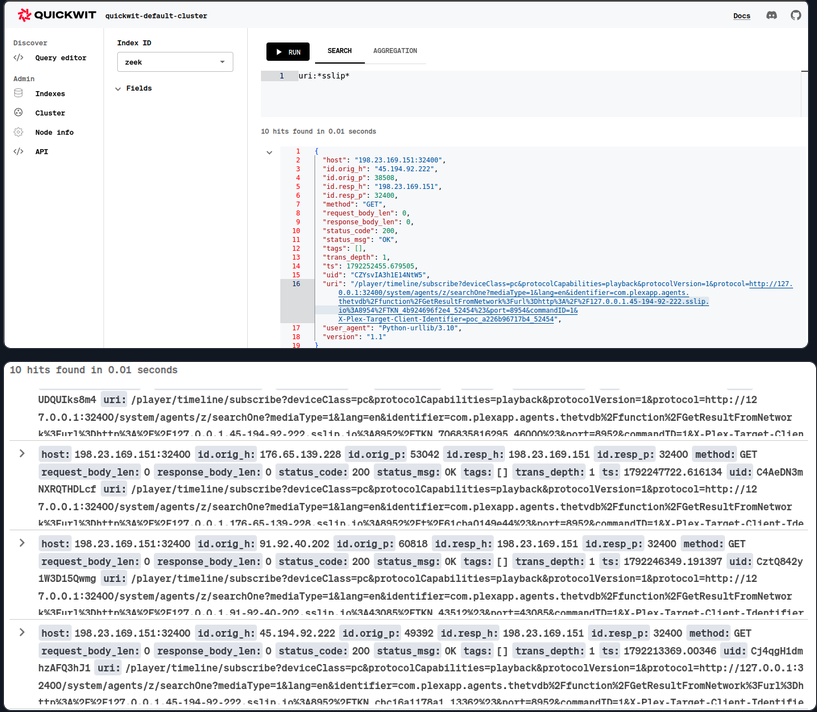
Plex shipped fixes in 1.43.3 by Sep 1, yet one researcher's honeypot running a vulnerable version was exploited on Oct 17, a day after the Plex2Shell chain (CVE-2026-96652, -96654, -96655, -96656) went public. He saw an XMRig miner and a proxy tool dropped. Plex's Sep 1 notice listed no CVEs, and Plex did not immediately respond to Ars Technica.
https://www.boredhackerblog.info/2026/10/plex-vulnerabilities-being-exploited-in.html
 www.boredhackerblog.infoPlex vulnerabilities being exploited in the wild to drop a cryptominerIntro: (No AI was involved in writing, research, etc...) If you see weird fonts and spacing, blame Blogger. Skip to "In the wild exploitati...

#Plex2Shell Exploit Used to Turn Vulnerable #Plex Servers Into Crypto Miners
https://securityaffairs.com/201324/hacking/plex2shell-exploit-used-to-turn-vulnerable-plex-servers-into-crypto-miners.html
#securityaffairs #hacking
 Security AffairsPlex2Shell Exploit Used to Turn Vulnerable Plex Servers Into Crypto Miners - Security AffairsAttackers exploit Plex2Shell flaws to install crypto miners and proxy software. Admins should update their Plex Media Server.