X XFediYour place in the Fediverse
XFEDI

#digitalforensics

ActivityPub

Public posts with this hashtag.

When people say: "I can always tell an AI photo" usually means "I notice the bad ones". That's what it means to me today.

The usual advice is to count the fingers, check the teeth and earrings, and look for nonsense text in the background. It was good advice a couple of years ago. However, every new generator fixes exactly the "tells" people talk about.

Detection that works is trained: samples of real and generated content, compared until something separates them. It beats the human eye by a long way, but a detector can only recognise what it has been shown.

That is the problem with the arms race:
- Stable Diffusion's founder estimated its 2022 training compute at about US$600k (256 GPUs, ~150k GPU-hours); he put DALL-E 2 at roughly 1M GPU-hours
- Stanford's AI Index: ~US$78M of compute for GPT-4, ~US$191M for Gemini Ultra
- Epoch AI: hardware is roughly half to two-thirds of a frontier model's cost, staff 29–49%
- 2025 deepfake-detection rounds I could find: tens of millions
- Running a model once it exists: our 17-second explainer video took one GPU, ~5 hours, under A$10 (~US$6.50), open-licensed models

The risk that worries me most: a private generator with only a handful of images ever released. Nothing to train on, no detector has seen it, and eyeballing won't catch it. Worse if it also forges a camera's metadata and fingerprint, which works for cameras that don't protect their output. Camera makers are now signing and watermarking at the hardware level, so imitating that means breaking the protection, not copying a few EXIF fields.

So what still works? There's a check most people never think of: instead of trying to prove a photo is AI, try to prove it's real. It often tells you more, and it doesn't care which generator made the fake.

The full article covers how that works, why a screenshot or a forward can wipe out the evidence, the one thing I would tell anyone asked to judge a photo, the cost breakdown with sources, and the guides we wrote for each question people send me:

https://kennethbspringer.au/2026/10/21/is-this-photo-real-why-ai-is-making-that-harder-to-answer/?utm_source=mastodon&utm_medium=social&utm_campaign=article-26

#AI #Deepfakes #DigitalForensics #DFIR #ContentAuthenticity #infosec
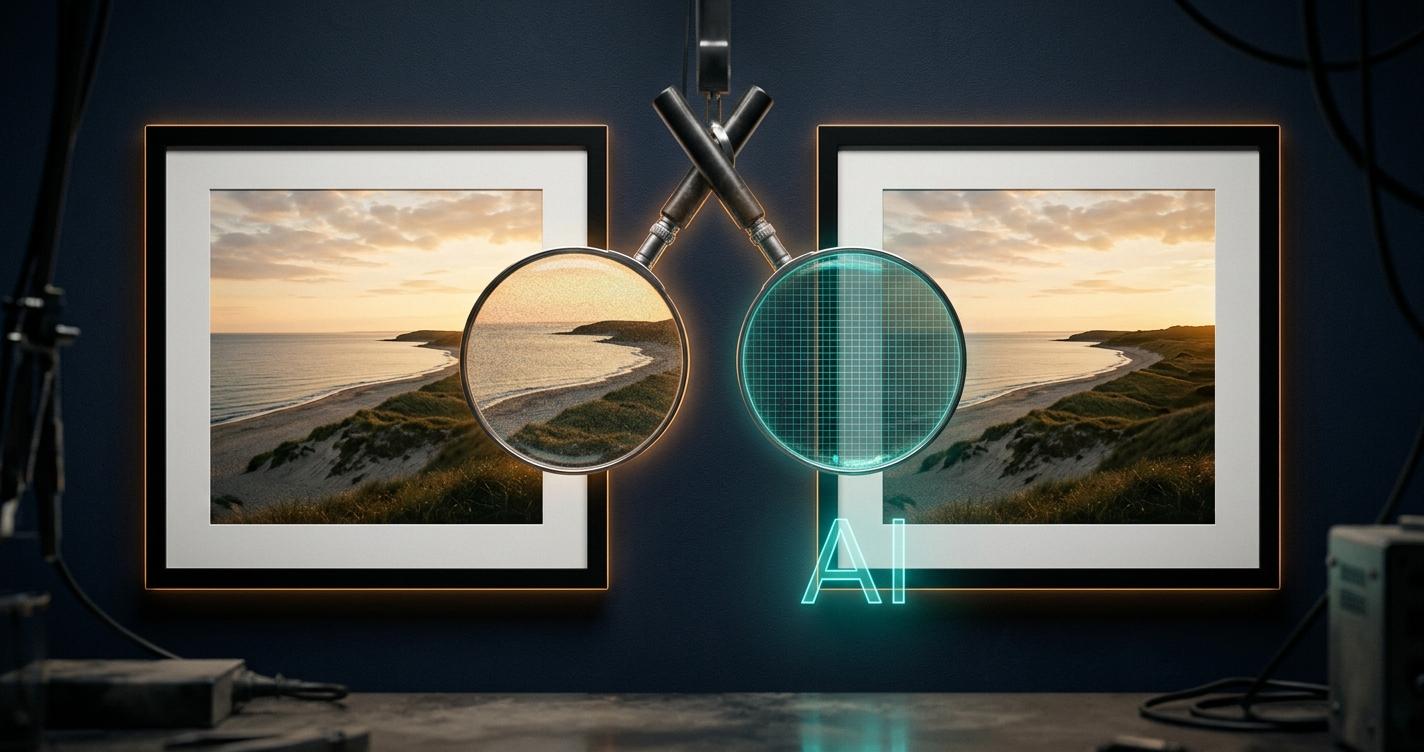
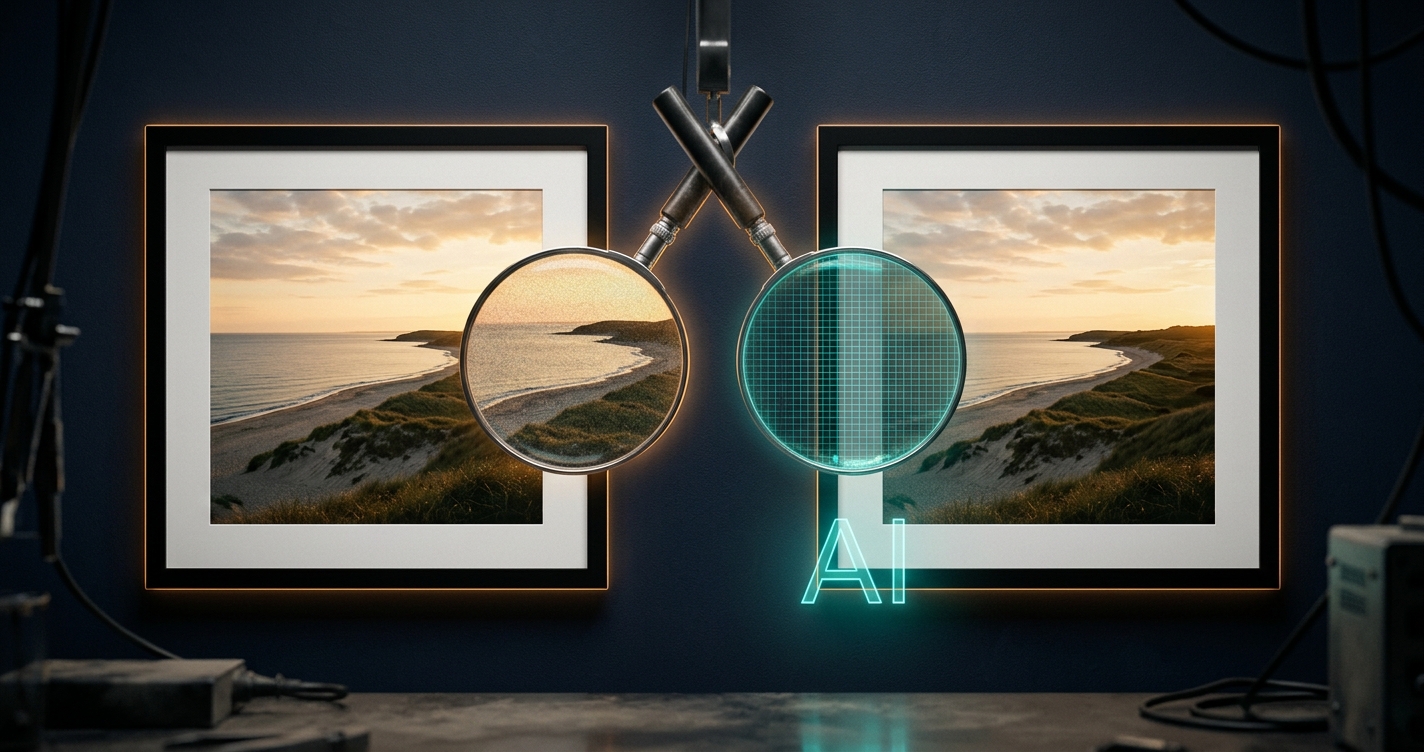
Which is real or fake illustration. Two magnifying glasses one over real and the other over AI generated, both looks the same, hard to tell the difference
kennethbspringer.auIs This Photo Real? Why AI Is Making That Harder to Answer — Kenneth B. SpringerCan you still spot an AI photo by eye? Why detection is getting harder, what it costs to build a generator, and the checks that still work.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

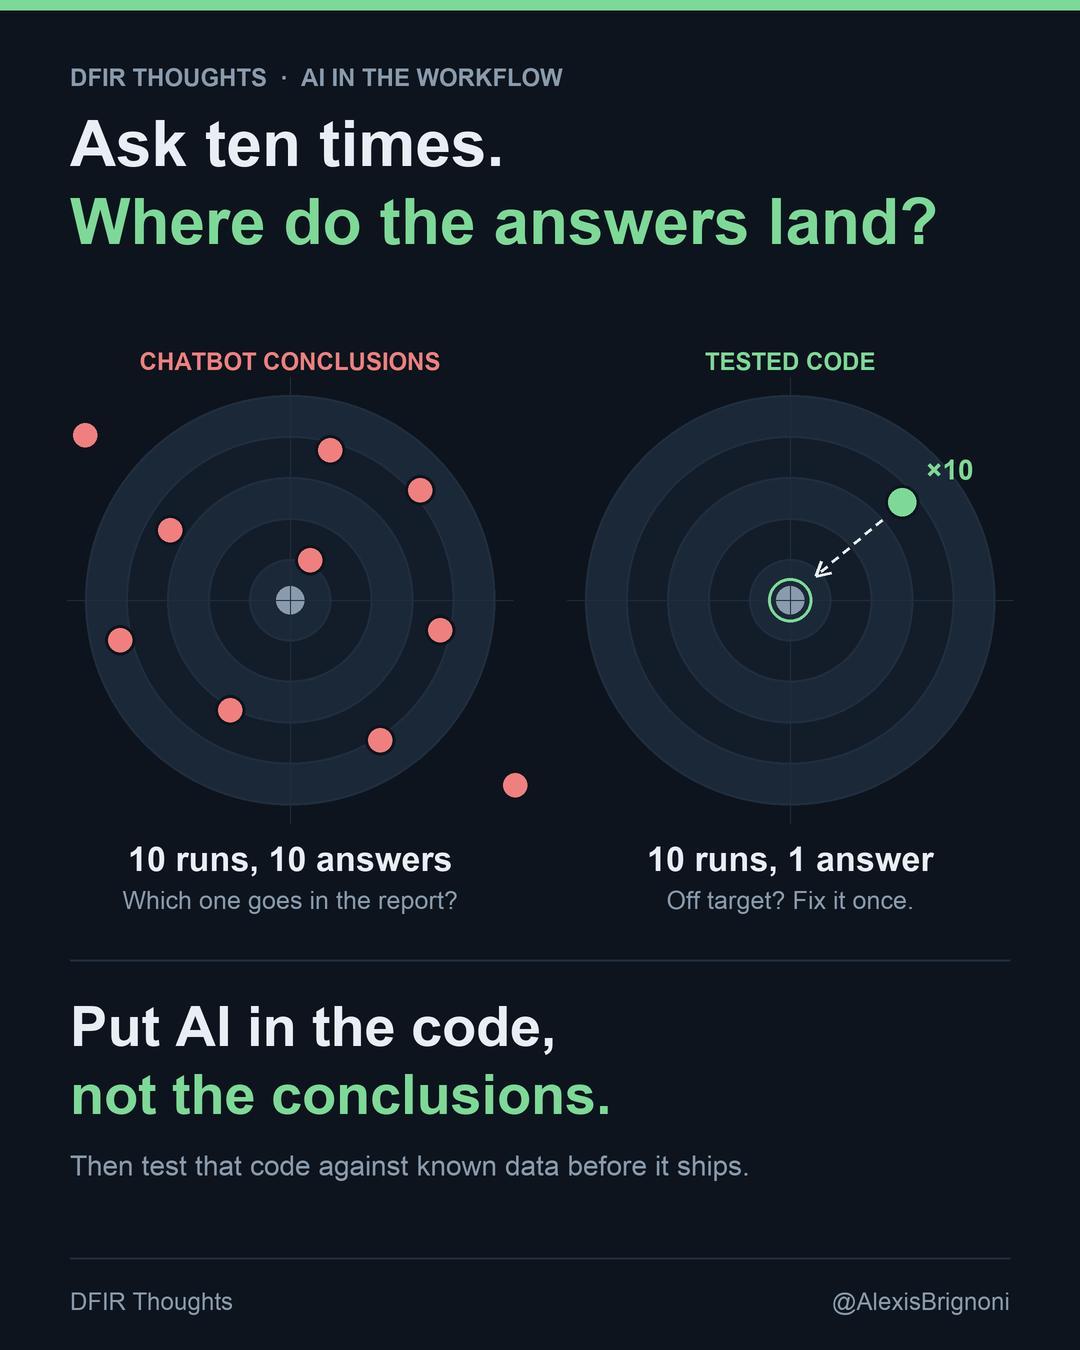
New DFIR Thoughts post: Put AI in the code, not the conclusions 🎯

Ask a chatbot the same question ten times, get ten answers. Tested code gives one, and if it's wrong, you fix it once.

https://leapps.org/blog-post?post=2026-10-20-put-ai-in-the-code-not-the-conclusions

#DFIR #DigitalForensics #AI

Media attachment
LEAPPsDFIR Thoughts: Put AI in the code, not the conclusions — LEAPPs BlogHanding examiners a chatbot that draws conclusions from parsed data is the wrong way to bring AI into digital forensics. Here is why, and what I do instead with a known-data corpus, tested code and CI checks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
J

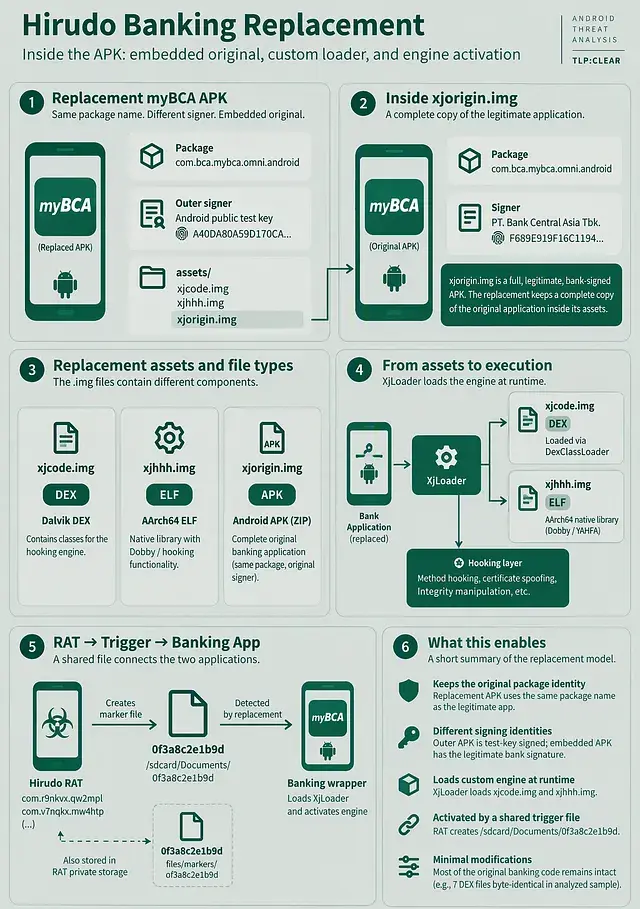
I’ve published an independent technical investigation into Hirudo, an Android banking RAT, focusing on its Indonesian banking-app replacement workflow, recovered APK artifacts, and associated infrastructure. This independent investigation was inspired by the research published by ThreatFabric. Motivated by their findings, I conducted a separate static reverse-engineering investigation focusing on Indonesian banking-app replacement artifacts, MQTT-based RAT communications, and additional infrastructure indicators. Sharing these findings with the cybersecurity community Cyber Defense Indonesia & Surabaya Hacker Link, to contribute to technical knowledge-sharing and further research into Android banking malware.

LINK:https://jeffanzos.medium.com/reverse-engineering-hirudo-indonesian-banking-targets-apk-replacement-and-rat-infrastructure-2b2890f0e4ca

Findings include: Banking app replacement (Recovered samples) associated with m-BCA, myBCA, BNI, BRI, BTN, Livin, JakOne, and BSI.

RAT infrastructure: Hardcoded C2 references and MQTT broker configurations recovered from DEX code, including 134[.]122.153[.]8:18085 and 134[.]122.153[.]8:1884.

APK internals: Hooking-engine artifacts, shared trigger-file mechanisms, certificate-substitution evidence, and embedded development paths.

Infrastructure pivots: Additional API endpoints, APK-processing panels, and certificate/DNS correlations for further investigation. The analysis is based primarily on static reverse engineering and supporting OSINT evidence. Live infrastructure behavior, several suspected relationships, and threat-actor attribution remain unverified. The objective is to document reproducible technical evidence and provide additional pivots for malware researchers, threat hunters, and incident responders.

#CyberSecurity #ThreatIntelligence #MalwareAnalysis #ReverseEngineering #DFIR #ThreatHunting #AndroidSecurity #DigitalForensics #InfoSec #InformationSecurity #CyberDefense #FinancialSecurity

Media attachment
MediumReverse-Engineering Hirudo: Indonesian Banking Targets, APK Replacement, and RAT InfrastructureAn independent technical investigation into Hirudo, focusing on Indonesian banking-app replacement workflows, artifacts recovered from…
↩ Reply ♡ 0 · ↻ 0 ↗ Original