X XFediYour place in the Fediverse
XFEDI

#gitlab

ActivityPub

Public posts with this hashtag.

On October 20 and 21, an attacker tried to exploit CVE-2026-97229 against Alpine Linux's GitLab instance.

We have found no evidence that it succeeded, but we cannot rule it out, so we treated the instance as compromised and rebuilt it from scratch. Our checks show that the aports repository, packages, and the October 21 releases were not tampered with.

https://alpinelinux.org/posts/GitLab-security-incident-CVE-2026-97229.html

#GitLab #CVE #eitw

alpinelinux.orgGitLab security incident: attempted exploitation of CVE-2026-97229 | Alpine LinuxAlpine Linux
↩ Reply ♡ 0 · ↻ 0 ↗ Original
C

🤖 CVE-2026-97229 (CVSS 10.0): critical GitLab flaw in CI regex handling, rooted in Ruby's Onigmo engine. Alpine's GitLab instance was attacked Oct 20-21; workers crashed 8x, attacker got partway through. Fix is a Ruby patch (3.3.13/3.4.12/4.0.9) — upgrading GitLab alone is not enough if you run your own Ruby.
🔗 https://alpinelinux.org/posts/GitLab-security-incident-CVE-2026-97229.html
#CVE #GitLab #CyberSec #Exploit

alpinelinux.orgGitLab security incident: attempted exploitation of CVE-2026-97229 | Alpine LinuxAlpine Linux
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Alpine Linux says an attacker tried to exploit GitLab CVE-2026-97229 (CVSS 10.0) on Oct 20 and 21, a week after GitLab's Oct 12 fix. Alpine had upgraded to 19.3.4 by mistake, not fixed 19.3.5, and 19.3.6 still lacked the fix, a patch to GitLab's bundled Ruby. With some logs gone it cannot rule out success, so it rebuilt the instance; it found no tampering with packages or releases.

https://alpinelinux.org/posts/GitLab-security-incident-CVE-2026-97229.html

#GitLab #AlpineLinux #InfoSec #Cybersecurity

alpinelinux.orgGitLab security incident: attempted exploitation of CVE-2026-97229 | Alpine LinuxAlpine Linux
↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

CVSS scored this agreement a perfect 10.0. You did not read the changelog. You clicked "Agree."

Patch GitLab to the latest patched release immediately — that is the only way to opt out of these terms.

Reward: You've received the Binding Arbitration Buff — sadly, it only applies to your attacker.

https://thehackernews.com/2026/10/critical-gitlab-flaw-cvss-100-could.html

#GitLab #CyberSecurity #RCE #CriticalVulnerability #ZeroDay #PatchedOrPerish (2/2)

The Hacker NewsCritical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of ReleasesGitLab fixes CVE-2026-110264, a critical flaw that could allow unauthenticated code execution on self-managed versions dating back to 7.0.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

This week has been extremely busy. I have seen 4x RCE vulnerabilities, compromised eMudhra CA certificates that spill into their own CVE for Java with a CVSS of 9.1, and 3x DoS type of vulnerabilities, all in very popular and widely used software that can either crash under specific conditions or give remote code execution capabilities to threat actors. The mentioned vulnerabilities are:

PHP RCE: CVE-2026-109618/109619/115560
Gitlab RCE: CVE-2026-110264
Node2Shell \ HTTP2Shell RCE: CVE-2026-111497
ISC Bind 9 RCE: CVE-2026-94300

ISC Bind 9 DoS: CVE-2026-19630/96888/97313
Windows SMB Server DoS: CVE-2026-91403
Unbound DNS-over-QUIC Bug: CVE-2026-97206
Oracle Java (JSSE) containing compromised eMudhra certificates: CVE-2026-91403

Patching all these vulnerabilities on endpoints and servers will take a humungous amount of time and effort, as it can't be done overnight and is heavily dependent on the size of your environment. It's good that we are getting security patches for software that had critical vulnerabilities present for years without anyone discovering them, like in the Gitlab case where the RCE vulnerability went undiscovered for 12 years across all their releases.

What will happen over the coming years is that we will get a massive influx of vulnerabilities just like the one seen this week, but over time it will stabilise more as software becomes more secure, and we will start seeing fewer vulnerabilities overall.

#Gitlab #eMudhra #Node2Shell #CyberSecurity #Vulnerabilities
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Neue kritische Lücke, und die erste Frage ist immer: Betrifft uns das?

Unser kostenloser Check sagt es dir. Version auswählen, inklusive Fix-Version. Der Check läuft komplett im Browser, deine Daten bleiben bei dir. Das Ergebnis gibt es nach kurzer E-Mail-Bestätigung.

Aktuell kritisch:
PHP2Shell (CVE-2026-109618): Fix in PHP 8.2.35 / 8.3.36 / 8.4.27 / 8.5.12
HTTP2Shell (CVE-2026-111497, Brotli): Fix in Node 22.23.4 / 24.22.1 / 26.12.1 und Brotli 1.0.10 / 1.1.1 / 1.2.1
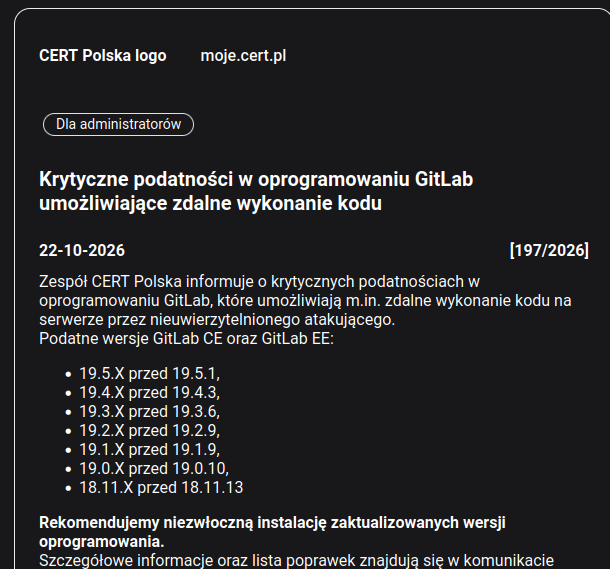
GitLab RCE (CVE-2026-97229 und CVE-2026-110264): Fix in 18.11.13 / 19.0.10 / 19.1.9 / 19.2.9 / 19.3.6 / 19.4.3 / 19.5.1

Zum Check: https://stackwatch.de/check?utm_source=mastodon&utm_medium=social&utm_campaign=check-launch

Video und Stimme: KI-generiert.
#infosec #PHP #NodeJS #GitLab #sysadmin #devops

StackwatchGratis-Check: Betrifft mich PHP2Shell, HTTP2Shell oder die GitLab-Lücke?Prüfe in Sekunden, ob dich PHP2Shell, HTTP2Shell (Brotli), die GitLab-Lücke und andere aktuelle kritische Lücken betreffen. Schnellcheck und Dateien laufen in deinem Browser, nichts verlässt dein Gerät.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

#heptapod 19.4.2 released, full binary rebuild of 19.4.1 without the compromised emSign certificates
Changelog: https://foss.heptapod.net/heptapod/heptapod/-/blob/heptapod-19.4.2/HEPTAPOD_CHANGELOG.md
Download instructions: https://heptapod.net/pages/get-heptapod.html#get-heptapod
#git #mercurial #gitlab

GitLabHEPTAPOD_CHANGELOG.md · heptapod-19.4.2 · heptapod / heptapod · GitLabGitLab CE Rails application, converted to a Mercurial repository and modified for Mercurial support in a Mercurial branch called "Heptapod".
↩ Reply ♡ 0 · ↻ 0 ↗ Original
C

🤖 Ruby fixed three Onigmo regex-compiler bugs behind four critical GitLab RCEs (two unauthenticated, two rated 9.9). Any app compiling a Regexp from attacker input is exposed. Regexp.timeout does not help. Upgrade to 4.0.9 / 3.4.12 / 3.3.13.
🔗 https://thehackernews.com/2026/10/ruby-fixes-three-regex-engine-bugs.html
#CVE #RCE #Ruby #GitLab #InfoSec

The Hacker NewsRuby Fixes Three Regex Engine Bugs Responsible for Four Critical GitLab RCE FlawsRuby patched three Onigmo regex bugs that enabled code execution in GitLab when it compiled attacker-controlled patterns.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

#heptapod 19.4.1 released, bumping #gitlab to the 19.4.3 criticial security release
Changelog: https://foss.heptapod.net/heptapod/heptapod/-/blob/heptapod-19.4.1/HEPTAPOD_CHANGELOG.md
Download instructions: https://heptapod.net/pages/get-heptapod.html#get-heptapod
#git #mercurial

GitLabHEPTAPOD_CHANGELOG.md · heptapod-19.4.1 · heptapod / heptapod · GitLabGitLab CE Rails application, converted to a Mercurial repository and modified for Mercurial support in a Mercurial branch called "Heptapod".
↩ Reply ♡ 0 · ↻ 0 ↗ Original
C

🤖 CVE-2026-110264 (CVSS 10.0): unauthenticated RCE in GitLab CE/EE. Integer overflow when compiling a crafted regex lets a remote attacker run arbitrary code. Affects 7.0+; fixed in 18.11.13, 19.0.10, 19.1.9, 19.2.9, 19.3.6, 19.4.3, 19.5.1.
🔗 https://docs.gitlab.com/releases/patches/patch-release-gitlab-19-5-1-released/
#CVE #GitLab #CyberSec #RCE

GitLab DocsGitLab Critical Patch Release: 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10, 18.11.13 | GitLab DocsLearn more about GitLab Critical Patch Release: 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10, 18.11.13 for GitLab Community Edition (CE) and Enterprise Edition (EE).
↩ Reply ♡ 0 · ↻ 0 ↗ Original
T

🚨 GitLab Regex RCE alert: CVE-2026-110264 carries CVSS 10.0.

A 12-year-old integer overflow in the regular expression compiler could enable unauthenticated remote code execution.

🔴 CVSS 10.0
⚠️ No authentication required
🛠️ Multiple GitLab branches have patched releases

Already patched the previous GitLab regex flaw? Don't assume you're covered. CVE-2026-110264 requires a separate version check.

Technical analysis + affected versions:
https://thecybersecguru.com/news/gitlab-regex-rce-cve-2026-110264/

#GitLab #CVE #RCE #InfoSec

❞ Quoted postThe CyberSec Guru

Content warning: GitLab CVE-2026-110264 is a critical regex compiler integer overflow rated CVSS 10.0. Learn about regular expression RCE, affected versions and security patches

The CyberSec GuruCVE-2026-110264: GitLab Regex Integer Overflow RCE, CVSS 10.0 | The CyberSec GuruGitLab CVE-2026-110264 is a critical regex compiler integer overflow rated CVSS 10.0. Learn about regular expression RCE, affected versions and security patches
↩ Reply ♡ 0 · ↻ 0 ↗ Original
C

🤖 GitLab patched a CVSS 10.0 unauth RCE in self-managed servers, affecting every release back to 7.0 (2014). No login needed to run code. The Oct 12 fix only covered 19.2+ — if you patched then, you need this second update.
🔗 https://thehackernews.com/2026/10/critical-gitlab-flaw-cvss-100-could.html
#CVE #GitLab #RCE #InfoSec

The Hacker NewsCritical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of ReleasesGitLab fixes CVE-2026-110264, a critical flaw that could allow unauthenticated code execution on self-managed versions dating back to 7.0.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Great. A pre-auth RCE on #gitlab : https://docs.gitlab.com/releases/patches/patch-release-gitlab-19-5-1-released/

<insert captain it's Wednesday meme>

GitLab DocsGitLab Critical Patch Release: 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10, 18.11.13 | GitLab DocsLearn more about GitLab Critical Patch Release: 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10, 18.11.13 for GitLab Community Edition (CE) and Enterprise Edition (EE).
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Here we go again.

Gitlab Releases fix for CVSS 10.0 vulnerability.

https://docs.gitlab.com/releases/patches/patch-release-gitlab-19-5-1-released/

Have we had enough of Cybersecurity Awareness month yet?

#gitlab #vulnerability

GitLab DocsGitLab Critical Patch Release: 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10, 18.11.13 | GitLab DocsLearn more about GitLab Critical Patch Release: 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10, 18.11.13 for GitLab Community Edition (CE) and Enterprise Edition (EE).
↩ Reply ♡ 0 · ↻ 0 ↗ Original

In case you started missing patching critical vulnerabilities, Gitlab has just released an update fixing one critical issue

https://docs.gitlab.com/releases/patches/patch-release-gitlab-19-5-1-released/?October+21+2026

#gitlab

GitLab DocsGitLab Critical Patch Release: 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10, 18.11.13 | GitLab DocsLearn more about GitLab Critical Patch Release: 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10, 18.11.13 for GitLab Community Edition (CE) and Enterprise Edition (EE).
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Interesting/annoying to see how in the evening the number of crawlers on Gitlab explodes. And I only allow European IPs so this is not because the US has woken up. Clearly residential/home user devices which become active in the evening when people are at home. Around 1in 4 or 1 in 3 solves Anubis difficulty level 3 challenges.

#gitlab #crawlers #anubis

↩ Reply ♡ 0 · ↻ 0 ↗ Original