X XFediYour place in the Fediverse
XFEDI

#infosec

ActivityPub

Public posts with this hashtag.

In Japan, the ransomware name everyone knows is Qilin, thanks to the Asahi attack.

On the leak sites, 2026 belongs to The Gentlemen: 23 Japanese organizations listed this year (ransomware.live), vs 15 for Qilin. Group-IB says it grew out of a Qilin affiliate team, and it hands affiliates compromised FortiGates.

The brand changes; the way in doesn't.

https://japancyberwatch.com/articles/japan-ransomware-groups-2026-the-gentlemen-qilin

#ransomware #infosec #Japan #ThreatIntel

japancyberwatch.comJapan's Ransomware Headlines Say Qilin. The Leak Sites Say The GentlemenQilin became a household name in Japan after the Asahi attack. In 2026, a group that grew out of Qilin's own affiliates, The Gentlemen, has listed more Japanese organizations than any other. What the data shows, and why the name matters less than the way in.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Cybersecurity is a leadership problem: Why the management model needs to catch up

Cybersecurity fails when treated as just a tech problem. The real issue? Leadership. CISOs can't do it alone—organizations need clear accountability, cross-level collaboration, and board involvement. Better tools mean nothing without proper governance and sustained management discipline. It's time to break the cycle.

https://www.csoonline.com/article/4234532/cybersecurity-is-a-leadership-problem-why-the-management-model-needs-to-catch-up.html

#InfoSec #CyberSecurity #Leadership

CSO OnlineCybersecurity is a leadership problem: Why the management model needs to catch upWe keep buying better security tech, but the real gaps are ownership and follow-through, so cybersecurity can’t stay the CISO’s problem alone.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

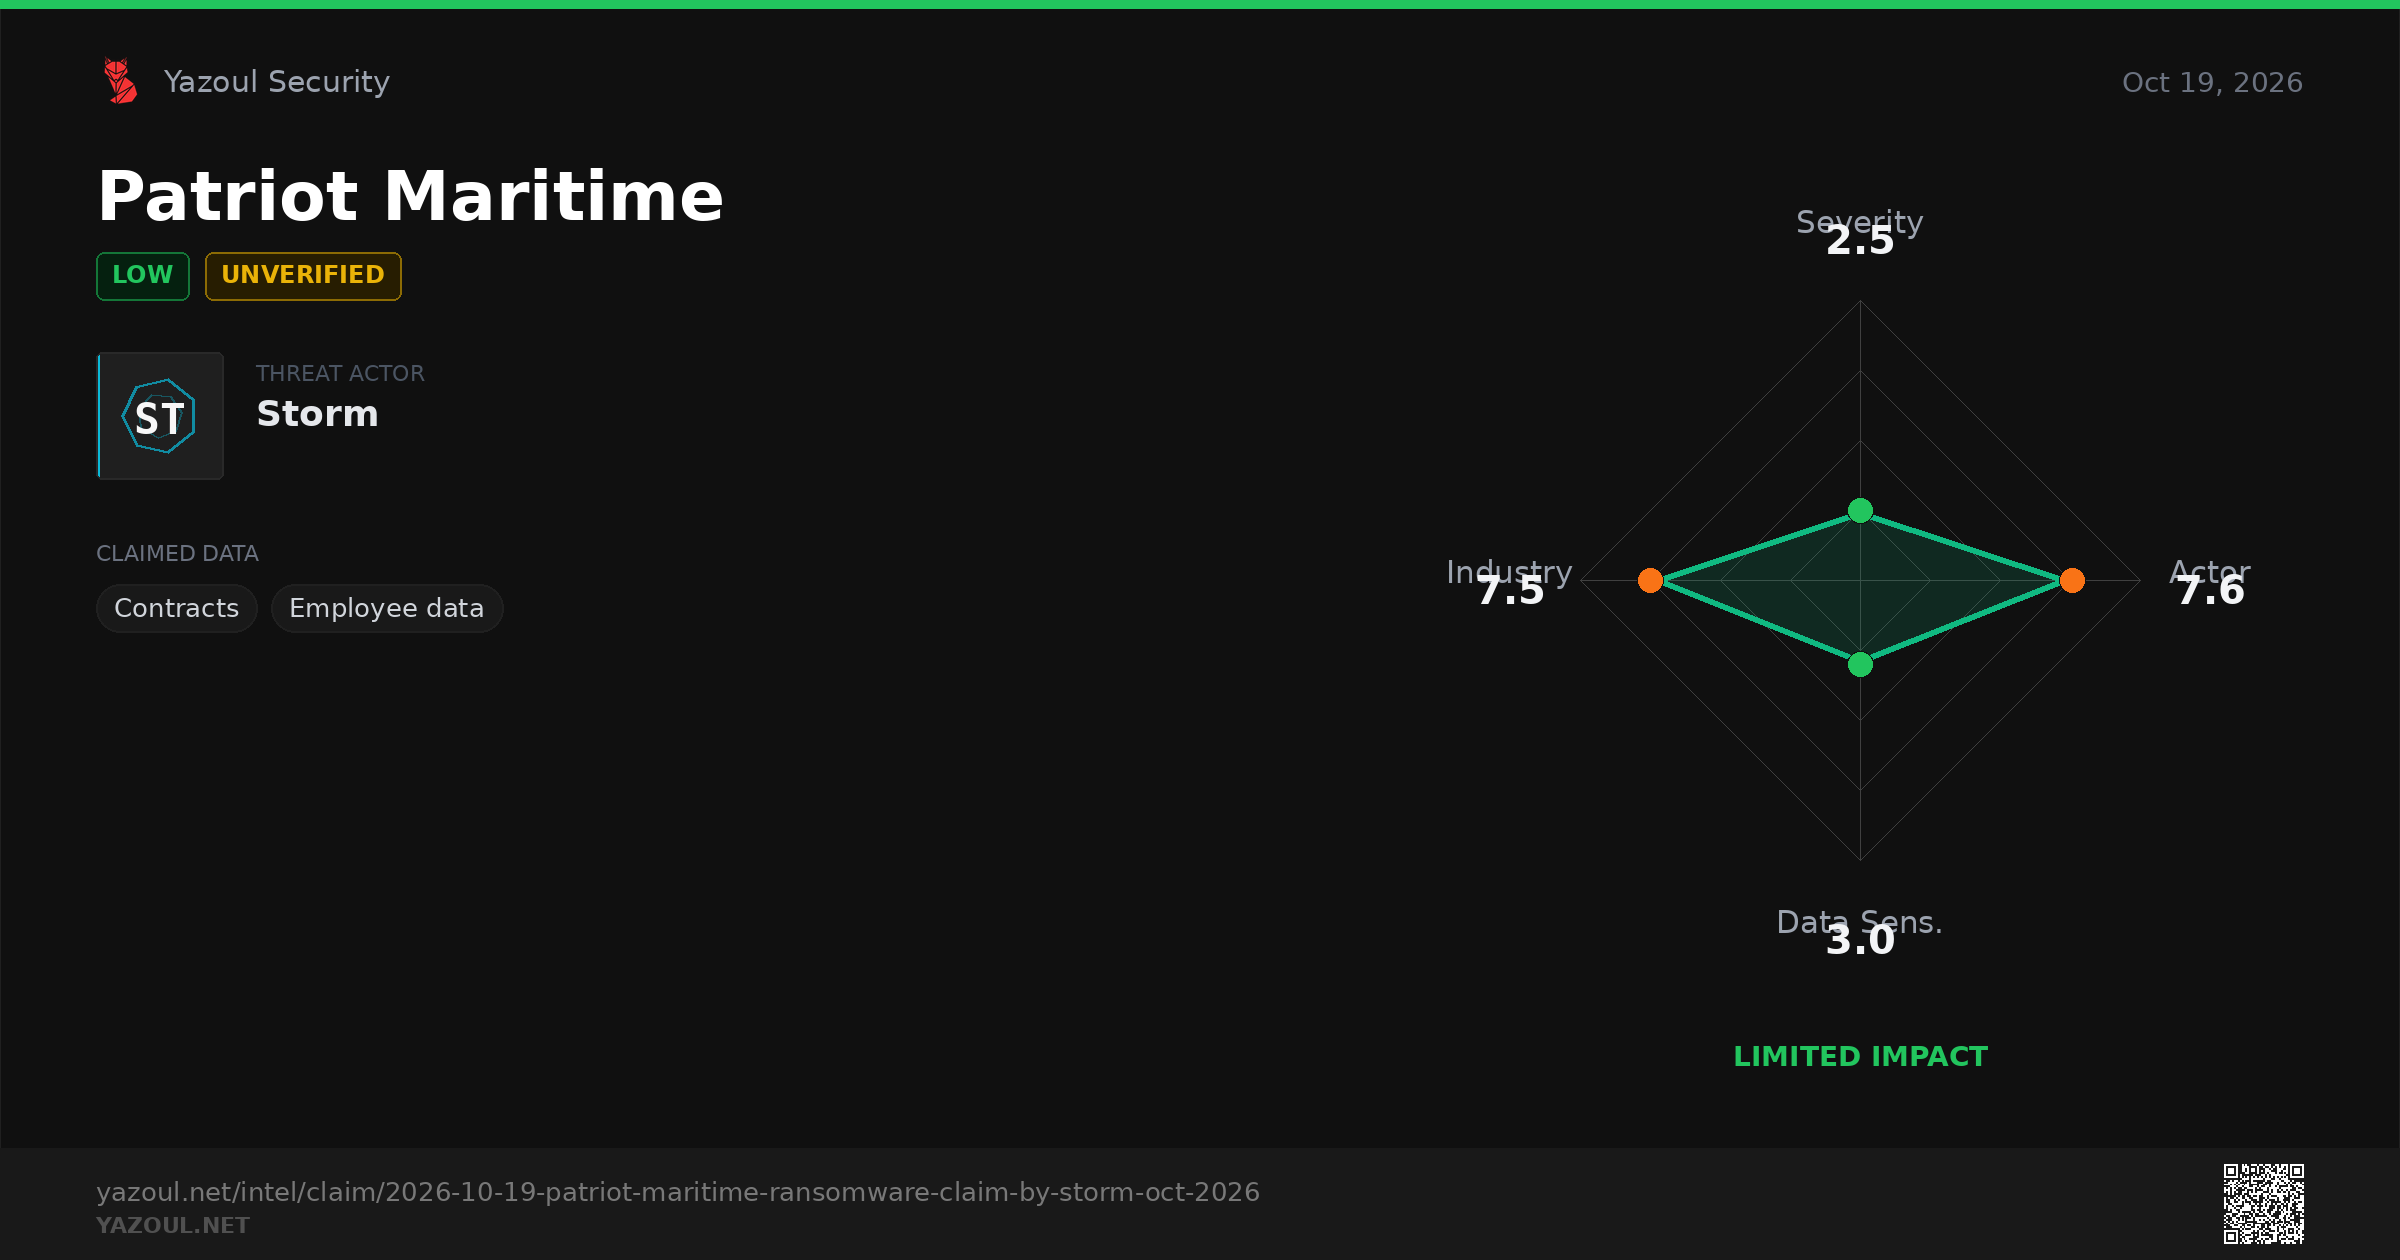
🛡 THREAT INTEL | Patriot Maritime

🟢 Actor "Storm" claims Undisclosed

Allegedly exposed
• Contracts
• Employee data

⚠️ Unverified claim

https://www.yazoul.net/intel/claim/2026-10-19-patriot-maritime-ransomware-claim-by-storm-oct-2026

by Yazoul AI

#DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec

Yazoul SecurityPatriot Maritime Ransomware Claim by Storm (Oct 2026)Storm ransomware group allegedly claims Patriot Maritime as a victim, threatening sensitive maritime contractor data. Read our unverified threat intel analysis now.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

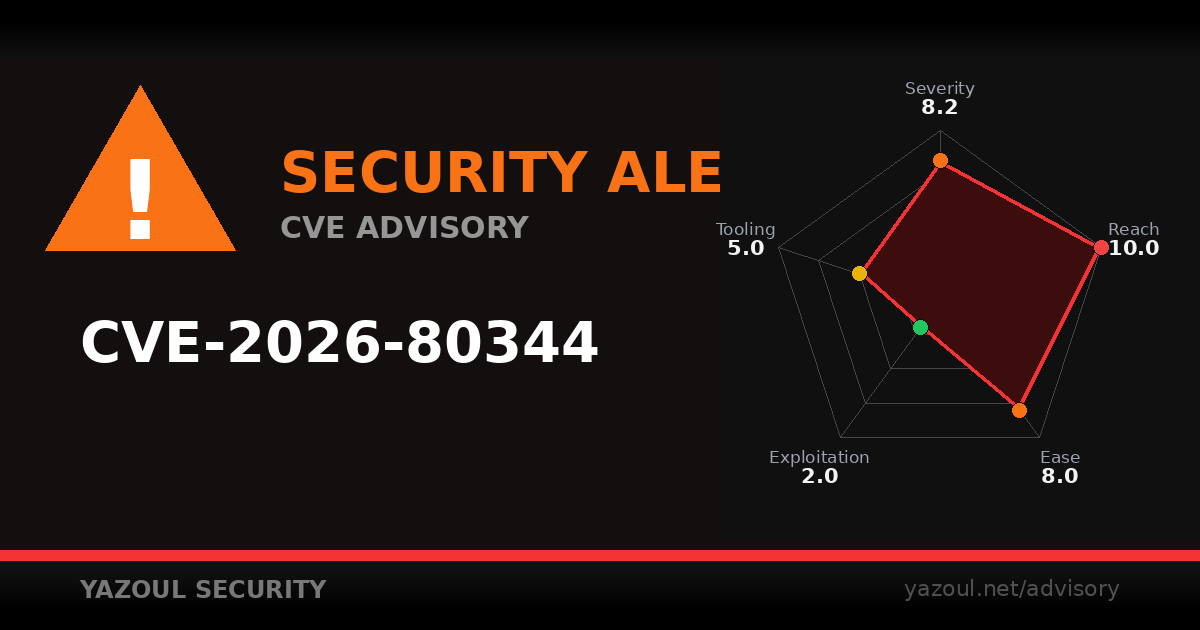
⚠️ New security advisory:

CVE-2026-80344 affects multiple systems.

• Impact: Significant security breach potential
• Risk: Unauthorized access or data exposure
• Mitigation: Apply patches within 24-48 hours

Full breakdown:
https://www.yazoul.net/advisory/cve/cve-2026-80344-apache-camel-as2-ssrf-enables-internal-network-access-poc

by Yazoul AI

#InfoSec #ZeroDay #ThreatIntel

Yazoul SecurityApache Camel AS2 SSRF enables internal network access (CVE-2026-80344) [PoC]CVE-2026-80344: Apache Camel AS2 SSRF (CVSS 8.2) lets remote senders pick the MDN destination host and leak credentials. Update to 4.23.0, 4.18.5, or 4.22.1.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Tech took a beating this past week. It was the main target for attackers (ranking #2 out of 12 sectors) with 193 stories hitting the wire.

https://theperimetersite.com/report/377

#supplychain #infosec

The Perimeter Site48 New Technology Sector Incidents Hit Wire as ConnectWise Supply…Tech took a beating this past week. It was the main target for attackers (ranking #2 out of 12 sectors) with 193 stories hitting the wire.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

The 7 biggest issues CISOs and security teams face today

Security leaders face mounting pressure as AI-driven cyberattacks surge. 68% of CISOs report increased stress, with 73% unprepared for major breaches. The shift from prevention to resilience is critical—78% view generative AI as a security risk. Key priorities: close the 95% skills gap, strengthen AI infrastructure security, align programs with org needs, and maintain foundational practices.

https://www.csoonline.com/article/4232208/the-7-biggest-issues-cisos-and-security-teams-face-today.html

#InfoSec #CyberSecurity #AI

CSO OnlineThe 7 biggest issues CISOs and security teams face todayFrom escalating AI-enabled threats to persistent skills gaps, security leaders are reshaping their agendas to address several key long-standing and emerging concerns.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🛡️ Manager, MDR & Threat Hunting at Zscaler
📍 Remote (US)
💰 $144k–$205k/yr

Apply: https://blueteamjobs.com/job/manager-mdr-and-threat-hunting-zscaler-x1fw4e/

#BlueTeam #InfoSec #CyberSecurityJobs #SecurityOperationsLeadership

BlueTeamJobsManager, MDR & Threat Hunting at Zscaler | BlueTeamJobsZscaler is hiring a Manager, MDR & Threat Hunting, Remote (US). Pay: $144k–$205k a year. Zscaler (NASDAQ: ZS) accelerates digital transformation so…
↩ Reply ♡ 0 · ↻ 0 ↗ Original
C

🤖 Plex2Shell: a 4-vuln chain in Plex Media Server is now exploited in the wild, one day after public PoC. Attackers chain the flaws to deploy crypto miners and a Linux reverse-proxy backdoor on internet-facing servers.

🔗 https://thehackernews.com/2026/10/hackers-exploit-plex2shell-flaws-to.html
#Exploit #InfoSec #Malware #CyberSec

The Hacker NewsHackers Exploit Plex2Shell Flaws to Install Crypto Miners and Linux Proxy BackdoorAttackers exploit four Plex Media Server flaws chained as Plex2Shell to deploy XMRig miners and reverse proxy software after PoC release.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

AI agents are changing the math on software spending

AI agents are reshaping enterprise software pricing. Companies like Microsoft, Salesforce, and SAP are ditching traditional per-seat licensing for hybrid models combining fixed subscriptions with consumption-based charges. CIOs must now budget for workflow complexity and execution frequency, not just user count. Success requires rethinking forecasting strategies and potential budget shifts between IT and business units.

https://www.techtarget.com/it-strategy/news/366652139/AI-agents-are-changing-the-math-on-software-spending

#InfoSec #CyberSecurity

IT StrategyAI agents are changing the math on software spending | TechTargetAI agents add usage-based charges to seat licensing. CIOs must compare workflow costs, forecast consumption and decide who pays for agent activity.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

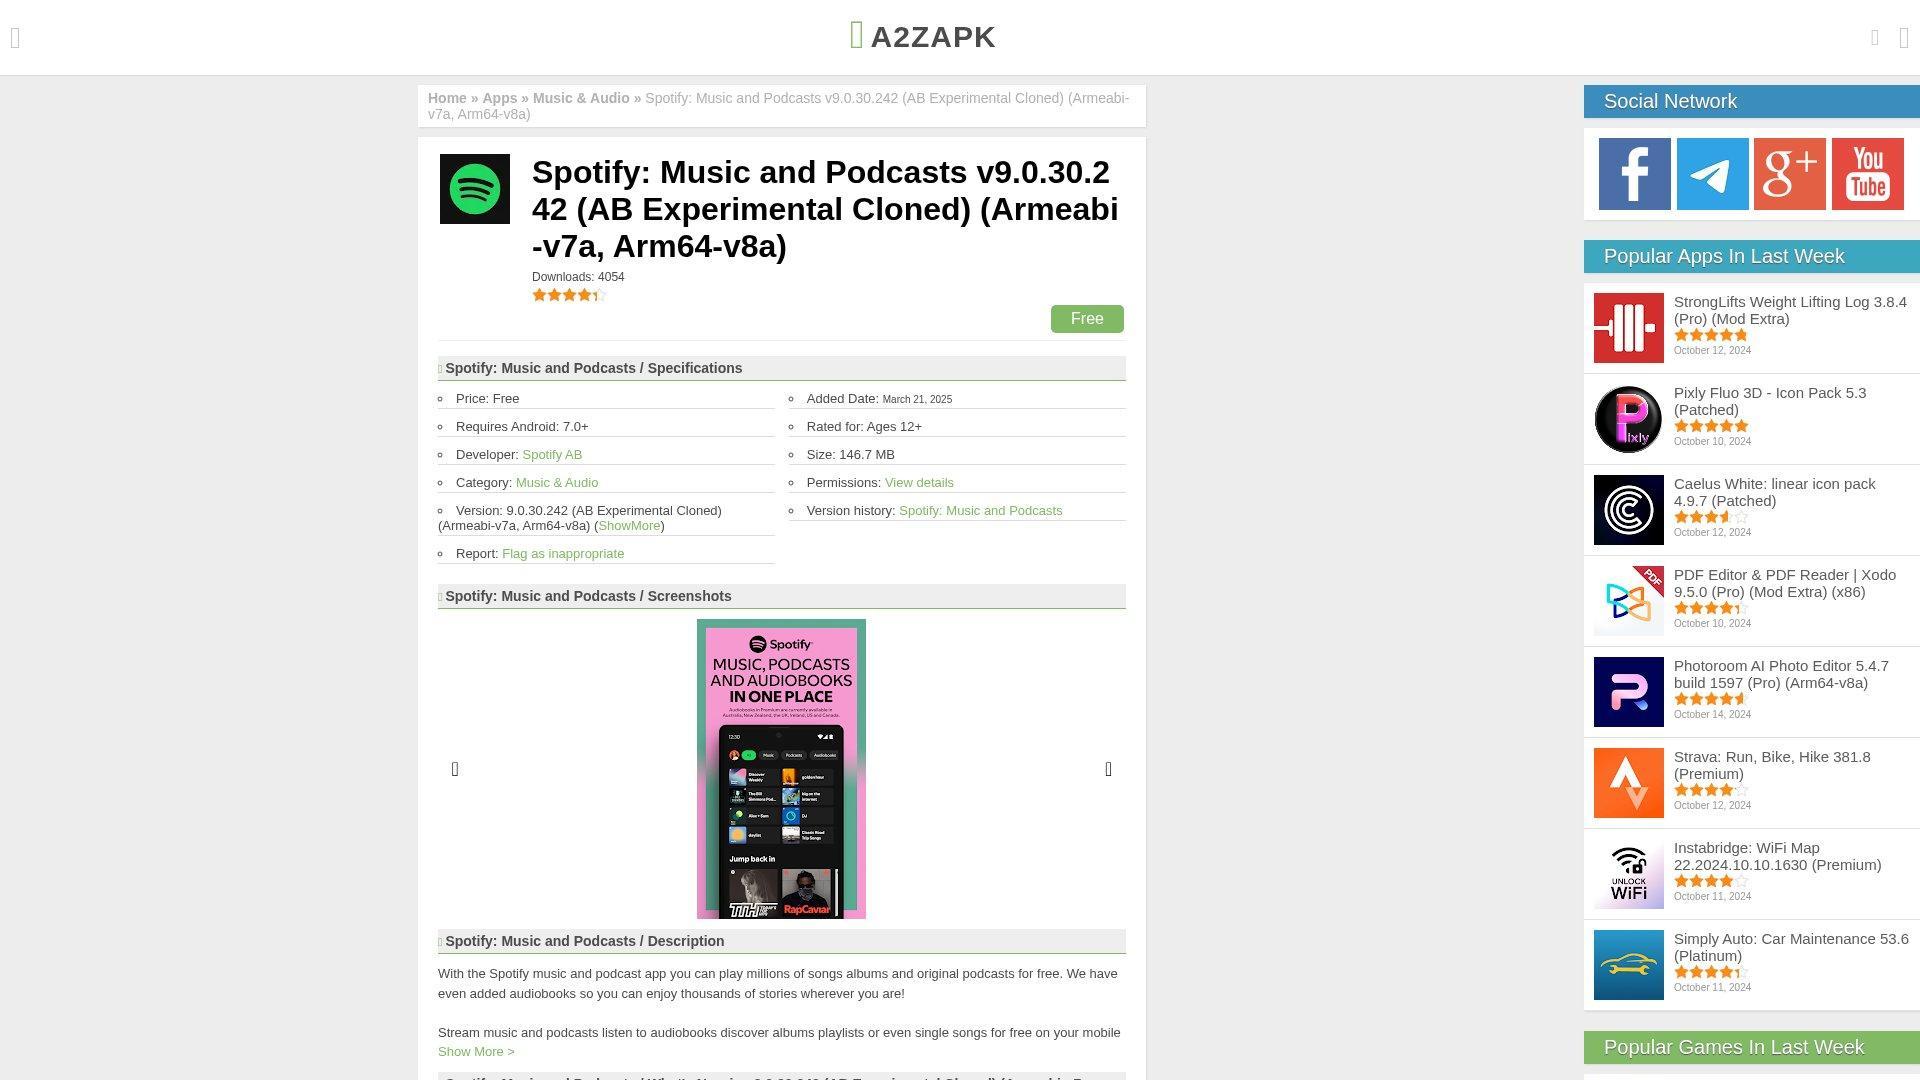
Possible Phishing 🎣
on: ⚠️hxxp[:]//a2zapk[.]co/1368404-spotify-music-and-podcasts-9-0-30-242-ab-experimental-cloned-armeabi-v7a-arm64-v8a-a2z[.]html
🧬 Analysis at: https://urldna.io/scan/6ad654733b77500002f4d97a
#cybersecurity #phishing #infosec #urldna #scam #infosec

Media attachment
urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
↩ Reply ♡ 0 · ↻ 0 ↗ Original

#introduction, round two. I'm Solomon: retired chef, network and systems engineer, CySA+, finishing an M.S. in cybersecurity at USF.

I build Brigade, open-source tooling that keeps AI coding agents honest: verified runs with signed exit codes, a code graph agents check before editing, and an evidence log of what they did. I also run a homelab SOC on Wazuh, TheHive, and MISP.

Here for blue team, agent security, and homelabs.

https://brigade.tools

#infosec #blueteam #aisecurity #homelab

BrigadeBrigade - trackable work for coding-agent fleetsTrack coding-agent tasks, receipts, shared memory, and synced tools across tools, repos, and sessions. Local files. No required daemon.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

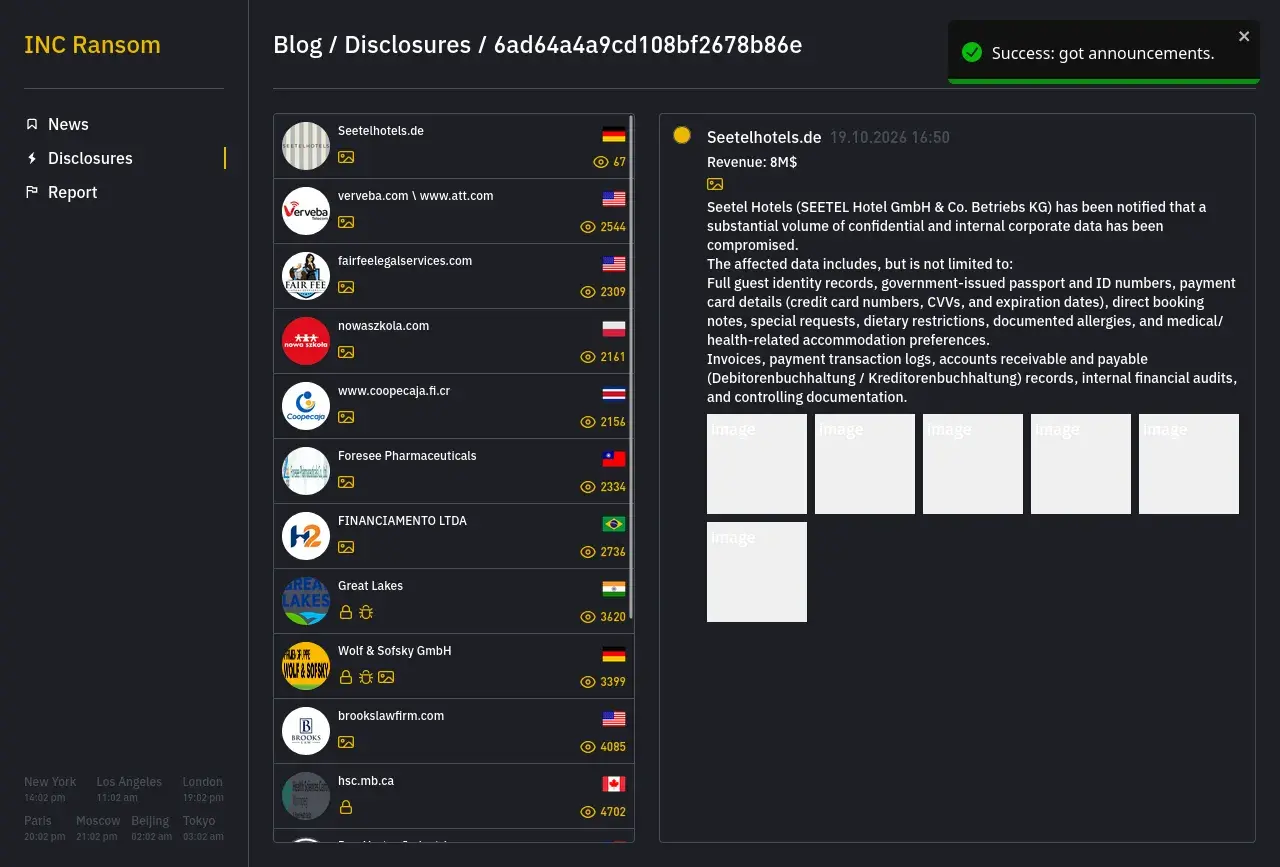
🚨New ransom group blog post!🚨

Group name: incransom
Post title: Seetelhotels.de
Organization: Seetel Hotels
Location: 🇩🇪 DE
Sector: Hospitality & Tourism
Info: https://cti.fyi/#disclosure/incransom/Seetelhotels.de

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Thank you Splunk, a Cisco Company for sponsoring BSides Edmonton 2026. It was a great event thanks to your support.

We’re excited for 2027, our 10th year!
Secure your spot here: https://bsidesyeg.org/SponsorNextYear

https://www.splunk.com
https://www.linkedin.com/company/splunk/

#BSides #BSidesEdmonton #BSidesYEG #YEG #Infosec #informationsecurity #CyberSec #CyberSecurity

Media attachment
Google DocsBSides Edmonton 2027 Sponsor ApplicationBSides Edmonton is back for it's 10th year! Building on the success of our prior events, we are asking for sponsors to be part of the team to deliver another first-rate cybersecurity conference in Edmonton. Alberta. We are a community-driven, non for profit event. Date: Monday September 13 & Tuesday September 14, 2027 Location: TBA If your organization wants to: Connect directly with the cyber
↩ Reply ♡ 0 · ↻ 0 ↗ Original