X XFediYour place in the Fediverse
XFEDI

#ransomware

ActivityPub

Public posts with this hashtag.

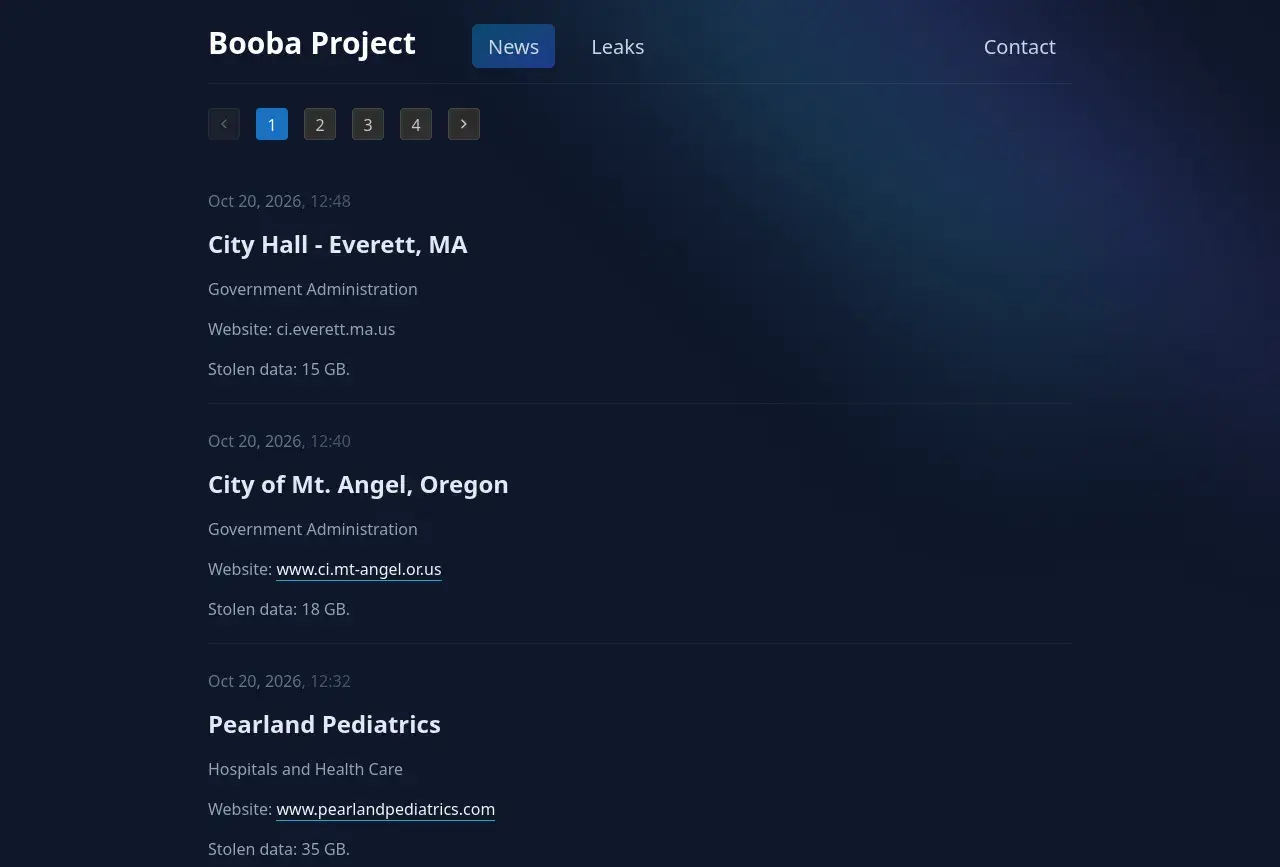
🚨New ransom group blog posts!🚨

Group name: Booba Project
Post title: City Hall - Everett, MA
Organization: Everett City Hall
Location: 🇺🇸 US
Sector: Government & Public Sector
Info: https://cti.fyi/#disclosure/Booba%20Project/City%20Hall%20-%20Everett%2C%20MA

Group name: Booba Project
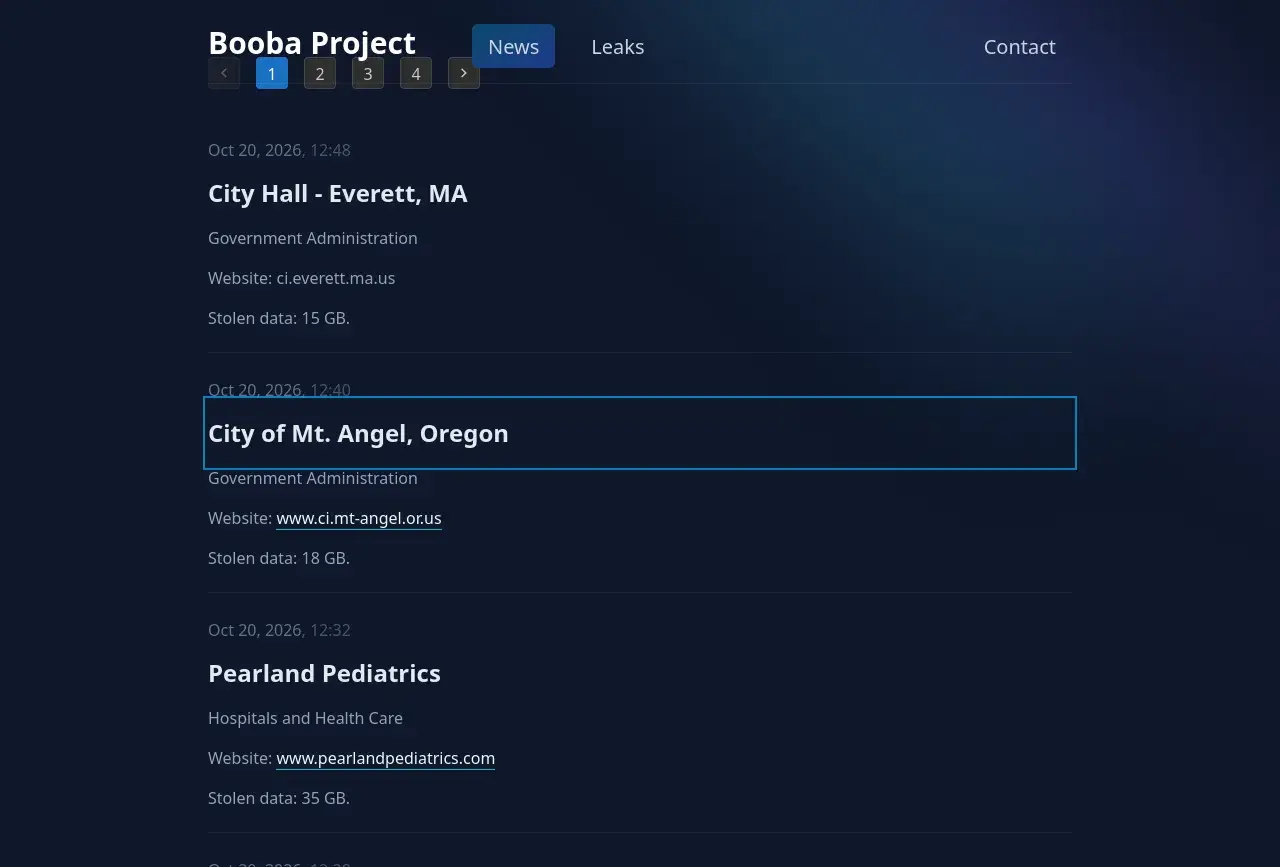
Post title: City of Mt. Angel, Oregon
Organization: City of Mt. Angel
Location: 🇺🇸 US
Sector: Government & Public Sector
Info: https://cti.fyi/#disclosure/Booba%20Project/City%20of%20Mt.%20Angel%2C%20Oregon

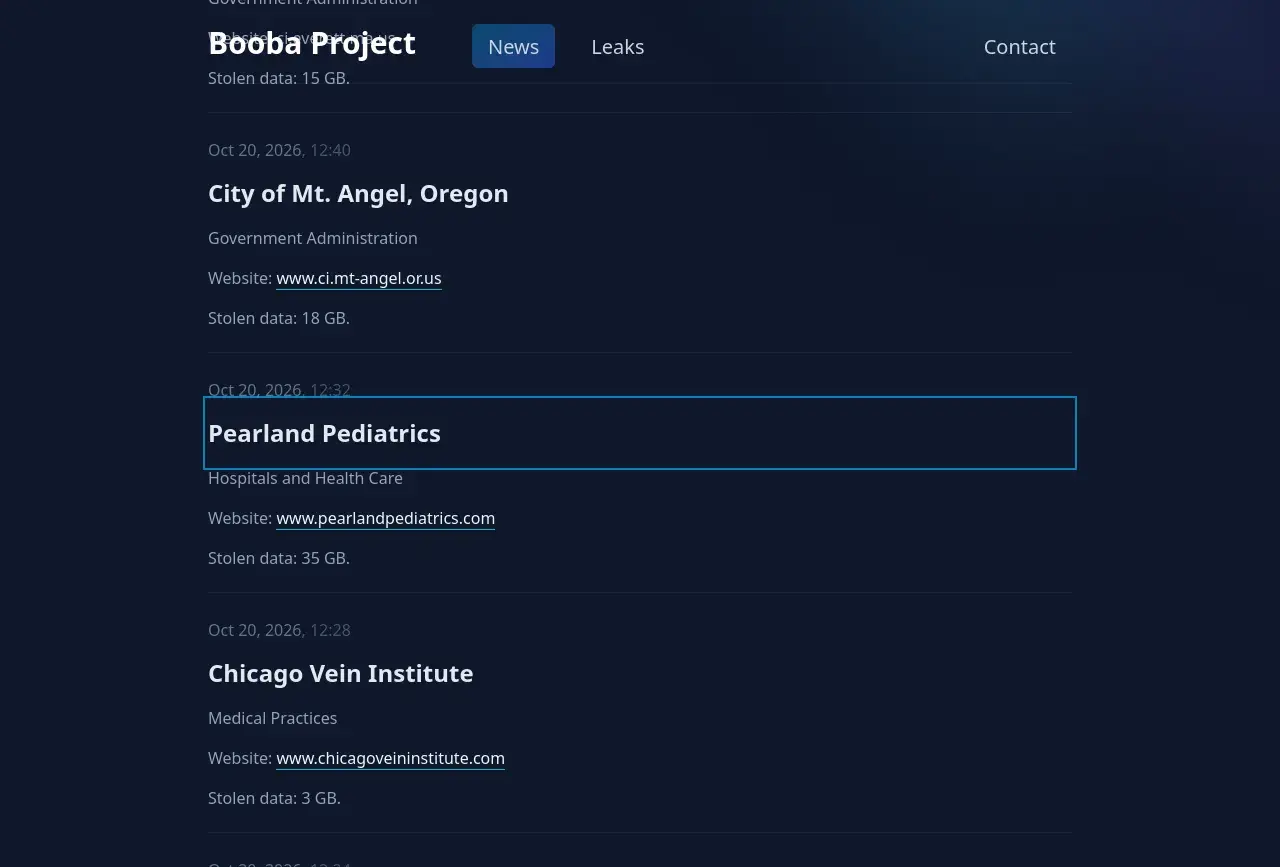
Group name: Booba Project
Post title: Pearland Pediatrics
Location: 🇺🇸 US
Sector: Healthcare
Info: https://cti.fyi/#disclosure/Booba%20Project/Pearland%20Pediatrics

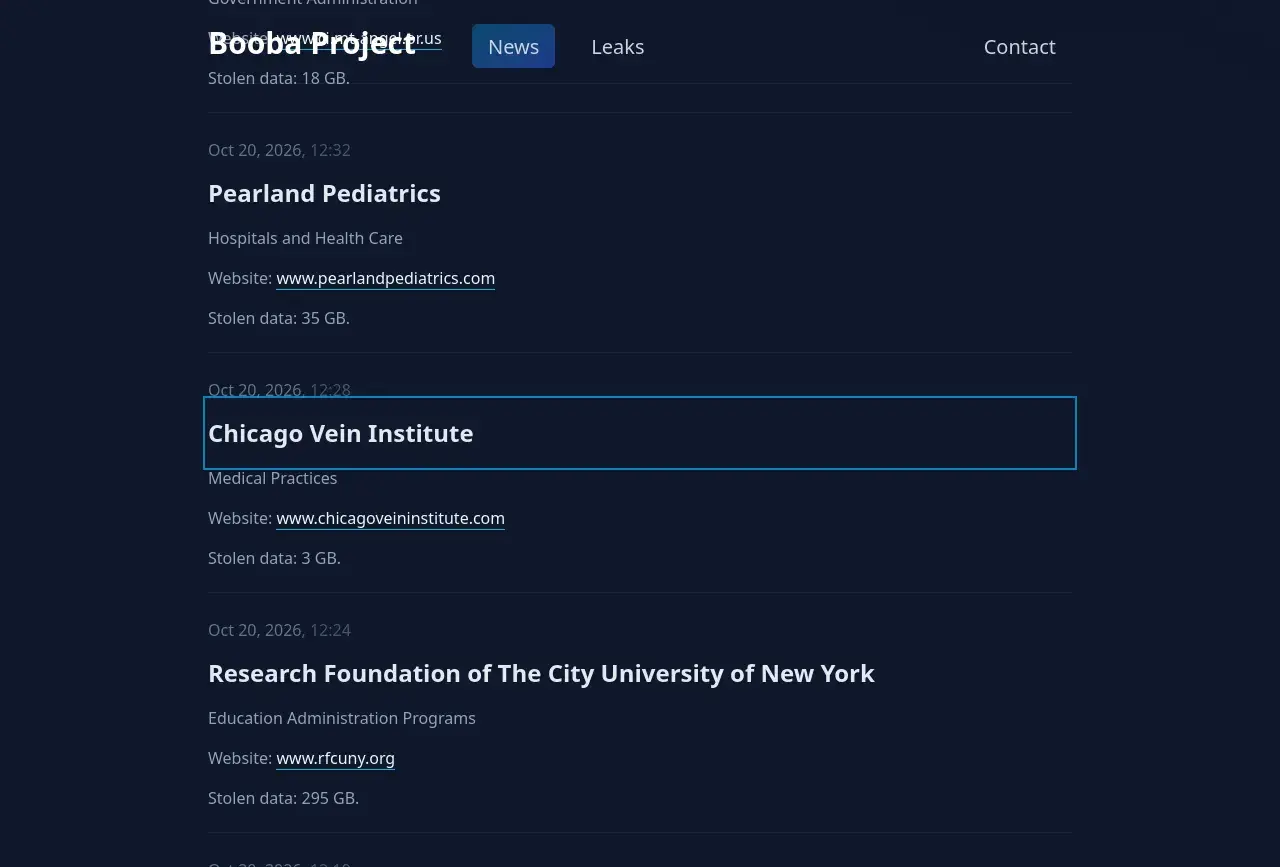
Group name: Booba Project
Post title: Chicago Vein Institute
Location: 🇺🇸 US
Sector: Healthcare
Info: https://cti.fyi/#disclosure/Booba%20Project/Chicago%20Vein%20Institute

Group name: Booba Project
Post title: Research Foundation of The City University of New York
Location: 🇺🇸 US
Sector: Education
Info: https://cti.fyi/#disclosure/Booba%20Project/Research%20Foundation%20of%20The%20City%20University%20of%20New%20York

Group name: Booba Project
Post title: COASTAL CAROLINA NEUROPSYCHIATRIC CENTER, PA
Organization: COASTAL CAROLINA NEUROPSYCHIATRIC CENTER
Location: 🇺🇸 US
Sector: Healthcare
Info: https://cti.fyi/#disclosure/Booba%20Project/COASTAL%20CAROLINA%20NEUROPSYCHIATRIC%20CENTER%2C%20PA

#ransomware #cti #threatintelligence #cybersecurity #infosec
Media attachmentMedia attachmentMedia attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

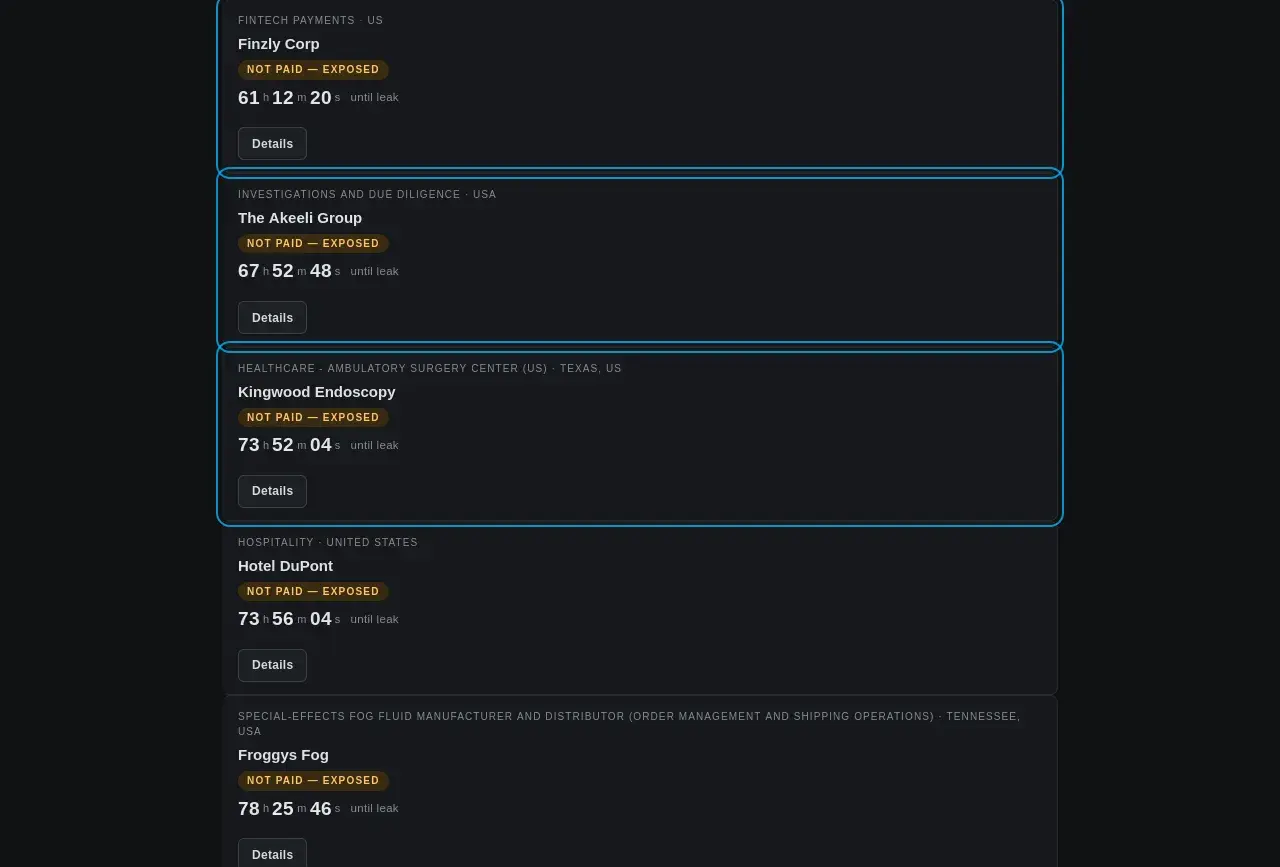
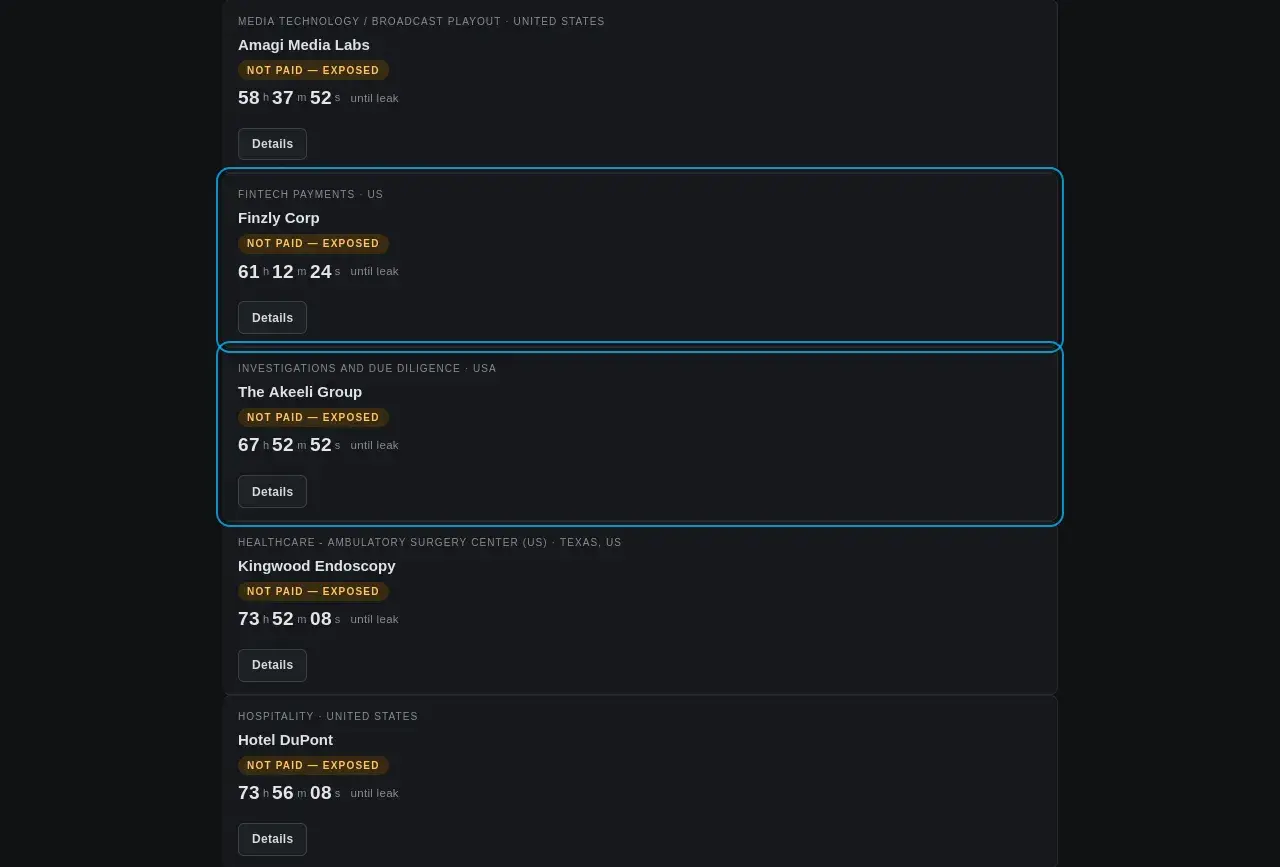
🚨New ransom group blog posts!🚨

Group name: N0n
Post title: Finzly Corp
Location: 🇺🇸 US
Sector: Financial Services
Info: https://cti.fyi/#disclosure/N0n/Finzly%20Corp

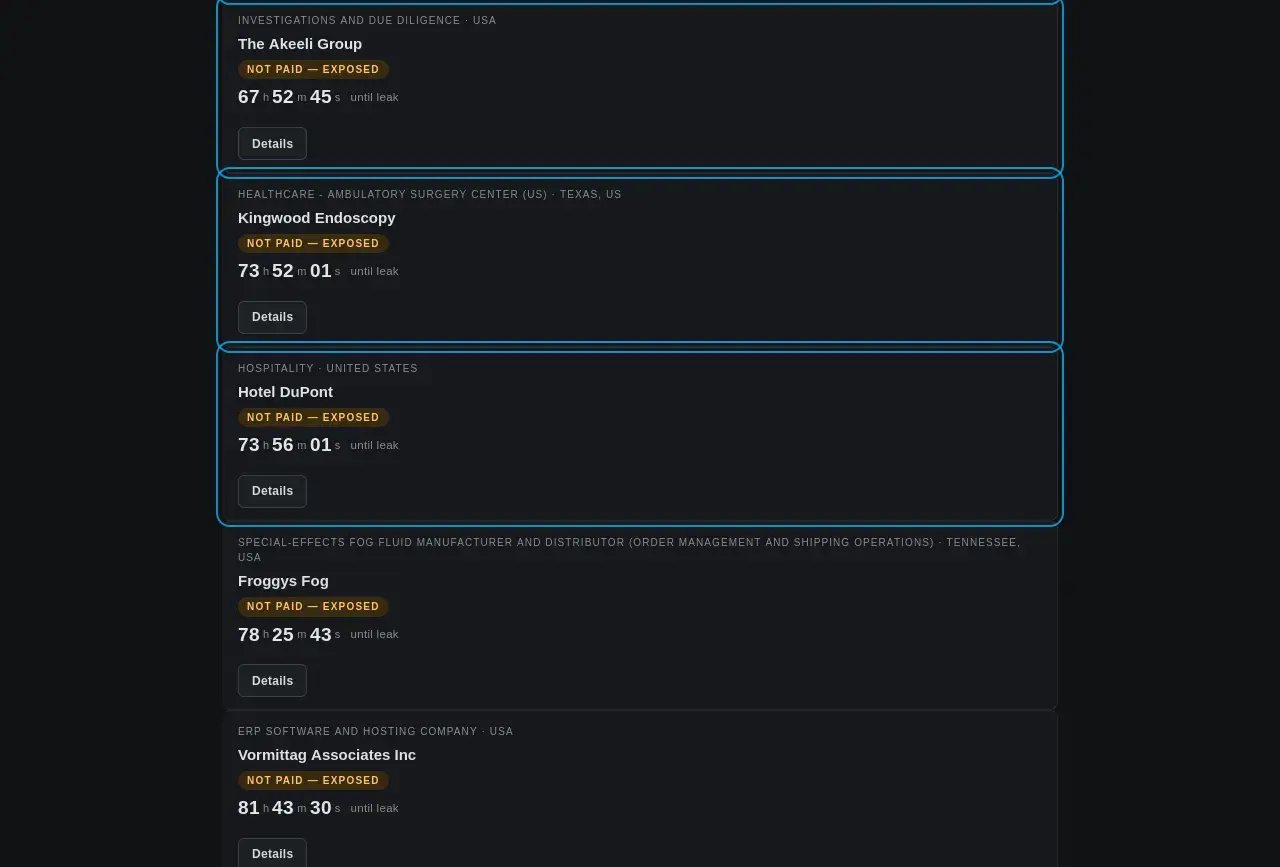
Group name: N0n
Post title: The Akeeli Group
Location: 🇺🇸 US
Sector: Professional Services
Info: https://cti.fyi/#disclosure/N0n/The%20Akeeli%20Group

Group name: N0n
Post title: Kingwood Endoscopy
Location: 🇺🇸 US
Sector: Healthcare
Info: https://cti.fyi/#disclosure/N0n/Kingwood%20Endoscopy

Group name: N0n
Post title: Hotel DuPont
Location: 🇺🇸 US
Sector: Hospitality & Tourism
Info: https://cti.fyi/#disclosure/N0n/Hotel%20DuPont

Group name: N0n
Post title: Froggys Fog
Location: 🇺🇸 US
Sector: Manufacturing
Info: https://cti.fyi/#disclosure/N0n/Froggys%20Fog

Group name: N0n
Post title: Vormittag Associates Inc
Location: 🇺🇸 US
Sector: Technology
Info: https://cti.fyi/#disclosure/N0n/Vormittag%20Associates%20Inc

Group name: N0n
Post title: Company #93
Info: https://cti.fyi/#disclosure/N0n/Company%20%2393

Group name: N0n
Post title: Company #94
Info: https://cti.fyi/#disclosure/N0n/Company%20%2394

Group name: N0n
Post title: Company #95
Info: https://cti.fyi/#disclosure/N0n/Company%20%2395

Group name: N0n
Post title: Company #96
Info: https://cti.fyi/#disclosure/N0n/Company%20%2396

Group name: N0n
Post title: Company #97
Info: https://cti.fyi/#disclosure/N0n/Company%20%2397

Group name: N0n
Post title: Company #98
Info: https://cti.fyi/#disclosure/N0n/Company%20%2398

#ransomware #cti #threatintelligence #cybersecurity #infosec
Media attachmentMedia attachmentMedia attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

NightSpire Ransomware Claim Follows Colorado County System Disruption

Colorado County, Texas, reported a disruption affecting government systems and potentially threatening essential public services. The NightSpire ransomware group claimed responsibility for the disruption

****
#cybersecurity #infosec #incident #ransomware
https://beyondmachines.net/event_details/nightspire-ransomware-claim-follows-colorado-county-system-disruption-o-d-n-s-s/gD2P6Ple2L

BeyondMachinesNightSpire Ransomware Claim Follows Colorado County System DisruptionColorado County, Texas, reported a disruption affecting government systems and potentially threatening essential public services. The NightSpire ransomware group claimed responsibility for the disruption
↩ Reply ♡ 0 · ↻ 0 ↗ Original

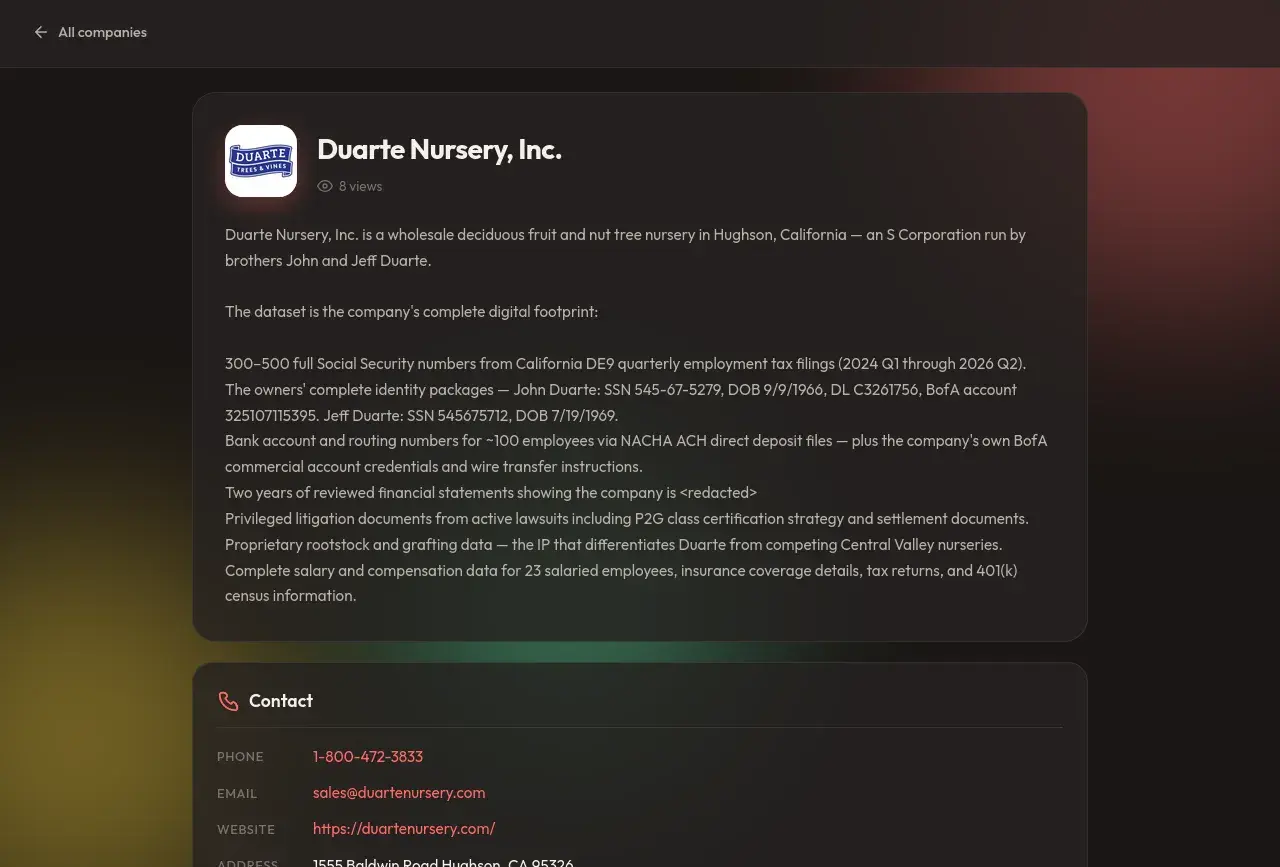
🚨New ransom group blog post!🚨

Group name: aurora
Post title: Duarte Nursery, Inc.
Location: 🇺🇸 US
Sector: Agriculture & Food
Info: https://cti.fyi/#disclosure/aurora/Duarte%20Nursery%2C%20Inc.

#ransomware #cti #threatintelligence #cybersecurity #infosec
Media attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Frazer LLP Discloses 2025 Qilin Ransomware Attack and Data Theft

Frazer LLP, a California accounting firm, confirmed a ransomware attack which occurred in March 2025 claimed by the Qilin group. The firm is offering identity protection services to affected clients.

****
#cybersecurity #infosec #incident #ransomware
https://beyondmachines.net/event_details/frazer-llp-discloses-2025-qilin-ransomware-attack-and-data-theft-k-z-7-2-i/gD2P6Ple2L

BeyondMachinesFrazer LLP Discloses 2025 Qilin Ransomware Attack and Data TheftFrazer LLP, a California accounting firm, confirmed a ransomware attack which occurred in March 2025 claimed by the Qilin group. The firm is offering identity protection services to affected clients.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

We are deeply sorry for the inconvenience of your arrest and are working to resolve it in 5-7 business years.

Operators: coordinate with law enforcement and monitor for gang retaliation activity following high-profile arrests of affiliated threat actors.

Reward: You've received the Handcuffs of Account Termination. They are Soulbound.

https://www.bitdefender.com/en-us/blog/hotforsecurity/qilin-ransomware-arrested-synnovis-patient-death

#Ransomware #Qilin #Synnovis #CyberSecurity (2/2)

Hot for SecurityPolice arrest Qilin ransomware suspect on holiday, as links made to Synnovis hack that contributed to patient's deathA 28-year-old Russian man has been arrested by German police, suspected of being a key member of the Qilin ransomware gang.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🚨New ransom group blog posts!🚨

Group name: payload
Post title: Brüninghoff Group
Location: 🇩🇪 DE
Sector: Construction
Info: https://cti.fyi/#disclosure/payload/Br%C3%BCninghoff%20Group

Group name: payload
Post title: BW Office World
Location: 🇩🇪 DE
Sector: Other
Info: https://cti.fyi/#disclosure/payload/BW%20Office%20World

#ransomware #cti #threatintelligence #cybersecurity #infosec
Media attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

In Japan, the ransomware name everyone knows is Qilin, thanks to the Asahi attack.

On the leak sites, 2026 belongs to The Gentlemen: 23 Japanese organizations listed this year (ransomware.live), vs 15 for Qilin. Group-IB says it grew out of a Qilin affiliate team, and it hands affiliates compromised FortiGates.

The brand changes; the way in doesn't.

https://japancyberwatch.com/articles/japan-ransomware-groups-2026-the-gentlemen-qilin

#ransomware #infosec #Japan #ThreatIntel

japancyberwatch.comJapan's Ransomware Headlines Say Qilin. The Leak Sites Say The GentlemenQilin became a household name in Japan after the Asahi attack. In 2026, a group that grew out of Qilin's own affiliates, The Gentlemen, has listed more Japanese organizations than any other. What the data shows, and why the name matters less than the way in.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

Monitor for updates on ShinyHunters operations and associated ransomware campaigns — this disruption may shake loose affiliates looking for new footing.

Reward: You've received the Scales of Unhinged Justice — a rare cosmetic that glows slightly whenever someone in your party is secretly the villain.

https://krebsonsecurity.com/2026/10/feds-suspect-ransom-negotiator-ran-shinyhunters-extortion-site/

#Ransomware #CyberSecurity #ShinyHunters #Cybercrime #LawEnforcement #BustedIRL (3/3)

krebsonsecurity.comFeds Suspect Ransom Negotiator Ran ShinyHunters Extortion Site – Krebs on Security
↩ Reply ♡ 0 · ↻ 0 ↗ Original

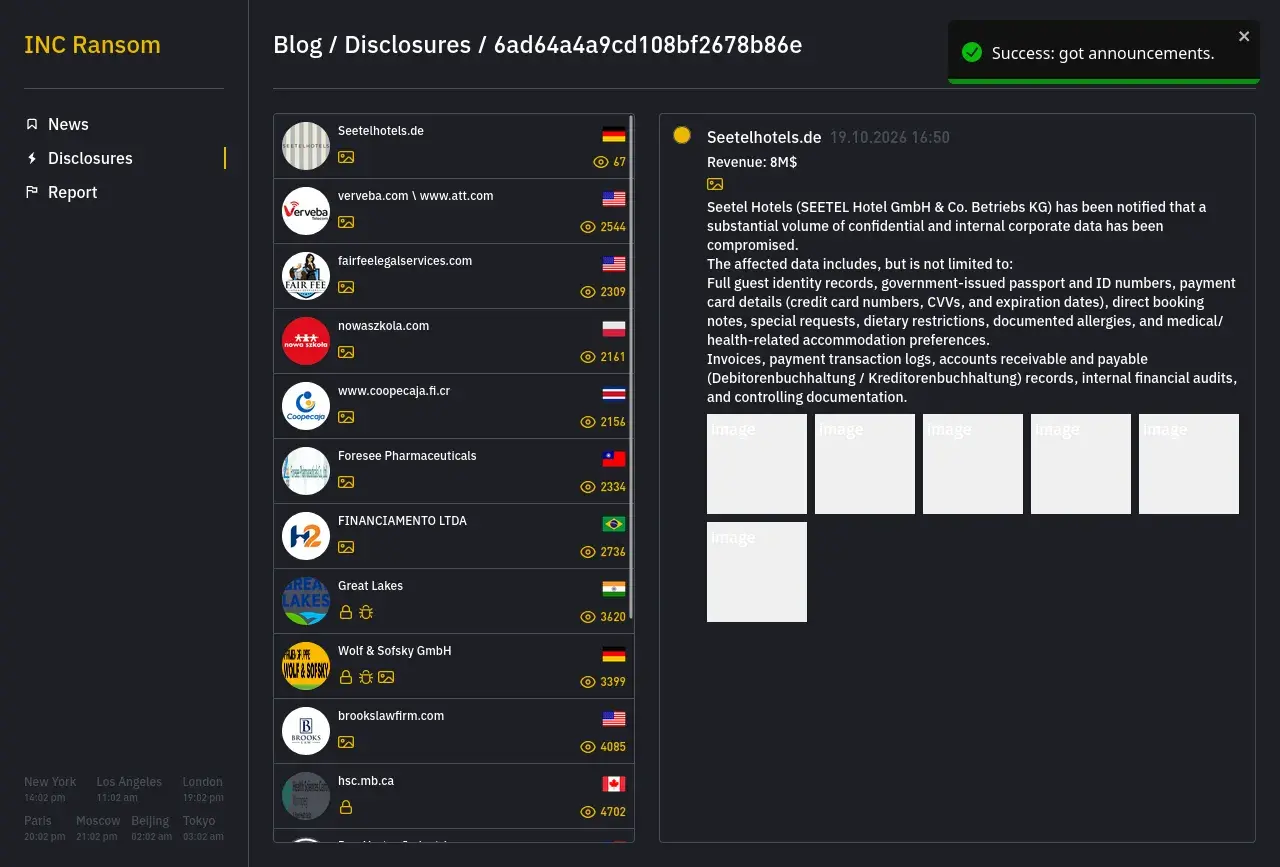
🚨New ransom group blog post!🚨

Group name: incransom
Post title: Seetelhotels.de
Organization: Seetel Hotels
Location: 🇩🇪 DE
Sector: Hospitality & Tourism
Info: https://cti.fyi/#disclosure/incransom/Seetelhotels.de

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

KrebsOnSecurity alleges executives tied to ransomware negotiation services helped operate the ShinyHunters extortion site. Separately, DOJ sentenced a former negotiator in a BlackCat-related extortion case. Both raise integrity risks for third-party incident response. #Ransomware #ShinyHunters #ThreatIntelligence

https://cyberworldops.eu/en/report-alleges-ransomware-negotiation-executives-helped-operate

Report Alleges Ransomware Negotiation Executives Helped Operate ShinyHunters Extortion Site
CyberWorldOpsReport Alleges Negotiators Helped Run ShinyHunters SiteReport says U.S. investigators suspect ransomware negotiators helped run ShinyHunters' Shinywire extortion site, citing anonymous sources.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

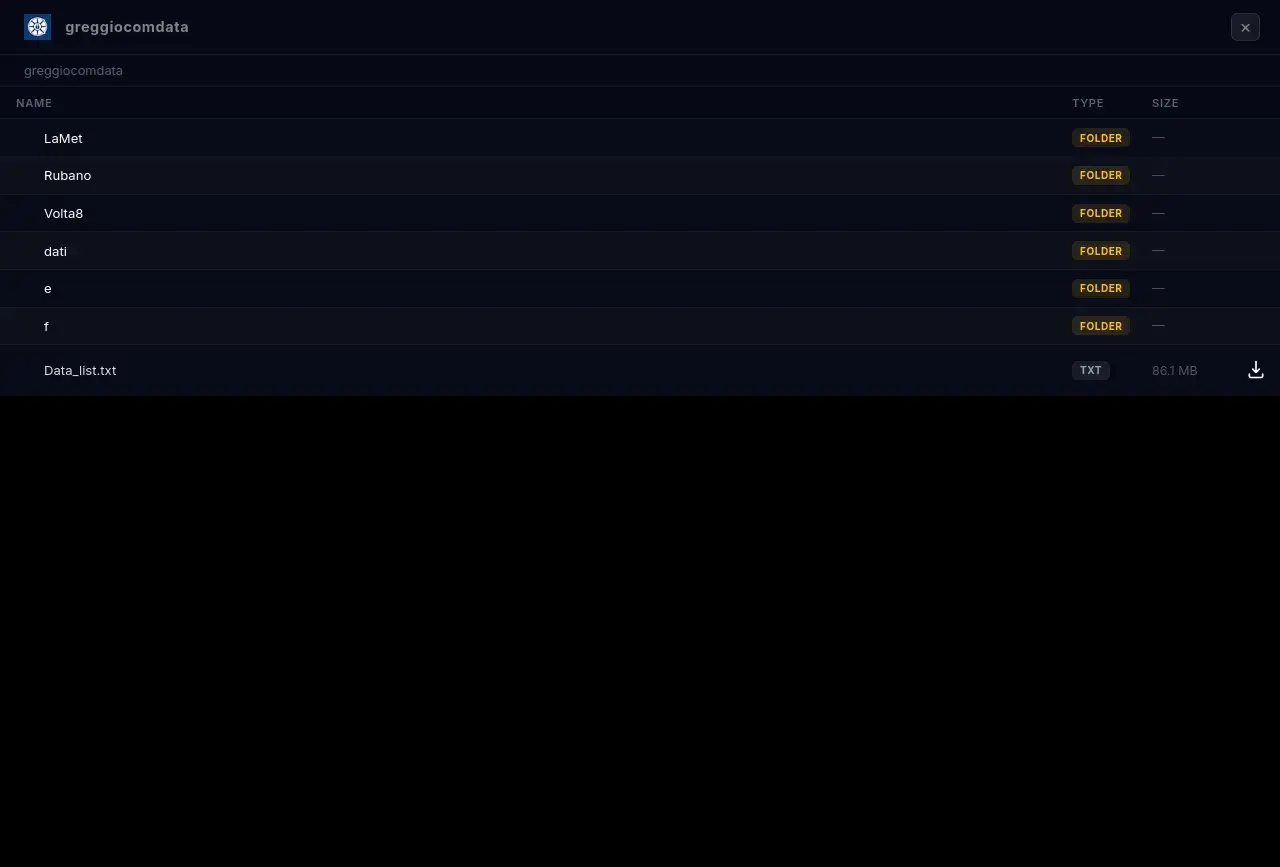
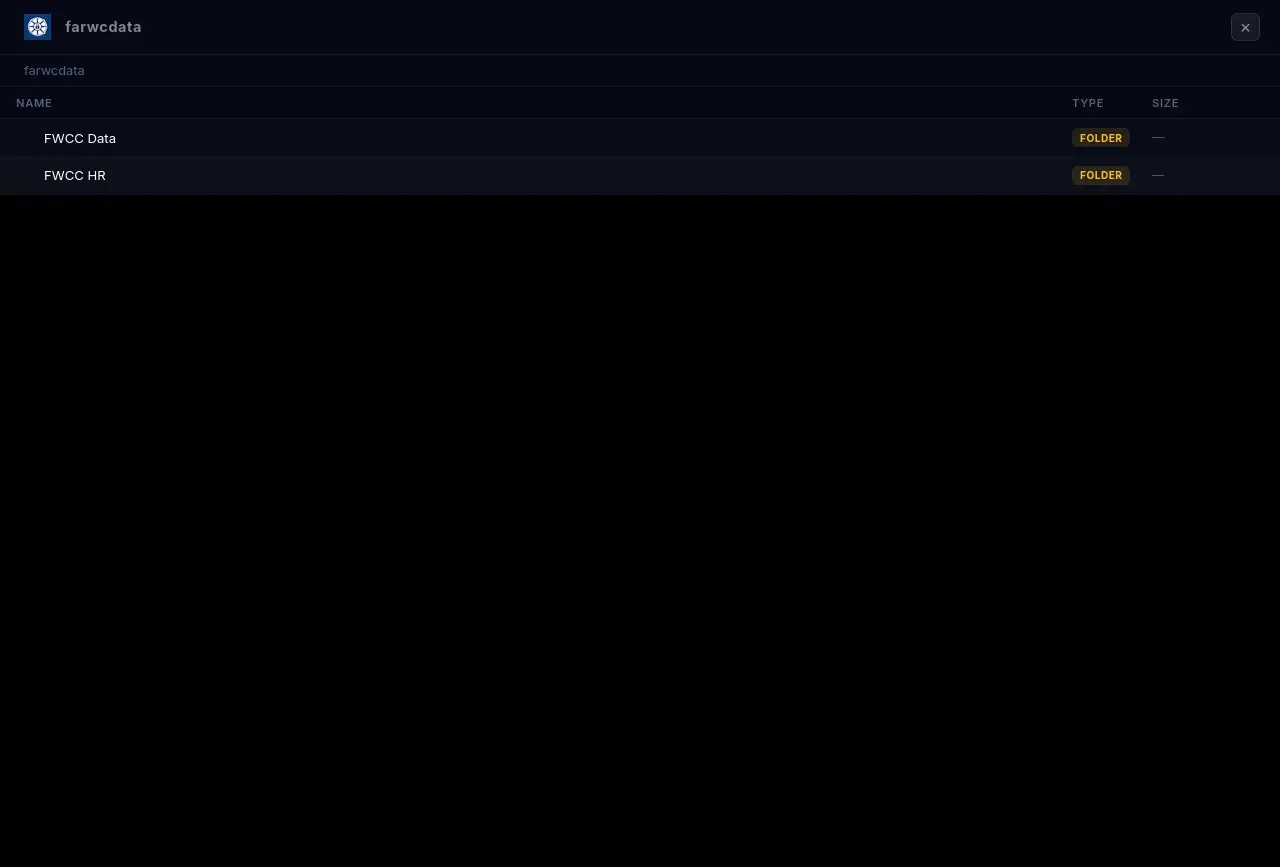
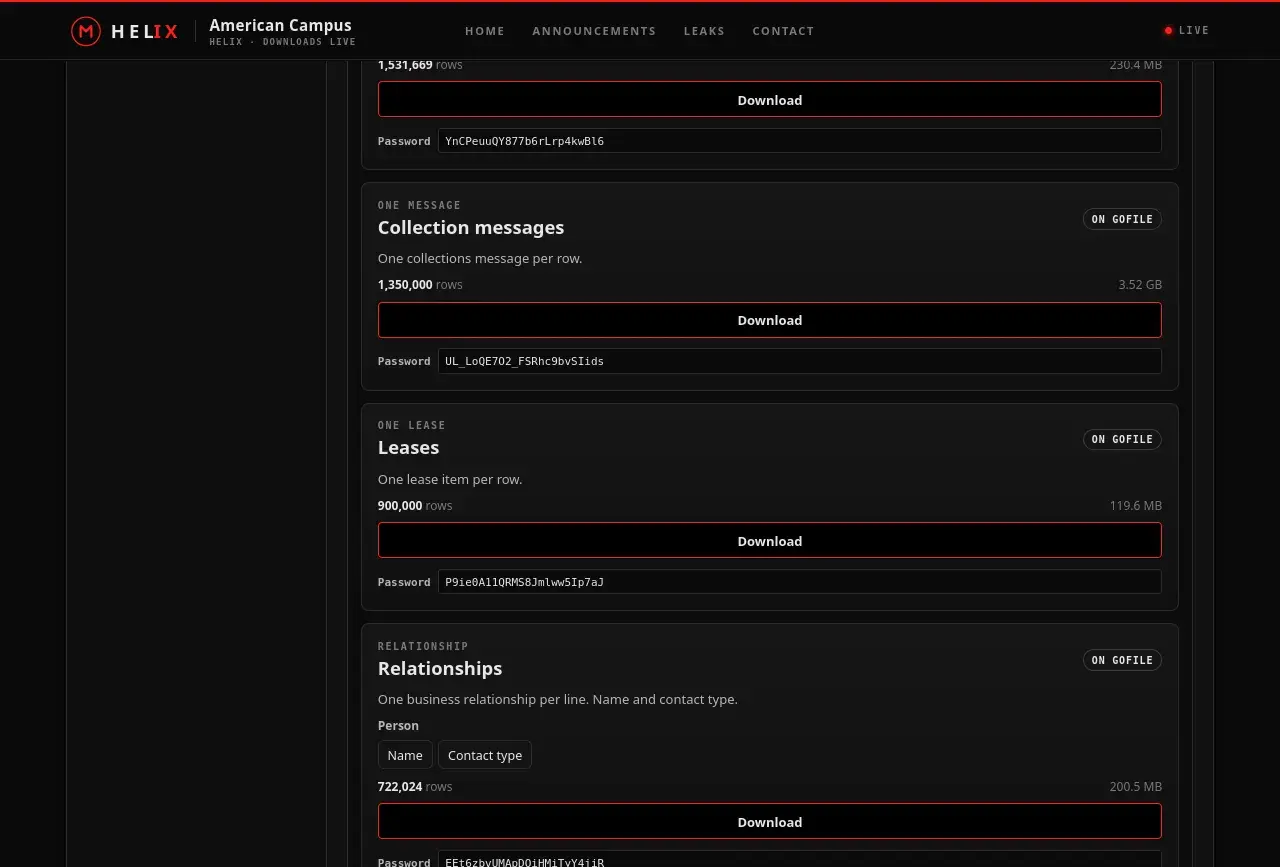
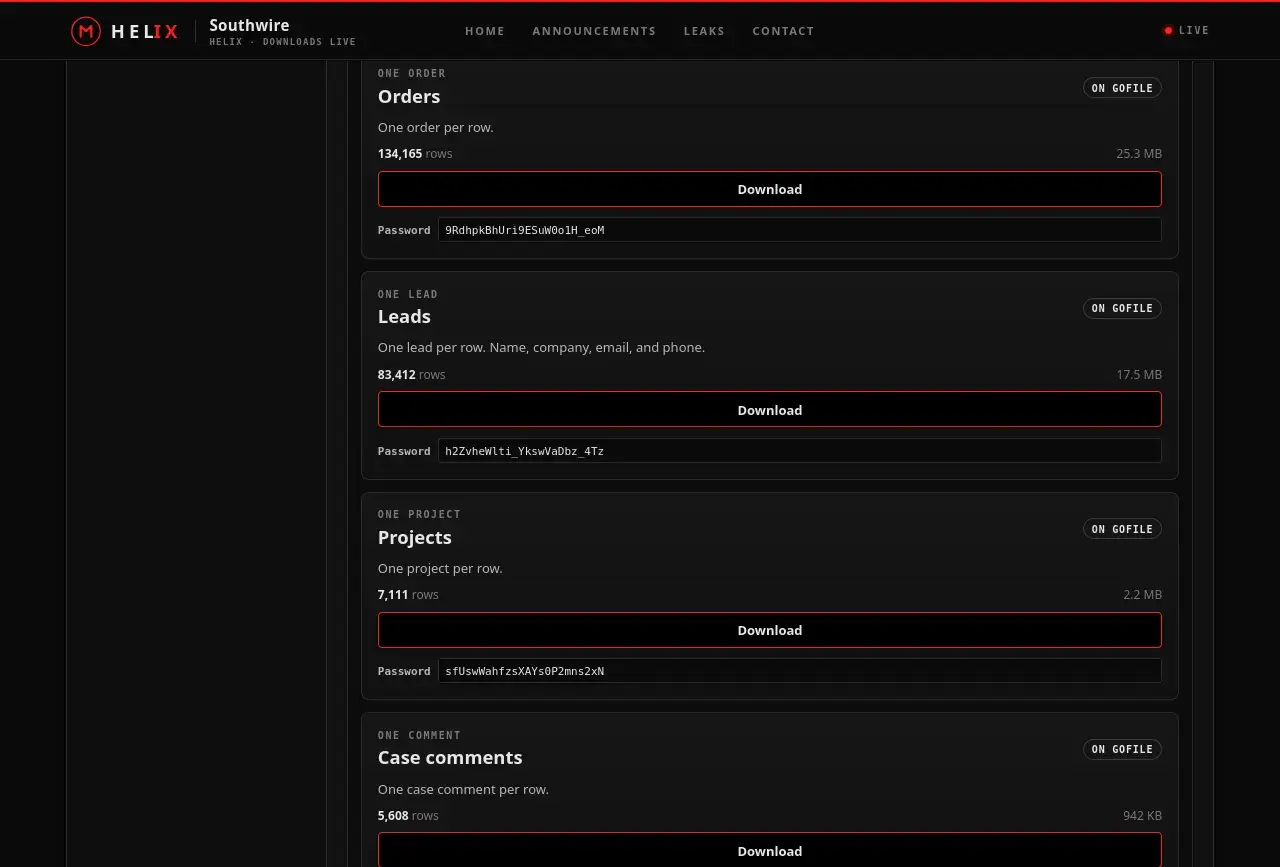
🚨New ransom group blog posts!🚨

Group name: Deadlock
Post title: Greggio Argento
Location: 🇮🇹 IT
Sector: Technology
Info: https://cti.fyi/#disclosure/Deadlock/Greggio%20Argento

Group name: Deadlock
Post title: Far West Contractors
Sector: Construction
Info: https://cti.fyi/#disclosure/Deadlock/Far%20West%20Contractors

Group name: Helix
Post title: American Campus
Location: 🇺🇸 US
Sector: Education
Info: https://cti.fyi/#disclosure/Helix/American%20Campus

Group name: Helix
Post title: Southwire
Location: 🇺🇸 US
Sector: Manufacturing
Info: https://cti.fyi/#disclosure/Helix/Southwire

Group name: Helix
Post title: Quikrete
Location: 🇺🇸 US
Sector: Construction
Info: https://cti.fyi/#disclosure/Helix/Quikrete

Group name: Helix
Post title: Smith Douglas Homes
Location: 🇺🇸 US
Sector: Construction
Info: https://cti.fyi/#disclosure/Helix/Smith%20Douglas%20Homes

Group name: Helix
Post title: Bay Alarm
Location: 🇺🇸 US
Sector: Technology
Info: https://cti.fyi/#disclosure/Helix/Bay%20Alarm

Group name: Helix
Post title: Personify Health
Location: 🇺🇸 US
Sector: Healthcare
Info: https://cti.fyi/#disclosure/Helix/Personify%20Health

Group name: Helix
Post title: Rheem Global
Location: 🇺🇸 US
Sector: Manufacturing
Info: https://cti.fyi/#disclosure/Helix/Rheem%20Global

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachmentMedia attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original