Everything is hacked! This is fine? 🫠
XFEDI
ActivityPubRemote profile
Socket
Socket is a developer-first security platform that protects your code from both vulnerable and malicious dependencies. Next-gen SCA + SBOM + 0-day prevention. LOVED BY DEVELOPERS.
Open remote profile ↗Posts
The PHP Foundation says Chainguard unilaterally broke the embargo and published built images containing the critical RCE fixes more than six hours early:
“This disregarded weeks of work by many parties toward a coordinated disclosure.”
 socket.devPHP Foundation Says Chainguard Broke Security Embargo Ahead of Emergency PatchesThe PHP Foundation says Chainguard broke a security embargo ahead of critical RCE patches, as leaks disrupted the coordinated release.
🚨 PHP has released emergency patches for two critical RCE vulnerabilities. Organizations unable to patch are advised to take affected systems offline.
Believe it or not, PHP still runs an enormous amount of the web. And nearly half of #PHP sites run EOL versions.
The vulnerabilities let attackers execute code on web servers without logging in. Cloudflare is already seeing exploits in the wild.
Patch the PHP runtime now. https://socket.dev/blog/php-critical-rce-patches
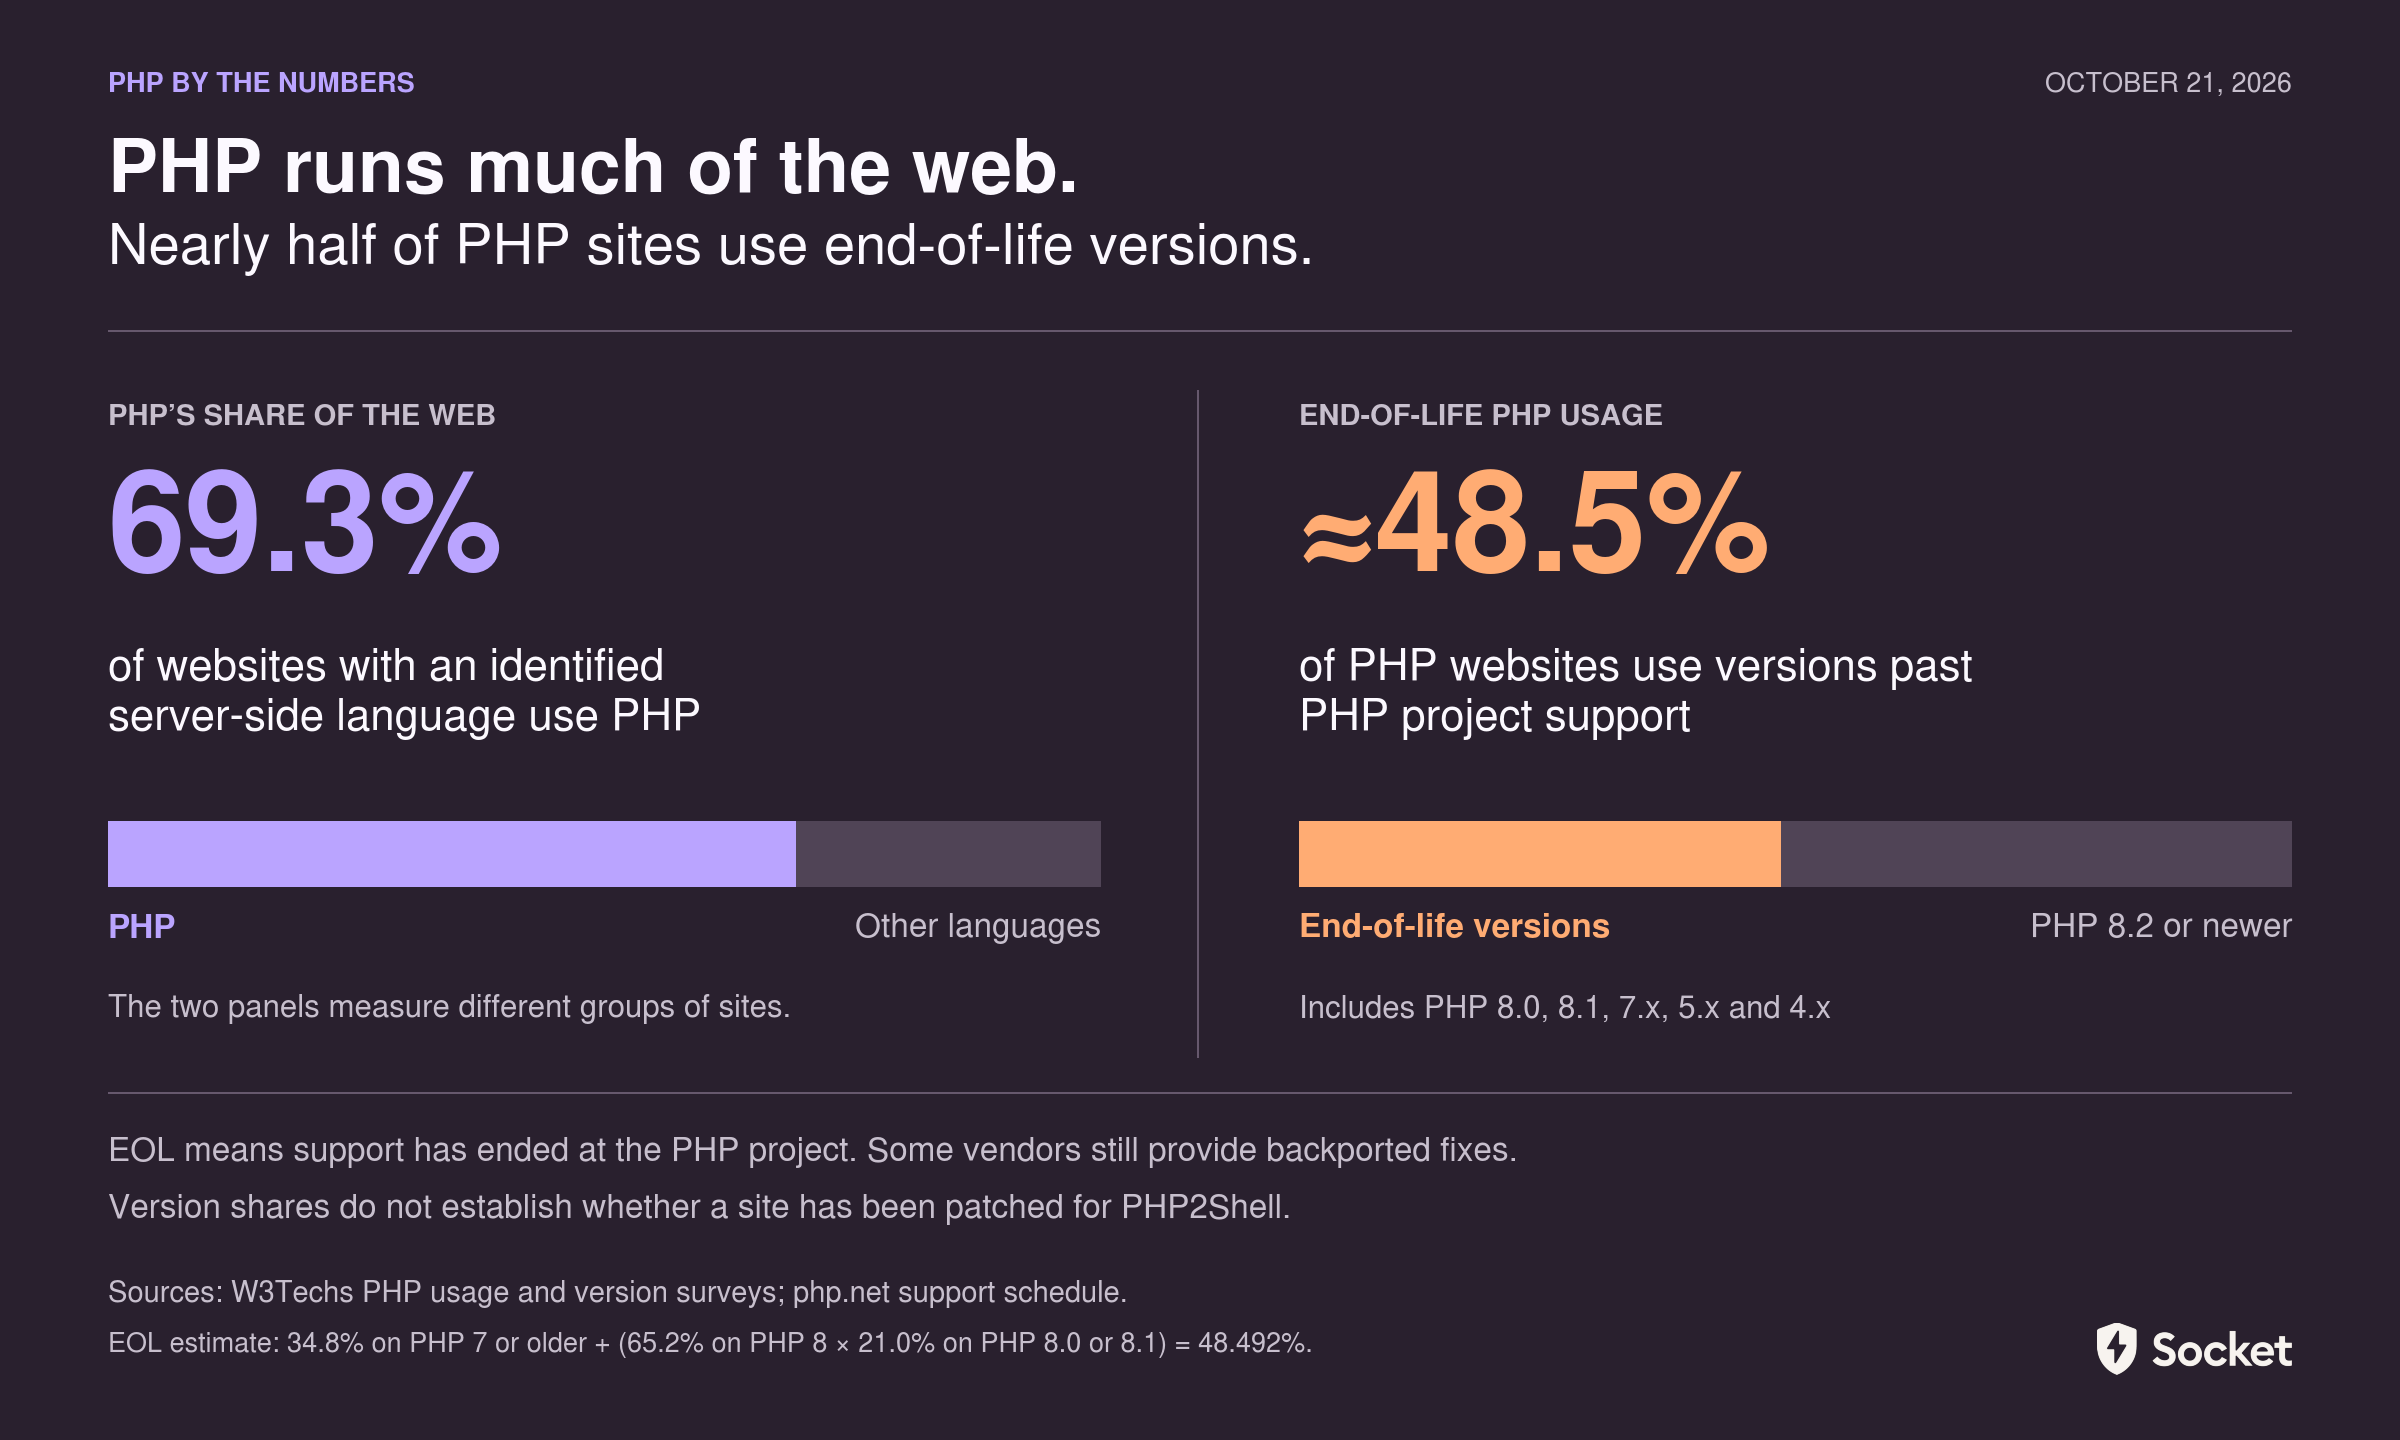
 socket.devPHP Patches Critical RCE Vulnerabilities, Organizations Urged to Take Unpatched Sites OfflinePHP releases emergency patches for two critical RCE vulnerabilities as agencies urge organizations to take unpatched sites offline.
🚨 LiteLLM, a Python package for connecting to AI model providers with 92M+ monthly downloads, has been compromised.
Version 1.107.0 ships credential-stealing malware through PyPI wheels and Docker images, targeting cloud credentials, developer secrets, and AI tools.
The malware runs at Python startup, even without importing LiteLLM. The release workflow built container images from a lookalike repository.
Full analysis: https://socket.dev/blog/litellm-compromise
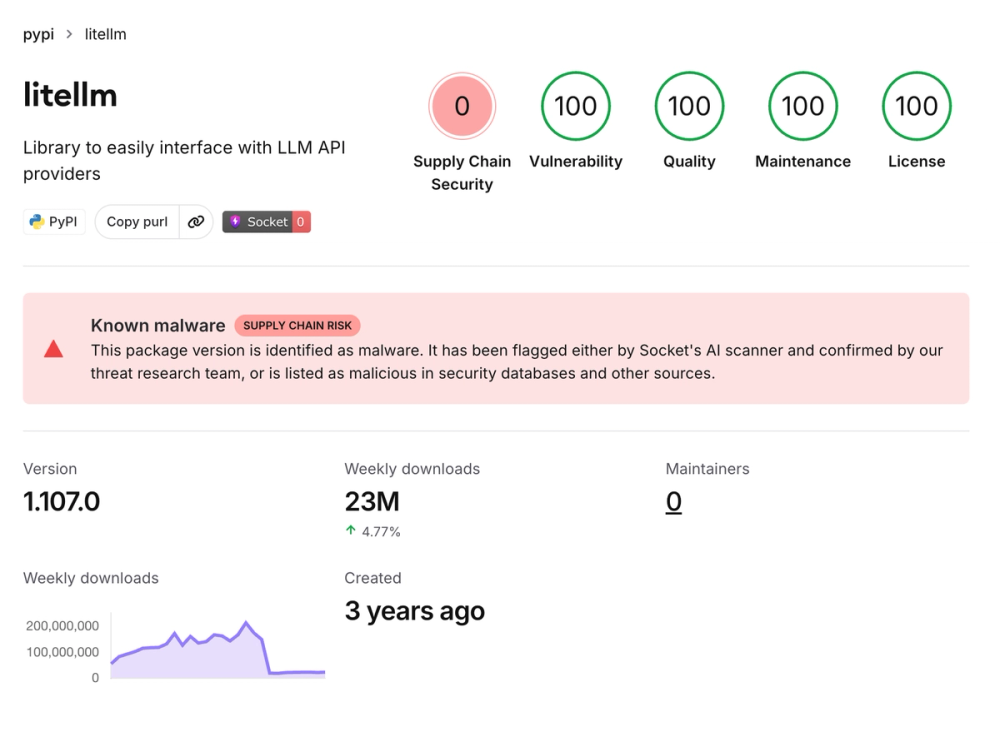 socket.devLiteLLM PyPI Package and Docker Images Compromised to Steal Cloud and AI CredentialsA supply chain attack compromised LiteLLM 1.107.0 on PyPI and Docker, spreading malware that steals cloud credentials, developer secrets, and AI provider keys.
vlt 1.5.0 links agent skills from your dependencies to coding agents, with versions pinned by your lockfile.
The default skills filter uses Socket data to exclude packages flagged as malware before their instructions reach your agents.
 socket.devvlt 1.5.0 Adds Agent Skills Managementvlt 1.5.0 links skills from JavaScript dependencies to coding agents, with lockfile versioning and Socket data to filter out known malicious packages.
🧊 Rust 1.100 will let developers put fresh dependency releases on ice.
Cargo’s opt-in cooldowns give researchers and maintainers time to catch malicious crates before more projects pull them in.
 socket.devRust 1.100 Will Add Dependency Cooldowns to CargoRust 1.100 will add opt-in dependency cooldowns to Cargo, giving security scanners and maintainers time to catch malicious crate releases.
Don't tell Michael Scott the bankruptcy system is down 🤐